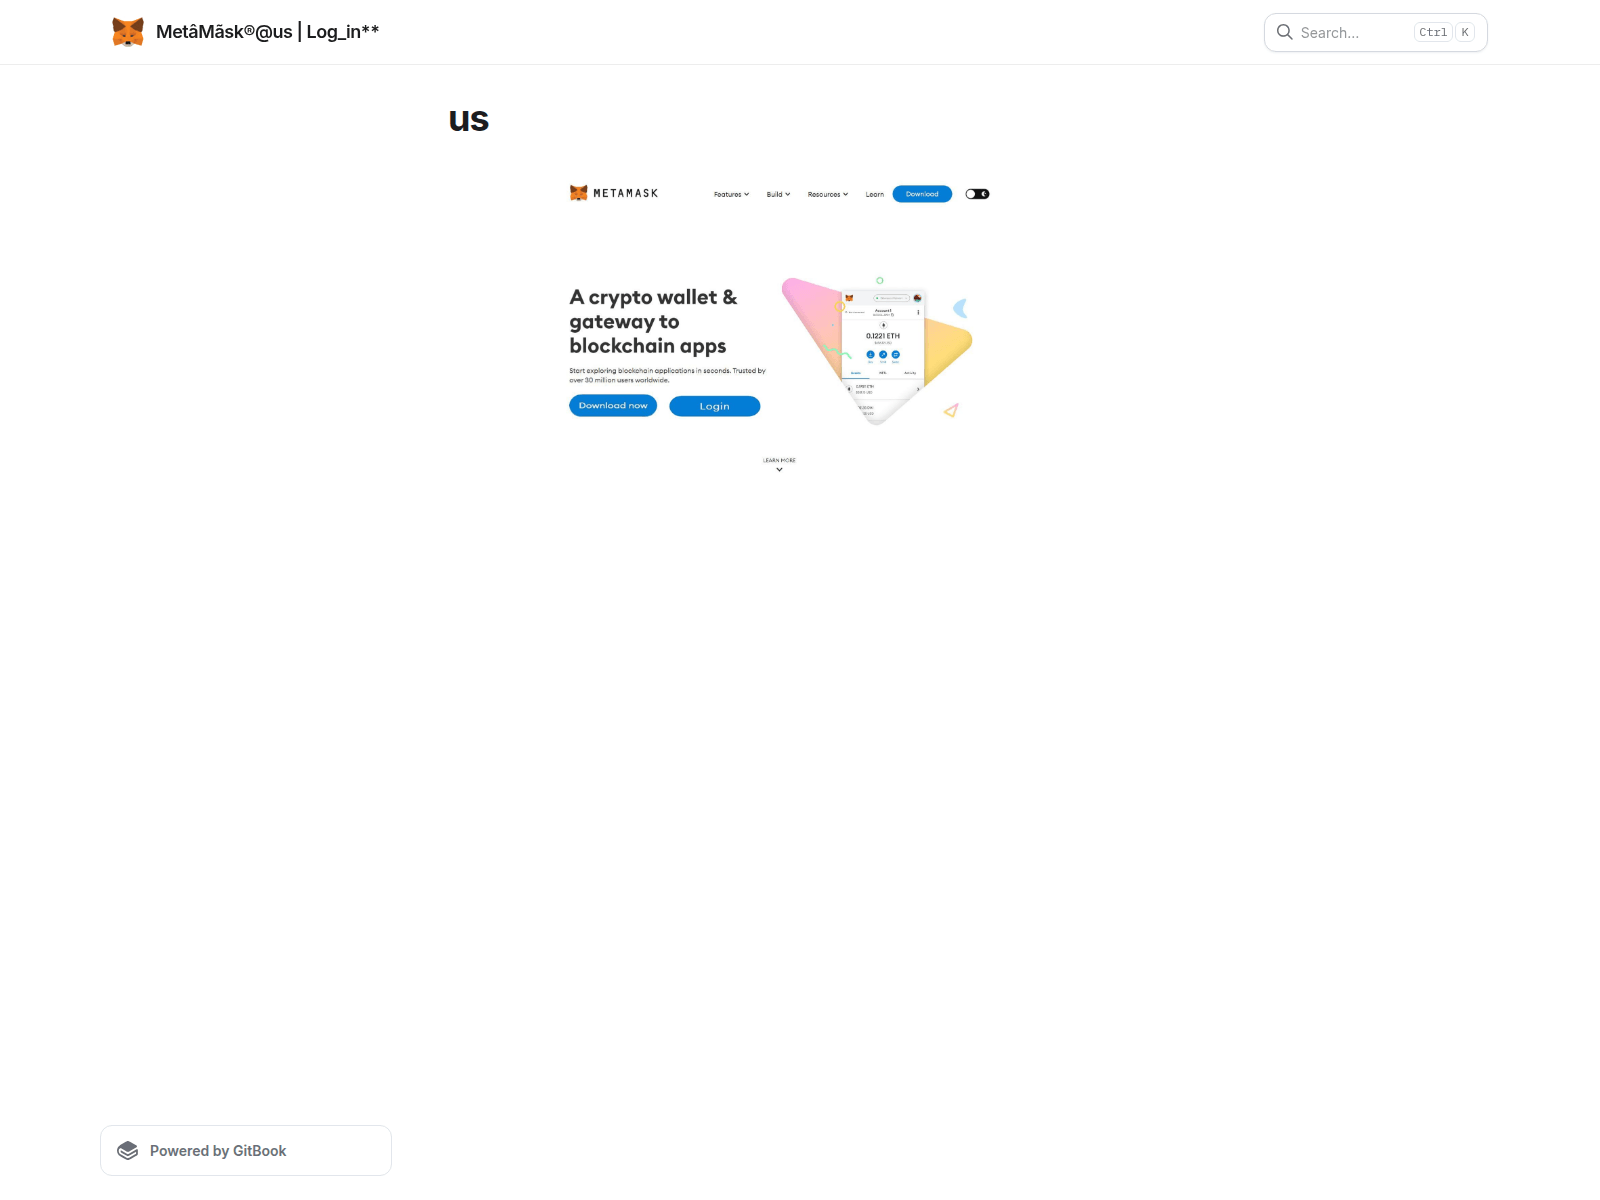
The captured metamzklogana.gitbook.io page is a GitBook document headed "MetāMāsk®@us | Log_in" with a search field and a "Powered by GitBook" badge. Its main content is an embedded landing section branded "METAMASK" with navigation links for Features, Build, Resources and Learn, plus a Download button. The landing section presents the headline "A crypto wallet & gateway to blockchain apps" alongside a wallet illustration, with "Download now" and "Login" buttons and a "LEARN MORE" link below.
URLScan截图 · 2026-11-07 13:37 UTC · SHA-256 1d581e8f…c8e0663
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
The captured metamzklogana.gitbook.io page is a GitBook document headed "MetāMāsk®@us | Log_in" with a search field and a "Powered by GitBook" badge. Its main content is an embedded landing section branded "METAMASK" with navigation links for Features, Build, Resources and Learn, plus a Download button. The landing section presents the headline "A crypto wallet & gateway to blockchain apps" alongside a wallet illustration, with "Download now" and "Login" buttons and a "LEARN MORE" link below.
The stored VirusTotal domain result reports 13 detections out of 92 engines. ESET reported "phishing"; VIPRE reported "phishing".
metamzklogana.gitbook.io: GitBook page with MetaMask-branded landing
AI 描述
PhishDestroy records metamzklogana.gitbook.io as a GitBook page headed MetāMāsk®@us | Log_in showing an embedded MetaMask-branded landing section.
AI摘要
The captured metamzklogana.gitbook.io page is a GitBook document headed "MetāMāsk®@us | Log_in" with a search field and a "Powered by GitBook" badge. Its main content is an embedded landing section branded "METAMASK" with navigation links for Features, Build, Resources and Learn, plus a Download button. The landing section presents the headline "A crypto wallet & gateway to blockchain apps" alongside a wallet illustration, with "Download now" and "Login" buttons and a "LEARN MORE" link below. The stored VirusTotal domain result reports 13 detections out of 92 engines. ESET reported "phishing"; VIPRE reported "phishing".
The website's owner is hiding his identity on WHOIS using a paid service This website does not have many visitors This website is being iframed by another website IPQS flagged this website for Phishing IPQS has flagged this website as suspicious
According to the SSL check the certificate is valid The owner of the site has claimed the domain name for a long time This website has existed for quite some years DNSFilter considers this website safe
最新的 HTTP 观察结果RedirectingHTTP redirect observed80%2026-11-21 11:26 UTC
RDAP注册
观测时间线last reachable: 2026-11-21 11:26 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.