URLQuery
2 det.
打开报告

PhishDestroy 于 2026-10-27 首次记录了 mainnetvault-portal.com。被外部黑名单列入:ScamSniffer。
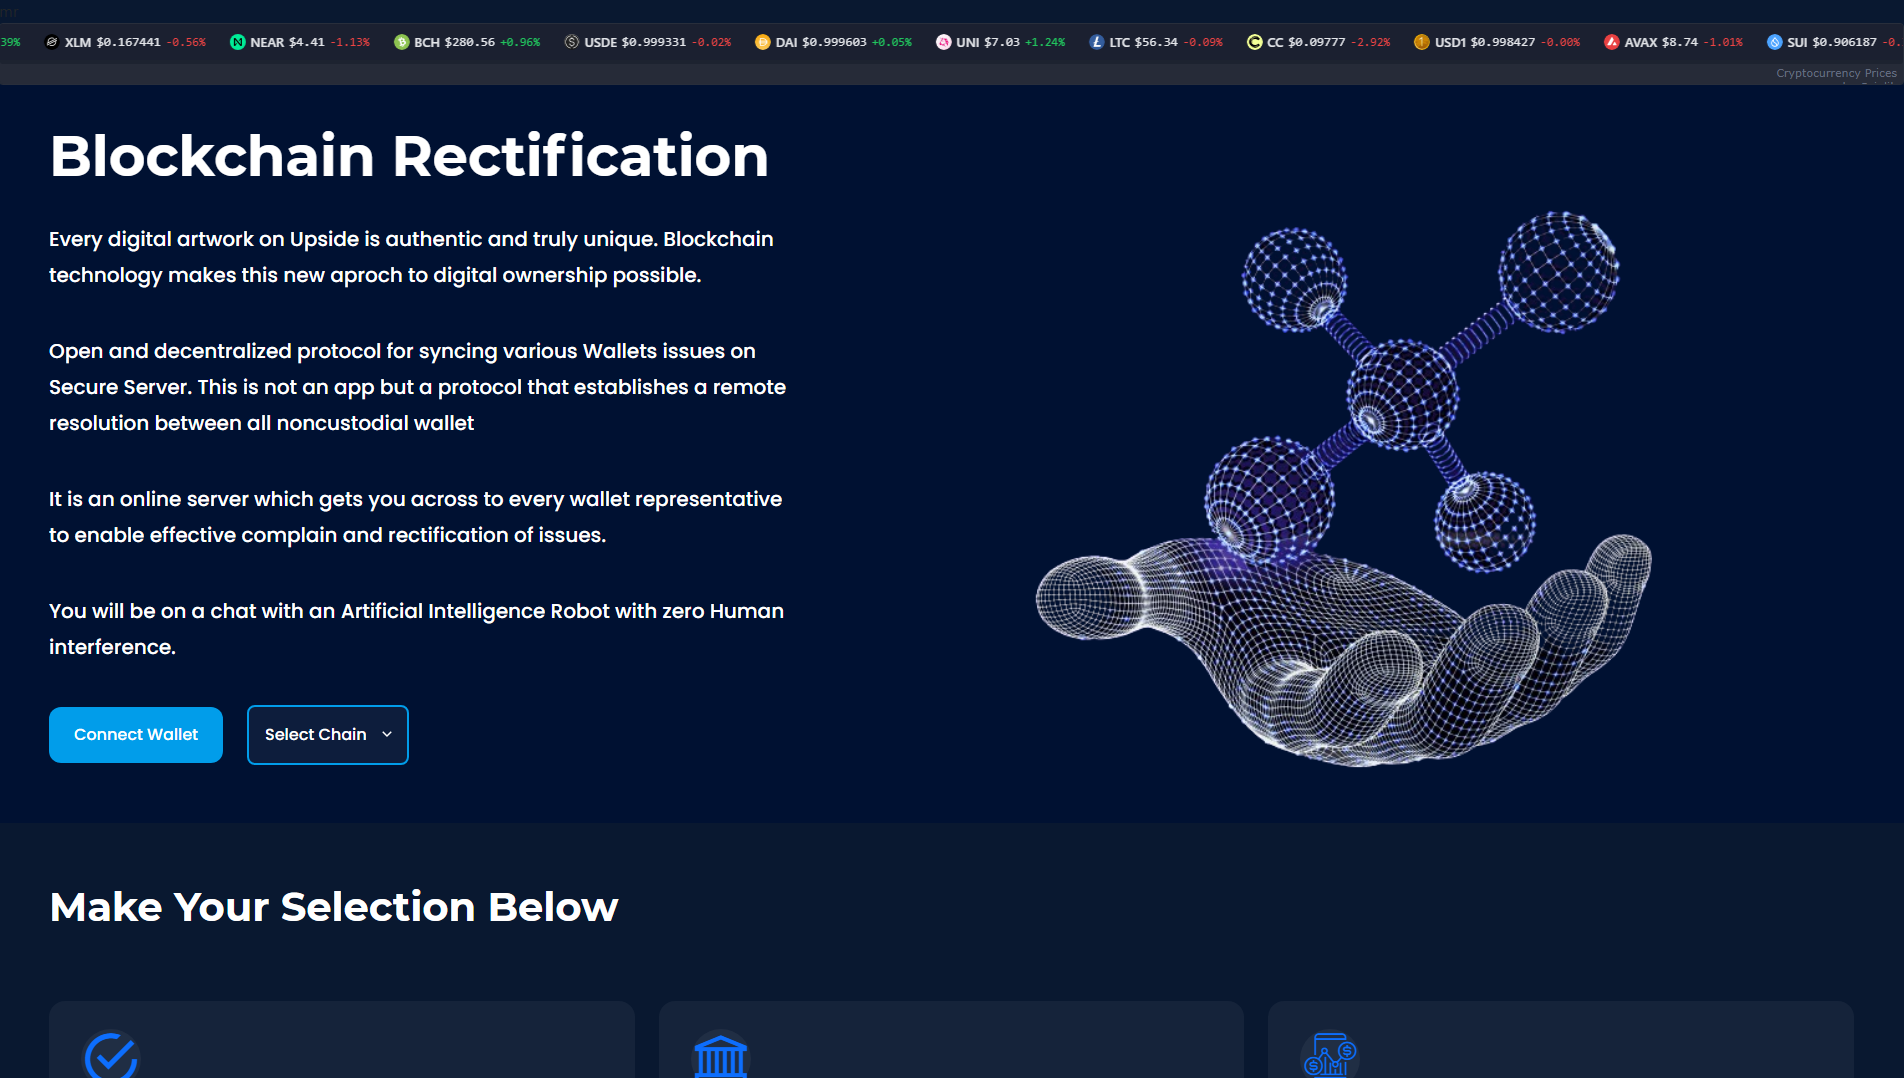
页面标题: “Blockchain Rectification - We are here to help you resolve your crypto related issues”
选择实际发生的情况,并随着操作进程逐项勾选相应步骤。勾选记录仅保存在当前浏览器中。
专家视图包含所有部分:DNS、TLS、网络请求、哈希值以及原始 JSON 数据。
已发送报告日志记录了首份外发报告的时间为 。记录的收件人是 abuse@joker.com. 最新的存储可用性证据仍显示该域名可访问; 26 days 自首份外发报告发布以来,已过去……
ICANN RAA §3.18 描述了域名注册商的滥用联系渠道及处理义务。本节记录了发送时间戳、收件人列表、案件标识符以及后续的可用性。本节内容本身并不构成对收件、确认、调查、整改或合同违约的证明。
PhishDestroy 保存了 mainnetvault-portal.com 的记录。各来源的观测有各自的日期;缺少检查并不代表安全。
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
PhishDestroy 于 2026-10-27 首次记录了 mainnetvault-portal.com。被外部黑名单列入:ScamSniffer。风险:严重(证据评分 100/100)。注册商:CSL Computer Service L…。状态:可达 · 访问受限。托管:Cloudflare, Inc。PhishDestroy 已发送1 份滥用举报。请勿输入登录凭据,也不要连接钱包。
 172.67.203.37Cloudflare, Inc. · CDN
 CSL Computer Service L…
PhishDestroy分析,早期未经审核的版本
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
PhishDestroy’s intake AI classified the domain as malicious because the recorded page title advertises a “Blockchain Rectification” service and the page excerpt describes a “Connect Wallet” flow for deposit, withdrawal, asset recovery and reward claims. The domain was first seen by PhishDestroy on 2026-10-27, eight days after its registration on 2026-10-19. An HTTP 200 response with the recorded title was captured on 2026-10-27.
In a wallet‑drainer scheme the attacker presents a bogus support or recovery service and convinces the victim to link a non‑custodial wallet via a Web3 connection. Once linked, the site can request transaction approvals that transfer funds to addresses controlled by the attacker without needing the victim’s private keys. The victim’s consent to approve transactions is the only requirement for the theft.
VirusTotal scanned the domain on 2026-10-27 with 92 engines and reported zero malicious or suspicious detections, and Google Safe Browsing also returned a clean result on that date. PhishDestroy’s internal blocklist flagged the domain as malicious on 2026-10-27, and OTX recorded two pulses mentioning it on the same day. A urlscan capture from 2026-10-20 showed a 403 response and an engine‑based malicious score of 40 with tags urlscan‑ml and urlscan‑ml‑60c5e22, while its overall verdict was clean.
The domain was registered on 2026-10-19 through CSL Computer Service Langenbach GmbH d/b/a joker.com. DNS records at the time resolved to Cloudflare IP addresses 104.21.74.133 and 172.67.203.37, indicating the site was served behind Cloudflare’s CDN. The TLS certificate, issued by Let’s Encrypt, was valid from 2026-10-19 to 2027-01-23, and no DNSSEC records were observed.
Users should not click any “Connect Wallet” button on this site and must never share private keys or seed phrases; if a wallet was connected, revoke all approvals and consider moving funds to a new wallet. Organizations should add mainnetvault-portal.com to their blocklists and monitor network logs for any attempts to access the domain or initiate wallet connections. Security teams can enrich threat‑intel feeds with the recorded registration and hosting details to aid correlation with other incidents.
2 det.
打开报告网络钓鱼
打开报告本摘要与上方的带日期扫描件有所不同。为保留来源信息,本摘要予以保留,但不会覆盖所选的源观测数据。
25/100
可信度评分,数值越低,情况越糟
打开报告恶意
SHA-256 834f9e05…0c408c2
单独存储的监控快照;不会替换主报告记录,也不会确定当前的可用性。
2 community references
打开报告78 / 100 · 启发式得分 · 0 个品牌引用 · 1 个分类
仅为内容启发式评分;并非最终评分
打开报告此过时的监控分析与上文的主要PhishDestroy分析是分开的。启发式评分并非经过测量的概率。
叙事生成元数据
打开报告叙述生成日期与观测日期不同。这些是保留的出版字段,并非额外的独立检测结果。
结果反映各来源的采集时间。零检出不代表安全。OTX 引用为社区发布的内容。
已存档的页面、网络和扫描器观测结果,按来源和观测时间分组。
| 邮件配置 | MX: _dc-mx.c44e1e9bd1ad.mainnetvault-portal.com; Spf: v=spf1 +a +mx +ip4:142.44.137.26 ~all; Dkim: default; Dkim bits: 2048; Spf lookups: 0 |
|---|---|
| CAA 记录 | Domain: mainnetvault-portal.com |
| DNS防护结果 | Resolvers: 12; Blocked count: 0 |
| 网络档案观察 | Last: 2026-10-27T05:56:33Z; First: 2026-10-27T05:56:33Z; Changes: 0; Days archived: 1; Avg page bytes: 5208 |
| 页面标题与元数据 | Title: Blockchain Rectification - We are here to help you resolve your crypto related issues; Keywords: ethereum, cryptocurrency, wallet, mobile, connect, bridge, relay, proxy, standard, protocol, crypto, tokens, dapp; Themecolor: #ffffff; Description: 1. Click the above, 2. Select Issue Type 3. Select Wallet Type, 4. Input Necessary information, 5. Validate; Twittercard: Summary large image; Twittersite: @syncwallet |
| 追踪器 | Requests: 98; Trackers: (Name: Google Tag; Company: Google; Country: US; Category: Advertising; Requests: 1), (Name: Microsoft Clarity; Company: Microsoft; Country: US; Category: Site Analytics; Requests: 1) |
| 表单与混合内容 | Third party scripts: 0 |
| 状态 | Up: ✓; Code: 200; Timings: DNS: 13; TLS: 15; Wait: 399; Connect: 19; Download: 0; Response ms: 446 |
| TLS连接 | Alpn: h2; Cipher: TLS_AES_256_GCM_SHA384; Protocol: TLSv1.3; Versions: TLSv1, TLSv1.1, TLSv1.2, TLSv1.3; Authorized: ✓; Forward secrecy: ✓ |
| 端口 | Open: 80, 443, 8080 |
| Carbon | Bytes: 27383; Co2 grams: 0.001; Cleaner than: 50 |
| DNS server | NS: (IP: 162.159.44.127; Host: thaddeus.ns.cloudflare.com), (IP: 172.64.32.67; Host: ara.ns.cloudflare.com); Zone: mainnetvault-portal.com |
| 位置 | IP: 2606:4700:3033::ac43:cb25; ASN: 13335; Org: Cloudflare, Inc.; City: Toronto; Country: CA |
| SSL | Issuer: Let's Encrypt / YE2; Subject: mainnetvault-portal.com |
| DNS 记录 | A: 104.21.74.133, 172.67.203.37; MX: Exchange: _dc-mx.c44e1e9bd1ad.mainnetvault-portal.com; Priority: 0; NS: ara.ns.cloudflare.com, thaddeus.ns.cloudflare.com; Soa: Nsname: ara.ns.cloudflare.com; Hostmaster: dns.cloudflare.com; Serial: 2418428137; Refresh: 10000; Retry: 2400; Expire: 604800; Minttl: 1800; Txt: v=spf1 +a +mx +ip4:142.44.137.26 ~all, google-site-verification=TE5eJvGCPGIi2nx7cPXfVGZAGH5dSyGae9wZs4pBn6s, v=spf1 ip4:142.44.137.26 +a +mx +ip4:66.70.150.237 ~all; Aaaa: 2606:4700:3033::ac43:cb25, 2606:4700:3033::6815:4a85 |
| DNSsec | Ds: ✗; Rrsig: ✗; Dnskey: ✗ |
| Hsts | Message: Site does not serve any HSTS headers. |
| HTTP 安全策略 | Xframeoptions: SAMEORIGIN; Referrerpolicy: strict-origin-when-cross-origin; Xxssprotection: 1; mode=block; Permissionspolicy: geolocation=(), microphone=(), camera=(); Xcontenttypeoptions: nosniff; Contentsecuritypolicy: ✗; Stricttransportpolicy: ✗; Crossoriginopenerpolicy: ✗; Crossoriginembedderpolicy: ✗; Crossoriginresourcepolicy: ✗ |
| 防火墙 | Waf: Cloudflare; Has waf: ✓ |
| Get IP | IP: 2606:4700:3033::6815:4a85; Family: 6 |
| 重定向 | Chain: https://mainnetvault-portal.com |
| 技术栈 | Technologies: Bootstrap, React, toastr, OWL Carousel, Select2, jQuery, decimal.js, Cloudflare, HTTP/3 |
| 社交媒体资料 | Profiles: https://x.com/syncwallet |
| 页面链接 | External: https://coinlib.io/; External count: 1; Internal count: 1 |
| 注册记录 | Registrar: CSL Computer Service Langenbach GmbH d/b/a joker.com; Created: 2026-10-19T18:24:36Z; Updated: 2026-10-25T11:30:13Z; Expires: 2027-10-19T18:24:36Z; Status: clientTransferProhibited https://icann.org/epp; Nameservers: ara.ns.cloudflare.com, thaddeus.ns.cloudflare.com |
| HTTP 头 | Headers: Server: cloudflare; Content type: text/html; X frame options: SAMEORIGIN; X content type options: nosniff; Referrer policy: strict-origin-when-cross-origin; Permissions policy: geolocation=(), microphone=(), camera=() |
 Scamadviser 警告 25/100
根据记录在案的证据,PhishDestroy将mainnetvault-portal.com评定为严重风险等级(证据评分 100/100);该记录首次出现于2026-10-27。被外部黑名单列入:ScamSniffer。本站评分和名单收录本身不能证明欺诈。请核对每个来源的日期和具体网址。
鉴于上述风险信号,请勿在此处连接钱包、签署消息或approve代币权限。已确认的区块链交易无法撤销。
请保留地址、日期、付款或交易详情以及相关信息,以便向警方或其他主管机关报案。 报案并不保证能追回款项。 分步帮助指南:紧急处理指南。
最近检查
4e5367e7e375582947085e0d8d11297cab81a215d82bfee0f2c125adeb821557 · 14518 bytes 2dab10d601e94830cec84eaf231d391def9711e4ec89c6c70df800908e123543 · 240272 bytes 78ff1a8255e182915108365b4465589d3a75f19117fdf295a35bfaa78e513b5b · 240538 bytes 3d272048f569ea12f0491458038f91f045f8d7e7e87252d5e8e511e9872cb7d0 · 6546 bytes b09d5c057626e4e62aa6220c8ed54ed8181721735df27d905311d1fe3b6959e9 · 240493 bytes dc9108cd7f3124046d982b41ac080c372eb897551f92c56cf76eedd3b6145dd5 · 18309 bytes 03811baf12590fae0e462067066b29d1398c20f8c6b6dd2f6e39c4db34395995 · 636407 bytes  172.67.203.37 Cloudflare 共享边缘 源IP已隐藏 Edge-IP 声誉不属于此域。 (US) 172.67.203.37Toronto, CA
Edge-IP 声誉不属于此域。
ara.ns.cloudflare.comthaddeus.ns.cloudflare.comnsname: ara.ns.cloudflare.comhostmaster: dns.cloudflare.comserial: 2418428137refresh: 10000retry: 2400expire: 604800minttl: 1800_dc-mx.c44e1e9bd1ad.mainnetvault-portal.compriority 0位置信息描述的是 IP 网络。
ce704fab08b8209d4193b9c71288f872d0a85e4b6335dbb456f420b729efc696*.mainnetvault-portal.commainnetvault-portal.com已保存的证书元数据。未带时区的证书日期按存档原样显示。传输加密并不能证明该网站值得信任。
Google PageSpeed Insights — 移动端性能审核: mainnetvault-portal.com ·
由本地采集流程保留的带时间戳的响应元数据。以下各项数值均对应所显示的存档时间。
http://mainnetvault-portal.com/Content-Type: text/htmlCache-Control: public, max-age=2592000服务器: cloudflareCF-Cache-Status: DYNAMICContent-Encoding: gzip690fa85f5ec82895fdff952710956e160f029b76183006b2e028465229d6bd49summary_large_imageh2=":443"; ma=60public, max-age=2592000DYNAMICa50f744568539bf7-FRAkeep-alivegziptext/htmlTue, 27 Oct 2026 05:55:51 GMTThu, 26 Nov 2026 05:55:51 GMTTue, 11 Jun 2024 06:33:16 GMT{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}geolocation=(), microphone=(), camera=()strict-origin-when-cross-origin{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=HcXsV9xK7VfxbJKYhTd1Uaha%2FAAR8iuPfdKf9sCWuUAFbiKkIBrAXOpNmhGDKO7pPP80wp1KYyL46QHvWrRxmrZh%2Bgr1iGtomykIhoibQHnURyEvGlPUtjc3M3Z5ATU02a88HHfmkwqcloudflarechunkedAccept-EncodingnosniffSAMEORIGINLiteSpeed1; mode=block由采集器保留的数值;较长的值可能在采集时被截短。
估算时间描述的是一个观测时间窗口。它并不能证明注册商采取了措施,也不代表网站变为不可访问的确切时刻。
网络请求: 101 SHA-256 哈希值: 100 URLScan扫描:
URLScan在加载页面时记录的网络请求。URLScan并非为每个请求都提供哈希值。 PhishDestroy 于 2026-10-29 01:55 UTC 检索到了此列表。
在 URLScan 上打开此扫描 01a17c13-be83-7328-aa8d-4e67325700d3 ↗
加载已保存的数据;不会打开该可疑网站。
| # | 网络请求 | HTTP方法 · 状态码 | 类型 | 未压缩大小 | 响应正文的SHA-256哈希值 |
|---|
比较浏览器与爬虫各自收到的内容,并检查是否存在 Keitaro 流量分发。
我们的扫描器无法完成此项检查。
mainnetvault-portal.com 已记录事件:15。这些记录描述了收集到的证据、外发通知及黑名单发布情况;它们并不意味着调查已完全结束或该网站已被下线。
生命周期
在注册后7天 12小时报告
我们扫描可疑网址,审查公开检测结果,并通过相应的滥用举报渠道提交证据。上方的带日期事件记录了该域名的相关记录。下方的目录说明了更全面的工作流程。
捕获渲染后的页面、请求以及可见的基础设施。
比较各引擎的检测结果,并保留分析时间戳。
检查Google当前是否将该URL列为不安全。
查看公开扫描结果及其记录的网络和分类数据。
查找相关指标参考及相关社区情报。
对比存档的截图并保留历史背景信息。
查找匹配的指标及相关威胁记录。
检查证书记录及相关主机名。
比较安全解析器的响应,并记录观察到的拦截情况。
检查公共DNS、TLS、HTTP及技术暴露面。
用于扫描、信誉检查和报告的安全服务列于下方。某项服务被列出并不意味着该服务已收到、接受或针对该特定域名采取了行动。已记录的提交内容显示在上方通知历史记录中。
 GoogleSafe Browsing↗ GoogleWeb Risk↗
 MicrosoftSmartScreen↗
 VirusTotalURL分析↗
 Cloudflare雷达 / 滥用行为举报↗
 YandexSafe Browsing↗
 URLScan.io公开扫描↗
 ESET示例 / URL 提交↗
 BitdefenderURL提交↗
 NortonSafe Web↗
 Symantec网站评审↗
 AviraURL 报告↗
 Avast / AVGURL 报告↗
 卡巴斯基OpenTIP↗
 Dr.Web在线扫描器↗
 Netcraft滥用行为报告↗
 PhishTank社区举报↗
 APWG eCX网络钓鱼情报↗
 PhishStats公开信息流↗
 Phish.Report主机滥用↗
 Spamhaus域名声誉↗
 PolySwarm多引擎分析↗
 CheckPhishURL 扫描↗
 Quttera恶意软件扫描↗
 URLquery浏览器分析↗
 Criminal IP资产情报↗
 CRDFThreat Center↗ Scamadviser信誉检查↗
 MyWOT社区声誉↗
按来源浏览该域名的完整历史记录。下载内容包含所选来源的每条记录。日期将保留其原始字段标签。
将所有记录下载为 JSON 格式| ID | 存储的数据 |
|---|
相同网站图标 辅助信号 4
类似标题 辅助信号 4
注册商:CSL Computer Service L… 仅限探索 6
每条辐条代表该域名与本报告相关联的一个原因。节点大小表示VirusTotal的检测结果,虚线节点表示已下线,完整列表如下。 相关报告完整列表
同一网站图标文件的哈希值相同,或者记录的页面标题以相同的20个字符开头。内容匹配并不能证明存在共用的网络钓鱼工具包或所有者。
与其他4个域名共享
通过同一家注册商注册。一家注册商通常为数百万互不相关的客户提供服务,因此这仅表明数据归属同一群体,而非证明存在关联。
PD-20261027-0FB5A8 收件人: abuse@joker.com AUP & Terms of Service Violations: Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices. Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension. Applicable Legal Framework (US): 18 U.S.C. § 1343 - Wire Fraud 18 U.S.C. § 1030 - Computer Fraud and Abuse Act (CFAA) 15 U.S.C. § 45 - FTC Act (Deceptive Practices) Federal laws prohibit wire fraud, computer fraud, and deceptive business practices. Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
根据您实际采取的行动采取相应措施。如果输入了密码:请立即更改密码,并检查是否在其他地方重复使用过该密码。如果支付过款项或提供过银行卡信息:请联系您的银行或支付服务商。如果下载了文件:请对设备进行病毒扫描。然后报告该事件。
该草稿仅供您个人保留。
首先确保资金安全:致电您的银行或撤销钱包授权。 当务之急 →
请根据您提供过的信息选择相应的步骤。请将本报告的副本与您自己的记录一并保存。
停止使用可疑网站。请通过官方应用或您已信任的网址访问真正的服务。
请将原始邮件、收据、消息和截图保存在安全的地方。基于事实的时间线有助于受理机构了解事件经过。 IC3 证据指南 ↗
mainnetvault-portal.com)即使你并不了解所有细节—— 不管怎样都要提交报告. 即使信息不完整,对调查仍有帮助。
举报并不能保证追回损失或启动调查,但及时、准确的交易数据可以帮助执法机构和服务提供商追踪事件。
使用存储的阻止列表、WHOIS、DNS 和公共扫描证据进行威胁分析
立即扫描将可疑域名提交至我们的威胁数据库——保护社区
报告最近的网络钓鱼报告和观察到的可用性变化
监控本报告汇总了已保存的页面快照、注册与网络记录、扫描器结果以及 PhishDestroy 举报历史。每个来源均保留各自的观测日期。打开来源报告即可查看原始结果。
AI 辅助分析的撰写时间: . 该内容描述了当时可获得的证据;后续的来源核查可能会导致情况发生变化。
快照记录的是当时显示的内容。扫描器结果记录的是该服务商在检查时的评估。有效证书或零检出结果都不能保证安全。