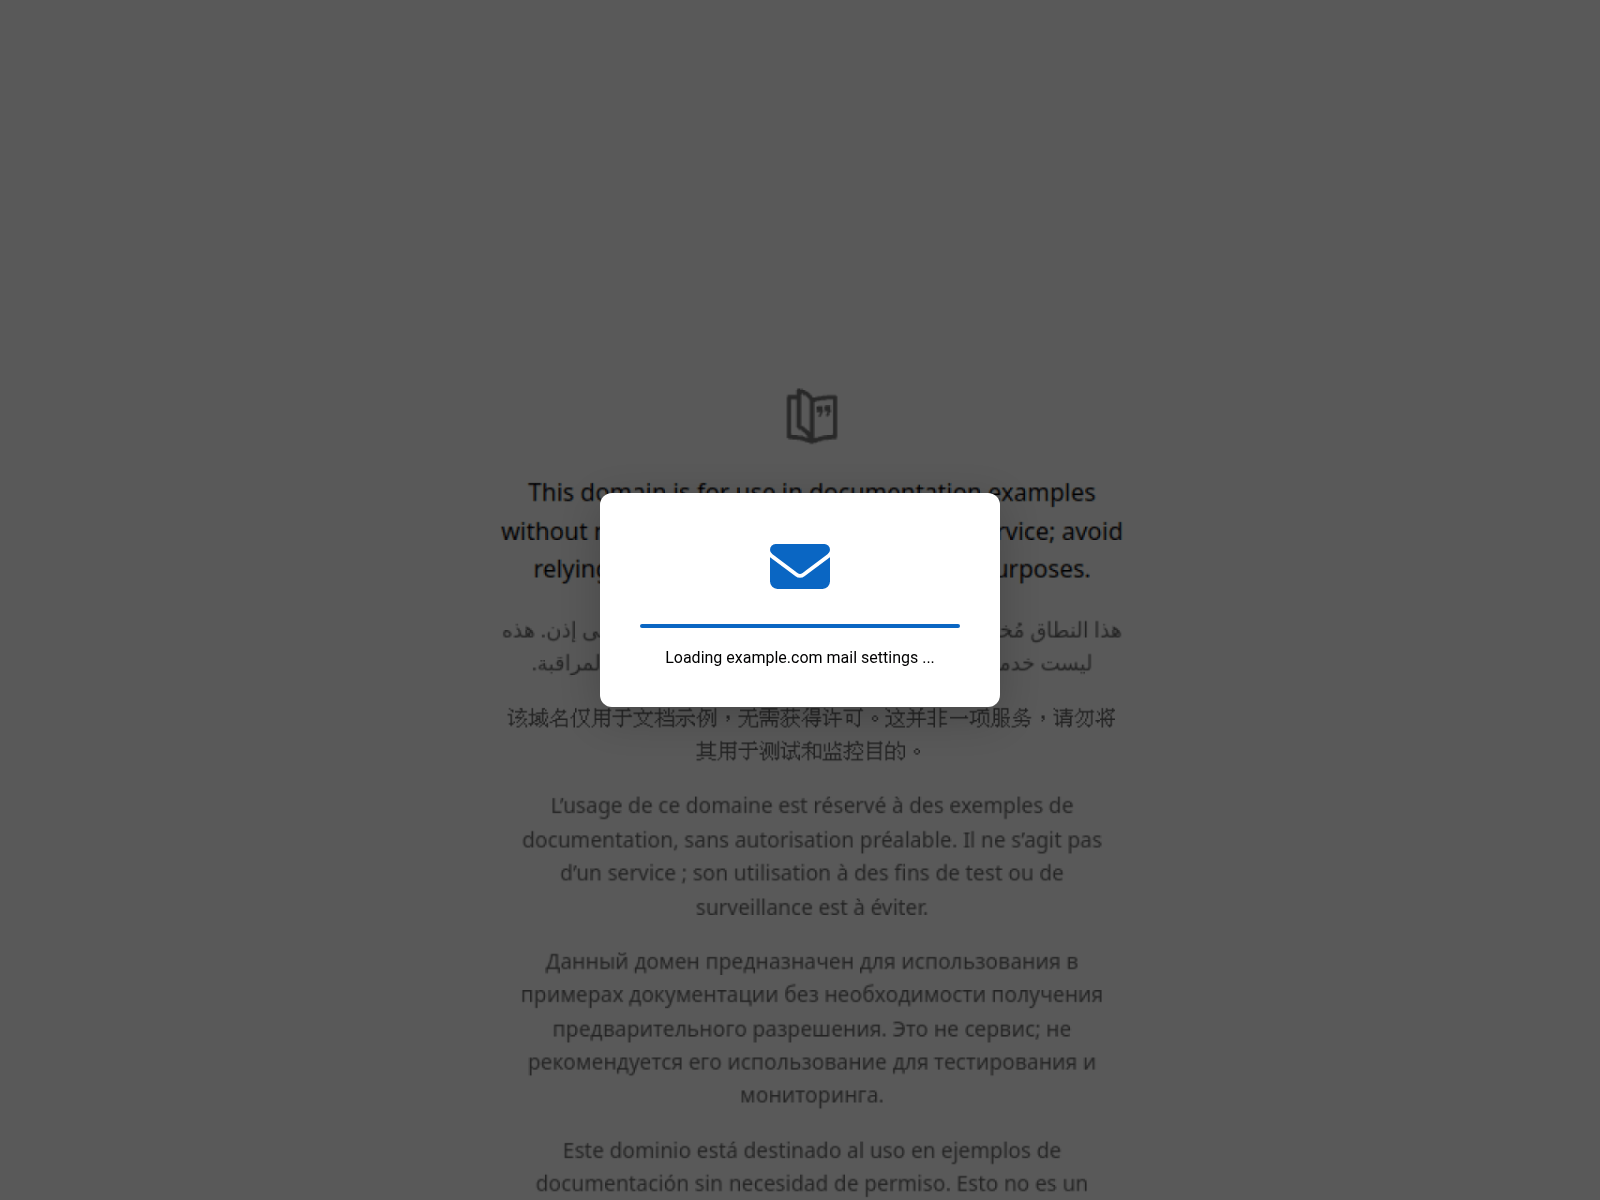
The domain kope-two.vercel.app hosted a fraudulent login interface designed to capture account credentials and passwords. Anyone who submitted a password on this page should immediately change their credentials on the actual service provider account.
URLScan截图 · 2026-11-18 01:06 UTC · SHA-256 651cb6c6…7afe2e5
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
Page layout and credential input
The page hosted on kope-two.vercel.app presents a modal dialog centered over a grey background displaying standard documentation placeholder text in multiple languages, including English, Arabic, Chinese, French, Russian, and Spanish. A prominent blue email envelope icon sits above a loading bar and the text "Loading example.com mail settings...". The interface is built to simulate a standard webmail login portal. It prompts visitors to input account credentials into a password field. Once the user interacts with the form, any entered data is transmitted directly to the backend controlled by the threat actor.
Credential harvesting risks
Because the page features a password field designed to capture authentication details, visitors who type their credentials risk immediate account compromise. Attackers typically use harvested passwords to access personal email accounts, reset linked services, or launch further attacks. The presentation relies on deceptive loading elements to trick users into believing they are authenticating a legitimate mail service session.
Security vendor telemetry
urlscan classified the page as malicious, 9 of 92 VirusTotal engines flagged it on 17 Nov 2026, and OpenPhish blocks it, and PhishDestroy's evidence score for it is 75/100 (critical). Independent scanners and security feeds confirm the malicious nature of the deployment on vercel.app. Furthermore, still responded on 18 Nov 2026 at 10:37 UTC, indicating active availability on the network.
kope-two.vercel.app — Credential harvesting mail login page
AI 描述
kope-two.vercel.app presents a fake email login capturing account passwords, flagged by urlscan and 9 VirusTotal engines. Do not type sensitive data.
AI摘要
Page layout and credential input The page hosted on kope-two.vercel.app presents a modal dialog centered over a grey background displaying standard documentation placeholder text in multiple languages, including English, Arabic, Chinese, French, Russian, and Spanish. A prominent blue email envelope icon sits above a loading bar and the text "Loading example.com mail settings...". The interface is built to simulate a standard webmail login portal. It prompts visitors to input account credentials into a password field. Once the user interacts with the form, any entered data is transmitted directly to the backend controlled by the threat actor. Credential harvesting risks Because the page features a password field designed to capture authentication details, visitors who type their credentials risk immediate account compromise. Attackers typically use harvested passwords to access personal email accounts, reset linked services, or launch further attacks. The presentation relies on deceptive loading elements to trick users into believing they are authenticating a legitimate mail service session. Security vendor telemetry urlscan classified the page as malicious, 9 of 92 VirusTotal engines flagged it on 17 Nov 2026, and OpenPhish blocks it, and PhishDestroy's evidence score for it is 75/100 (critical). Independent scanners and security feeds confirm the malicious nature of the deployment on vercel.app. Furthermore, still responded on 18 Nov 2026 at 10:37 UTC, indicating active availability on the network.
来源Vercelmechanism: Deployment Disabledsource: Current Http Probe
证据层Availability: Provider blockedContent: Provider blockedDNS: Stale
最新的 HTTP 观察结果观察到提供商阻塞Vercel Deployment DisabledVercelDeployment Disabled95%服务提供商标识已验证2026-11-21 02:00 UTC
RDAP注册
观测时间线last reachable: 2026-11-18 12:13 UTCcurrent episode first observed: 2026-11-19 00:08 UTCobserved RIP window: 2026-11-18 12:13 UTC → 2026-11-19 00:08 UTC · 11.92hmidpoint estimate ≈ 2026-11-18 18:10 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
技术 · 2 identified
V
Vercel
PaaS
Vercel is a cloud platform for static frontends and serverless functions.

 Vercel


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT