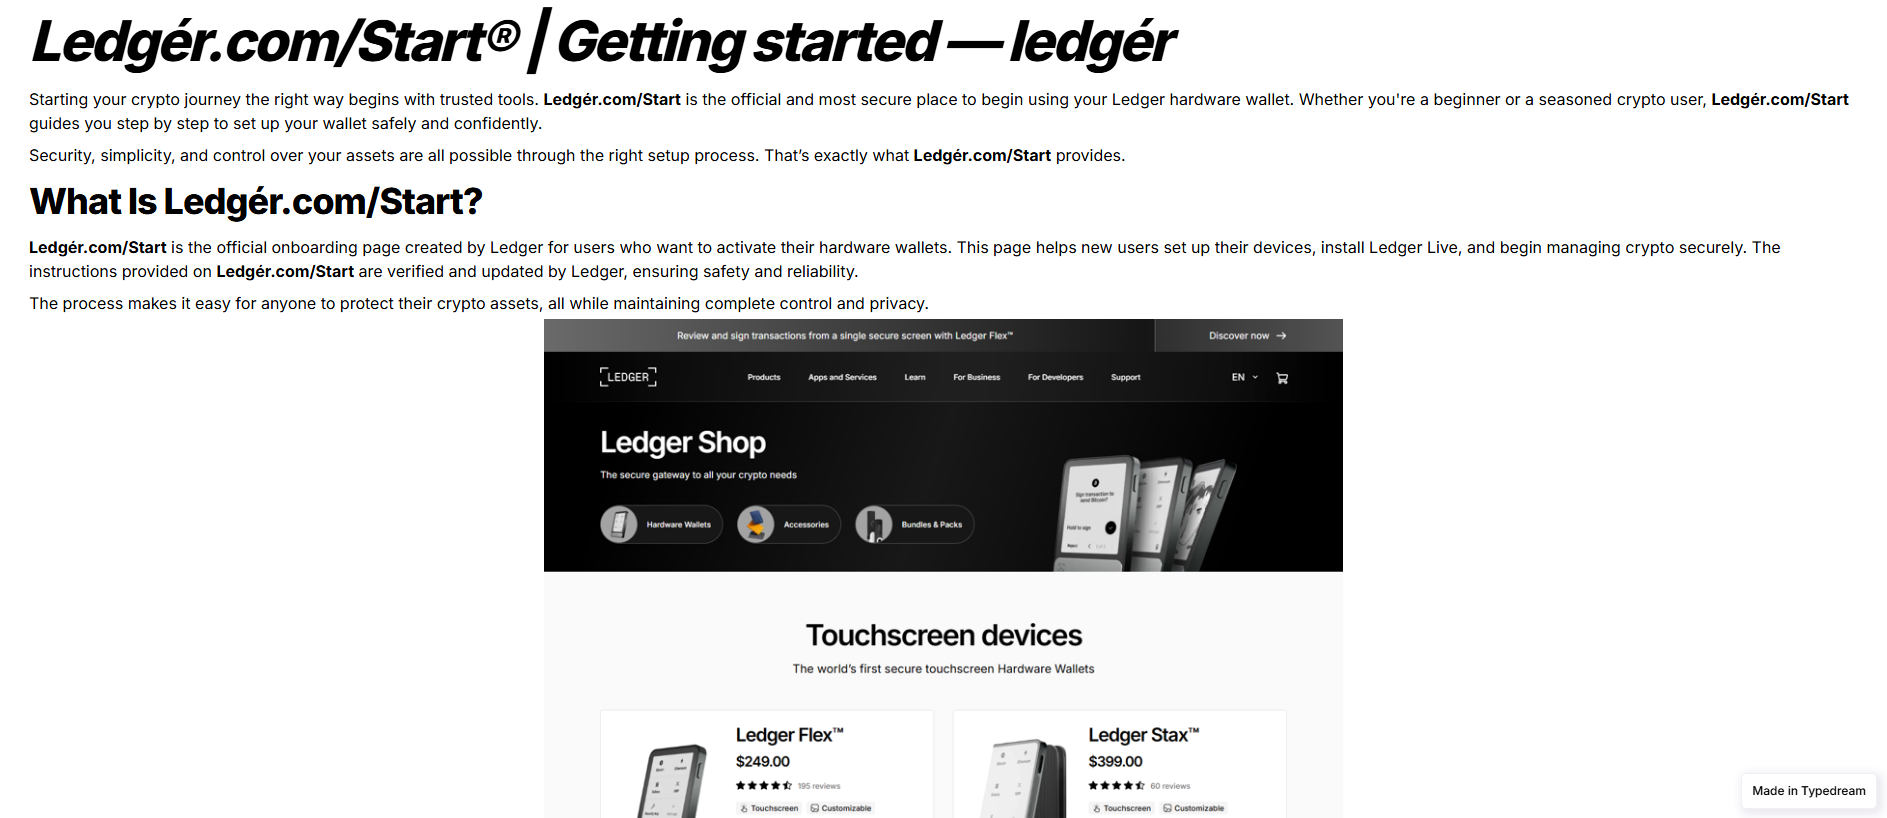
PhishDestroy listed insert-en-begin-ledger.typedream.app as suspicious based on automated scans that flagged it as malicious by several vendors. The recorded page title was "Official Site® | Ledgér.com/Start® | Getting started — ledgér". The site returned HTTP 200 on 2026-10-27, the date it was first observed by PhishDestroy.
诈骗手法解析
The detections indicate the site is considered malicious, but the captured page did not show concrete phishing forms, credential harvesters, or transaction prompts. As a result the listing reflects a general risk that the domain could be used for fraudulent purposes without confirming a specific scam technique.
证据
VirusTotal on 2026-10-27 reported three malicious detections from alphaMountain.ai, Ermes and SOCRadar. Google Safe Browsing checked the domain on the same date and did not flag it. urlscan.io captured the page on 2026-10-27 and assigned a malicious verdict with a score of 100, categorising it as phishing and linking it to the Ledger brand. OpenPhish listed the domain, and PhishDestroy’s internal blocklist marked it as malicious on 2026-10-27. OTX showed zero pulses on the check date.
基础设施
The recorded IP address was 188.114.97.1, associated with Cloudflare, Inc. in Canada, with additional observed IPs 188.114.96.3 and 188.114.97.3. The TLS certificate for typedream.app was issued by Google Trust Services, valid from 2026-09-23 to 2026-12-22. The domain age was recorded as 0 days, while the apex domain has been registered for 2081 days. No registrar information is available.
What to do
Visitors should avoid entering any personal or financial information on this site and monitor relevant accounts for unexpected activity. Organizations can block the exact subdomain and watch for traffic to the recorded Cloudflare IPs. Security teams should add the listed detections to their threat feeds and treat any interaction with the domain as potentially compromised.
PhishDestroy flagged insert-en-begin-ledger.typedream.app as suspicious on 2026-10-27 after multiple VirusTotal vendors and urlscan marked it malicious.
AI摘要
Overview PhishDestroy listed insert-en-begin-ledger.typedream.app as suspicious based on automated scans that flagged it as malicious by several vendors. The recorded page title was "Official Site® | Ledgér.com/Start® | Getting started — ledgér". The site returned HTTP 200 on 2026-10-27, the date it was first observed by PhishDestroy. How the scam works The detections indicate the site is considered malicious, but the captured page did not show concrete phishing forms, credential harvesters, or transaction prompts. As a result the listing reflects a general risk that the domain could be used for fraudulent purposes without confirming a specific scam technique. Evidence VirusTotal on 2026-10-27 reported three malicious detections from alphaMountain.ai, Ermes and SOCRadar. Google Safe Browsing checked the domain on the same date and did not flag it. urlscan.io captured the page on 2026-10-27 and assigned a malicious verdict with a score of 100, categorising it as phishing and linking it to the Ledger brand. OpenPhish listed the domain, and PhishDestroy’s internal blocklist marked it as malicious on 2026-10-27. OTX showed zero pulses on the check date. Infrastructure The recorded IP address was 188.114.97.1, associated with Cloudflare, Inc. in Canada, with additional observed IPs 188.114.96.3 and 188.114.97.3. The TLS certificate for typedream.app was issued by Google Trust Services, valid from 2026-09-23 to 2026-12-22. The domain age was recorded as 0 days, while the apex domain has been registered for 2081 days. No registrar information is available. What to do Visitors should avoid entering any personal or financial information on this site and monitor relevant accounts for unexpected activity. Organizations can block the exact subdomain and watch for traffic to the recorded Cloudflare IPs. Security teams should add the listed detections to their threat feeds and treat any interaction with the domain as potentially compromised. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a17d78-7484-7559-b45d-acf6f5e3879d/ Cloudflare Radar report: https://radar.cloudflare.com/scan/c2fad4de-acf4-48f1-85d8-8c5bf0c9e138 Stored capture screenshot: https://urlscan.io/screenshots/01a17d78-7484-7559-b45d-acf6f5e3879d.png Cloudflare Radar screenshot (2026-10-27T16:36:23Z): https://screenshots.phishdestroy.io/cf/c2fad4de-acf4-48f1-85d8-8c5bf0c9e138.png URLScan screenshot (2026-10-26T22:10:46Z): https://screenshots.phishdestroy.io/us/01a17a43-fd55-75b0-9c7c-b7720e33e4a5.png URLScan capture report: https://urlscan.io/result/01a17a43-fd55-75b0-9c7c-b7720e33e4a5/ URLScan screenshot (2026-10-27T16:37:47Z): https://screenshots.phishdestroy.io/us/01a17e39-7c25-75c4-b9c8-efa36b698450.png URLScan capture report: https://urlscan.io/result/01a17e39-7c25-75c4-b9c8-efa36b698450/ VirusTotal report: https://www.virustotal.com/gui/domain/insert-en-begin-ledger.typedream.app Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=insert-en-begin-ledger.typedream.app Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Ogurl: https://insert-en-begin-ledger.typedream.page/; Title: Official Site® | Ledgér.com/Start® | Getting started — ledgér; Ogtype: website; Ogtitle: Official Site® | Ledgér.com/Start® | Getting started — ledgér; Ogsitename: gfghfghs; Description: A website made with Typedream.; Twittercard: summary; Twittersite: @typedreamHQ; Ogdescription: A website made with Typedream.

 188.114.96.3


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT