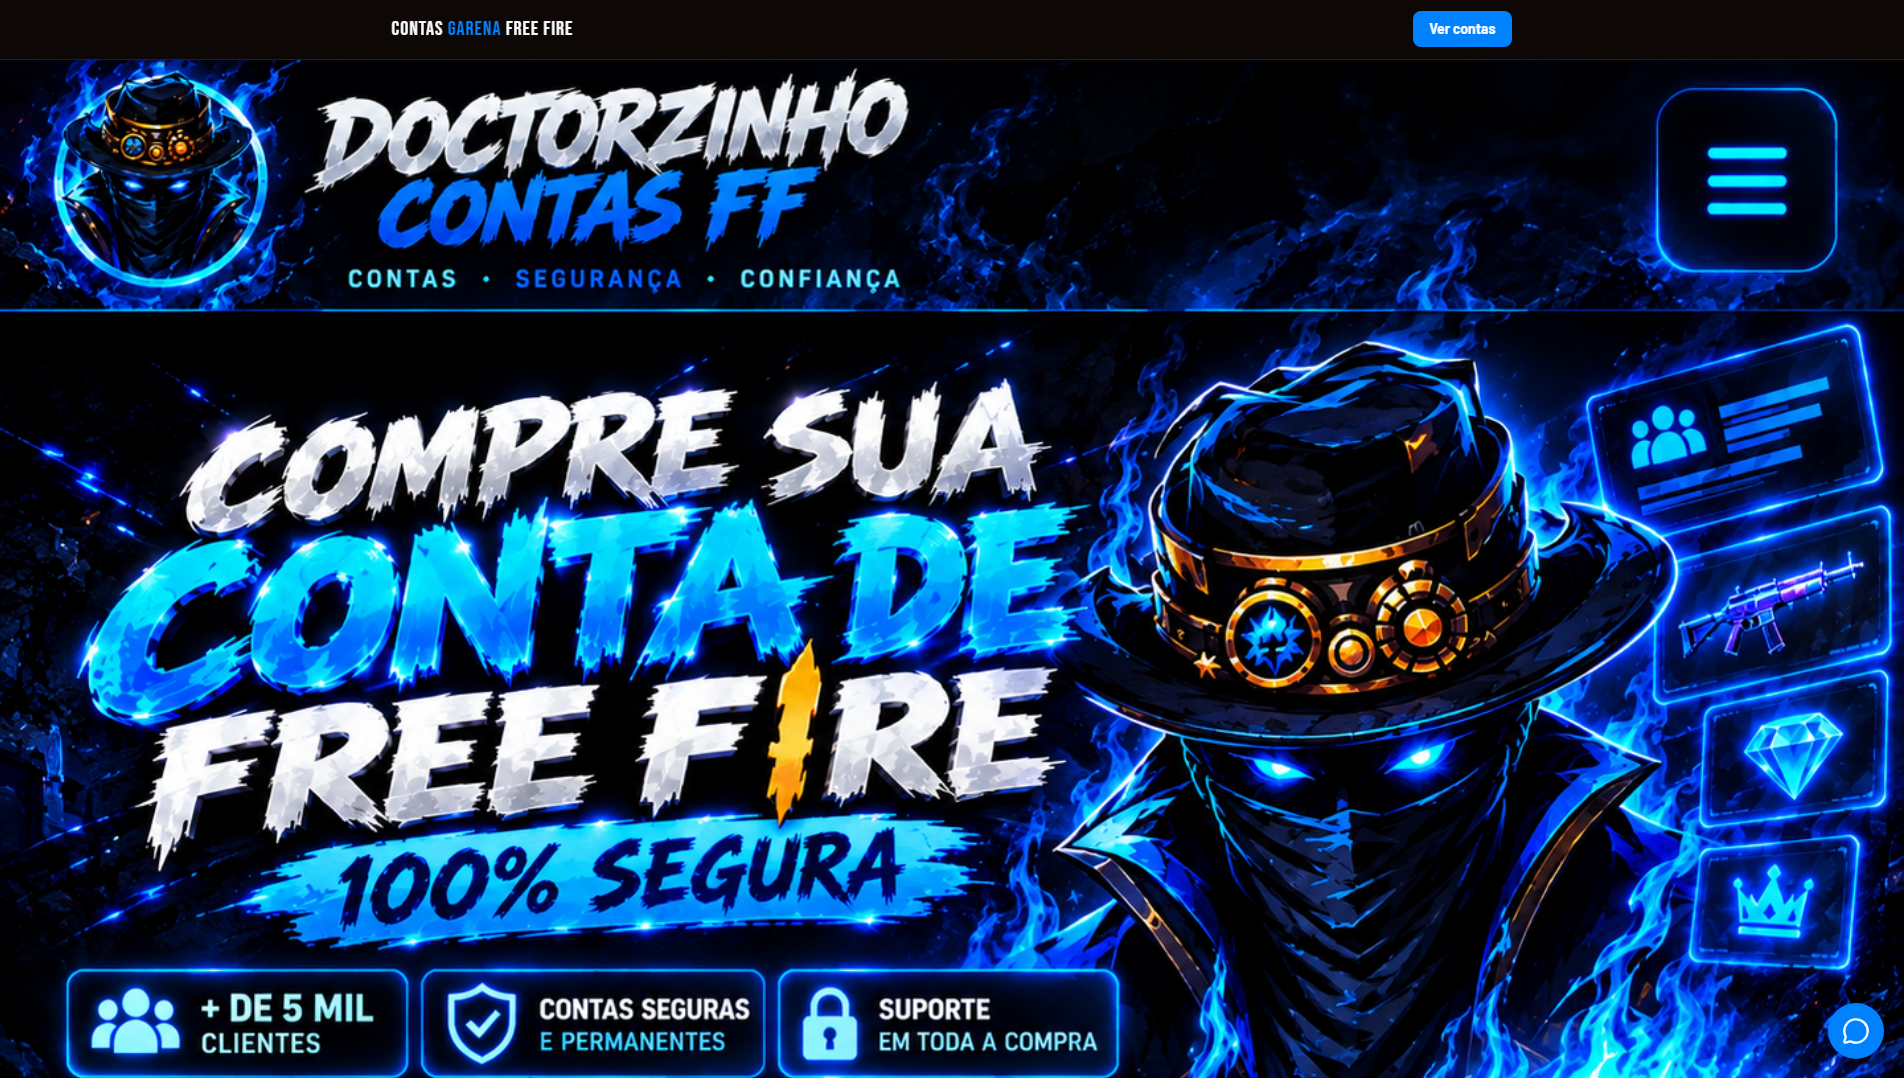
As observed on 2026-10-26, the captured screenshot shows a Portuguese-language account shop whose banner reads COMPRE SUA CONTA DE FREE FIRE 100% SEGURA, with badges claiming + de 5 mil clientes, contas seguras e permanentes and suporte em toda a compra. The page title read Contas Garena Free Fire — Loja de contas. PhishDestroy listed the domain after several antivirus vendors classified it as phishing and an external blocklist carried it, first seen on 2026-10-26.
诈骗手法解析
The captured page offered Garena Free Fire accounts for sale with promises of secure, permanent accounts, fast delivery and purchase support. Buyers were steered to an external WhatsApp contact link to finish the deal away from the site. As a category risk, payment is collected up front while the account details or personal data requested for the transfer can be harvested without any genuine account being delivered.
证据
The screenshot shows the sale banner, the trust badges and an external WhatsApp contact link as observed on 2026-10-26; page inspection recorded a TanStack and React style front end with Lovable events and Tinybird globals, Google Fonts and Google Static trackers, and 4 distinct script SHA256 hashes for campaign pivoting, the first beginning 084dbefa2895. On 2026-10-26 the urlscan engine verdict scored the page malicious at 97 while the overall urlscan verdict remained clean, and the redirect funnel was a single HTTP to HTTPS 307 hop. VirusTotal flagged the domain as malicious, with Kaspersky, Sophos, G-Data and Forcepoint labelling it phishing. Google Safe Browsing was not flagged and Spamhaus was not listed on 2026-10-26, while OpenPhish and the PhishDestroy internal blocklist held it and OTX recorded 3 pulses.
基础设施
Signals recorded name servers at a commercial DNS registrar with serving through the Cloudflare network and its WAF enabled; a shared CDN address reveals no operator identity. Notable weaknesses: CSP, X-Frame-Options, Permissions-Policy, COOP, COEP and CORP absent; HSTS present with a one-year max-age but no preload; X-Content-Type-Options and Referrer-Policy present. TLS 1.3, AES-256-GCM, forward secrecy, ALPN h2; no SPF, DKIM or DMARC; CAA present; DNSSEC unsigned.
What to do
If you submitted payment or personal data through freefirecentral.shop, change your password on the genuine Garena Free Fire service, enable two-factor authentication and treat any further contact as suspicious. Monitor the accounts used for the purchase and report the incident through official channels. Defenders should block freefirecentral.shop at the proxy, DNS or mail layer and hunt for that exact domain in logs.
freefirecentral.shop — Garena Free Fire account sale scam
AI 描述
PhishDestroy assesses freefirecentral.shop as a fake Garena Free Fire account shop designed to capture buyer payments and data.
AI摘要
Overview As observed on 2026-10-26, the captured screenshot shows a Portuguese-language account shop whose banner reads COMPRE SUA CONTA DE FREE FIRE 100% SEGURA, with badges claiming + de 5 mil clientes, contas seguras e permanentes and suporte em toda a compra. The page title read Contas Garena Free Fire — Loja de contas. PhishDestroy listed the domain after several antivirus vendors classified it as phishing and an external blocklist carried it, first seen on 2026-10-26. How the scam works The captured page offered Garena Free Fire accounts for sale with promises of secure, permanent accounts, fast delivery and purchase support. Buyers were steered to an external WhatsApp contact link to finish the deal away from the site. As a category risk, payment is collected up front while the account details or personal data requested for the transfer can be harvested without any genuine account being delivered. Evidence The screenshot shows the sale banner, the trust badges and an external WhatsApp contact link as observed on 2026-10-26; page inspection recorded a TanStack and React style front end with Lovable events and Tinybird globals, Google Fonts and Google Static trackers, and 4 distinct script SHA256 hashes for campaign pivoting, the first beginning 084dbefa2895. On 2026-10-26 the urlscan engine verdict scored the page malicious at 97 while the overall urlscan verdict remained clean, and the redirect funnel was a single HTTP to HTTPS 307 hop. VirusTotal flagged the domain as malicious, with Kaspersky, Sophos, G-Data and Forcepoint labelling it phishing. Google Safe Browsing was not flagged and Spamhaus was not listed on 2026-10-26, while OpenPhish and the PhishDestroy internal blocklist held it and OTX recorded 3 pulses. Infrastructure Signals recorded name servers at a commercial DNS registrar with serving through the Cloudflare network and its WAF enabled; a shared CDN address reveals no operator identity. Notable weaknesses: CSP, X-Frame-Options, Permissions-Policy, COOP, COEP and CORP absent; HSTS present with a one-year max-age but no preload; X-Content-Type-Options and Referrer-Policy present. TLS 1.3, AES-256-GCM, forward secrecy, ALPN h2; no SPF, DKIM or DMARC; CAA present; DNSSEC unsigned. What to do If you submitted payment or personal data through freefirecentral.shop, change your password on the genuine Garena Free Fire service, enable two-factor authentication and treat any further contact as suspicious. Monitor the accounts used for the purchase and report the incident through official channels. Defenders should block freefirecentral.shop at the proxy, DNS or mail layer and hunt for that exact domain in logs. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a17903-064c-77bc-b19e-e91f7d1108b0/ Cloudflare Radar report: https://radar.cloudflare.com/scan/f08bf2a8-4620-41d5-a1fc-0e8365c70f57 URLQuery report: https://urlquery.net/report/ee01e4f0-b0c3-40aa-9f68-a66a0575758a Stored capture screenshot: https://i.ibb.co/Qv1P3ZJq/891bef993ad6.png Cloudflare Radar screenshot (2026-10-26T16:19:34Z): https://screenshots.phishdestroy.io/cf/f08bf2a8-4620-41d5-a1fc-0e8365c70f57.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/ee01e4f0-b0c3-40aa-9f68-a66a0575758a.png URLScan screenshot (2026-10-11T22:17:32Z): https://screenshots.phishdestroy.io/us/01a12d0a-cbc6-777d-801a-0ff959257a7d.png URLScan capture report: https://urlscan.io/result/01a12d0a-cbc6-777d-801a-0ff959257a7d/ URLScan screenshot (2026-10-26T13:02:57Z): https://screenshots.phishdestroy.io/us/01a1784e-316f-719d-8cd0-eca944cceba4.png URLScan capture report: https://urlscan.io/result/01a1784e-316f-719d-8cd0-eca944cceba4/ VirusTotal report: https://www.virustotal.com/gui/domain/freefirecentral.shop Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=freefirecentral.shop Archived copy: https://web.archive.org/web/20261026161812/https://freefirecentral.shop/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Title: Contas Garena Free Fire — Loja de contas; Author: Lovable; Ogtype: website; Ogimage: https://pub-bb2e103a32db4e198524a2e9ed8f35b4.r2.dev/lovp_2th0jf8dze9nz972jq9f5hnc4f/3adde347ecc6631b568bd3da3eb93116_1791399367625.png; Ogtitle: Contas Garena Free Fire; Description: Compre sua conta de Free Fire com segurança, entrega rápida e suporte na troca de dados.; Twittercard: Summary large image; Twittersite: @Lovable; Ogdescription: Contas de Free Fire com entrega rápida e acompanhamento na troca de dados.
最新的 HTTP 观察结果RedirectingHTTP redirect observed80%2026-11-22 11:37 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:37 UTClast content: 2026-11-09 03:35 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 Name.com
 185.158.133.1


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT