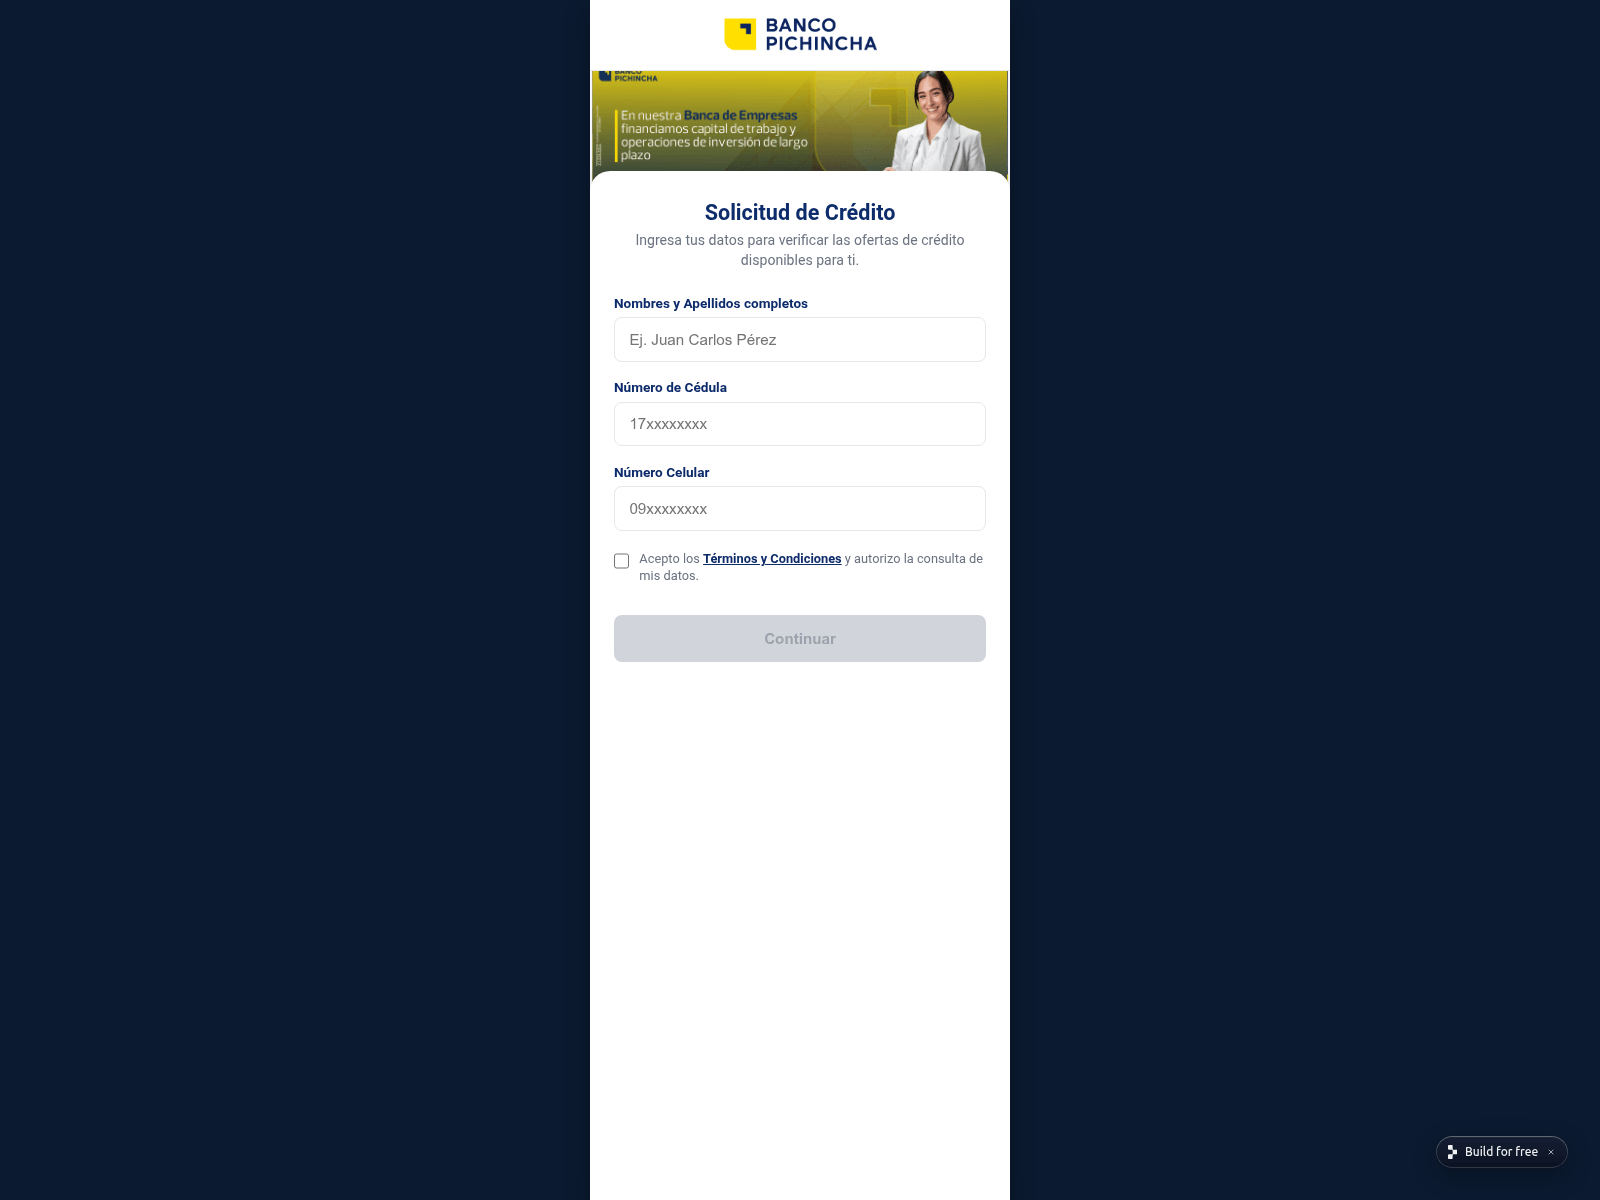
The page mimics Banco Pichincha in Spanish, presenting a "Solicitud de Crédito" form asking visitors to enter their full name, national ID number, and mobile phone number. If you entered your personal details into this form, contact your bank immediately to secure your accounts.
URLScan截图 · 2026-11-07 06:14 UTC · SHA-256 51da1764…ab7e0c3
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
Banco Pichincha credit application layout and text
The page displays the Banco Pichincha logo at the top alongside a promotional banner reading "En nuestra Banca de Empresas financiamos capital de trabajo y operaciones de inversión de largo plazo". Below this banner, the headline reads "Solicitud de Crédito", accompanied by the instruction "Ingresa tus datos para verificar las ofertas de crédito disponibles para ti." The form provides three input fields with placeholder examples: "Nombres y Apellidos completos" ("Ej. Juan Carlos Pérez"), "Número de Cédula" ("17xxxxxxxxx"), and "Número Celular" ("09xxxxxxxxx"). A checkbox requires agreement to "Términos y Condiciones" before clicking the grey "Continuar" button. The entire interface runs on the replit.app developer platform using an unverified subdomain address.
Security vendor telemetry and detections
22 of 92 engines on VirusTotal flagged it on 8 Nov 2026, Google Safe Browsing flags it, and Cloudflare Radar rated it malicious (Phishing, Security threats), its PhishDestroy evidence score is 85/100 (critical). Independent security scanners including Kaspersky, ESET and BitDefender classify the submission endpoint as malicious, confirming that automated protections recognize the threat rather than treating it as a false positive.
Risks of data collection on unverified subdomains
Pages requesting national ID numbers and phone numbers typically harvest identity details to facilitate targeted financial fraud or unauthorized account access. Because the form operates on unverified developer infrastructure rather than official banking domains, any information entered is sent directly to malicious operators. Victims who submit their details often encounter follow-up phishing attempts or fraudulent phone calls impersonating bank representatives.
Recommended actions for affected visitors
If you already submitted your personal details on this page, immediately monitor your bank accounts for unauthorized activity and notify financial authorities. Always navigate to Banco Pichincha through official channels rather than clicking links found in unverified messages.
来源证据VirusTotal 22 / 92 · Google Safe Browsing: 被标记5 个来源
ecuadorsalvanuevasvidas--nuevavidaecuado.replit.app hosted a fake Banco Pichincha credit application, flagged by 22 VirusTotal engines and Google Safe Browsing.
AI摘要
Banco Pichincha credit application layout and text The page displays the Banco Pichincha logo at the top alongside a promotional banner reading "En nuestra Banca de Empresas financiamos capital de trabajo y operaciones de inversión de largo plazo". Below this banner, the headline reads "Solicitud de Crédito", accompanied by the instruction "Ingresa tus datos para verificar las ofertas de crédito disponibles para ti." The form provides three input fields with placeholder examples: "Nombres y Apellidos completos" ("Ej. Juan Carlos Pérez"), "Número de Cédula" ("17xxxxxxxxx"), and "Número Celular" ("09xxxxxxxxx"). A checkbox requires agreement to "Términos y Condiciones" before clicking the grey "Continuar" button. The entire interface runs on the replit.app developer platform using an unverified subdomain address. Security vendor telemetry and detections 22 of 92 engines on VirusTotal flagged it on 8 Nov 2026, Google Safe Browsing flags it, and Cloudflare Radar rated it malicious (Phishing, Security threats), its PhishDestroy evidence score is 85/100 (critical). Independent security scanners including Kaspersky, ESET and BitDefender classify the submission endpoint as malicious, confirming that automated protections recognize the threat rather than treating it as a false positive. Risks of data collection on unverified subdomains Pages requesting national ID numbers and phone numbers typically harvest identity details to facilitate targeted financial fraud or unauthorized account access. Because the form operates on unverified developer infrastructure rather than official banking domains, any information entered is sent directly to malicious operators. Victims who submit their details often encounter follow-up phishing attempts or fraudulent phone calls impersonating bank representatives. Recommended actions for affected visitors If you already submitted your personal details on this page, immediately monitor your bank accounts for unauthorized activity and notify financial authorities. Always navigate to Banco Pichincha through official channels rather than clicking links found in unverified messages.
最新的 HTTP 观察结果RedirectingHTTP redirect observed80%2026-11-21 11:16 UTC
RDAP注册
观测时间线last reachable: 2026-11-21 11:16 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 34.117.33.233


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT