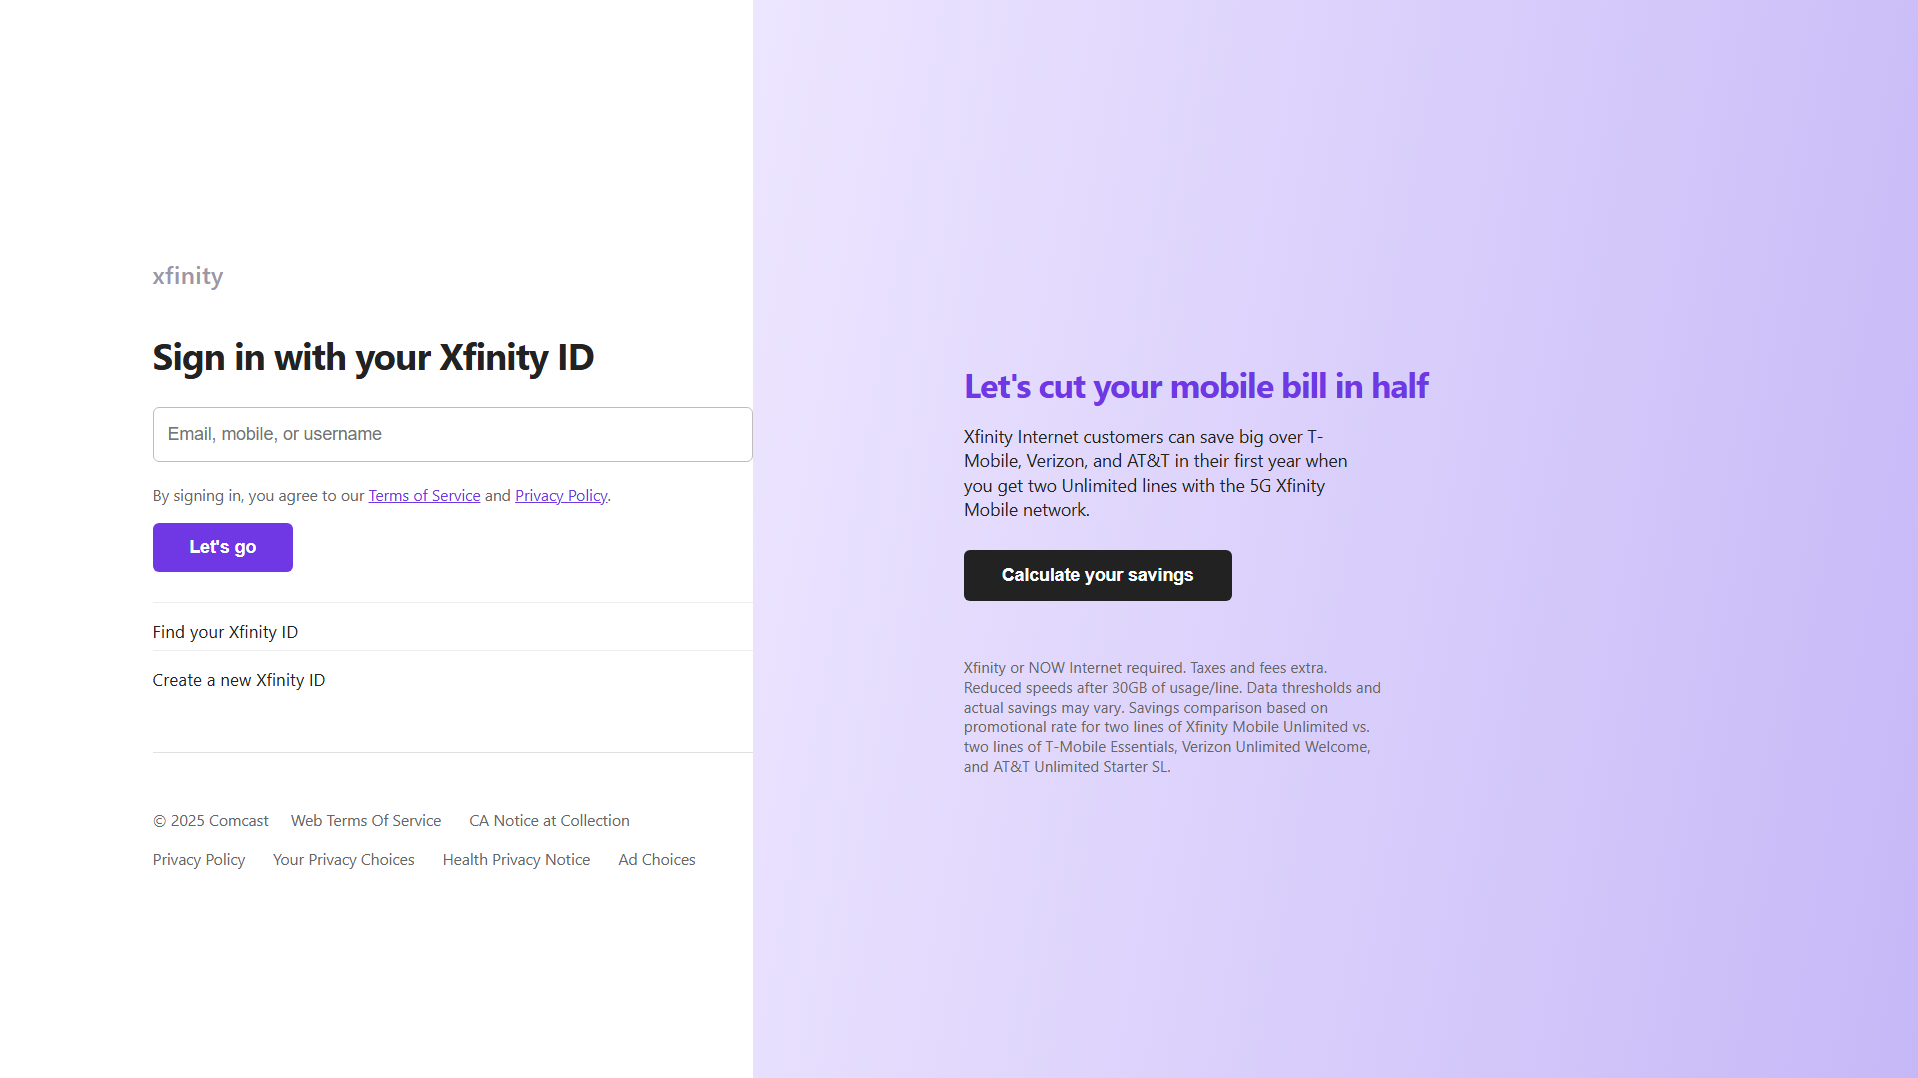
PhishDestroy’s automated assessment classifies comcast-seven.vercel.app as a credential‑phishing page that imitates an Xfinity login. The recorded page title “Xfinity Sign In” was captured on 2026-10-23, and the site returned HTTP 200 on the check performed on 2026-10-26. Intake recorded the domain because Google Safe Browsing flagged a social‑engineering redirect to www.xfinity.com. The domain was first seen by PhishDestroy on 2026-10-23.
诈骗手法解析
Credential‑phishing sites replicate legitimate login interfaces to trick users into submitting usernames and passwords, which attackers can later use to access the victims’ accounts or sell the credentials.
证据
VirusTotal reported 22 malicious detections out of 92 engines on 2026-10-23 (and 21 malicious plus 1 suspicious on 2026-10-10). Google Safe Browsing marked the domain as a SOCIAL_ENGINEERING threat on both 2026-10-10 and 2026-10-25. urlscan.io gave a malicious verdict for phishing targeting Xfinity on 2026-10-23, and external blocklists Phishunt and PhishFeed list the domain (checked 2026-10-26). PhishDestroy’s internal blocklist includes it; Spamhaus DBL did not list the domain (checked 2026-10-23) and OTX shows zero pulses (checked 2026-10-23).
基础设施
The domain is 30 days old as of the observations and resolves to Amazon‑owned IP addresses 64.29.17.131, 64.29.17.195 and 216.198.79.195 within ASN 16509. It is served through Vercel’s CDN and presents a TLS certificate for *.vercel.app issued by Google Trust Services, valid from 2026-08-29 to 2026-11-27. No registrar details are available.
What to do
Users should not enter any credentials on the site; if they have, they must change their Xfinity password immediately and enable multi‑factor authentication. Organizations should block the exact domain at the network perimeter, monitor for any traffic or credential submissions to it, and keep the domain under observation for future changes.
PhishDestroy classifies comcast-seven.vercel.app as a credential‑phishing site mimicking an Xfinity Sign‑In page, first seen 2026-10-23.
AI摘要
Overview PhishDestroy’s automated assessment classifies comcast-seven.vercel.app as a credential‑phishing page that imitates an Xfinity login. The recorded page title “Xfinity Sign In” was captured on 2026-10-23, and the site returned HTTP 200 on the check performed on 2026-10-26. Intake recorded the domain because Google Safe Browsing flagged a social‑engineering redirect to www.xfinity.com. The domain was first seen by PhishDestroy on 2026-10-23. How the scam works Credential‑phishing sites replicate legitimate login interfaces to trick users into submitting usernames and passwords, which attackers can later use to access the victims’ accounts or sell the credentials. Evidence VirusTotal reported 22 malicious detections out of 92 engines on 2026-10-23 (and 21 malicious plus 1 suspicious on 2026-10-10). Google Safe Browsing marked the domain as a SOCIAL_ENGINEERING threat on both 2026-10-10 and 2026-10-25. urlscan.io gave a malicious verdict for phishing targeting Xfinity on 2026-10-23, and external blocklists Phishunt and PhishFeed list the domain (checked 2026-10-26). PhishDestroy’s internal blocklist includes it; Spamhaus DBL did not list the domain (checked 2026-10-23) and OTX shows zero pulses (checked 2026-10-23). Infrastructure The domain is 30 days old as of the observations and resolves to Amazon‑owned IP addresses 64.29.17.131, 64.29.17.195 and 216.198.79.195 within ASN 16509. It is served through Vercel’s CDN and presents a TLS certificate for *.vercel.app issued by Google Trust Services, valid from 2026-08-29 to 2026-11-27. No registrar details are available. What to do Users should not enter any credentials on the site; if they have, they must change their Xfinity password immediately and enable multi‑factor authentication. Organizations should block the exact domain at the network perimeter, monitor for any traffic or credential submissions to it, and keep the domain under observation for future changes. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a1661f-27d6-7420-9fb1-f5f62d465c83/ URLQuery report: https://urlquery.net/report/1af2422b-10b1-4f4c-ab81-790418c354e9 Stored capture screenshot: https://i.ibb.co/jvV3406W/f28d2c8a870e.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/1af2422b-10b1-4f4c-ab81-790418c354e9.png URLScan screenshot (2026-09-24T13:01:51Z): https://screenshots.phishdestroy.io/us/01a0d381-c26d-70f8-b0c3-9f2045eece7b.png URLScan capture report: https://urlscan.io/result/01a0d381-c26d-70f8-b0c3-9f2045eece7b/ URLScan screenshot (2026-09-25T15:35:36Z): https://screenshots.phishdestroy.io/us/01a0d934-dc95-7422-8251-be793f98b7cd.png URLScan capture report: https://urlscan.io/result/01a0d934-dc95-7422-8251-be793f98b7cd/ URLScan screenshot (2026-09-26T14:02:56Z): https://screenshots.phishdestroy.io/us/01a0de06-987e-76dc-b0dd-67152256d8ec.png URLScan capture report: https://urlscan.io/result/01a0de06-987e-76dc-b0dd-67152256d8ec/ URLScan screenshot (2026-09-29T00:20:46Z): https://screenshots.phishdestroy.io/us/01a0ea88-f6f3-728a-8bbb-600b31734984.png URLScan capture report: https://urlscan.io/result/01a0ea88-f6f3-728a-8bbb-600b31734984/ URLScan screenshot (2026-10-10T10:47:53Z): https://screenshots.phishdestroy.io/us/01a1256c-720d-753f-a3de-e72e20b83481.png URLScan capture report: https://urlscan.io/result/01a1256c-720d-753f-a3de-e72e20b83481/ URLScan screenshot (2026-10-22T20:24:17Z): https://screenshots.phishdestroy.io/us/01a16549-18d1-77e3-a636-2c1ade4a943e.png URLScan capture report: https://urlscan.io/result/01a16549-18d1-77e3-a636-2c1ade4a943e/ VirusTotal report: https://www.virustotal.com/gui/domain/comcast-seven.vercel.app Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=comcast-seven.vercel.app Archived copy: https://web.archive.org/web/20261010135717/https://comcast-seven.vercel.app/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/

 216.198.79.195


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT