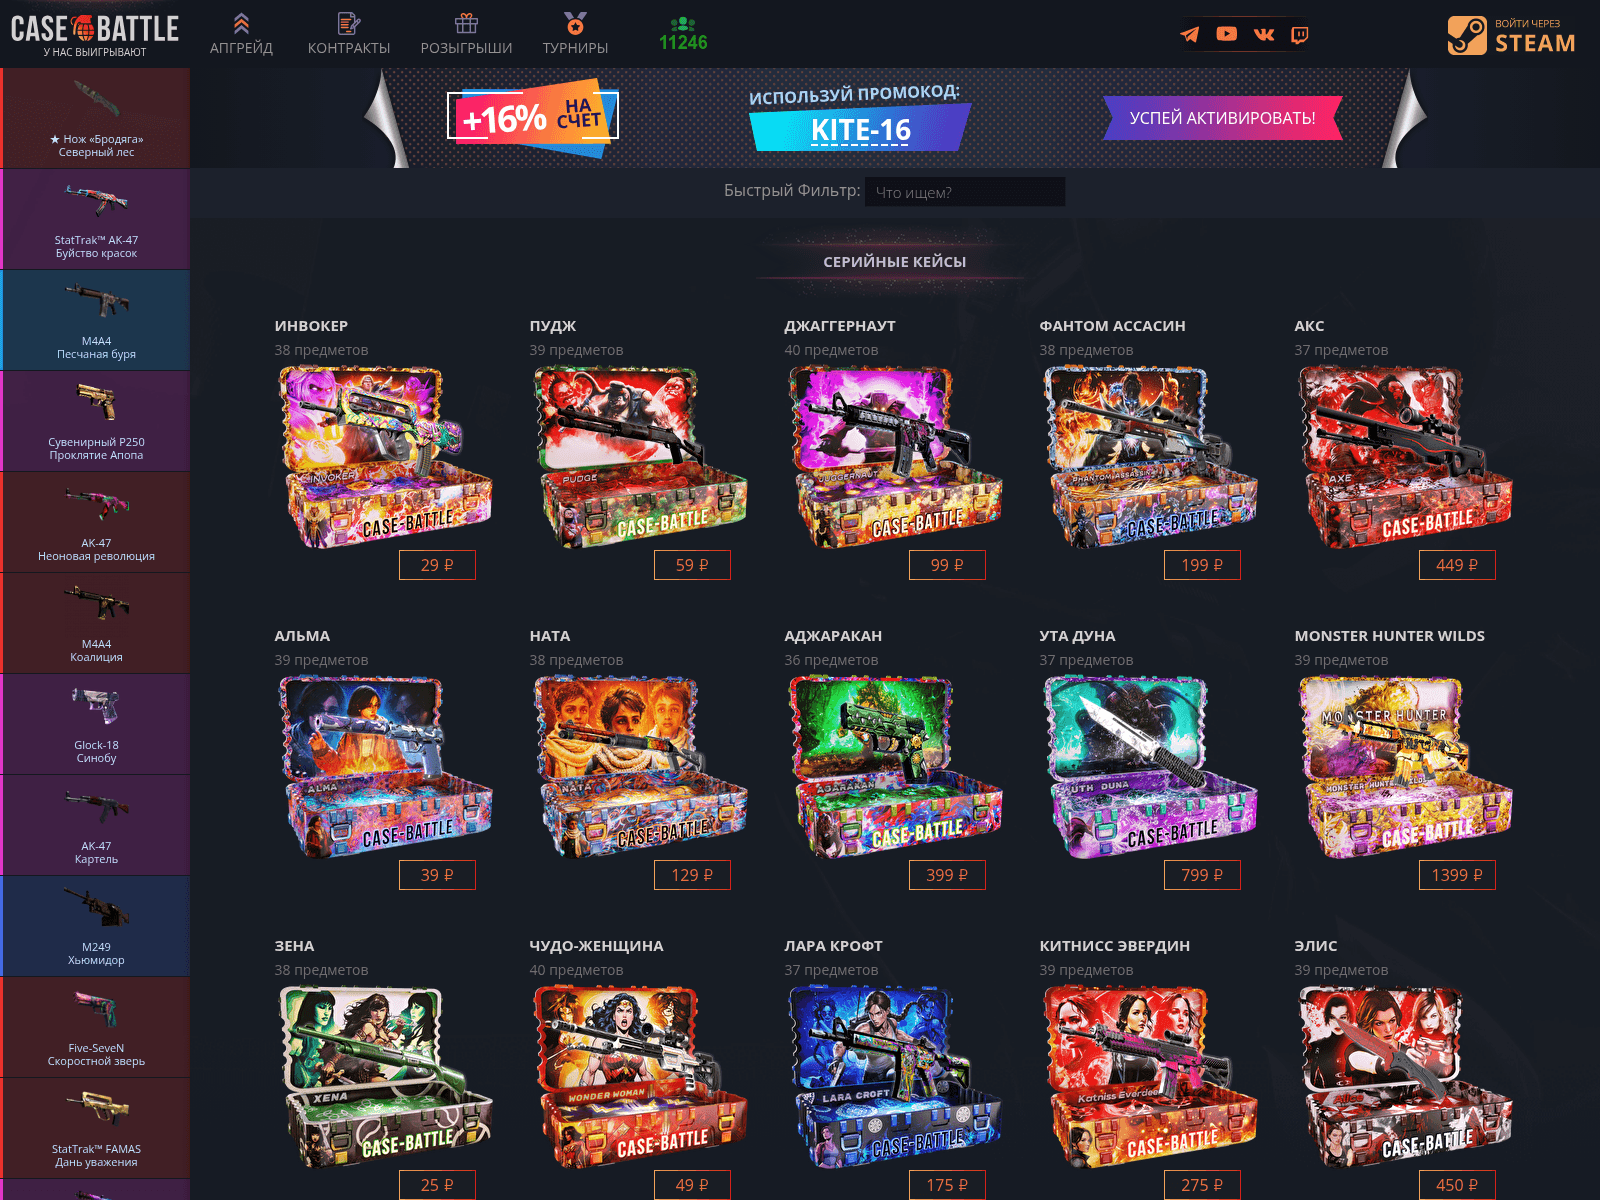
On 2026-11-14, casse-battle.com showed a dark interface headed "CASE BATTLE" with the tagline "У НАС ВЫИГРЫВАЮТ" and a Steam-branded sign-in button labeled "ВОЙТИ ЧЕРЕЗ STEAM." A banner advertises a promo code "KITE-16" with a "+16% НА СЧЁТ" offer and an "УСПЕЙ АКТИВИРОВАТЬ!" call to action, alongside a quick-filter search field. The main area lists serial cases such as "ИНВОКЕР," "ПУДЖ," and "ДЖАГГЕРНАУТ," each with an item count and a ruble price.
分析报告仅提供英文版本
页面标题: “CASE-BATTLE :: Официальный Сайт — Кейсы, Апгрейды CS2 (CS:GO), Новые Возможности!”
URLScan截图 · 2026-11-14 07:16 UTC · SHA-256 61920081…d86c4b4
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
On 2026-11-14, casse-battle.com showed a dark interface headed "CASE BATTLE" with the tagline "У НАС ВЫИГРЫВАЮТ" and a Steam-branded sign-in button labeled "ВОЙТИ ЧЕРЕЗ STEAM." A banner advertises a promo code "KITE-16" with a "+16% НА СЧЁТ" offer and an "УСПЕЙ АКТИВИРОВАТЬ!" call to action, alongside a quick-filter search field. The main area lists serial cases such as "ИНВОКЕР," "ПУДЖ," and "ДЖАГГЕРНАУТ," each with an item count and a ruble price.
The stored VirusTotal domain result reports 4 detections out of 92 engines. Emsisoft reported "phishing"; Fortinet reported "phishing".
casse-battle.com: CASE BATTLE page listing priced item cases
AI 描述
PhishDestroy records casse-battle.com as a CASE BATTLE page listing named item cases with ruble prices, a promo code banner, and a Steam-branded sign-in option.
AI摘要
On 2026-11-14, casse-battle.com showed a dark interface headed "CASE BATTLE" with the tagline "У НАС ВЫИГРЫВАЮТ" and a Steam-branded sign-in button labeled "ВОЙТИ ЧЕРЕЗ STEAM." A banner advertises a promo code "KITE-16" with a "+16% НА СЧЁТ" offer and an "УСПЕЙ АКТИВИРОВАТЬ!" call to action, alongside a quick-filter search field. The main area lists serial cases such as "ИНВОКЕР," "ПУДЖ," and "ДЖАГГЕРНАУТ," each with an item count and a ruble price. The stored VirusTotal domain result reports 4 detections out of 92 engines. Emsisoft reported "phishing"; Fortinet reported "phishing".
New Domains 网络钓鱼 Security threats 网络钓鱼 Security Risks
注册商背景NiceNIC
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
证据层Availability: DNS inactiveContent: UnreachableDNS: NXDOMAINRegistration: Active
RDAP注册有效NICENIC INTERNATIONAL GROUP CO., LIMITED · IANA 3765RDAP HTTP 200source: Rdap Status CollectorclientDeleteProhibitedclientTransferProhibitedexpires 2027-11-05 19:17 UTC已检查 2026-11-15 06:10 UTC
观测时间线last reachable: 2026-11-16 03:44 UTClast content: 2026-11-16 03:44 UTCcurrent episode first observed: 2026-11-17 05:12 UTCobserved RIP window: 2026-11-16 03:44 UTC → 2026-11-17 05:12 UTC · 25.48hmidpoint estimate ≈ 2026-11-16 16:28 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 NiceNIC
 188.114.97.3


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT