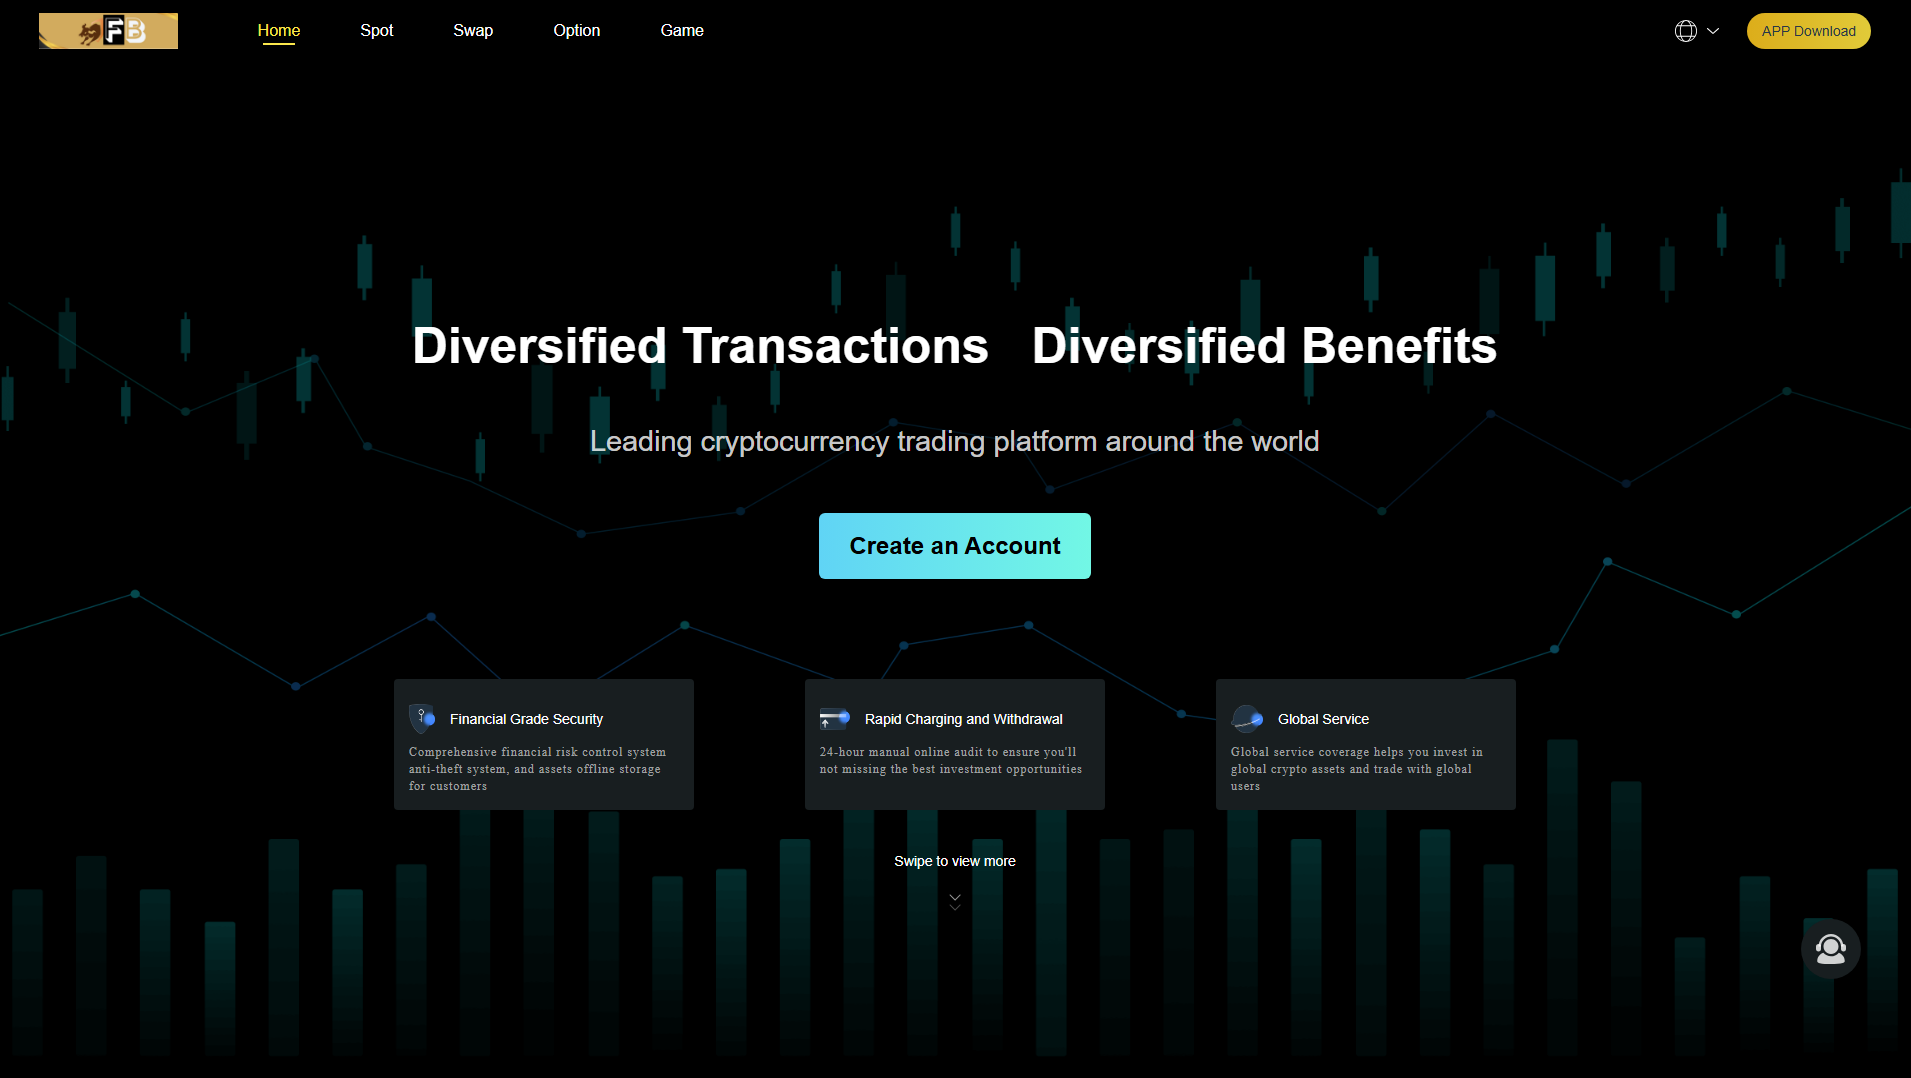
bruttlyntrade.com is an impersonation phishing page. Its domain name suggests a trading platform, but the page itself is titled "FB", a label commonly associated with Facebook. PhishDestroy first detected it on 2026-08-31, and it was still online and serving content on 2026-10-19. Anyone who reaches it through an ad, a direct message or a "trading opportunity" link is the intended target.
诈骗手法解析
Impersonation pages copy the look of a trusted brand so that visitors hand over what they would normally give only to the real service, usually a login, a phone number or a verification code. With a page titled "FB", the likely goal is a Facebook-style sign-in or verification prompt, and anything entered is sent straight to the operators. A hijacked social media account can then be used to spread the same lure to the victim's contacts or to push fake investment offers, which fits the trading theme of the domain name.
证据
Five of 92 VirusTotal engines flagged the domain as of 2026-10-14: alphaMountain.ai, Forcepoint ThreatSeeker, Gridinsoft, SOCRadar and desenmascara.me. That count is low, so many browsers and filters will still let the page load without a warning. It appears in five AlienVault OTX threat pulses, which means other researchers have independently tied it to malicious activity. Among blocklists, PhishDestroy currently lists it.
基础设施
The domain was registered on 2026-07-03 through Realtime Register B.V., 59 days before PhishDestroy detected it. This kind of short gap is typical of domains set up for a specific campaign. The site is hosted on Skycloud Computing co., Ltd. in Taiwan. It has a standard domain-validated certificate from Sectigo, so the browser padlock only confirms an encrypted connection and says nothing about whether the site is legitimate.
What to do
If you typed a Facebook or other password on this page, change it right away from the official app, enable two-factor authentication, and log out of all other sessions. If you shared a verification code, check your recent login activity and recovery email and phone settings for changes you did not make. Warn your contacts not to trust investment or trading messages sent from your account. If the site also pushed you toward deposits, send no more money and treat any "fee" required to withdraw as part of the scam. Defenders should block the domain at DNS and the proxy, and search logs for any users who visited it.
bruttlyntrade.com is an impersonation phishing page titled "FB" that targets visitors' login credentials and personal details. Still live and dangerous.
AI摘要
Overview bruttlyntrade.com is an impersonation phishing page. Its domain name suggests a trading platform, but the page itself is titled "FB", a label commonly associated with Facebook. PhishDestroy first detected it on 2026-08-31, and it was still online and serving content on 2026-10-19. Anyone who reaches it through an ad, a direct message or a "trading opportunity" link is the intended target. How the scam works Impersonation pages copy the look of a trusted brand so that visitors hand over what they would normally give only to the real service, usually a login, a phone number or a verification code. With a page titled "FB", the likely goal is a Facebook-style sign-in or verification prompt, and anything entered is sent straight to the operators. A hijacked social media account can then be used to spread the same lure to the victim's contacts or to push fake investment offers, which fits the trading theme of the domain name. Evidence Five of 92 VirusTotal engines flagged the domain as of 2026-10-14: alphaMountain.ai, Forcepoint ThreatSeeker, Gridinsoft, SOCRadar and desenmascara.me. That count is low, so many browsers and filters will still let the page load without a warning. It appears in five AlienVault OTX threat pulses, which means other researchers have independently tied it to malicious activity. Among blocklists, PhishDestroy currently lists it. Infrastructure The domain was registered on 2026-07-03 through Realtime Register B.V., 59 days before PhishDestroy detected it. This kind of short gap is typical of domains set up for a specific campaign. The site is hosted on Skycloud Computing co., Ltd. in Taiwan. It has a standard domain-validated certificate from Sectigo, so the browser padlock only confirms an encrypted connection and says nothing about whether the site is legitimate. What to do If you typed a Facebook or other password on this page, change it right away from the official app, enable two-factor authentication, and log out of all other sessions. If you shared a verification code, check your recent login activity and recovery email and phone settings for changes you did not make. Warn your contacts not to trust investment or trading messages sent from your account. If the site also pushed you toward deposits, send no more money and treat any "fee" required to withdraw as part of the scam. Defenders should block the domain at DNS and the proxy, and search logs for any users who visited it. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a056b8-c092-736a-8500-4ced9cf72035/ VirusTotal report: https://www.virustotal.com/gui/domain/bruttlyntrade.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=bruttlyntrade.com Archived copy: https://web.archive.org/web/20260831073202/https://bruttlyntrade.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
The Tranco rank (how much traffic) is rather low The server of the site has several low reviewed other websites SSL certificate was not identified The age of this site is (very) young. The site does not allow us to analyze its content
证据层Availability: Content servingContent: Content served at rootDNS: Resolved
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-21 23:43 UTC
RDAP注册
观测时间线last reachable: 2026-11-21 23:43 UTClast content: 2026-11-21 23:43 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 223.26.14.18


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT