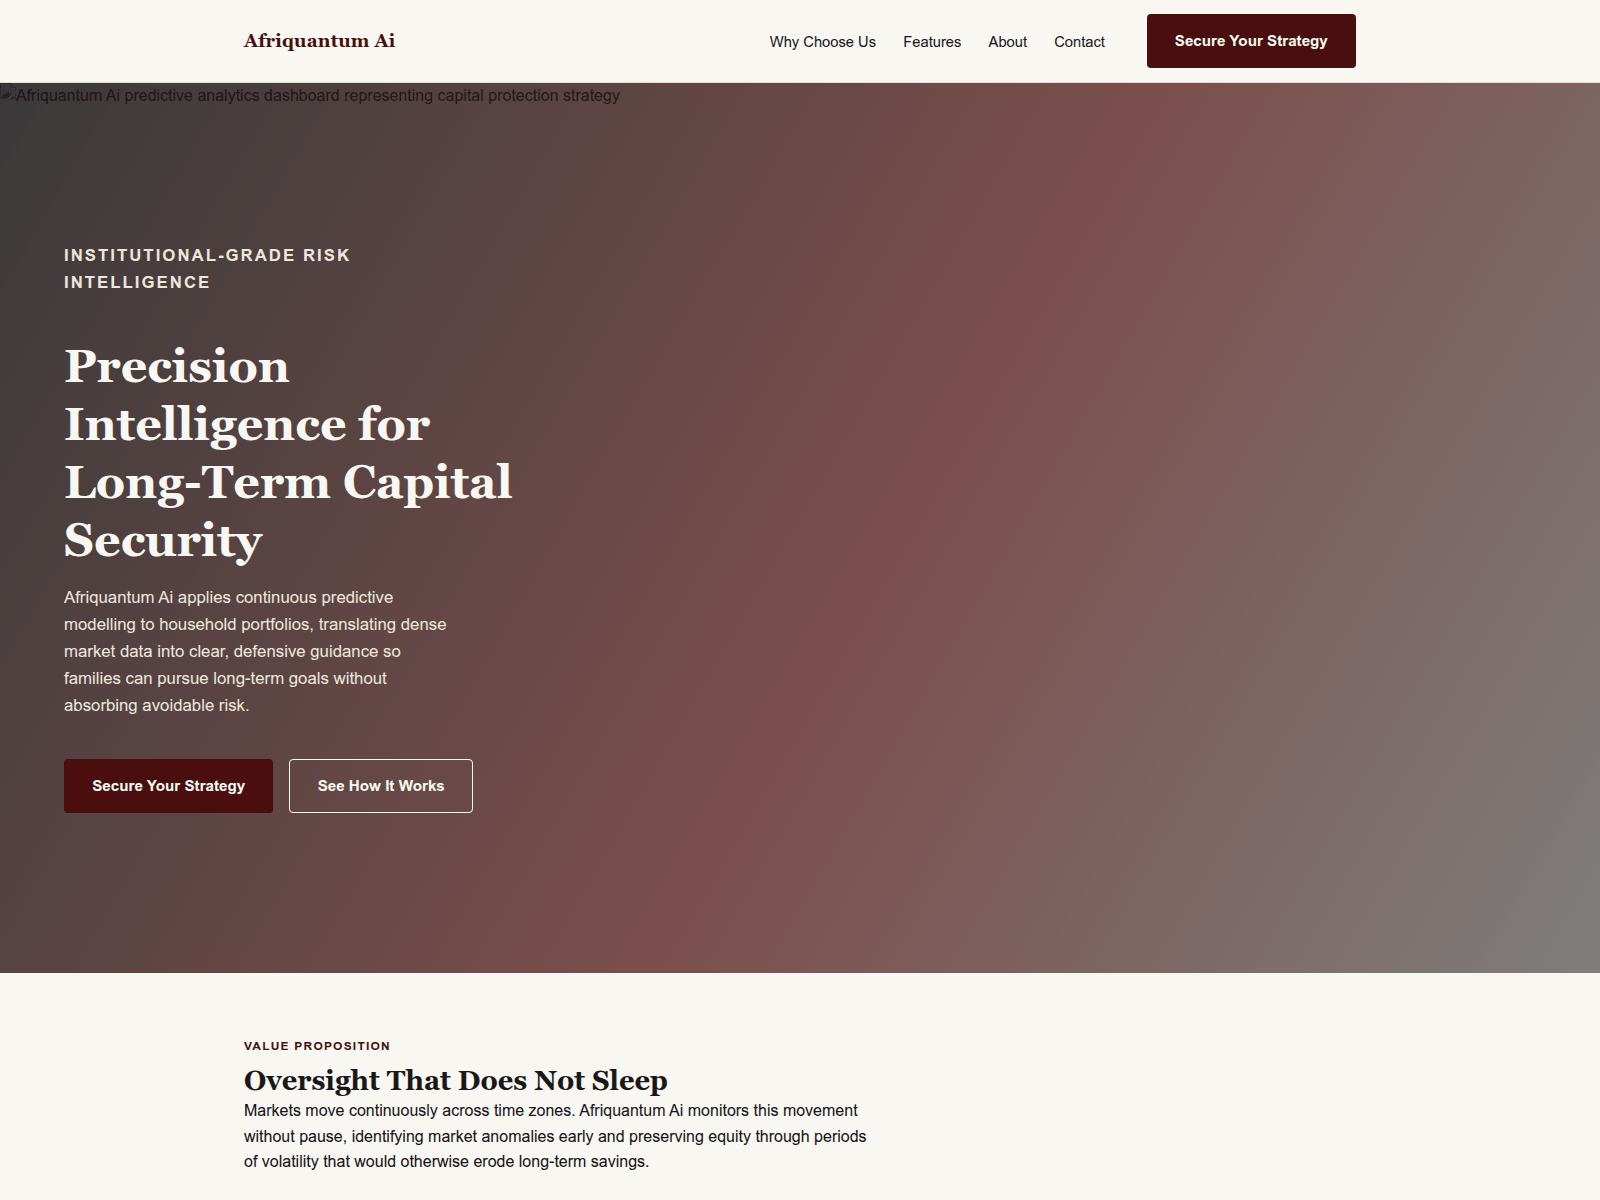
The captured afriquantumai.net landing page is branded "Afriquantum Ai" and presents itself as institutional-grade risk intelligence for long-term capital security. Its hero section promises continuous predictive modelling applied to household portfolios, with the main interaction being a prominent "Secure Your Strategy" button offered alongside a secondary "See How It Works" link. A value-proposition section below reinforces the pitch with the heading "Oversight That Does Not Sleep," describing continuous market monitoring across time zones.
分析报告仅提供英文版本
页面标题: “Afriquantum Ai — AI Platform for Long-Term Capital Security”
The captured afriquantumai.net landing page is branded "Afriquantum Ai" and presents itself as institutional-grade risk intelligence for long-term capital security. Its hero section promises continuous predictive modelling applied to household portfolios, with the main interaction being a prominent "Secure Your Strategy" button offered alongside a secondary "See How It Works" link. A value-proposition section below reinforces the pitch with the heading "Oversight That Does Not Sleep," describing continuous market monitoring across time zones.
The stored VirusTotal domain result reports 3 detections out of 92 engines. Sophos reported "phishing"; Netcraft reported "malicious".
afriquantumai.net - Afriquantum Ai capital security landing page
AI 描述
PhishDestroy records afriquantumai.net, a landing page branded Afriquantum Ai offering predictive risk intelligence for long-term capital security.
AI摘要
The captured afriquantumai.net landing page is branded "Afriquantum Ai" and presents itself as institutional-grade risk intelligence for long-term capital security. Its hero section promises continuous predictive modelling applied to household portfolios, with the main interaction being a prominent "Secure Your Strategy" button offered alongside a secondary "See How It Works" link. A value-proposition section below reinforces the pitch with the heading "Oversight That Does Not Sleep," describing continuous market monitoring across time zones. The stored VirusTotal domain result reports 3 detections out of 92 engines. Sophos reported "phishing"; Netcraft reported "malicious".


 Dynadot
 158.94.210.119


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT