VirusTotal
9 / 92 engine detections
Mở báo cáo

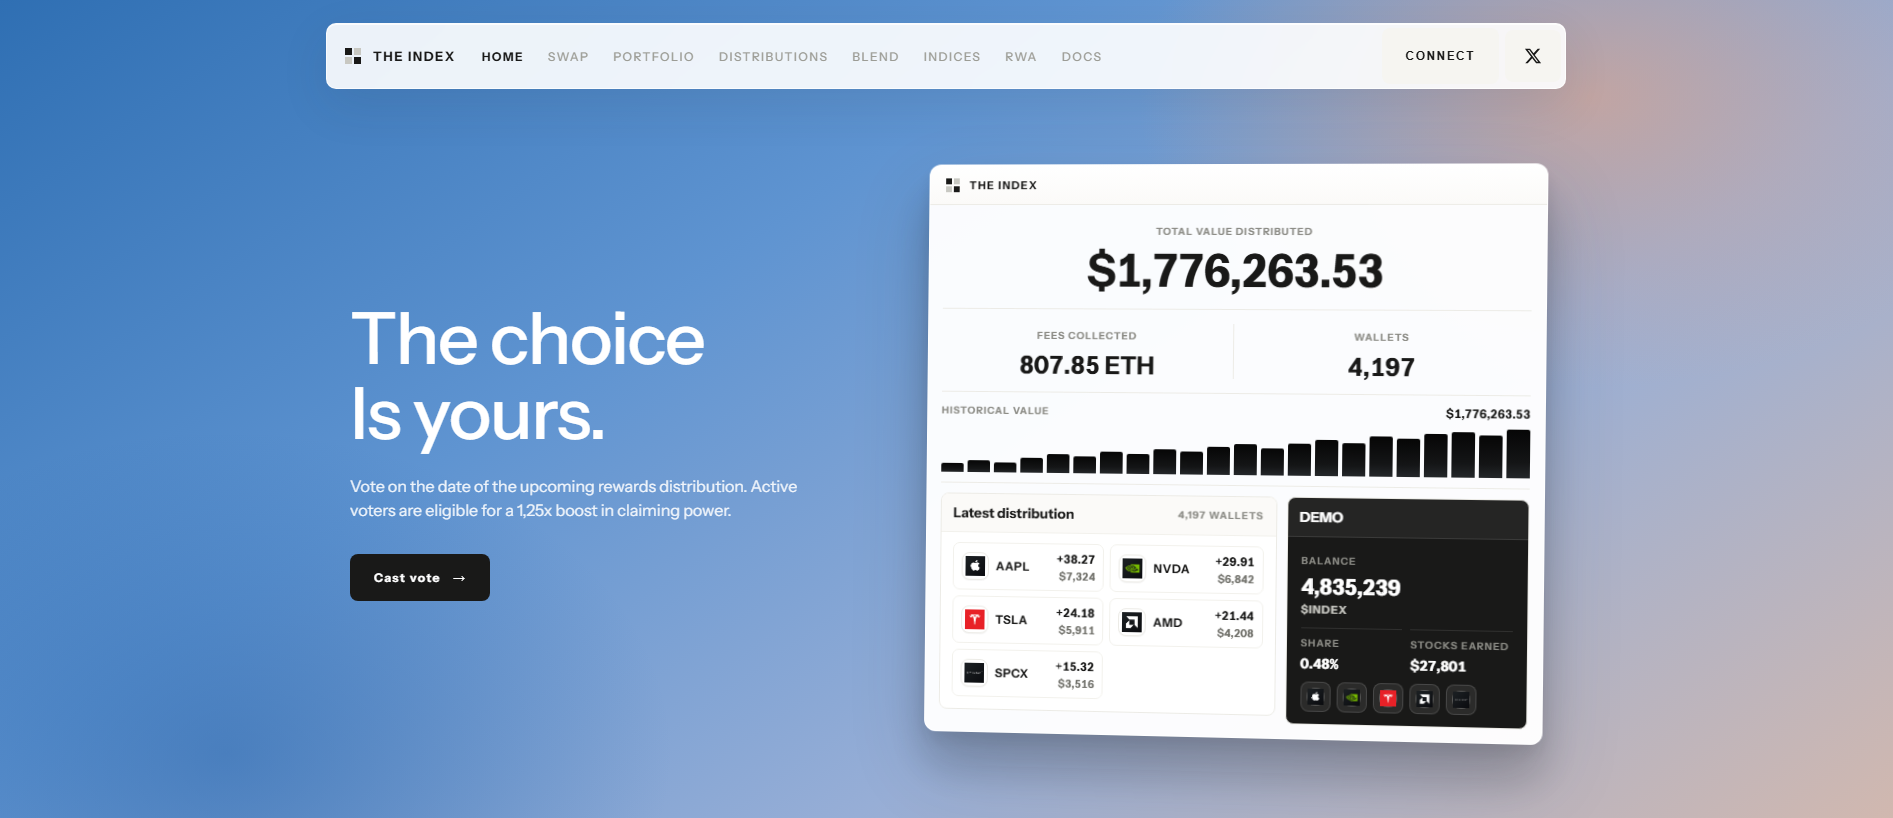
“The Index — hold it, get paid in stocks”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@spaceship.com.
The latest stored availability evidence still shows the domain reachable; 13 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Giả mạo Lido: theindexfinance.forum — Hoạt động được biết đến lần cuối (HTTP 200). Tóm tắt bằng chứng: VirusTotal 9/92 (alphaMountain.ai, BitDefender, CRDF…
Phân tích chi tiết của PhishDestroy AI bên dưới được giữ bằng tiếng Anh để bảo toàn hồ sơ pháp chứng gốc.
9 / 92 engine detections
Mở báo cáo3 det.
Mở báo cáoSuspicious
Mở báo cáo4 community references
Mở báo cáoNo threat flag
Mở báo cáoNo malicious flag
Mở báo cáoResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
theindexfinance.forum is an impersonation phishing page that presents itself as The Index under the tagline "hold it, get paid in stocks." It targets crypto holders who are drawn to passive-income offers tied to traditional markets. PhishDestroy first flagged it on 2026-10-07, the same day the domain was registered. As of 2026-10-19 the site was still online and serving its content.
The pitch is simple: hold an asset associated with The Index and receive stock payouts in return. Impersonation pages like this borrow a project's name and promise to win trust, then steer visitors toward the step that matters to the operator, usually connecting a wallet, signing a transaction, or handing over credentials to "claim" or "activate" rewards. Whatever is signed or entered goes to the attacker, not to the real project, and the promised stock dividends never arrive. The forum-style domain name adds a veneer of community legitimacy to an otherwise fake offer.
Four days after registration, 9 of 92 VirusTotal engines classified the domain as malicious, including Kaspersky, BitDefender, Fortinet, Forcepoint ThreatSeeker, G-Data, Gridinsoft, CRDF and alphaMountain.ai. That is a modest count, but it comes from well-established vendors. Wallet-focused defenses agree. MetaMask, ScamSniffer and SEAL all block the domain alongside PhishDestroy, which means many wallet users are already warned before the page loads. The domain also appears in four AlienVault OTX threat pulses, showing other researchers are tracking it.
The domain was registered through Spaceship, Inc. on 2026-10-07 and was caught the same day, which points to a freshly built page launched immediately rather than a compromised older site. Traffic runs through Cloudflare (AS13335) in the US, so the visible address belongs to Cloudflare's network and conceals the actual origin server.
If you connected a wallet to this site, use a token-approval checker to revoke any permissions you granted, and move remaining funds to a fresh wallet if you signed anything you did not fully understand. If you entered a password, email or seed phrase, change the password and enable 2FA wherever it was reused. Treat any exposed seed phrase as fully compromised and migrate your assets at once. Only use The Index through channels you have verified independently. Defenders should block theindexfinance.forum at DNS and proxy level and watch for lookalike forum or finance domains that reuse the "get paid in stocks" lure.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
0x12f190a9f9d7d37a250758b26824b97ce941bf54Format validated · Domain analysis0x2e0847e8910a9732eb3fb1bb4b70a580adad4fe3Format validated · Domain analysis0x322f0929c4625ed5bad873c95208d54e1c003b2dFormat validated · Domain analysis0x39ADB8acD07427D338b5f1AfAb436A04AbFdB7c4Format validated · Domain analysis0x4a0e65a3eccec6dbe60ae065f2e7bb85fae35eeaFormat validated · Domain analysis0x5f10a1c971b69e47e059e1dc91901b59b3fb49c3Format validated · Domain analysis0x6330d8c3178a418788df01a47479c0ce7ccf450bFormat validated · Domain analysis0x822cc93ffd030293e9842c30bbd678f530701867Format validated · Domain analysis0x86923f96303d656e4aa86d9d42d1e57ad2023fdcFormat validated · Domain analysis0x894e1ec2d74ffe5aef8dc8a9e84686accb964f2aFormat validated · Domain analysis0xaf3d76f1834a1d425780943c99ea8a608f8a93f9Format validated · Domain analysis0xb0992820e760d836549ba69bc7598b4af75dee03Format validated · Domain analysis0xb90a19ff0af67f7779aff50a882a9cff42446400Format validated · Domain analysis0xc0d6457c16cc70d6790dd43521c899c87ce02f35Format validated · Domain analysis0xc72b96e0e48ecd4dc75e1e45396e26300bc39681Format validated · Domain analysis0xd0601ce157db5bdc3162bbac2a2c8af5320d9eecFormat validated · Domain analysis0xd917b029c761d264c6a312bbbcda868658ef86a6Format validated · Domain analysis0xe93237c50d904957cf27e7b1133b510c669c2e74Format validated · Domain analysis0xff080c8ce2e5feadaca0da81314ae59d232d4afdFormat validated · Domain analysisIoC extraction recorded 2026-10-08 04:00:54 UTC
Last checked
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Danh tiếng của Edge-IP không được quy cho tên miền này.
kristin.ns.cloudflare.compete.ns.cloudflare.comLocation describes the IP network.
7085f13ed55189e119b41660f8e0112bfc34af684c8ebb32c766f99fc9c77449Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of theindexfinance.forum · checked Oct 7, 2026
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
alive_content: raw=ok; http=200; via=https_proxy; server=cloudflare
theindexfinance.forum
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Không rõ→live_content
content_served
Không rõ→live_content
content_served
Không rõ→live_content
content_served
Không rõ→live_content
content_served
Không rõ→live_content
content_served
Không rõ→live_content
content_served
Không rõ→live_content
content_served
Không rõ→live_content
content_served
Không rõ→live_content
content_served
Không rõ→live_content
content_served
Không rõ→live_content
content_served
Không rõ→inactive
http_no_content
Có thể truy cập
No threat flag
View source9/92 engine detections
View source4 community references
View sourcePD-20261007-3C8AA8
Page captured
View sourcetheindexfinance.forum
View source30 tên miền tương tự đã lưu
Mỗi làn là một lý do khiến một tên miền được liên kết với máy chủ này. Kích thước nút biểu thị các phát hiện từ VirusTotal, còn các nút có đường gạch ngang đã ngừng hoạt động. Danh sách đầy đủ được trình bày dưới đây.
Có cùng mã băm favicon hoặc cùng tiêu đề trang với máy chủ này.
Các báo cáo này giải quyết cùng một IP biên được chia sẻ. Chúng giúp khám phá báo cáo nhưng không ngụ ý quyền sở hữu chung hoặc máy chủ gốc được chia sẻ.
Reports with the same collector label. A shared label does not establish impersonation or common ownership. View matching reports →
Được đăng ký thông qua cùng một nhà đăng ký tên miền. Một nhà đăng ký tên miền phục vụ hàng triệu khách hàng không có mối liên hệ với nhau, do đó việc này chỉ cho thấy sự trùng hợp về số liệu chứ không chứng minh được mối liên hệ nào.
PD-20261007-3C8AA8 Recipient: abuse@spaceship.com Nếu bạn đã nhập thông tin xác thực tài khoản, thông tin cá nhân hoặc thông tin thanh toán hoặc đã tải xuống tệp từ miền này, hãy hành động ngay lập tức. Dưới đây là các nguồn lực giúp bạn báo cáo vụ việc và bảo vệ chính mình.


Chọn quốc gia của bạn để nhận liên hệ tội phạm mạng chính thức hoặc soạn thảo đơn khiếu nại →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
theindexfinance.forum)Dù bạn chưa nắm rõ tất cả các chi tiết — vẫn nên nộp báo cáo. Ngay cả những thông tin không đầy đủ cũng vẫn có ích cho công tác điều tra.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Phân tích mối đe dọa bằng cách sử dụng danh sách chặn được lưu trữ, WHOIS, DNS và bằng chứng quét công khai
Quét ngayHãy gửi các tên miền đáng ngờ đến cơ sở dữ liệu mối đe dọa của chúng tôi — để bảo vệ cộng đồng
Báo cáoCác báo cáo lừa đảo gần đây và những thay đổi về tính khả dụng được quan sát thấy
Theo dõiTheo dõi các mối đe dọa đang diễn ra hoặc phản đối danh sách này nếu bạn cho rằng đây là kết quả báo động sai
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.