Chuyển đến báo cáo bảo mật
Bảo mật miền và thông tin về mối đe dọa
bhbdistributors.shop favicon

bhbdistributors.shop

“BHB DISTRIBUTORS INCORPORATED | BHB DISTRIBUTORS”

Nhà đăng ký
Dynadot
Resolved IP
162.222.90.202
Registered
24/05/2026
PhishDestroy assessment Quan trọng
sẵn có Hoạt động được biết đến lần cuối Quan sát khả năng tiếp cận được lưu trữ mới nhất Đã quan sát thấy · HTTP probe
Tổng số phát hiện Virus: 6/92 Loại lừa đảo: E-Commerce Scam
OTX: 3 refs 16/10/2026 1 Report Sent
API
Tên miền này đã bị đánh dấu là có hại
Công cụ bảo mật báo cáo phát hiện: 6. Hãy hết sức thận trọng — không nhập thông tin xác thực hoặc thông tin cá nhân.
ABUSE NOTICE · 72H+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@dynadot.com. The latest stored availability evidence still shows the domain reachable; 4 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
4 days
Reports sent
1
Latest case ID
PD-20261016-7F7192
Current status
HTTP 200 at latest stored check
VirusTotal
engine detections
Google Safe Browsing
OTX
community references
Page captures
open gallery
Domain age
Reports sent
view timeline
Tóm tắt báo cáo

Lừa đảo: bhbdistributors.shop — Hoạt động được biết đến lần cuối (HTTP 200). Tóm tắt bằng chứng: VirusTotal 6/92 (CRDF, Forcepoint ThreatSeeker, Gridinsoft…

Phân tích chi tiết của PhishDestroy AI bên dưới được giữ bằng tiếng Anh để bảo toàn hồ sơ pháp chứng gốc.

Source evidenceVirusTotal 6 / 92 · OTX 3 references 6 sources

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

Analysis

Quan trọng
VirusTotal
6 / 92
OTX
3 community refs
Page captures
2

PhishDestroy threat report

Overview

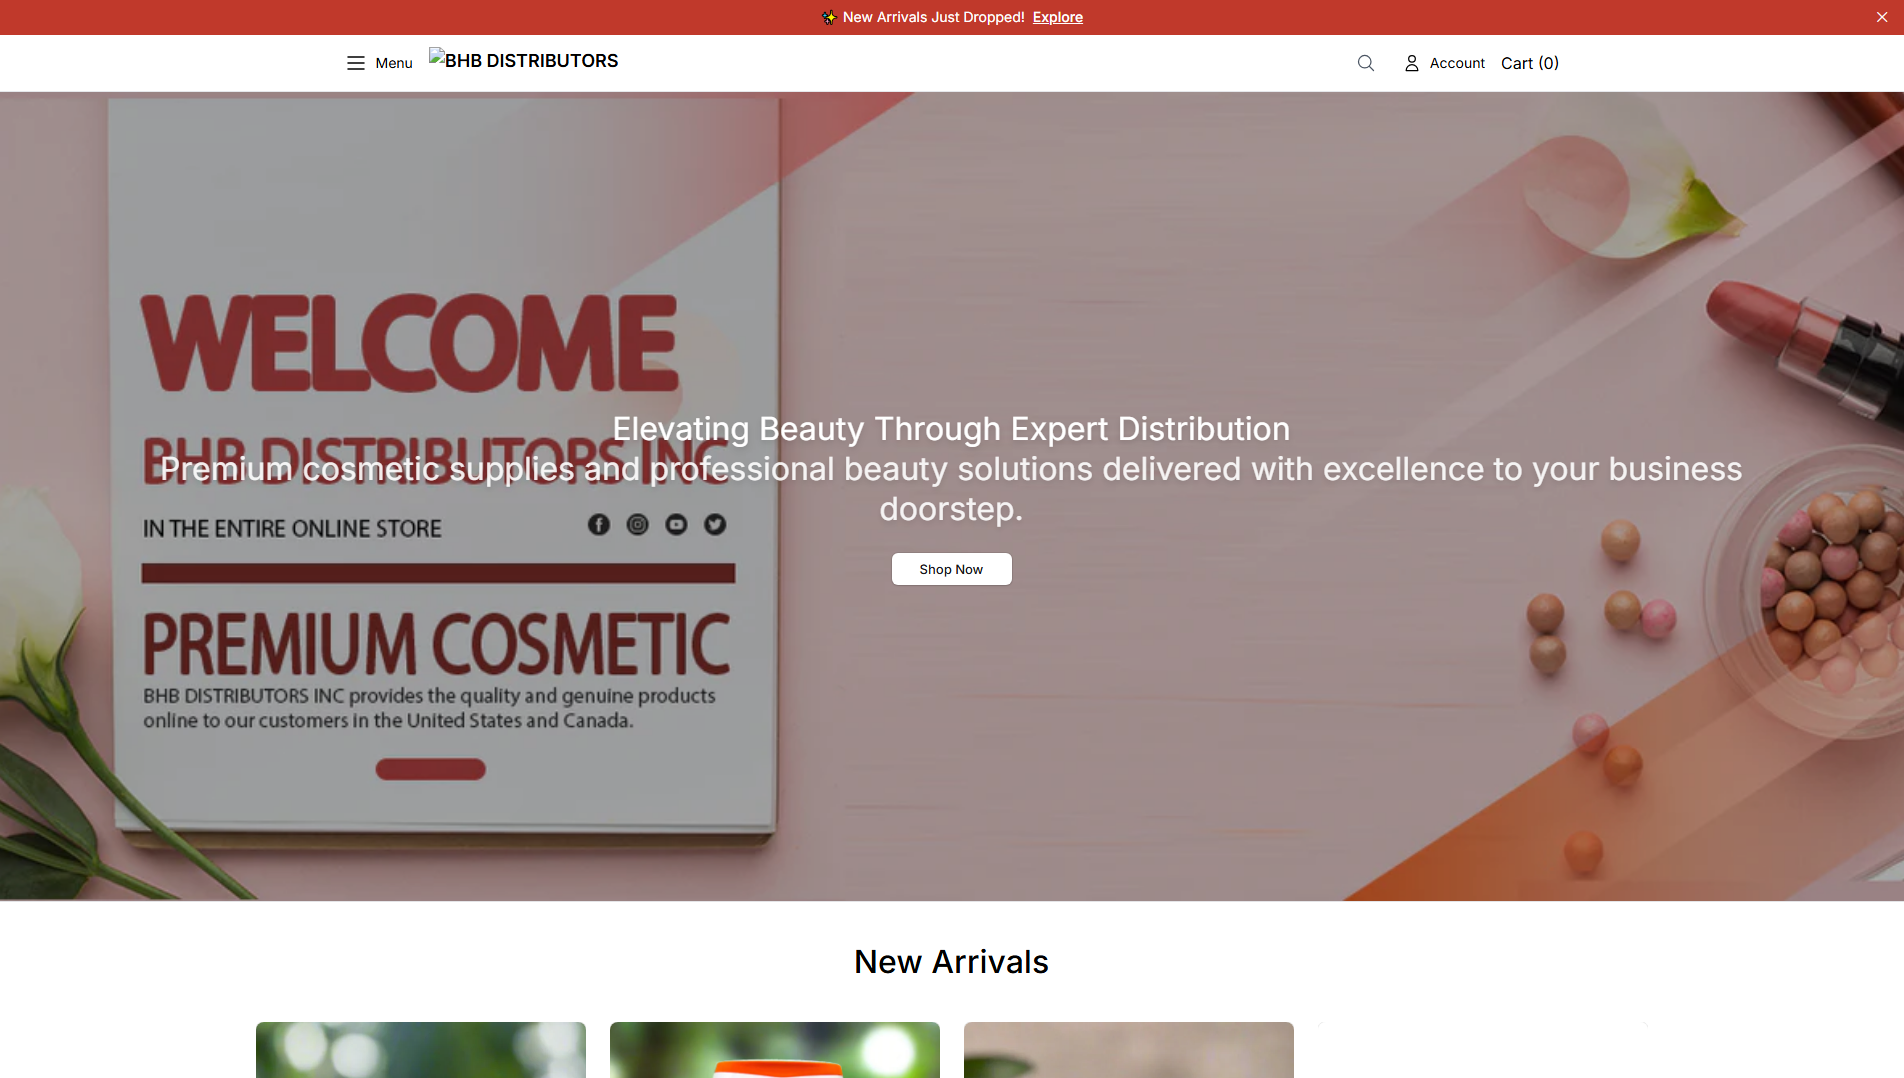
bhbdistributors.shop is a fraudulent storefront that presents itself as BHB Distributors Incorporated, a wholesale-style distributor. It targets online shoppers looking for products at attractive prices. PhishDestroy first flagged it on 2026-10-16. As of 2026-10-19 the site is still online and serving its shop content, so it can still take orders.

How the scam works

Fake shops like this one show a professional-looking catalog under a business name, here "BHB DISTRIBUTORS INCORPORATED", to suggest an established company. Shoppers add items to a cart and pay at checkout. The goods then never ship, or something worthless arrives instead. Victims lose the money they paid. They can also lose the name, address, phone number and payment details entered at checkout, which can be reused for fraud or follow-up phishing.

Evidence

urlscan.io rates the site malicious and specifically identifies it as a fake shop, which matches our classification. On VirusTotal, 6 of 92 engines flagged it as of 2026-10-19: CRDF, Forcepoint ThreatSeeker, Gridinsoft, LevelBlue, Netcraft and URLQuery. That count is modest, so most security products will not block the site yet. The domain also appears in 3 AlienVault OTX threat pulses, showing that other researchers have tied it to malicious activity.

Infrastructure

The domain was registered through Dynadot Inc. on 2026-05-24, almost five months before we detected it. That gap suggests it either sat idle or ran quietly before drawing attention. It is hosted on the Malakmadze Web LLC network in Georgia. The Let's Encrypt certificate only means the connection is encrypted and shows a padlock. It says nothing about whether the shop is legitimate.

What to do

If you paid on this site, contact your bank or card issuer right away, report the charge as fraud and ask for a chargeback. Ask them to replace the card if you entered its full details. If you paid by bank transfer, crypto or a payment app, report it to that provider immediately, since recovery depends on acting quickly. Expect phishing emails, texts or calls that use your order details, and do not respond to anyone offering refunds for a fee. If you created an account, change that password everywhere you reused it. Defenders should block the domain at web and DNS filters and watch for staff or customers who have visited it.

Blocklist matchesPhishDestroy 1
PhishDestroy PhishDestroy list View source

Bản chụp đã lưu · 2 captures

Observed page title
BHB DISTRIBUTORS INCORPORATED | BHB DISTRIBUTORS
Chứng chỉ TLS
Được cấp bởi Let's Encrypt / YE1 · stored validity ends in 79 days

Domain details

Tên miền
URLScan verdict Độc hại score 100 Phishing brand: Fakeshop report ↗
Uy tín IP abuse score 0/100 0 reports checked 16/10/2026
OTX tags 2026-10activeall-domainsblocklistcontentcryptotên miềndrainerfraudmonthlyphishdestroyphishingscam
Nhà đăng ký Dynadot US(US)
Liên hệ báo cáo lạm dụngabuse@rashost.com, abuse@dynadot.com
Cơ quan đăng ký ICANNICANN Lookup (RDAP) →
Đăng kýĐược tạo 24/05/2026 (149d) — Expires 24/05/2027
Trạng thái HTTP200
Chi tiết kỹ thuậtProvenance & timestamps
Lần đầu tiên được phát hiện16/10/2026
DOM Analysisanalyzed 16/10/2026score 73/100
Submitted URLhttp://bhbdistributors.shop/
Favicon Hash
Mã vụ việc
ICANN OVERSIGHT

Bối cảnh công nhận và RAA

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Việc công nhận là một hợp đồng, không phải con dấu bảo đảm an toàn. Xác minh các khoản phí của ICANN Đọc RAA §3.18 PHISHDESTROY INVESTIGATIONICANN funding, contracts, and DNS abuse oversight
Accountability draft Không có nội dung nào được tự động gửi.

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
162.222.90.202
Network ASN
AS199242
Organization
Beijing Ruihao Kai Yuan Technology Co., Ltd
Observed location
GE

Máy chủ tên 2

  • roan.ns.cloudflare.com
  • virginia.ns.cloudflare.com

Location describes the IP network.

Chứng chỉ TLS

Issuer
Let's Encrypt / YE1
Valid from
2026-10-10 04:02:29
Valid until
2027-01-08 04:02:28
Validity
Within stored validity dates
Collection time
2026-10-16 01:02:07 UTC
Collection source
PhishDestroy collector
Certificate fingerprintde364b09782e01f8c7dab7d9cb06cdff8d2b0a9104d794650074760994b8de06

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Latest Classified Outcome 2026-10-19 22:46:15 UTC

Primary outcome Nội dung đang hoạt động reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation Nội dung đang hoạt động Ordinary HTTP content served 90% 2026-10-19 22:46:15 UTC
RDAP registration Không rõ
Observed timeline last reachable: 2026-10-19 22:46:15 UTC last content: 2026-10-19 22:46:15 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Recorded subdomains1

Hostnames retained in the domain record or Certificate Transparency cache. A hostname alone does not establish current availability or malicious activity.

  • www.bhbdistributors.shopDomain record

The original observation time is not recorded for these hostnames.

Công nghệ · 1 identified
Detected via Cloudflare Radar · Wappalyzer engine
Báo cáo tên miền này Gửi bằng chứng và góp phần bảo vệ người khác

Phân tích của VirusTotal

6 / Nhà cung cấp bảo mật 92 đã gắn cờ miền này
View on VT
Last analyzed First positive detection Previous stored snapshot: 0 detections
CRDF
Forcepoint ThreatSeeker
Gridinsoft
LevelBlue
Netcraft
URLQuery

Bằng chứng lưu trữ

Wayback Machine Snapshot
Một ảnh chụp nhanh lịch sử có sẵn để xem xét bằng chứng
View Archive
Phân tích hiệu suất trang

Google PageSpeed Insights — mobile performance audit of bhbdistributors.shop · checked Oct 16, 2026

82
Needs Work
Performance
FCP
2.89s
First Contentful Paint
LCP
3.68s
Largest Contentful Paint
CLS
0.025
Cumulative Layout Shift
TBT
106ms
Total Blocking Time
SI
4.46s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Stored Capture Evidence 1 snapshot

Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.

Archived HTTP response HTTP 200
Requested URL: http://bhbdistributors.shop/
Final URL: https://bhbdistributors.shop/
BHB DISTRIBUTORS INCORPORATED | BHB DISTRIBUTORS
BHB DISTRIBUTORS INCORPORATED
Phản ứng
HTTP 200
HTML body
269.0 KB
Compressed
39.9 KB
Links
28 internal · 0 external
Detected technologies
react
Selected response headers
Cache-Control: private, no-cache, no-store, max-age=0, must-revalidate
Content-Encoding: gzip
Content-Type: text/html; charset=utf-8
Security headers present
X-Frame-OptionsX-Content-Type-OptionsX-XSS-ProtectionReferrer-Policy
HSTS: not observed DNSSEC: not observed WAF / firewall: not observed Cloaking flag: not observed
Open Graph title: BHB DISTRIBUTORS INCORPORATED
Open Graph description: BHB DISTRIBUTORS INCORPORATED
Twitter card: summary_large_image
Saved response-header values · 13
Alt-Svc
h3=":443"; ma=2592000
Cache-Control
private, no-cache, no-store, max-age=0, must-revalidate
Content-Encoding
gzip
Content-Type
text/html; charset=utf-8
Date
Fri, 16 Oct 2026 00:30:17 GMT
Link
; rel=preload; as="style"
Referrer-Policy
strict-origin-when-cross-origin
Transfer-Encoding
chunked
Vary
RSC, Next-Router-State-Tree, Next-Router-Prefetch, Next-Router-Segment-Prefetch, Accept-Encoding
Via
1.1 Caddy
X-Content-Type-Options
nosniff
X-Frame-Options
SAMEORIGIN
X-XSS-Protection
1; mode=block

Values retained by the collector; long values may be shortened during collection.

Registration & observation details3

Availability observations

Last reachable observation
Last content observation
Estimate basis
Currently reachable

An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.

Stored observation history11

Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.

  1. Availability monitor · Recorded state

    Không có sẵn→Có thể truy cập

  2. Availability monitor · Recorded state

    Có thể truy cập→Không có sẵn

  3. Availability monitor · Recorded state

    Không rõ→live_content

    content_served

  4. Availability monitor · Recorded state

    Không có sẵn→Có thể truy cập

  5. Availability monitor · Recorded state

    Có thể truy cập→Không có sẵn

Earlier observations 6
  1. Availability monitor · Recorded state

    Không rõ→live_content

    content_served

  2. Availability monitor · Recorded state

    Không rõ→live_content

    content_served

  3. Availability monitor · Recorded state

    Không có sẵn→Có thể truy cập

  4. Availability monitor · Recorded state

    Có thể truy cập→Không có sẵn

  5. Availability monitor · Recorded state

    Không rõ→live_content

    content_served

  6. Availability monitor · First collection record

    Có thể truy cập

Recorded activity

6 entries
  1. Google Safe Browsing

    No threat flag

    View source
  2. VirusTotal

    6/92 engine detections

    View source
  3. Abuse report sent

    PD-20261016-7F7192

    abuse@dynadot.com
  4. AlienVault OTX

    3 community references

    View source
  5. Added to PhishDestroy

    bhbdistributors.shop

    View source
  6. URLScan

    Page captured

    View source

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

bhbdistributors.shop

Bằng chứng và các báo cáo bên ngoài

Ảnh chụp bằng chứng đã gửi
Sent: Ledger records: 1 Case ID: PD-20261016-7F7192 Recipient: abuse@dynadot.com
PDF notice generated Notice text archived (291 chars)
Abuse notice text as sent to the provider
Registrar: Dynadot LLC / Dynadot Inc (United States)
Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
Phân tích sâu
Help & reporting

Bạn có bị ảnh hưởng bởi trang web này không?

6 evidence signal groups linked 1 stored notification records Hoạt động được biết đến lần cuối
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Nếu bạn đã nhập thông tin xác thực tài khoản, thông tin cá nhân hoặc thông tin thanh toán hoặc đã tải xuống tệp từ miền này, hãy hành động ngay lập tức. Dưới đây là các nguồn lực giúp bạn báo cáo vụ việc và bảo vệ chính mình.

Official reporting routes

Hãy cảnh giác với những kẻ lừa đảo lợi dụng việc phục hồi dữ liệu! Tội phạm có thể liên hệ lại với nạn nhân trong khi giả làm điều tra viên, luật sư hoặc nhân viên phục hồi. Không trả phí trả trước hoặc chia sẻ thông tin đăng nhập. Tìm hiểu thêm về gian lận trong quá trình phục hồi →

Hãy báo cáo với chính quyền địa phương

Chọn quốc gia của bạn để nhận liên hệ tội phạm mạng chính thức hoặc soạn thảo đơn khiếu nại →.

Danh mục 97 quốc gia

Template-based draft · optional AI wording assistance requires separate consent

Bản nháp có sự hỗ trợ của AI - chi tiết sự cố được nhà cung cấp AI xử lý · Hãy tự mình xem xét và gửi nó
After a phishing incident

Các khuyến nghị và lời khuyên dành cho nạn nhân

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

Tôi nên làm gì ngay lập tức?

Khẩn cấp

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • Thay đổi tất cả mật khẩu — email, tài khoản Exchange, bất kỳ dịch vụ nào sử dụng chung mật khẩu
  • Bật xác thực hai yếu tố (2FA) sử dụng ứng dụng xác thực (không phải SMS). Tắt tính năng khôi phục bằng SMS
  • Thẻ đóng băng nếu bạn đã nhập thông tin tài khoản ngân hàng trên trang web lừa đảo

Tôi nên thu thập những thông tin nào cho báo cáo của mình?

Hướng dẫn của FBI

Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • Ngày và giờ chính xác — của mỗi giao dịch và lần tiếp xúc đầu tiên với kẻ lừa đảo
  • Ảnh chụp màn hình — trang web lừa đảo, tin nhắn trò chuyện, email, giao dịch ví điện tử, mạng xã hội
  • Tất cả các URL và tên miền được kẻ lừa đảo sử dụng (bao gồm bhbdistributors.shop)
  • Truyền thông — các email, tin nhắn, số điện thoại, tên người dùng mà kẻ lừa đảo đã sử dụng

Dù bạn chưa nắm rõ tất cả các chi tiết — vẫn nên nộp báo cáo. Ngay cả những thông tin không đầy đủ cũng vẫn có ích cho công tác điều tra.

Tôi nên báo cáo vụ lừa đảo này ở đâu?

  • FBI IC3 — Trung tâm Tiếp nhận Khiếu nại về Tội phạm Mạng (Hệ thống báo cáo liên bang Hoa Kỳ)
  • Europol — Báo cáo về tội phạm mạng tại châu Âu (EU)
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • Cảnh sát địa phương — lập biên bản chính thức, ngay cả khi họ không thể hành động ngay lập tức

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do phishing scams typically work?

  • Các trang web giả mạo — các bản sao giống hệt đến từng pixel của các trang web chính thống, chỉ khác một chút về tên miền
  • Giết mổ lợn — niềm tin được xây dựng trong nhiều tuần qua Telegram/WhatsApp/các ứng dụng hẹn hò, sau đó tiền bị đánh cắp
  • Các chiêu lừa đảo lợi dụng việc phục hồi — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • Các chiêu lừa đảo sử dụng trí tuệ nhân tạo — các video deepfake, các vụ lừa đảo qua email tự động và các trang web do trí tuệ nhân tạo tạo ra khiến việc phát hiện hành vi gian lận trở nên khó khăn hơn

Làm thế nào để tôi có thể tự bảo vệ mình trong tương lai?

  • Đánh dấu các trang web chính thức — Đừng bao giờ nhấp vào các liên kết trong email, tin nhắn trực tiếp (DM) hoặc quảng cáo
  • Xác minh tên miền — kiểm tra xem PhishDestroy Trước khi thực hiện bất kỳ tương tác nào, hãy kiểm tra HTTPS, chính tả và thời gian hoạt động của tên miền.
  • "Quá tốt để là sự thật" = lừa đảo — lợi nhuận được đảm bảo, sự ủng hộ của người nổi tiếng, thời hạn gấp rút

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

Luôn cập nhật thông tin, luôn an toàn

Theo dõi các mối đe dọa đang diễn ra hoặc phản đối danh sách này nếu bạn cho rằng đây là kết quả báo động sai

Dòng tin tức về các mối đe dọa thời gian thực Khiếu nại về thông tin đăng tải này
About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

Nhúng báo cáo này

Hãy chia sẻ thông tin tình báo về mối đe dọa này trên trang web hoặc blog của bạn

embed.html
<iframe
  src="https://phishdestroy.io/vi/embed/domain/bhbdistributors.shop"
  title="PhishDestroy threat report for bhbdistributors.shop"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>