URLQuery
2 det.
Mở báo cáo
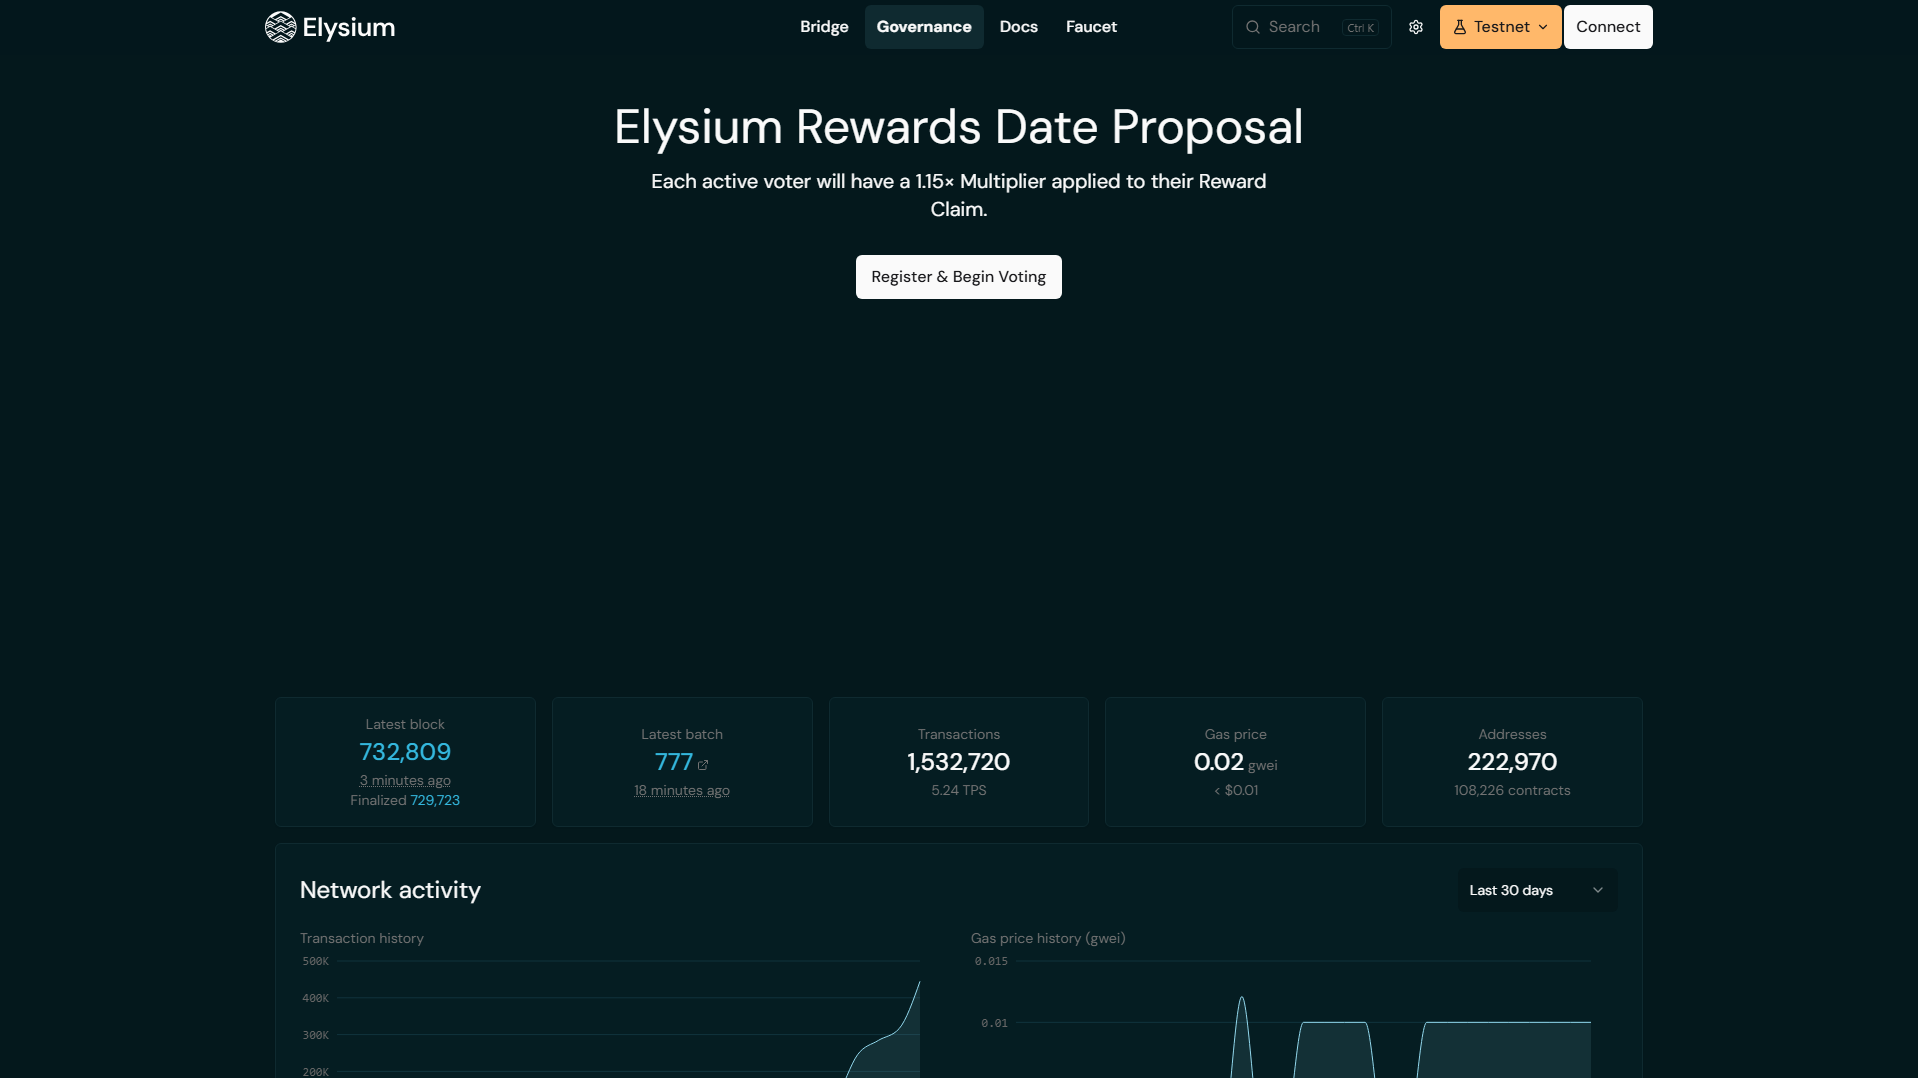
“Elysium | Governance”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@dynadot.com.
The latest stored availability evidence still shows the domain reachable; 41 hours has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
app-elysium.xyz — Hoạt động được biết đến lần cuối (HTTP 301). Loại lừa đảo: Impersonation. Tóm tắt bằng chứng: VirusTotal 0/92; URLQuery 2 det.; PhishDestroy score 78/100. Nhà đăng ký: Dynadot.
Phân tích chi tiết của PhishDestroy AI bên dưới được giữ bằng tiếng Anh để bảo toàn hồ sơ pháp chứng gốc.
2 det.
Mở báo cáoSuspicious
Mở báo cáo0 / 92 engine detections
Mở báo cáo4 community references
Mở báo cáoNo threat flag
Mở báo cáoNo malicious flag
Mở báo cáoResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
AI-assisted evidence review
The domain app-elysium.xyz was documented in a VirusTotal scan on 2026-10-17, where it was checked by 92 scanners with zero detections. Additionally, app-elysium.xyz appears in the PhishDestroy internal listing, which catalogs domains for ongoing observation.
VirusTotal checked app-elysium.xyz on 2026-10-17, recording zero detections out of 92 total scanners. OTX referenced the domain with four pulses on 2026-10-17. The PhishDestroy internal listing includes app-elysium.xyz as of the latest evidence review. The domain was registered with Dynadot Inc on 2026-09-29.
VirusTotal provides a record of how app-elysium.xyz was evaluated by a wide range of external scanners, documenting the results of those checks. OTX contains references to the domain through its pulse system, which measures its mention in shared intelligence feeds. The PhishDestroy internal listing is a publisher-specific catalogue that stores domains for continued observation, contributing to the domain's recorded profile.
For app-elysium.xyz, retain the VirusTotal scan results and OTX pulse references for future comparison with subsequent intelligence records. Preserve the PhishDestroy internal listing entry to support ongoing monitoring. Review each source's evidence regularly to track any new observations or changes in recorded data.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
0x0B809f9C0aD91248DB28d4B5C2B59c563ea49C81Format validated · Domain analysis0x0E865d156da937191d7C4814126718f583447798Format validated · Domain analysis0x10ce23992Bea3709F4E73f875665c0B59A32eBDaFormat validated · Domain analysis0x245bFe8c6c2429f6a7743d53377Ae39b98500459Format validated · Domain analysis0x4A611D95495F8a90779FFd39986aab85359A2CDfFormat validated · Domain analysis0x57A48162BD894964db10b2751a2e89Ae0FA56523Format validated · Domain analysis0x58E5dfF1f9f63153De9824055b711741faC71aAAFormat validated · Domain analysis0x7551Bb3D085021bcEC0812B18A268Ee6A888C4a0Format validated · Domain analysis0x93dD4317e1B4807b1Cd7CdF46bA11266D43e76E8Format validated · Domain analysis0x9672D621C16d8E599c2e20Cc6EEDDf9402aC2a17Format validated · Domain analysis0xA4b000000000000000000073657175656e636572Format validated · Domain analysis0xCebC1EAD2f2DEB930b84412A752EfcD54567D4bCFormat validated · Domain analysis0xaC00056863176dD5120FF79710cEcE1dAF62A125Format validated · Domain analysis0xb5C933bf1f00063696865260E578c0cd7dB7d755Format validated · Domain analysis0xb94A38a4aC46970559E89E566f2486a3Fc56BE5aFormat validated · Domain analysisIoC extraction recorded 2026-10-18 04:00:33 UTC
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Danh tiếng của Edge-IP không được quy cho tên miền này.
delilah.ns.cloudflare.comlochlan.ns.cloudflare.comLocation describes the IP network.
2d53405c0ce67adc3331ef19721ca6bdaedfe57f218bb609cddfc840b918a68dSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
https://app-elysium.xyz/voteContent-Type: text/html;charset=utf-8CF-Cache-Status: DYNAMICContent-Encoding: gzipServer: cloudflare1d827b2ac019adb0b48727e61bf6a218c90b12c0f84883252b1bf32c1aa8646ch3=":443"; ma=86400DYNAMICa4be05896b3dffb2-EWRkeep-alivegziptext/html;charset=utf-8Sat, 17 Oct 2026 08:44:29 GMT{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=nRCC91TS%2BO8YtWZ2KJe9TaQ9TfJ2%2BhPLG1er5aEMwBNJqo2JWqme%2F3ZS9MWkfWzAGRoKDwZJMlv3HoGvgv0DHR3xbtzy5Wufro4jZXT%2BMbZfaYEFcIDdpIHhzdHjeJEpUdE%3D"cloudflarecfCacheStatus;desc="DYNAMIC"chunkedAccept-EncodingValues retained by the collector; long values may be shortened during collection.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
redirect: raw=redirect_301; http=301; via=http_proxy; location=https://app-elysium.xyz/; server=cloudflare
app-elysium.xyz
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Không rõ→redirected
http_redirect
Không rõ→redirected
http_redirect
Có thể truy cập
No threat flag
View source4 community references
View source0/92 engine detections
View sourcePD-20261017-BC01B7
Page captured
View sourceapp-elysium.xyz
View sourceMỗi làn là một lý do khiến một tên miền được liên kết với máy chủ này. Kích thước nút biểu thị các phát hiện từ VirusTotal, còn các nút có đường gạch ngang đã ngừng hoạt động. Danh sách đầy đủ được trình bày dưới đây.
Các báo cáo này giải quyết cùng một IP biên được chia sẻ. Chúng giúp khám phá báo cáo nhưng không ngụ ý quyền sở hữu chung hoặc máy chủ gốc được chia sẻ.
Được đăng ký thông qua cùng một nhà đăng ký tên miền. Một nhà đăng ký tên miền phục vụ hàng triệu khách hàng không có mối liên hệ với nhau, do đó việc này chỉ cho thấy sự trùng hợp về số liệu chứ không chứng minh được mối liên hệ nào.
PD-20261017-BC01B7 Recipient: abuse@dynadot.com Registrar: Dynadot LLC / Dynadot Inc (United States) Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
Nếu bạn đã nhập thông tin xác thực tài khoản, thông tin cá nhân hoặc thông tin thanh toán hoặc đã tải xuống tệp từ miền này, hãy hành động ngay lập tức. Dưới đây là các nguồn lực giúp bạn báo cáo vụ việc và bảo vệ chính mình.


Chọn quốc gia của bạn để nhận liên hệ tội phạm mạng chính thức hoặc soạn thảo đơn khiếu nại →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
app-elysium.xyz)Dù bạn chưa nắm rõ tất cả các chi tiết — vẫn nên nộp báo cáo. Ngay cả những thông tin không đầy đủ cũng vẫn có ích cho công tác điều tra.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Phân tích mối đe dọa bằng cách sử dụng danh sách chặn được lưu trữ, WHOIS, DNS và bằng chứng quét công khai
Quét ngayHãy gửi các tên miền đáng ngờ đến cơ sở dữ liệu mối đe dọa của chúng tôi — để bảo vệ cộng đồng
Báo cáoCác báo cáo lừa đảo gần đây và những thay đổi về tính khả dụng được quan sát thấy
Theo dõiTheo dõi các mối đe dọa đang diễn ra hoặc phản đối danh sách này nếu bạn cho rằng đây là kết quả báo động sai
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.