
Tìm kiếm các tên miền đang được theo dõi và xem xét các bằng chứng đã lưu trữ, các kết quả phát hiện cũng như tình trạng khả dụng mới nhất được ghi nhận.
Tìm trong các báo cáo đã lưu. Thao tác này không gửi báo cáo mối đe dọa. Không có bản ghi không có nghĩa là tên miền an toàn.
232,387
Tổng số được theo dõi
226,566
Phát hiện VT
93,668
Lần cuối được nhìn thấy đang hoạt động
138,719
Không có sẵn tại thời điểm kiểm tra lần cuối
8
VT Đang chờ xử lý
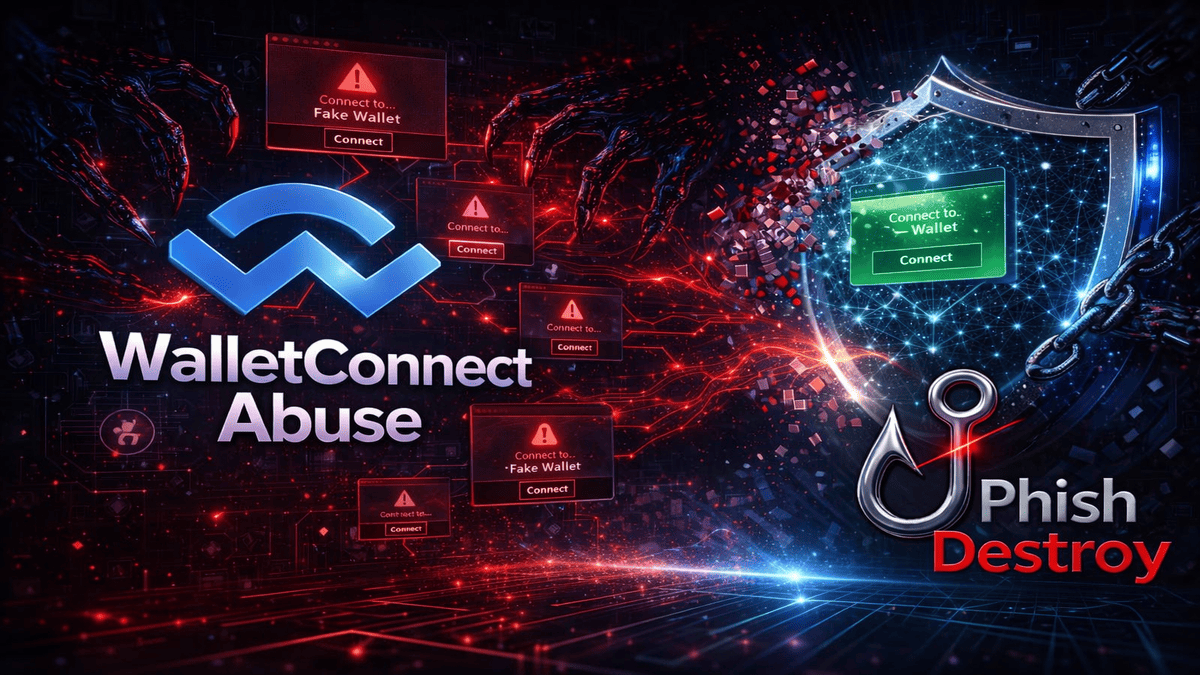
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake Tên miền
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of Lừa đảo qua email Pages
Lừa đảo qua email pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of Độc hại Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical Phân tích
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. Cơ sở hạ tầng-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea Lừa đảo qua email Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App Lừa đảo (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
Yêu cầu for private keys or seed phrases
Unexpected transaction requests
Kém website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1 Always verify domain authenticity
2 Enable two-factor authentication
3 Use hardware wallets for transactions
4 Regularly update security software
5 Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 597 domains tracked for this threat type
WalletConnect Abuse 597 domains


duplicate-disabled-6924.invalid

earn-plasma.to
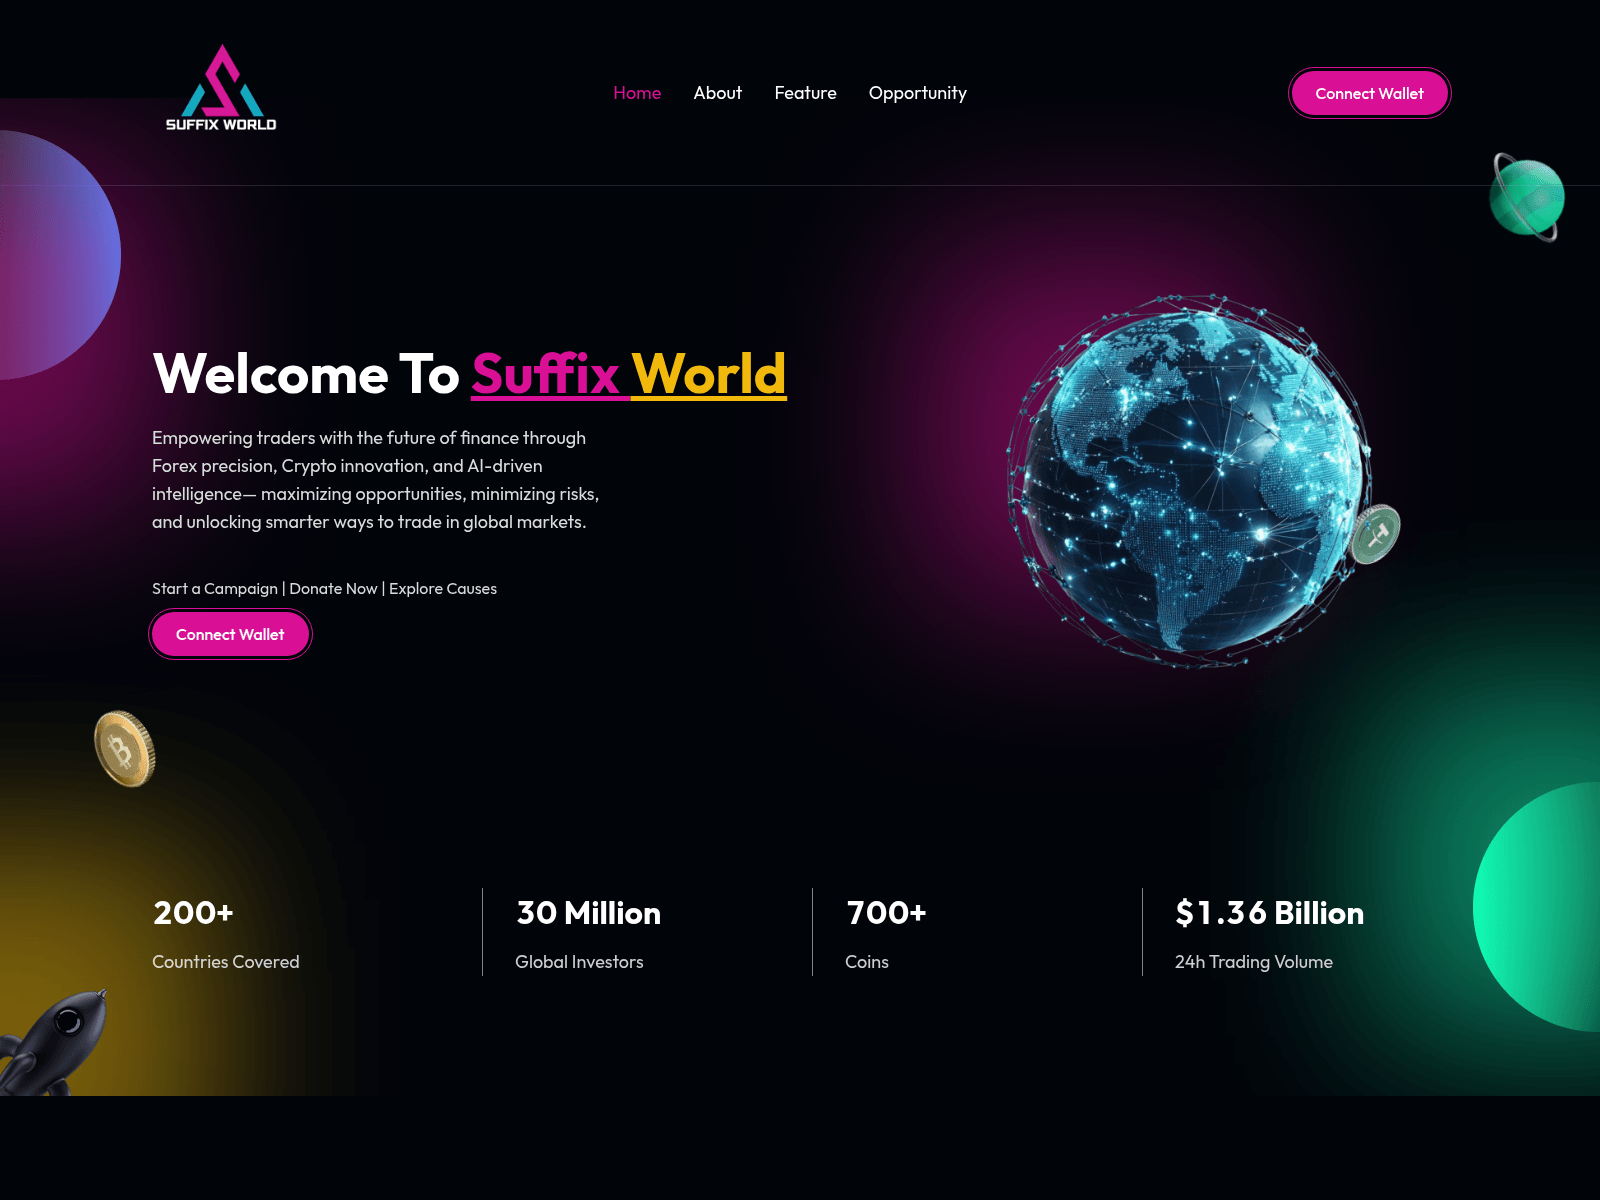
freshcenterr986.store

getpol.org

houdinizwap.com

hyperliquid.com-api-gateway-v1-gateway-dex.cloud

iucim.com

launchpol.com

mail.asssiterr.network

mailer.token2049.cyou

myneighborealice.xyz
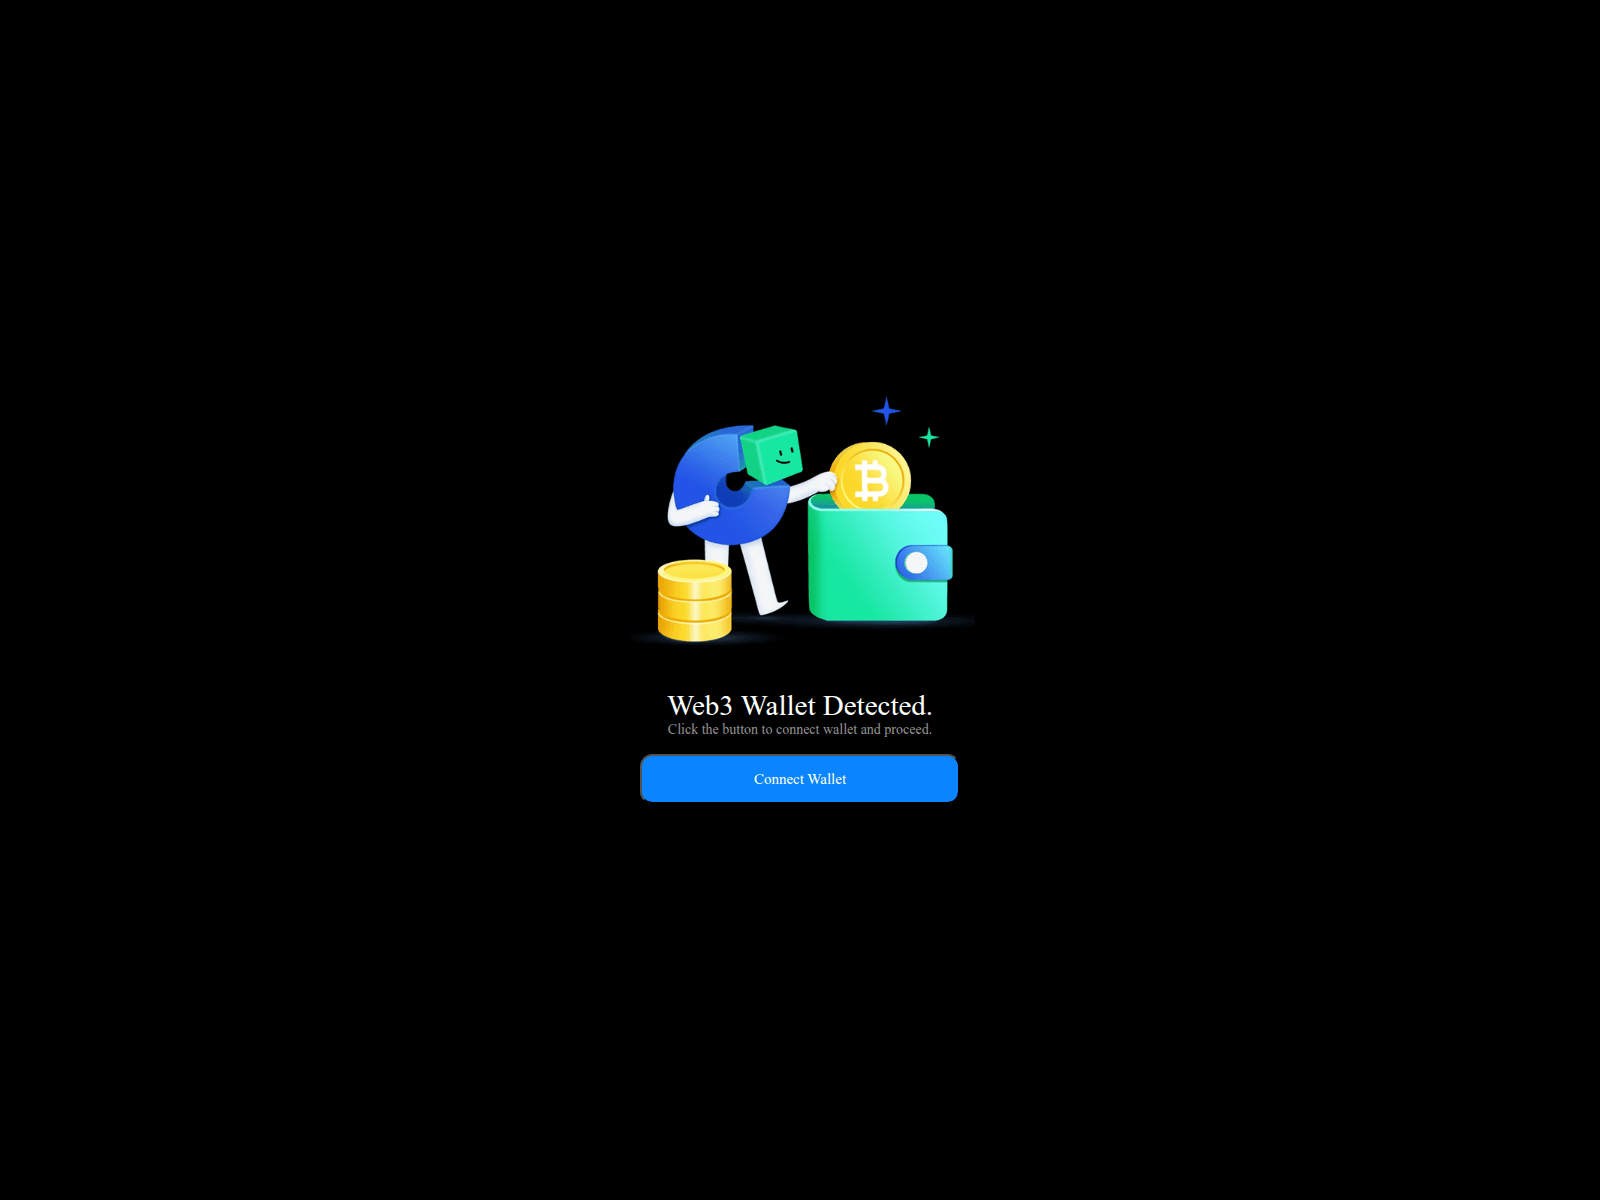
mztrn.com
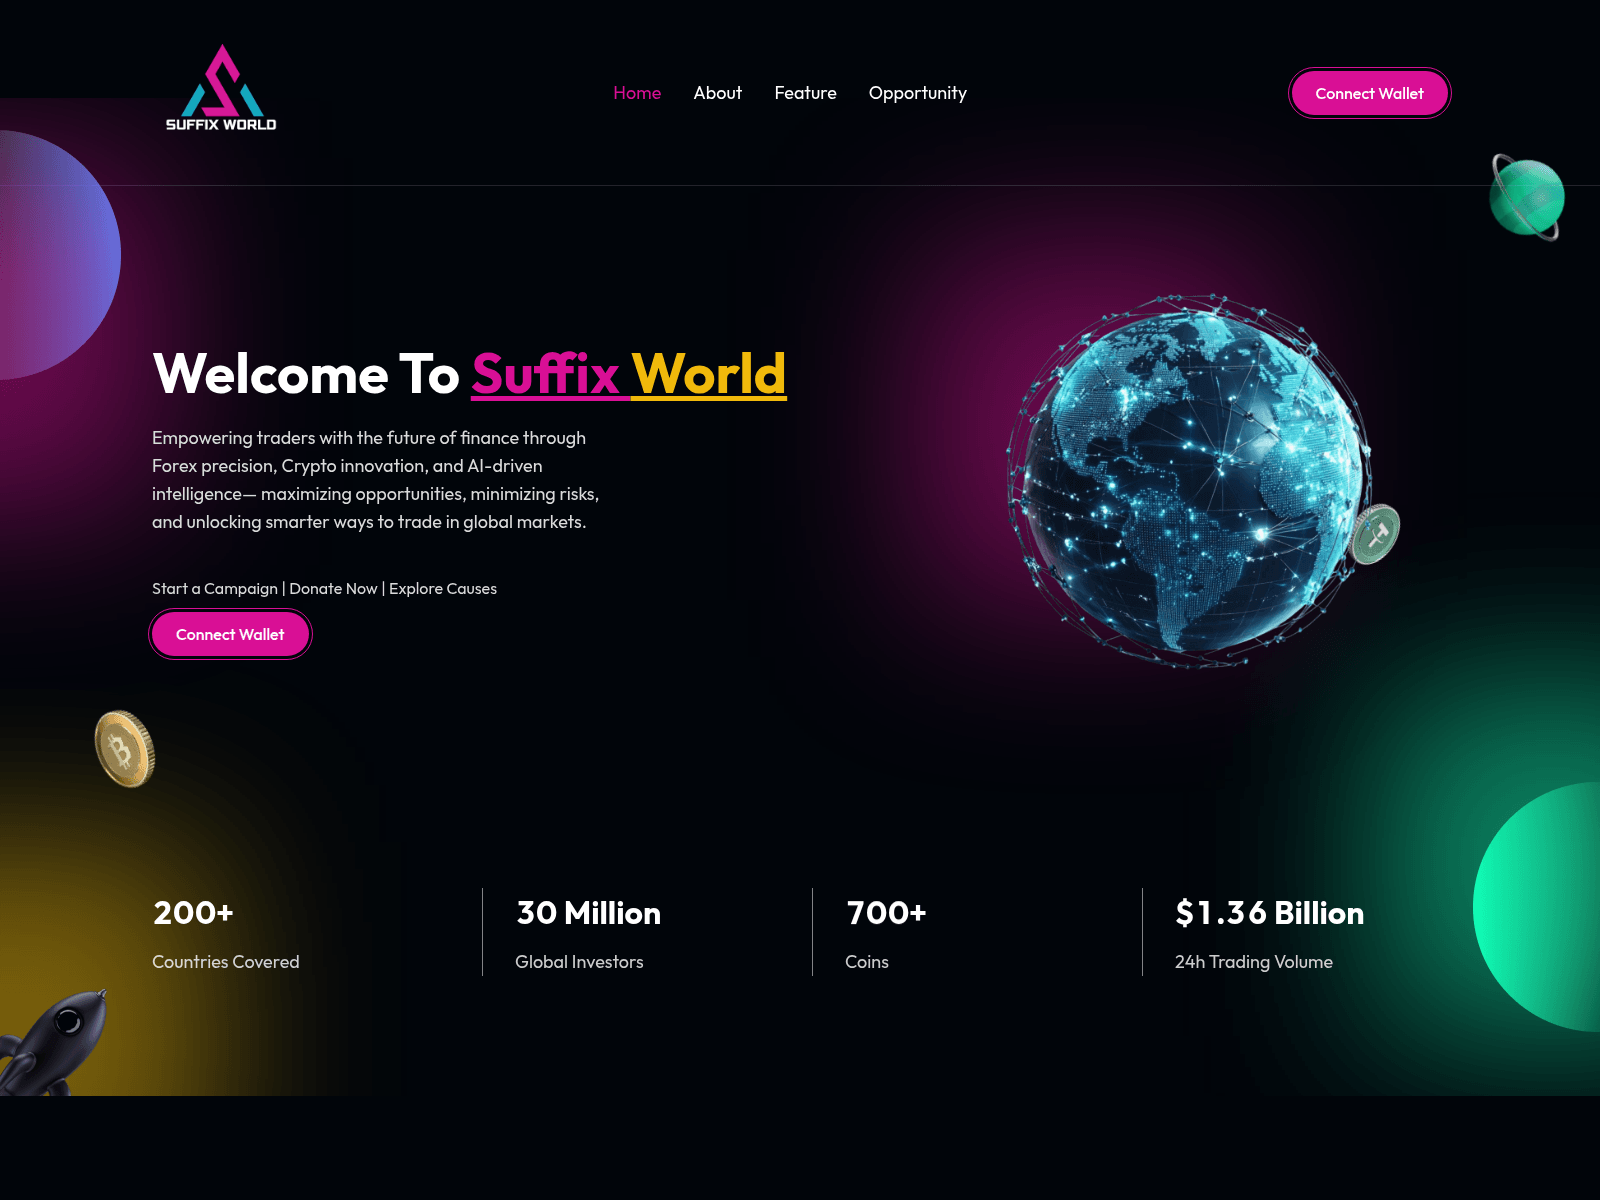
neatmarkett639.store

netcoins.shop

obtain-pol.com

onchain-crypto-max.cc
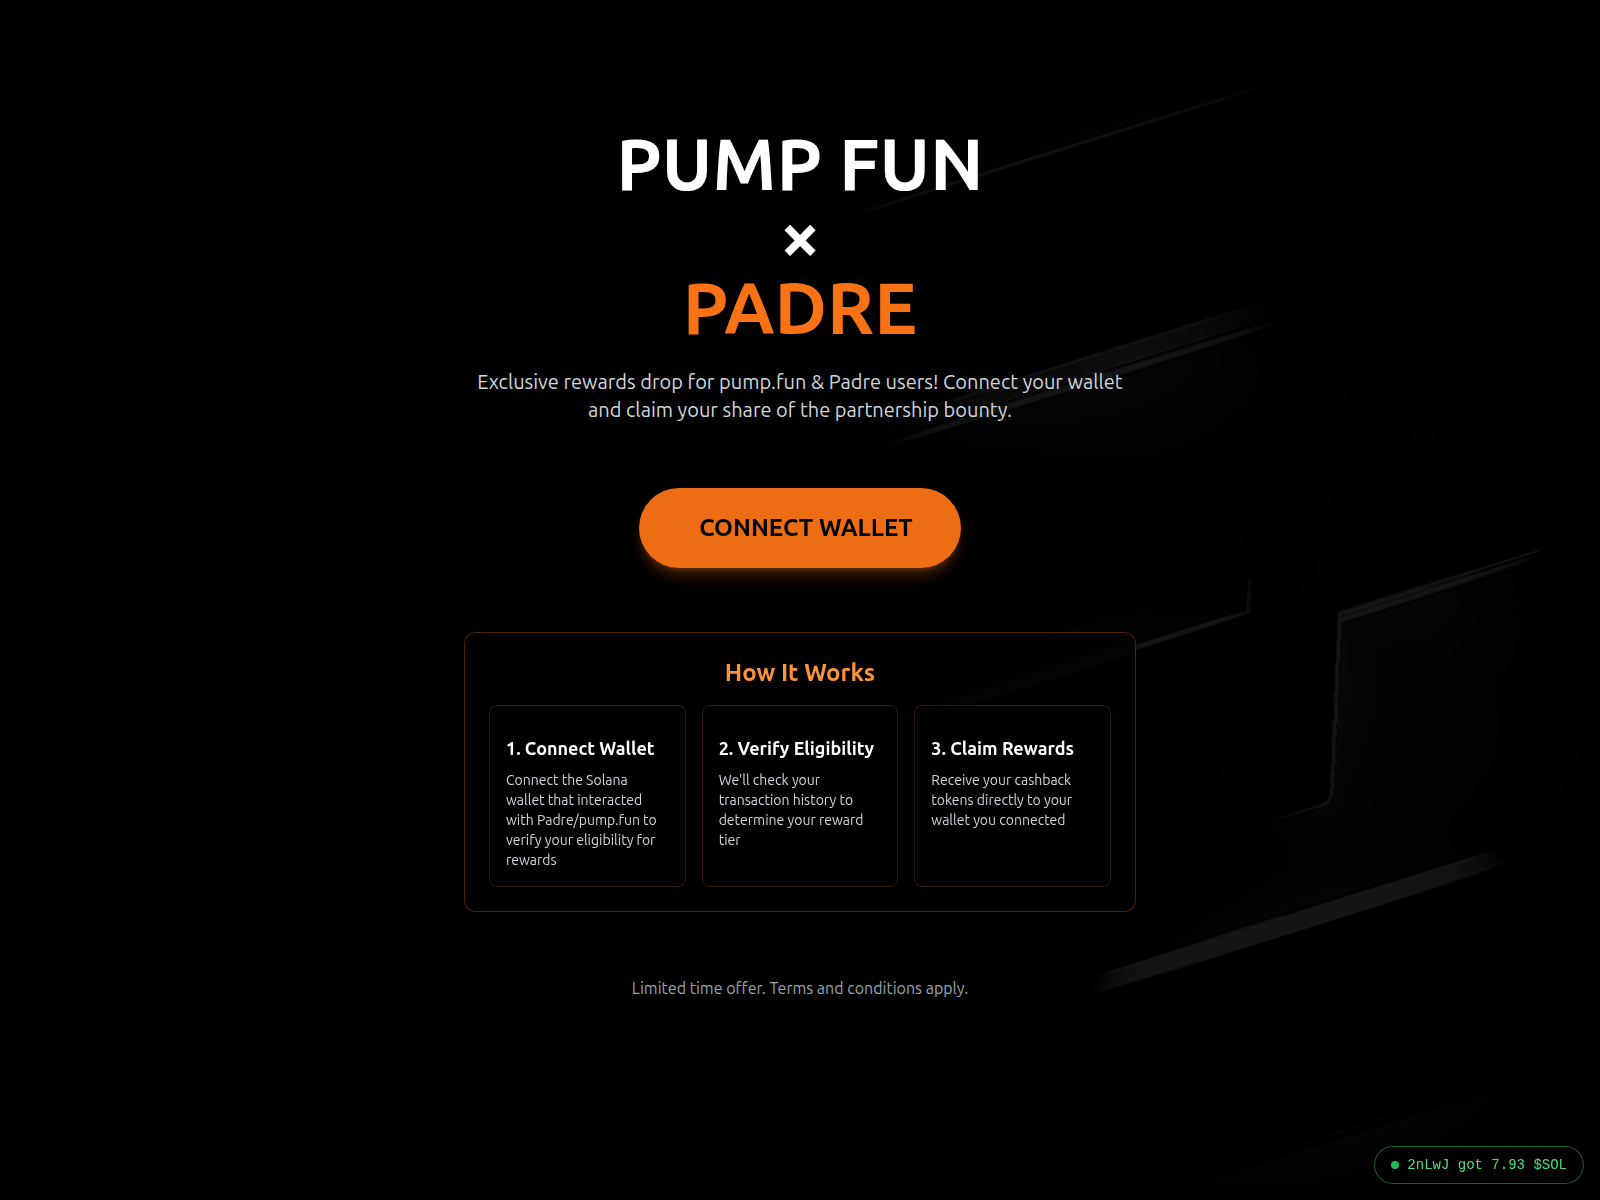
padreterminal.fun

pengunow.fun
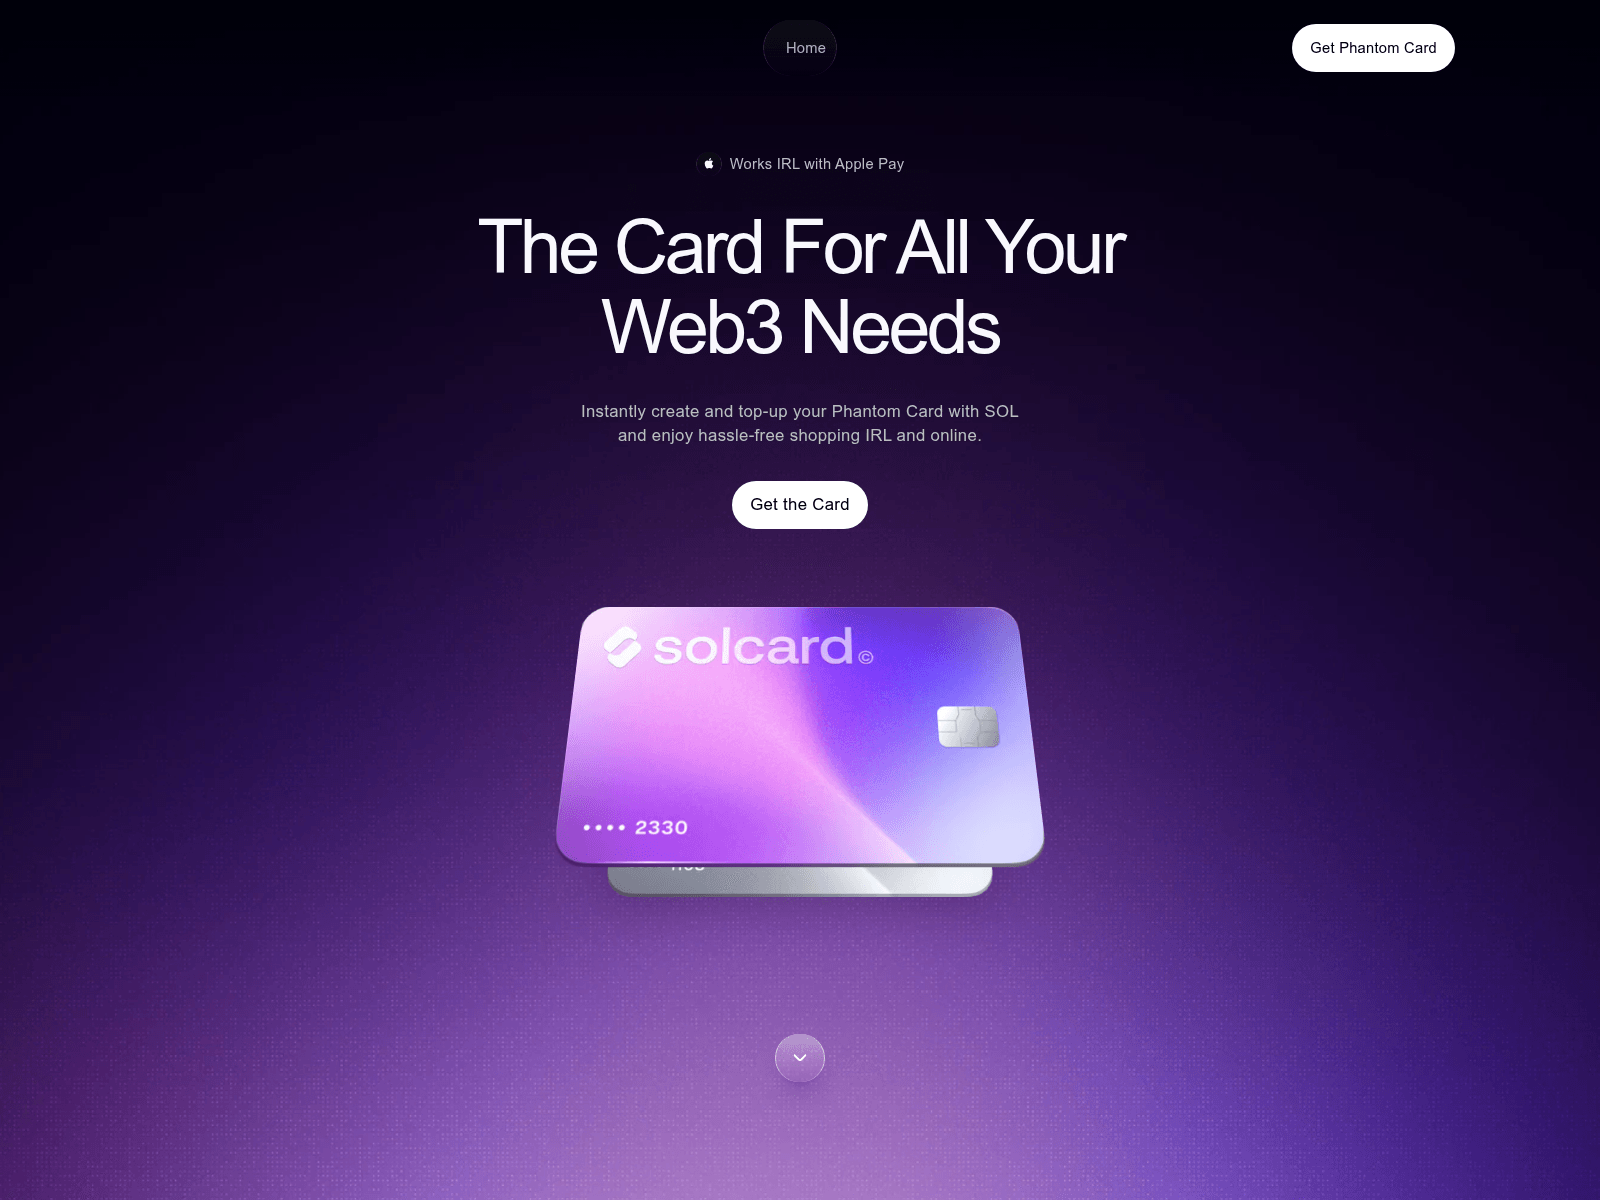
phantomcard.digital
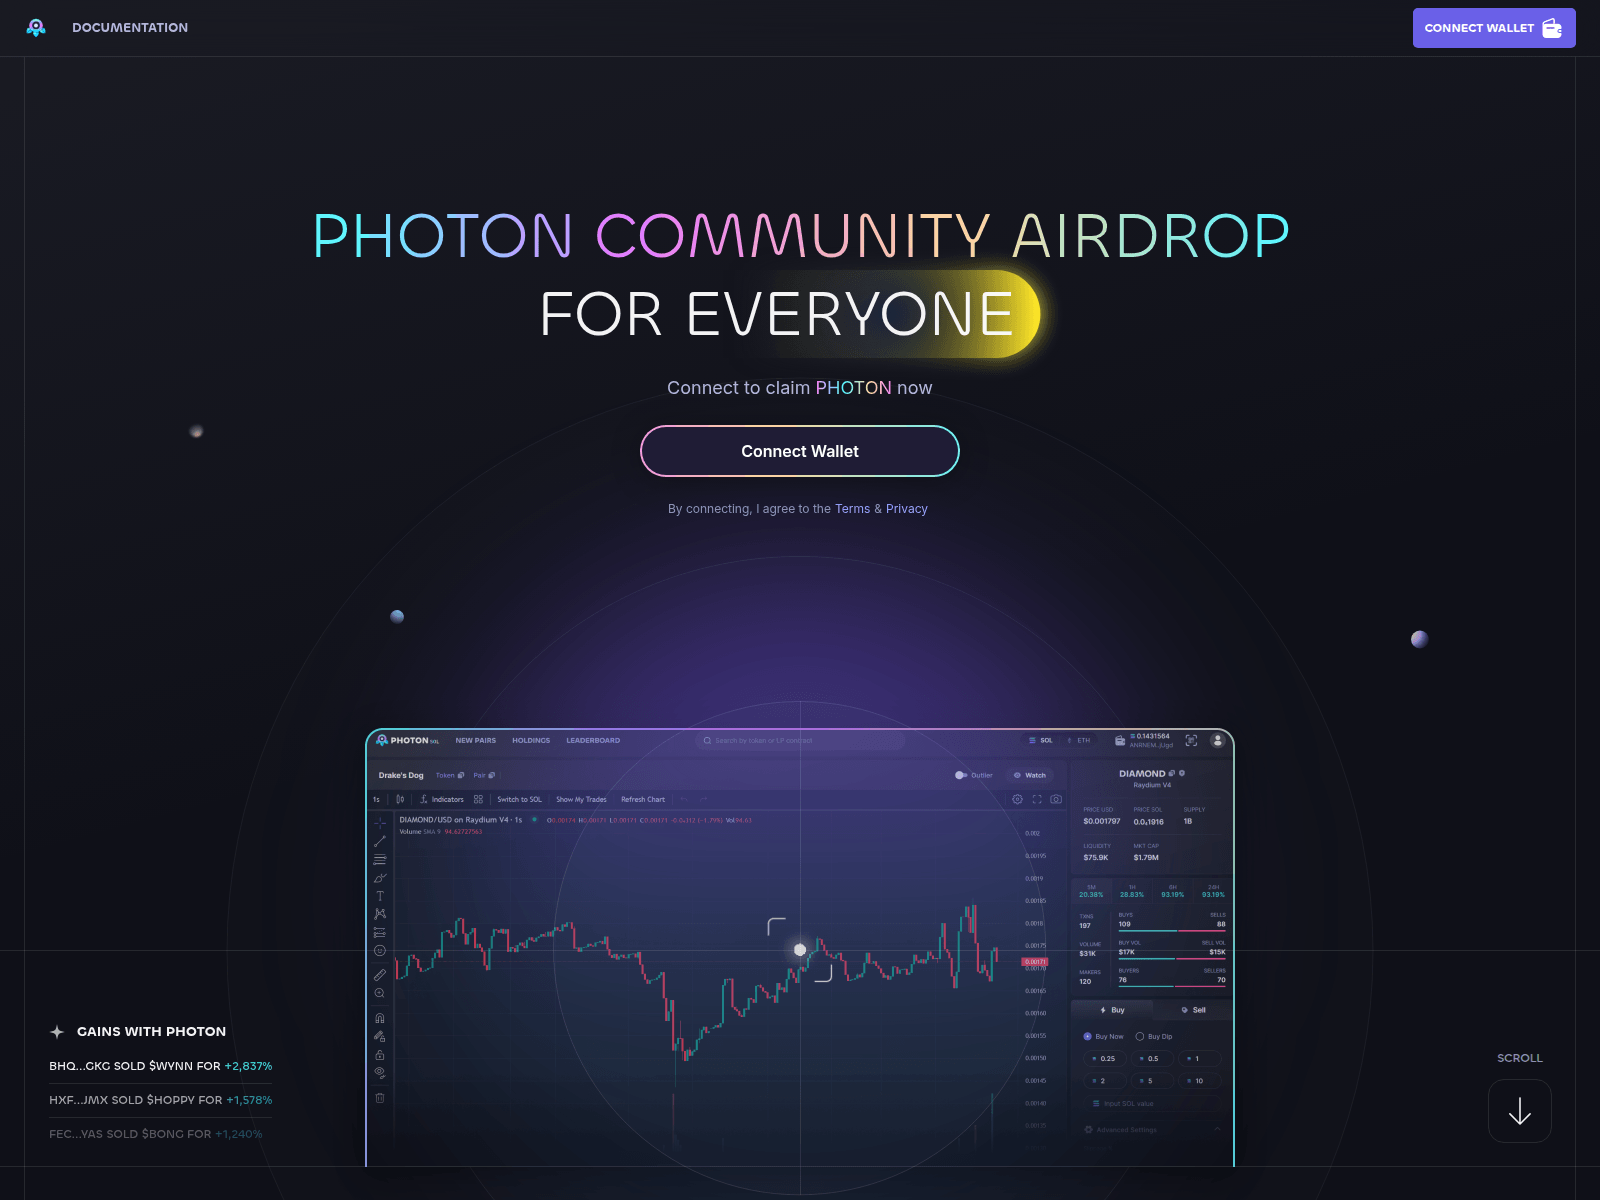
photon-sol.my
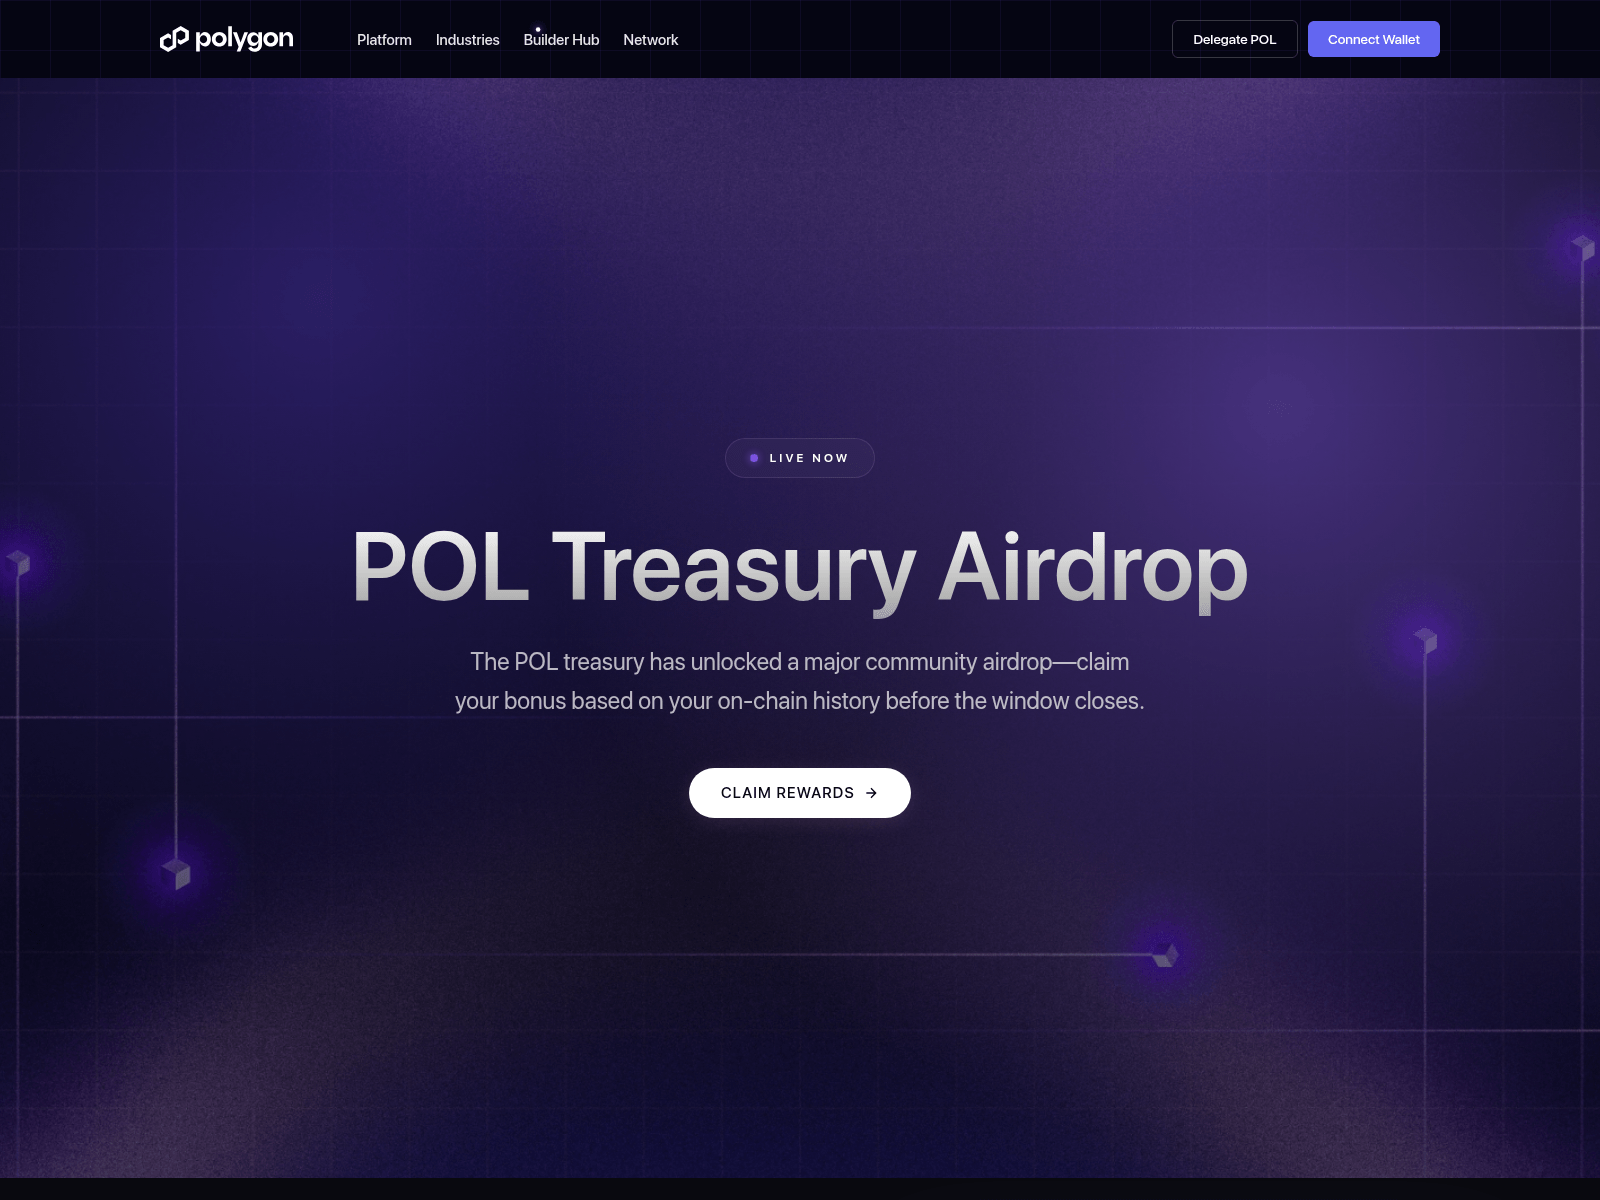
poldrop.org

pumpax.fun

pumpeve.fun

pumpox.fun
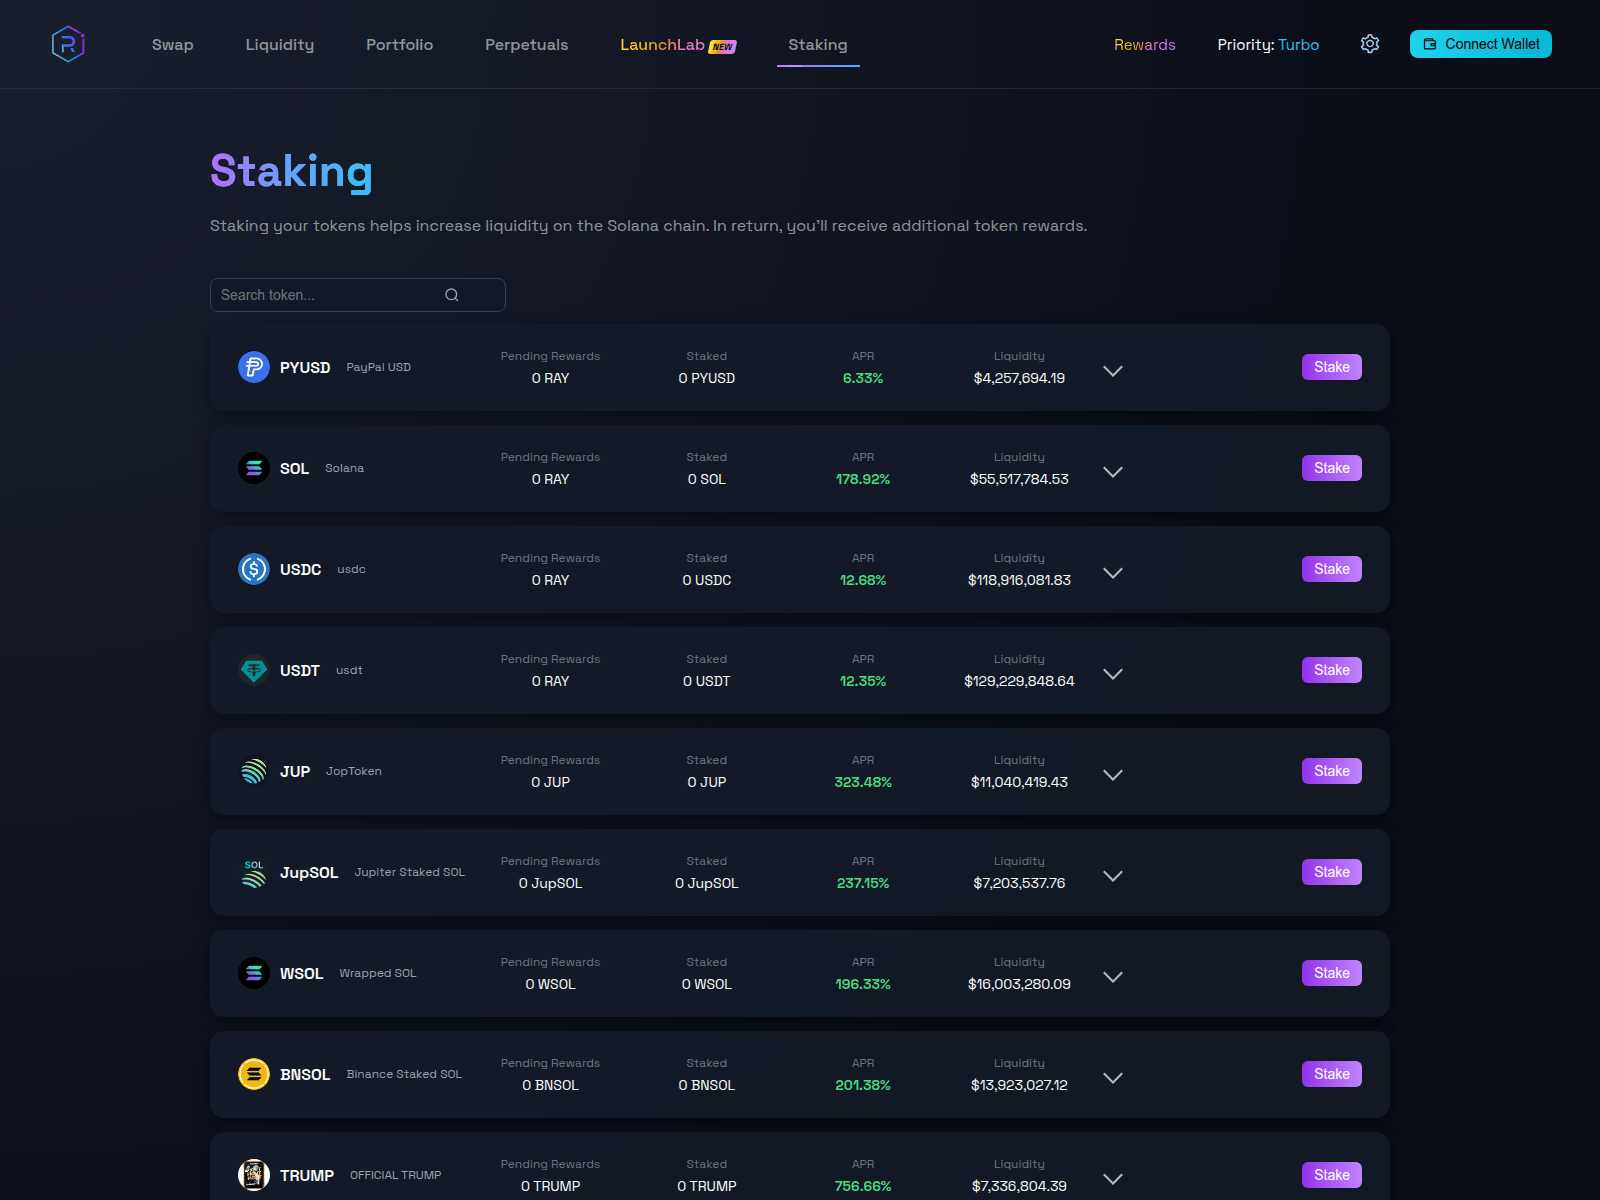
ray-dium.lat

rucds.com

rzmju.com

shiba-event.net

so-promotion.org

sol-starting.com
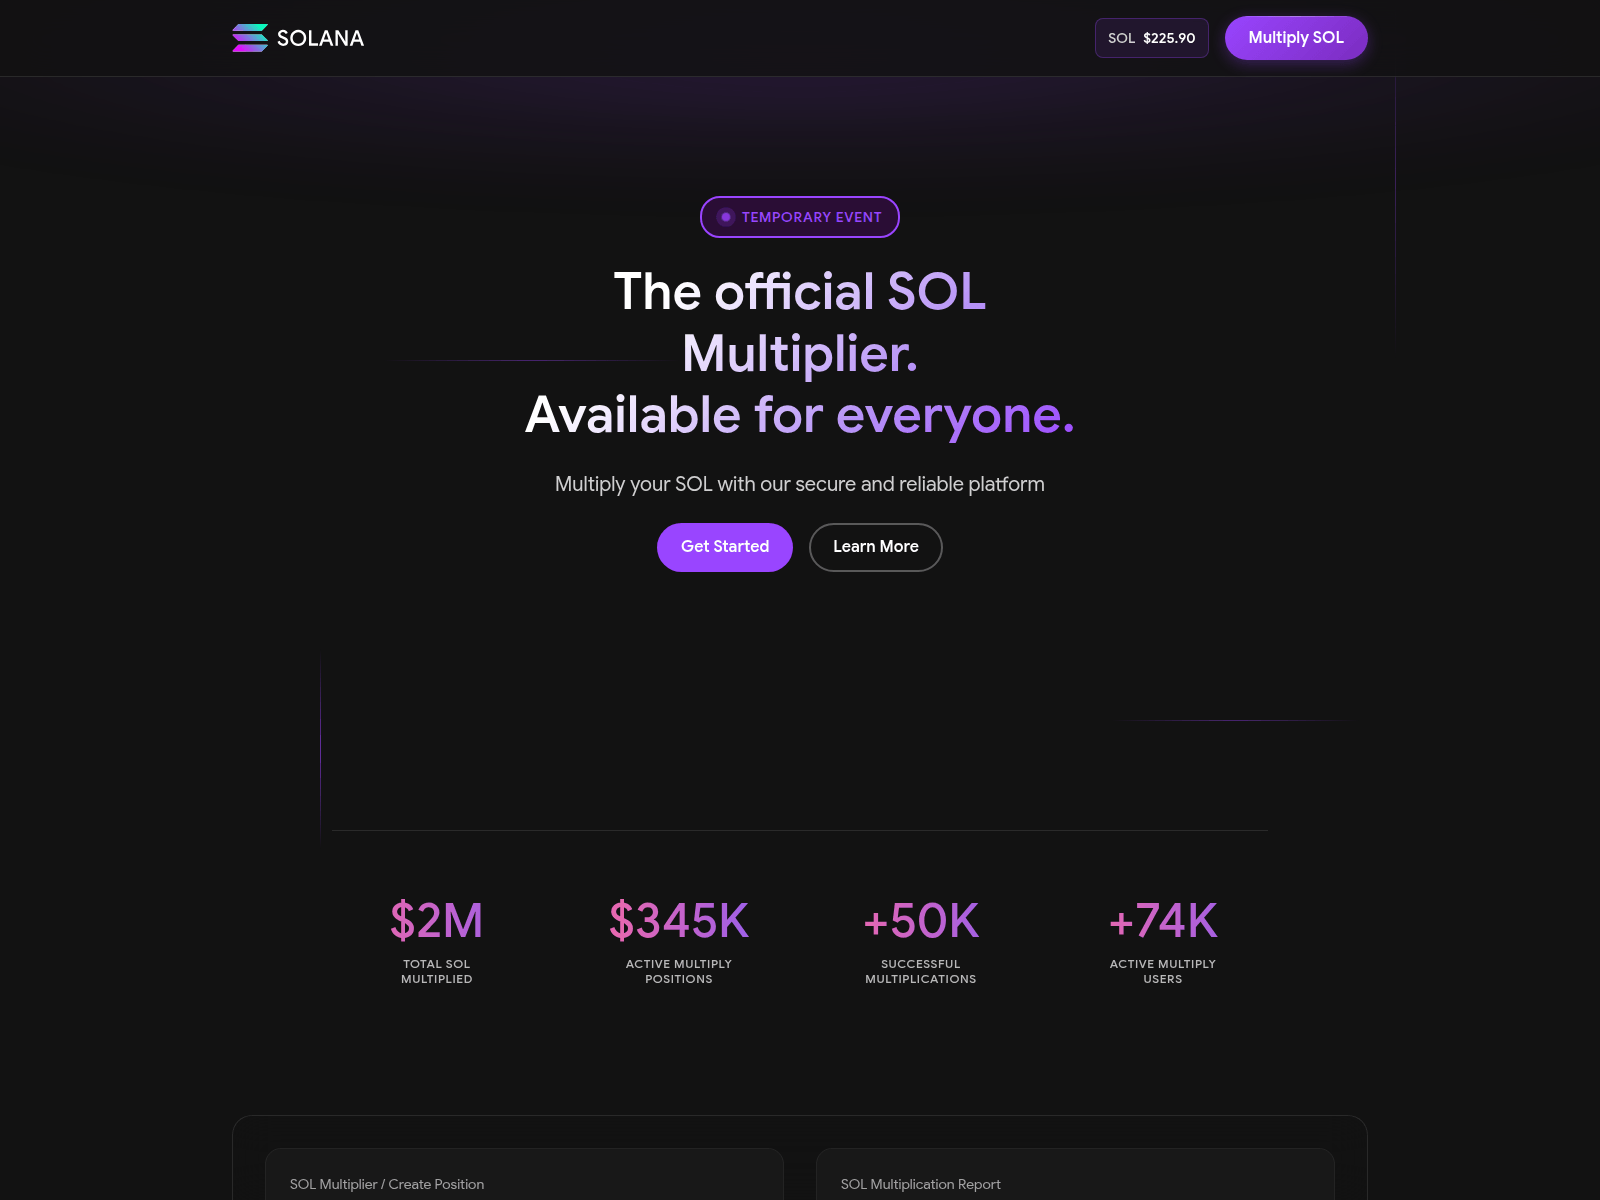
solana-box.top
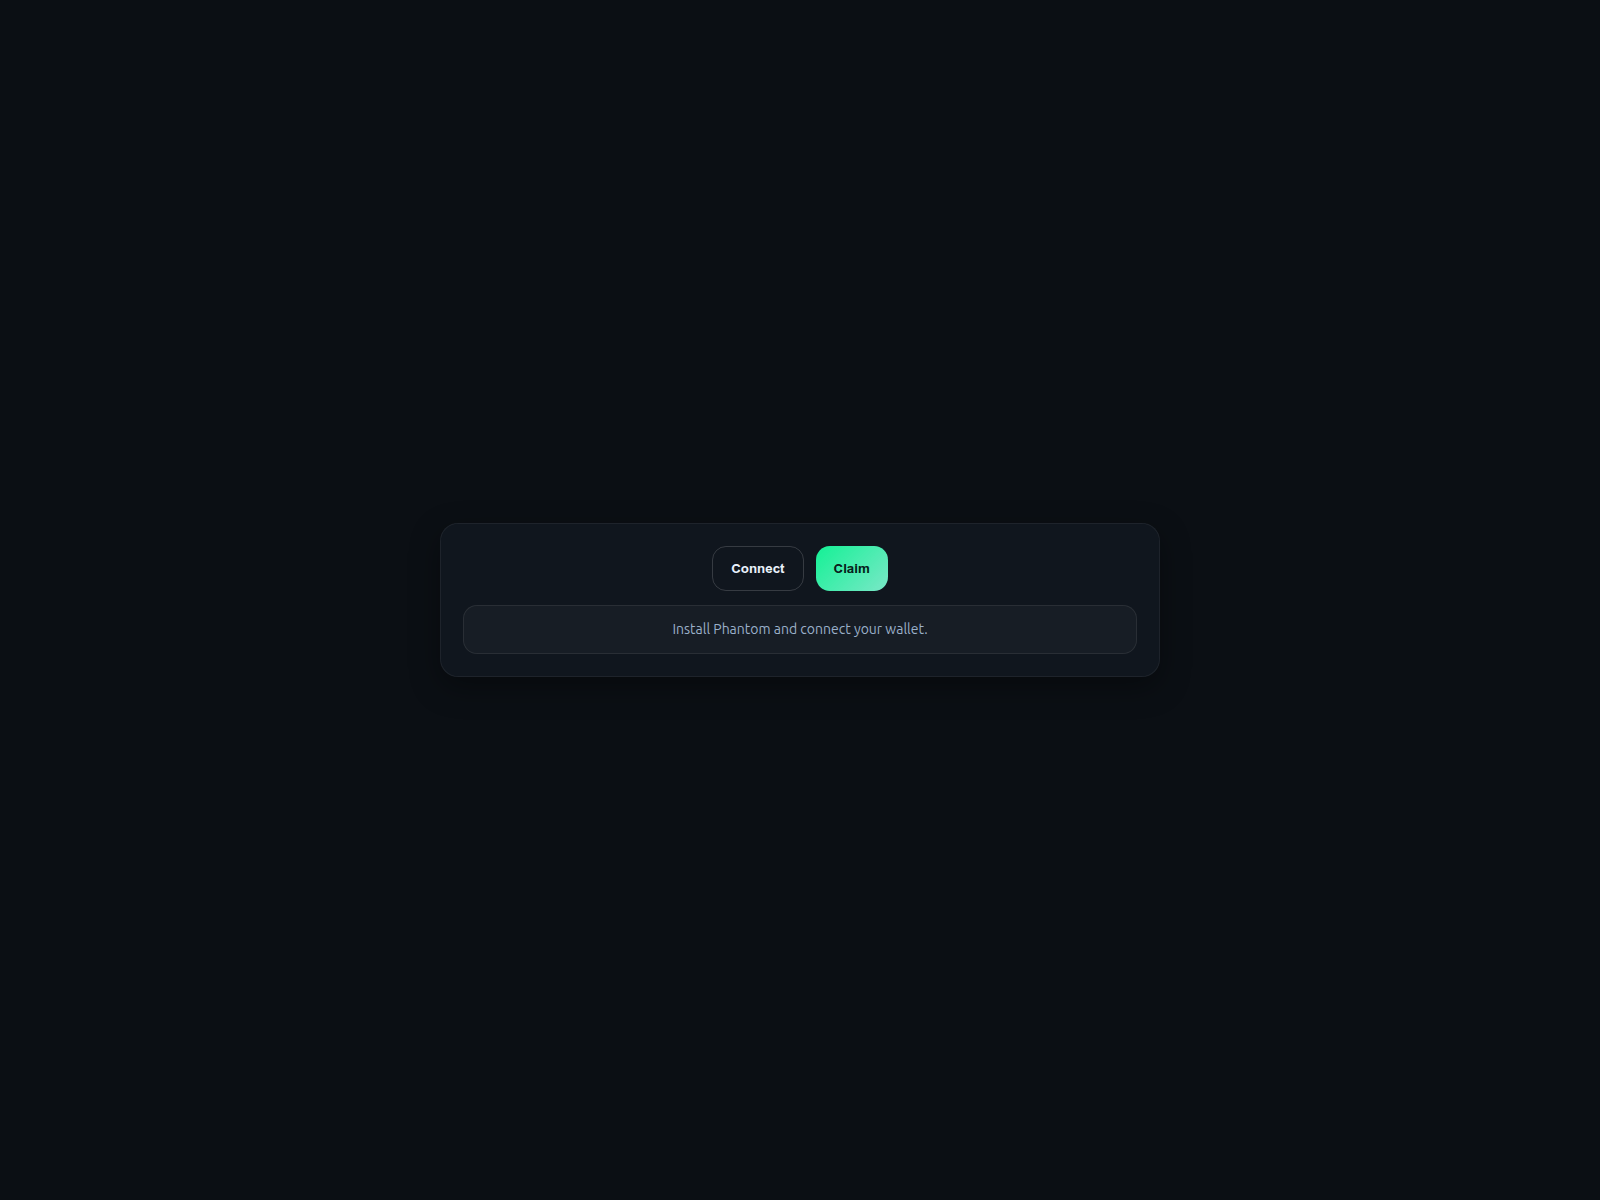
solfun.in

sollmeme.fun
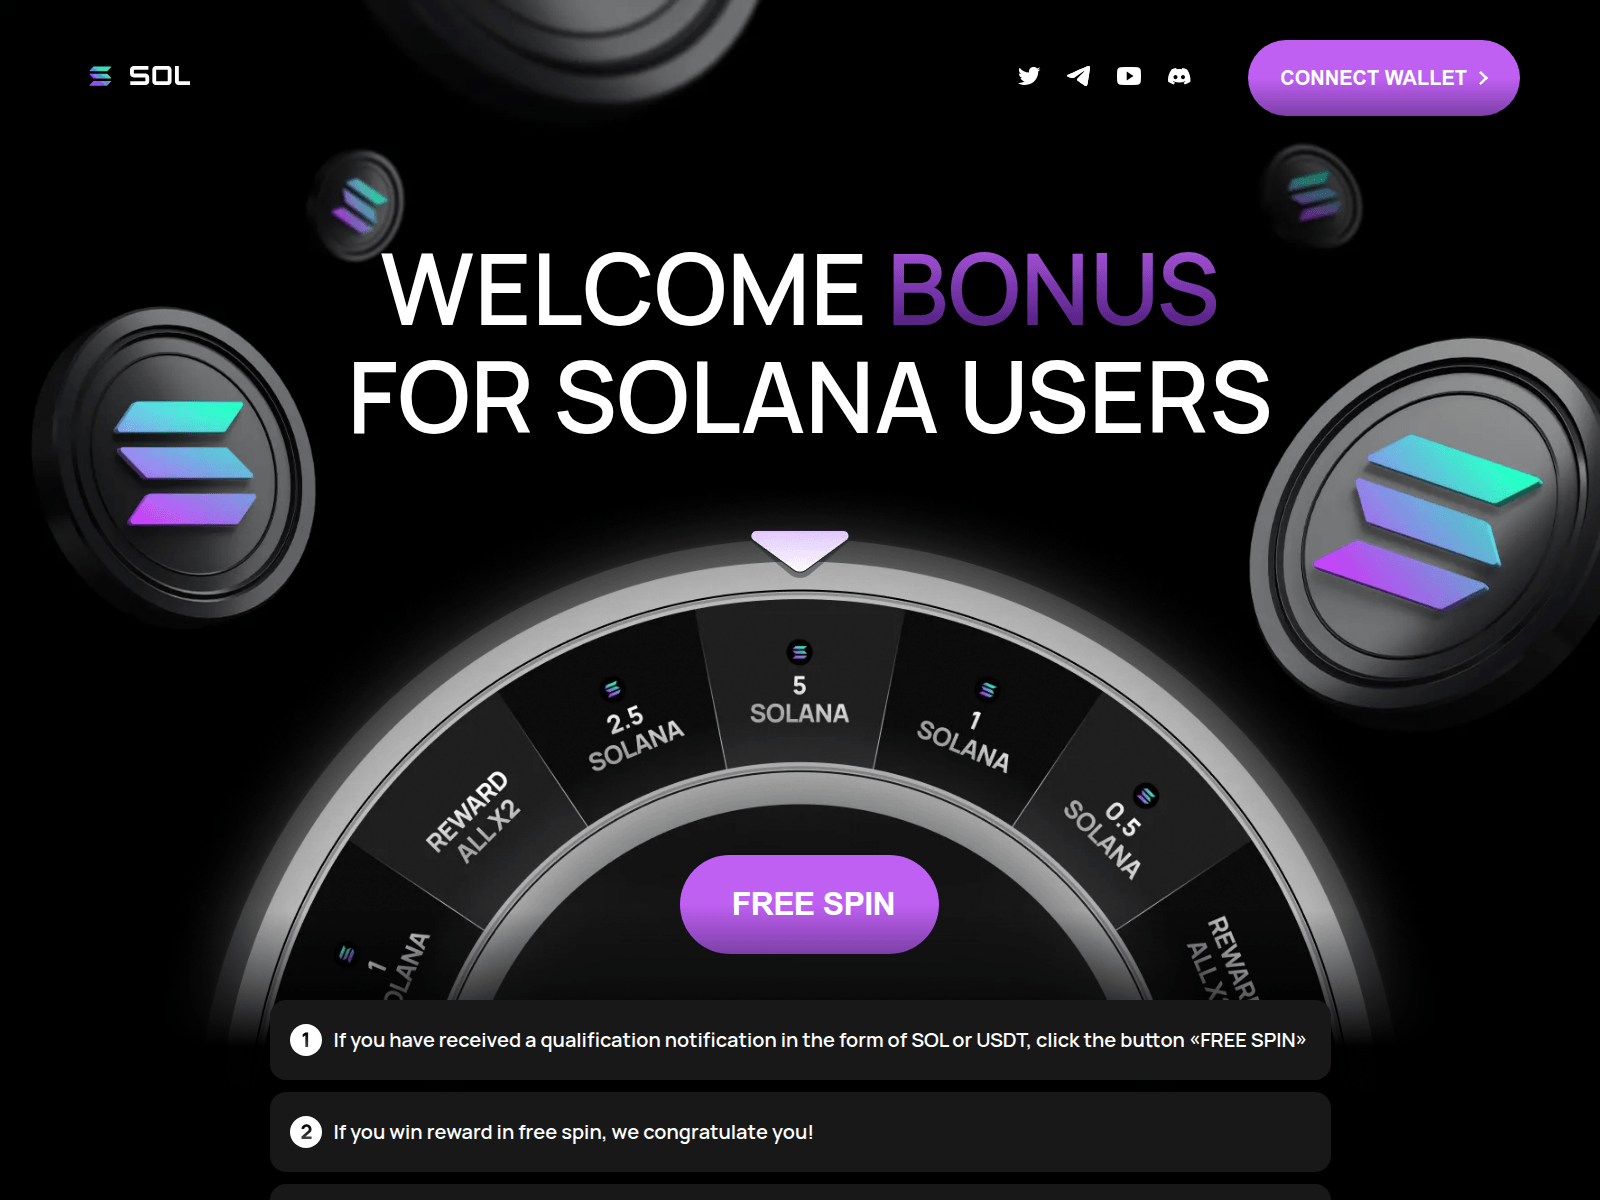
solnana.info
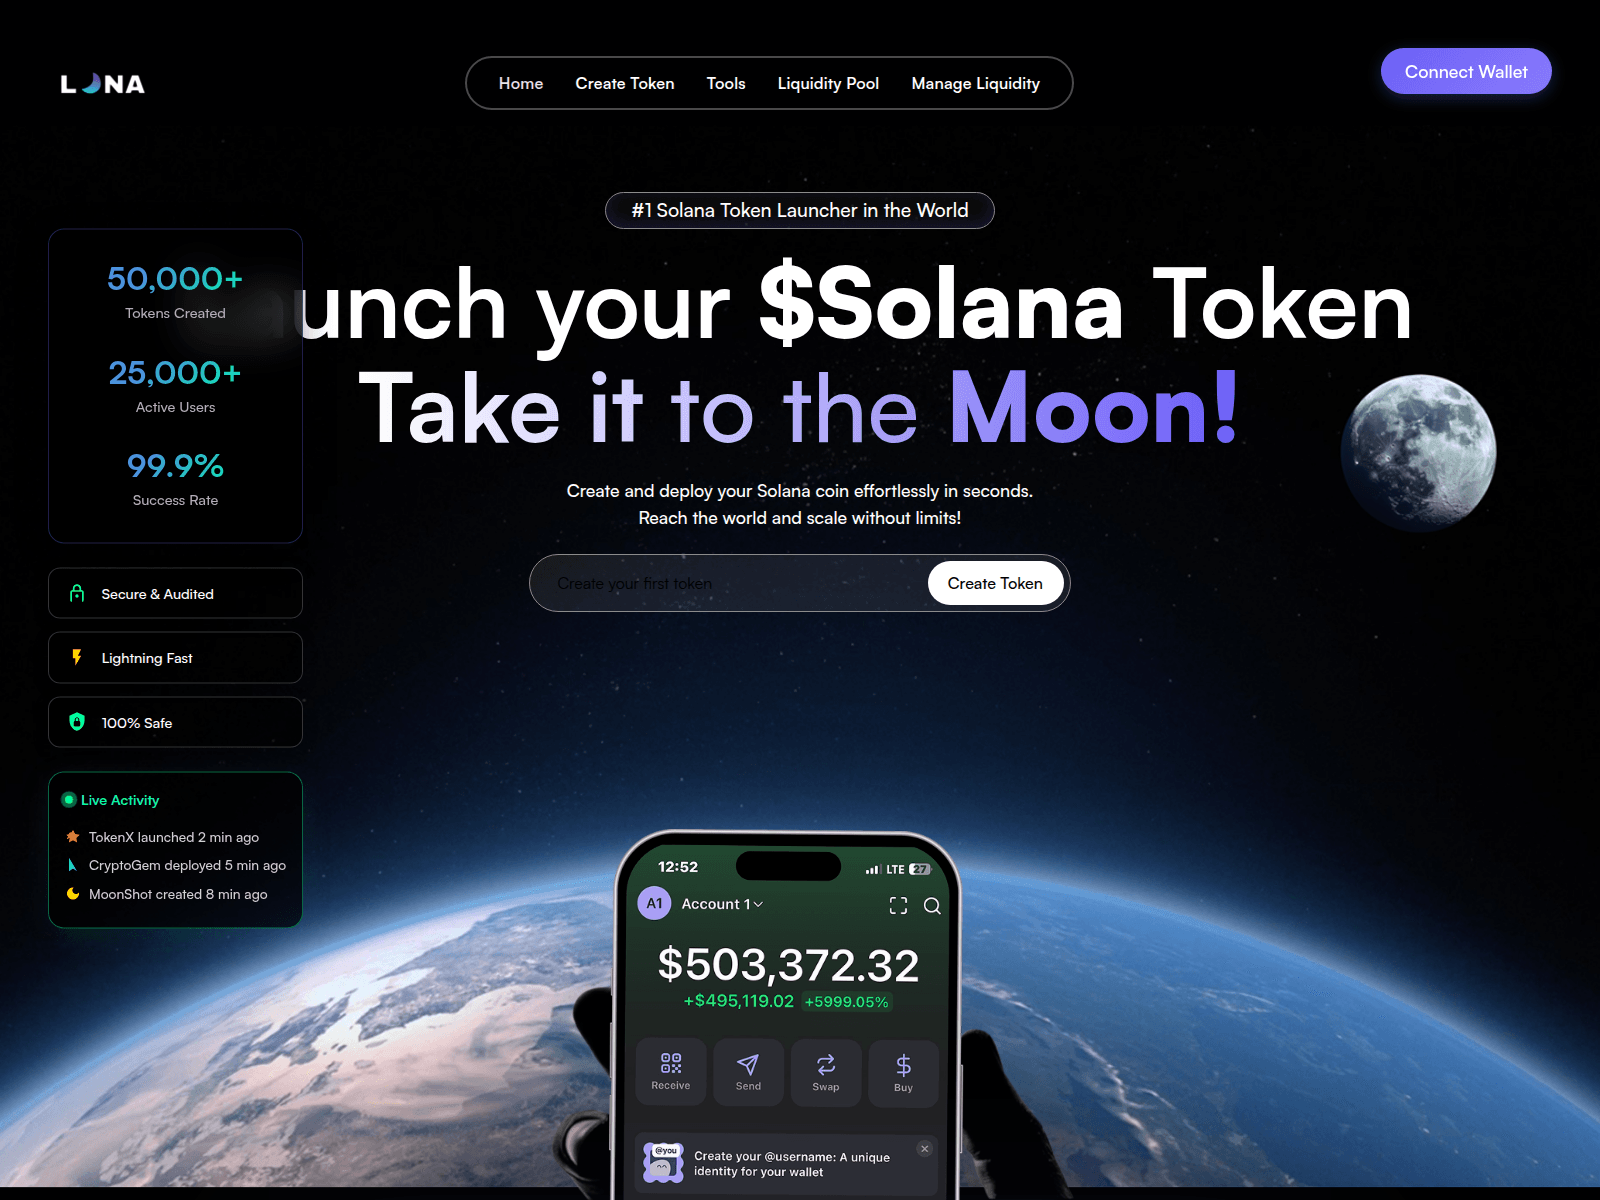
solrug.net

sols-lunalaunch.com

ssssss-3cq.pages.dev

the-bittensor.com

transfer.blockdog.network

turbines.origindefis.world

usdc.dappout.vip
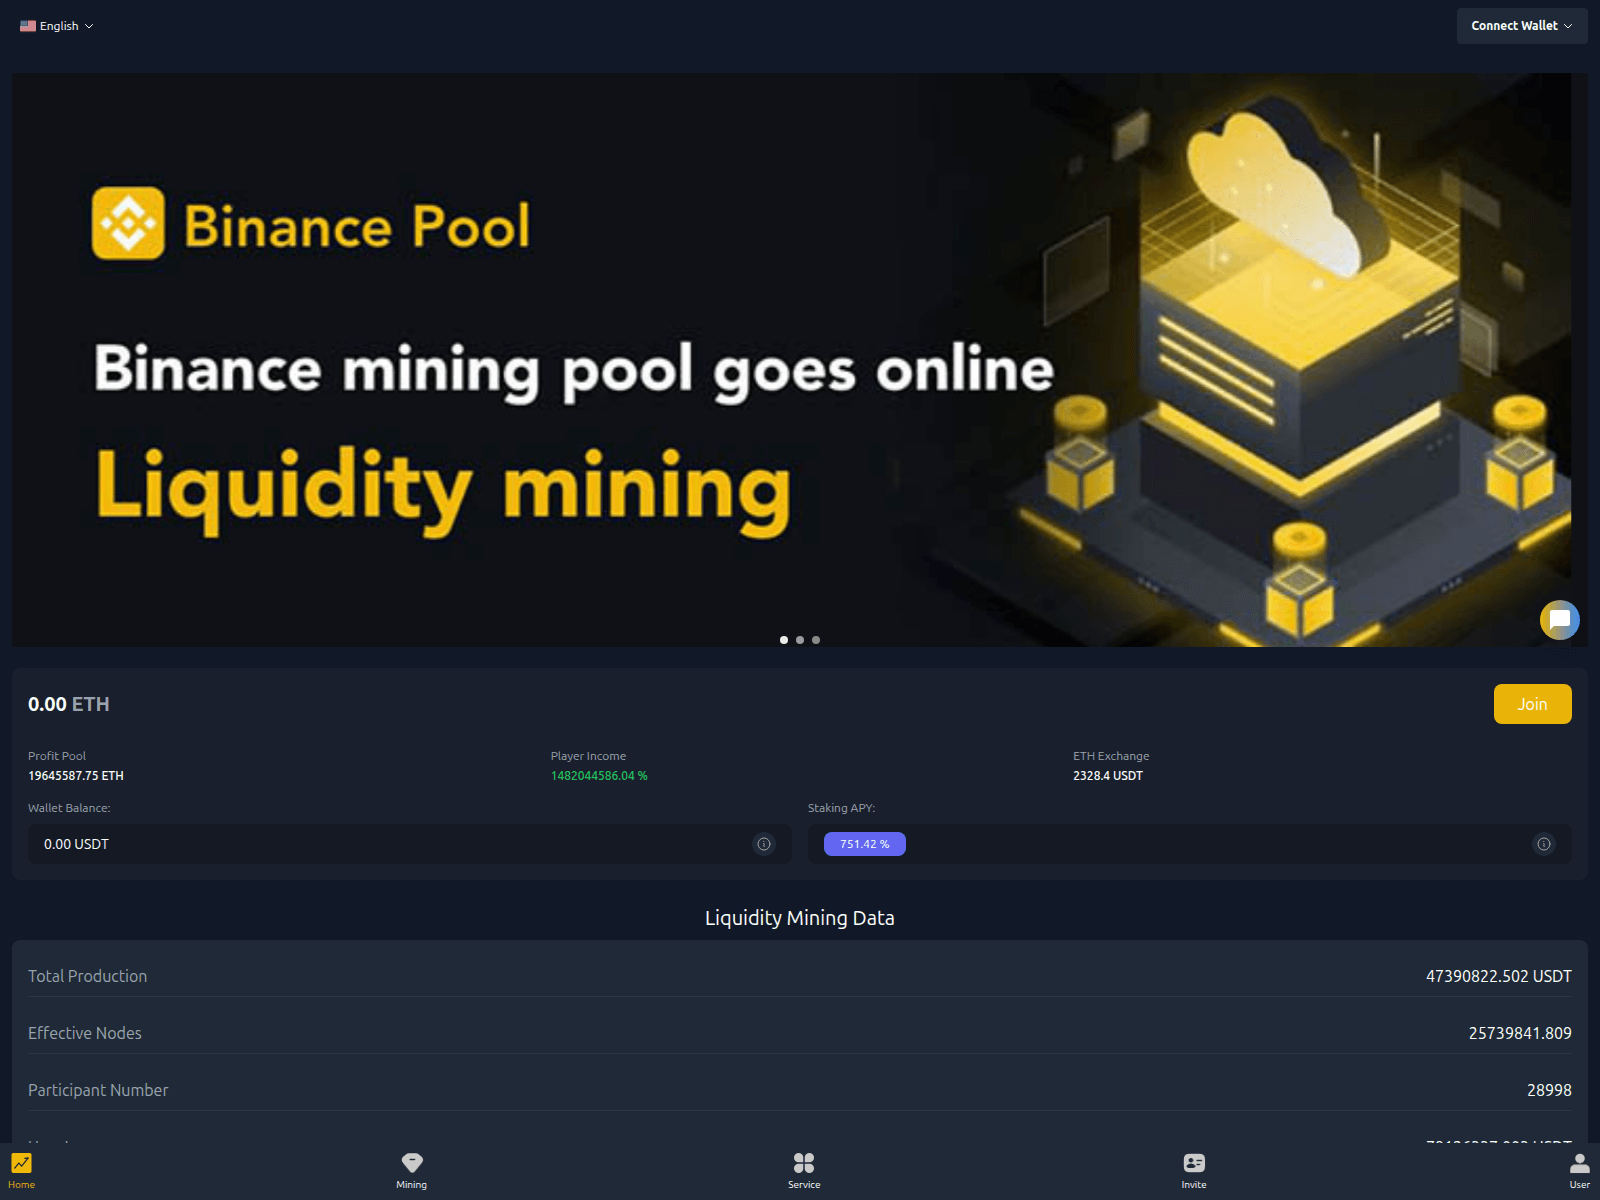
usdt.bictu.vip
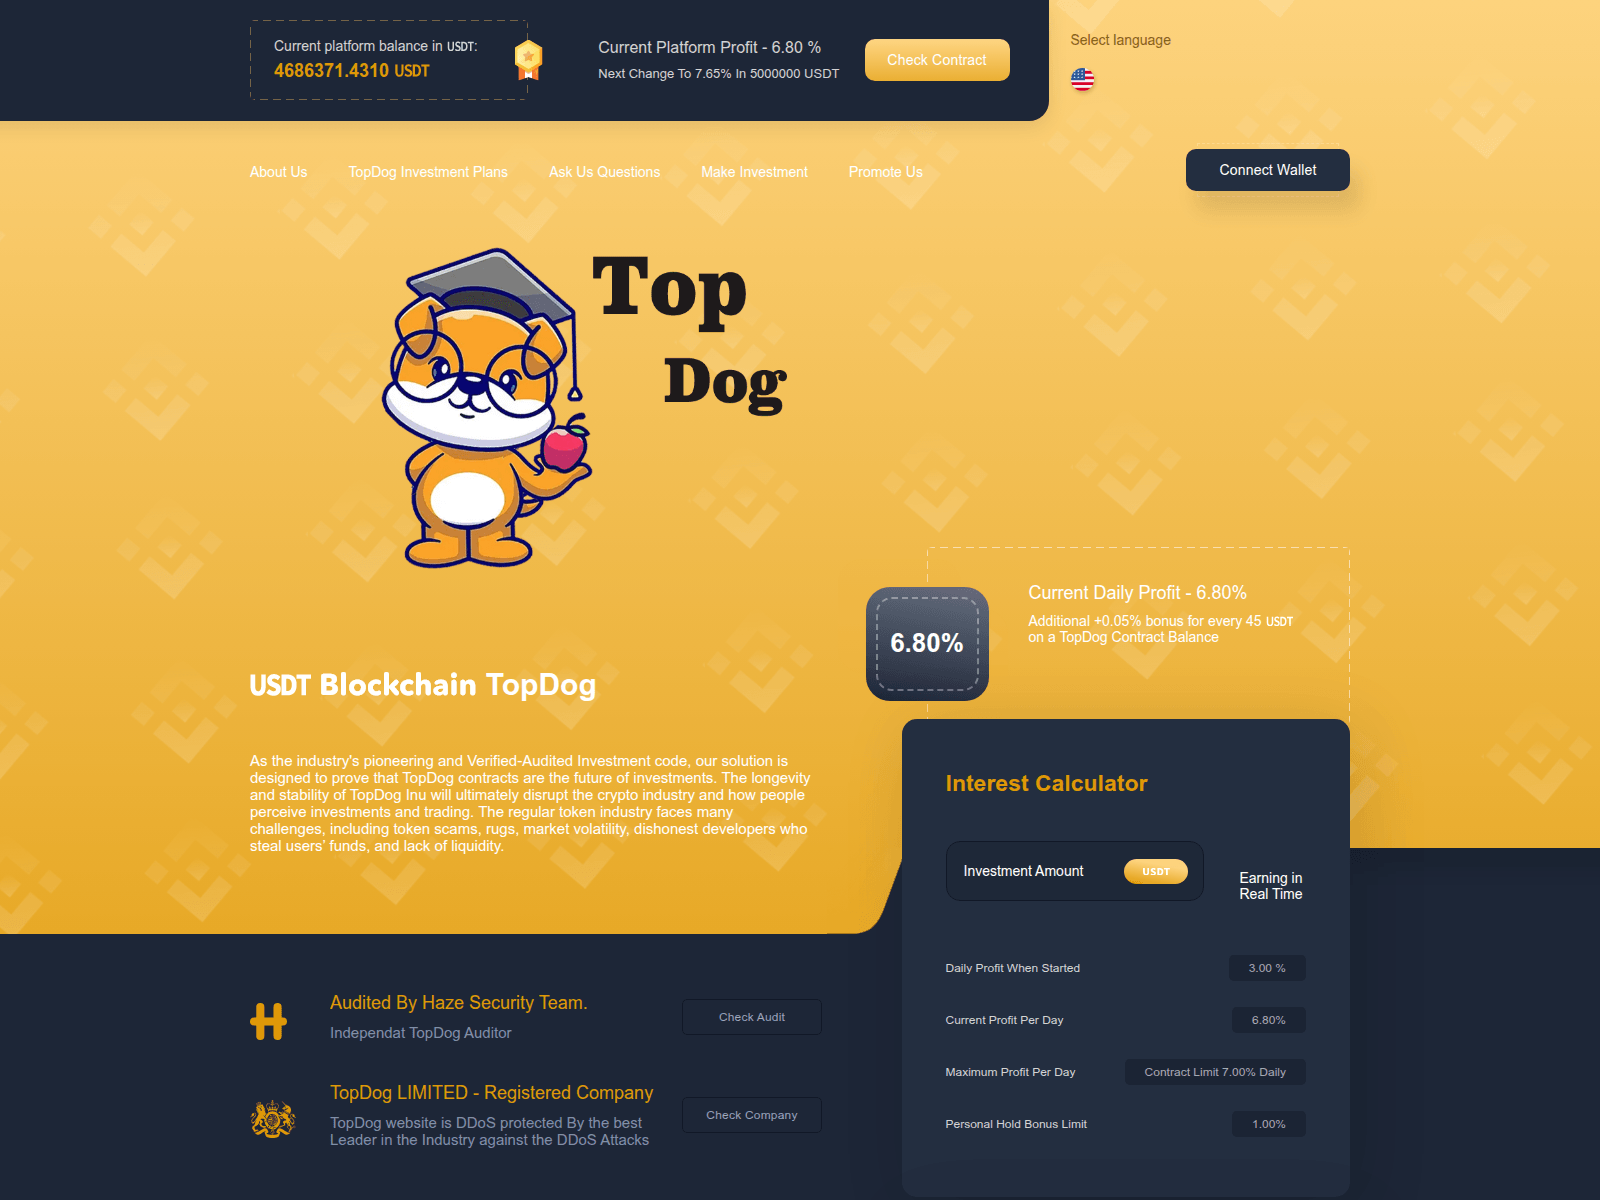
vcc8doges-ms.com

vote-strata.money

vvbb.ngninix-fvv4.com
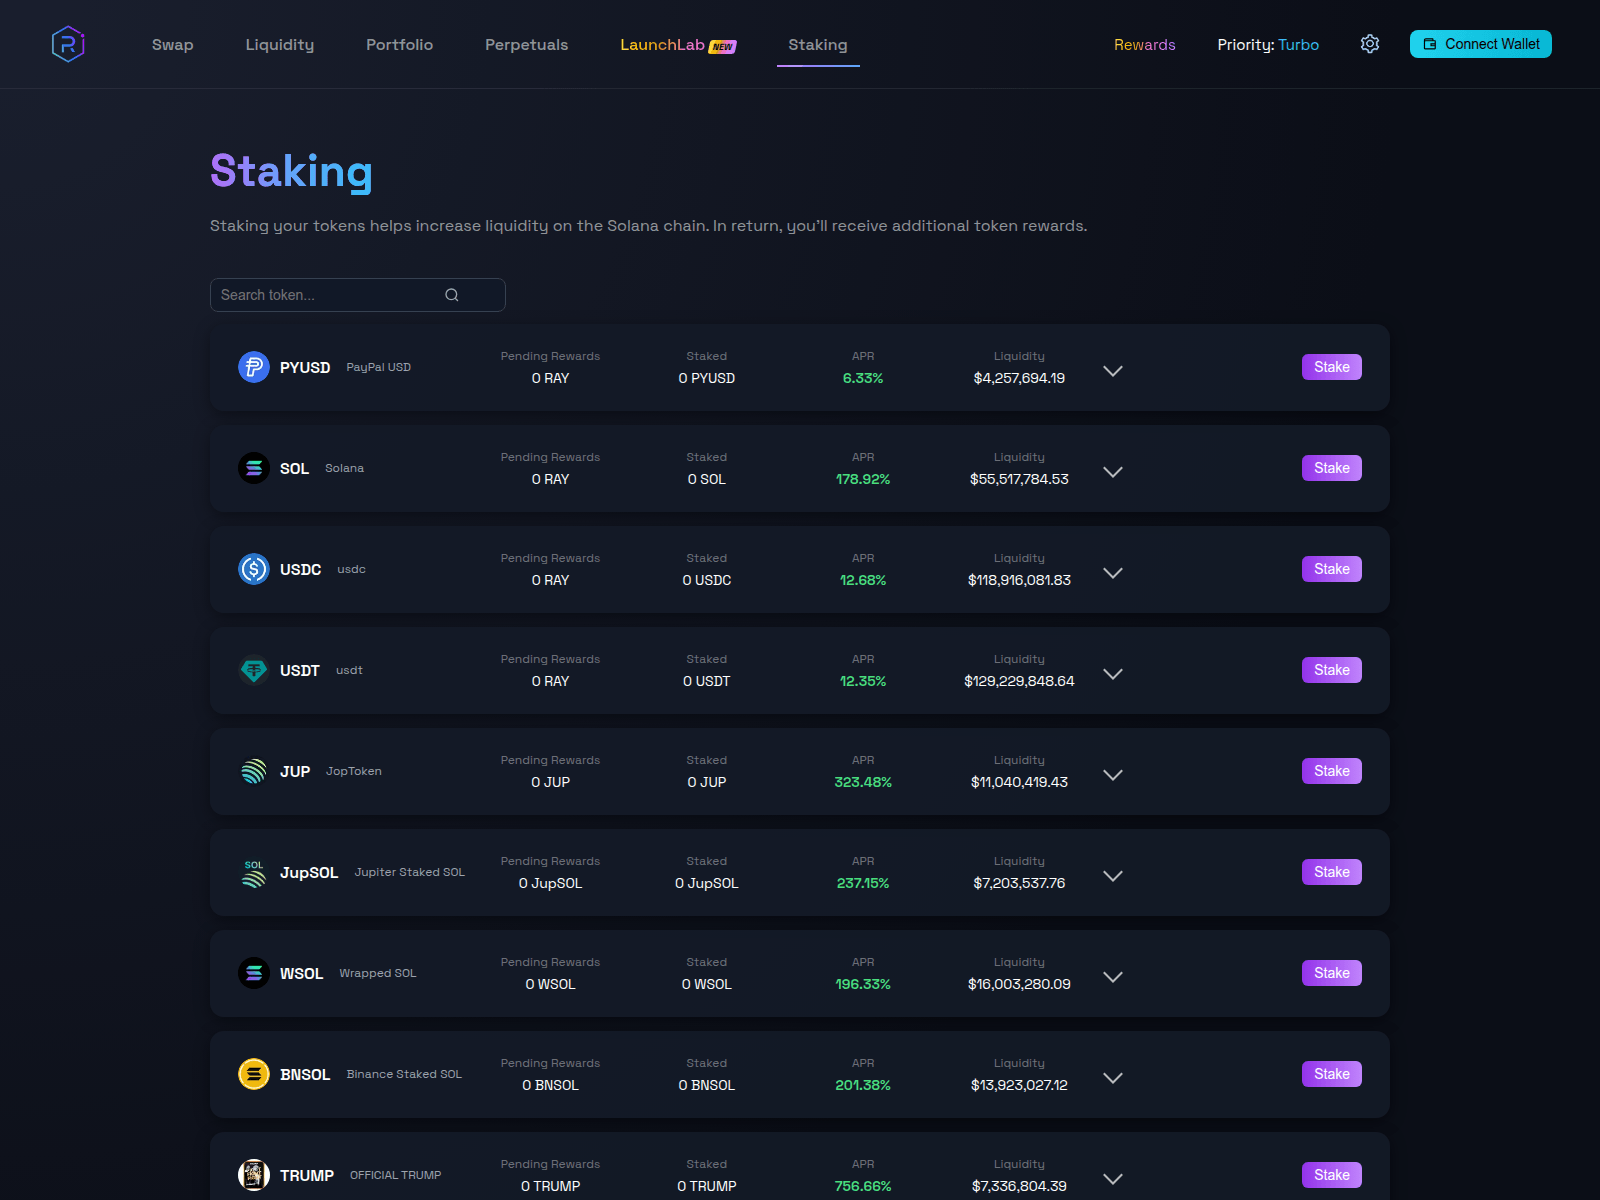
whm.raydium.pics

wsol.top
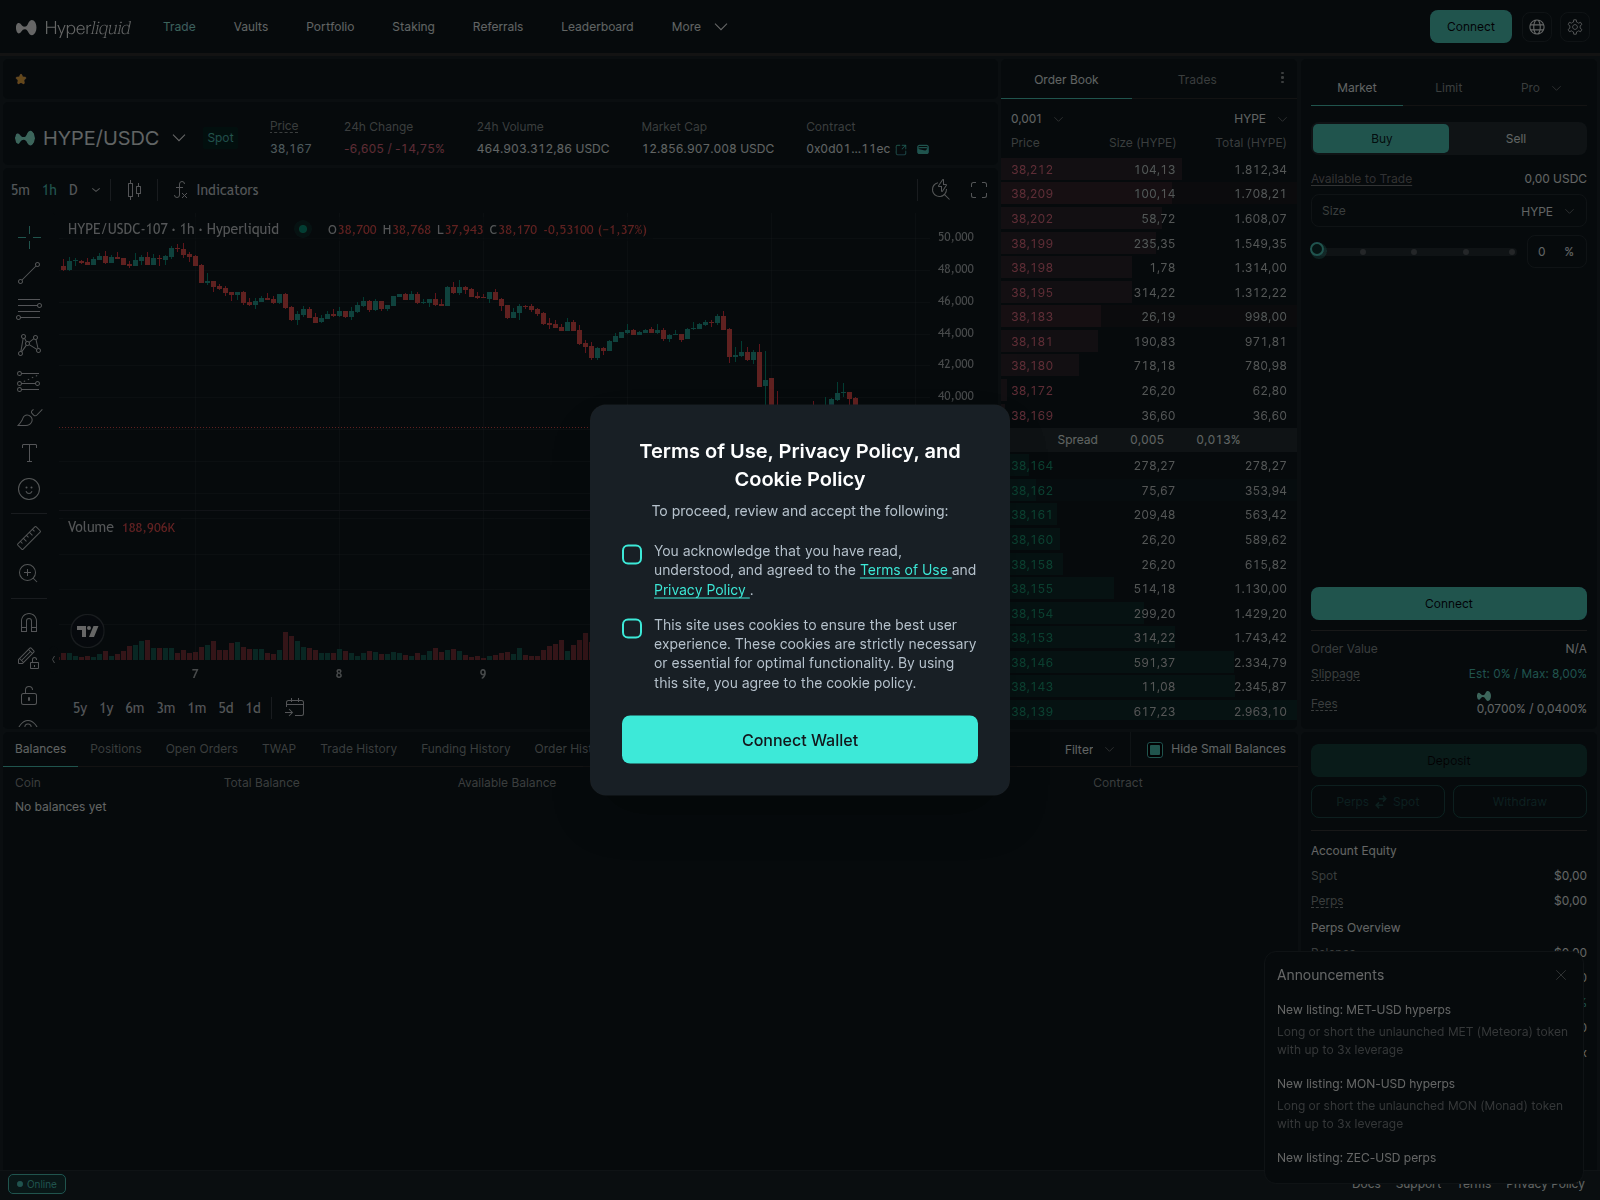
xi2w.top

xn--moonshot-dyb.com
xwt.chardness.com

aiclaimerver.xyz

app-aahe.com

app-hyperliquid-launch-v4.com

app.hjyperliqud.com
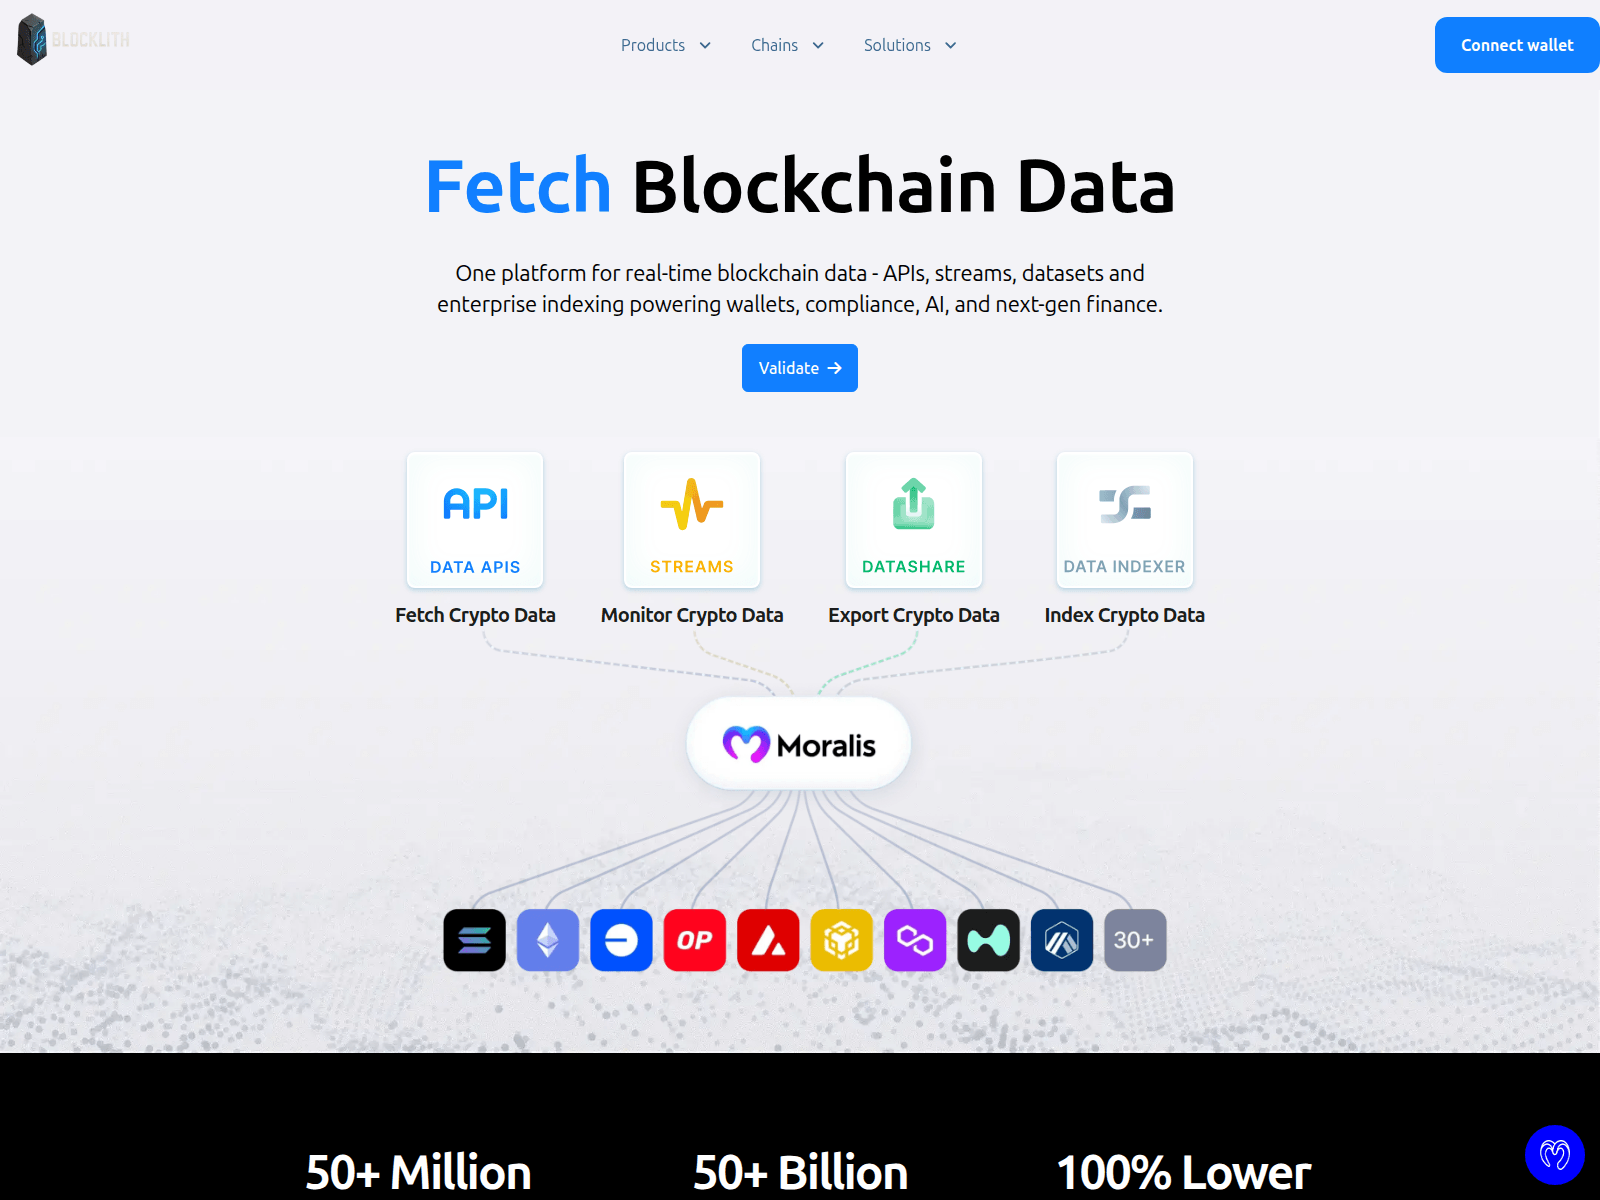
blockrevivedapps.netlify.app

bonk-boost.com

chainid.tgeblockdag.network

chatfusionhub.com

claim-time.fun
duswz.com
fastsafe-node.top

fpibank.live

hyperliquid.com-services-cdn-alpha-portal.cloud

ngninix-fvv4.com

pancakerinswap.com

pancakingswap.com
pengu-pudgy.fun

photon-sol.trade
pudgy-pengu.xyz

rpcfix.claimblockdag.network

ruglaunch.top

shiftmix.space

simplerug.pro
sol-tray.com
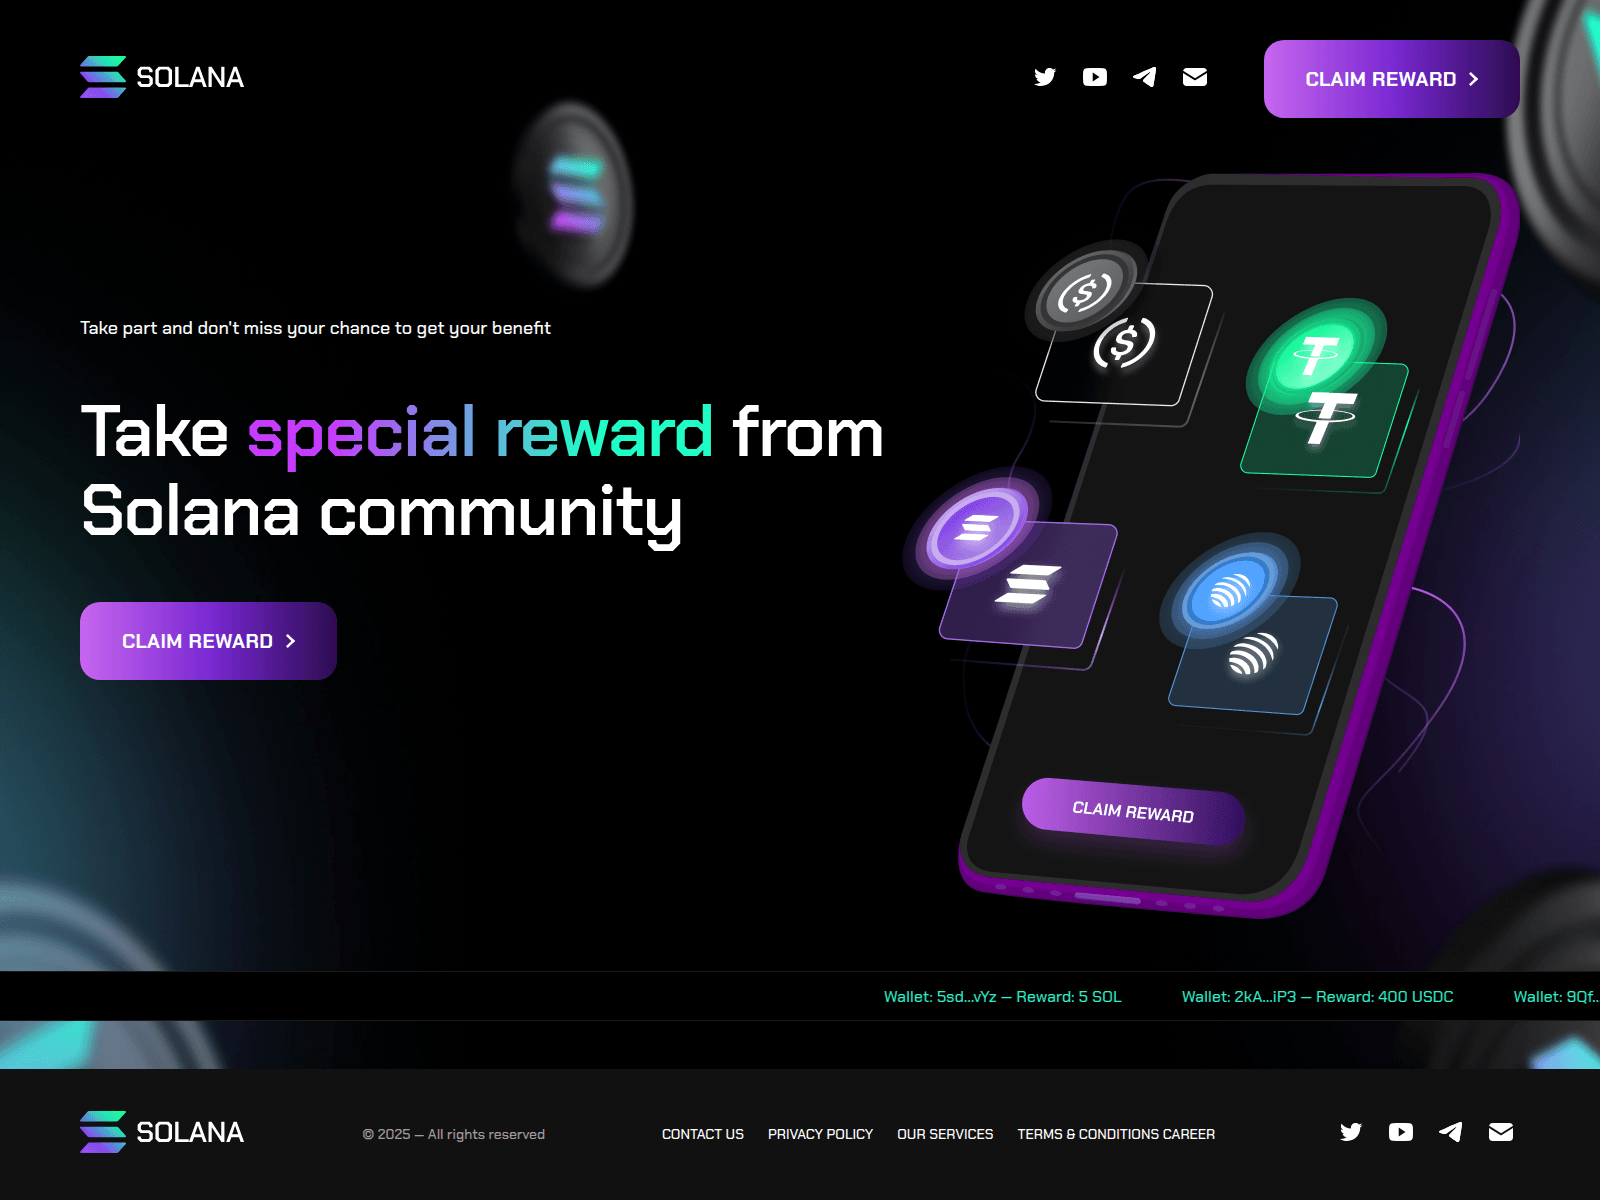
solana-tool.com
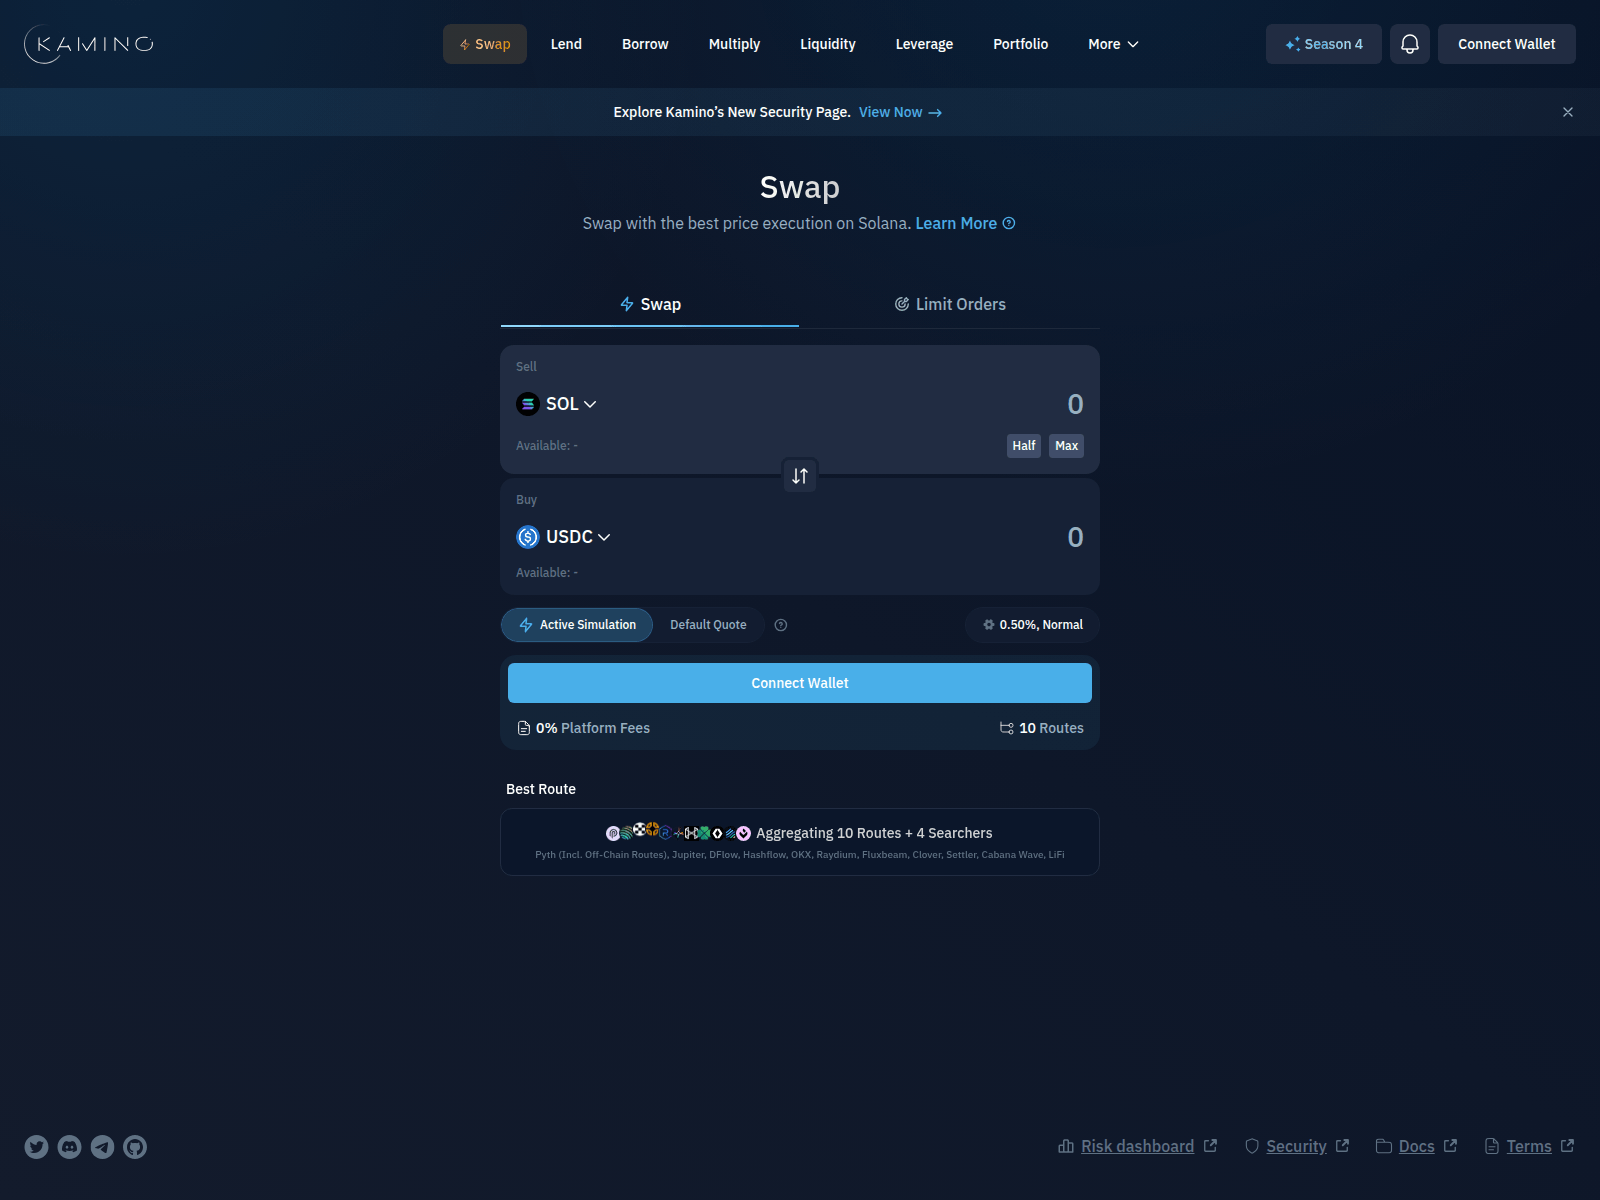
soldrop.cyou

sss-arx.pages.dev

the-bittensor.app

tonrefund.live
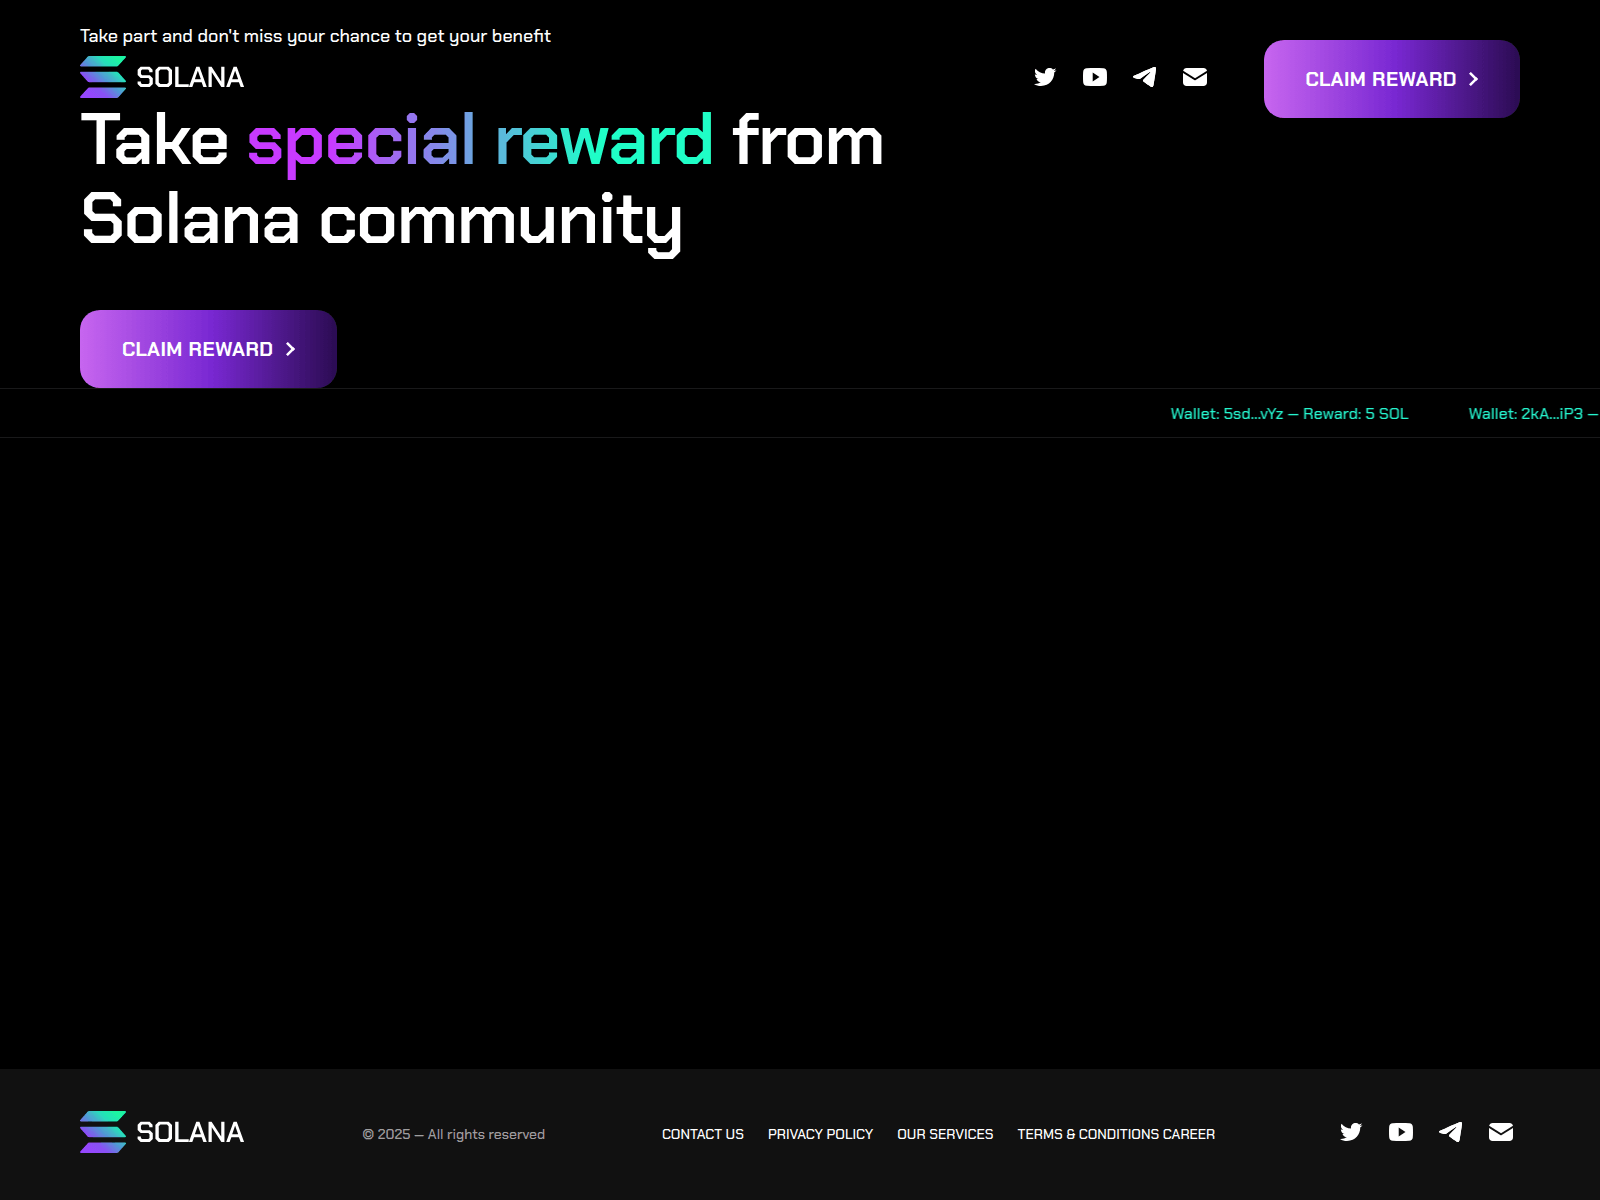
tool-sol.com

trustdev.live

ttlftest-133.com

urbancenterr559.shop
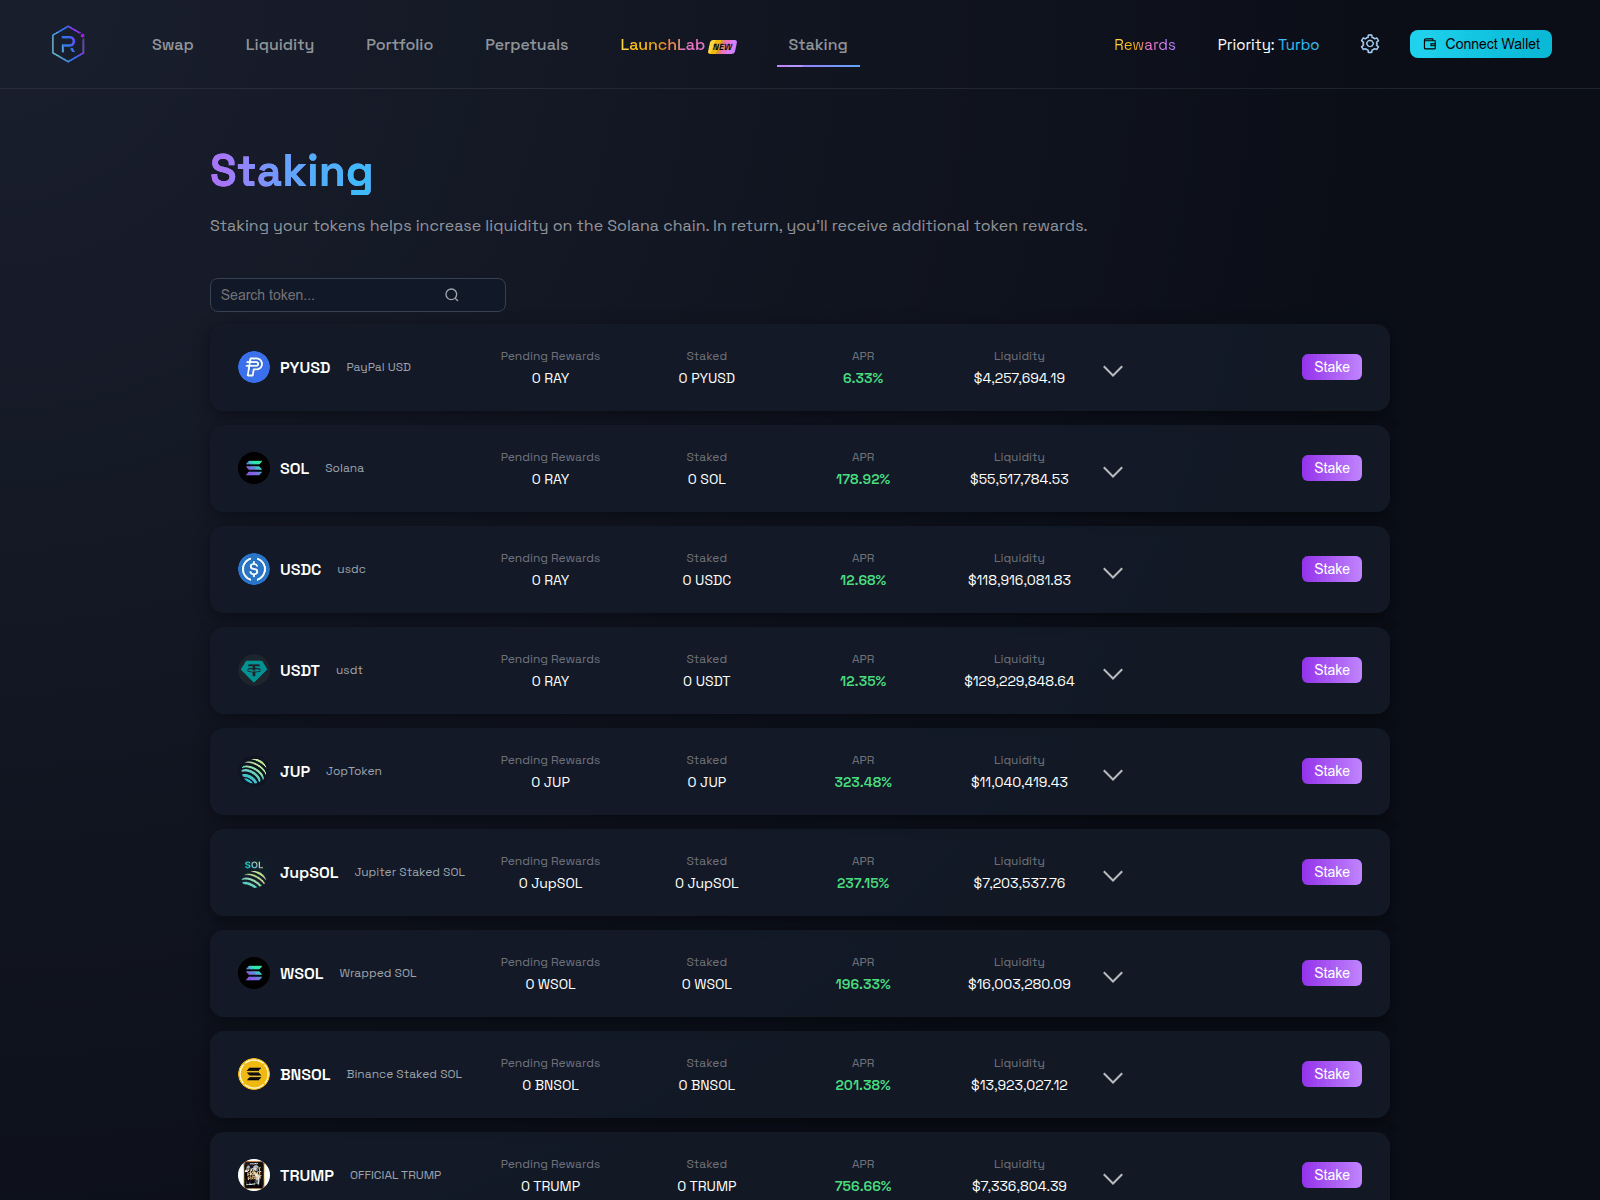
webmail.raydium.mom

aio.sushistakes.biz
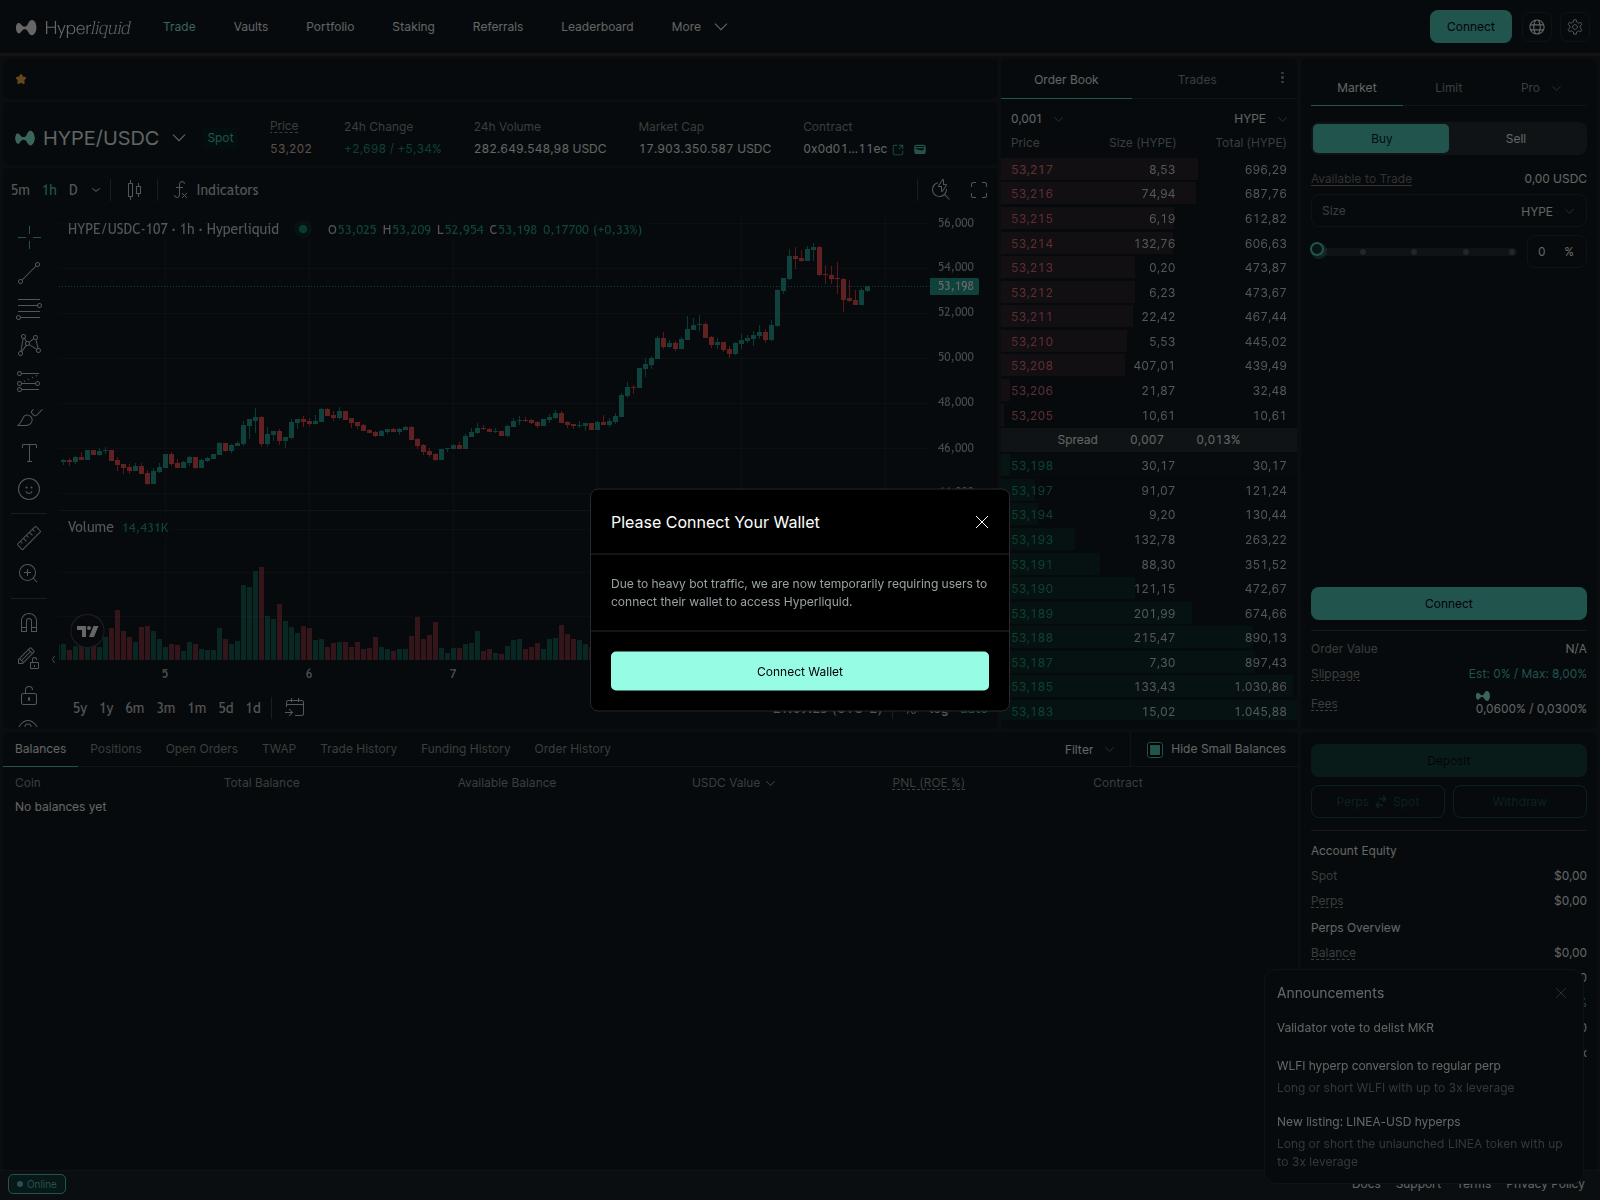
app.hciperliquid.com
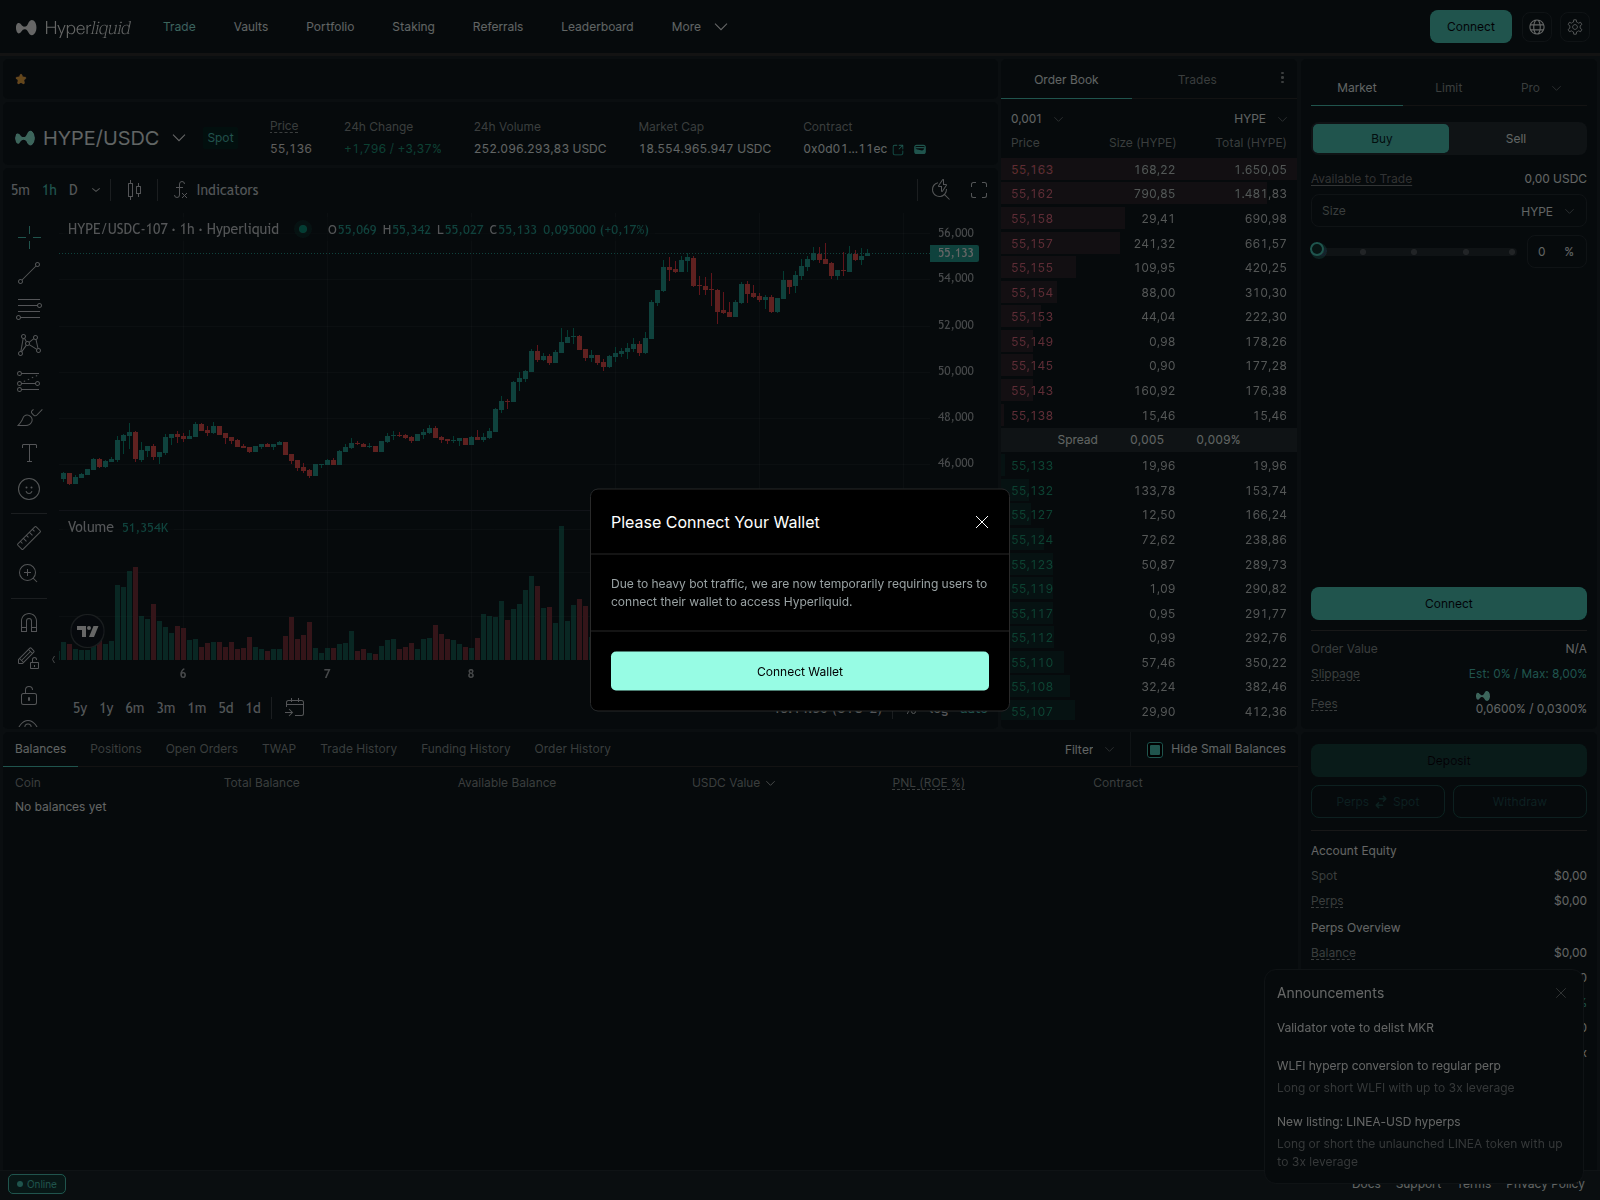
app.heroliquid.com
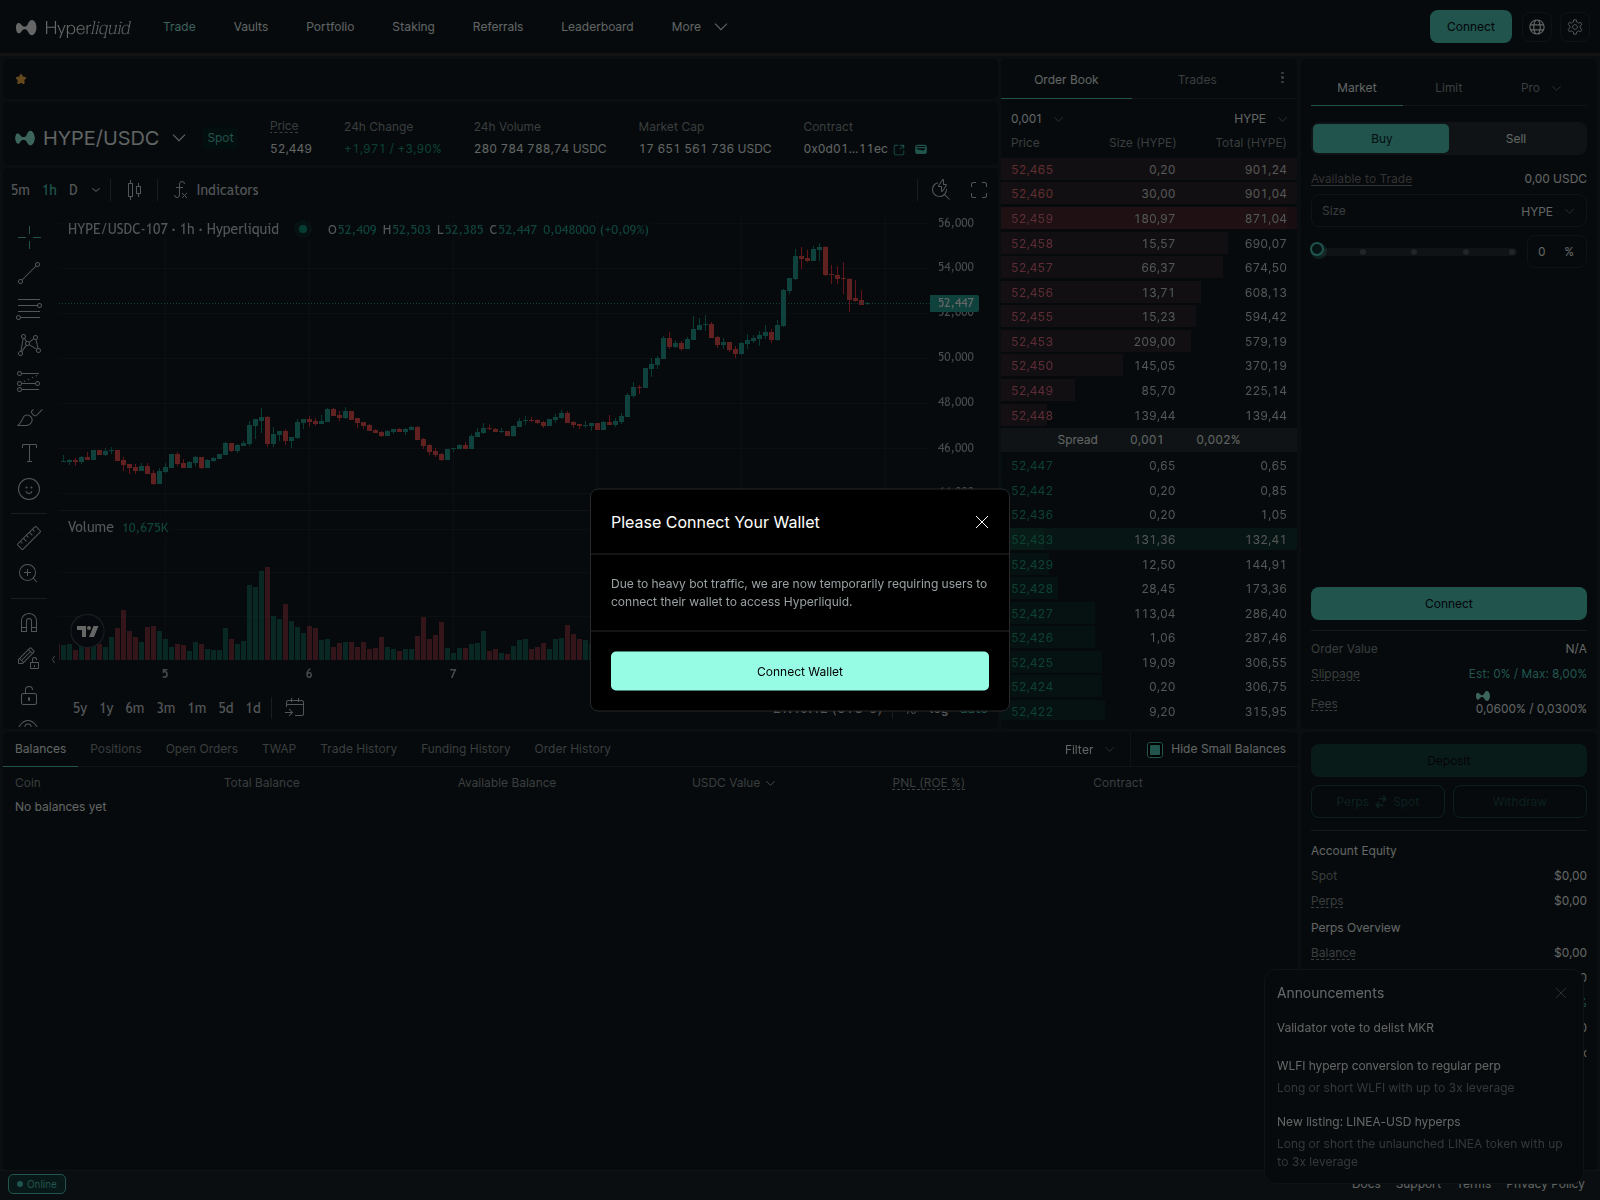
app.hilperliquid.com

app.huiperliquid.com

app.huiyperliquid.com

halborncybersecurity.pages.dev

halborndapp.pages.dev

noltrix.netlify.app

pumppresaledev.pages.dev

swap.hyperoquid.com

symbiosis-app.finance
web3.defiperpetualstaking.top
Pipeline ứng phó với các mối đe dọa
Cách thức xác minh từng miền trong trung tâm này và cách thức vô hiệu hóa các mối đe dọa đã được xác nhận. Trực quan hóa toàn bộ quy trình →
Kiểm tra thông tin tình báo về mối đe dọa— Mỗi tên miền đều được quét và đối chiếu với:
urlscan.ioẢnh chụp màn hình · DOM · HTTPVirusTotalHơn 90 công cụ chống virusGoogle Safe BrowsingBáo cáo minh bạchCloudflare RadarDNS · chứng chỉ · danh mụcAlienVault OTXCác bản tin tình báo về mối đe dọaWayback MachineBằng chứng lịch sửabuse.ch ThreatFoxPhân tích tương quan IOCcrt.shTính minh bạch của chứng chỉBộ lọc bảo mật DNSQuad9 · AdGuard · CleanBrowsingWeb-Kiểm traQuét toàn diện
 urlscan.io
 VirusTotal
 Google Safe Browsing
 Cloudflare Radar
 Wayback Machine
 abuse.ch ThreatFox
 crt.sh
 Web-Kiểm tra
Đồng bộ hóa nhà cung cấp toàn cầu— Các trường hợp phát hiện đã được xác nhận sẽ được gửi đến 29 đối tác:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalNguồn dữ liệu phát hiệnCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioQuét công khaiESETWebGuardBitdefenderTrao đổi thông tin về mối đe dọaNortonSafe WebSymantecĐánh giá trang webAviraPhát hiện trên đám mâyAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebCông cụ quét trực tuyếnNetcraftGỡ bỏ APIPhishTankPhiếu bầu đã được xác minhAPWG eCXNguồn cấp dữ liệu hàng loạtPhishStatsMở feedPhish.ReportLạm dụng dịch vụ lưu trữSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraQuét phần mềm độc hạiURLquerySandboxCriminal IPThông tin tài sảnCRDFThreat CenterScamadviserĐiểm tin cậyMyWOTWeb of Trust
 Google
 Google
 Microsoft
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 Kaspersky
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT