
Tìm kiếm các tên miền đang được theo dõi và xem xét các bằng chứng đã lưu trữ, các kết quả phát hiện cũng như tình trạng khả dụng mới nhất được ghi nhận.
221,203
Tổng số được theo dõi
215,388
Phát hiện VT
93,348
Lần cuối được nhìn thấy đang hoạt động
127,855
Không có sẵn tại thời điểm kiểm tra lần cuối
0
VT Đang chờ xử lý
How This Attack Works
Solana Drainer threats exploit vulnerabilities in Solana's crypto ecosystem to steal funds. Understanding their operation is crucial for prevention.
STEP 1
Target Identification
Attackers identify potential victims through phishing emails and fake websites.
STEP 2
Phishing Execution
Victims are lured to malicious sites mimicking legitimate platforms, like phantomairdrop.com.
STEP 3
Credential Harvesting
Once on the fake site, victims input sensitive information, believing it to be secure.
STEP 4
Fund Drainage
Attackers utilize harvested credentials to access wallets and drain funds via illicit transactions.
Technical Analysis
Solana Drainer attacks leverage phishing techniques to exploit the Solana blockchain. Attackers often create copycat websites using top TLDs such as .com, .xyz, and .cc, with domains hosted by registrars like Cloudflare, Inc. and PDR Ltd. These sites employ deceptive JavaScript and HTML code to mimic legitimate interfaces, tricking users into entering their private keys or seed phrases. Once credentials are obtained, attackers interact with the Solana blockchain via RPC calls to execute unauthorized transactions. The usage of smart contract functions like `transfer` and `approve` allows attackers to swiftly move funds out of victims' accounts. The infrastructure often involves a network of proxy servers to obfuscate the origin of the attack and make tracing back to the perpetrators difficult.
Real Cases
Phantom Wallet Breach (2023)
$2 million stolen
Attackers created a fraudulent Phantom wallet site to harvest user credentials, resulting in a $2 million theft.
SolUnion Scam (2024)
$1.5 million stolen
Using the domain phantom.solunion.cc, scammers executed a sophisticated phishing attack, stealing $1.5 million in SOL.
VaultBenefits Exploit (2024)
$3 million stolen
A fake airdrop campaign via vaultbenefits.net led to credential compromise and a subsequent $3 million drain.
How to Detect
Unsolicited emails or messages offering free SOL or airdrops
Websites with slight misspellings of legitimate names
Requests for private keys or seed phrases
Suspicious URL structures or unfamiliar TLDs like .xyz or .cc
Lack of HTTPS security on sites claiming to be secure
How to Protect Yourself
1
Verify URLs carefully before interacting
2
Enable multi-factor authentication on your wallet
3
Never share your private key or seed phrase
4
Regularly check transaction histories for unauthorized activity
5
Use official wallet apps and browser extensions
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 2,752 domains tracked for this threat type
Solana Drainer 2,752 domains

jeetdrop.top
jeffreycoin.app

jitoget.xyz

jitoreward.com
join-franklinsturtle.xyz
join-nyans.xyz
join-ploi.xyz
join-trolls.xyz

jun.ng

jup-official.com
jupcoin-x.org

jupiter-ag.net
kamlno.pro

launch-memecoin.company
listia.privatesol.shop

livdephantom.icu

lobstarsolana.net
luciass.onsolana.cc
luna-start.pro

lunacreate.net
magictissue01.shop
mail.solanagreen.eu

mastebot.network
masterbot-drop.fun

masterbotmigration.world
mavryk-testnet.live
maya.bitpump.fun
meemz.top
meteora-solana.pages.dev
meteora.team
meteorag.app
meterora.ag
mig-bert.xyz
mitosisdefi.run

monshoot-vote.org

moodeng.top
moonshot-verify.com


moonshotvotes.xyz
multichainsynth.online
nanj.offcoin.one
nbdfu.my

npcsolana.fun
nvnnq.gdn

olrgm1.cfd
paidsolana.com
panel.phantom-enterprise.ru
penguin.offcoin.one
people.allocation.id

pfpmeme.run

phan.beer

phantom-analytics.kolibrio.xyz
phantom-app.co.uk
phantom-solana-wallet-ee.pages.dev
phantom-space-4k8.pages.dev
phantom-spins.com
phantom.com.vn
phantom.reffinet.com

phantomav8.com
phantomclick519.top
phantomhouse.shop
phantominsure.com
phantomix.xyz
phantomm.lovable.app
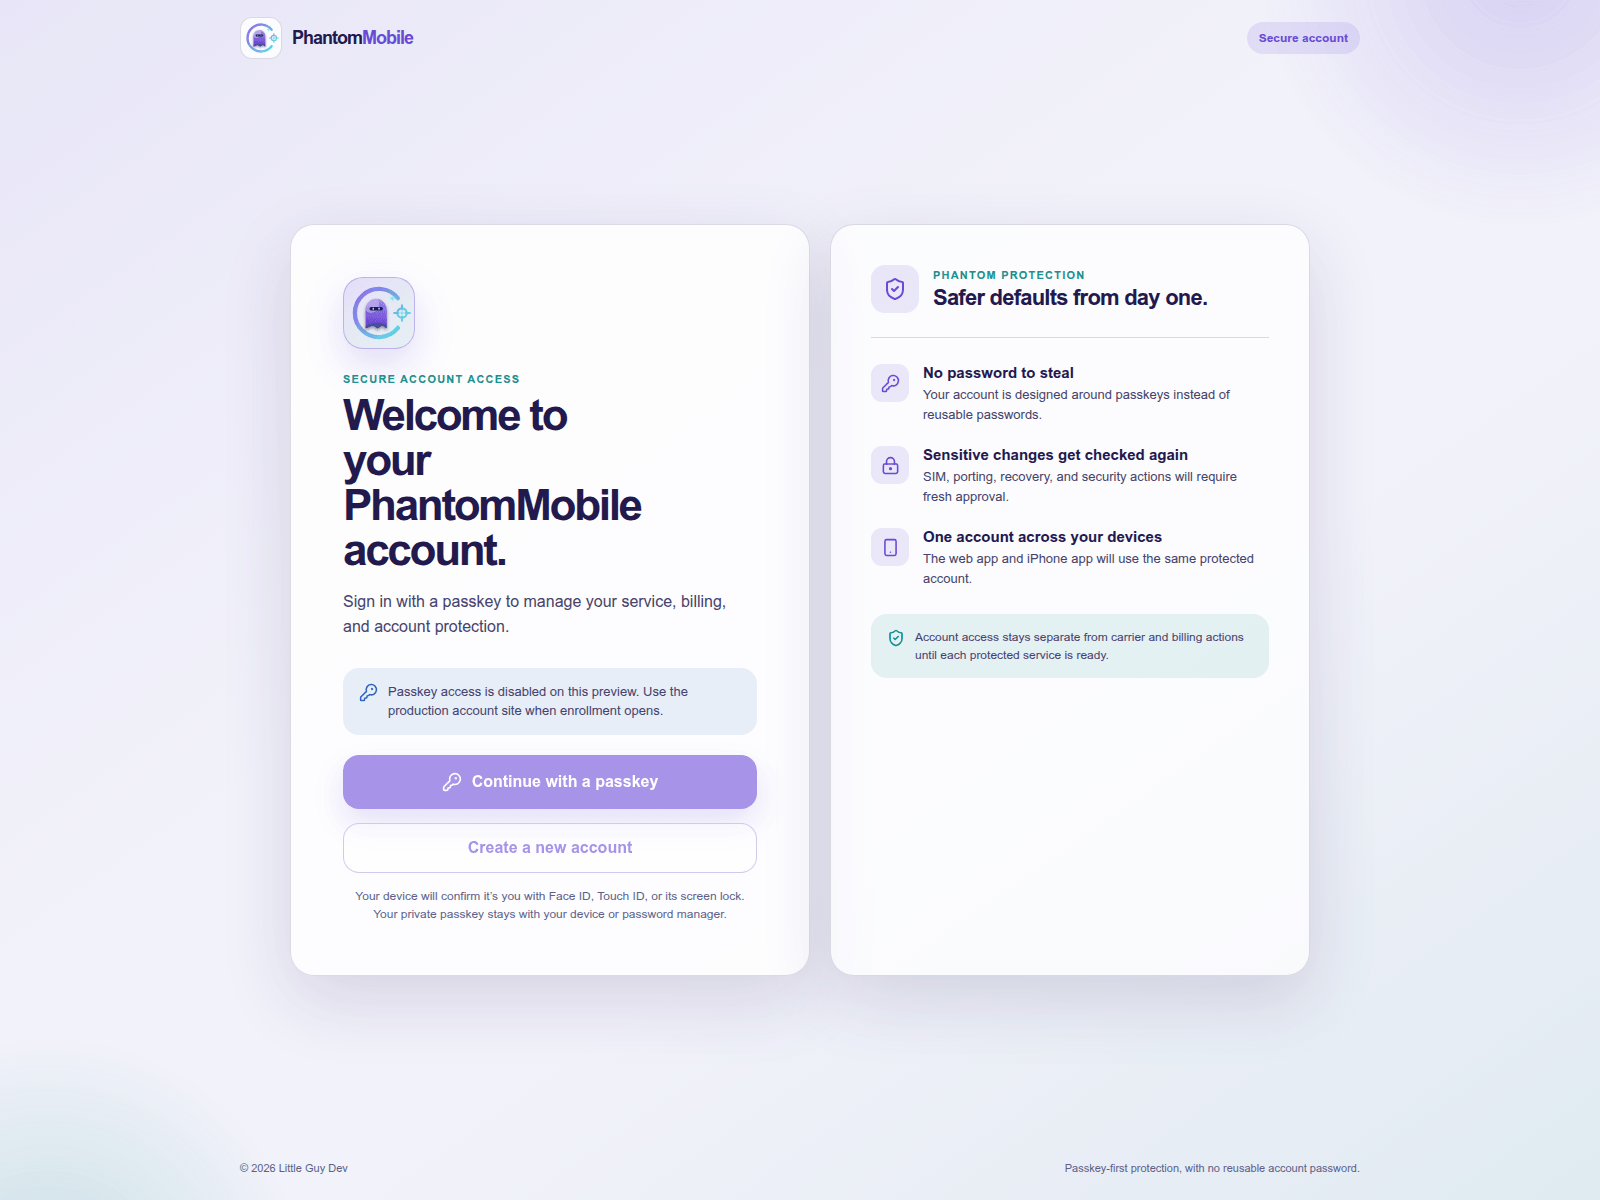
phantommobile-account.web.app

phantommonolith.shop
phantoms.pages.dev

phantomwallet.in
phantomworld242.top

photon-solana.top
pikamoonsolanatygaclaim.pages.dev
pippinloves.top
portal.phantombillstickers.com
presidentxi.live

psyopanimesol.fun

pumpapp.top
pumpfun-stream.live
pumpfunairdrop.live

pumpfunairdrop.online
punch-solana.com
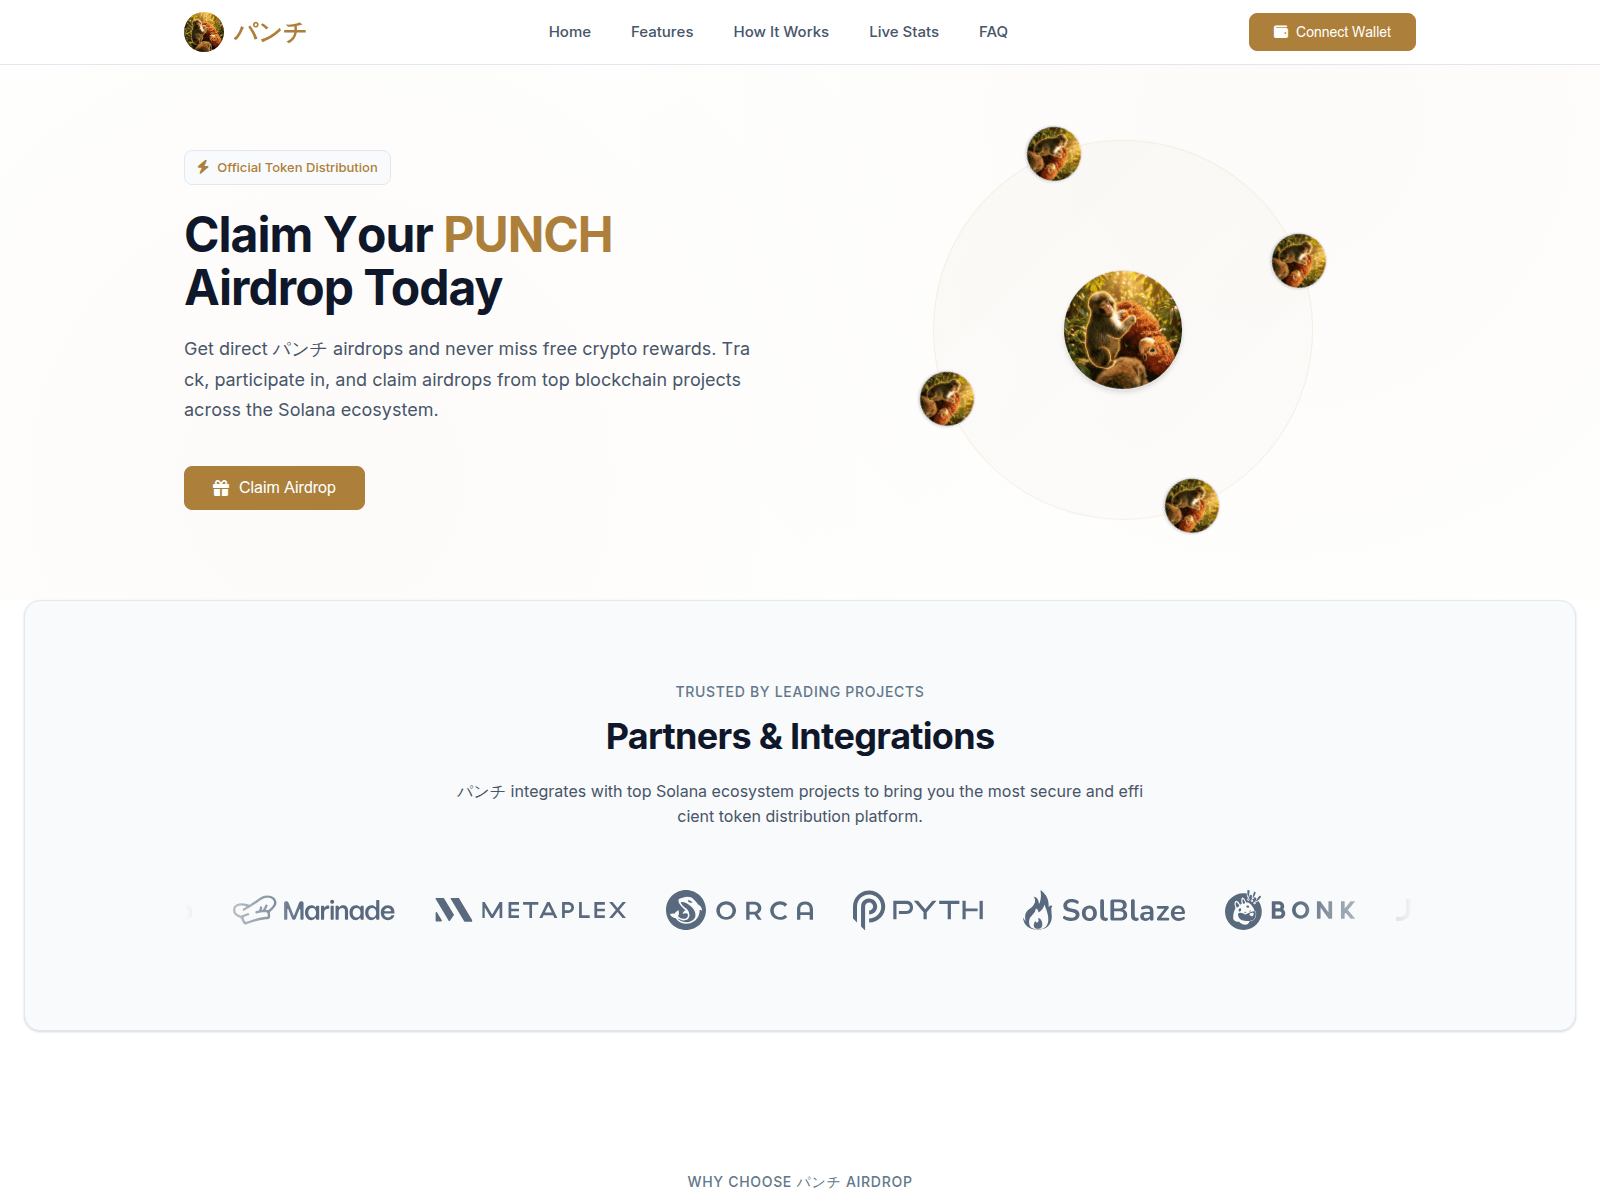
punchcoin.net

punchmonkeysolana.com

punchonsolana.live
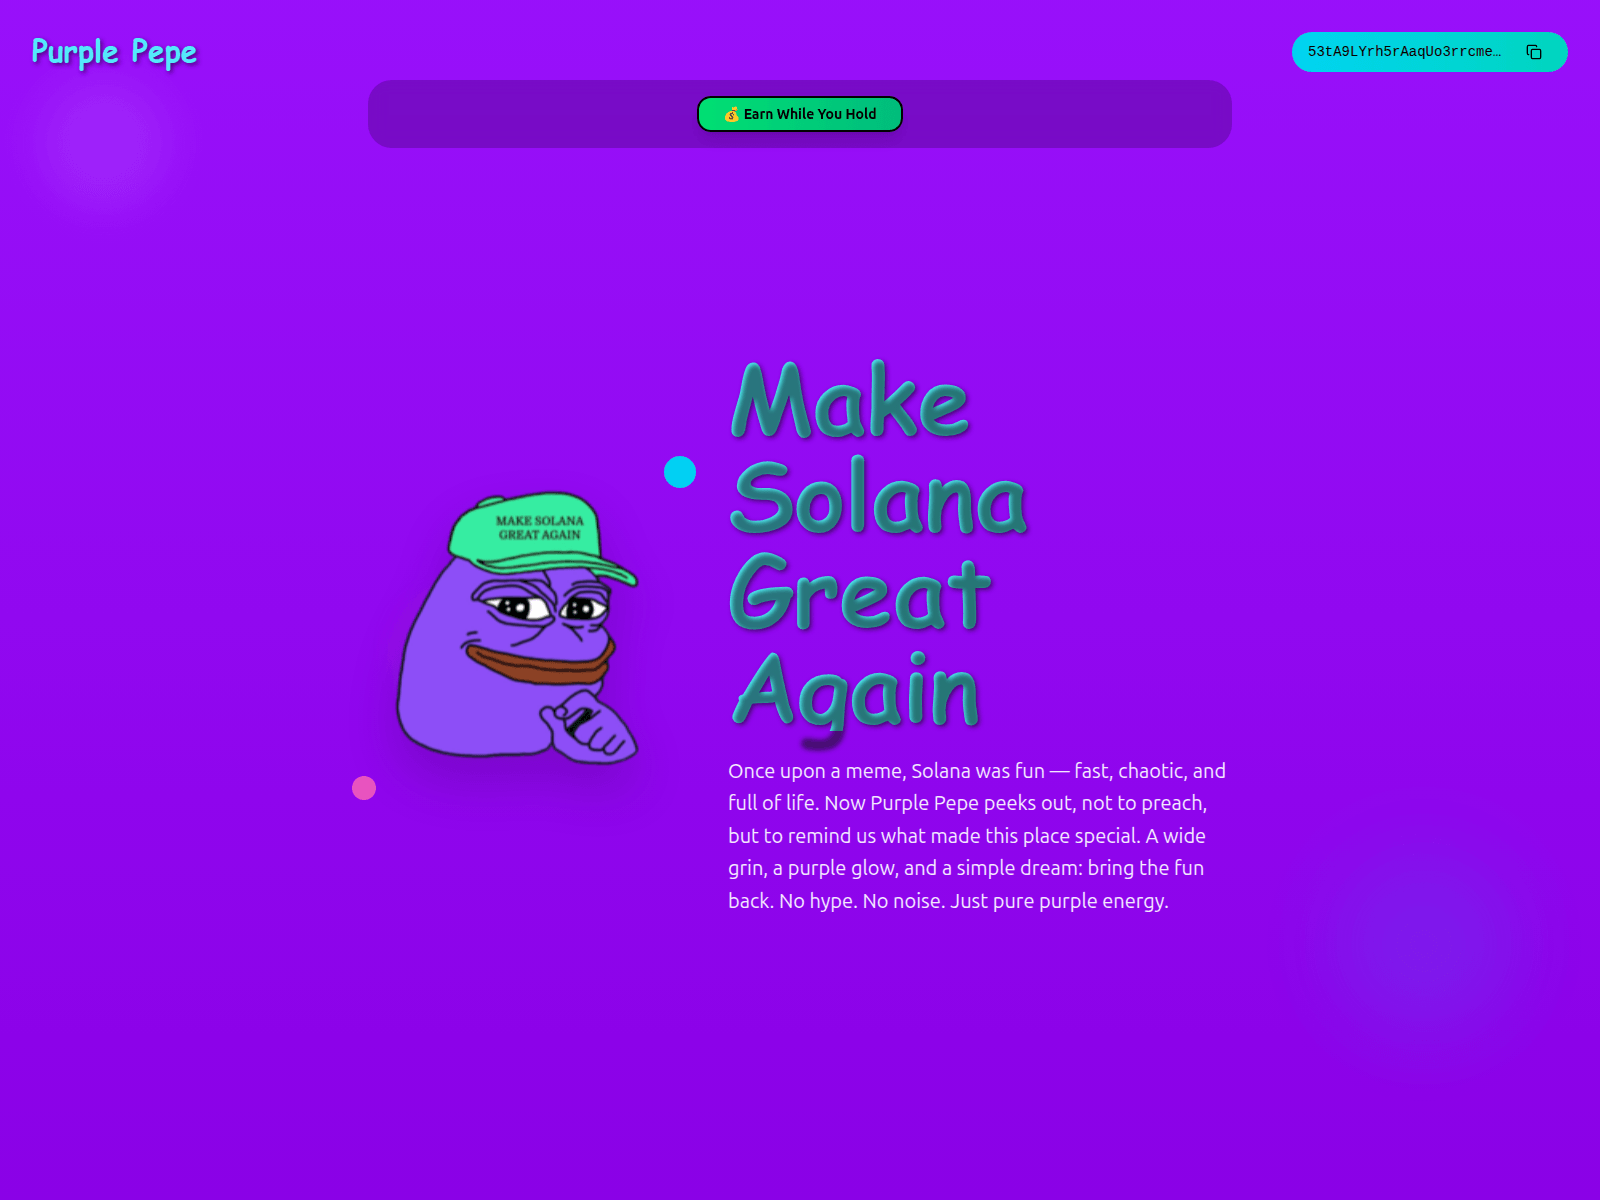
purplepepe.world
raydium.cx

raydiums.live

register-2026.fun

register-attention.fun

register-fafo.live

register-nocode.fun

register-pie.fun

register-poketcg.fun

register-shaw.fun
register-whitewale.com

rekill-register.fun
rhino.trade

ruglife.top

rugtools.lol
Pipeline ứng phó với các mối đe dọa
Cách thức xác minh từng miền trong trung tâm này và cách thức vô hiệu hóa các mối đe dọa đã được xác nhận. Trực quan hóa toàn bộ quy trình →
Kiểm tra thông tin tình báo về mối đe dọa— Mỗi tên miền đều được quét và đối chiếu với:
urlscan.ioẢnh chụp màn hình · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency Báo cáoCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Bảo mật FiltersQuad9 · AdGuard · CleanBrowsingWeb-Kiểm traFull surface scan
 crt.sh
Đồng bộ hóa nhà cung cấp toàn cầu— Các trường hợp phát hiện đã được xác nhận sẽ được gửi đến 29 đối tác:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecĐánh giá trang webAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftGỡ bỏ APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.Báo cáoHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust