




Безпека домену та аналіз загроз

syn-thalora.live
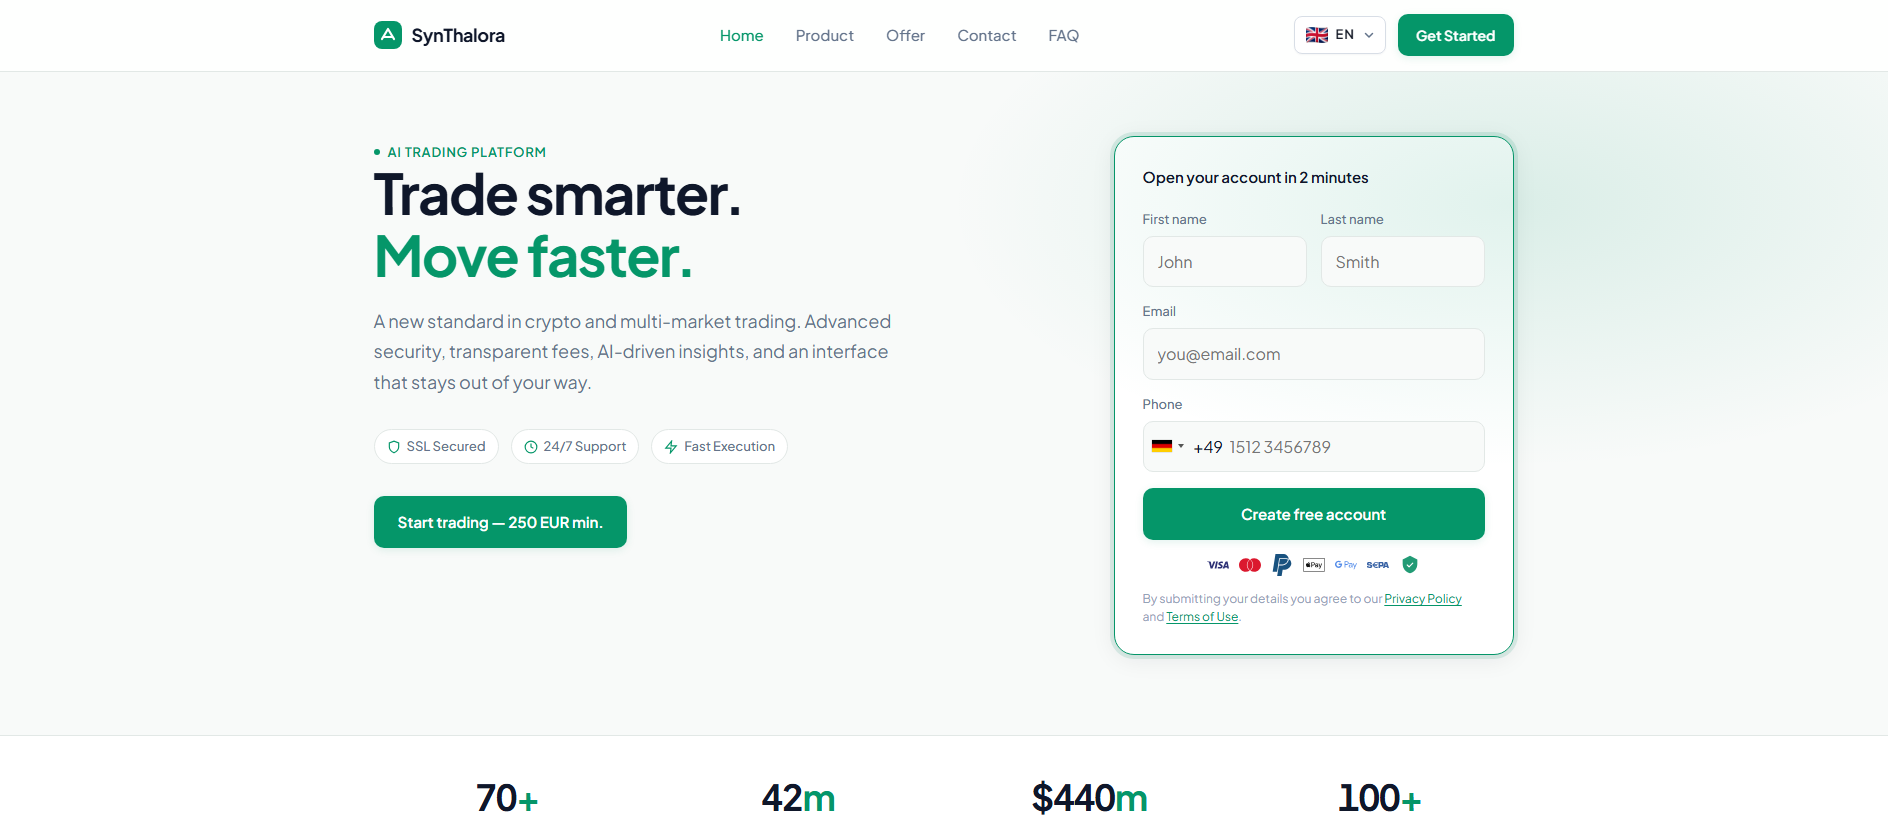
“SynThalora | AI-Powered Trading Platform”
Загрозливий вердикт
Критичний
100/100 оцінка доказів
Доступність
Останній відомий активний
Останнє збережене спостереження доступності
Сигнали ризику
Виявлення VirusTotal: 16/89
Уособлення бренду: Argent
Останній відомий активний
Actions
API
ABUSE NOTICE · 24H+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@dynadot.com.
The latest stored availability evidence still shows the domain reachable; 28 hours has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
28 hours
Reports sent
1
Latest case ID
PD-20260922-850D39
Current status
HTTP 200 at latest stored check
Огляд звіту
syn-thalora.live — Останній відомий активний (HTTP 200). Уособлення бренду: Argent; Тип шахрайства: Fake Exchange. Зведення доказів: VirusTotal 16/89 (alphaMountain.ai, BitDefender, CRDF, CyRadar, ESET); URLQuery 2 det.; URLScan capture; Google Safe Browsing flagged; CF Radar malicious; PhishDestroy score 100/100. Реєстратор: Dynadot.
Докладний аналіз PhishDestroy AI нижче залишено англійською, щоб зберегти оригінальний криміналістичний запис.
Зведення доказів
КРИТИЧНИЙ
PhishDestroy first observed syn-thalora.live on Sep 22, 2026. Stored content metadata identifies Argent as the apparent target. The captured page title is “SynThalora | AI-Powered Trading Platform”. Page analysis recorded additional brand references to Ethereum, PayPal, and Signal. Stored page analysis classifies the content as fake exchange. Current evidence score: 100/100 (critical).
Positive findings are stored from 4 sources: VirusTotal, Google Safe Browsing, Cloudflare Radar, and URLQuery. On Sep 23, 2026 at 14:01 UTC, VirusTotal recorded 16 detections among 89 engines: alphaMountain.ai, BitDefender, CRDF, CyRadar, ESET, Forcepoint ThreatSeeker, Fortinet, G-Data, Google Safe Browsing, Gridinsoft, Kaspersky, Lionic, Seclookup, SOCRadar, Sophos, VIPRE; Google Safe Browsing flagged the domain: Social Engineering. Cloudflare Radar classified the hostname as malicious and assigned the categories malware and security threats; its verdict timestamp was not retained. URLQuery recorded 2 detections; no observation timestamp was retained. Non-positive and contextual checks: AlienVault OTX listed 4 community pulse references (not vendor detections) on Sep 23, 2026 at 14:02 UTC. The separate external-blocklist snapshot contained no matches on Sep 23, 2026 at 10:20 UTC. URLScan captured the page on Sep 22, 2026 at 09:48 UTC.
HTTP 200 was recorded on Sep 23, 2026 at 10:00 UTC. Registration records for the domain list Dynadot Inc as the registrar and Jul 27, 2026 as the creation date. At collection time, the hostname resolved to 172.67.138.108 on AS13335 (Cloudflare, Inc.). The IP and ASN identify shared Cloudflare edge infrastructure; the origin server is not established by this address. The stored server header is nginx. DOM analysis on Sep 22, 2026 at 10:20 UTC returned 100/100. The evidence archive retains 3 visual captures from PhishDestroy and URLScan. TLS metadata lists Google Trust Services / WE1 as the certificate issuer with validity through Nov 16, 2026; checked Sep 22, 2026 at 10:02 UTC.
The content indicators and 4 positive source findings support the current Argent-themed fake exchange classification.
VirusTotal
16 det.
URLQuery
2 det.
OTX references
CF Radar
Шкідливий
URLScan
Сертифікат TLS
Google Trust Services / WE1
Вік
2 mo New
Зафіксований статус
Останній відомий активний 200

DestroyList
У списку
Reports Sent
1
Обсяг даних
VirusTotal
16 / 89
URLQuery
2 det.
OTX
4 community references
CF Radar
provider verdict: malicious
URLScan capture
збережений звіт
TLS
valid certificate, 53d
WHOIS
2 mo old
Знімок екрана
3 captures · 2 sources
Розвіддані з мережевої безпеки
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Status Check Sep 22, 2026 · 11:37 UTCTelemetry event observed.
-
Threat First Observed Sep 22, 2026 · 11:36 UTCDomain ingestion complete. Initial state is marked as unknown pointing to IP
172.67.138.108.
Процес реагування на загрози Pipeline
Відкриття
Checks
Reports
Доступність
12/13
Sent Report Recorded
Stored sent-report record for registrar Dynadot Inc, hosting provider, 1 abuse contact
abuse@dynadot.com
Статус у публічних блоклистах
Аналіз виявлення та ухилення
Перевірка маскування та розподілу трафіку
Ще не відскановано
Наразі не зафіксовано жодних відмінностей між роботами-павуками та браузерами
Збережені дані спостережень за взаємодією веб-сканера та браузера для цього хоста, а також перевірка відбитків у режимі реального часу для систем розподілу трафіку типу «Кейтаро».
- Збережений прапор маскування
- Ще не відскановано
- Останнє сканування маскування
- Заголовок сервера, який бачить сканер
cloudflare
Примітка щодо сканера: alive_content: raw=ok; http=200; via=https_proxy; server=cloudflare
Перевірка відбитків пальців у режимі реального часу за адресою TDS
Сім відбитків Keitaro та порівняння «краулер проти браузера», що запускаються зі сканера PhishDestroy, коли ця панель відкрита.
Очікування
Збережений знімок · 3 sources
Аналітика доменів
Домен
Google Safe Browsing
Позначено
Social engineering checked 23.09.2026
Сервер / ASN
nginx · AS13335 Cloudflare, Inc.
IP Context
Cloudflare shared edge
origin IP hidden
Репутація Edge-IP не пов’язана з цим доменом.
OTX Tags
2026-09activeall-domainsblocklistcontentcryptoдомениdrainerfraudmonthlyphishdestroyphishingscam
Реєстратор
Dynadot
 (US)
(US)
IP-адреса
172.67.138.108
CDN
Геолокація Toronto, CA
МережаAS13335 · Cloudflare, Inc.
Початкова IP-адреса прихована за проксі CDN. Результати зворотного IP для крайової адреси містять непов’язаних орендарів; для пошуку джерела потрібен пасивний DNS або дані прозорості сертифіката.
РеєстраціяСтворено 27.07.2026 (57d · New) — Expires 27.07.2027
Статус HTTP200
Технічні подробиціDNS, SAN-адреси SSL, мітки часу
Вперше виявлено22.09.2026
DOM Analysis
IoC Extraction
Submitted URLhttp://syn-thalora.live/
Сервери іменjulissa.ns.cloudflare.comrajeev.ns.cloudflare.com
TLS Fingerprint
TLS Observation
Favicon Hash
ID справи
ICANN OVERSIGHT
Акредитація та контекст RAA
Акредитація та контекст RAA
Registrar accreditation and DNS abuse obligations
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
Accreditation is a contract, not a safety certification.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Акредитація — це договір, а не знак безпеки.
Перевірити збори ICANN
Прочитати RAA §3.18
PHISHDESTROY INVESTIGATIONICANN funding, contracts, and DNS abuse oversight
Технології · 4 identified
jsDelivr
CDN
Cloudflare Browser Insights
Analytics
RUM
Cloudflare
CDN
HTTP/3
Miscellaneous
Detected via Cloudflare Radar · Wappalyzer engine
Поскаржитися на цей домен
Надішліть докази та допоможіть захистити інших
Аналіз VirusTotal
16 / 89 постачальників безпеки позначили цей домен
View on VT
Last analyzed Previous stored snapshot: 16 detections
alphaMountain.ai
BitDefender
CRDF
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Google Safe Browsing
Gridinsoft
«Касперський»
Lionic
Seclookup
SOCRadar
Sophos
VIPRE
Аналіз продуктивності сайту
Google PageSpeed Insights — mobile performance audit of syn-thalora.live · checked Sep 22, 2026
92
Good
Performance
FCP
2.62s
First Contentful Paint
LCP
2.62s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
3.08s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Докази та зовнішні звіти
Аналіз безпеки
Знімок надісланих доказів
Sent: Ledger records: 1
Case ID:
PD-20260922-850D39 Recipient: abuse@dynadot.com Page title stored with report: SynThalora | AI-Powered Trading Platform
PDF notice generated Notice text archived (291 chars)
Abuse notice text as sent to the provider
Registrar: Dynadot LLC / Dynadot Inc (United States)
Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
OSINT та розвідка
DNS та мережа
SEO та домен
Чи вплинув на вас цей сайт?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
Якщо ви ввели облікові дані облікового запису, особисту чи платіжну інформацію або завантажили файл із цього домену, негайно вживіть заходів. Нижче наведено ресурси, які допоможуть вам повідомити про інцидент і захистити себе.

«Action Fraud»
Повідомте про шахрайство та кіберзлочинність в Англії, Уельсі та Північній Ірландії
Contact centre0300 123 2040
PhishDestroy listing review Не звіт правоохоронних органів
Оскарження домену
Надішліть запит на перевірку, якщо ви володієте цим доменом і вважаєте, що інформація про нього неправильна
Остерігайтеся шахраїв, які обіцяють повернути втрачені кошти! Злочинці можуть знову зв’язатися з жертвами, видаючи себе за слідчих, адвокатів або агентів із відновлення. Не сплачуйте авансових зборів і не діліться обліковими даними. Дізнайтеся більше про шахрайство у сфері відшкодування збитків →
Зверніться до місцевих органів влади
Виберіть свою країну, щоб отримати офіційні контакти кіберзлочинців або створити проект скарги →.
Довідник 97 країн
Чернетка за допомогою штучного інтелекту — деталі інциденту обробляються постачальником штучного інтелекту
Перегляньте та подайте його самостійно
Пов’язана інфраструктура та звіти
- Пряме посилання Використовує ту саму реєстрацію або ідентичний фішинговий набір.
- Допоміжний сигнал Спільна інфраструктура або цільовий бренд; це не є доказом того, що оператори є одним і тим самим.
- Тільки для ознайомлення Внесено до списку для навігації; не має спільних атрибутів із цим хостом.
Кожна смуга позначає одну з причин, через яку домен пов’язаний із цим хостом. Розмір вузла вказує на виявлення VirusTotal, а вузли, позначені пунктирною лінією, вже не працюють. Повний перелік наведено нижче.
Збіги за змістом 2
Однаковий хеш фавікону або однаковий заголовок сторінки, як у цього хоста.
Інші звіти про спільний Cloudflare edge 2
Ці звіти приводять до тієї самої спільної крайової IP-адреси. Вони допомагають у виявленні звітів, але не передбачають спільного володіння чи спільного вихідного сервера.

Argent видавання себе за когось іншого 8
Ці домени також націлені на користувачів Argent. Переглянути всі загрози типу «Argent» →
Той самий реєстратор: Dynadot 6
Зареєстровані через одного й того самого реєстратора. Один реєстратор обслуговує мільйони клієнтів, які не пов’язані між собою, тому це лише об’єднує дані, а не доводить наявність зв’язку.


Останні повідомлення про загрози 4
Нещодавно додані звіти з бази даних PhishDestroy. Ці посилання для виявлення не передбачають спільної інфраструктури чи власності.


Перевірити будь-який домен
Аналіз загроз за допомогою збереженого списку блокувань, WHOIS, DNS і загальнодоступних доказів сканування
Сканувати заразПовідомити про фішинг
Додавайте підозрілі домени до нашої бази даних загроз — захищайте спільноту
ПовідомитиПотокова стрічка про загрози
Останні звіти про фішинг і помічені зміни доступності
ВідстежуватиБудьте в курсі подій, дбайте про свою безпеку
Слідкуйте за актуальними загрозами або оскаржте цей запис, якщо вважаєте, що це помилкова тривога