Перейти до звіту про безпеку
Безпека домену та аналіз загроз
duplicate-disabled-179297.invalid favicon

duplicate-disabled-179297.invalid

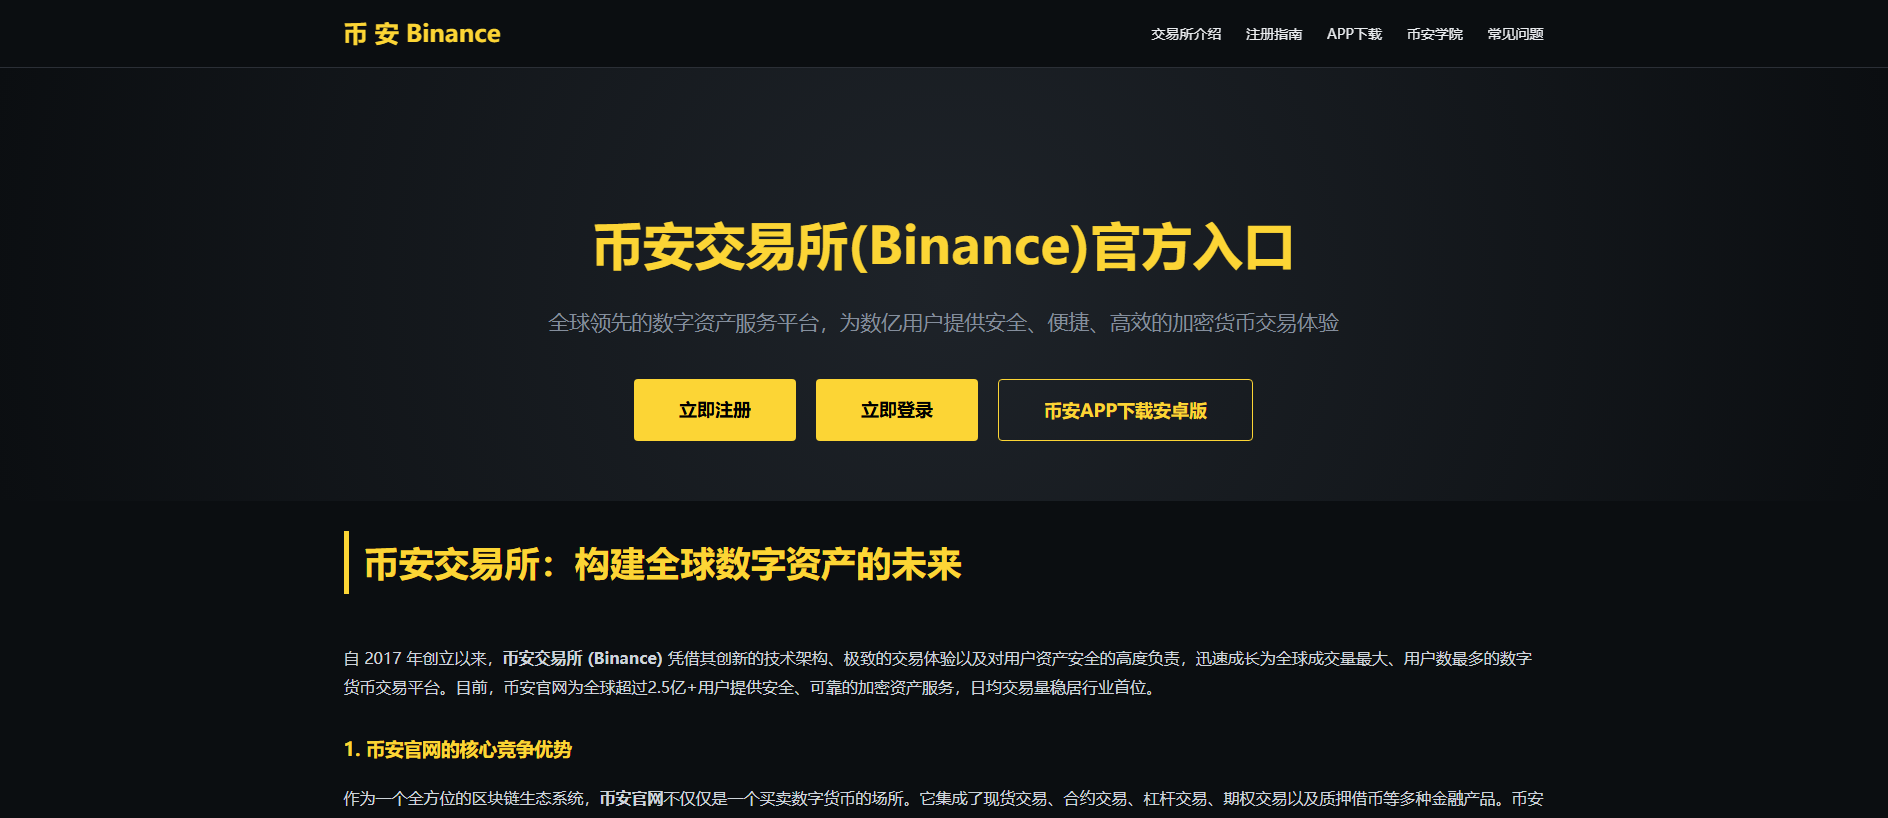
“币安官网 | 币安交易所(Binance)官方App下载及注册登录入口”

Реєстратор
GoDaddy
Resolved IP
101.32.10.247
Registered
24.02.2026
Загрозливий вердикт Критичний
Доступність Контент недоступний Вміст був недоступний під час останнього спостереження
Виявлення VirusTotal: 17/89 URLQuery threat systems: 3 alerts Уособлення бренду: Binance
25.03.2026 Binance
API
Цей домен було позначено як шкідливий
Системи безпеки повідомляють про виявлення: 17. Будьте дуже обережні — не вводьте облікові дані чи особисту інформацію.
Огляд звіту

The domain www.home-binance.com, impersonating Binance, is currently down or taken down. This domain was registered on 2026-02-24.

Докладний аналіз PhishDestroy AI нижче залишено англійською, щоб зберегти оригінальний криміналістичний запис.

VirusTotal
VirusTotal
17 det.
URLQuery
URLQuery
3 threat alerts
DNS Security
3/14
CF Radar
Шкідливий
URLScan
URLScan
Сертифікат TLS
Прострочений або неперевірений
Вік
8 mo
Зафіксований статус
Контент недоступний
PhishDestroy
DestroyList
У списку

Source evidence

9 sources

Блокування DNS

3/14

PhishStats

checked — no match recorded

Google Safe Browsing

Checked; no threat flag recorded

Повідомити
Розвіддані з мережевої безпеки
DNS Provider Blocks 3 / 14
Brand Binance Cloudflare Family Cloudflare Security
Threat Detection Systems 3 alerts
Detection System Indicator Verdict Alert
OpenDNS www.home-binance.com phishing Phishing Block
Cloudflare DNS www.home-binance.com malicious Sinkholed
DNS4EU www.home-binance.com malicious Sinkholed
CF Cloudflare Radar Verdict Шкідливий
Security threats Phishing Security Risks Phishing

Зведення доказів

Критичний
VirusTotal
17/89
URLScan
Stored capture

This report details a newly registered domain, www.home-binance.com, which is an impersonation threat. The site’s page title, in Chinese, translates to "Binance Official Website | Binance Exchange (Binance) Official App Download and Registration Login Portal," explicitly claiming to be the legitimate Binance cryptocurrency exchange. The scam type is impersonation, posing the threat of credential theft or financial fraud by tricking users into entering sensitive information.

Technical analysis confirms the malicious nature of the domain. VirusTotal flagged the site with 17 detections out of 95 vendors. The domain was created on 2026-02-24 and registered through GoDaddy.com, LLC. It resolves to IP address 101.32.10.247, located in Hong Kong and hosted by Tencent Cloud Computing. The SSL certificate is issued by Let's Encrypt (R13), and the nameservers are ns71.domaincontrol.com and ns72.domaincontrol.com.

The site is currently offline. Its GridinSoft trust score is 0 out of 100, and the DOM risk score is 73, indicating a high risk level. The combination of recent registration, brand impersonation, and poor trust metrics confirms this domain is a threat, though its current offline status limits immediate risk.

Аналіз виявлення та ухилення

Перевірка маскування та розподілу трафіку

Не спостерігалося У збереженому скані не було виявлено жодних слідів маскування

Збережені дані спостережень за взаємодією веб-сканера та браузера для цього хоста, а також перевірка відбитків у режимі реального часу для систем розподілу трафіку типу «Кейтаро».

Збережений прапор маскування
Не спостерігалося
Оцінка маскування
0/6
Останнє сканування маскування

Примітка щодо сканера: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='duplicate-disabled-179297.invalid', port=80): Max retries exceeded with url: / (Caused by

Перевірка відбитків пальців у режимі реального часу за адресою TDS
Сім відбитків Keitaro та порівняння «краулер проти браузера», що запускаються зі сканера PhishDestroy, коли ця панель відкрита.
Очікування

Збережений знімок · 3 captures

Заголовок сторінки
币安官网 | 币安交易所(Binance)官方App下载及注册登录入口
Impersonates
Binance
Сертифікат TLS
Certificate hostname mismatch · Виданий Let's Encrypt · stored validity ends in 88 days

Domain details

Домен
URLScan Verdict Шкідливий score 100 Phishing brand: Binance report ↗
Репутація IP abuse score 0/100 0 reports checked 12.09.2026
Реєстратор GoDaddy US(US)
Контакт для скаргabuse@godaddy.com, abuse@tencent.com
Реєстр ICANNICANN Lookup (RDAP) →
РеєстраціяСтворено 24.02.2026 (229d)
Час до першої недоступності 33 days
Що ми враховуємо Час, що минув від першого збереженого звіту про порушення до першого спостереження, що вміст був недоступний. Це не встановлює причину.
Що містить кожен звіт Збережені записи вихідних звітів можуть посилатися на докази, доступні на той час, наприклад вердикти постачальників, реєстраційні дані, деталі хостингу, класифікації або знімки екрана. Ця сторінка не визначає точного доставленого корисного навантаження, квитанції, підтвердження чи дії одержувача.
Технічні подробиціProvenance & timestamps
Вперше виявлено25.03.2026
Submitted URLhttp://www.home-binance.com/
Favicon Hash
ID справи
ICANN OVERSIGHT

Акредитація та контекст RAA

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft Нічого не надсилається автоматично.

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
101.32.10.247
Network ASN
AS132203
Organization
Tencent Cloud Computing
Observed location
Hong Kong, HK
Server header
nginx

Сервери імен 2

  • ns71.domaincontrol.com
  • ns72.domaincontrol.com

Location describes the IP network.

Сертифікат TLS

Issuer
Let's Encrypt
Valid from
2026-03-24 14:47:09
Valid until
2026-06-22 14:47:08
Hostname coverage
Certificate hostname mismatch
Validity
Stored certificate expired
Collection time
2026-03-25 20:46:17 UTC
Collection source
PhishDestroy collector
Certificate fingerprint8224ed532a1b5b2579536470b5721ad09fb4d3291e5c0c88c1e1bccd87f67554
Certificate names · 1 SANs
  • home-binance.com

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 101.32.10.247rapiddns.io

Latest Classified Outcome 2026-10-11 01:30:55 UTC

Primary outcome Невідомо reason: Probe Inconclusive 20% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Unreachable Content: Unknown DNS: Stale Registration: Unknown
Latest HTTP observation Невідомо Probe Inconclusive 20% 2026-10-11 01:30:55 UTC
RDAP registration Невідомо
Observed timeline last reachable: 2026-09-23 02:12:30 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Технології · 3 identified
Detected via Cloudflare Radar · Wappalyzer engine
Поскаржитися на цей домен Надішліть докази та допоможіть захистити інших

Аналіз VirusTotal

17 / 89 постачальників безпеки позначили цей домен
View on VT
Last analyzed
alphaMountain.ai
BitDefender
Chong Lua Dao
ESET
Emsisoft
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
«Касперський»
Lionic
Netcraft
Seclookup
SOCRadar
Sophos
VIPRE
Webroot
Аналіз продуктивності сайту

Google PageSpeed Insights — mobile performance audit of duplicate-disabled-179297.invalid · checked Mar 25, 2026

99
Good
Performance
FCP
1.54s
First Contentful Paint
LCP
1.54s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
2.31s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-09-25 01:31:10 UTC
    Domain state transitioned from alive to dead.

Процес реагування на загрози Pipeline

Відкриття
Analysis
Monitoring

14 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Загроза виявлена
duplicate-disabled-179297.invalid виявлено та додано до черги для повного аналізу
25.03.2026
URLScan.io Capture
Збережено URLScan report with capture artifacts
URLScan Verdict
URLScan returned a malicious verdict · score 100
29.07.2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
VirusTotal
17/89 recorded on VirusTotal
11.09.2026
DNS Security Blocks
Blocked by 3 of 14 checked DNS providers: Brand binance, Cloudflare family, Cloudflare security
CF Radar: Malicious
Cloudflare Radar classified this domain as Security threats, Phishing, Security Risks, phishing
Brand Impersonation
Impersonation of Binance
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
Technical Analysis Recorded
Звіт містить збережені результати технологічного або криміналістичного аналізу.
11.10.2026
Content Observed Unavailable
Моніторинг зафіксував недоступну відповідь; причина не була незалежно встановлена.
25.09.2026
Опубліковано список «DestroyList»
25.03.2026
Content Observed Unavailable
Останні збережені перевірки вказують на те, що повідомлений вміст недоступний; це не встановлює, хто або що спричинило зміну.
25.09.2026
Час до першої недоступності
Від виявлення до першого недоступного спостереження минуло 803 годин.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Схожі домени

Збережено 187 схожих доменів

Показати всі (88)
binabce.com replacement binacne.com transposition binan.ce.com subdomain binancecom.com various binanci.com vowel-swap binanco.com vowel-swap binancr.com replacement binancs.com replacement binancw.com replacement binande.com replacement binanfe.com replacement binanve.com replacement binanxe.com replacement binnace.com transposition binonce.com vowel-swap binsnce.com replacement binunce.com vowel-swap binynce.com replacement binznce.com replacement bniance.com transposition bunance.com replacement ibnance.com transposition ninance.com replacement b-inance.com hyphenation b8inance.com insertion b8nance.com replacement b9nance.com replacement bbinance.com repetition bhinance.com insertion bi-nance.com hyphenation biance.com omission bibance.com replacement bibnance.com insertion bihance.com replacement bihnance.com insertion biinance.com repetition bijnance.com insertion biknance.com insertion bimance.com homoglyph bimnance.com insertion bin-ance.com hyphenation binaance.com repetition binabnce.com insertion binace.com omission binahce.com replacement binamnce.com insertion binan-ce.com hyphenation binanbce.com insertion binanc-e.com hyphenation binanc.com omission binanc3.com replacement binancce.com repetition binancve.com insertion binancxe.com insertion binancz.com replacement binandce.com insertion binane.com omission binanec.com homoglyph binanhce.com insertion binanmce.com insertion binannce.com homoglyph binanvce.com insertion binanxce.com insertion binarnce.com homoglyph binasnce.com insertion binawnce.com insertion binbance.com insertion binhance.com insertion binmance.com insertion binnance.com homoglyph binnce.com omission binqance.com insertion binsance.com insertion binwnce.com replacement binyance.com insertion bionance.com insertion birnance.com homoglyph biunance.com insertion bjnance.com replacement bnance.com omission bninance.com insertion boinance.com insertion bonance.com replacement buinance.com insertion bvinance.com insertion clinance.com homoglyph dinarce.com homoglyph ginance.com replacement

Показано 100 із 187

Докази та зовнішні звіти

Глибокий аналіз

Чи вплинув на вас цей сайт?

5 evidence signal groups linked 0 reports recorded Контент недоступний
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Якщо ви ввели облікові дані облікового запису, особисту чи платіжну інформацію або завантажили файл із цього домену, негайно вживіть заходів. Нижче наведено ресурси, які допоможуть вам повідомити про інцидент і захистити себе.

Європол
Знайдіть офіційний канал звітності для вашої країни ЄС
National police directory
Остерігайтеся шахраїв, які обіцяють повернути втрачені кошти! Злочинці можуть знову зв’язатися з жертвами, видаючи себе за слідчих, адвокатів або агентів із відновлення. Не сплачуйте авансових зборів і не діліться обліковими даними. Дізнайтеся більше про шахрайство у сфері відшкодування збитків →

Зверніться до місцевих органів влади

Виберіть свою країну, щоб отримати офіційні контакти кіберзлочинців або створити проект скарги →.

Довідник 97 країн

Template-based draft · optional AI wording assistance requires separate consent

Чернетка за допомогою штучного інтелекту — деталі інциденту обробляються постачальником штучного інтелекту · Перегляньте та подайте його самостійно

Перевірити будь-який домен

Аналіз загроз за допомогою збереженого списку блокувань, WHOIS, DNS і загальнодоступних доказів сканування

Сканувати зараз

Повідомити про фішинг

Додавайте підозрілі домени до нашої бази даних загроз — захищайте спільноту

Повідомити

Потокова стрічка про загрози

Останні звіти про фішинг і помічені зміни доступності

Відстежувати

Будьте в курсі подій, дбайте про свою безпеку

Слідкуйте за актуальними загрозами або оскаржте цей запис, якщо вважаєте, що це помилкова тривога

Потокова стрічка про загрози Оскаржити це оголошення
HTML · IFRAME

Вбудувати цей звіт

Поділіться цією інформацією про загрози на своєму веб-сайті або в блозі

embed.html
<iframe
  src="https://phishdestroy.io/uk/embed/domain/duplicate-disabled-179297.invalid"
  title="PhishDestroy threat report for duplicate-disabled-179297.invalid"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>