VirusTotal
15 / 91
Повідомити

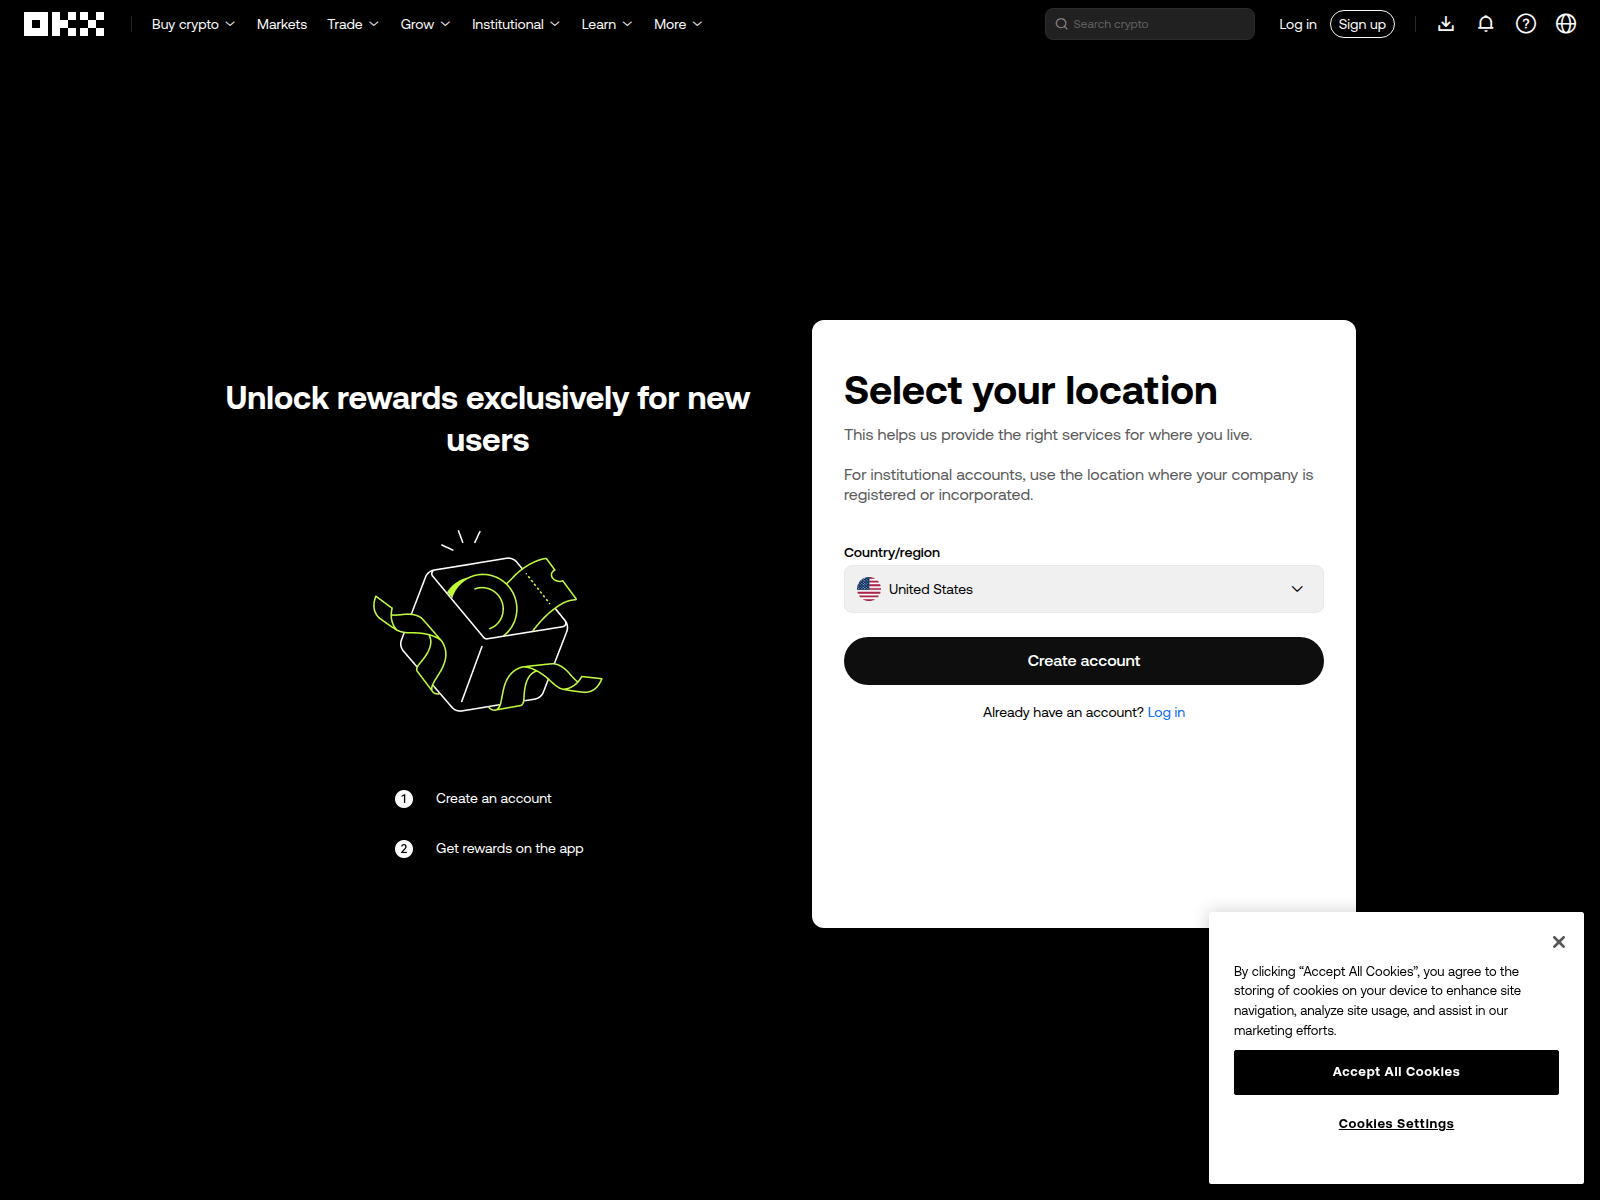
“Earn rewards when you get started on OKX | My referral code: 37602380 | OKX Europe”
cnouyi.org — Останній відомий активний (HTTP 302). Уособлення бренду: OKX; Тип шахрайства: Brand Impersonation. Зведення доказів: VirusTotal 15/91 (alphaMountain.ai, BitDefender, CyRadar, ESET, Emsisoft); URLQuery 3 alerts; URLScan malicious verdict; PhishDestroy score 100/100. Реєстратор: Dynadot.
Докладний аналіз PhishDestroy AI нижче залишено англійською, щоб зберегти оригінальний криміналістичний запис.

15 / 91
3 threat-system alerts
Повідомитиmalicious
Повідомитиchecked — no match recorded
23 community references
Повідомитиprovider verdict: clean
Повідомитизбережений звіт
 Повідомити
12 перевірено — блокувань немає
40/100
ПовідомитиChecked; no threat flag recorded
Повідомити| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Private YARA rules | static.okx.com/cdn/assets/okfe/util/ont/5.8.53/ont.js |
audit | Hunting_JS_WebAssembly |
| Hagezi Threat Feed | www.zhgwexpouy.net |
malicious | Sinkholed |
| DNS4EU | www.zhgwexpouy.net |
malicious | Sinkholed |
PhishDestroy identifies cnouyi.org as an active generic phishing domain posing as a fraudulent investment gateway designed to harvest cryptocurrency wallet credentials and private keys. This domain appears to deploy a drainer kit tailored to siphon digital assets under the guise of 'investment opportunities' or 'portfolio management tools.' No specific brand is directly mentioned in available telemetry, suggesting a generic financial-themed lure rather than a targeted impersonation. The threat actor behind this domain uses obfuscated JavaScript and fake transaction prompts to trick victims into connecting malicious wallet extensions or entering seed phrases.
This domain exhibits multiple red flags verified through forensic analysis. cnouyi.org was registered on December 18, 2025, through Dynadot Inc., just days ago. It resolves to IP 54.215.31.113 and leverages a legitimate SSL certificate from Let's Encrypt to appear trustworthy. However, VirusTotal analysis confirms only 1 out of 95 security vendors currently detect this threat, and it remains unflagged by Google Safe Browsing (GSB) as of the latest scan. The domain has not yet appeared on major blocklists, indicating a newly active campaign with low detection coverage.
As of current intelligence, cnouyi.org is flagged as 'active' with elevated risk. Immediate action is recommended: block this domain at network and endpoint levels, update browser and DNS blocklists, and warn users to avoid accessing financial services links from unsolicited emails or social media. While the current risk is elevated due to low detection, rapid response can mitigate potential victimization. However, the absence from major blocklists and fresh SSL issuance suggests the campaign may expand quickly. Users are advised to verify all financial websites via official channels and never enter wallet credentials on unofficial portals.
Збережені дані спостережень за взаємодією веб-сканера та браузера для цього хоста, а також перевірка відбитків у режимі реального часу для систем розподілу трафіку типу «Кейтаро».
Примітка щодо сканера: redirect: raw=redirect_302; http=302; via=https_proxy; location=https://www.oyigwcn.systems/join/37602380
 (US)
ns2.dyna-ns.netLocation describes the IP network.
9ed5422f94375ea9c9c750f15732c9b26195cbc8c82e49d64b2c8fd5fb1fe925Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of cnouyi.org · checked Apr 19, 2026
10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Збережено 89 схожих доменів
Повідомив 1 учасник спільноти; уперше помічено 19.04.2026
Якщо ви ввели облікові дані облікового запису, особисту чи платіжну інформацію або завантажили файл із цього домену, негайно вживіть заходів. Нижче наведено ресурси, які допоможуть вам повідомити про інцидент і захистити себе.


Виберіть свою країну, щоб отримати офіційні контакти кіберзлочинців або створити проект скарги →.
Template-based draft · optional AI wording assistance requires separate consent
Кожна смуга позначає одну з причин, через яку домен пов’язаний із цим хостом. Розмір вузла вказує на виявлення VirusTotal, а вузли, позначені пунктирною лінією, вже не працюють. Повний перелік наведено нижче.
Однаковий хеш фавікону або однаковий заголовок сторінки, як у цього хоста.
Частина фішингової кампанії «Airdrop Scam». Переглянути всі домени кампанії →
Ця вихідна IP-адреса містить кілька фішингових доменів — інфраструктура може бути спільною для кампаній.
Ці домени також націлені на користувачів OKX. Переглянути всі загрози типу «OKX» →
Зареєстровані через одного й того самого реєстратора. Один реєстратор обслуговує мільйони клієнтів, які не пов’язані між собою, тому це лише об’єднує дані, а не доводить наявність зв’язку.
Нещодавно додані звіти з бази даних PhishDestroy. Ці посилання для виявлення не передбачають спільної інфраструктури чи власності.
Аналіз загроз за допомогою збереженого списку блокувань, WHOIS, DNS і загальнодоступних доказів сканування
Сканувати заразДодавайте підозрілі домени до нашої бази даних загроз — захищайте спільноту
ПовідомитиОстанні звіти про фішинг і помічені зміни доступності
ВідстежуватиСлідкуйте за актуальними загрозами або оскаржте цей запис, якщо вважаєте, що це помилкова тривога







