
Здійснюйте пошук серед відстежуваних доменів та переглядайте збережені докази, виявлені випадки та останні дані щодо доступності.
219,813
Загальна кількість відстежених
213,488
Виявлено VT
91,906
Останнє підключення: активний
127,907
Недоступний під час останньої перевірки
563
VT — у процесі розгляду
How This Attack Works
Gambler Scam Panels exploit the allure of gambling to deceive users and extract financial information. Here's a breakdown of how these scams typically unfold:
STEP 1
Enticing Offer
Scammers create convincing gambling websites offering attractive bonuses or winnings.
STEP 2
User Engagement
Victims are drawn in by the promise of easy money and create accounts on these fraudulent platforms.
STEP 3
Data Collection
Scammers collect sensitive personal and financial data under the guise of account verification.
STEP 4
Financial Exploitation
Collected data is used for unauthorized transactions, leading to financial loss for the victim.
Technical Analysis
Gambler Scam Panels often utilize spoofed gambling websites that mimic legitimate platforms. Attackers use phishing kits to create replicas of popular gambling sites, embedding malicious scripts that capture user data. These sites are hosted on domains registered with less-regulated registrars like NICENIC INTERNATIONAL GROUP CO., LIMITED, WEBCC, and Dominet (HK) Limited. Additionally, they may leverage obfuscated JavaScript to hide malicious activities from casual inspection. In some cases, these scams involve fake cryptocurrency gambling, where smart contracts are manipulated to always favor the scammer, utilizing functions that are poorly documented and hard to audit.
Real Cases
SpinWin Scam (2024)
$2 million stolen
Users were lured by promises of high returns on a fake cryptocurrency gambling site, resulting in significant financial losses.
QuickBet Fraud (2023)
$1.5 million stolen
This scam used a well-designed imitation of a major gambling platform to collect user data and funds.
LuckyStrike Hoax (2024)
$3 million stolen
A fake lottery site that promised huge winnings but instead harvested sensitive financial information from users.
How to Detect
Unusually high bonuses or winnings promised
Poor website design with multiple typos
Unsecured website (missing HTTPS)
Unusually urgent demands for personal information
Домен registered recently with a non-reputable registrar
How to Protect Yourself
1
Verify the legitimacy of gambling sites before using them
2
Use secure passwords and two-factor authentication
3
Be wary of sites with unsecured connections
4
Regularly monitor financial statements for unauthorized transactions
5
Звіт suspicious sites to authorities and platforms like PhishDestroy
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 10,176 domains tracked for this threat type
Gambler Scam Panel 10,176 domains

zoabux.com

zozwex.com


1-win.rest

1-xbet.club

1rolls.cc

50centx.us

777-betspin.com

7dino.com

abadonbet.com
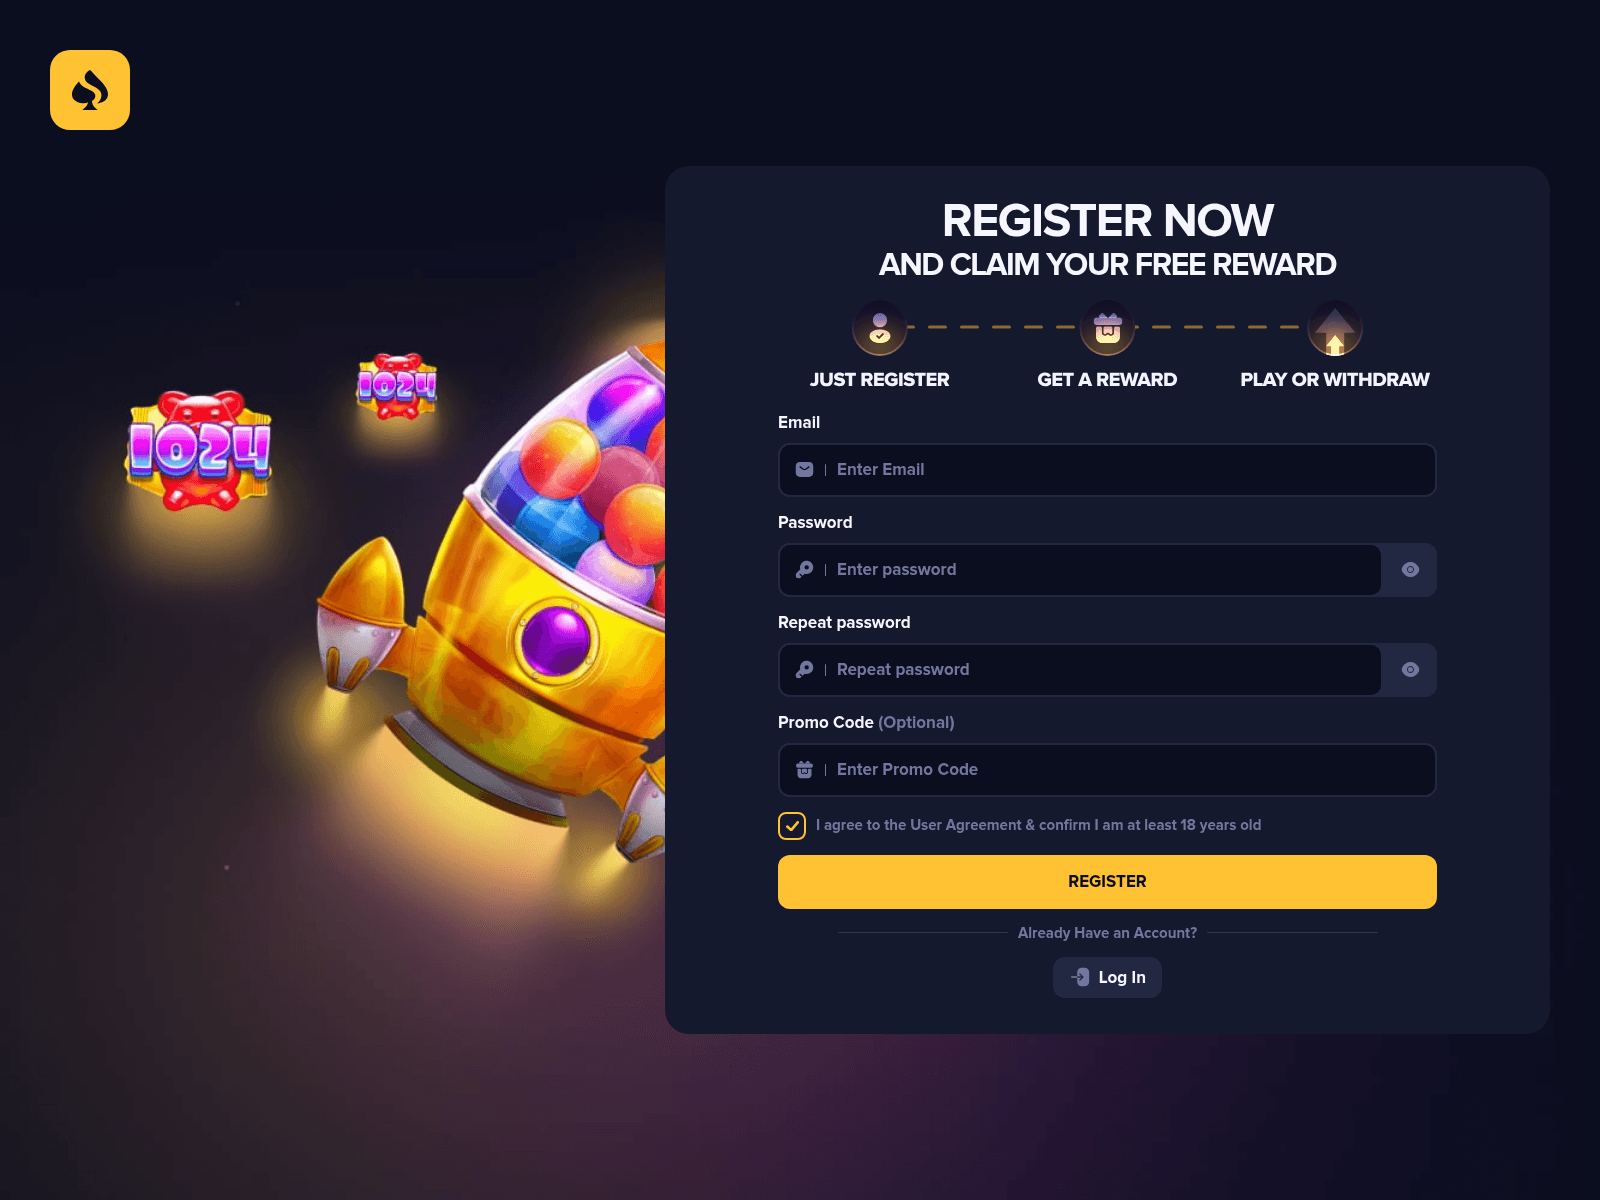
acey.win

aemobet.com

airswipe.cc

ankabox.com
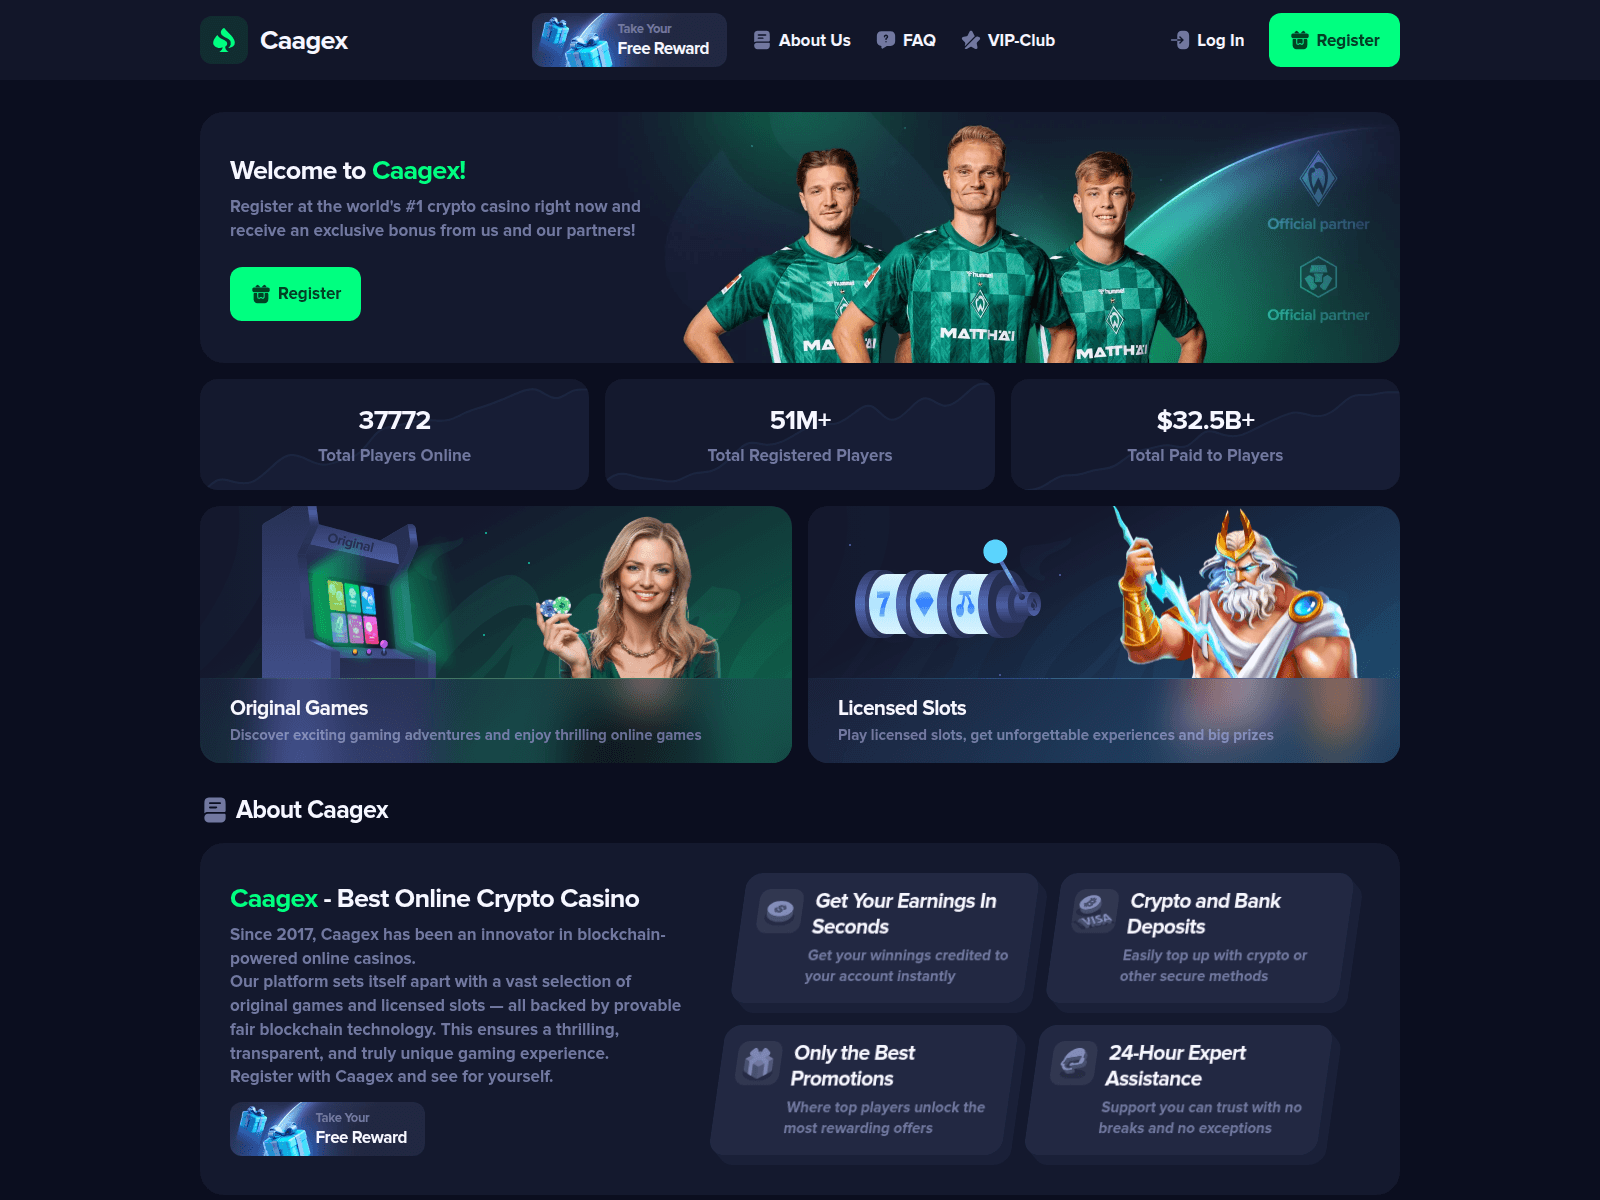
app.caagex.com
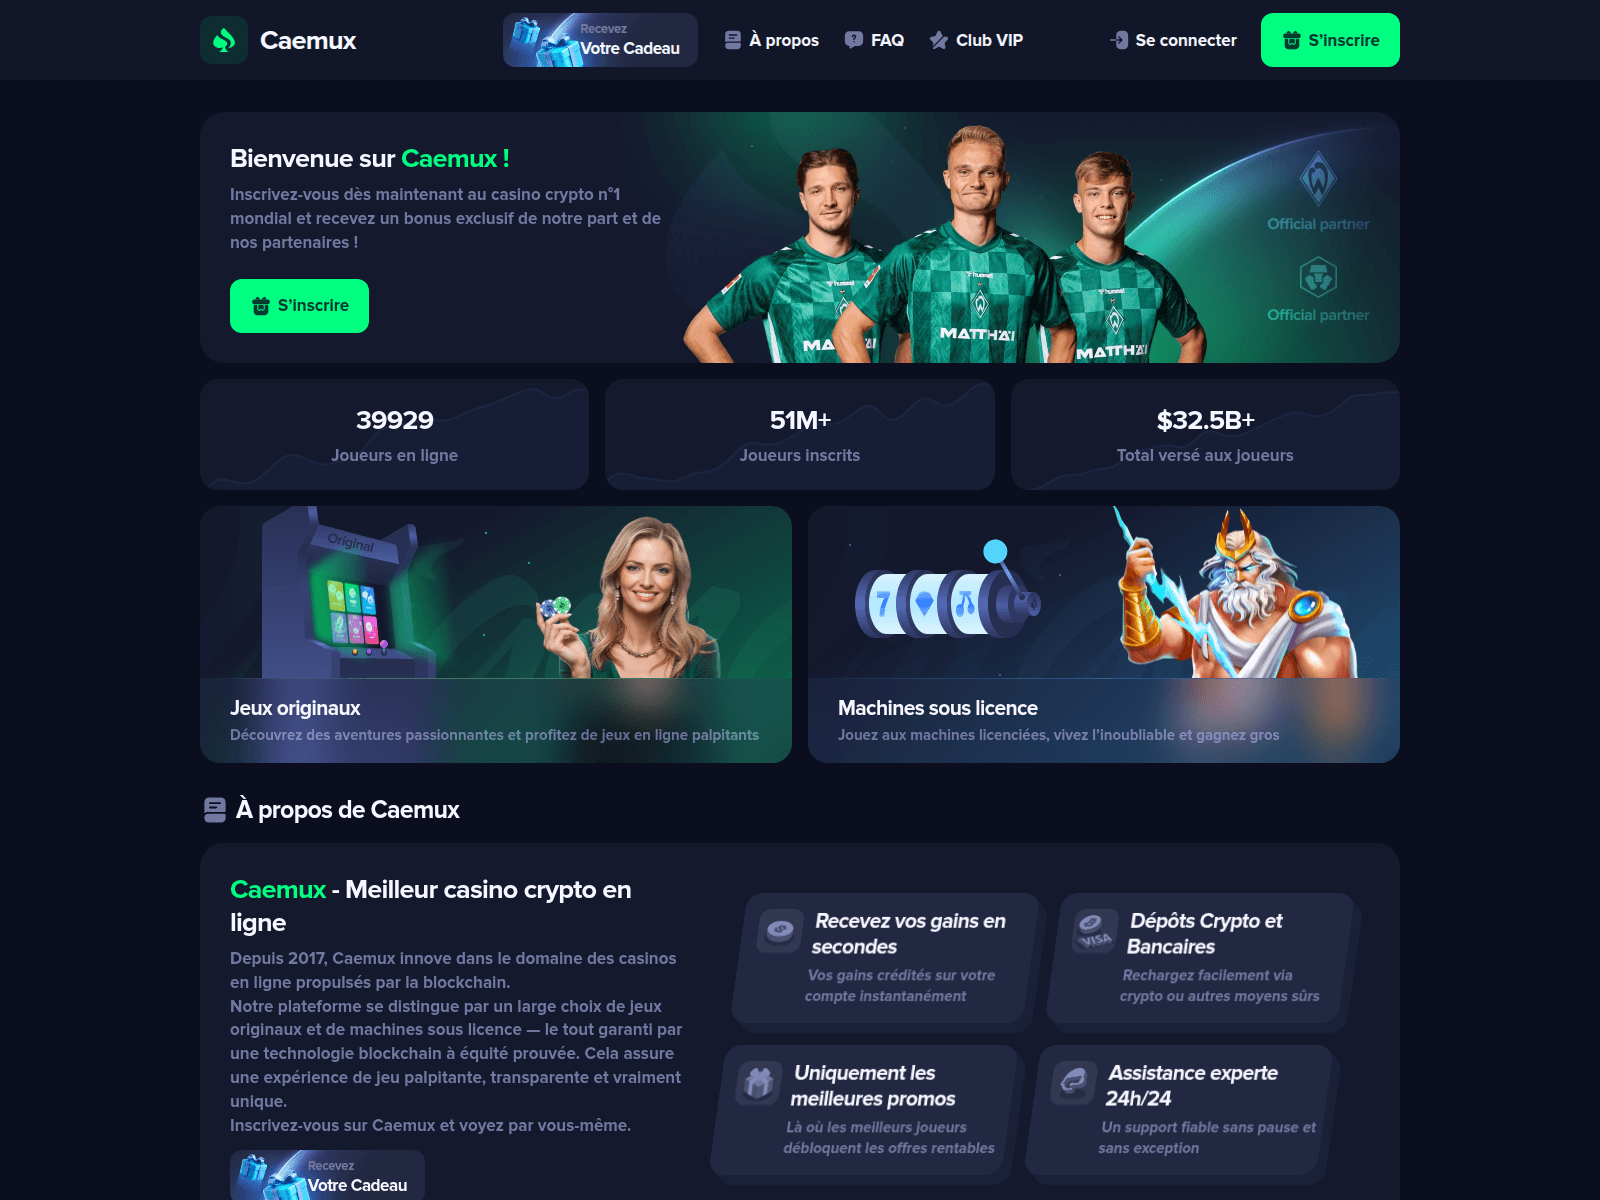
app.caemux.com

app.coavox.com
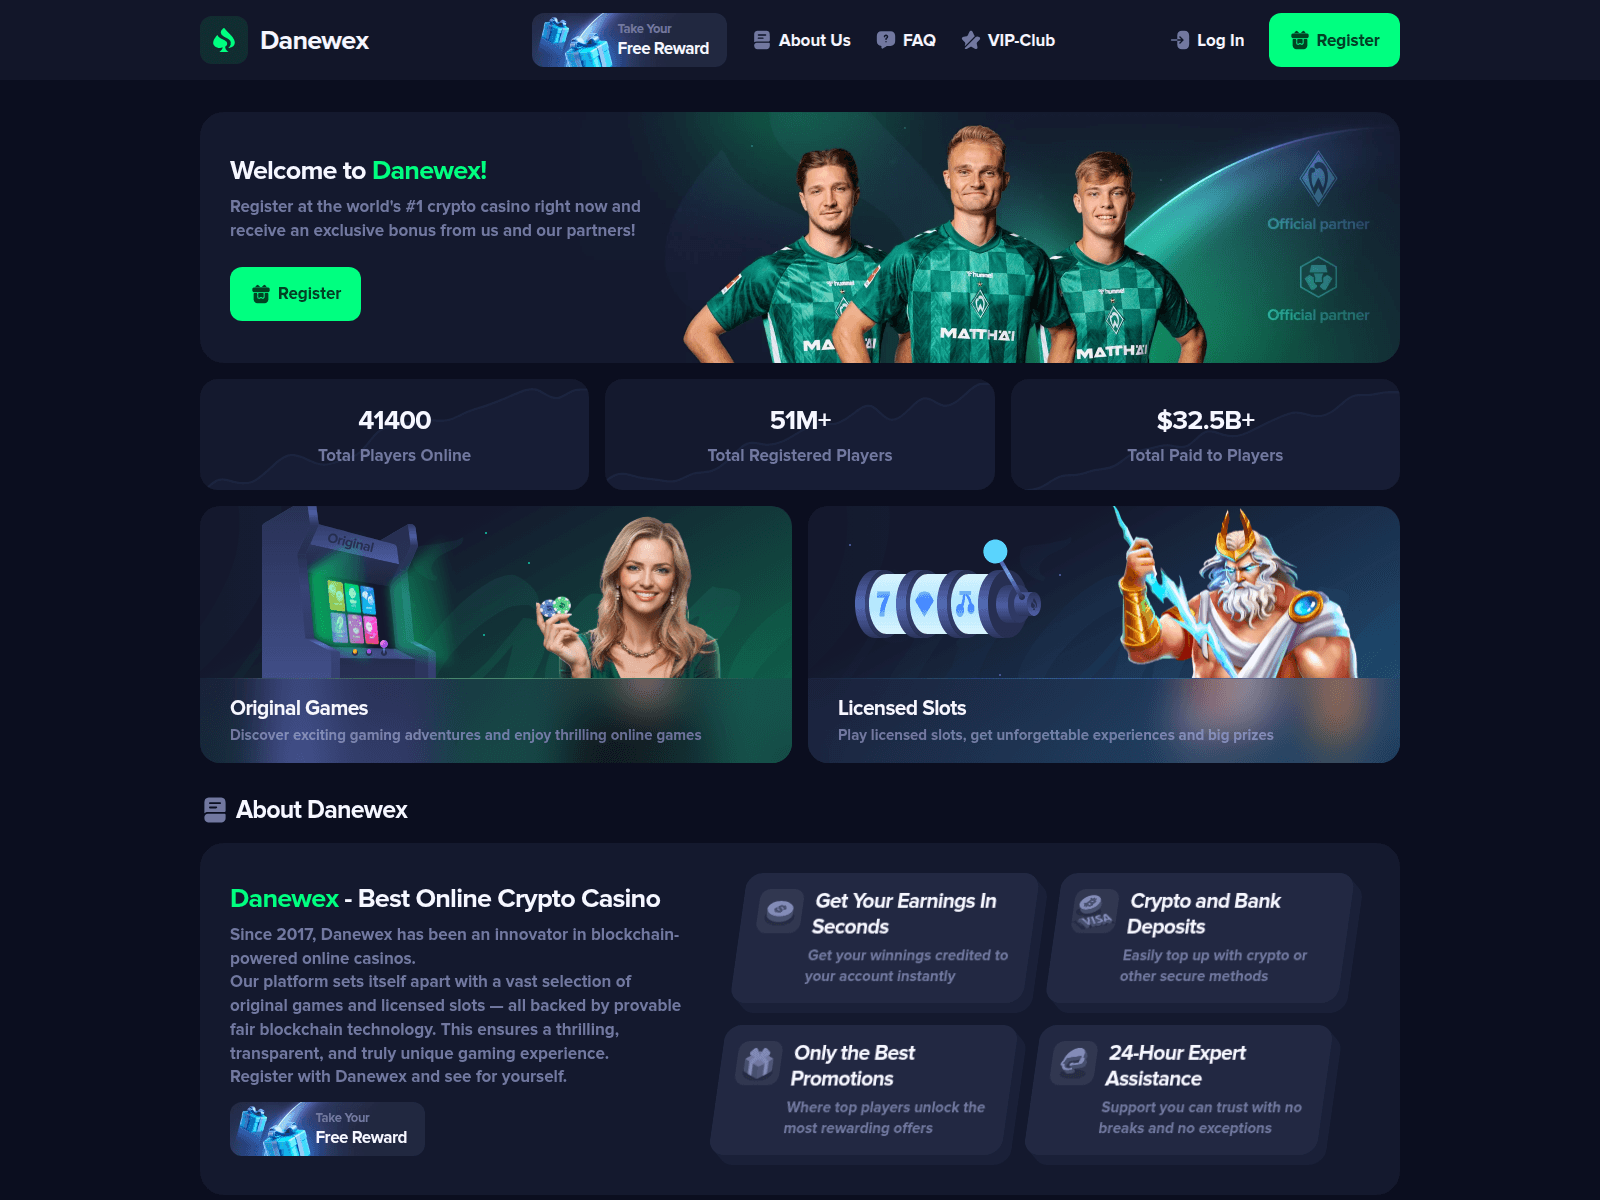
app.danewex.com

app.jaovex.com

app.paezax.com

arcace.net

arixswin.com

atazino.at

aviabet.pro

baorax.com

baronplace.com

beasterox.com
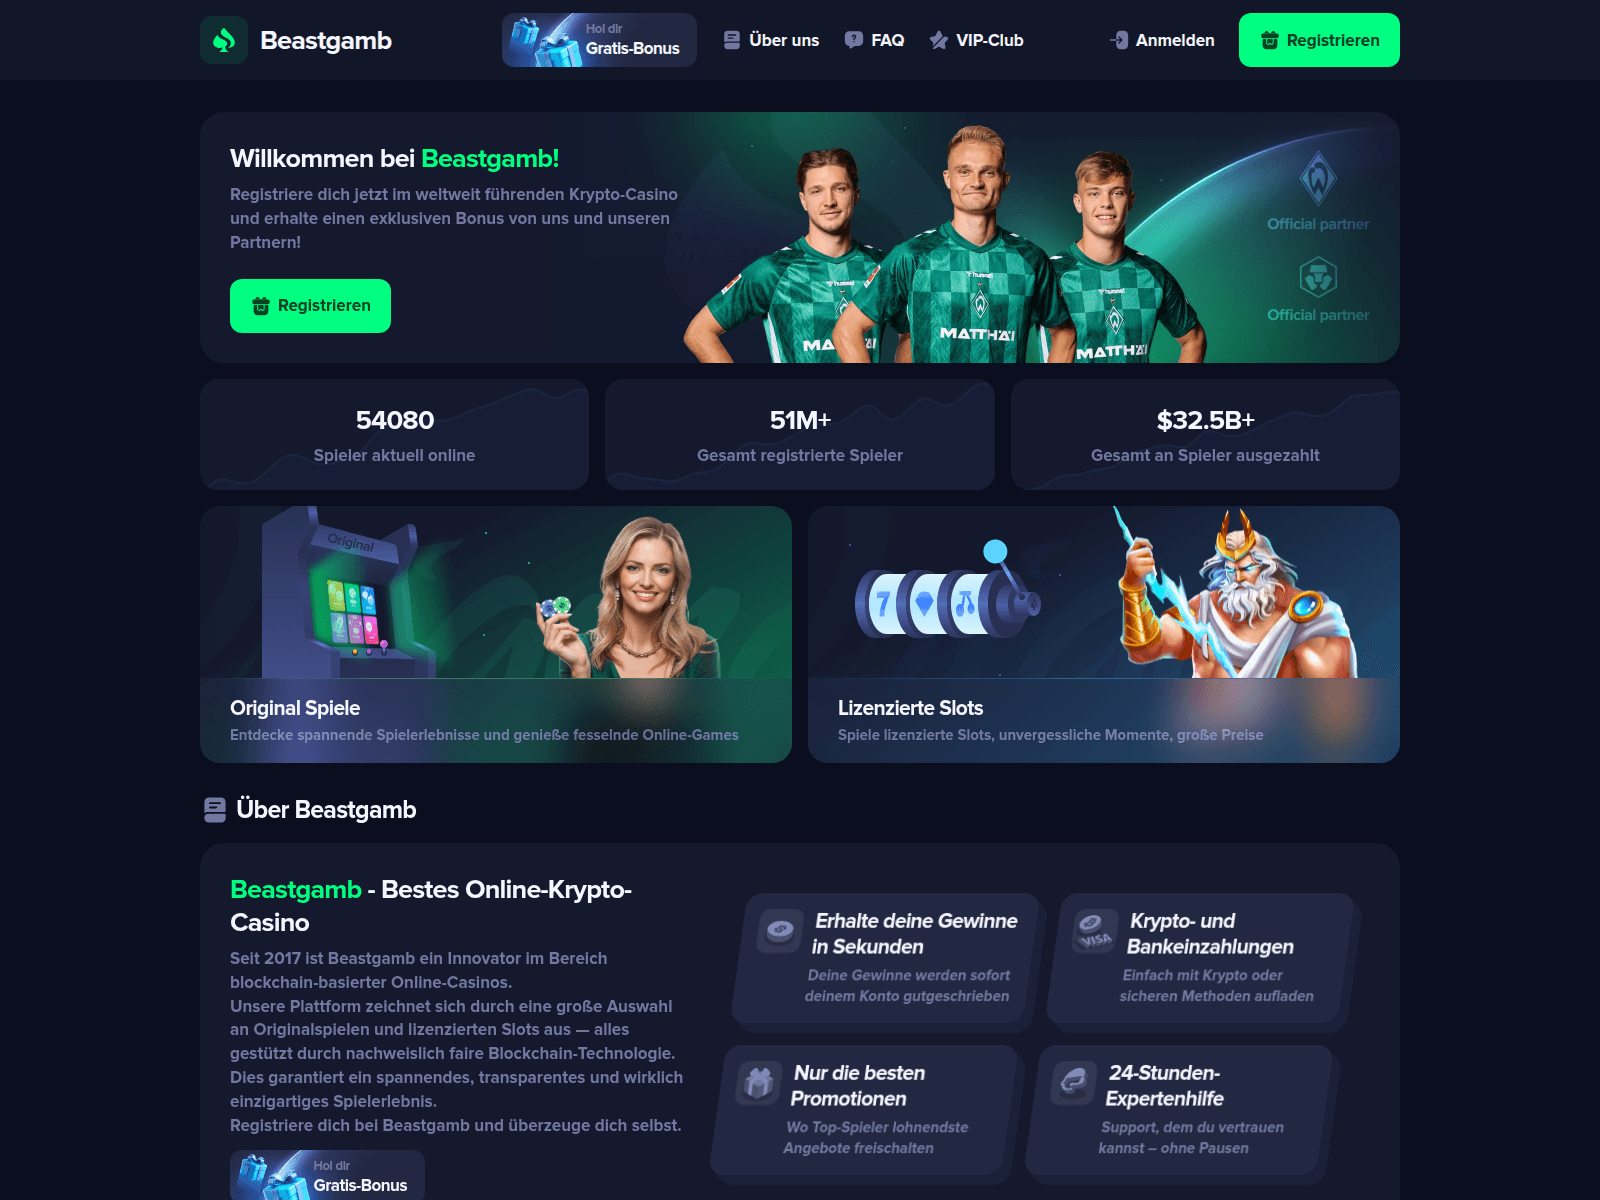
beastgamb.com

begambl.com

begofex.com

benewix.top

beorax.com

beowux.com

berodex.com

besgamb.cc

besowin156.pro

bestslotscasino.sbs
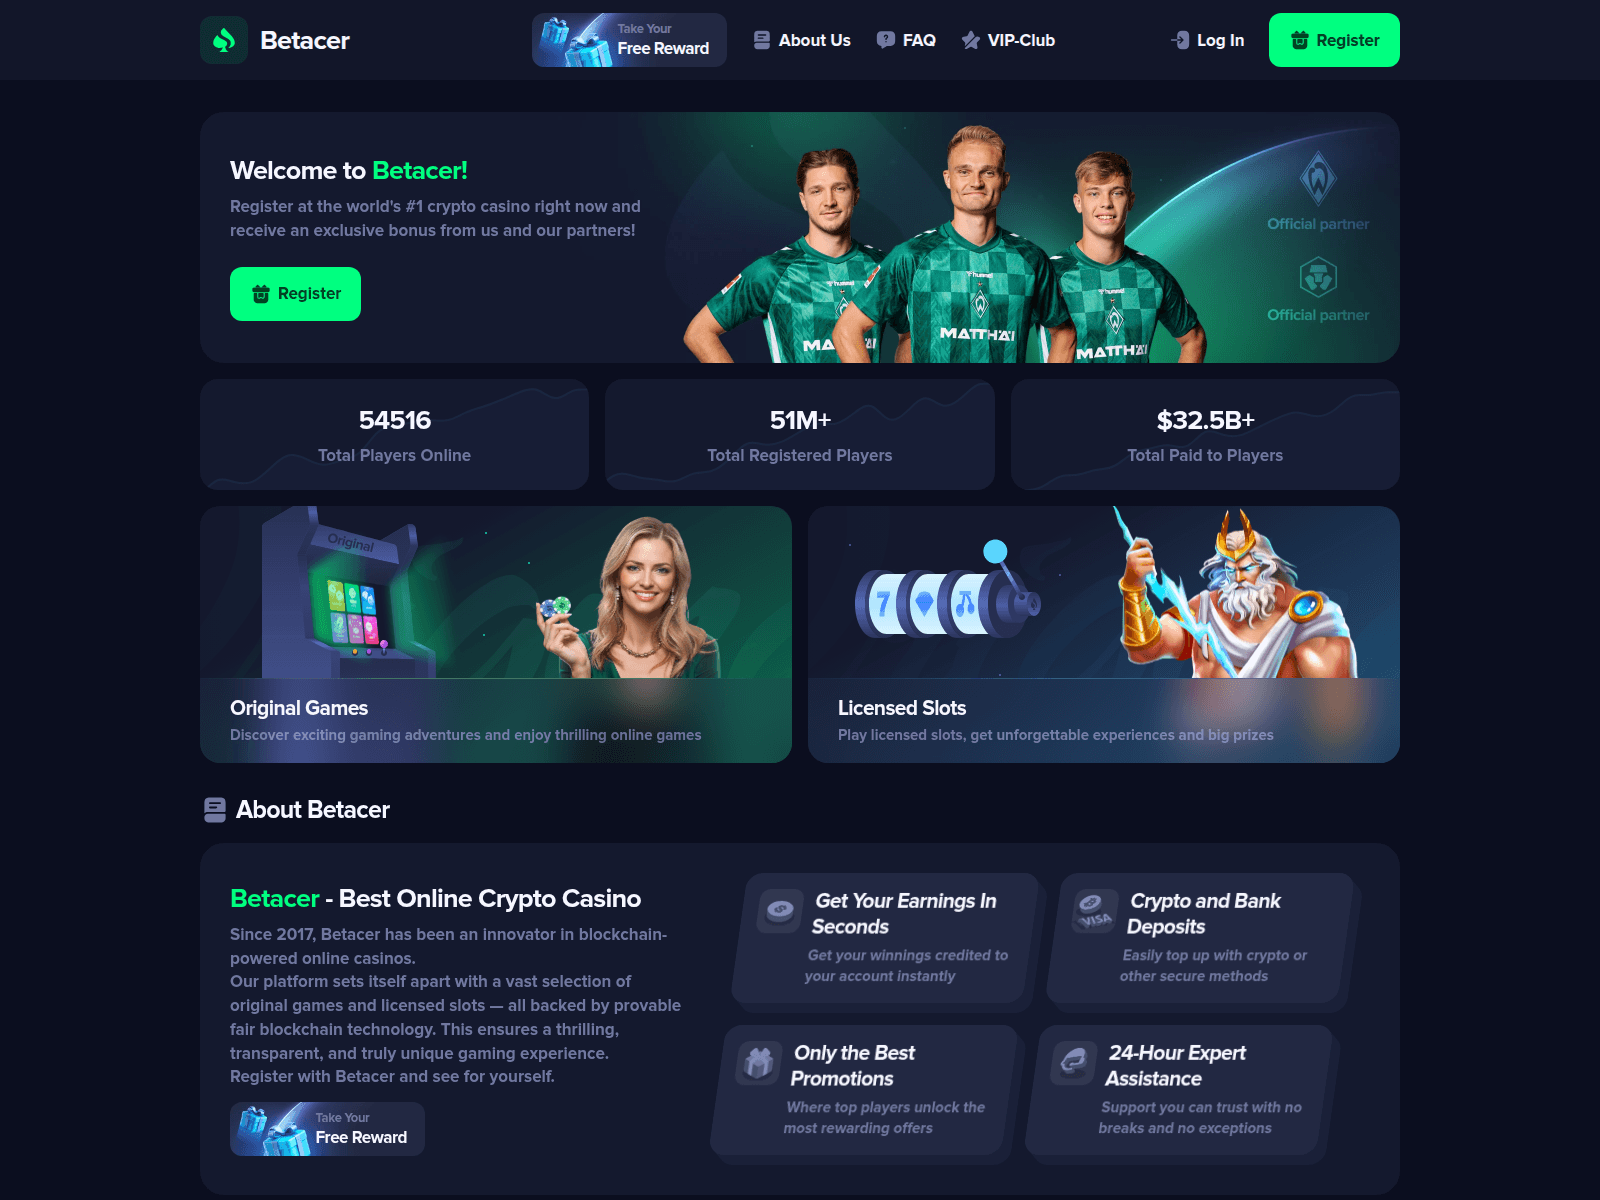
betacer.com

betaxar.com

betclub.cc

betexar.com

betkingdom.cc

betnoks.com

betrawin.com

betzillion.cc

betzu.cc

bigspin.cc

bigspins.bet

bigwinner.click

bisowex.com

bitroyale.pro

bitsler.fun

bixcas.com

blazzex.com

blyze.world

boanex.com

boegux.com

borncas.com

botawin.com

bregamb.cc

btgamb.com
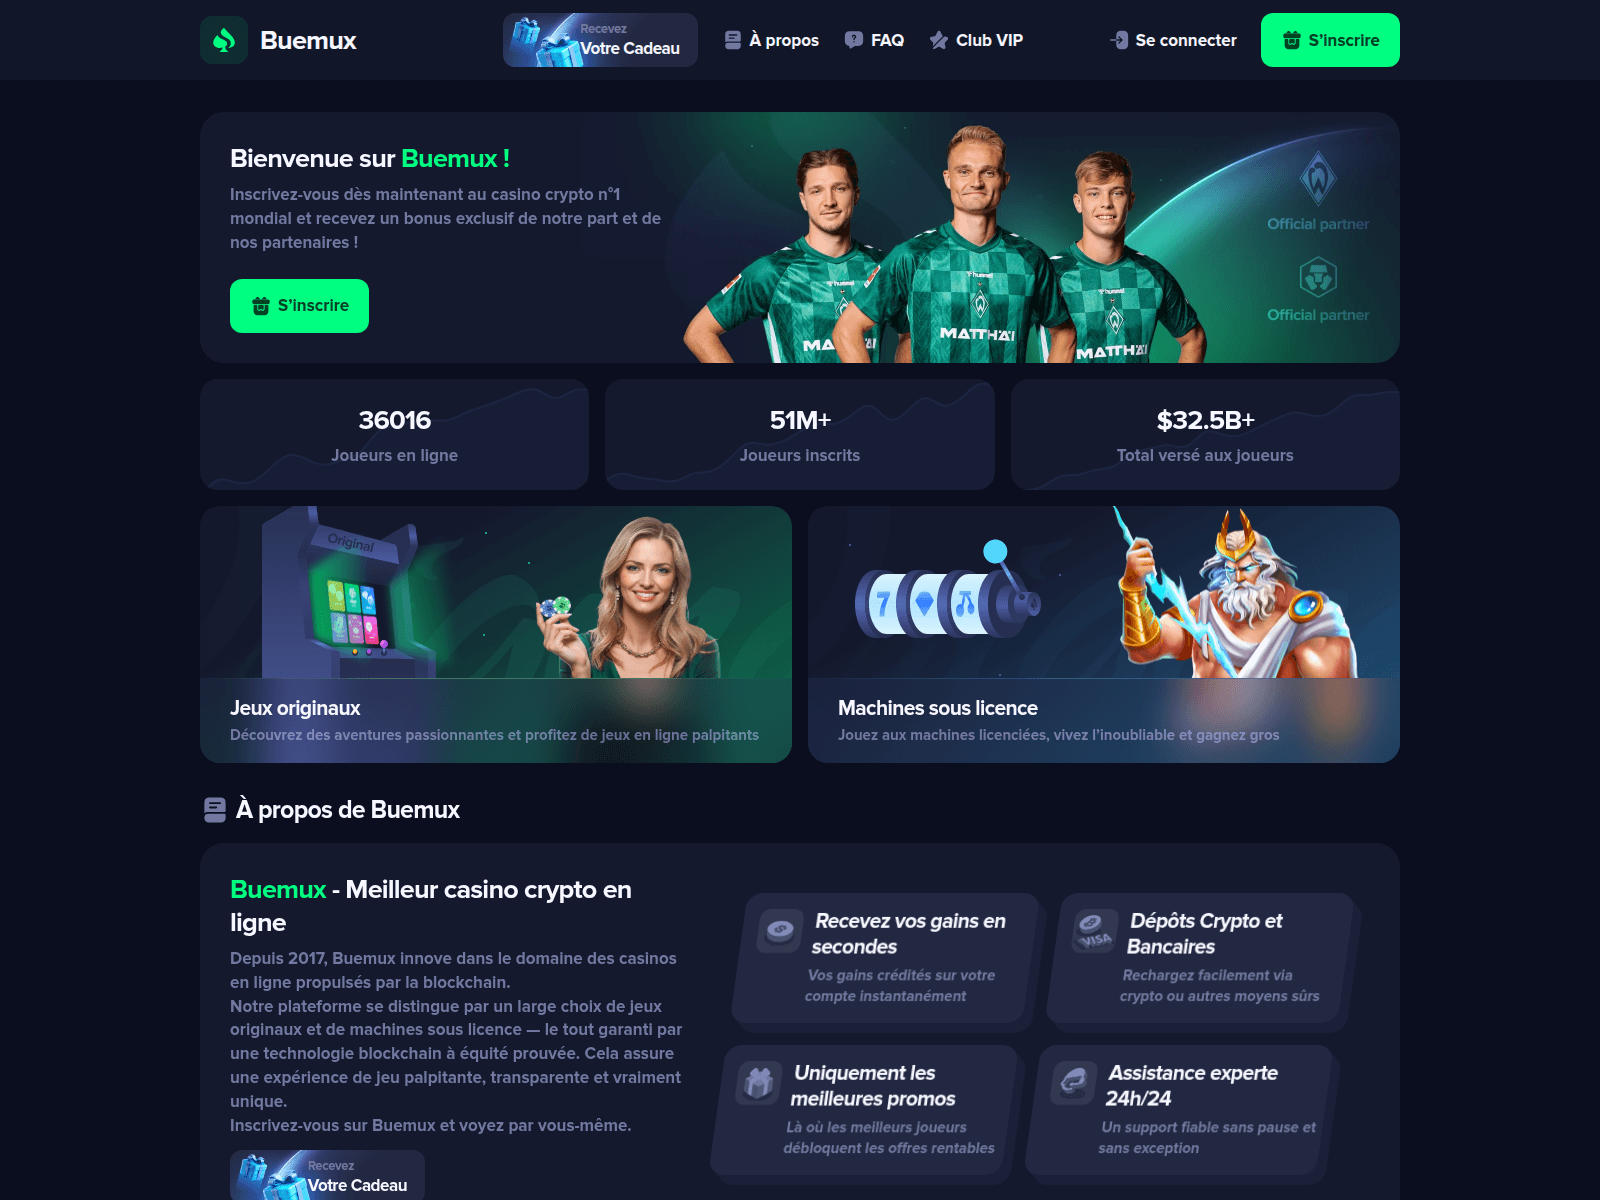
buemux.com
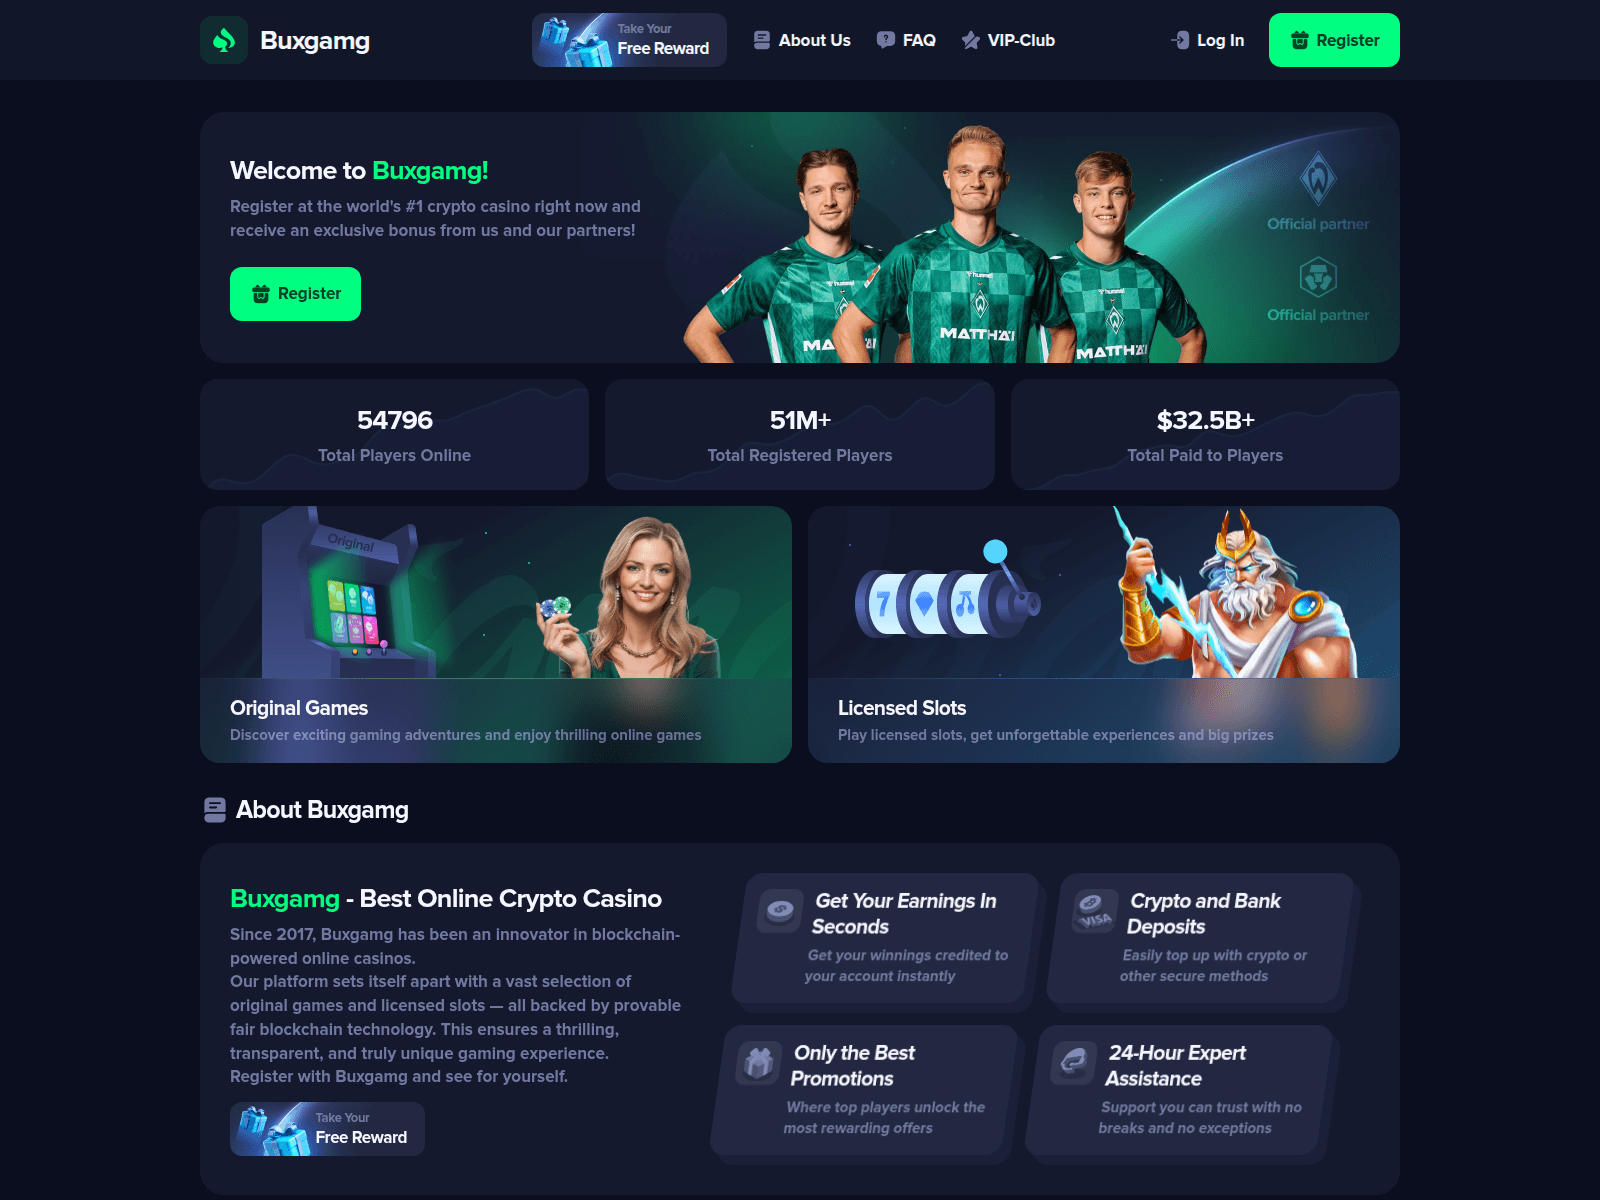
buxgamg.com

buzawin.com

cas5g.com

casg7.com

casgolden.com

casgrok.com

cashbet-x.com

cashcuz.com

casino-bets.me

casino.rackswin.com

casnax.com

caziwex.com

cenatplay.com

cenatx.com

cent50.bet

centslot.bet

chanced.bet
chupwin.com

ciodex.com

clarx.cc

cloxwin.com

coin-casinos.cc

coinluckyroll.net

coinsino.pro

coraslots.net

crashoracle.world

crownspin.cc

damespin.com
Процес реагування на загрози Pipeline
Як перевіряється кожен домен у цьому хабі та як нейтралізуються підтверджені загрози. Повна візуалізація технологічного процесу →
Перевірки даних про загрози— кожен домен проходить сканування та перехресну перевірку щодо:
urlscan.ioЗнімок екрана · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ЗвітCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Безпека FiltersQuad9 · AdGuard · CleanBrowsingWeb-ПеревіритиFull surface scan
 crt.sh
Глобальна синхронізація постачальників— підтверджені випадки передаються 29 партнерам:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecОгляд сайтуAviraCloud detectionAvast / AVGWeb Shield«Касперський»OpenTIPDr.WebOnline scannerNetcraftЛіквідація APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ЗвітHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust