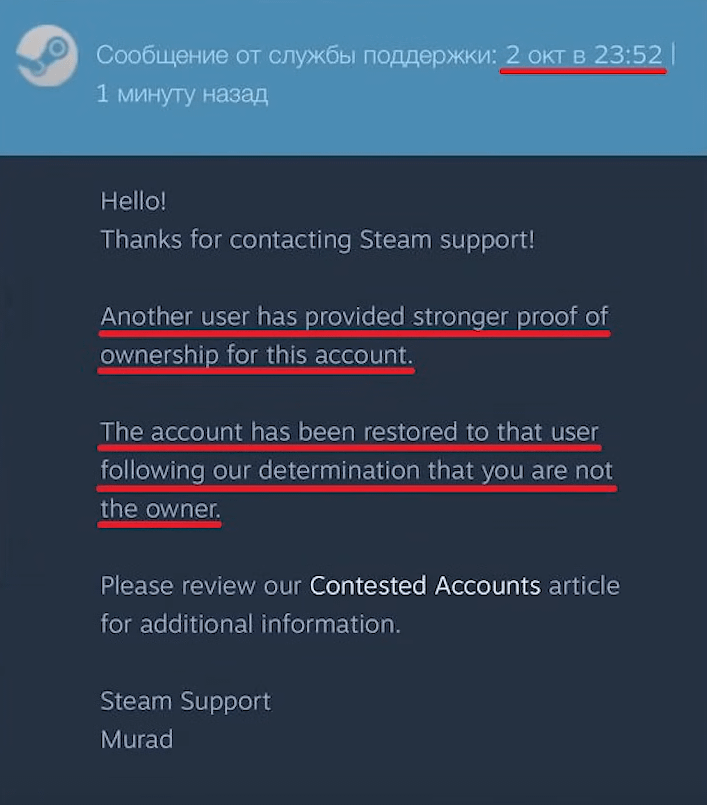
The Canned Refusals & Support Closures
Valve claims in marketing and forum posts that it operates an active enforcement regime protecting user security. In practice, victims of account hijacking, API redirection scams, and automated inventory drainage encounter an institutionalized, copy-paste refusal machine that closes tickets with zero human investigation.
Forensic Evidence: The Three Core Pillars of Support Refusal
The Roger Admission: API MitM Confirmed
In ticket response #1cp582i, Steam Support staff "Roger" admits in writing that attackers cancel legitimate trades via API and swap them with clone bots in milliseconds, but refuses to restore items and tells the victim to seek a "local PC technician".
7-Day Trade Hold Inaction
A victim provided SteamID64 of the hacker's accounts during the 7-day trade hold window. Support staff "Artem" and "Ilya" refused to freeze the stolen items, citing virtual item scarcity, and closed the ticket with an automated template.
Market Scarcity Over Property Rights
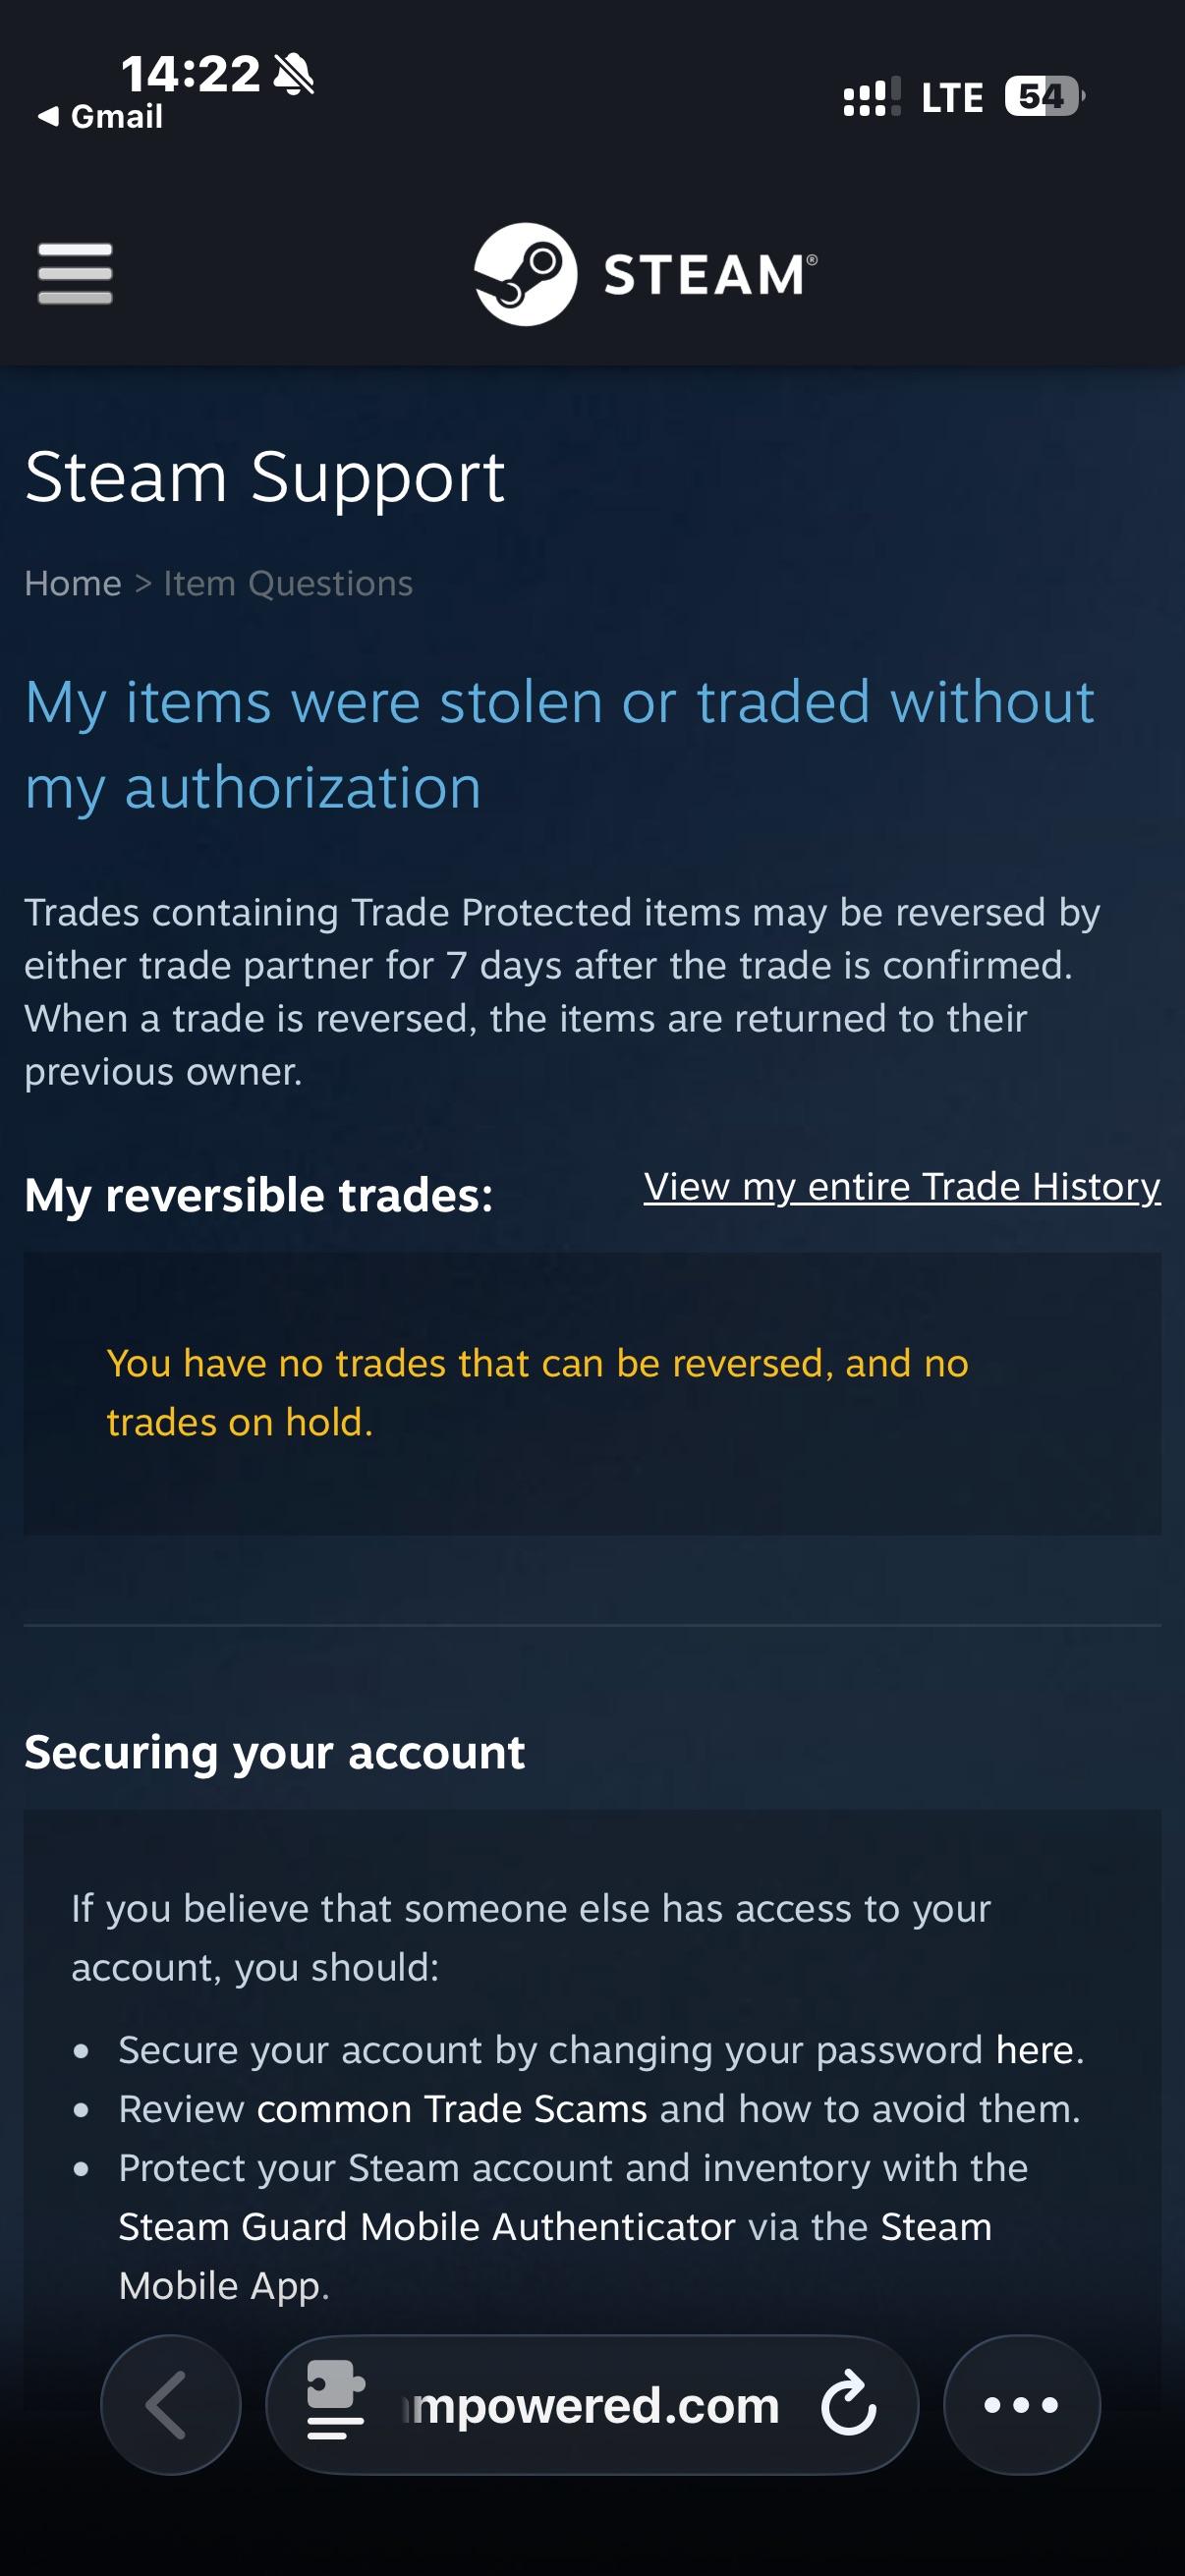
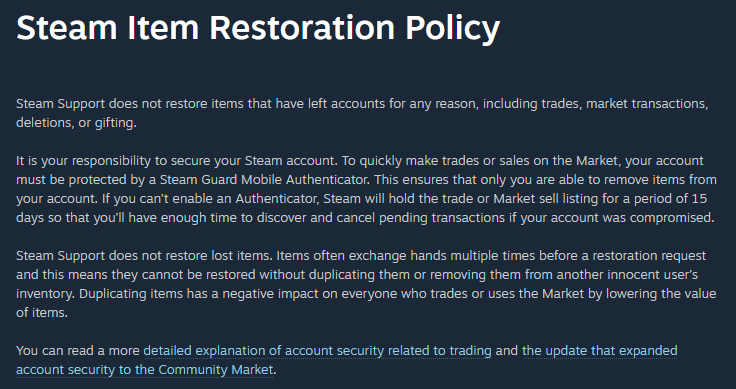
Valve's official Item Restoration Policy explicitly states that items are not returned because restoring them would "reduce scarcity and inflate the economy, lowering the value of items on the Community Market".
The Earliest Recorded Trade Substitution (22 March 2018)
Exactly one week before Valve imposed its controversial 7-day trade cooldown on Counter-Strike items, the trading community discovered the first live instances of the Steam Web API Trade Redirection exploit. Attackers hijacked web sessions to generate an unauthorized API key at steamcommunity.com/dev/apikey without mobile 2FA confirmation, enabling bots to cancel and swap trades in real time.
Verified Evidence Exhibits (137)
I lost many of my items and if theres a chance i could get it back : r/SteamScams
Was there case of someone getting back their items after scam ? : r/SteamScams
I lost many of my items and if theres a chance i could get it back : r/SteamScams
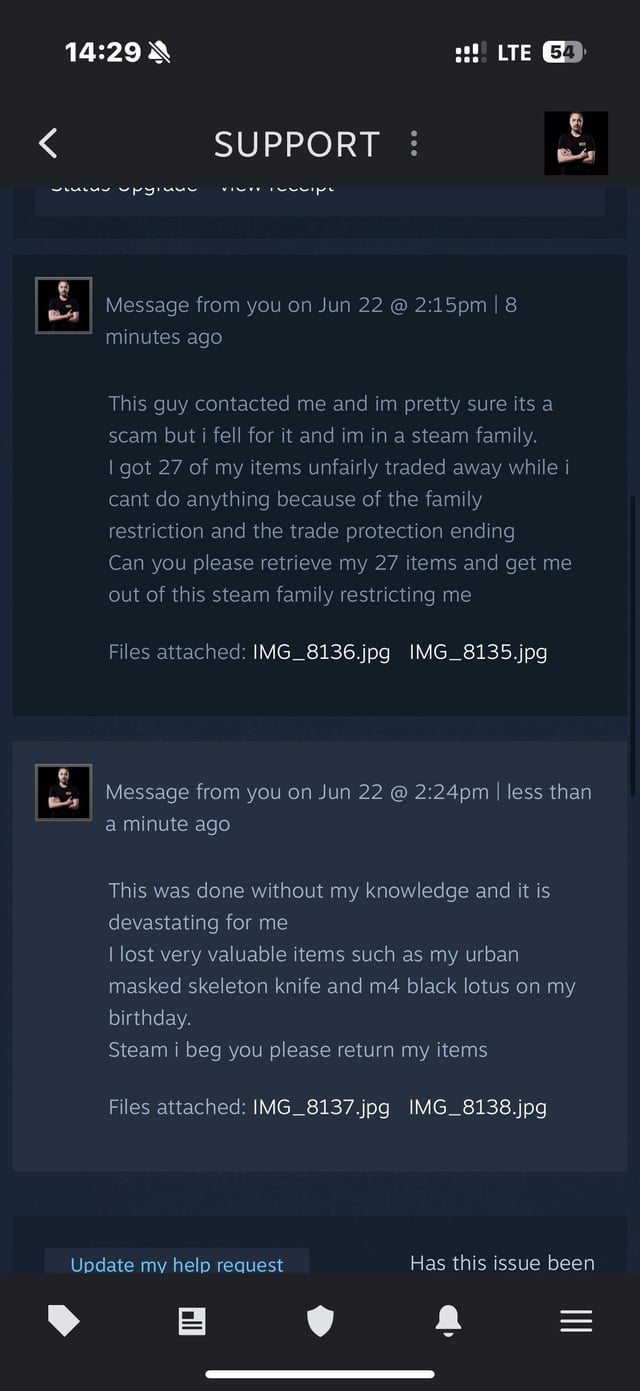
I lost many of my items and if theres a chance i could get it back : r/SteamScams
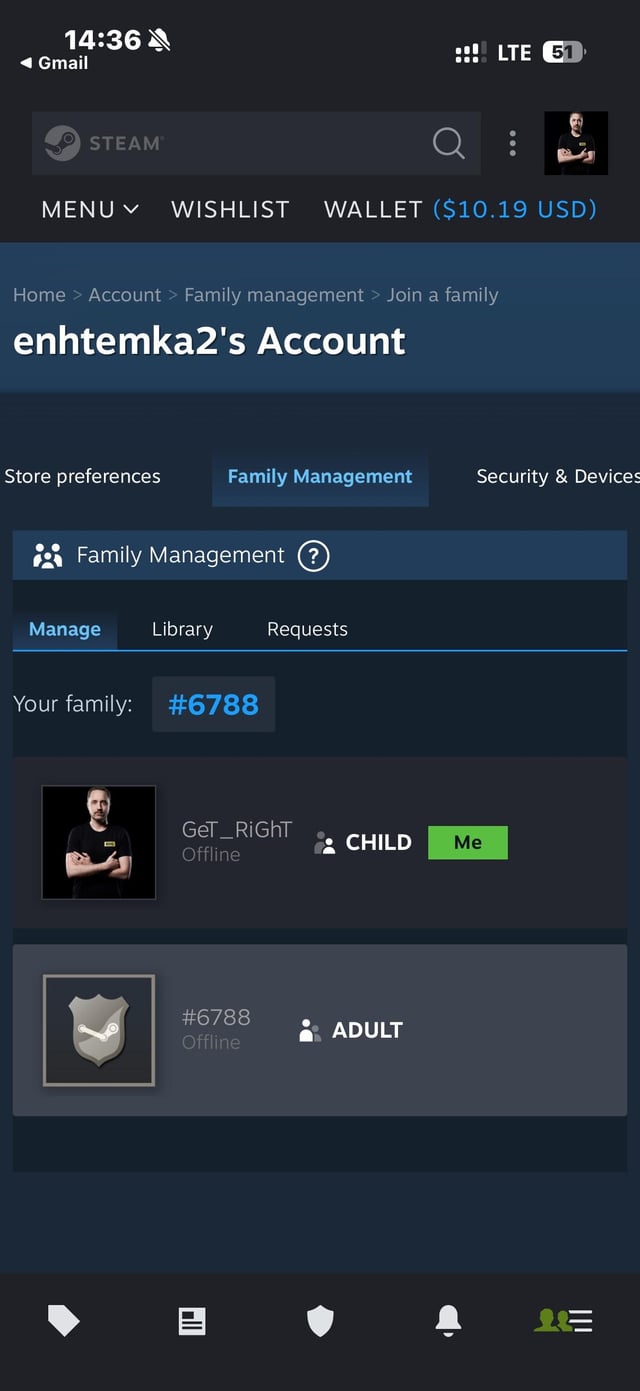
I lost many of my items and if theres a chance i could get it back : r/SteamScams
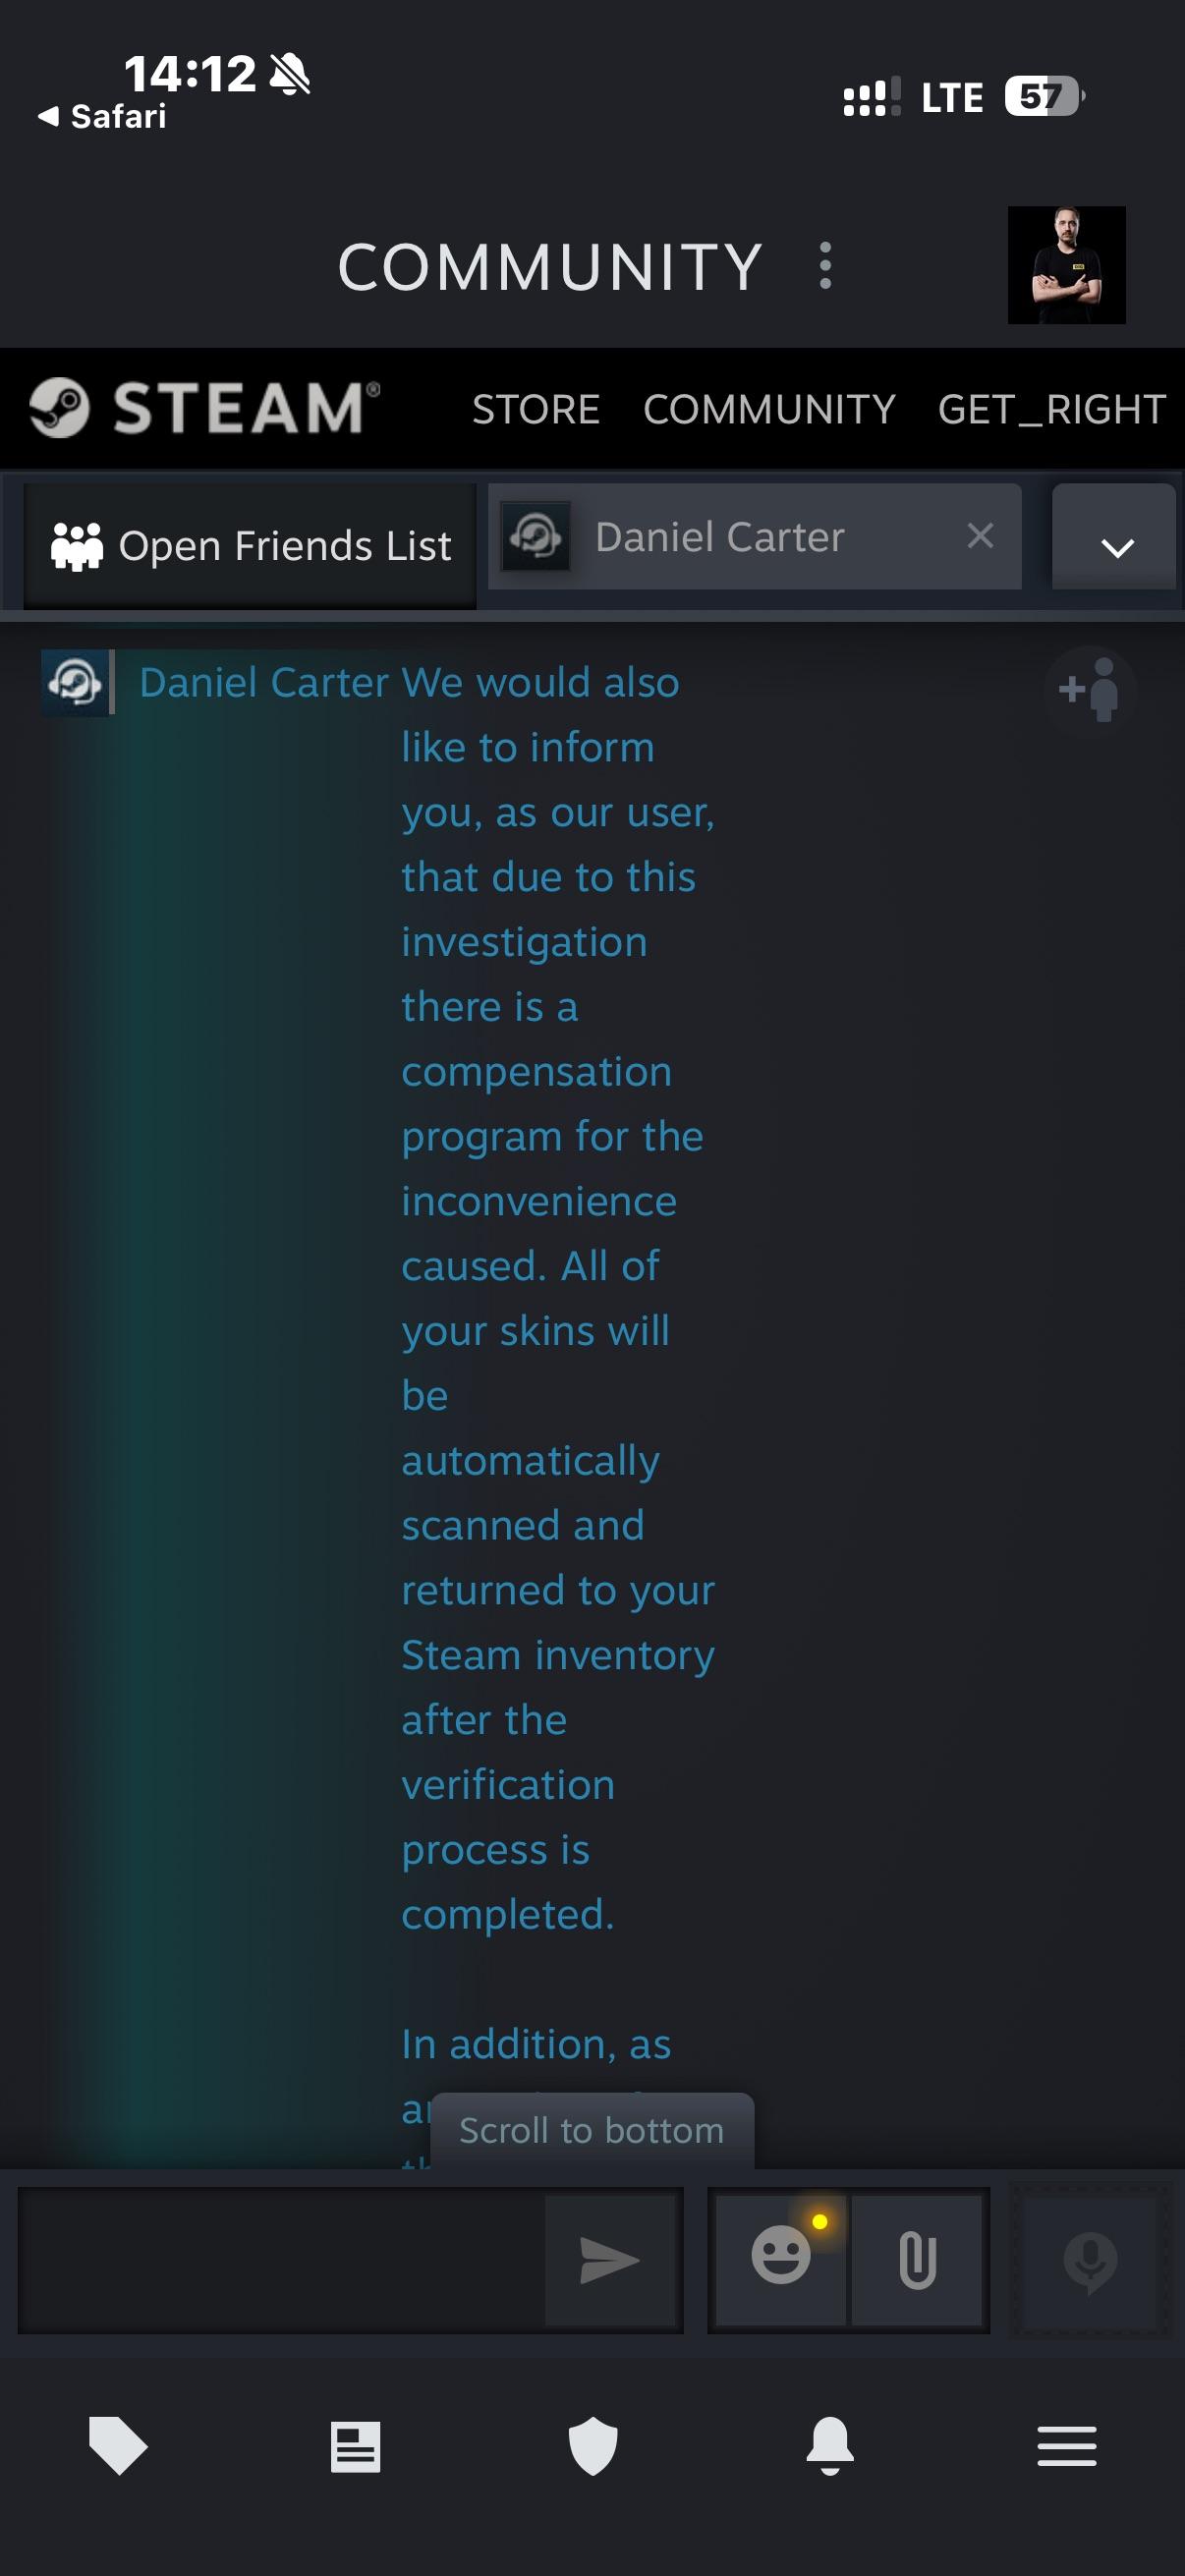
I lost many of my items and if theres a chance i could get it back : r/SteamScams
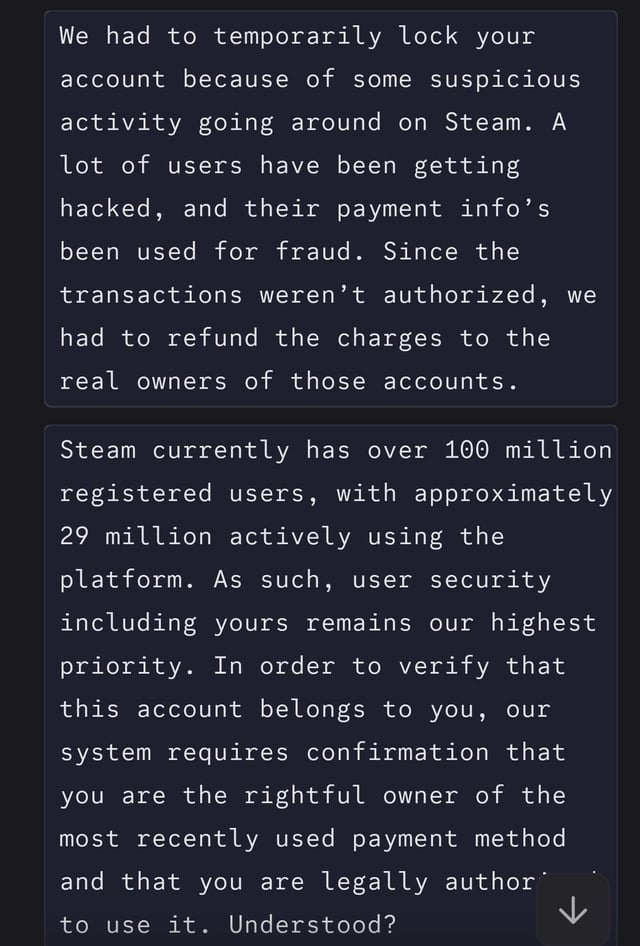
Is this normal with the Steam Support : r/Steam
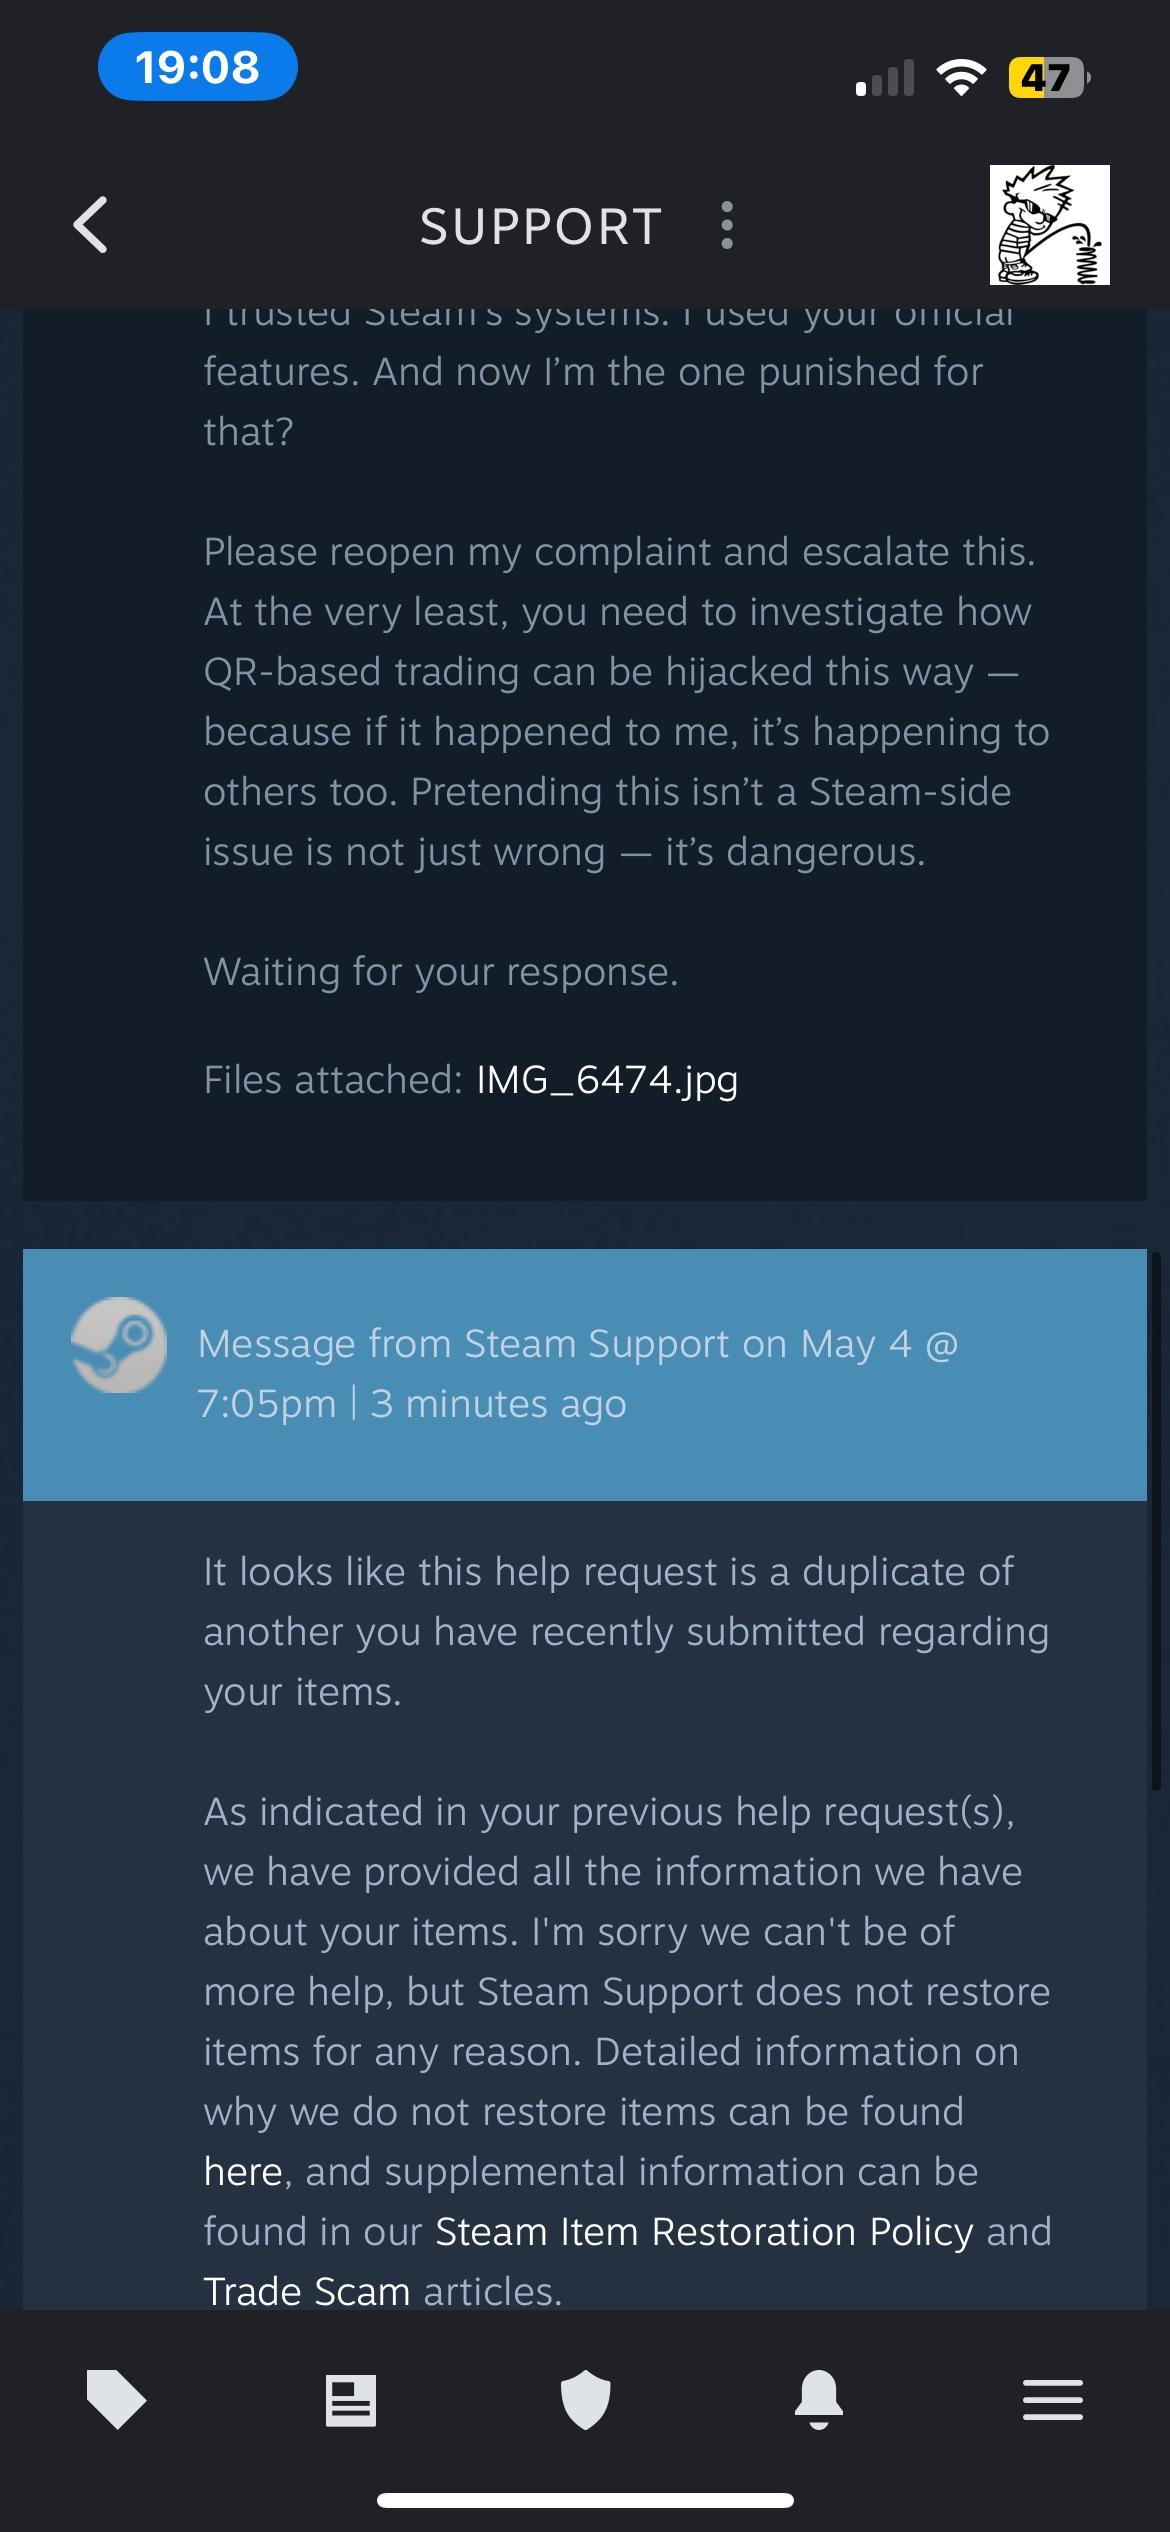
Steam Trade QR Scam – My Inventory Got Stolen and Support Closed My Ticket Without Helping : r/SteamScams
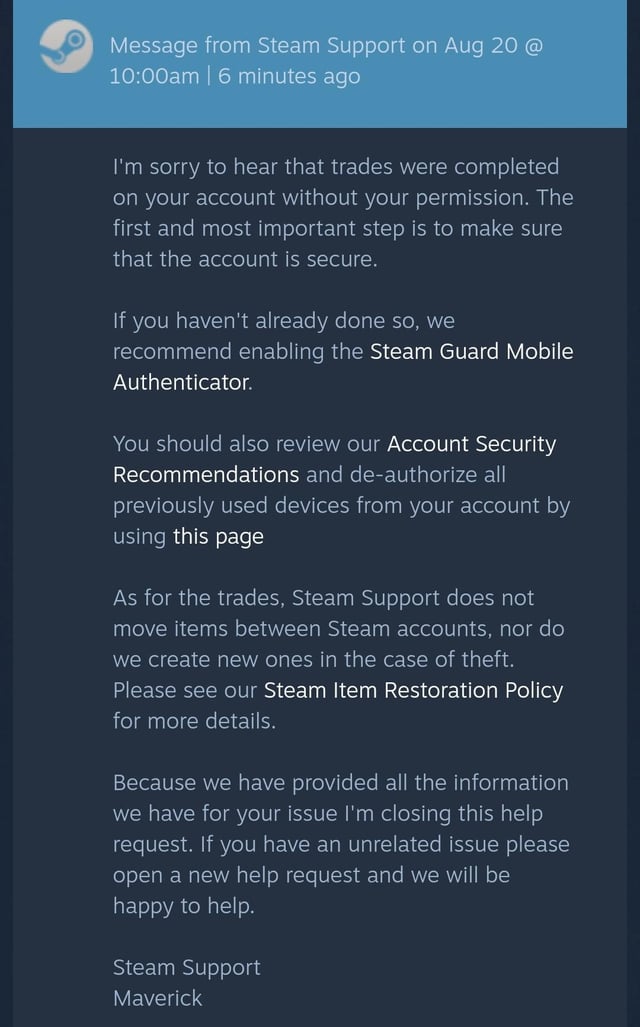
Hacked.. : r/cs2
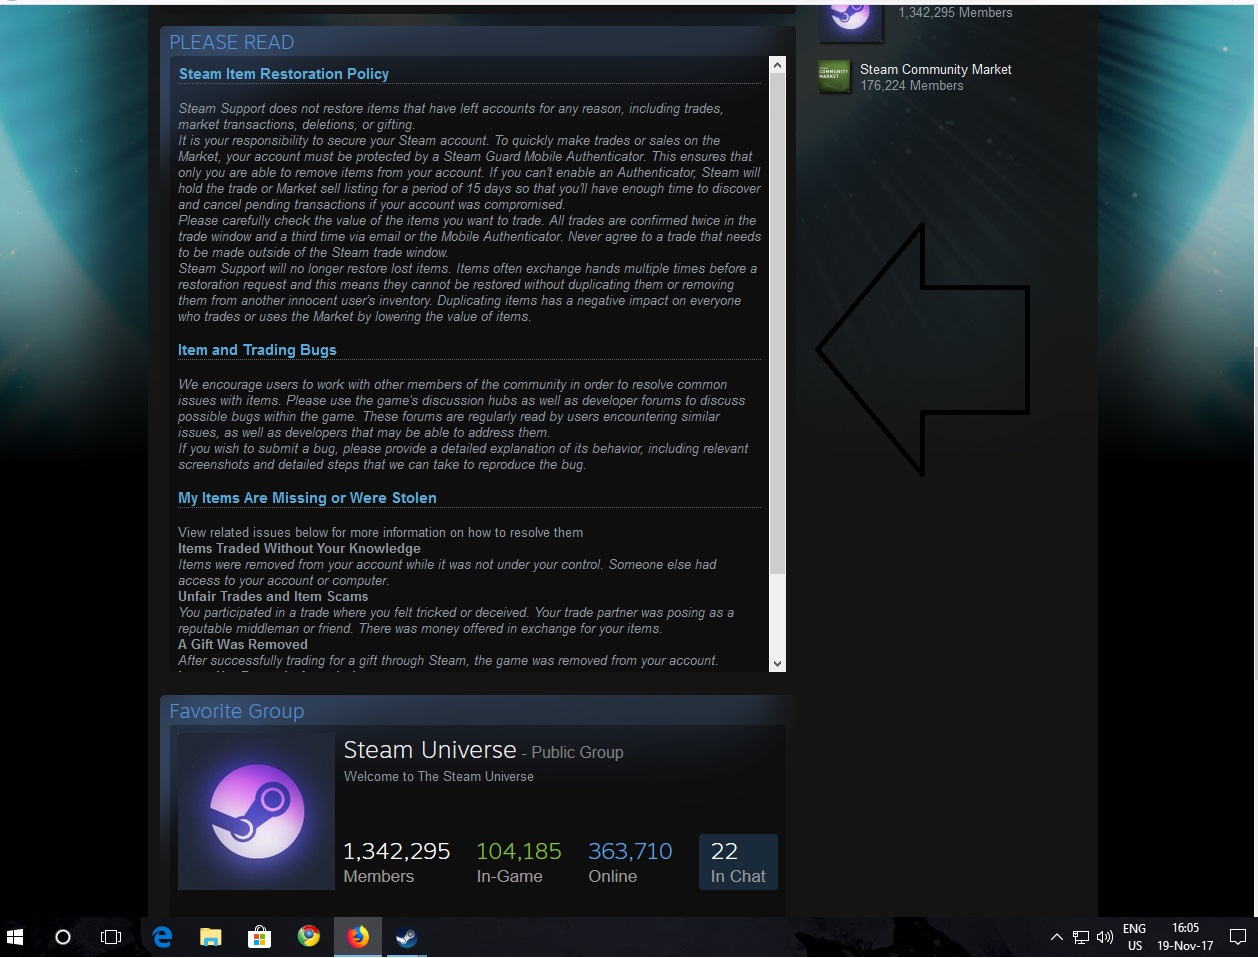
Steam 커뮤니티 :: 가이드 :: How to recognize a scammer
Сообщество Steam :: Руководство :: All scam methods explained!
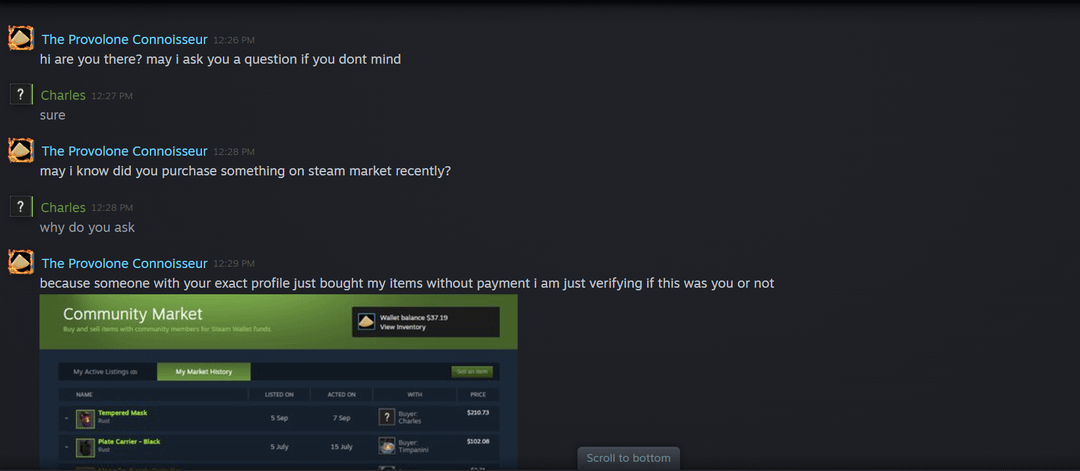
Fraud supposedly lol : r/Steam
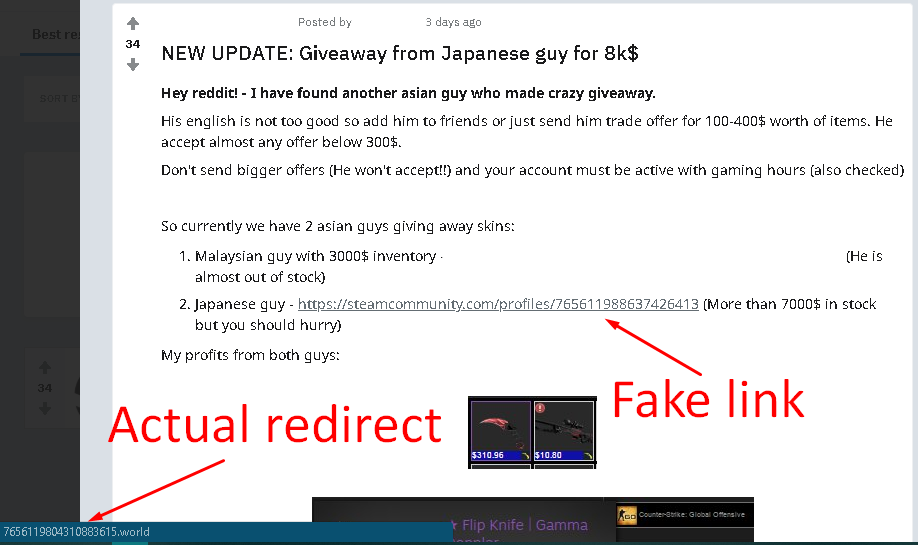
Сообщество Steam :: Руководство :: All scam methods explained!
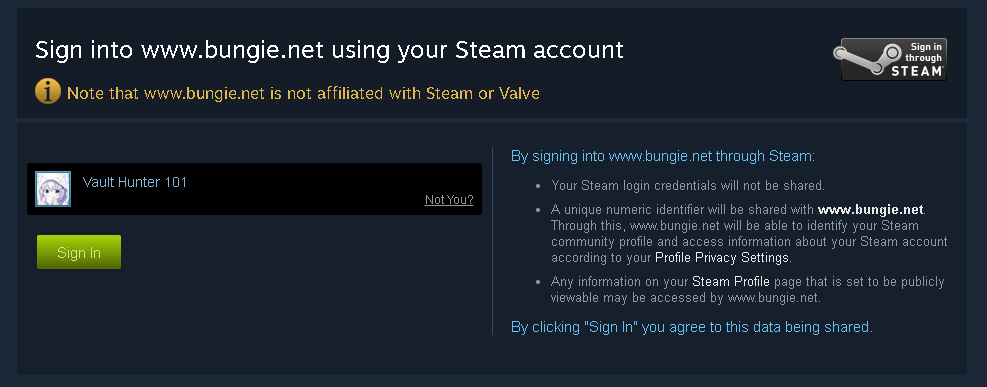
Сообщество Steam :: Руководство :: All scam methods explained!
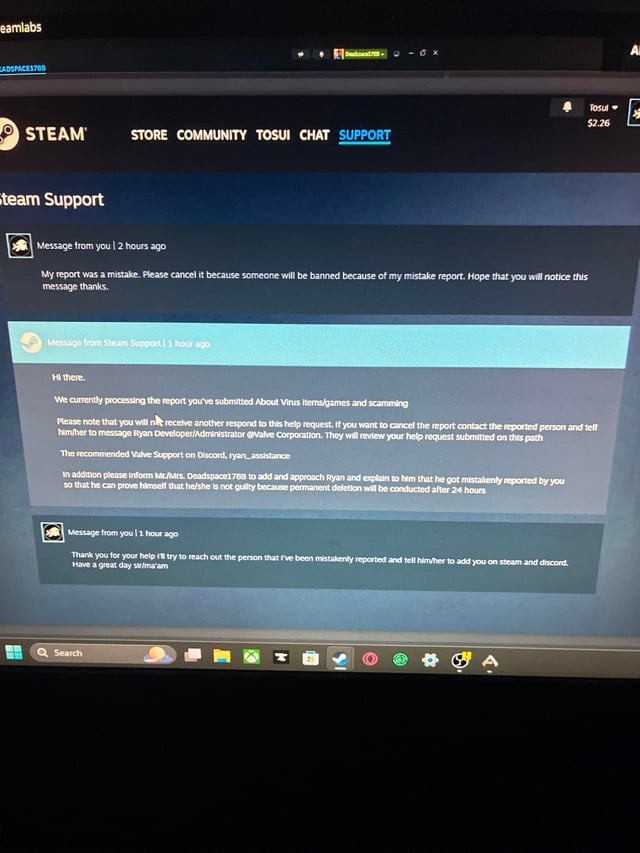
Reported by accident” : r/Steam
Is this normal with the Steam Support : r/Steam
Is this a scam? i think so but i'm not 100% sure as they don't fit the stereotypical fake account theme : r/Steam
Scammed for 800€ worth of CS2 items. Please help. : r/Steam
Steam Account was hacked and hacker emptied my inventory :: Help and Tips
Сообщество Steam :: Руководство :: All scam methods explained!
just got scammed, what can I do? : r/SteamScams
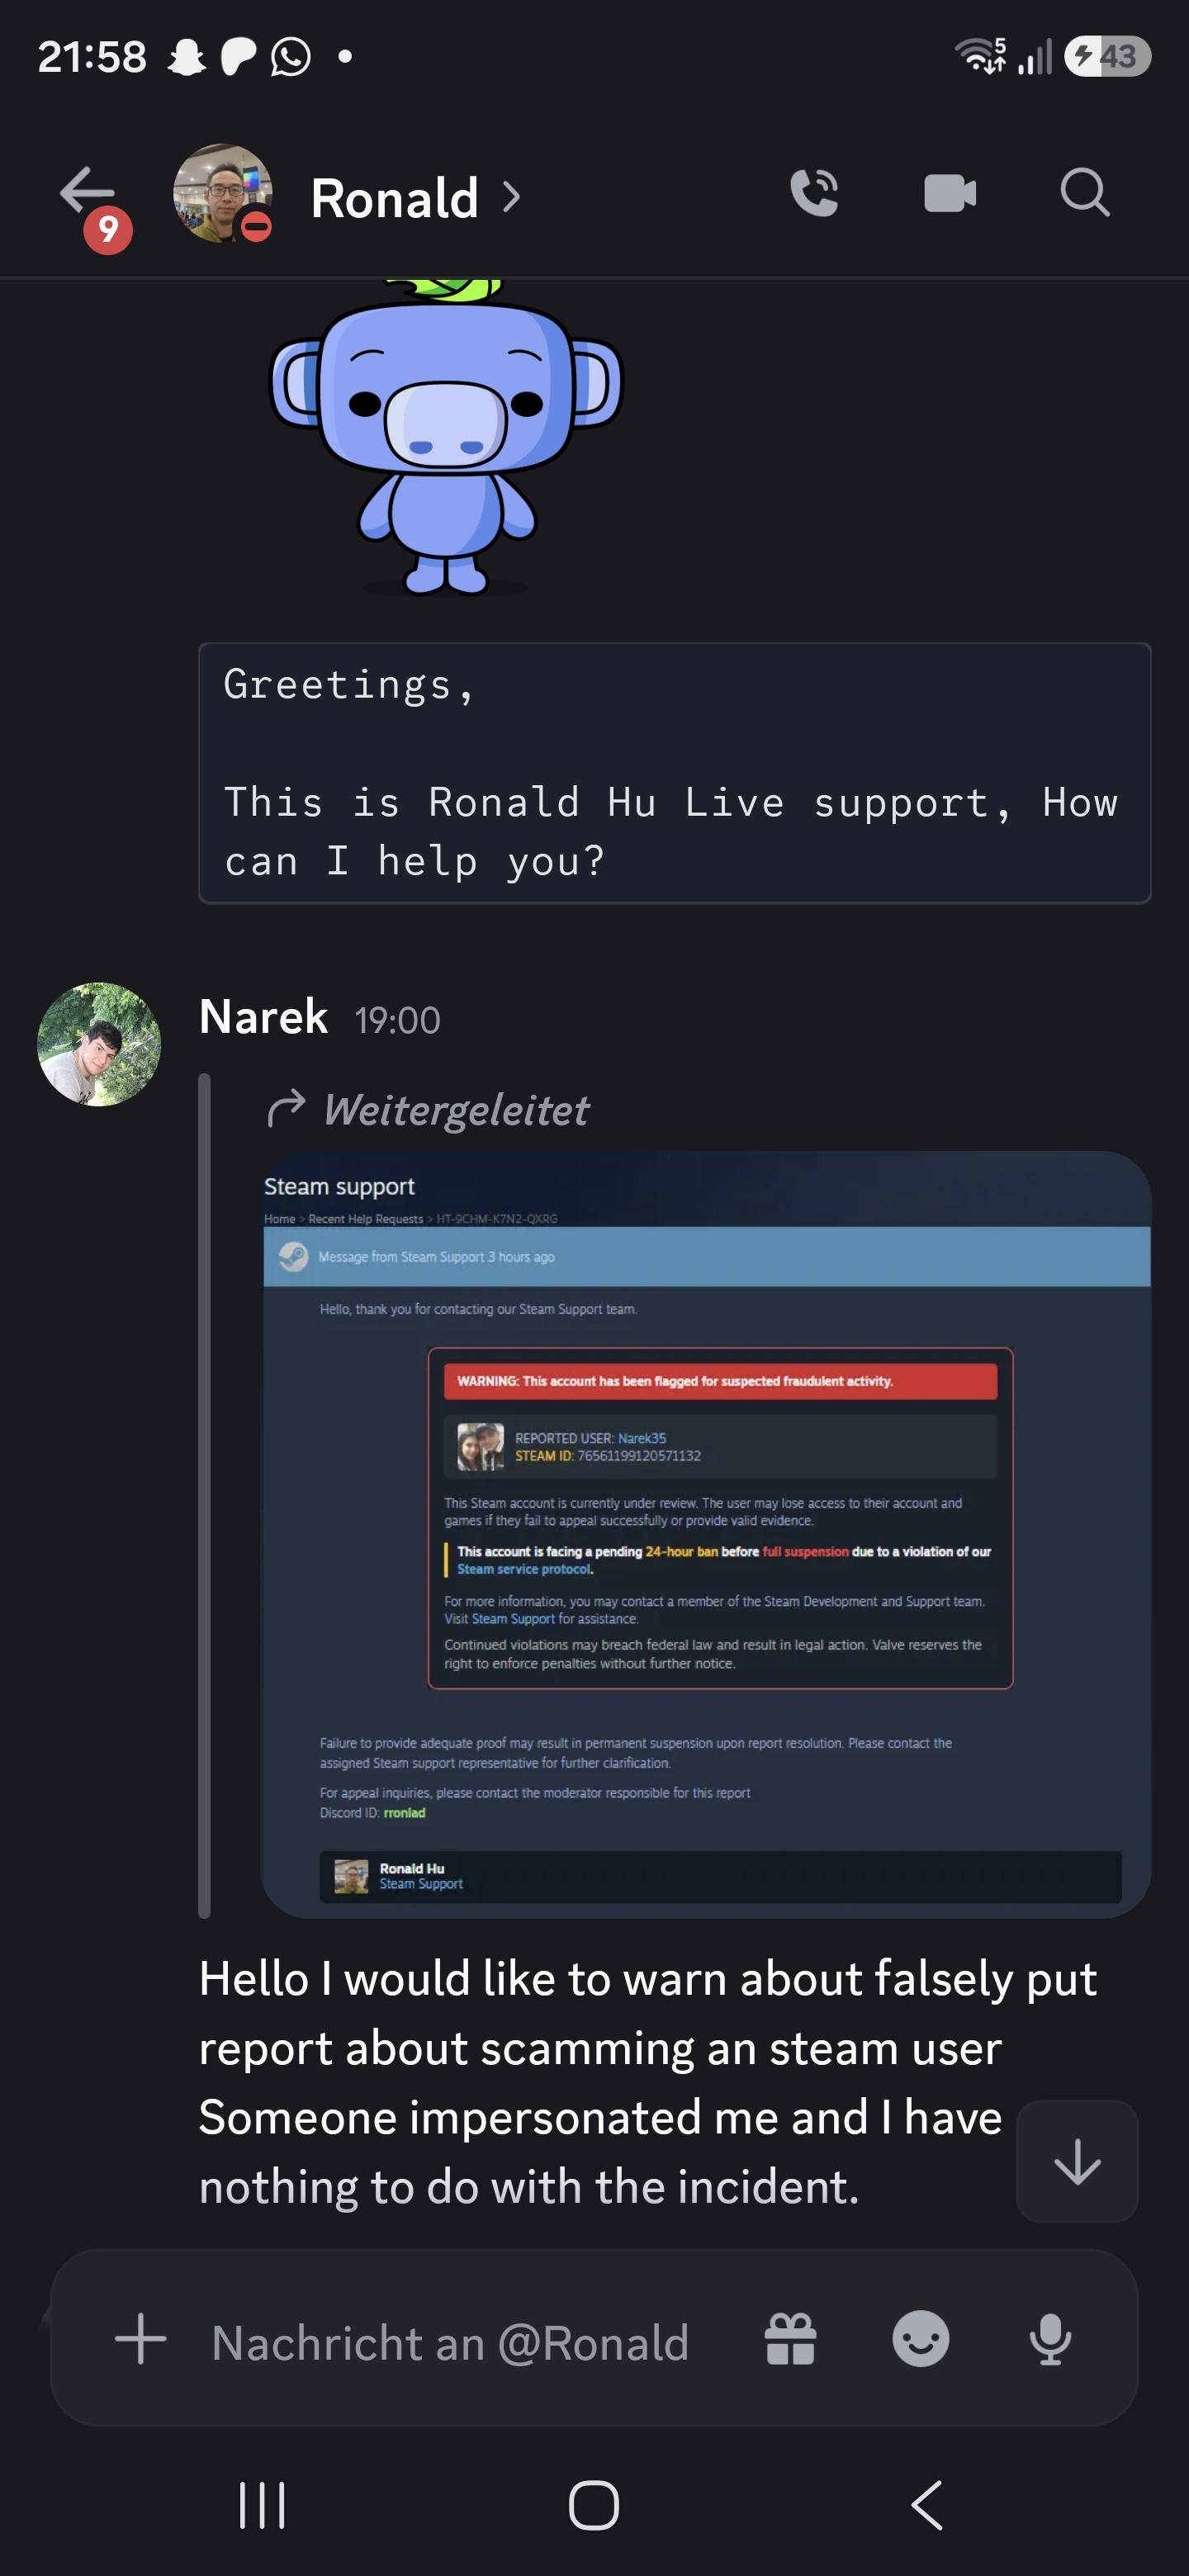
Is this normal with the Steam Support : r/Steam
Steam Topluluğu :: Rehber :: All scam methods explained!
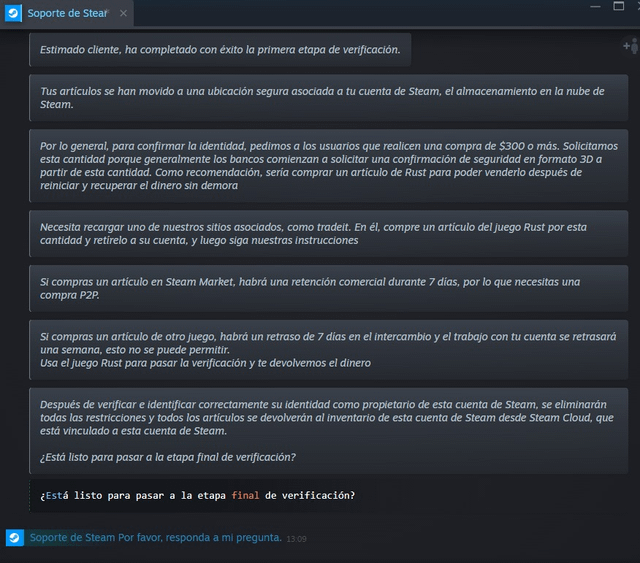
Title: My younger brother got scammed for 1500+ Dota 2 items) – need advice and warning : r/SteamScams
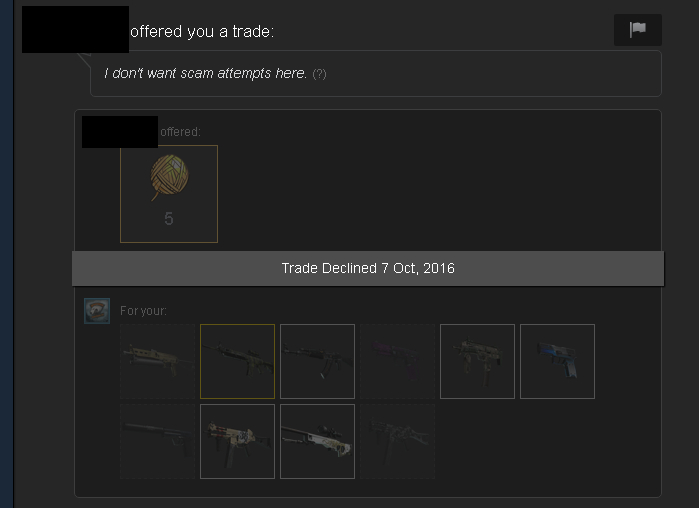
Сообщество Steam :: Руководство :: All scam methods explained!
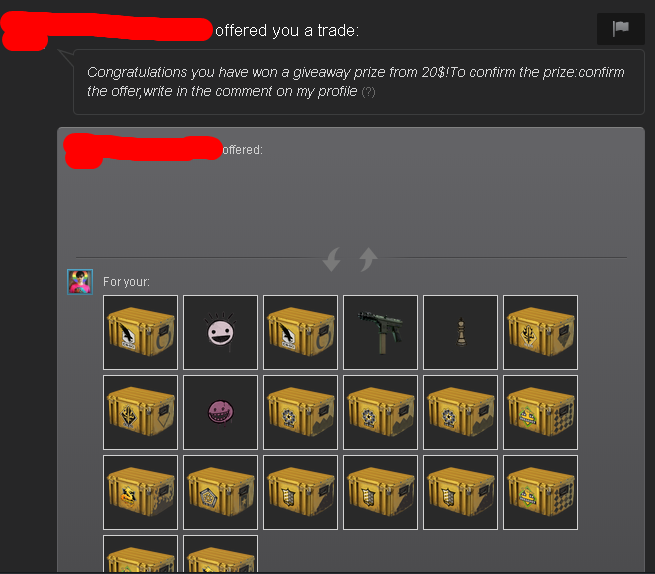
Steam-Community :: Guide :: All scam methods explained!
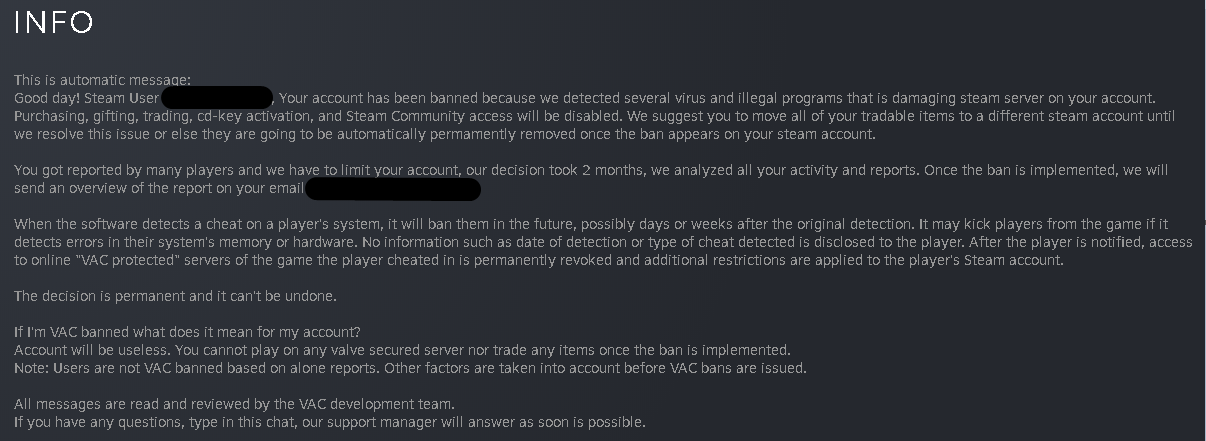
Steam-Community :: Guide :: All scam methods explained!
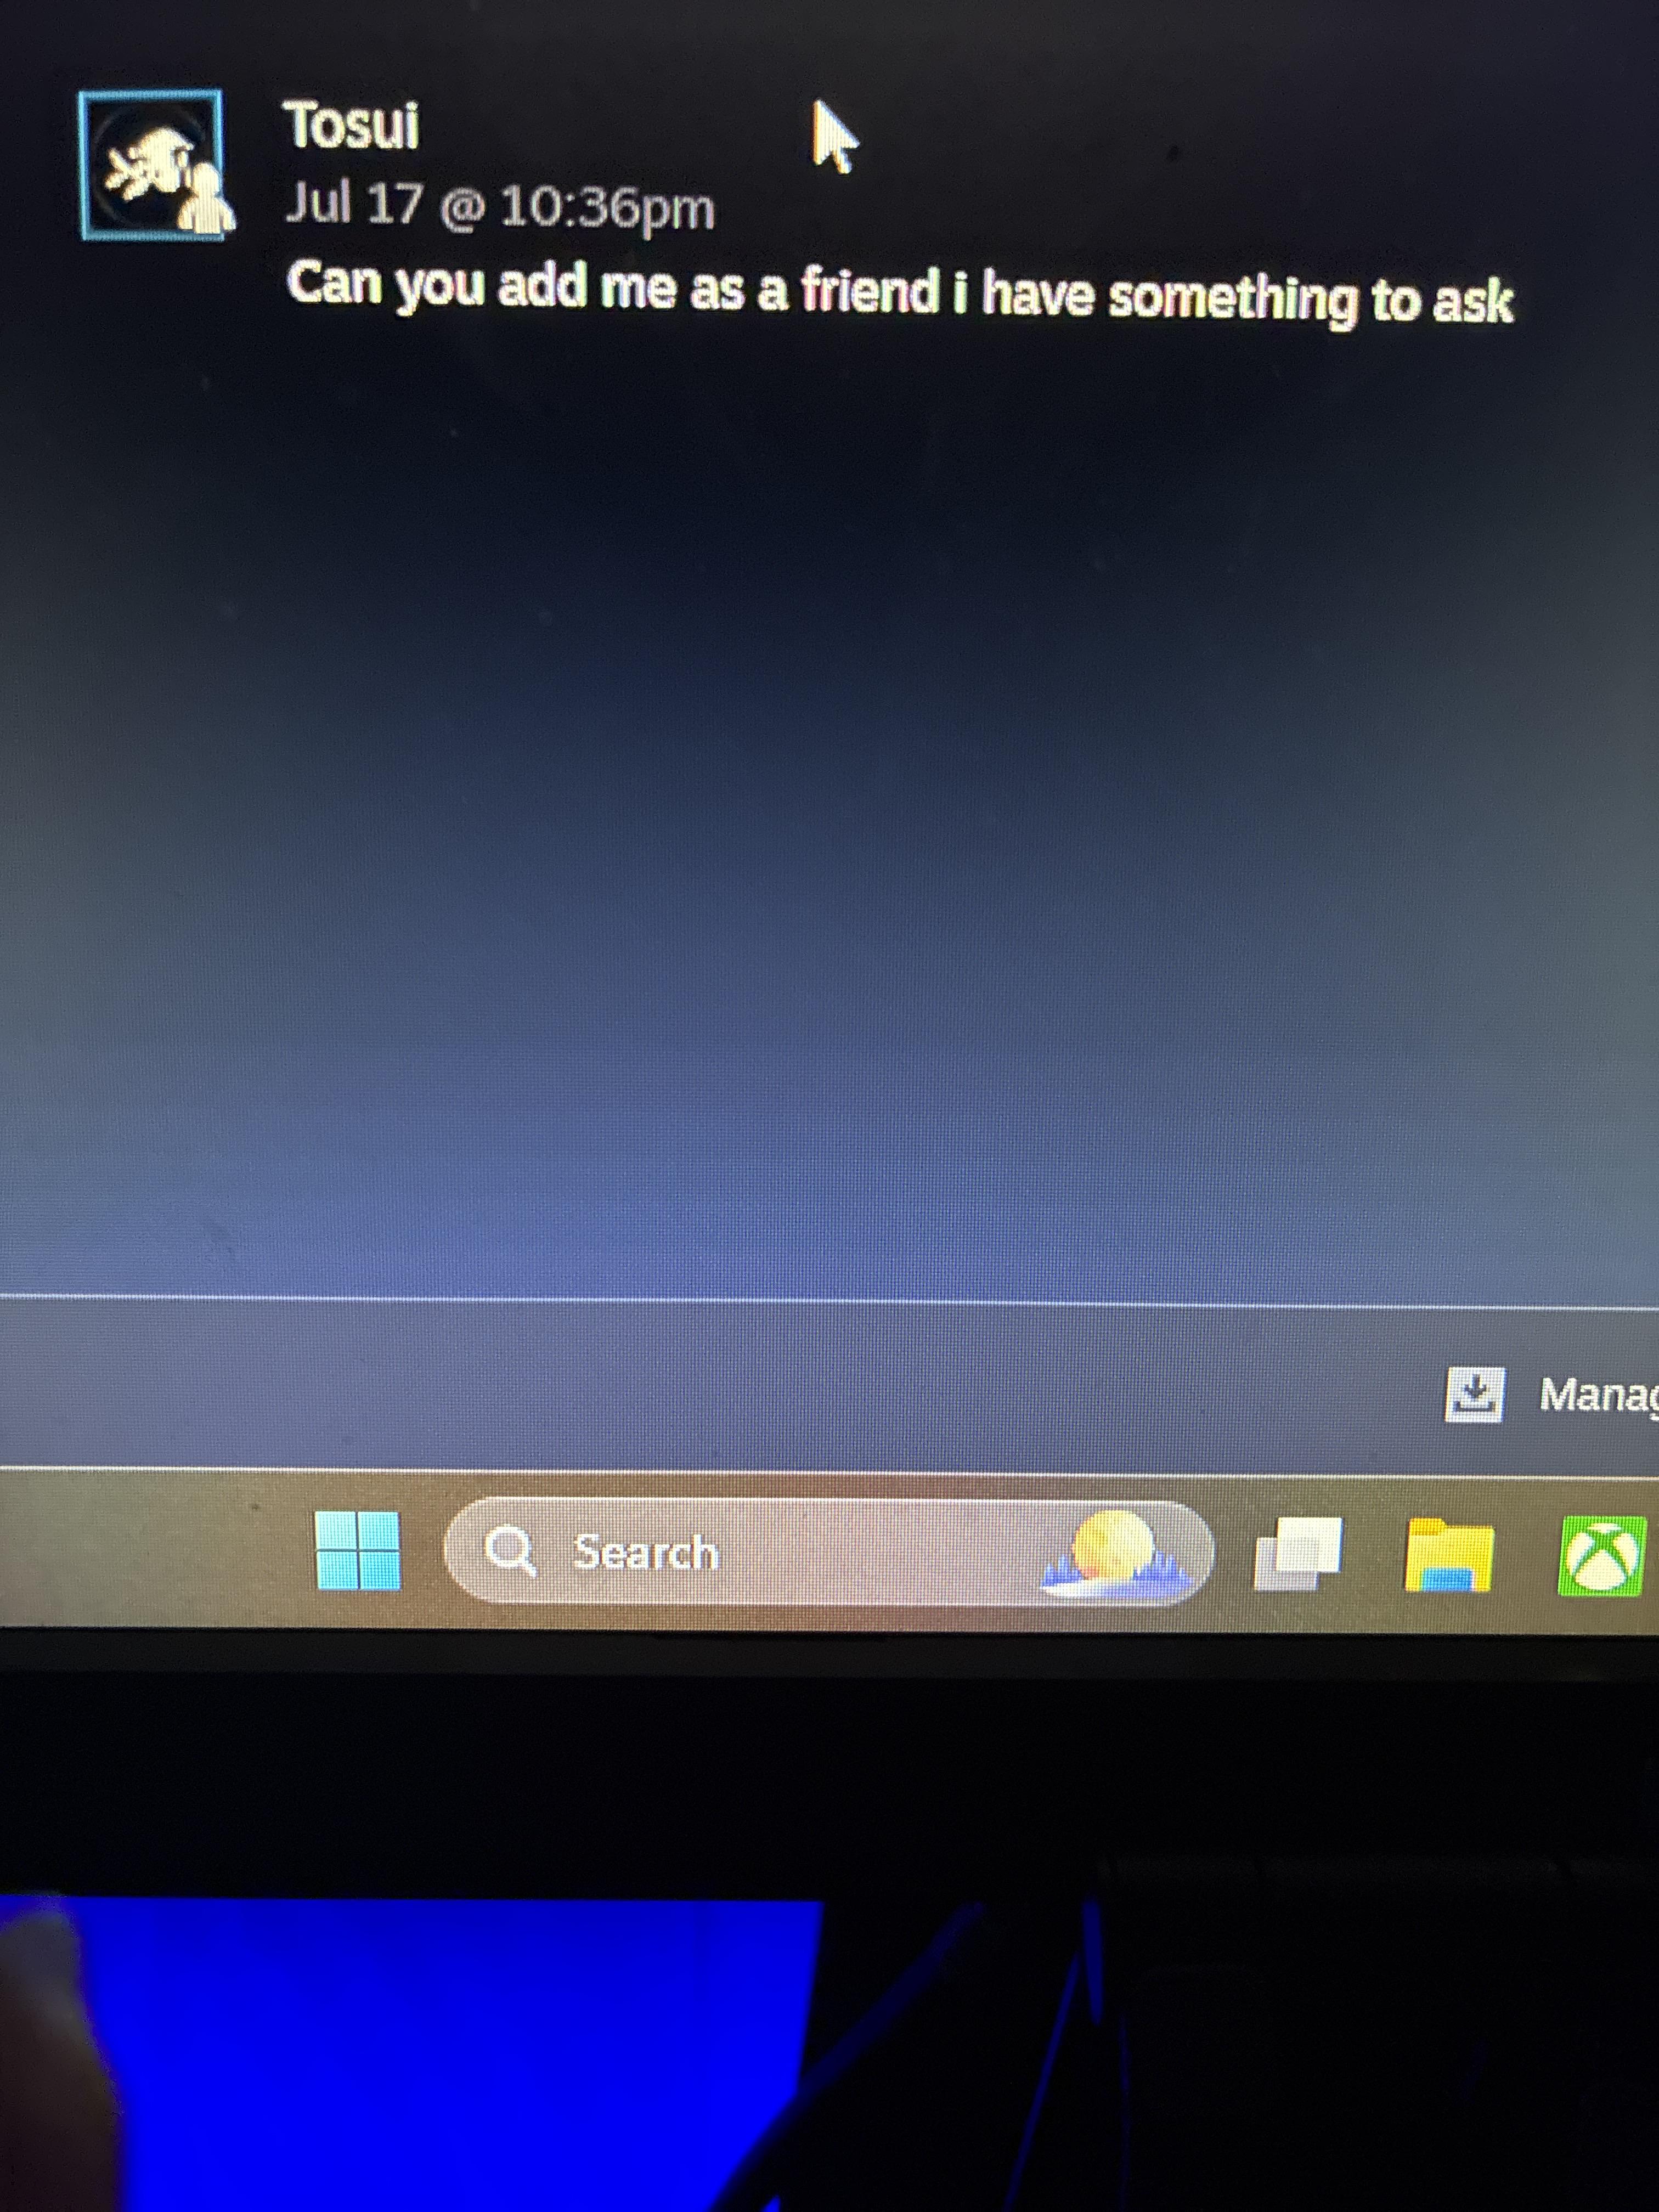
Reported by accident” : r/Steam
Steam Reviews | Read Customer Service Reviews of store.steampowered.com | 4 of 13
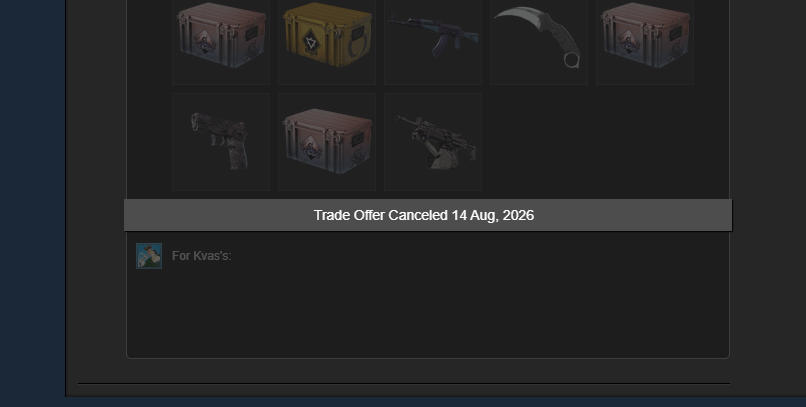
Scammed for 800€ worth of CS2 items. Please help. : r/Steam
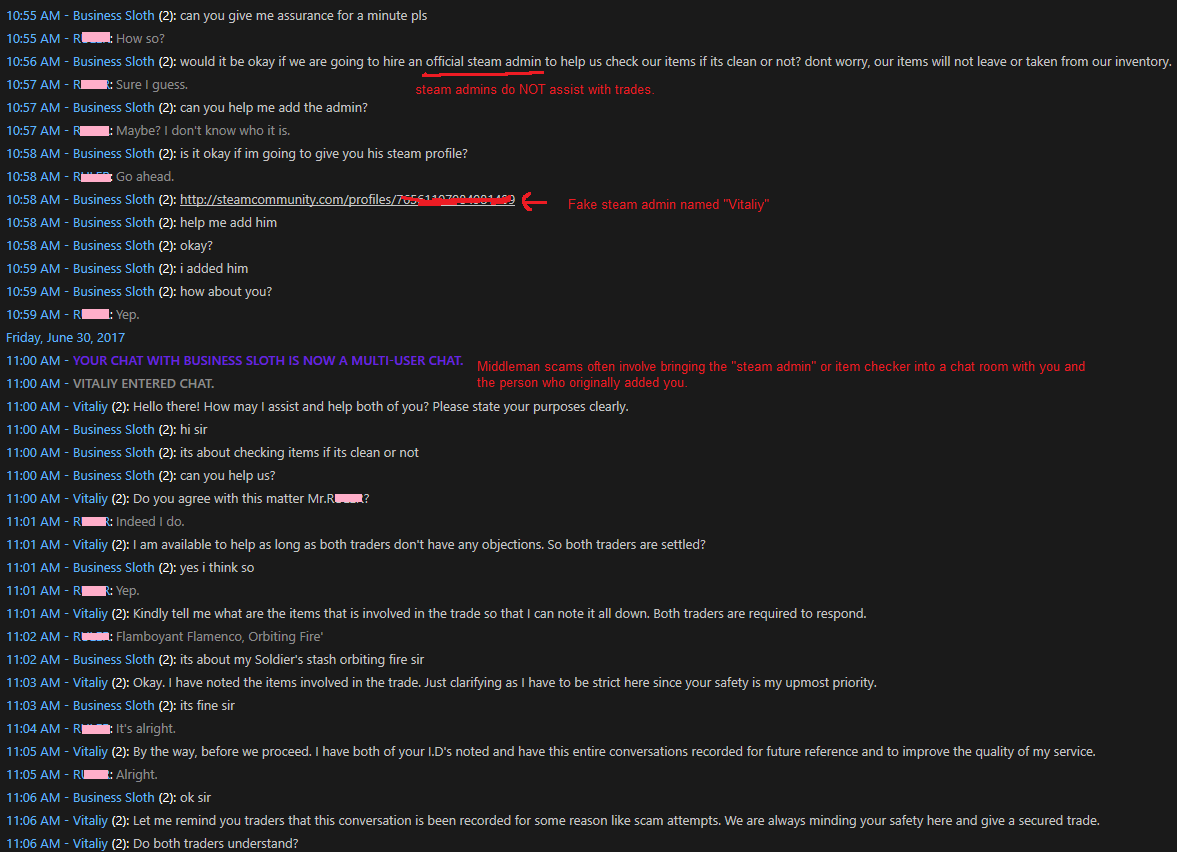
Steam Community :: Guide :: OP SKINS SCAM! Fake Bots! Fake Steam Admins! Fake Chrome Extensions! Item Checking!?
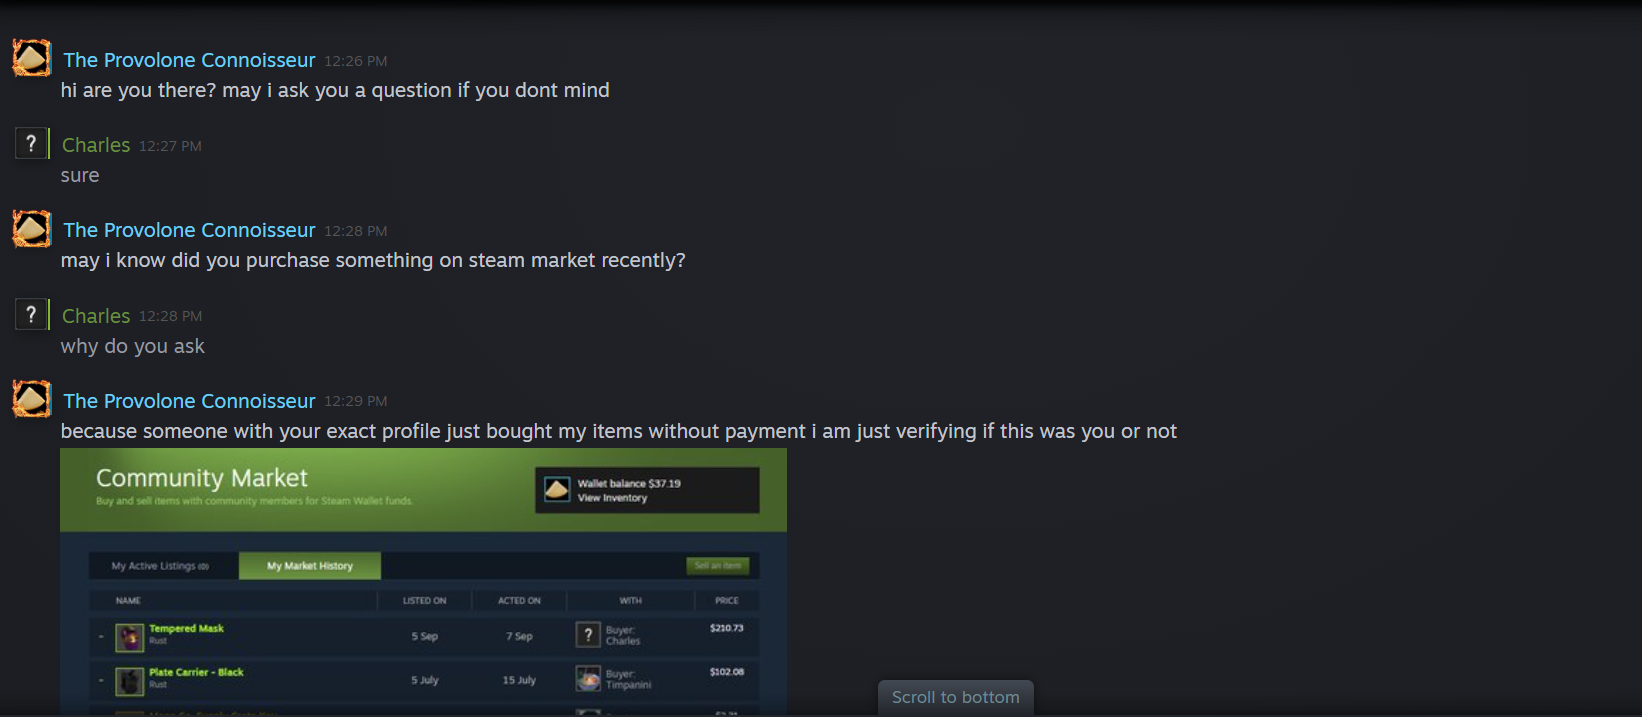
Fraud supposedly lol : r/Steam
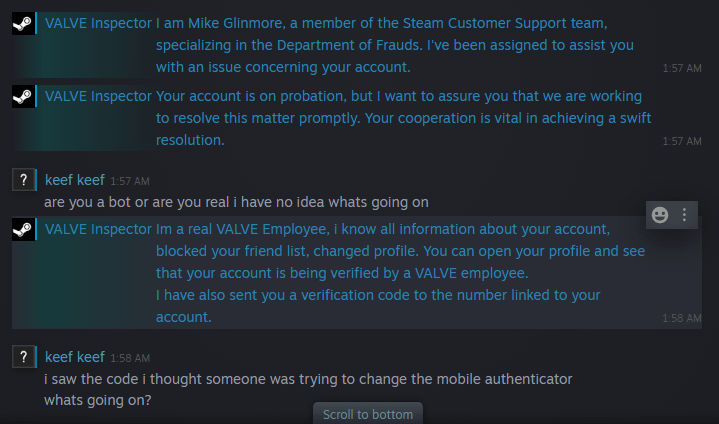
Scammed for 800€ worth of CS2 items. Please help. : r/Steam
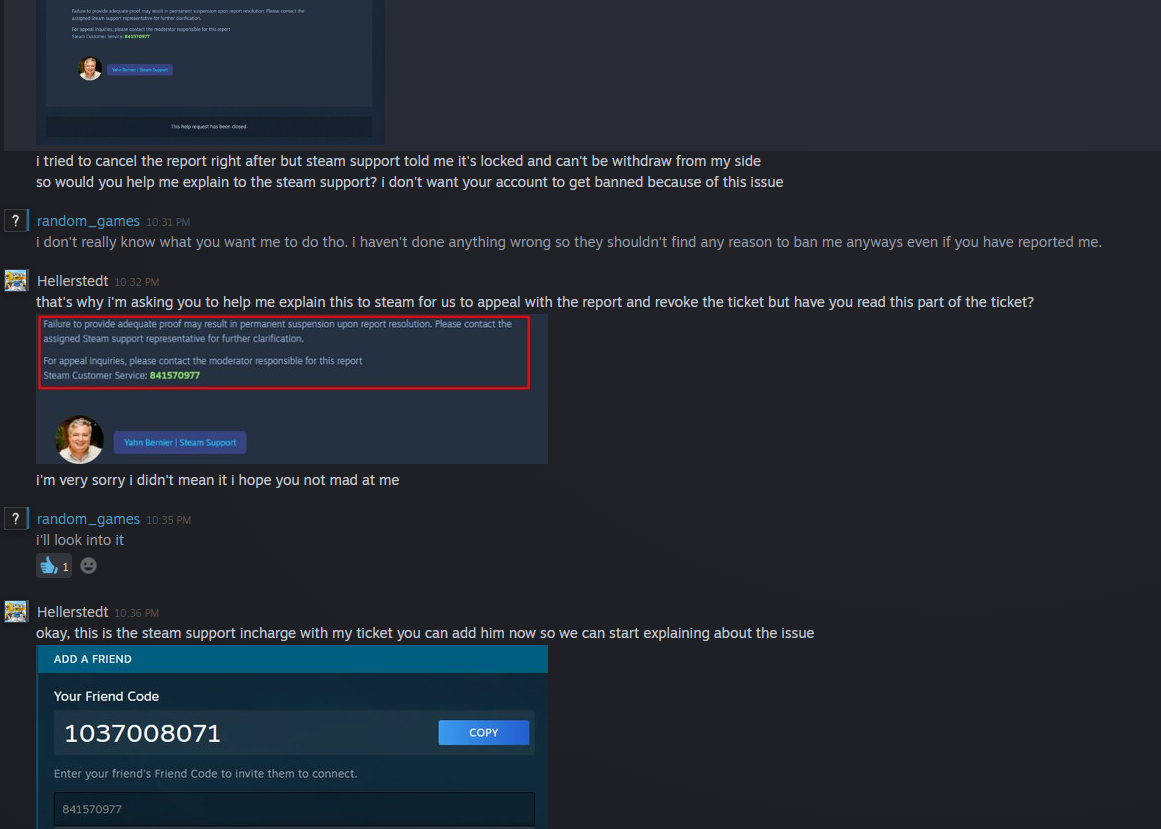
Is this a scam? i think so but i'm not 100% sure as they don't fit the stereotypical fake account theme : r/Steam
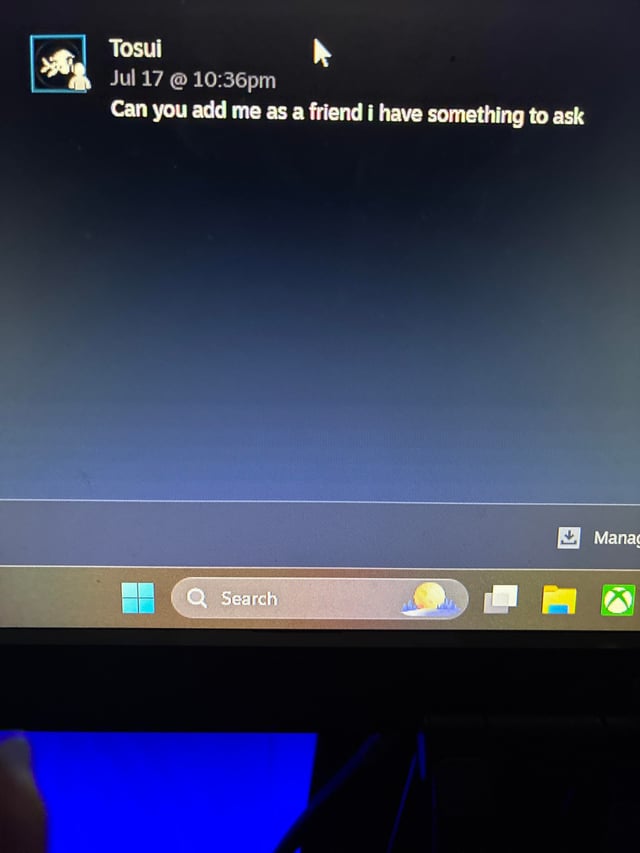
Reported by accident” : r/Steam
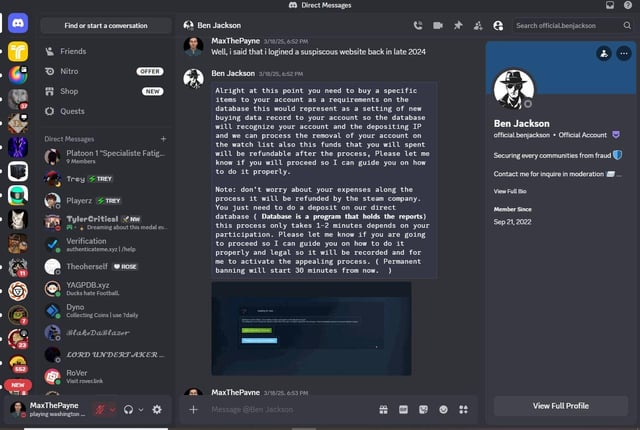
READ POST FIRST) question: was this thingy actually real? : r/Steam
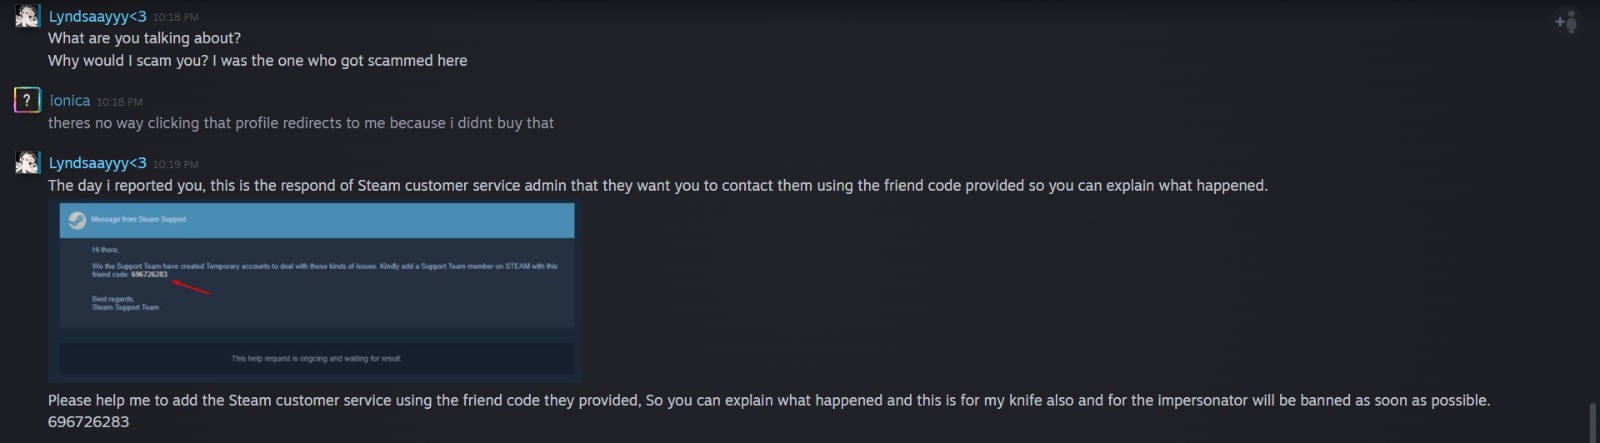
I actually took this seriously at first, then realized its just a scam : r/Steam
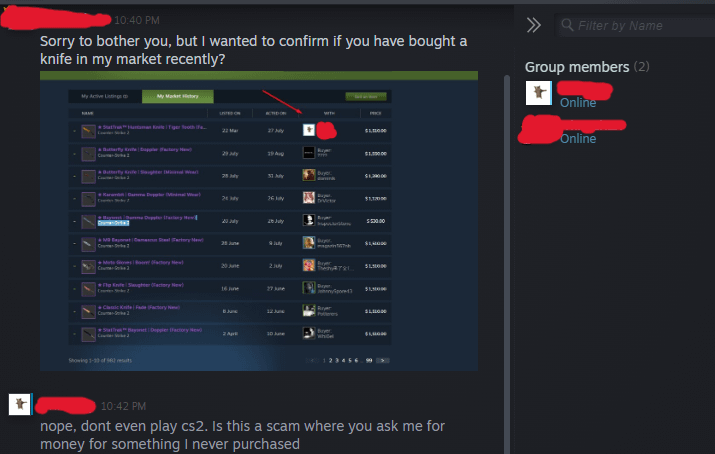
Is this a scam? : r/Steam
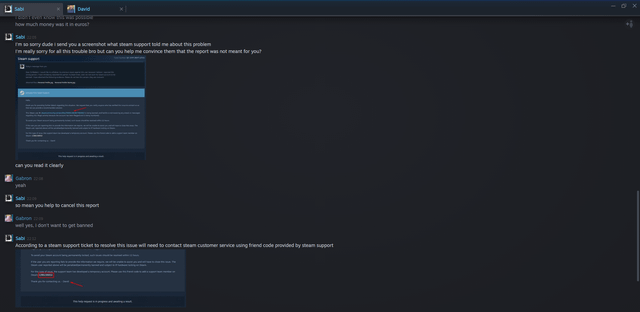
Scam? : r/Steam
Scam… : r/Steam
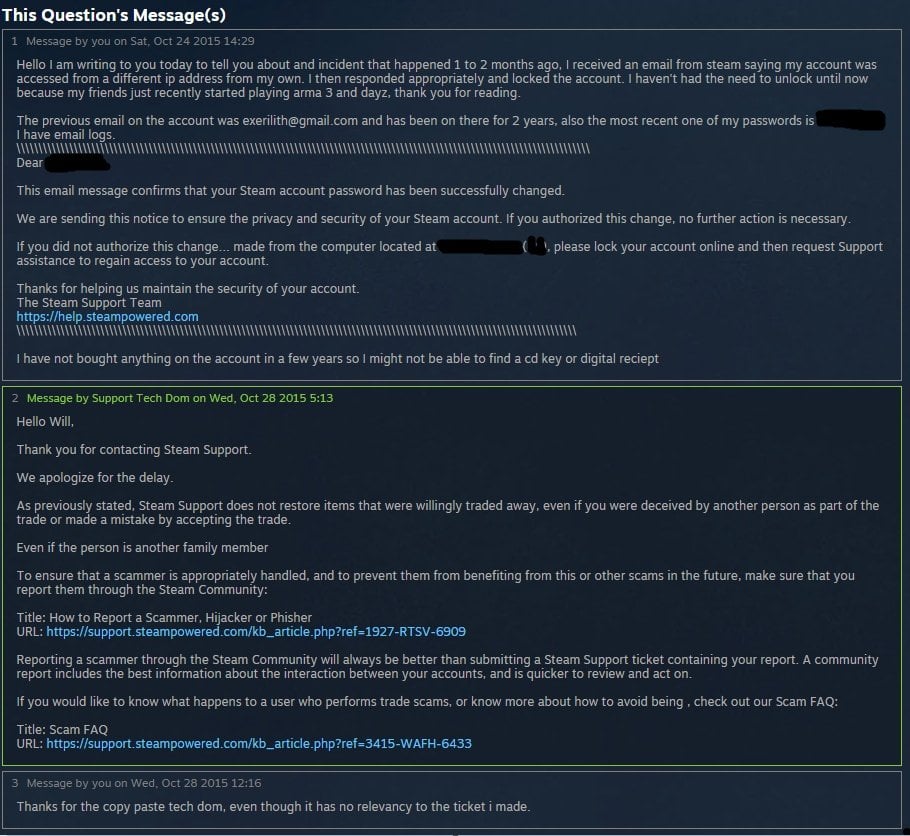
Kden : r/Steam
This is probably a scam isn't it? : r/Steam
Scam… : r/Steam
Confused about a possible scam? : r/Steam
Scam… : r/Steam
Confused about a possible scam? : r/Steam
Scam… : r/Steam
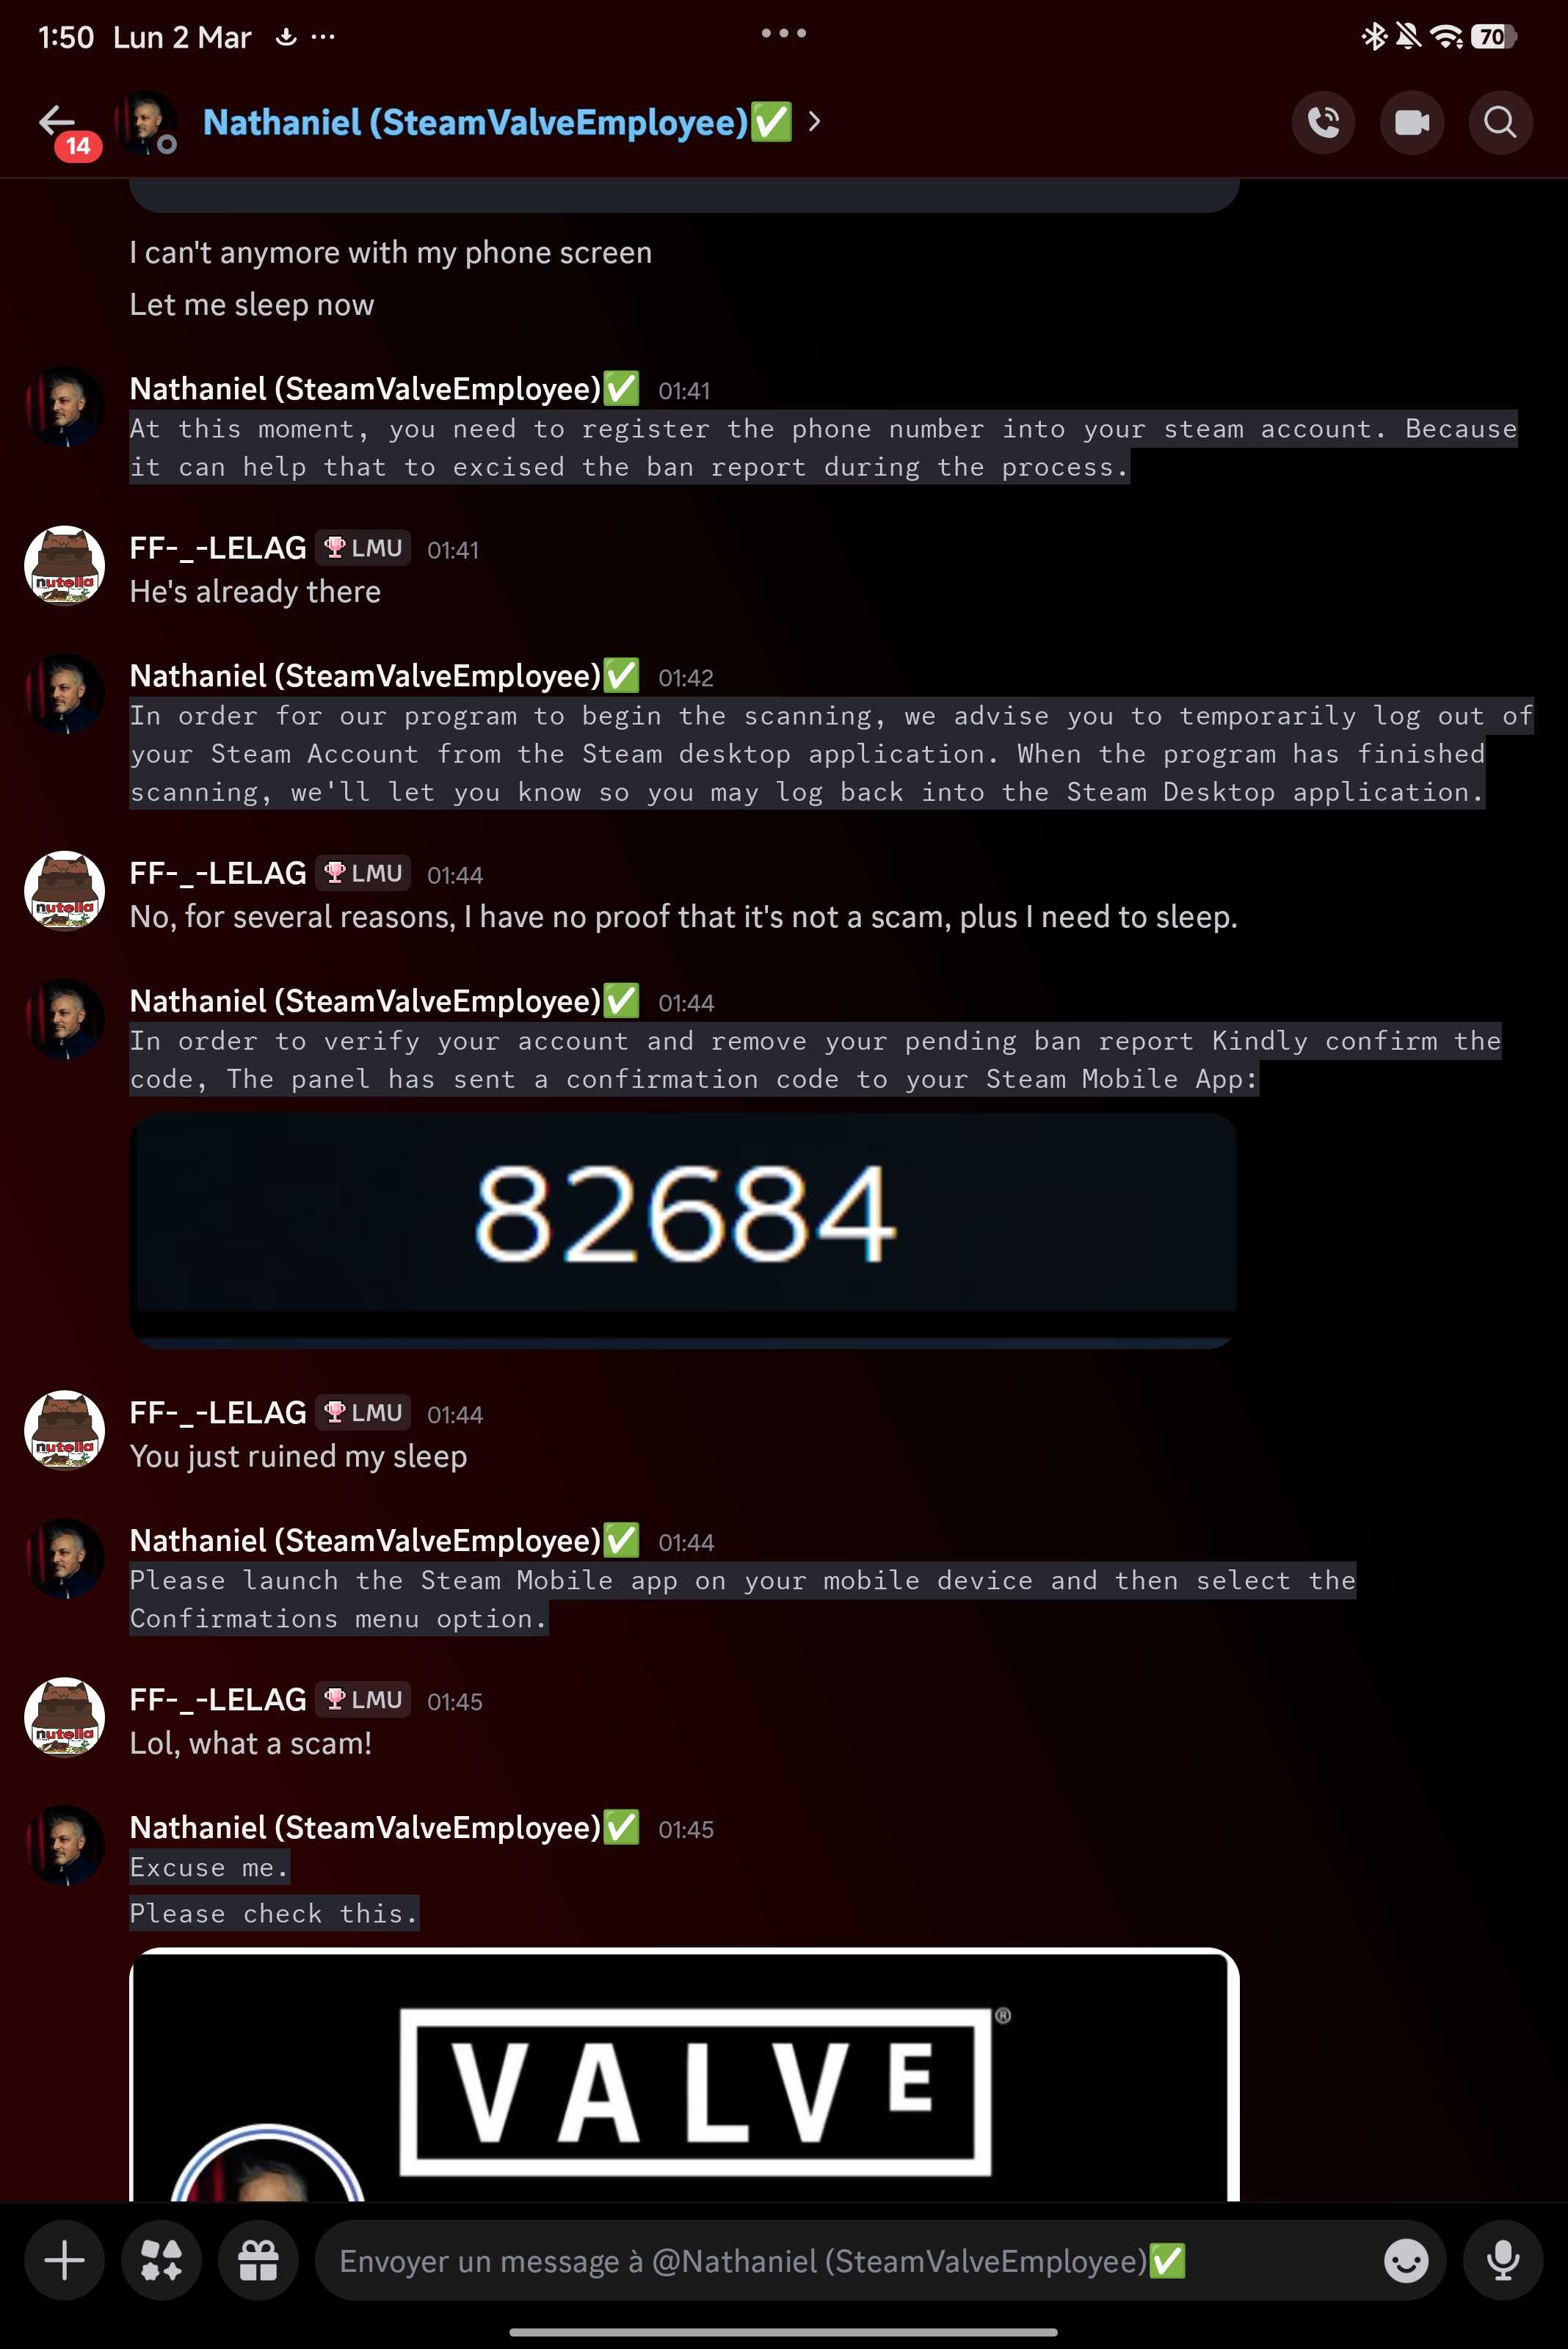
Was it a scam? : r/Steam
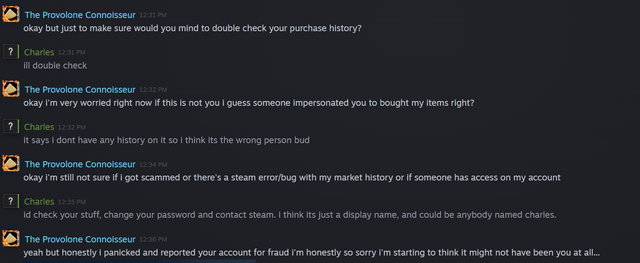
Fraud supposedly lol : r/Steam
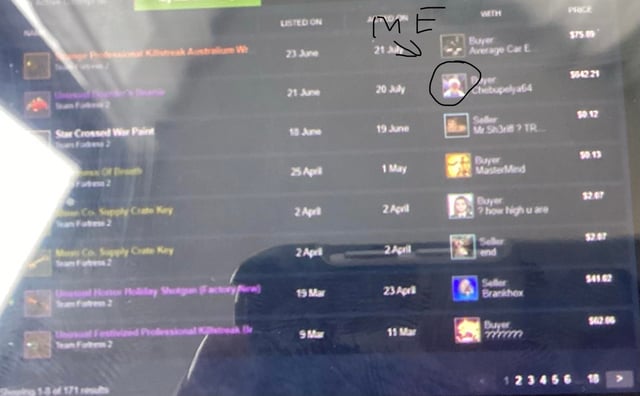
Scam… : r/Steam
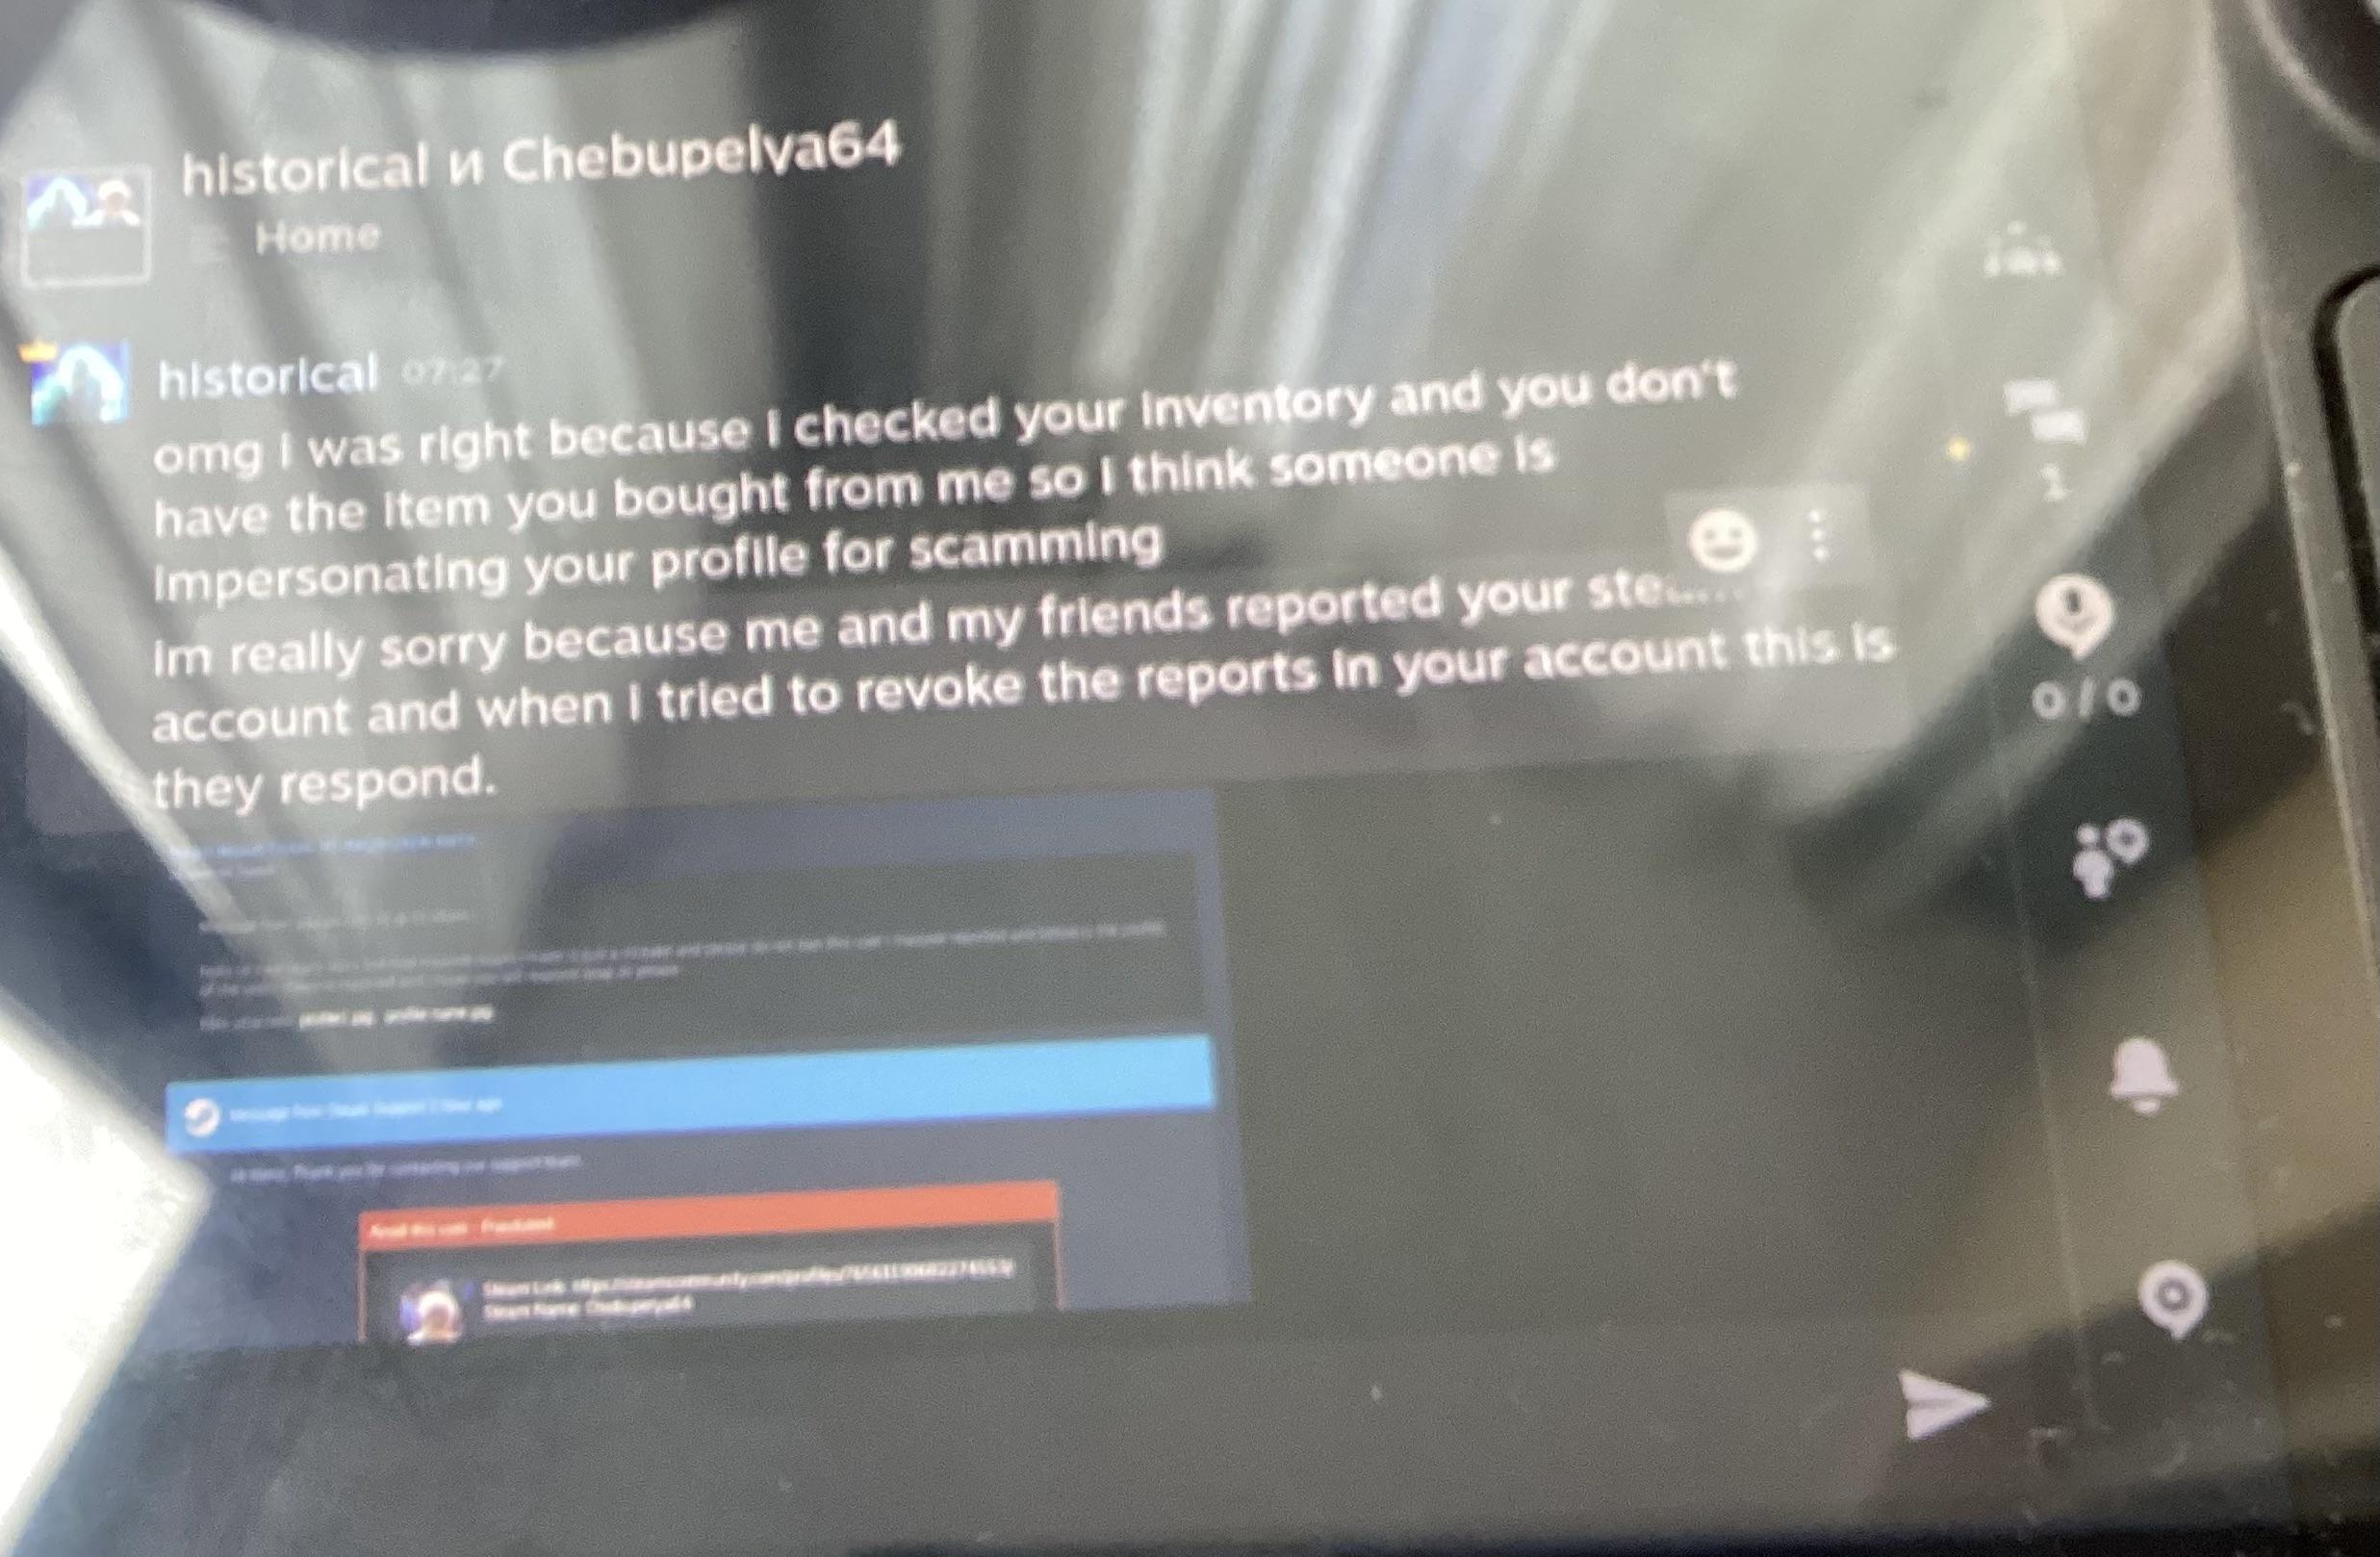
Scam… : r/Steam
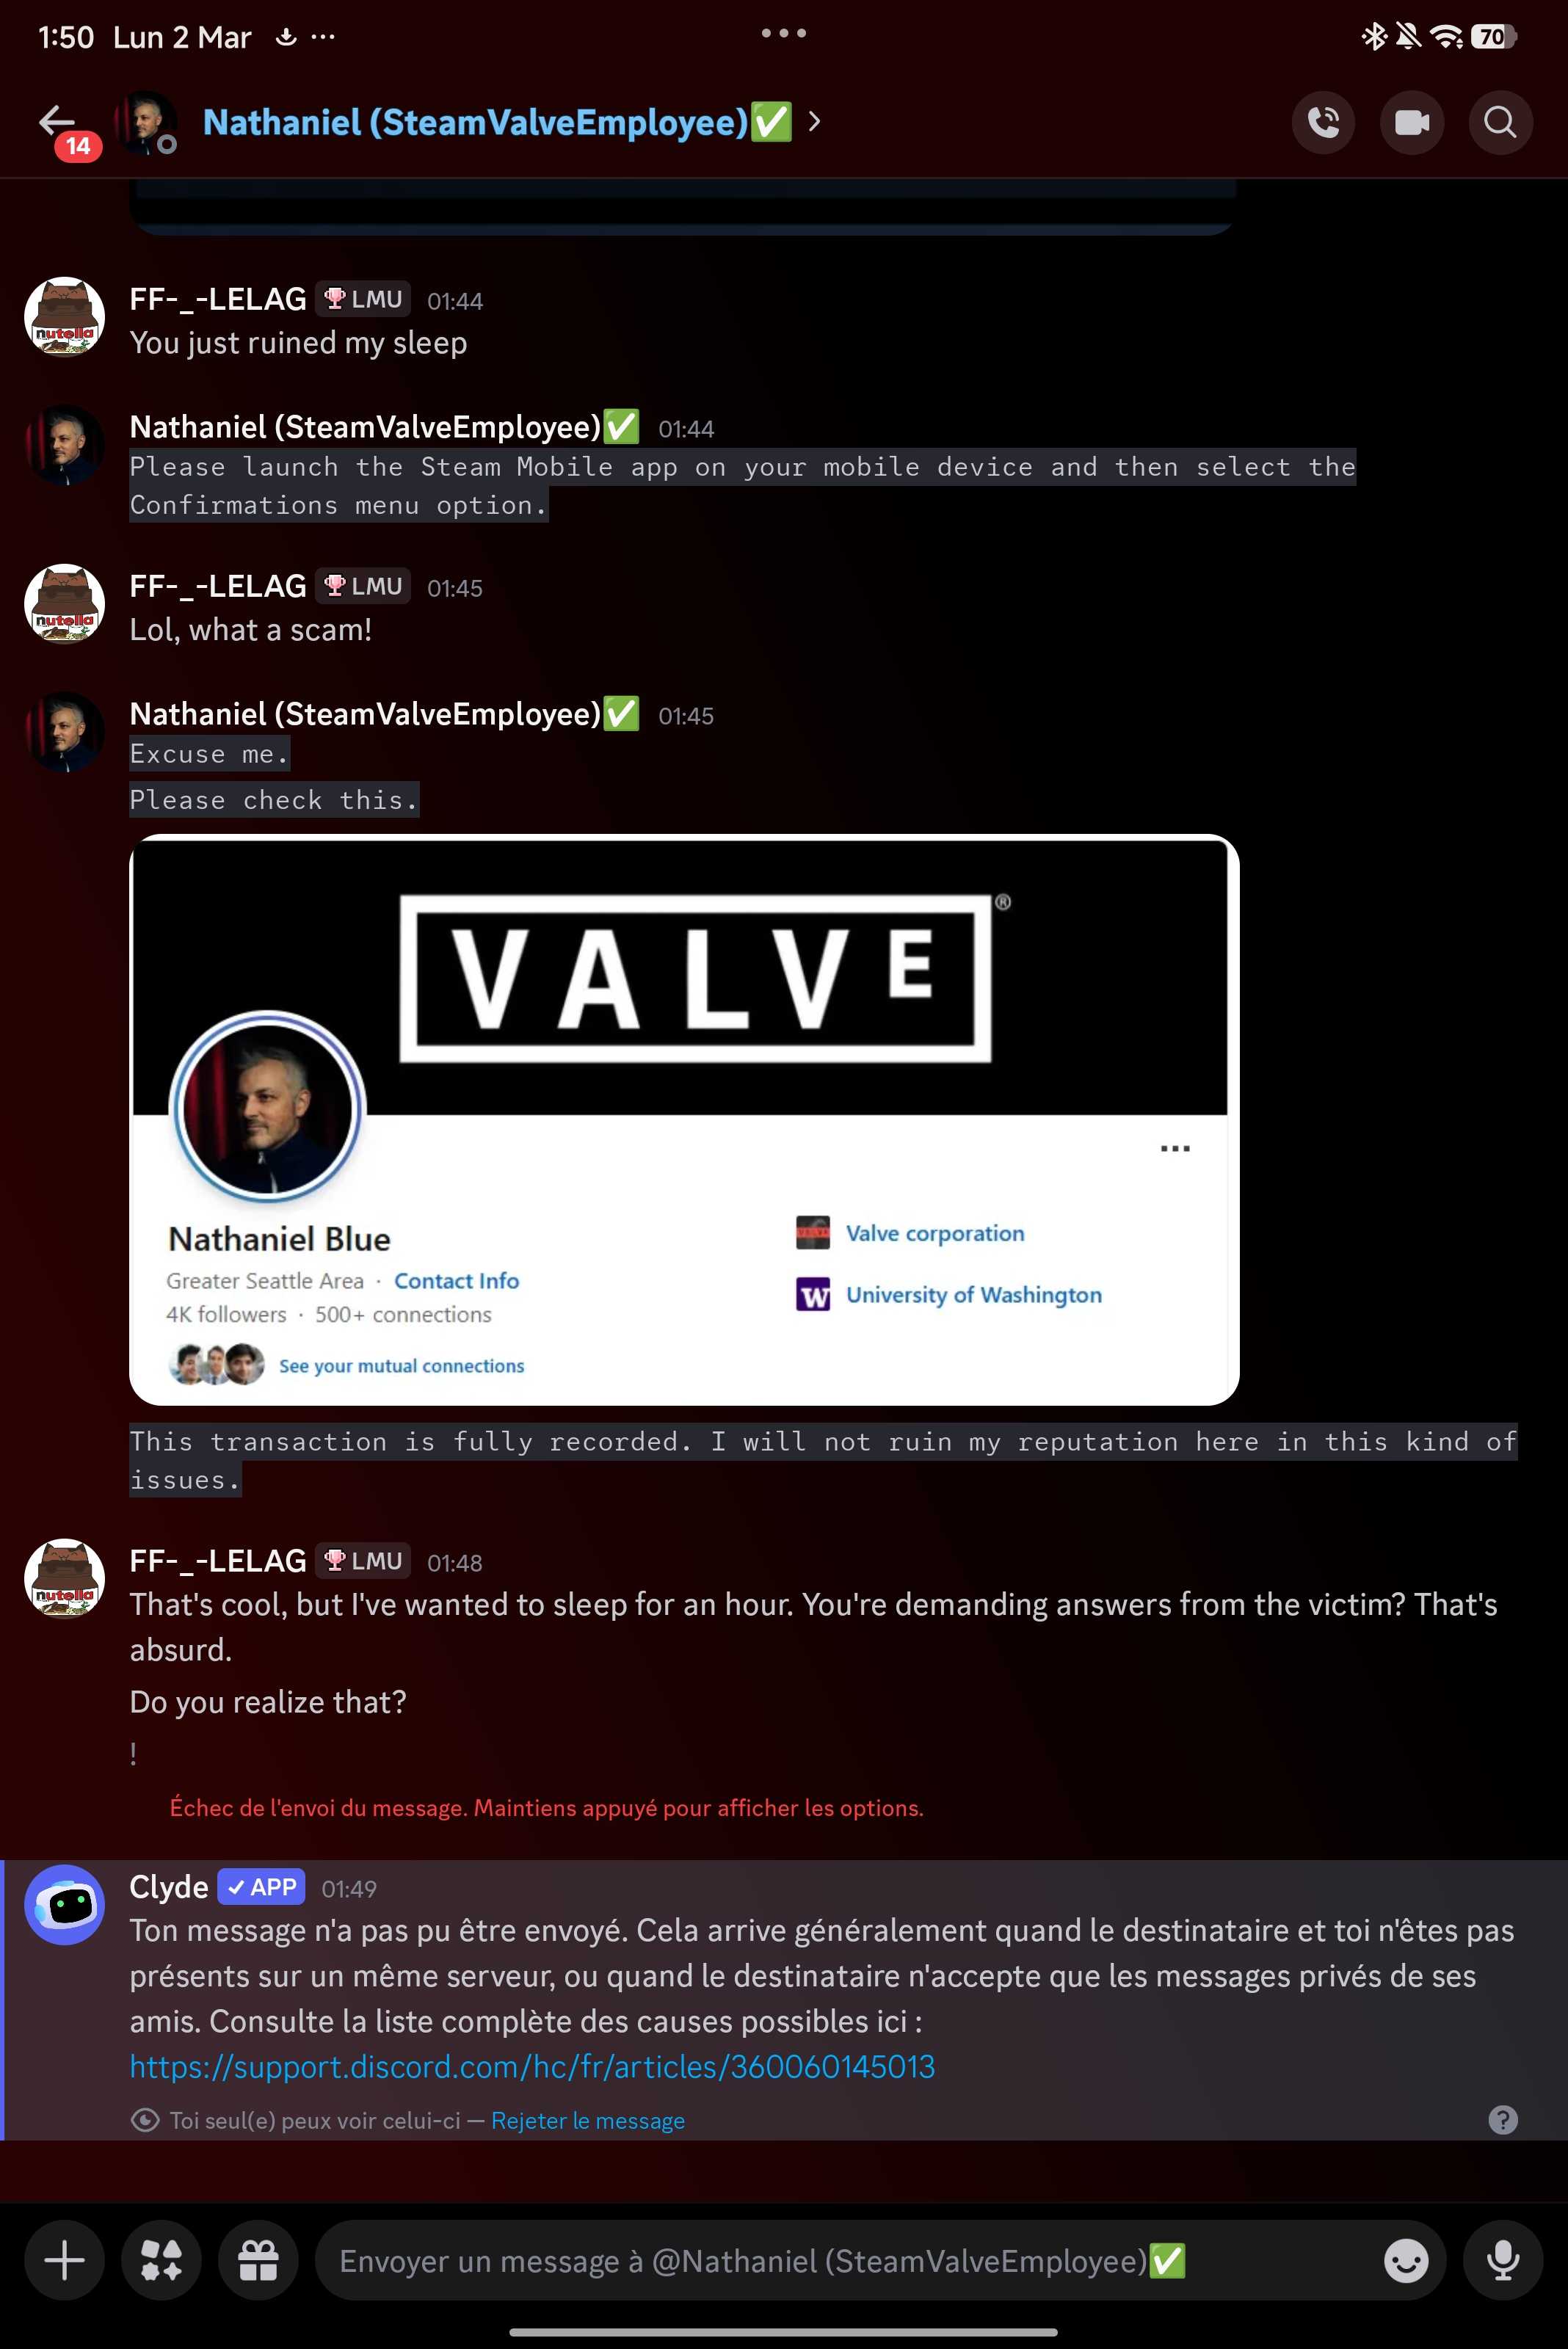
Was it a scam? : r/Steam
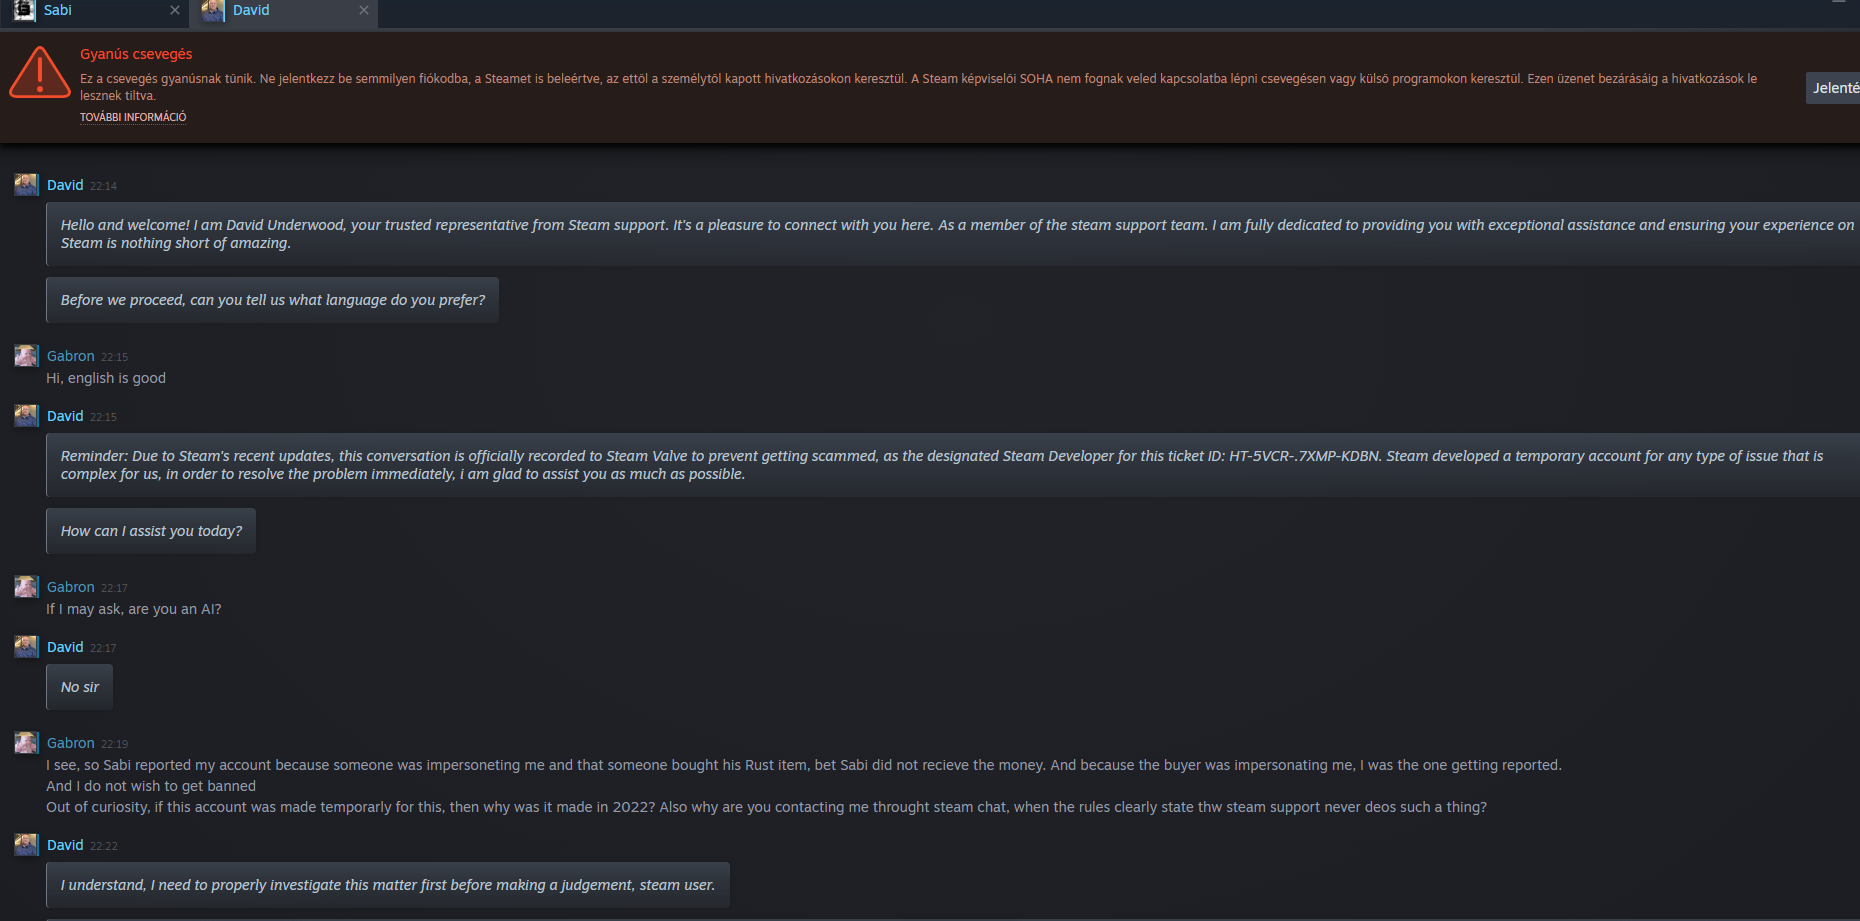
Scam? : r/Steam
Scam… : r/Steam
Scammed for 800€ worth of CS2 items. Please help. : r/Steam
This has to be a scam, right? : r/Steam
Scammed for 800€ worth of CS2 items. Please help. : r/Steam
Scam attempts? : r/Steam
Scam… : r/Steam
I actually took this seriously at first, then realized its just a scam : r/Steam
Is this a scam? i think so but i'm not 100% sure as they don't fit the stereotypical fake account theme : r/Steam
Not Sure What to do at this point. Help? Details in Comments : r/Steam
Not Sure What to do at this point. Help? Details in Comments : r/Steam
Not Sure What to do at this point. Help? Details in Comments : r/Steam
ive been getting these weird requests, any idea whats causing them and are they a breach attack? any help would be appreciated : r/Steam
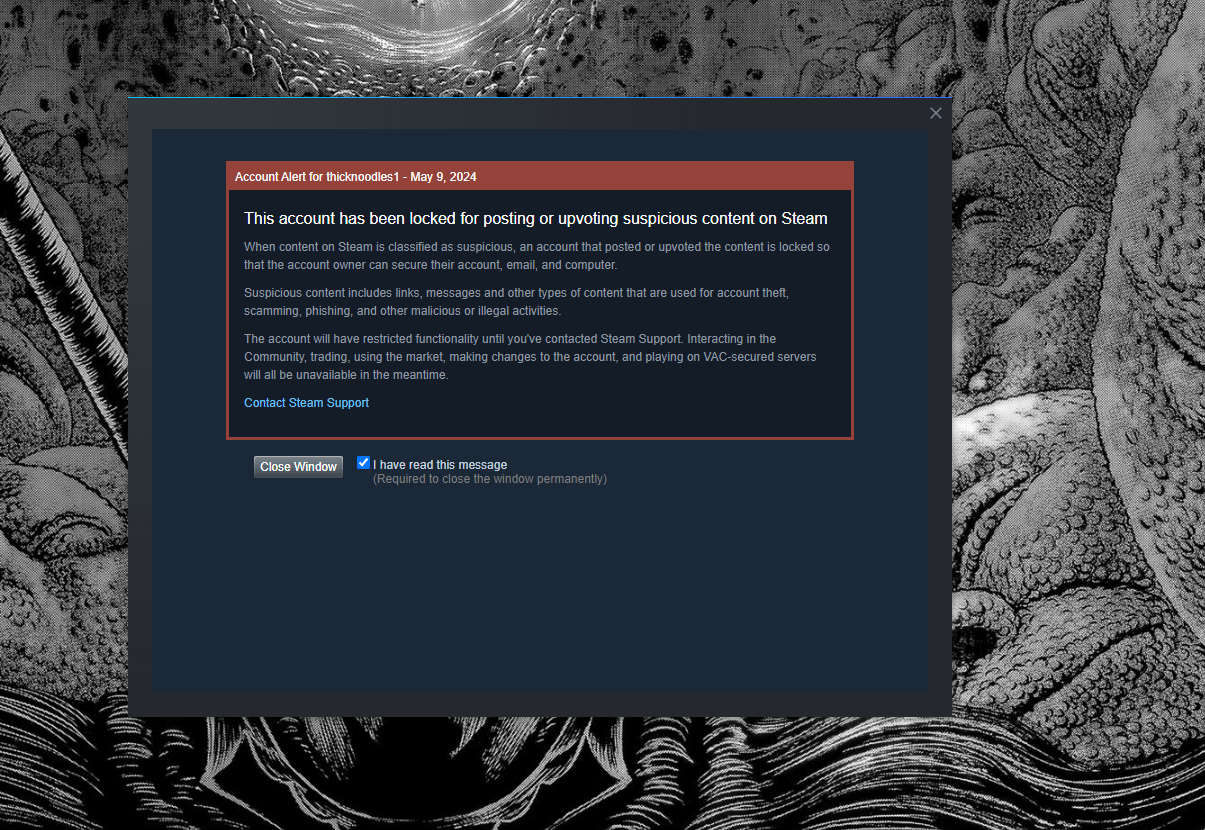
Should I be concerned about this? I've never posted or upvoted anything on Steam ever. : r/Steam
r/Steam Monthly Community Support Thread. : r/Steam
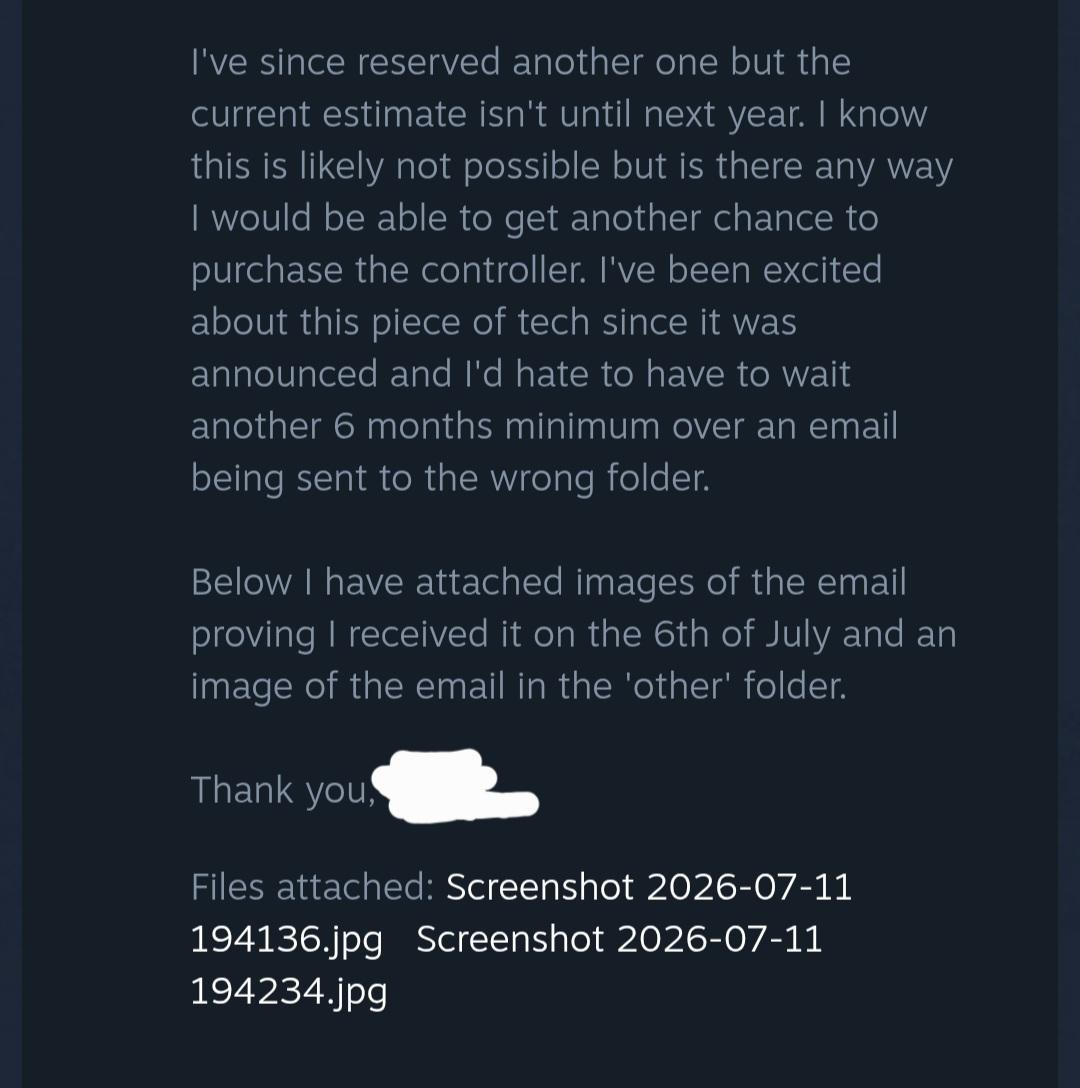
Steam support coming through as always : r/Steam
My friend recently got his account stolen, he contacted steam support and they replied saying he needed to update the info on his ticket. When going to create or update a ticket the site is down and ...
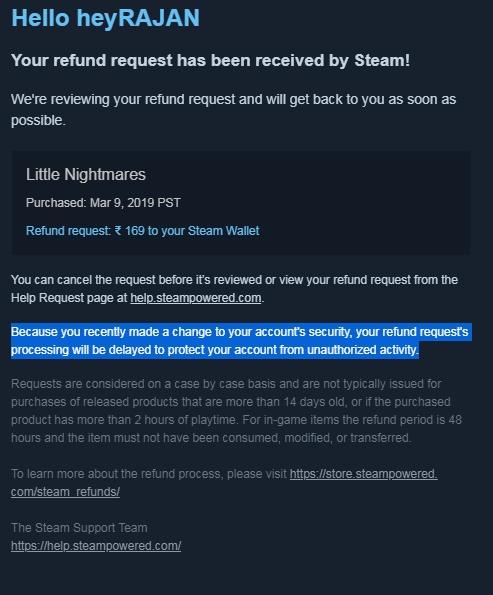
Can anyone tell me how long is it going to be on hold? *Read Selected Text : r/Steam
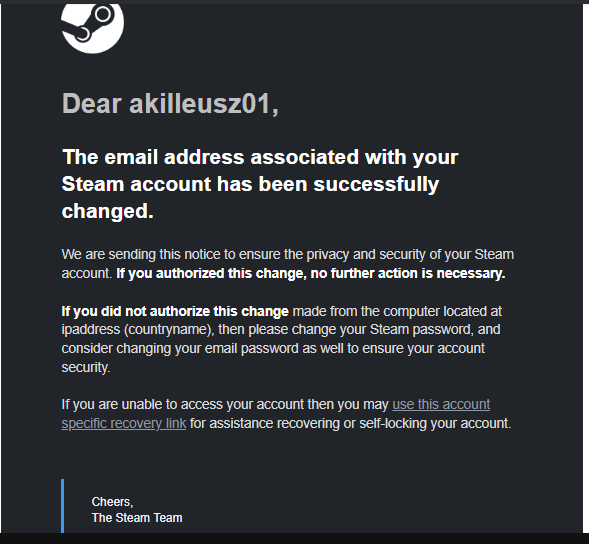
I got this email yesterday, is this legit? Also my email is the same and its still the old one : r/Steam
r/Steam Monthly Community Support Thread. : r/Steam
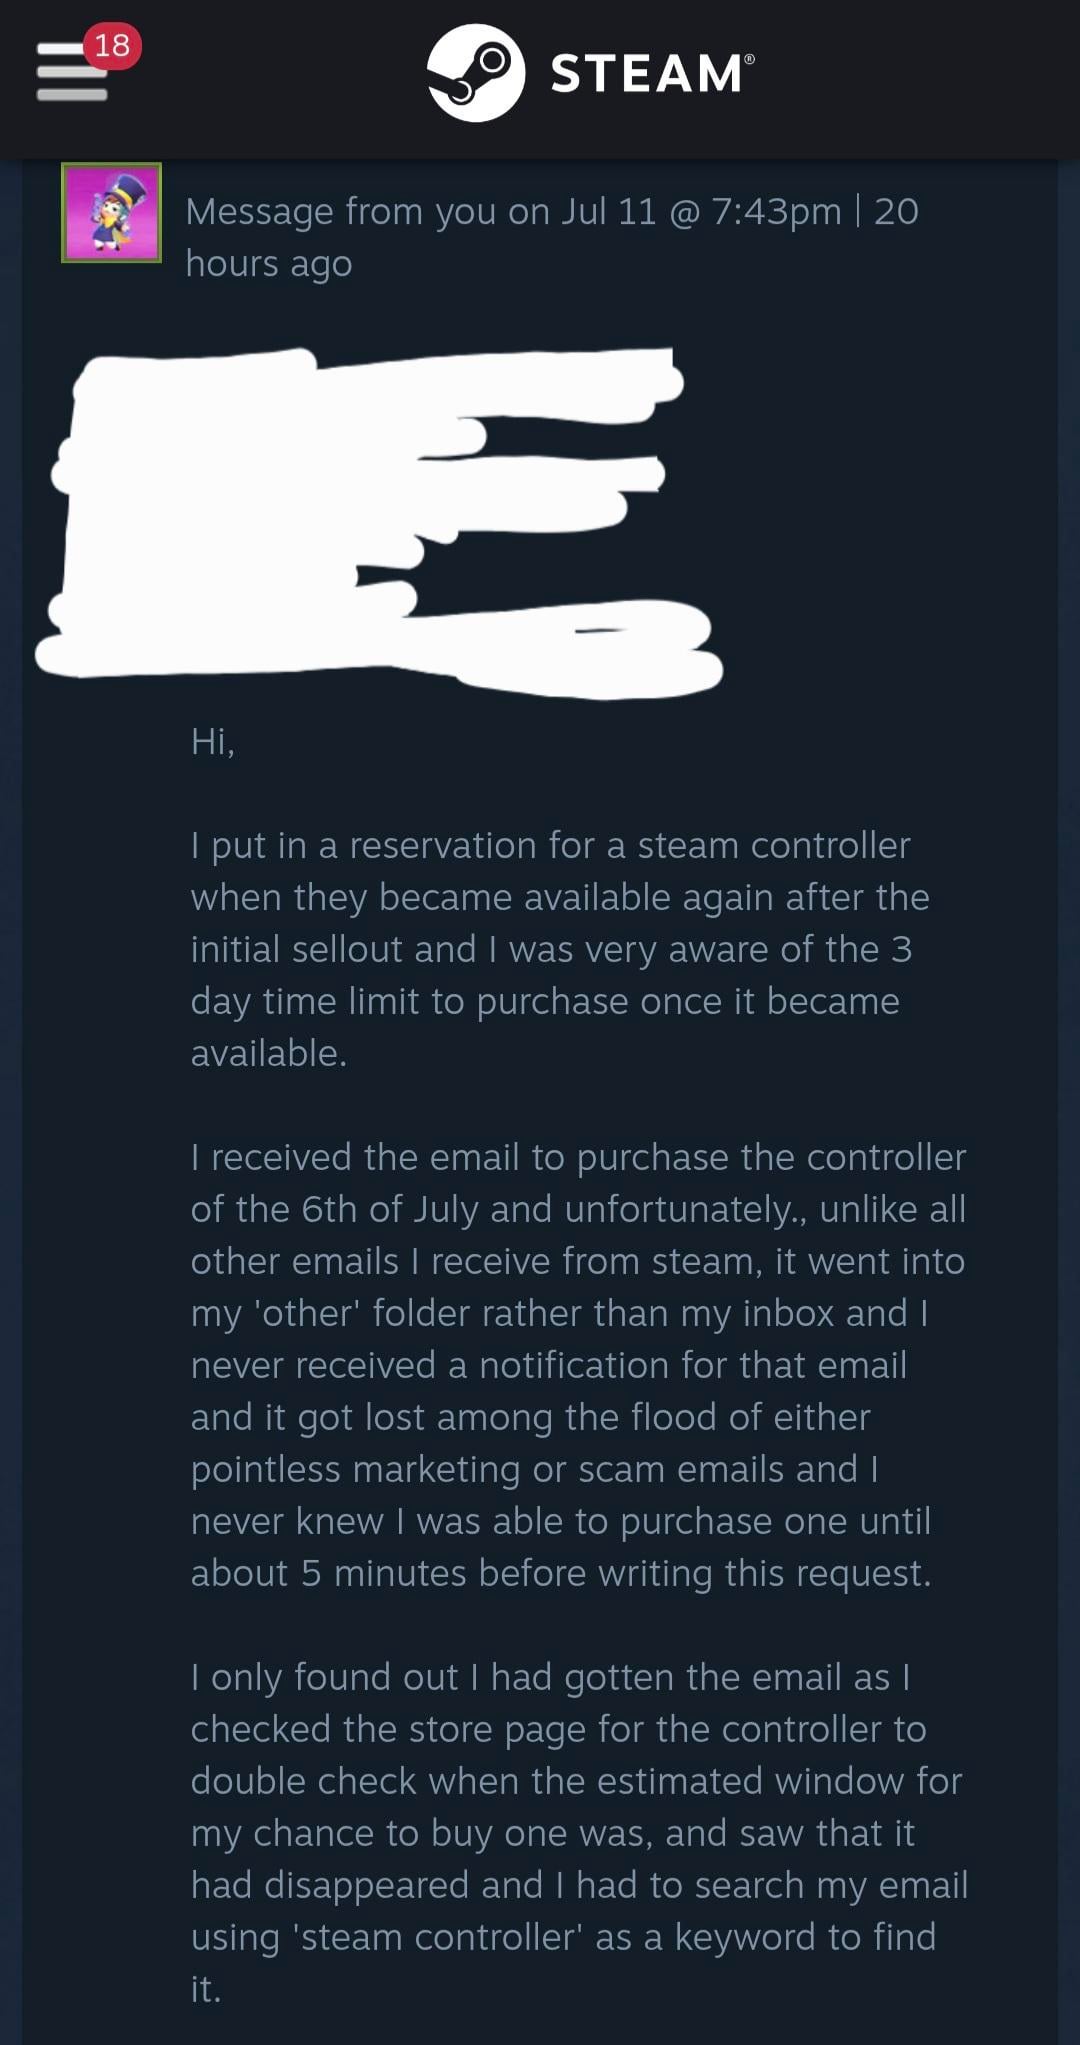
Steam support coming through as always : r/Steam
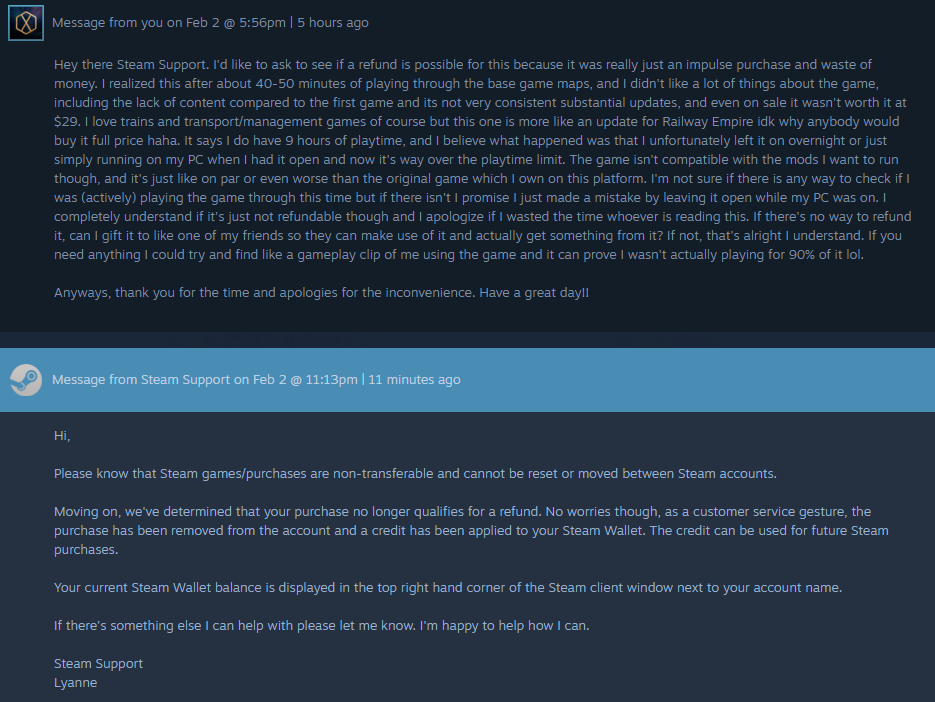
Steam Support is simply outstanding : r/Steam
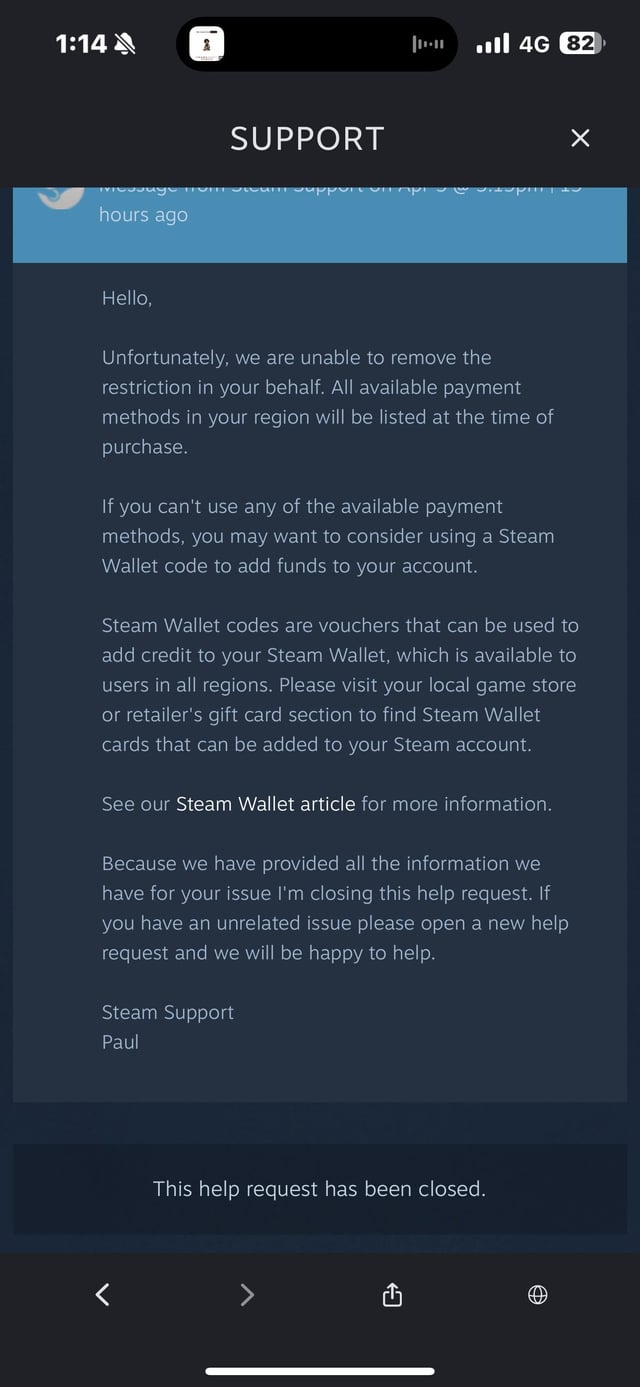
Hey anyone else faced this? : r/Steam
Wired Mail from Steam : r/Steam
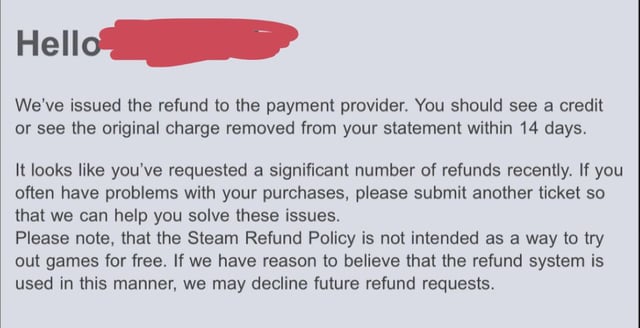
Has anyone actually had refund requests declined? : r/Steam
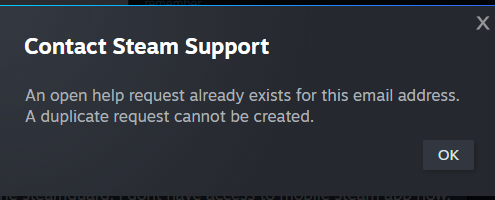
r/Steam Monthly Community Support Thread. : r/Steam
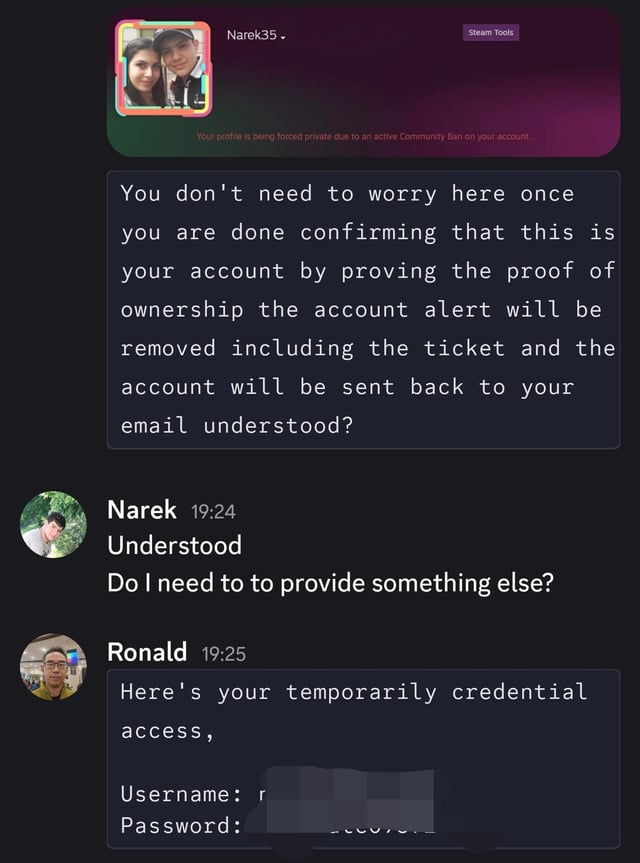
Is this normal with the Steam Support : r/Steam
r/Steam Monthly Community Support Thread. : r/Steam
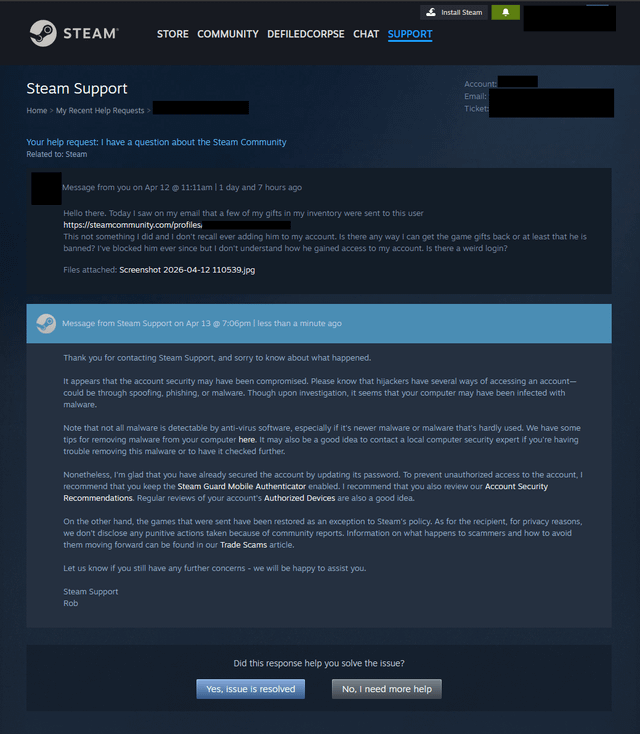
This is why Steam will always have me as a client : r/Steam
Steam did something for me, Which i will never forget : r/Steam
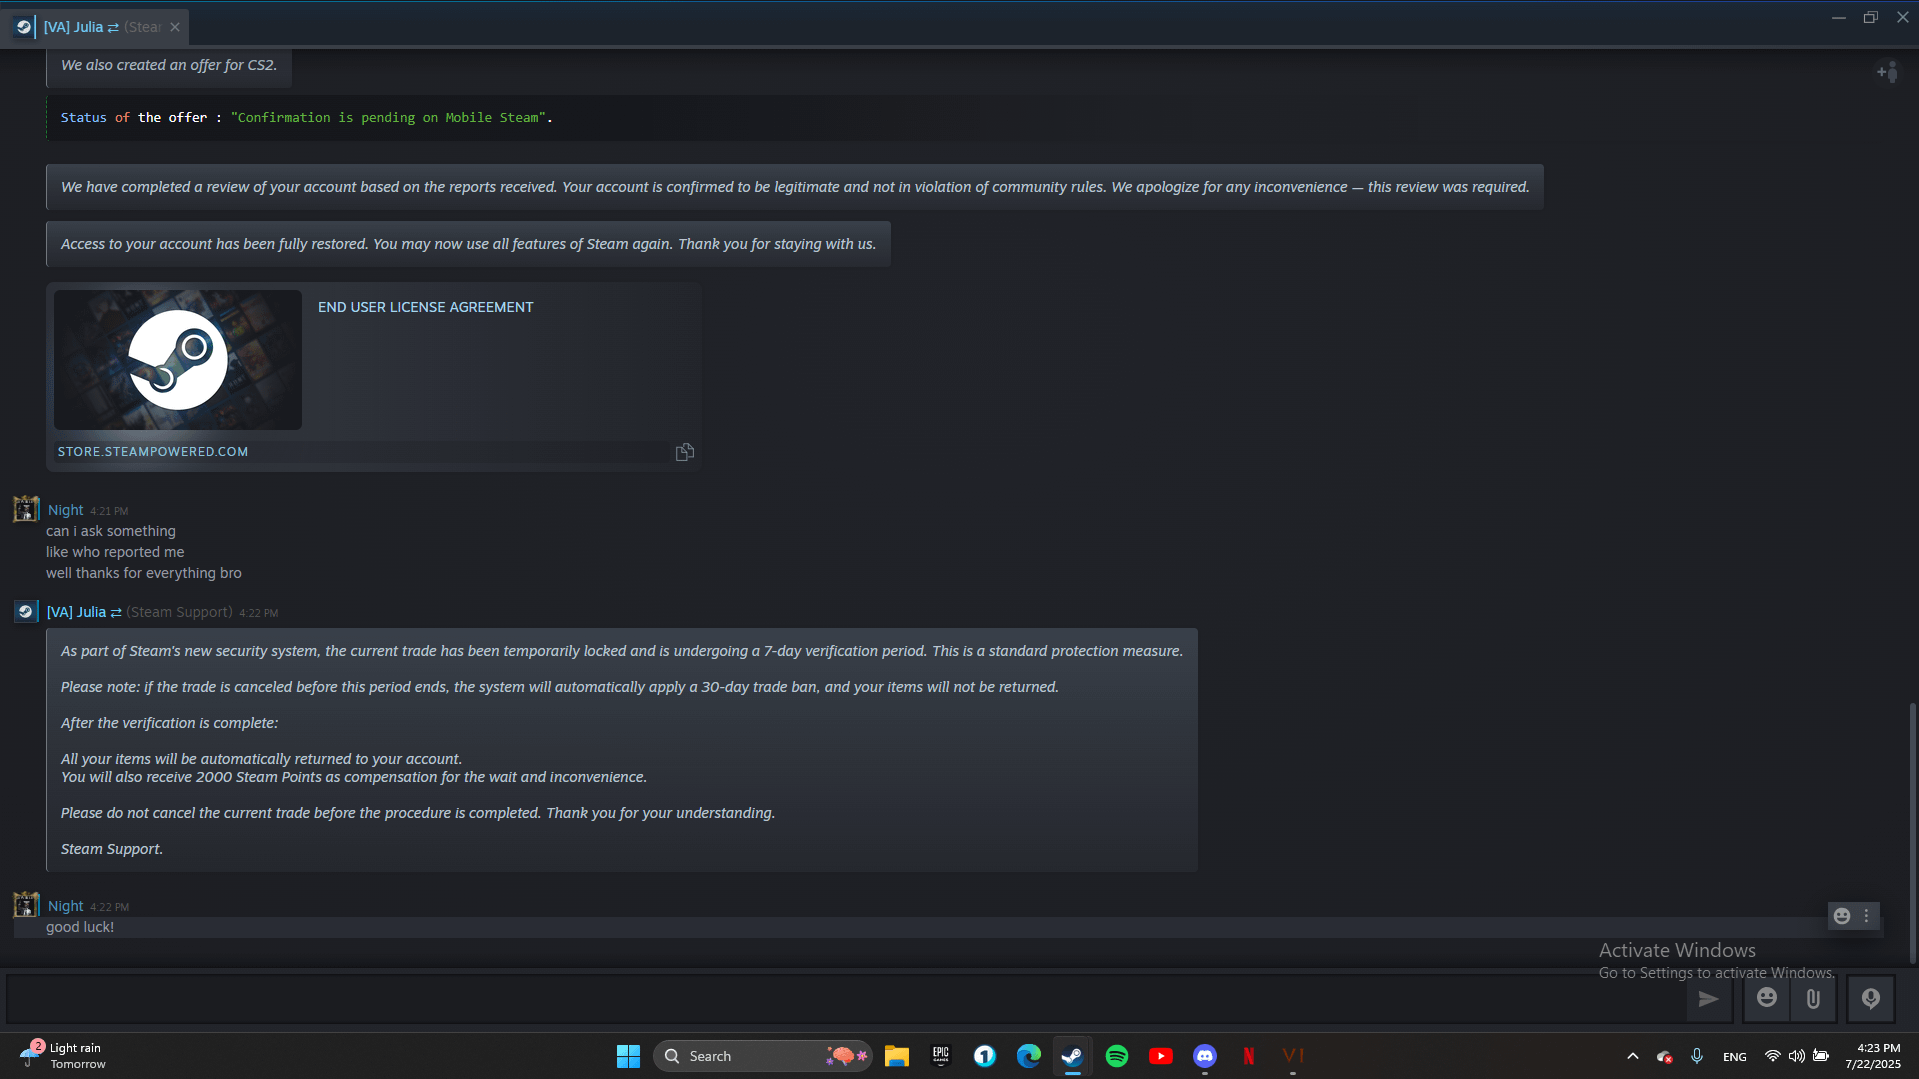
scam: [WARNING] Beware of Advanced Steam Support Scams – Don't Lose Your Items! : r/Steam
r/Steam Monthly Community Support Thread. : r/Steam
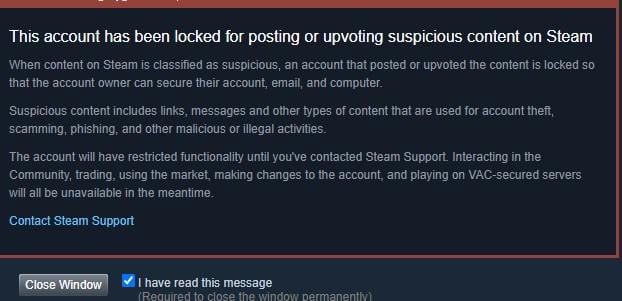
tf?, just got this message today, have not ever posted : r/Steam
r/Steam Monthly Community Support Thread. : r/Steam
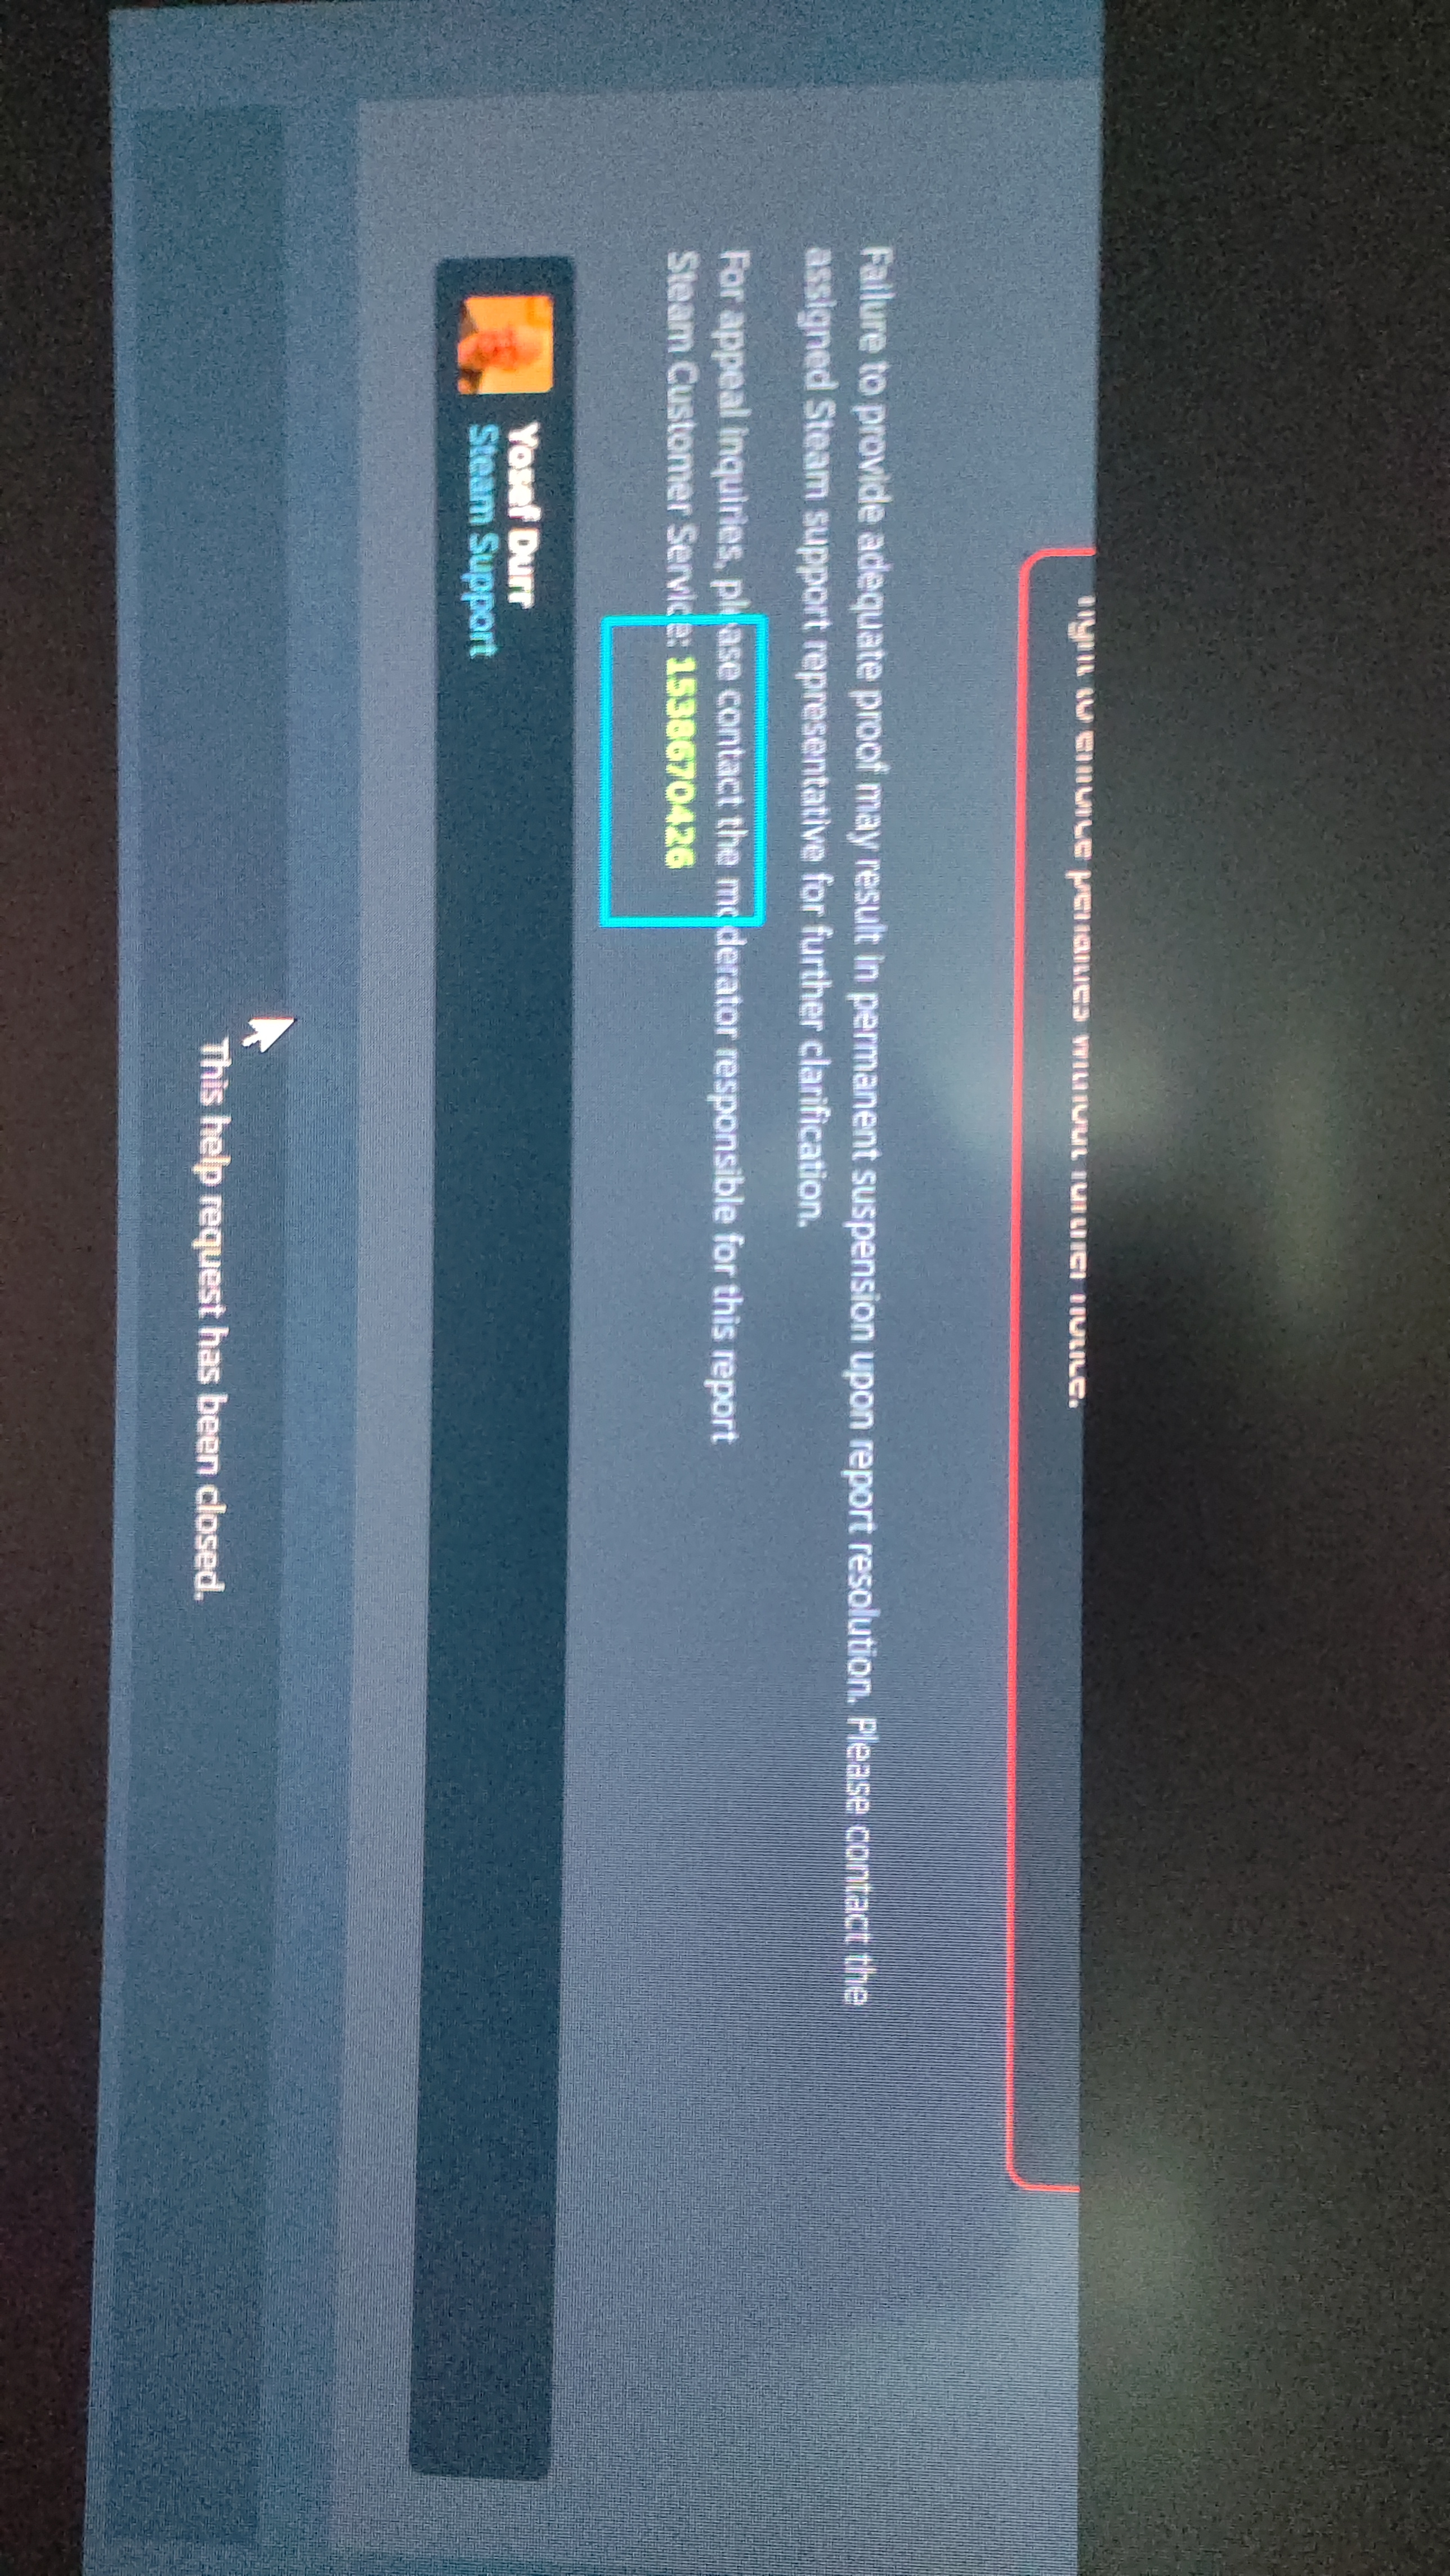
Props to Steam Support: Got my hacked account back in under 6 hours : r/Steam
Joining a family, where does this confirmation request get sent? : r/Steam
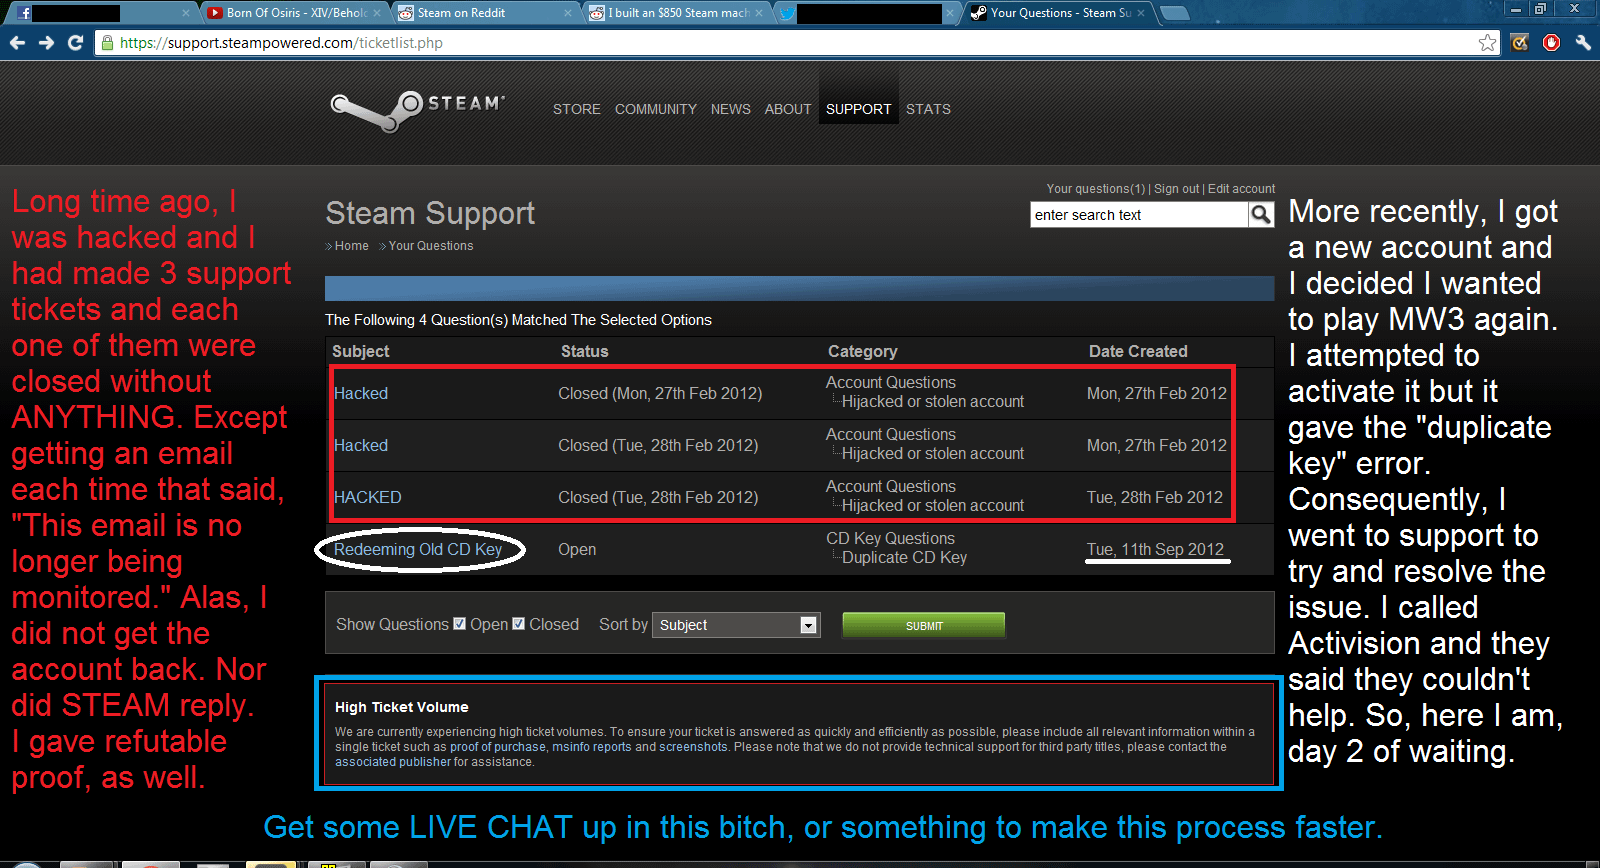
STEAM support is getting terrible. : r/Steam
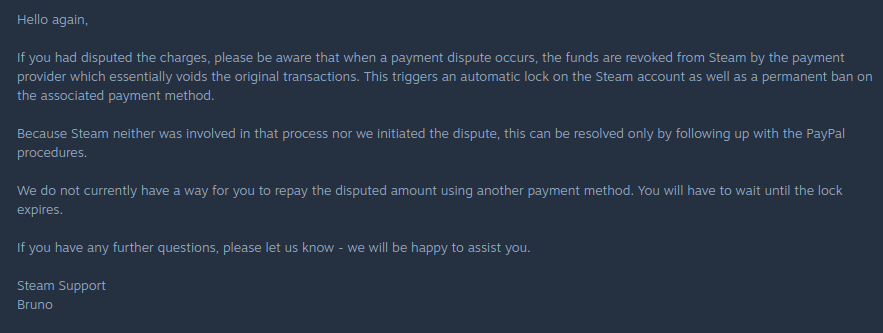
r/Steam Monthly Community Support Thread. : r/Steam
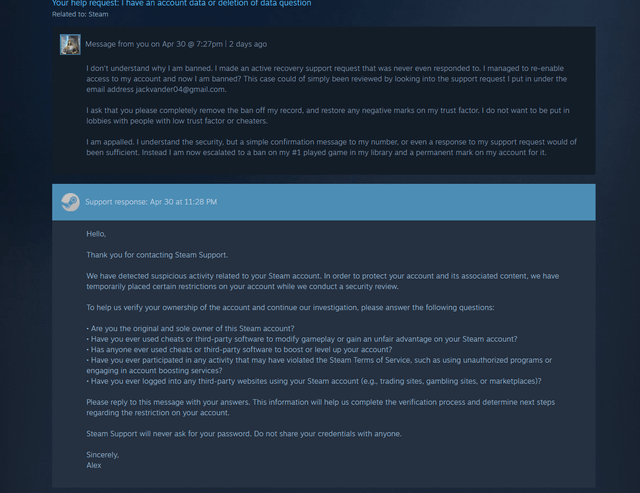
Steam Support Ticket Possibly Compromised ( HELP ) : r/cs2
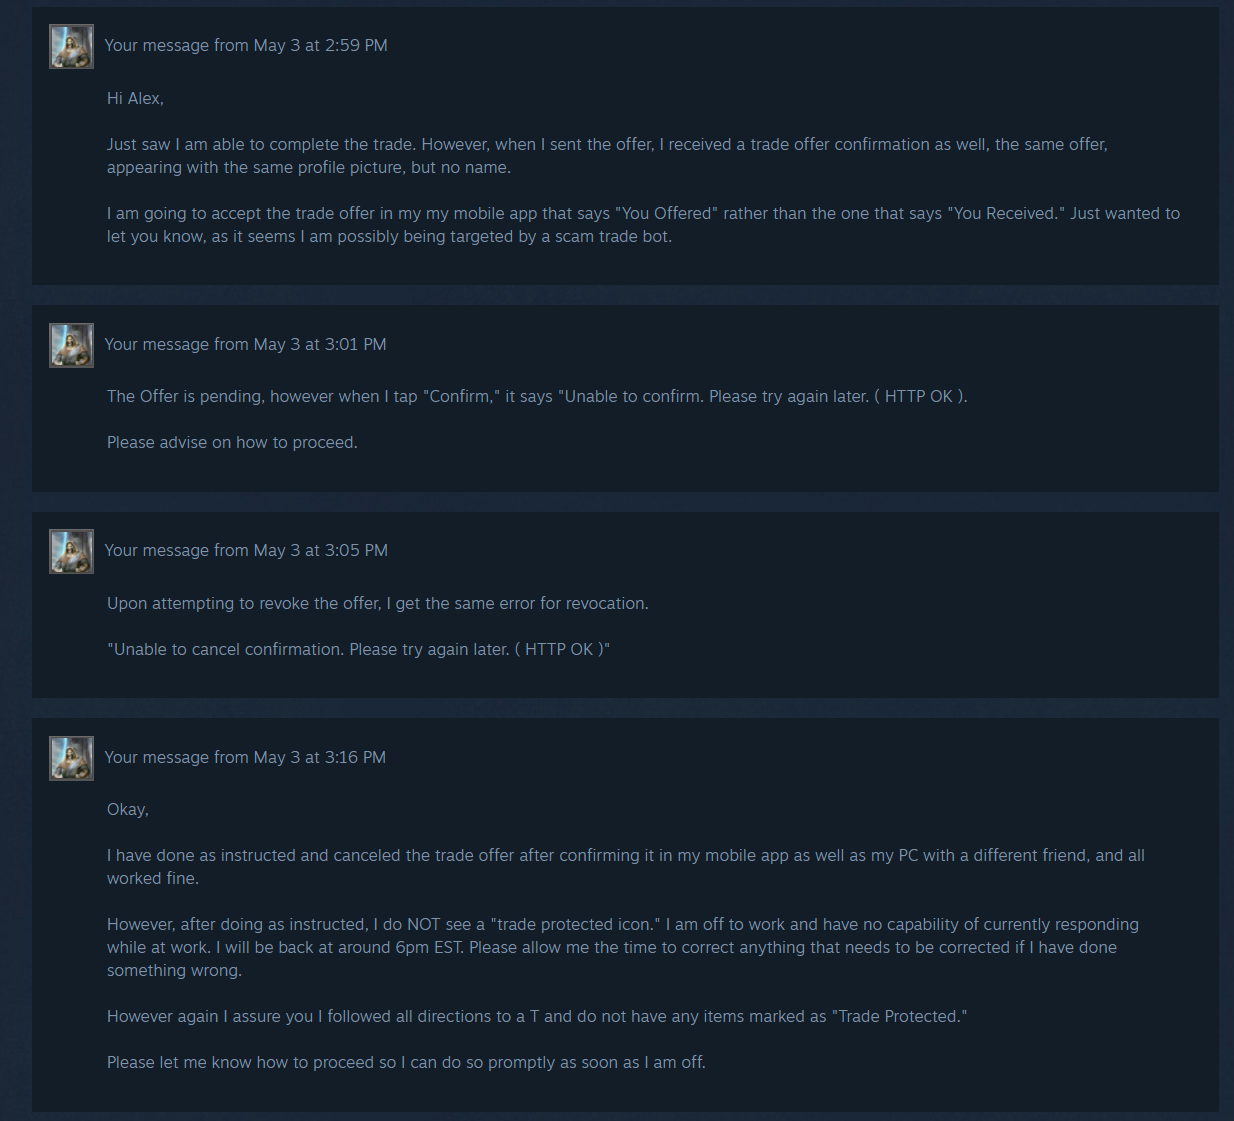
Steam Support Ticket Possibly Compromised ( HELP ) : r/cs2

Discord Steam Scam: Signs & What to Do
Welcome to Doll Town (@lifeindolltown) / X
How To Contact Steam Support (Quick Tutorial)
Steam Community :: Guide :: YIIN Defense Of YIIK: A Postmodern Review; ABSOLUTE TRUTH
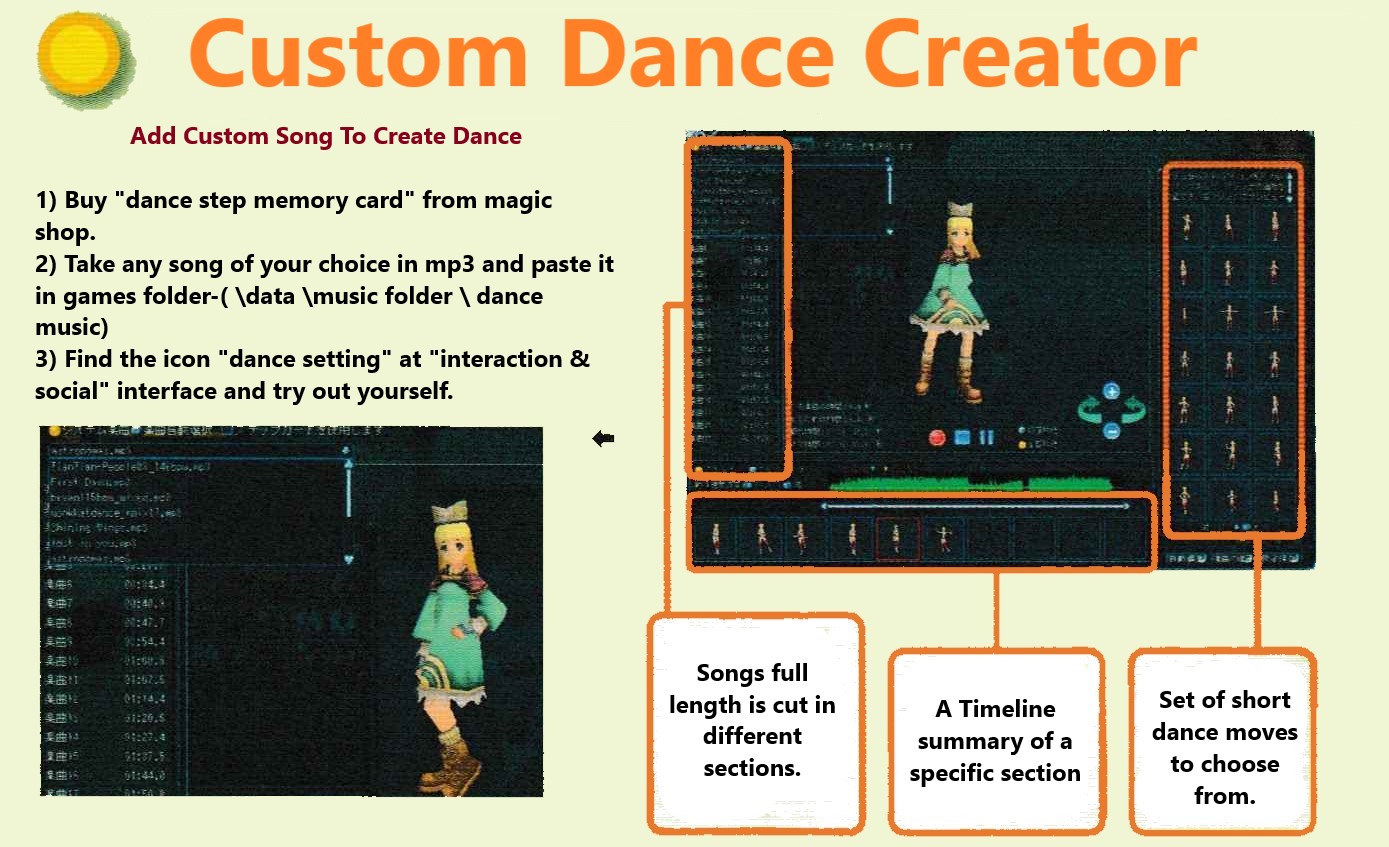
Steam Community :: Guide :: Road Map To Everything (still underway)
Ladies and Gentlemen, you’re officially Welcome to Doll Town. 🤍, https://t.co/054pxvD0Uk
Age Check Requirement to Chat Now Live Globally - Page 3 - Announcements - Developer Forum | Roblox
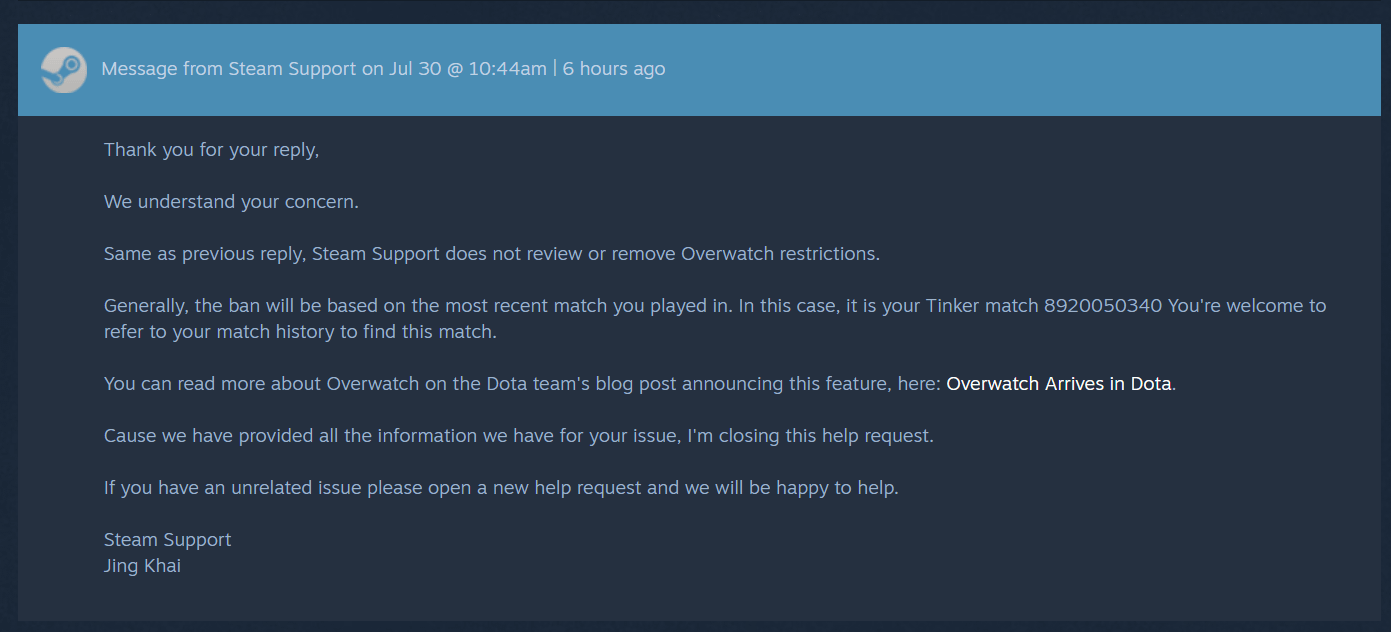
Part2 of: I got low priority after only 4 games. This time, Steam support provided me the match ID : r/DotA2
Steam Community :: Guide :: Murder at the Birch Tree Theater - Hint Guide
Steam Community :: Guide :: Murder at the Birch Tree Theater - Hint Guide
Steam Community :: Guide :: Murder at the Birch Tree Theater - Hint Guide
The fights did last around 17 minutes each though... : r/CalamityMod
Steam Community :: Guide :: Murder at the Birch Tree Theater - Hint Guide
Steam Community :: Guide :: Easter Eggs
Steam Community :: Guide :: Easter Eggs
Steam Community :: Guide :: Easter Eggs
The Game Awards 2016 : r/Steam
Steam-fællesskab :: Guide :: Guide for Moon [2020 updated]
Comunidade Steam :: Black Squad
Steam Community :: Guide :: Easter Eggs
Steam Community :: Guide :: Easter Eggs
Steam-Community :: Guide :: Guide for Origins [2020 updated]
Steam-fællesskab :: Guide :: Guide for Moon [2020 updated]
Steam-fællesskab :: Guide :: Guide for Moon [2020 updated]
Steam-fællesskab :: Guide :: Guide for Moon [2020 updated]
Steam Community :: Guide :: General Tips and Hard to Find Information
Steam-Community :: Guide :: Guide for Origins [2020 updated]
Thoughts about the game (Spoiler heavy) :: True Fear: Forsaken Souls Part 2 Allgemeine Diskussionen
Steam Community :: Guide :: Easter Eggs
Part2 of: I got low priority after only 4 games. This time, Steam support provided me the match ID : r/DotA2
Сообщество Steam :: Black Squad
Crashing after certain enemies :: GRANDIA II HD Remaster General Discussions
Сообщество Steam :: Black Squad
Part2 of: I got low priority after only 4 games. This time, Steam support provided me the match ID : r/DotA2
Haunted Arcade bei Steam
Steam Community :: Guide :: Card Tier List and Effectiveness
Haunted Arcade bei Steam
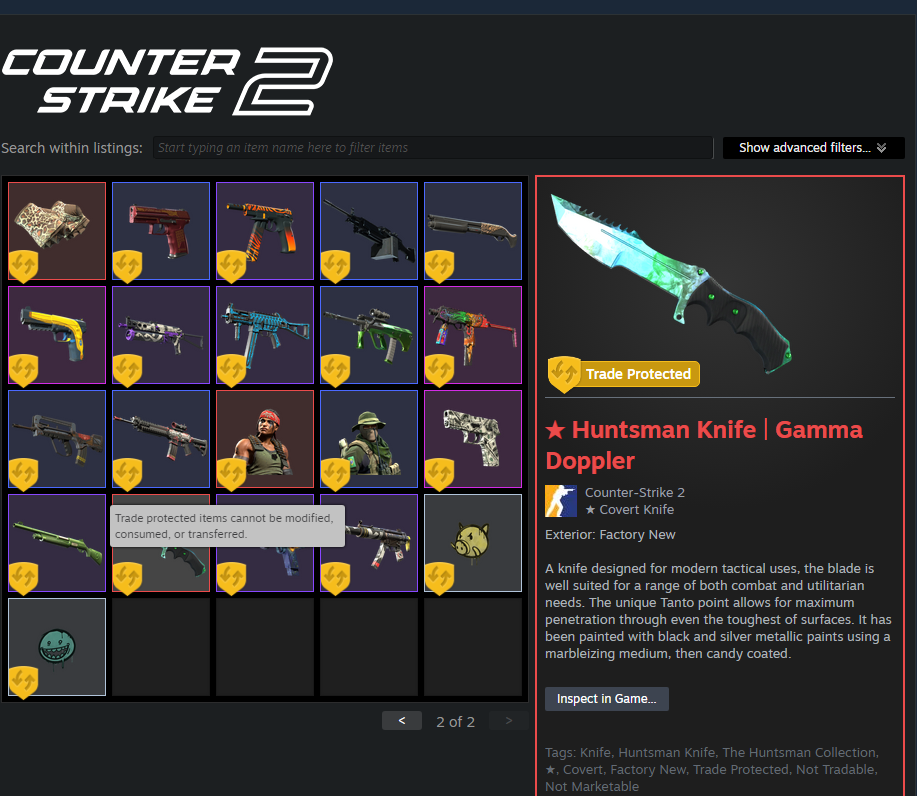
scam steam support nuked my cs2 inventory? : r/SteamScams
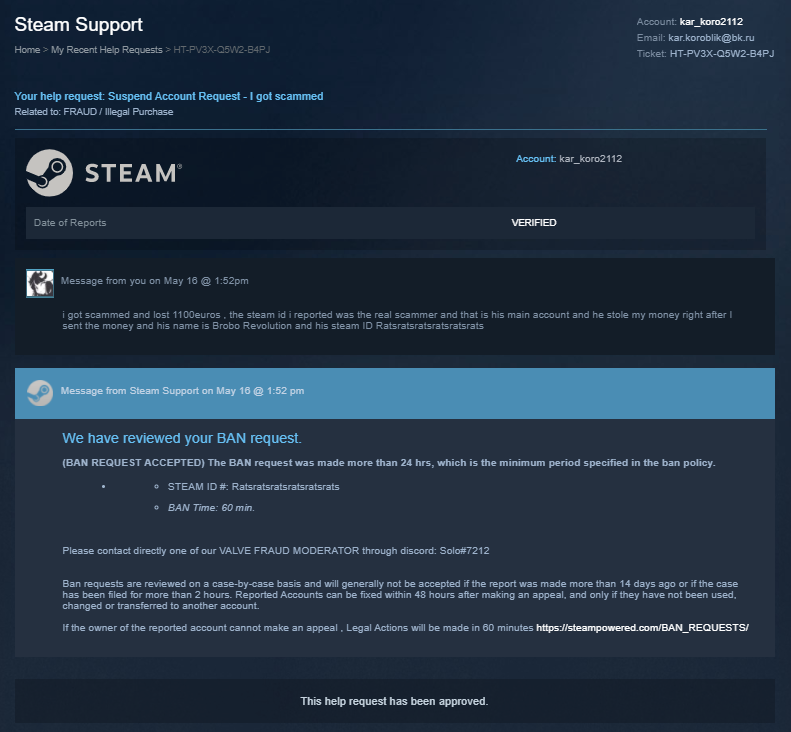
Is this a real message from steam support? : r/SteamScams
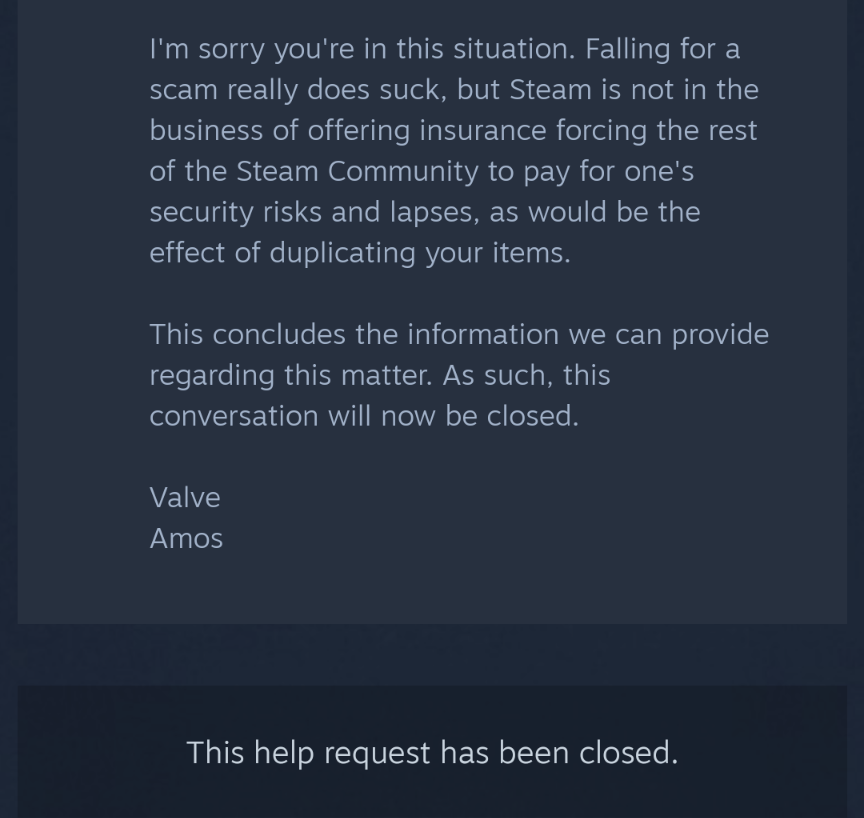
I was in contact with Steam Support for days because my account was hacked and they stole all of my items and this was their final response before closing my ticket after
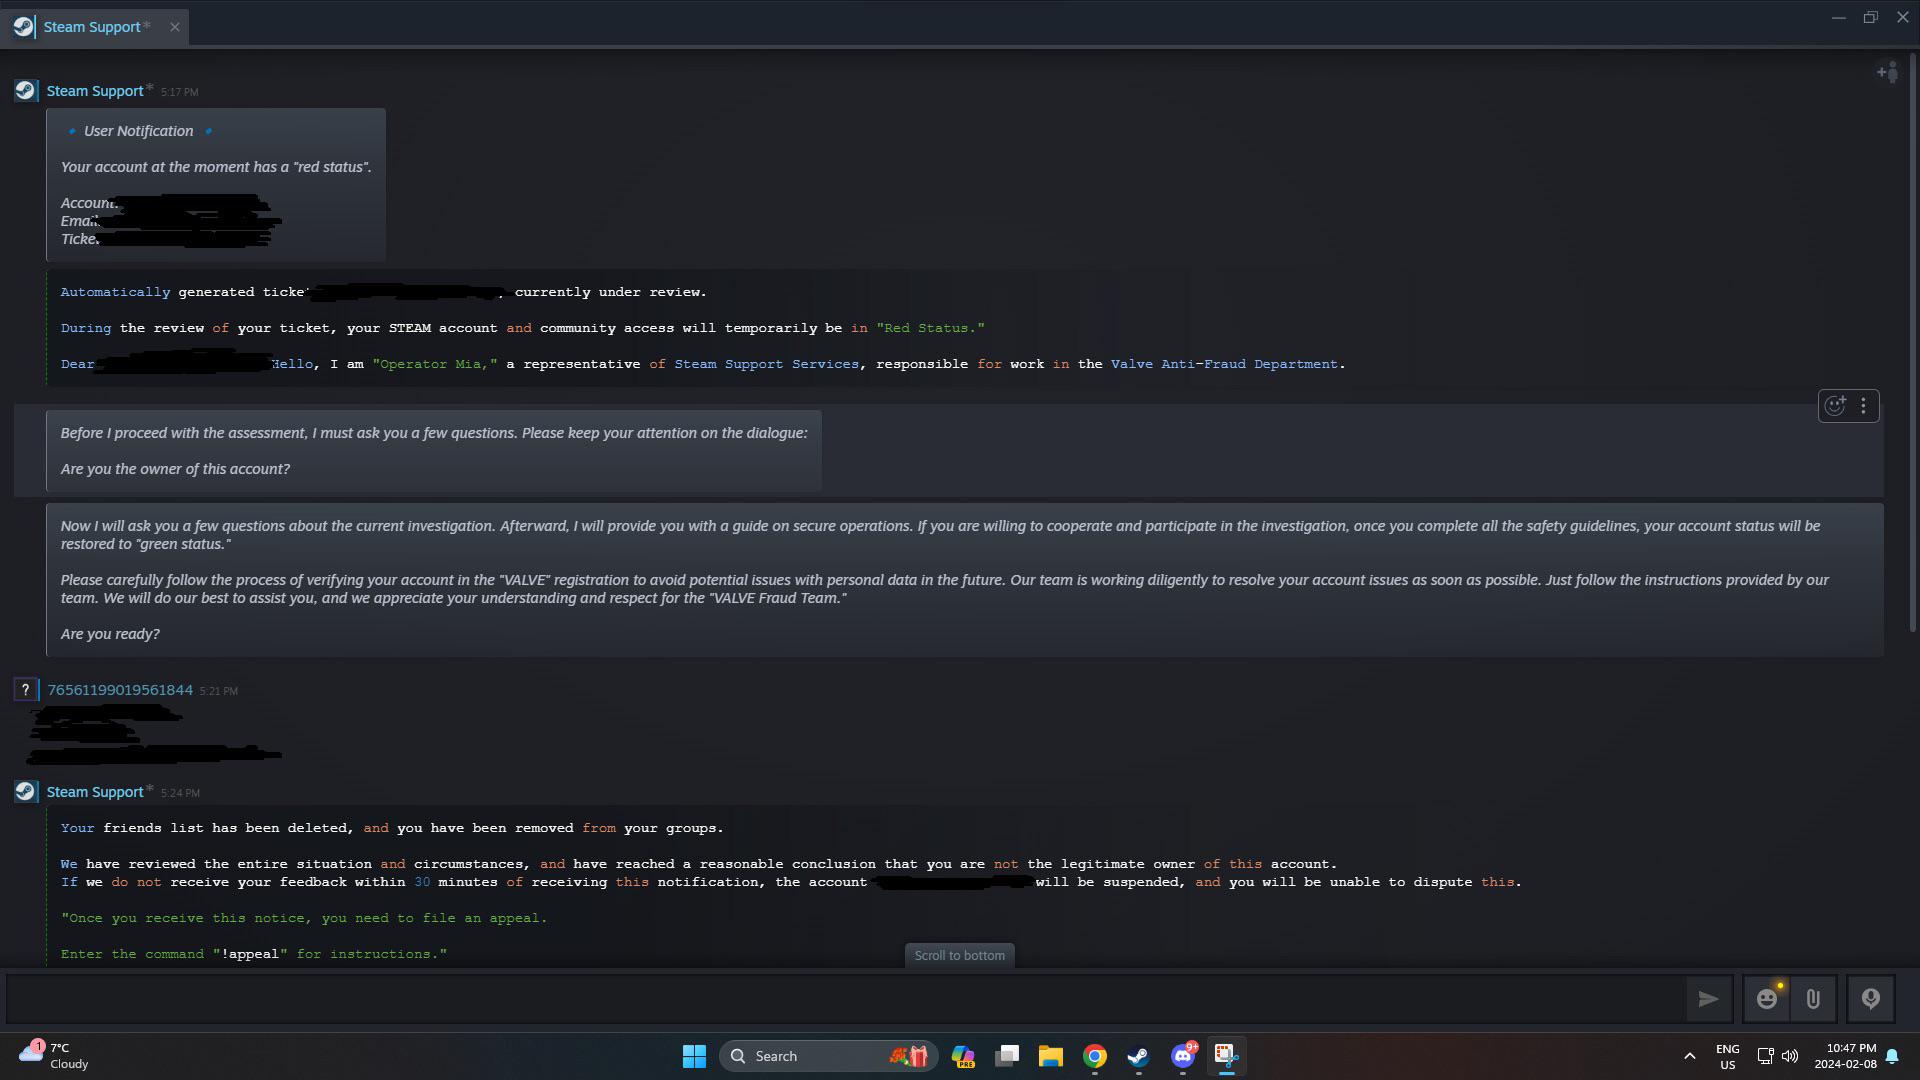
Real message from steam support? : r/SteamScams
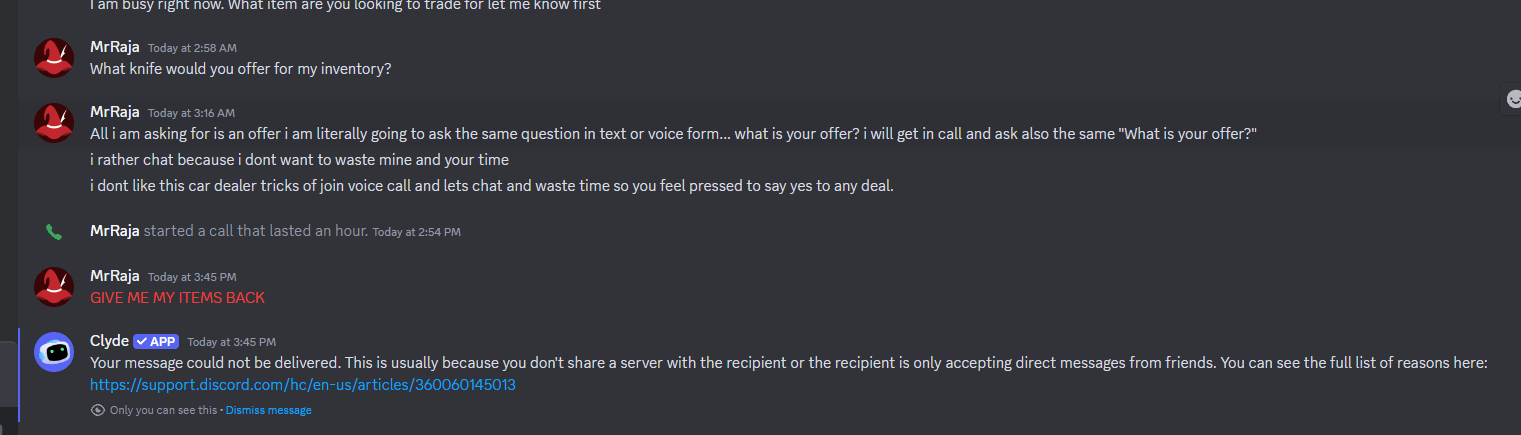
It finally happened to me... i lost my knife and many more items... I hope Steam Support returns them to me. : r/SteamScams
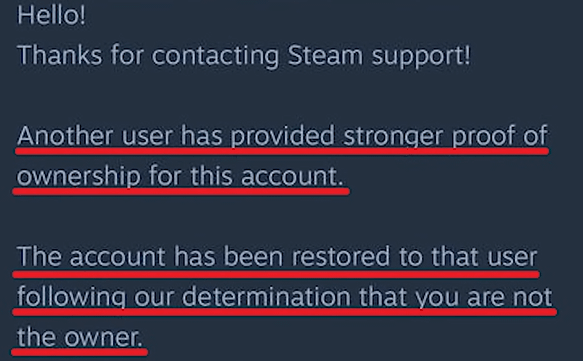
Steam support is stealing accounts again. : r/cs2
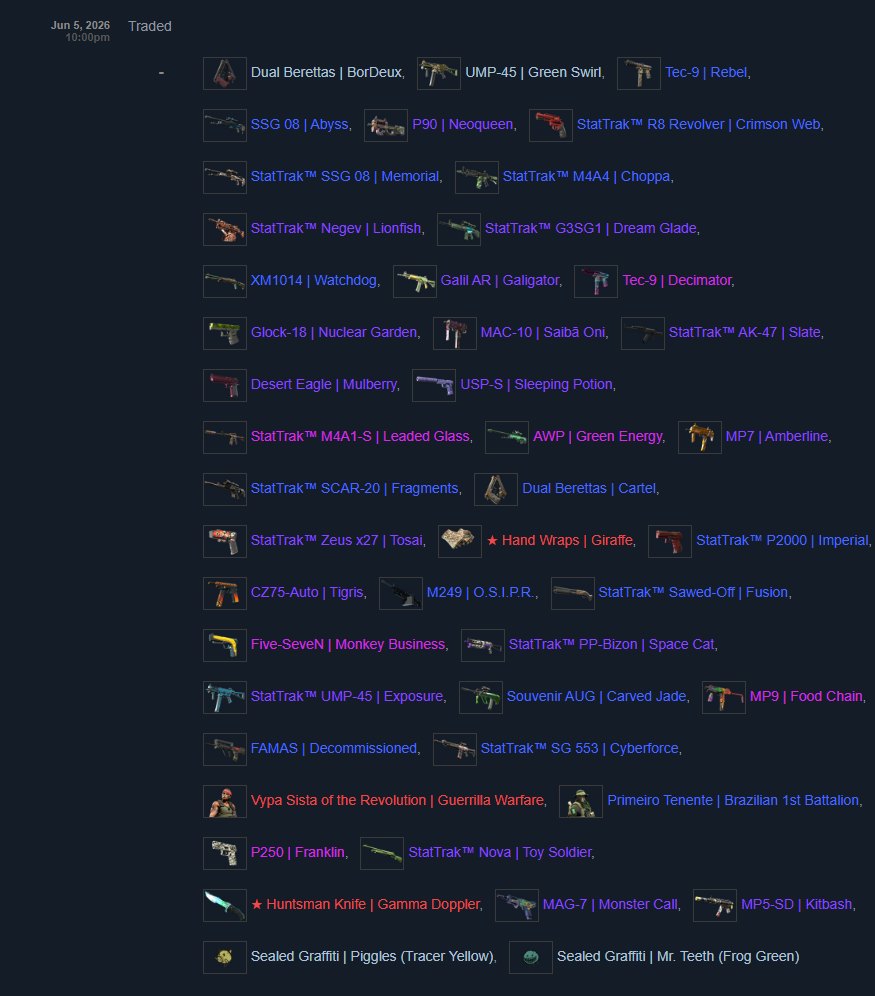
scam steam support nuked my cs2 inventory? : r/SteamScams