VirusTotal
2 / 92 engine detections
Abrir relatório

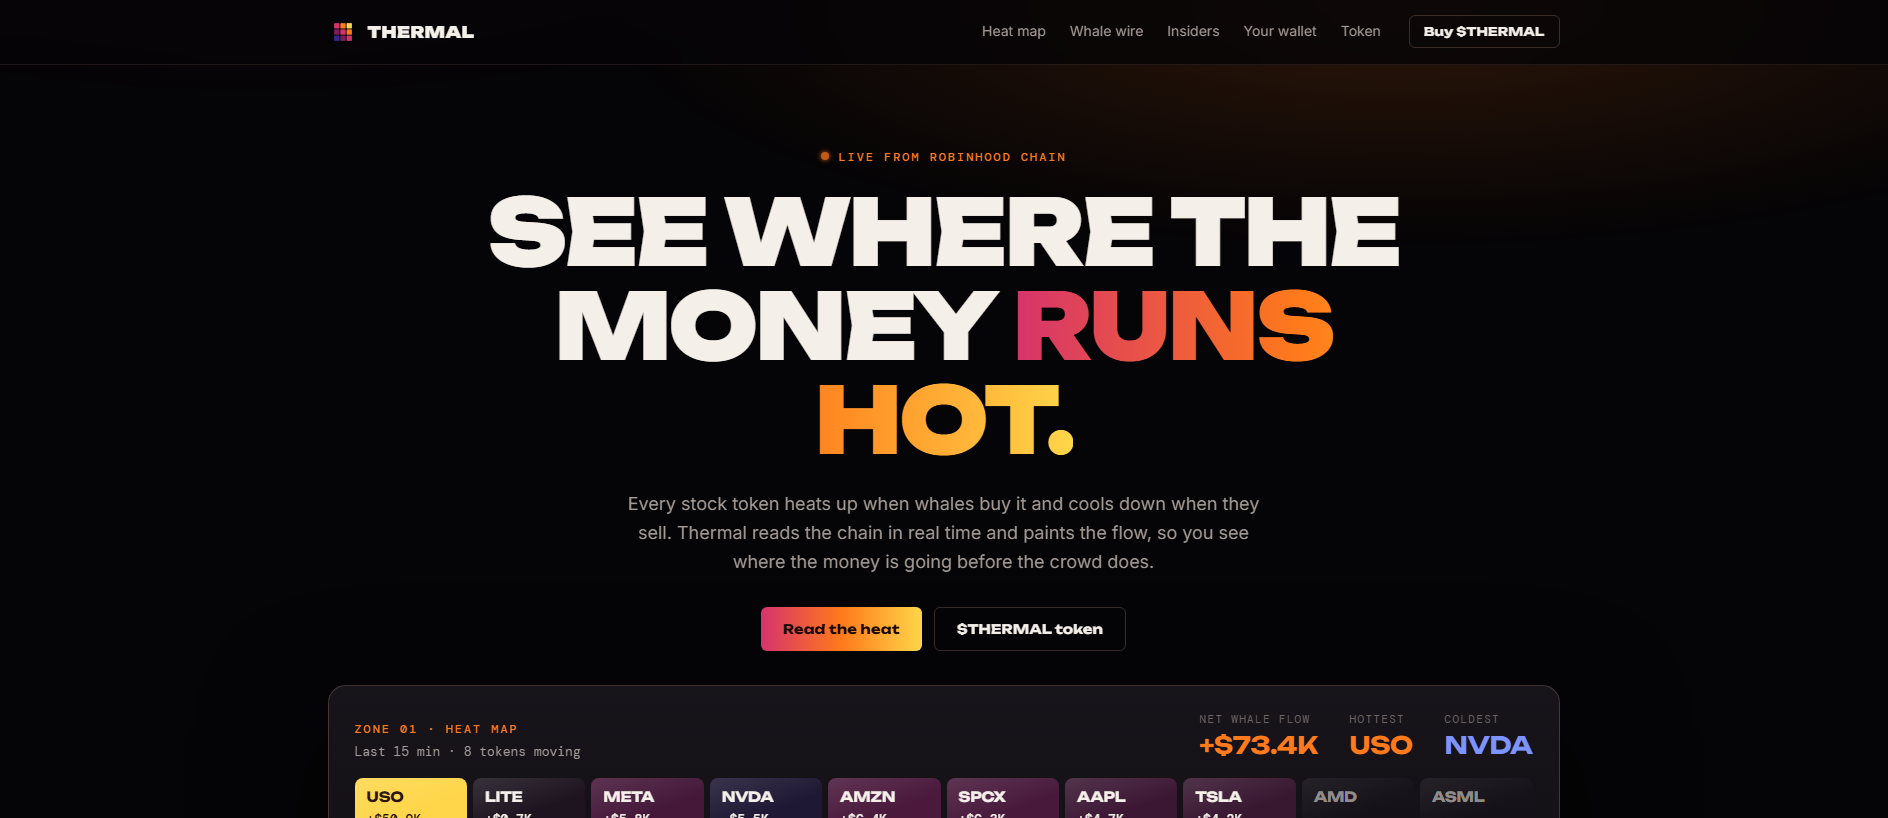
“Thermal — see where the money runs hot”
Imitação de American express: thermalrobin.xyz — Não verificado. Resumo das evidências: VirusTotal 2/92 (Forcepoint ThreatSeeker, Fortinet); URLScan capture…
A análise detalhada do PhishDestroy AI permanece em inglês para preservar o registro forense original.
2 / 92 engine detections
Abrir relatórioDBL_SPAM
Scan report
Abrir relatório4 community references
Abrir relatórioScan report
Abrir relatórioNo threat flag
Abrir relatórioPage capture
Abrir relatórioResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
PhishDestroy lists thermalrobin.xyz on its internal blocklist as a suspicious domain. The recorded page title is “Thermal — see where the money runs hot.” The domain was first seen by PhishDestroy on 2026-10-20, three days after its registration on 2026-10-17.
No specific malicious scheme has been observed for this domain; the listing reflects a general risk that the site could be used for phishing, fraud, or other illicit activity. The title alone does not prove any particular intent.
VirusTotal reported 2 detections out of 92 engines on 2026-10-20, with Forcepoint ThreatSeeker and Fortinet flagging the site. Google Safe Browsing checked on 2026-10-20 did not flag the URL. External blocklists checked on 2026-10-20 returned zero hits. PhishDestroy’s internal blocklist marked the domain as suspicious on 2026-10-20. OTX listed four pulses referencing the domain on 2026-10-20.
The domain was registered on 2026-10-17 through NICENIC INTERNATIONAL GROUP CO., LIMITED. The recorded IP address associated with the site is 188.114.97.3.
If you visited the site, do not assume compromise but avoid entering credentials or personal data. Change any passwords that may have been entered and monitor accounts for unusual activity. Security teams should add the exact domain to blocklists and review logs for connections to 188.114.97.3. Continue to monitor reputable threat feeds for any future updates on this domain.
 (RU)
PhishDestroy Investigation
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
A reputação do Edge-IP não é atribuída a este domínio.
kyrie.ns.cloudflare.comsuzanne.ns.cloudflare.comLocation describes the IP network.
Google PageSpeed Insights — mobile performance audit of thermalrobin.xyz · checked Oct 20, 2026
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
https://thermalrobin.xyz/Content-Type: text/htmlServer: cloudflareCF-Cache-Status: DYNAMICContent-Encoding: gzipsummaryh3=":443"; ma=86400DYNAMICa4d83d386abb1c85-FRAkeep-alivegzipupgrade-insecure-requeststext/htmlTue, 20 Oct 2026 13:06:19 GMTSat, 17 Oct 2026 07:41:35 GMT{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}hpanelhostinger{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=NZ4kRbY5k7ywZsj68kaBvnbYDSIvKbHvvGZ2Aypronq2yOr1mpkD49KabMaDqH77T26qTWxpKVTAQnN1O5INuh2TjaXUv3TS081KMb4JgoHEqI35Ooko4C6Dy6dNdGt0cCO7"}]}cloudflarechunkedAccept-EncodingLiteSpeedValues retained by the collector; long values may be shortened during collection.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Acessível
4 community references
View sourceNo threat flag
View source2/92 engine detections
View sourcePD-20261020-B431C3
thermalrobin.xyz
View sourcePage captured
View sourceCada faixa representa um motivo pelo qual um domínio está vinculado a este host. O tamanho dos nós indica as detecções do VirusTotal, e os nós tracejados já estão offline. As listas completas seguem abaixo.
Esses relatórios são resolvidos para o mesmo IP de borda compartilhado. Eles ajudam na descoberta de relatórios, mas não implicam propriedade comum ou um servidor de origem compartilhado.
Registrados pelo mesmo registrador. Um registrador atende a milhões de clientes sem qualquer relação entre si; portanto, isso apenas agrupa os registros, em vez de comprovar uma ligação.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
thermalrobin.xyz
PD-20261020-B431C3 Recipient: abuse@gen.xyz Registrar: NICENIC International Group Co., Limited (Hong Kong (China)) Policy Violations: “Services may be used only for lawful purposes… fraud, abuse and illegal activity prohibited. Violations may result in immediate suspension.” + dedicated abuse handling and takedown Applicable Laws: Crimes Ordinance Cap.200 (Fraud), Theft Ordinance Cap.210 §16A (fraud by deception), Personal Data (Privacy) Ordinance Cap.486
Se você inseriu credenciais de conta, informações pessoais ou de pagamento, ou baixou um arquivo deste domínio, tome medidas imediatas. Abaixo estão os recursos para ajudá-lo a relatar o incidente e se proteger.


Selecione seu país para obter contactos oficiais do cibercrime ou crie um rascunho de reclamação →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
thermalrobin.xyz)Mesmo que você não tenha todos os detalhes — registre uma ocorrência mesmo assim. Mesmo informações parciais ainda ajudam nas investigações.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Análise de ameaças usando lista de bloqueio armazenada, WHOIS, DNS e evidências de verificação pública
Digitalize agoraEnvie domínios suspeitos para nosso banco de dados de ameaças — proteja a comunidade
DenunciarRelatórios recentes de phishing e alterações de disponibilidade observadas
MonitorarMonitore ameaças em tempo real ou conteste esta listagem caso acredite que se trate de um falso positivo
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.