VirusTotal
11 / 91 engine detections
Abrir relatório

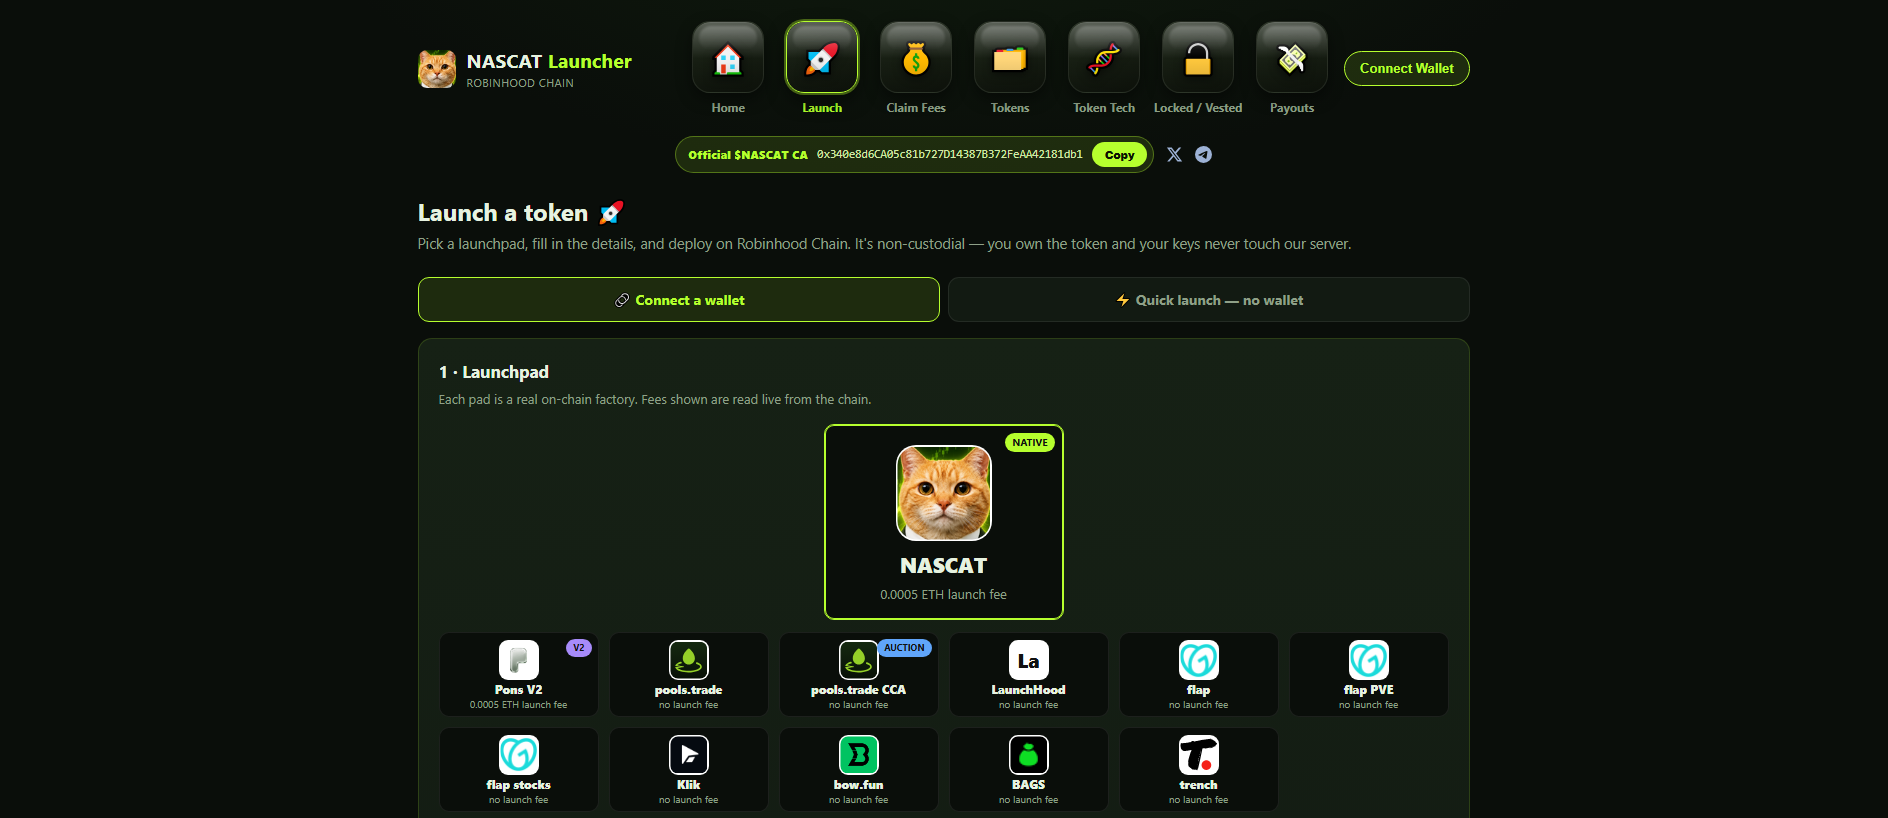
“NASCAT Launcher — launch a token on Robinhood Chain”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@digitalocean.com.
The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Imitação de Robinhood: launcher.robinhoodnascat.fun — Último ativo conhecido (HTTP 200). Resumo das evidências: VirusTotal 11/91 (ChainPatrol…
A análise detalhada do PhishDestroy AI permanece em inglês para preservar o registro forense original.
11 / 91 engine detections
Abrir relatórioDBL_PHISH
checked — no detections recorded
Abrir relatóriono community references
Abrir relatórioprovider verdict: clean
Abrir relatório80/100
Abrir relatórioNo threat flag
Abrir relatórioNo malicious flag
Abrir relatórioResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
launcher.robinhoodnascat.fun is a phishing page that uses the Robinhood name to pass itself off as "NASCAT Launcher," a tool for launching tokens on Robinhood Chain. It targets crypto users and would-be token creators who trust the Robinhood brand and want early access to a new chain. PhishDestroy first flagged it on 2026-09-15. As of 2026-10-19 the site was still online and serving its content, so it remains a live risk.
The page title, "NASCAT Launcher — launch a token on Robinhood Chain," frames the site as an official-looking launchpad tied to Robinhood. Fake launchpads like this usually ask visitors to connect a wallet and then sign transactions or pay a "launch" or "listing" fee. Those requests can hand over funds or grant token spending permissions to the operators. Anything sent or approved goes to the scammers, not to Robinhood, and on-chain transfers generally cannot be reversed.
On 2026-09-25, 11 of 91 VirusTotal engines flagged the domain. They included the crypto-focused ChainPatrol alongside BitDefender, Fortinet, Forcepoint ThreatSeeker, G-Data, Gridinsoft, CRDF and alphaMountain.ai. That is a minority of engines, but the backing goes beyond VirusTotal. MetaMask and SEAL, both centred on Web3 threats, list the domain, as does PhishDestroy. Spamhaus also lists it in its Domain Block List as DBL_PHISH, which means mail and network filters that use Spamhaus treat it as phishing.
The domain was registered through Name.com, Inc. on 2026-07-10, about two months before PhishDestroy detected it. That gap suggests it was set up ahead of time rather than thrown together the same day. The site runs on DigitalOcean cloud hosting in the United States. The "launcher" subdomain on a brand-themed .fun domain mimics the naming of real token launch tools.
Do not connect a wallet or pay any launch, listing or gas fee on this site. If you already connected, use a token approval checker to revoke any permissions granted during the visit. Move remaining assets to a fresh wallet if you signed anything you did not understand. Never type a seed phrase into a site like this; if you did, treat that wallet as compromised and empty it right away. Defenders should block the domain at DNS and the mail gateway, and report sightings to the hosting provider and registrar.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
0x03DfbBE0AC4E7bCDaFd08eD41A400326B77D8c80Format validated · Domain analysis0x05a3d1Cd21d0C88145E82600E62e7E496e0F222BFormat validated · Domain analysis0x05b37Fb53A299a1b874A619e1c4C404D52C36F4CFormat validated · Domain analysis0x0Bd7D308f8E1639FAb988df18A8011f41EAcAD73Format validated · Domain analysis0x0b5fb4031cae9163db10B169Ee72685F0EdC8545Format validated · Domain analysis0x0f17206447090e464C277571124dD2688E48AEA9Format validated · Domain analysis0x116F00968269B7bfbaD4109cE591d6E74c0601d4Format validated · Domain analysis0x117cc2133c37B721F49dE2A7a74833232B3B4C0CFormat validated · Domain analysis0x12e3c047bf9AeCAF9dDC98c05C31BFD1dd043993Format validated · Domain analysis0x12f190a9F9d7D37a250758b26824B97CE941bF54Format validated · Domain analysis0x156E175DD063a8cE274C50654eF40e0032b3fbcFFormat validated · Domain analysis0x1AF6446f07eb1d97c546AFC8c9544cBDF3AD5137Format validated · Domain analysis0x1Cdad396DB64BDa184d5182A97Dd9B3C62100b7DFormat validated · Domain analysis0x1D11f0496982706C5e14A514D4E79F2e6BdE4516Format validated · Domain analysis0x1b0E319c6A659F002271B69dB8A7df2F911c153EFormat validated · Domain analysis0x232B8ed6377BE97813853B0Ac104c4Cda8378d1BFormat validated · Domain analysis0x237c16D66590F67B886d978ACD362EAeaD8B18c7Format validated · Domain analysis0x28bABD556b60E53663B8615036479a29c2CDd1BfFormat validated · Domain analysis0x2D3186185956F332F26C63A9823c731d362340b8Format validated · Domain analysis0x2D427692E928fa156ec22acfaBaFA0447C5805B7Format validated · Domain analysishttps://t.me/NascatRHCStored page referenceIoC extraction recorded 2026-09-16 04:00:14 UTC
Last checked
For the registrable domain robinhoodnascat.fun behind this subdomain, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
ns1.vercel-dns.comns2.vercel-dns.comLocation describes the IP network.
1fae03874c13707ee2fc3c91d6d641291b2611eb24b3c09c714390b9501afe50Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of launcher.robinhoodnascat.fun · checked Sep 15, 2026
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
launcher.robinhoodnascat.fun
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
6→9
Acessível
No threat flag
View source11/91 engine detections
View sourcePD-20260915-FEB965
launcher.robinhoodnascat.fun
View sourcePage captured
View sourceCada faixa representa um motivo pelo qual um domínio está vinculado a este host. O tamanho dos nós indica as detecções do VirusTotal, e os nós tracejados já estão offline. As listas completas seguem abaixo.
Reports with the same collector label. A shared label does not establish impersonation or common ownership. View matching reports →
Registrados pelo mesmo registrador. Um registrador atende a milhões de clientes sem qualquer relação entre si; portanto, isso apenas agrupa os registros, em vez de comprovar uma ligação.
PD-20260915-FEB965 Recipient: abuse@digitalocean.com Se você inseriu credenciais de conta, informações pessoais ou de pagamento, ou baixou um arquivo deste domínio, tome medidas imediatas. Abaixo estão os recursos para ajudá-lo a relatar o incidente e se proteger.


Selecione seu país para obter contactos oficiais do cibercrime ou crie um rascunho de reclamação →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
launcher.robinhoodnascat.fun)Mesmo que você não tenha todos os detalhes — registre uma ocorrência mesmo assim. Mesmo informações parciais ainda ajudam nas investigações.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Análise de ameaças usando lista de bloqueio armazenada, WHOIS, DNS e evidências de verificação pública
Digitalize agoraEnvie domínios suspeitos para nosso banco de dados de ameaças — proteja a comunidade
DenunciarRelatórios recentes de phishing e alterações de disponibilidade observadas
MonitorarMonitore ameaças em tempo real ou conteste esta listagem caso acredite que se trate de um falso positivo
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.