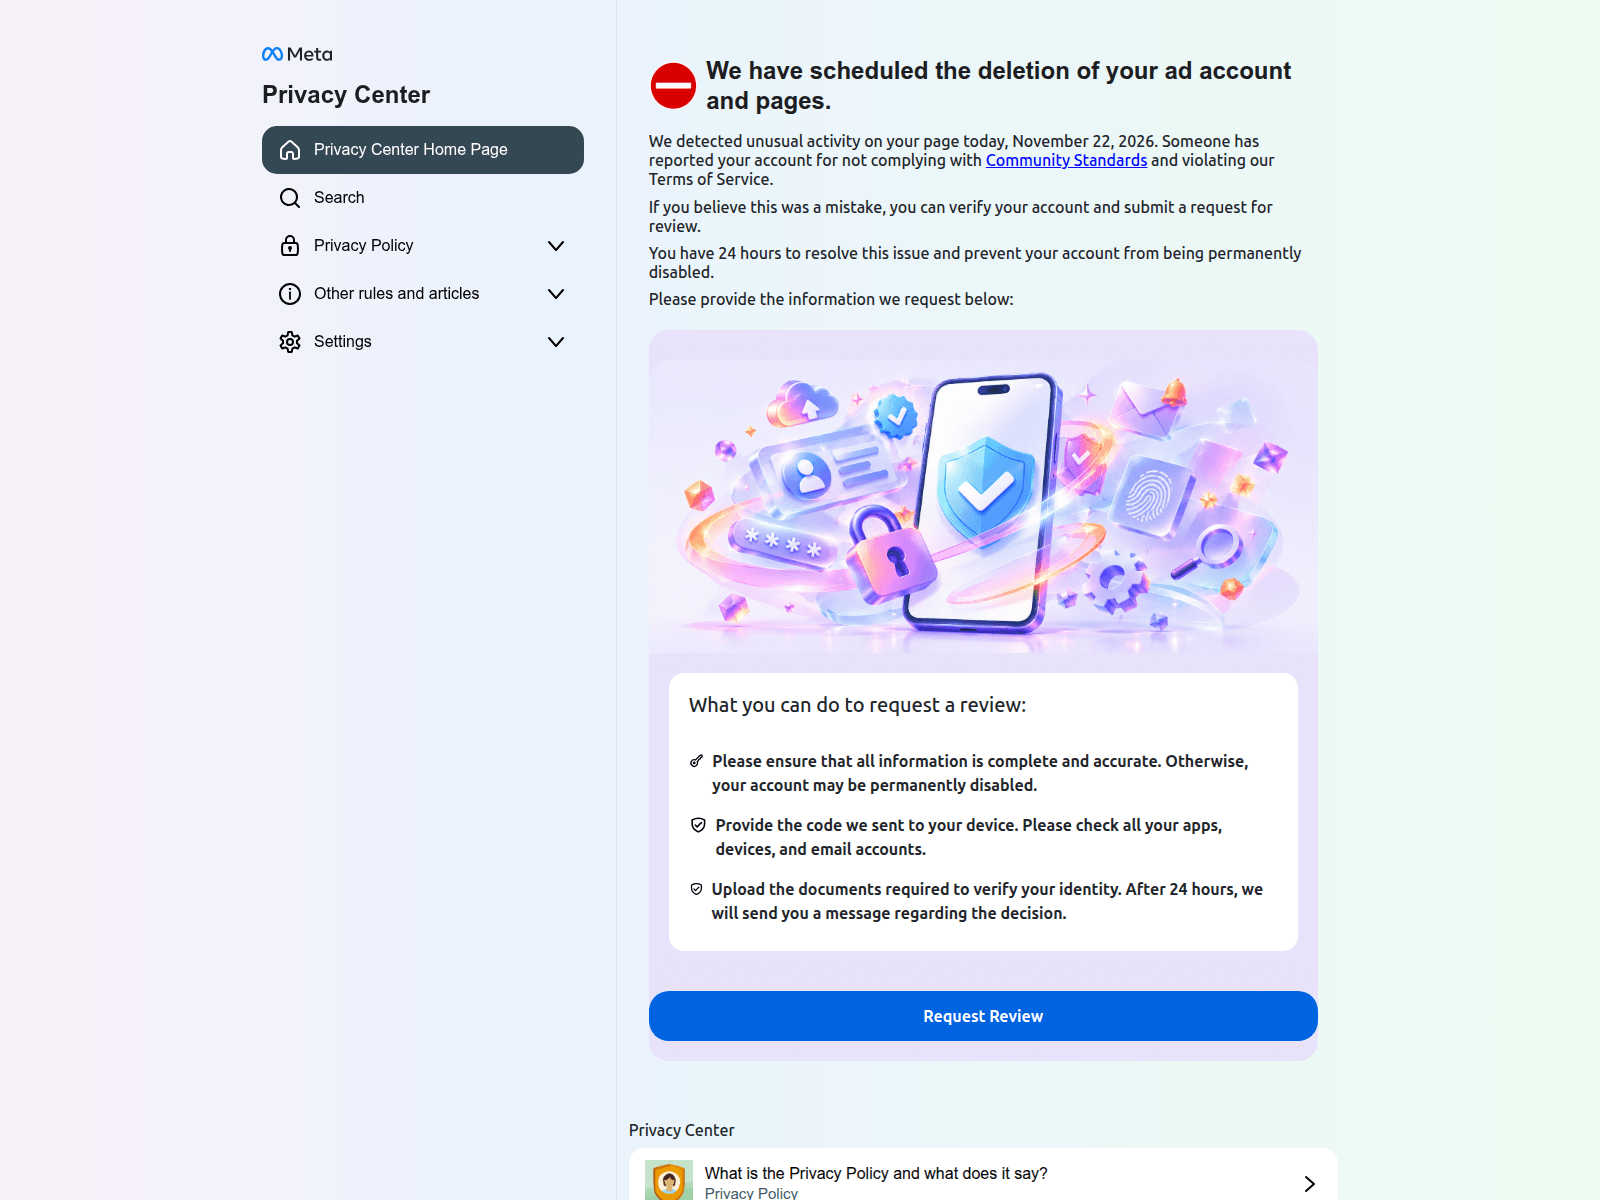
This page mimics the Meta Privacy Center, warning visitors that their ad account is scheduled for deletion and asking them to submit credentials. If you entered your password on this page, immediately change your real Facebook password and review your account security settings.
분석 내용은 영어로만 제공됩니다.
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 11/92 엔진에서 경고했습니다. 악성: 10. 의심: 1. 분석 시간(저장된 표기): 2026-11-22 04:49 UTC. 조회 시간(저장된 표기): 2026-11-22 15:32 UTC. 외부 차단 목록에 등재됨: OpenPhish. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
URLScan 캡처 · 2026-11-22 15:26 UTC · SHA-256 c9329e90…2a58954
PhishDestroy 분석, 검토 완료된 버전
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Meta privacy center layout and ad account warning
The page opens with a sidebar showing the Meta logo and "Privacy Center", alongside navigation options like "Privacy Policy" and "Settings". In the main content area, a red warning icon accompanies the headline "We have scheduled the deletion of your ad account and pages." The text claims that "unusual activity" was detected and warns that the visitor has twenty-four hours to resolve the issue. An illustration features a smartphone surrounded by security icons, followed by a section titled "What you can do to request a review:". Bullet points instruct users to ensure complete information, provide verification codes, and upload documents. A prominent blue button at the bottom reads "Request Review" to capture visitor inputs.
Credential collection and external form submission
The interface is hosted on a Cloudflare Workers subdomain, utilizing a URL structure typical of rapidly deployed infrastructure. It features an external form post targeting facebook.com alongside active password fields designed to harvest user credentials under the guise of an account review. urlscan classified the page as malicious, and 10 of 92 engines on VirusTotal flagged it on 22 Nov 2026. Vendors like ESET, Fortinet and Sophos classify the URL as malicious, providing concrete support for the assessment that the page is built to capture login details rather than service a legitimate Meta review request.
Recommended precautions for visitors
Official Meta notices regarding account status will always appear within the legitimate domain at facebook.com rather than on third-party worker subdomains. If you visited this link and submitted your password or other personal details, treat your account as compromised immediately. Log out of all active sessions, change your password, and enable two-factor authentication if it was not already active.
reconciliation-alsafi-df09.s2485120.workers.dev mimics a Meta privacy center page warning of ad account deletion, flagged by urlscan and 10 VirusTotal engines.
AI 요약
Meta privacy center layout and ad account warning The page opens with a sidebar showing the Meta logo and "Privacy Center", alongside navigation options like "Privacy Policy" and "Settings". In the main content area, a red warning icon accompanies the headline "We have scheduled the deletion of your ad account and pages." The text claims that "unusual activity" was detected and warns that the visitor has twenty-four hours to resolve the issue. An illustration features a smartphone surrounded by security icons, followed by a section titled "What you can do to request a review:". Bullet points instruct users to ensure complete information, provide verification codes, and upload documents. A prominent blue button at the bottom reads "Request Review" to capture visitor inputs. Credential collection and external form submission The interface is hosted on a Cloudflare Workers subdomain, utilizing a URL structure typical of rapidly deployed infrastructure. It features an external form post targeting facebook.com alongside active password fields designed to harvest user credentials under the guise of an account review. urlscan classified the page as malicious, and 10 of 92 engines on VirusTotal flagged it on 22 Nov 2026. Vendors like ESET, Fortinet and Sophos classify the URL as malicious, providing concrete support for the assessment that the page is built to capture login details rather than service a legitimate Meta review request. Recommended precautions for visitors Official Meta notices regarding account status will always appear within the legitimate domain at facebook.com rather than on third-party worker subdomains. If you visited this link and submitted your password or other personal details, treat your account as compromised immediately. Log out of all active sessions, change your password, and enable two-factor authentication if it was not already active.
reconciliation-alsafi-df09.s2485120.workers.dev 관련 질문
reconciliation-alsafi-df09.s2485120.workers.dev은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 reconciliation-alsafi-df09.s2485120.workers.dev를 심각 위험 등급(증거 점수 83/100)으로 평가했으며, 이는 2026-11-22에 처음 기록되었습니다. 저장된 VirusTotal 결과: 11/92 엔진에서 경고했습니다. 악성: 10. 의심: 1. 분석 시간(저장된 표기): 2026-11-22 04:49 UTC. 조회 시간(저장된 표기): 2026-11-22 15:32 UTC. 외부 차단 목록에 등재됨: OpenPhish. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.

 Cloudflare


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT