원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Overview
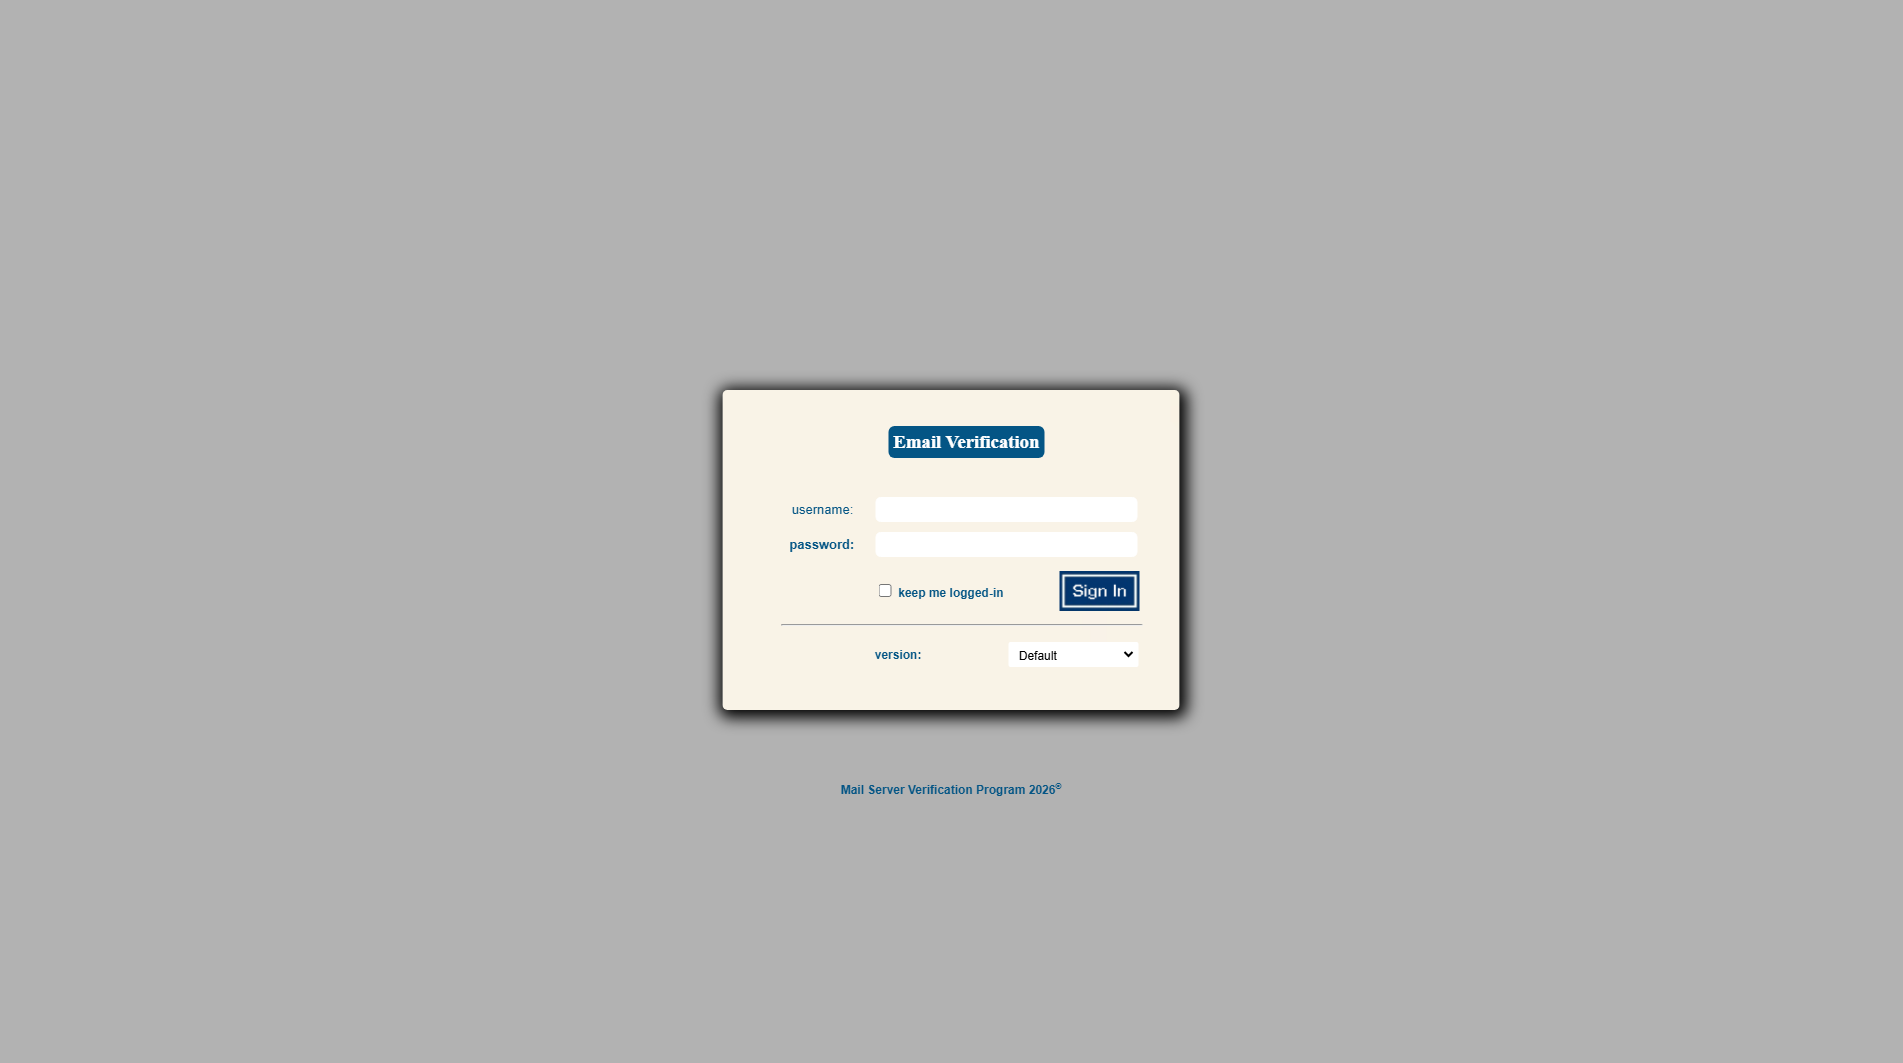
This hostname served an impersonation phishing page titled "Email Server Verification Program" from a subdomain that carries the Tommee Tippee name. It targeted people who could be persuaded that their email account needed verifying. PhishDestroy first detected it on 2026-08-24. The site has been offline since 2026-09-11, and on 2026-10-19 the root returned no content.
사기 수법
"Verification program" lures usually arrive by email, warning that the mailbox will be suspended or lose messages unless the user confirms their account. The link leads to a login form styled as a mail-server or webmail check, and whatever the victim types goes straight to the operator. A stolen mailbox is valuable because it can reset passwords for other services, including exchange and wallet accounts, and can be used to send more phishing to the victim's contacts. The hostname references Tommee Tippee while the page title presents a generic email server check. We classified the site as impersonation phishing.
증거
On 2026-09-04, 6 of 90 VirusTotal engines flagged the site: CRDF, CyRadar, Forcepoint ThreatSeeker, Fortinet, Gridinsoft and Sophos. That is a small share, but the six are independent vendors, and they agree with our classification. PhishDestroy is the only blocklist in our set that lists the hostname, so some filters may not have warned users while the page was live.
인프라
The parent domain ppddev.co.uk was registered on 2013-06-13 through eNom LLC, more than thirteen years before this page appeared. The operation used a long-standing name, not a freshly registered throwaway. The "pr-3549" label follows the pattern of a numbered preview or staging subdomain. The site was hosted in Great Britain on the Iomart Managed Services Limited network, with a Let's Encrypt certificate that made the page show a padlock in the browser.
What to do
If you entered an email address and password on this page, change that password right away. Then change it on every other account that reused it, starting with any linked to exchanges or wallets. Turn on app-based two-factor authentication, sign out all active sessions, and check the mailbox for forwarding rules or filters you did not create. Watch for password-reset emails you did not request. Defenders should block the hostname, search mail logs for messages linking to it, and reset credentials for any users who clicked through.
pr-3549.tommeetippee.ppddev.co.uk hosted an impersonation phishing page posing as an email server verification, aimed at harvesting mailbox logins.
AI 요약
Overview This hostname served an impersonation phishing page titled "Email Server Verification Program" from a subdomain that carries the Tommee Tippee name. It targeted people who could be persuaded that their email account needed verifying. PhishDestroy first detected it on 2026-08-24. The site has been offline since 2026-09-11, and on 2026-10-19 the root returned no content. How the scam works "Verification program" lures usually arrive by email, warning that the mailbox will be suspended or lose messages unless the user confirms their account. The link leads to a login form styled as a mail-server or webmail check, and whatever the victim types goes straight to the operator. A stolen mailbox is valuable because it can reset passwords for other services, including exchange and wallet accounts, and can be used to send more phishing to the victim's contacts. The hostname references Tommee Tippee while the page title presents a generic email server check. We classified the site as impersonation phishing. Evidence On 2026-09-04, 6 of 90 VirusTotal engines flagged the site: CRDF, CyRadar, Forcepoint ThreatSeeker, Fortinet, Gridinsoft and Sophos. That is a small share, but the six are independent vendors, and they agree with our classification. PhishDestroy is the only blocklist in our set that lists the hostname, so some filters may not have warned users while the page was live. Infrastructure The parent domain ppddev.co.uk was registered on 2013-06-13 through eNom LLC, more than thirteen years before this page appeared. The operation used a long-standing name, not a freshly registered throwaway. The "pr-3549" label follows the pattern of a numbered preview or staging subdomain. The site was hosted in Great Britain on the Iomart Managed Services Limited network, with a Let's Encrypt certificate that made the page show a padlock in the browser. What to do If you entered an email address and password on this page, change that password right away. Then change it on every other account that reused it, starting with any linked to exchanges or wallets. Turn on app-based two-factor authentication, sign out all active sessions, and check the mailbox for forwarding rules or filters you did not create. Watch for password-reset emails you did not request. Defenders should block the hostname, search mail logs for messages linking to it, and reset credentials for any users who clicked through. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a03308-2012-72ed-abf6-2458101fde8e/ VirusTotal report: https://www.virustotal.com/gui/domain/pr-3549.tommeetippee.ppddev.co.uk Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=pr-3549.tommeetippee.ppddev.co.uk Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
pr-3549.tommeetippee.ppddev.co.uk은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 pr-3549.tommeetippee.ppddev.co.uk를 심각 위험 등급(증거 점수 72/100)으로 평가했으며, 이는 2026-08-24에 처음 기록되었습니다. 저장된 VirusTotal 결과: 5/92 엔진에서 경고했습니다. 악성: 3. 의심: 2. 분석 시간(저장된 표기): 2026-10-11 13:26 UTC. 조회 시간(저장된 표기): 2026-10-23 16:46 UTC. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
IP 평판185.11.184.2190/100악용 점수 · 이 서버의 IP 주소에 대한 악용 신고 건수이며, 도메인에 대한 신고 건수가 아닙니다. 점수가 높을수록 상황이 더 심각합니다.이 IP 주소는 아직 악용 데이터베이스에 신고되지 않았으나, 도메인 자체는 피싱으로 인식되고 있습니다.신고 0건확인됨 2026-08-24
기록된 이벤트: 14. 이 기록들은 수집된 증거, 발송된 알림 및 차단 목록 등재를 설명하며, 조사가 완료되었거나 해당 사이트가 차단되었음을 확인하는 것은 아닙니다.
선제적 탐지 및 데이터 수집위협 데이터 수집 완료기록됨
위협 데이터 수집 완료
pr-3549.tommeetippee.ppddev.co.uk이 탐지되어 전체 분석을 위해 대기열에 추가됨
위협 인텔리전스 확인URLScan.io 캡처 · Cloudflare Radar 보고서 · VirusTotal · 수집된 포렌식 증거 · 기록된 기술 분석 · 사이트가 다시 온라인 상태가 되었습니다 · 콘텐츠가 더 이상 이용 불가능한 것으로 확인됨 · VirusTotal 탐지 건수 +1 · VirusTotal 탐지 건수 +3 · VirusTotal 탐지 건수 +1기록됨
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.

 185.11.184.219





 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT