PhishDestroy는 2026-10-23에 okx-usd.com를 처음 기록했습니다. 저장된 VirusTotal 결과: 12/92 엔진에서 경고했습니다. 악성: 11. 의심: 1. 분석 시간(저장된 표기): 2026-10-19 17:55 UTC. 조회 시간(저장된 표기): 2026-10-23 01:41 UTC. 외부 차단 목록에 등재됨: MetaMask, SEAL.
페이지 제목: “Okx”
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 12/92 엔진에서 경고했습니다. 악성: 11. 의심: 1. 분석 시간(저장된 표기): 2026-10-19 17:55 UTC. 조회 시간(저장된 표기): 2026-10-23 01:41 UTC. 외부 차단 목록에 등재됨: MetaMask, SEAL. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
전문가용 보기에는 DNS, TLS, 네트워크 요청, 해시, 원시 JSON 등 모든 섹션이 포함되어 있습니다.
ABUSE NOTICE · 7D+ OPEN 발송된 악용 신고는 기록되며, 저장된 최신 가용성 증거에 따르면 해당 도메인은 여전히 접속 가능한 상태입니다.
통지 및 현재 상황 관련 증거
전송된 보고서 원장에는 첫 번째 발신 보고서가 . 기록된 수신자: abuse@dynadot.com. 가장 최근에 저장된 가용성 정보에 따르면 해당 도메인은 여전히 접속 가능한 것으로 나타납니다.; 1 month 첫 번째 발신 보고서 이후로 시간이 지났습니다.
ICANN RAA §3.18 등록기관의 악용 신고 연락처 및 처리 의무를 설명합니다. 이 섹션에는 발신 타임스탬프, 수신자 목록, 사건 식별자 및 추후 확인 가능 여부가 기록됩니다. 이 정보만으로는 수신, 확인, 조사, 시정 조치 또는 계약 불이행을 입증할 수 없습니다.
첫 보고 이후 경과한 기간
1 month
발송된 신고
1
최신 사례 ID
PD-20261023-28FEA1
현재 현황
가장 최근에 저장된 검사 시점에서 활성 상태로 관측됨
보고서 요약
PhishDestroy에 okx-usd.com 기록이 저장되어 있습니다. 각 출처의 관측 날짜는 다르며, 검사가 없다는 사실은 안전을 의미하지 않습니다.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
분석
도메인 요약
PhishDestroy는 2026-10-23에 okx-usd.com를 처음 기록했습니다. 저장된 VirusTotal 결과: 12/92 엔진에서 경고했습니다. 악성: 11. 의심: 1. 분석 시간(저장된 표기): 2026-10-19 17:55 UTC. 조회 시간(저장된 표기): 2026-10-23 01:41 UTC. 외부 차단 목록에 등재됨: MetaMask, SEAL. 위험도: 심각 (증거 점수 100/100). 등록 대행자: Dynadot. 호스팅: Virtual Systems LLC. PhishDestroy는 악용 신고 1건을 보냈습니다. 로그인 정보를 입력하거나 지갑을 연결하지 마세요.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Overview
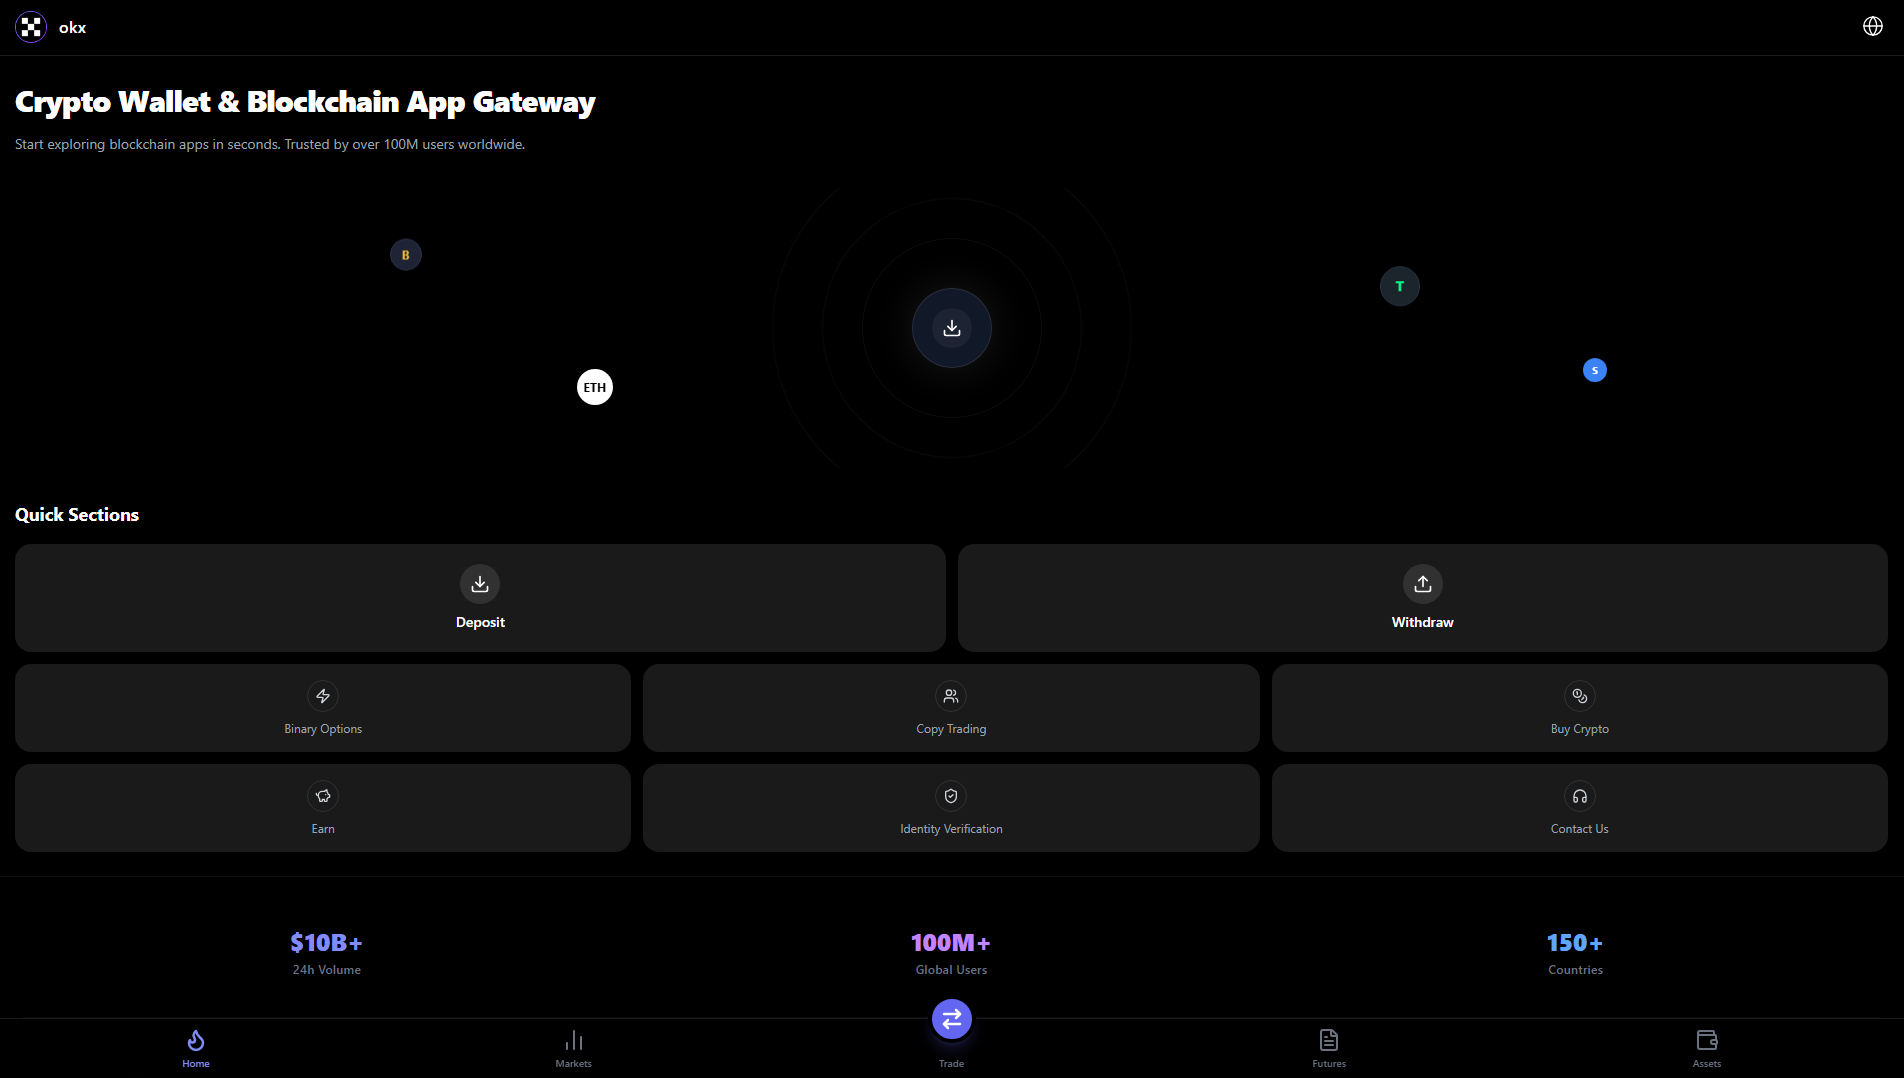
The captured screenshot from 2026-10-23 shows an OKX-branded landing page headed Crypto Wallet & Blockchain App Gateway, which promised blockchain apps in seconds and claimed trust from over 100M users. Quick sections offered Deposit, Withdraw, Binary Options, Copy Trading, Buy Crypto, Earn, Identity Verification and Contact Us above statistics of 10B+ volume, 100M+ users and 150+ countries. PhishDestroy listed the domain as Impersonation, first seen on 2026-10-23.
사기 수법
The Deposit, Withdraw, Buy Crypto and Identity Verification entry points present a familiar exchange interface that can lead visitors to submit login credentials, identity details or funds to an operator-controlled page. As a category risk, brand impersonation of this kind enables credential theft and fraudulent transfers while borrowing a legitimate platform's visual design.
증거
The screenshot shows OKX logo styling, a central download-style button and trust claims of 100M users and 150+ countries. urlscan scored the capture malicious with an ML score of 98 and an overall phishing score of 100 on 2026-10-23, labelling the brand OKX. VirusTotal flagged it as malicious. Google Safe Browsing, Spamhaus and OTX showed no listing and no pulses on checks dated 2026-10-23 and 2026-10-26, while MetaMask and SEAL blocklists and PhishDestroy's internal list flagged it and an HTTP request followed a 307 redirect to HTTPS; site inspection recorded an i18next library, 5 tracker requests and 1 distinct script SHA256 hash beginning 615ff996a983 for pivoting.
인프라
Notable weaknesses: missing CSP, unsigned DNSSEC and no SPF, DKIM or DMARC. TLS 1.3, AES-256-GCM, forward secrecy, ALPN h2; HSTS present with max-age 31536000 but without all subdomains; X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP and CORP absent; CAA records present. Registered through Dynadot Inc on 2026-05-11, with hosting recorded to Virtual Systems LLC.
What to do
If you submitted credentials through okx-usd.com, change your password on the genuine exchange and enable 2FA, then watch your account for unfamiliar activity. If you sent funds, contact your exchange or payment provider's support without delay. Defenders should block okx-usd.com at DNS, proxy and endpoint layers and pivot on the recorded script hash across telemetry.
서술 생성 날짜는 관측 날짜와 별개입니다. 이는 보존된 게시 필드일 뿐, 별도의 독립적인 탐지 결과가 아닙니다.
AI 제목
okx-usd.com — OKX impersonation phishing page
AI 설명
PhishDestroy assessed okx-usd.com as an impersonation phishing page presenting an OKX-branded wallet gateway and flags it for blocking.
AI 요약
Overview The captured screenshot from 2026-10-23 shows an OKX-branded landing page headed Crypto Wallet & Blockchain App Gateway, which promised blockchain apps in seconds and claimed trust from over 100M users. Quick sections offered Deposit, Withdraw, Binary Options, Copy Trading, Buy Crypto, Earn, Identity Verification and Contact Us above statistics of 10B+ volume, 100M+ users and 150+ countries. PhishDestroy listed the domain as Impersonation, first seen on 2026-10-23. How the scam works The Deposit, Withdraw, Buy Crypto and Identity Verification entry points present a familiar exchange interface that can lead visitors to submit login credentials, identity details or funds to an operator-controlled page. As a category risk, brand impersonation of this kind enables credential theft and fraudulent transfers while borrowing a legitimate platform's visual design. Evidence The screenshot shows OKX logo styling, a central download-style button and trust claims of 100M users and 150+ countries. urlscan scored the capture malicious with an ML score of 98 and an overall phishing score of 100 on 2026-10-23, labelling the brand OKX. VirusTotal flagged it as malicious. Google Safe Browsing, Spamhaus and OTX showed no listing and no pulses on checks dated 2026-10-23 and 2026-10-26, while MetaMask and SEAL blocklists and PhishDestroy's internal list flagged it and an HTTP request followed a 307 redirect to HTTPS; site inspection recorded an i18next library, 5 tracker requests and 1 distinct script SHA256 hash beginning 615ff996a983 for pivoting. Infrastructure Notable weaknesses: missing CSP, unsigned DNSSEC and no SPF, DKIM or DMARC. TLS 1.3, AES-256-GCM, forward secrecy, ALPN h2; HSTS present with max-age 31536000 but without all subdomains; X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP and CORP absent; CAA records present. Registered through Dynadot Inc on 2026-05-11, with hosting recorded to Virtual Systems LLC. What to do If you submitted credentials through okx-usd.com, change your password on the genuine exchange and enable 2FA, then watch your account for unfamiliar activity. If you sent funds, contact your exchange or payment provider's support without delay. Defenders should block okx-usd.com at DNS, proxy and endpoint layers and pivot on the recorded script hash across telemetry. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a1668a-4008-72c9-a8be-4b3cc1c5af10/ Cloudflare Radar report: https://radar.cloudflare.com/scan/a11fc8e8-c1c2-47ef-8931-c248474755ba URLQuery report: https://urlquery.net/report/472dc315-f94d-4336-b93b-1ad42d9fac67 Stored capture screenshot: https://i.ibb.co/rfyCkG8p/bf2b30347ddf.png Cloudflare Radar screenshot (2026-10-23T01:42:59Z): https://screenshots.phishdestroy.io/cf/a11fc8e8-c1c2-47ef-8931-c248474755ba.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/472dc315-f94d-4336-b93b-1ad42d9fac67.png URLScan screenshot (2026-10-17T18:28:26Z): https://screenshots.phishdestroy.io/us/01a14b1f-3b69-7172-8972-6002088481fb.png URLScan capture report: https://urlscan.io/result/01a14b1f-3b69-7172-8972-6002088481fb/ URLScan screenshot (2026-10-19T15:58:20Z): https://screenshots.phishdestroy.io/us/01a154e2-87b8-7732-ac05-ac7a02dd2d41.png URLScan capture report: https://urlscan.io/result/01a154e2-87b8-7732-ac05-ac7a02dd2d41/ URLScan screenshot (2026-10-19T21:27:50Z): https://screenshots.phishdestroy.io/us/01a15610-2b12-770f-a581-d46d0791dac4.png URLScan capture report: https://urlscan.io/result/01a15610-2b12-770f-a581-d46d0791dac4/ URLScan screenshot (2026-10-20T01:21:31Z): https://screenshots.phishdestroy.io/us/01a156e6-22dd-73e9-b074-9cf0b256d208.png URLScan capture report: https://urlscan.io/result/01a156e6-22dd-73e9-b074-9cf0b256d208/ URLScan screenshot (2026-10-20T05:17:16Z): https://screenshots.phishdestroy.io/us/01a157bd-dc39-756c-b9ef-33cac2da5451.png URLScan capture report: https://urlscan.io/result/01a157bd-dc39-756c-b9ef-33cac2da5451/ URLScan screenshot (2026-10-23T02:26:59Z): https://screenshots.phishdestroy.io/us/01a16695-2612-7468-a365-603c136da8bd.png URLScan capture report: https://urlscan.io/result/01a16695-2612-7468-a365-603c136da8bd/ VirusTotal report: https://www.virustotal.com/gui/domain/okx-usd.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=okx-usd.com Archived copy: https://web.archive.org/web/20261023014740/https://okx-usd.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Headers: Server: nginx; Content type: text/html; Strict transport security: max-age=31536000
보안 신호
Scamadviser 경고36/100
The owner of the website is using a service to hide their identity on WHOIS According to Tranco this site has a low rank High number of suspicious websites on this server The registrar has a high % of spammers and fraud sites This website is (very) young.
The SSL certificate is valid
네트워크 보안 인텔리전스
Cloudflare Radar 판정 결과악성
피싱 피싱 Security threats
okx-usd.com 관련 질문
okx-usd.com은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 okx-usd.com를 심각 위험 등급(증거 점수 100/100)으로 평가했으며, 이는 2026-10-23에 처음 기록되었습니다. 저장된 VirusTotal 결과: 12/92 엔진에서 경고했습니다. 악성: 11. 의심: 1. 분석 시간(저장된 표기): 2026-10-19 17:55 UTC. 조회 시간(저장된 표기): 2026-10-23 01:41 UTC. 외부 차단 목록에 등재됨: MetaMask, SEAL. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
okx-usd.com에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
okx-usd.com을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
IP 평판85.137.57.1930/100악용 점수 · 이 서버의 IP 주소에 대한 악용 신고 건수이며, 도메인에 대한 신고 건수가 아닙니다. 점수가 높을수록 상황이 더 심각합니다.이 IP 주소는 아직 악용 데이터베이스에 신고되지 않았으나, 도메인 자체는 피싱으로 인식되고 있습니다.신고 0건확인됨 2026-11-22
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.


 Dynadot
 85.137.57.193


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT