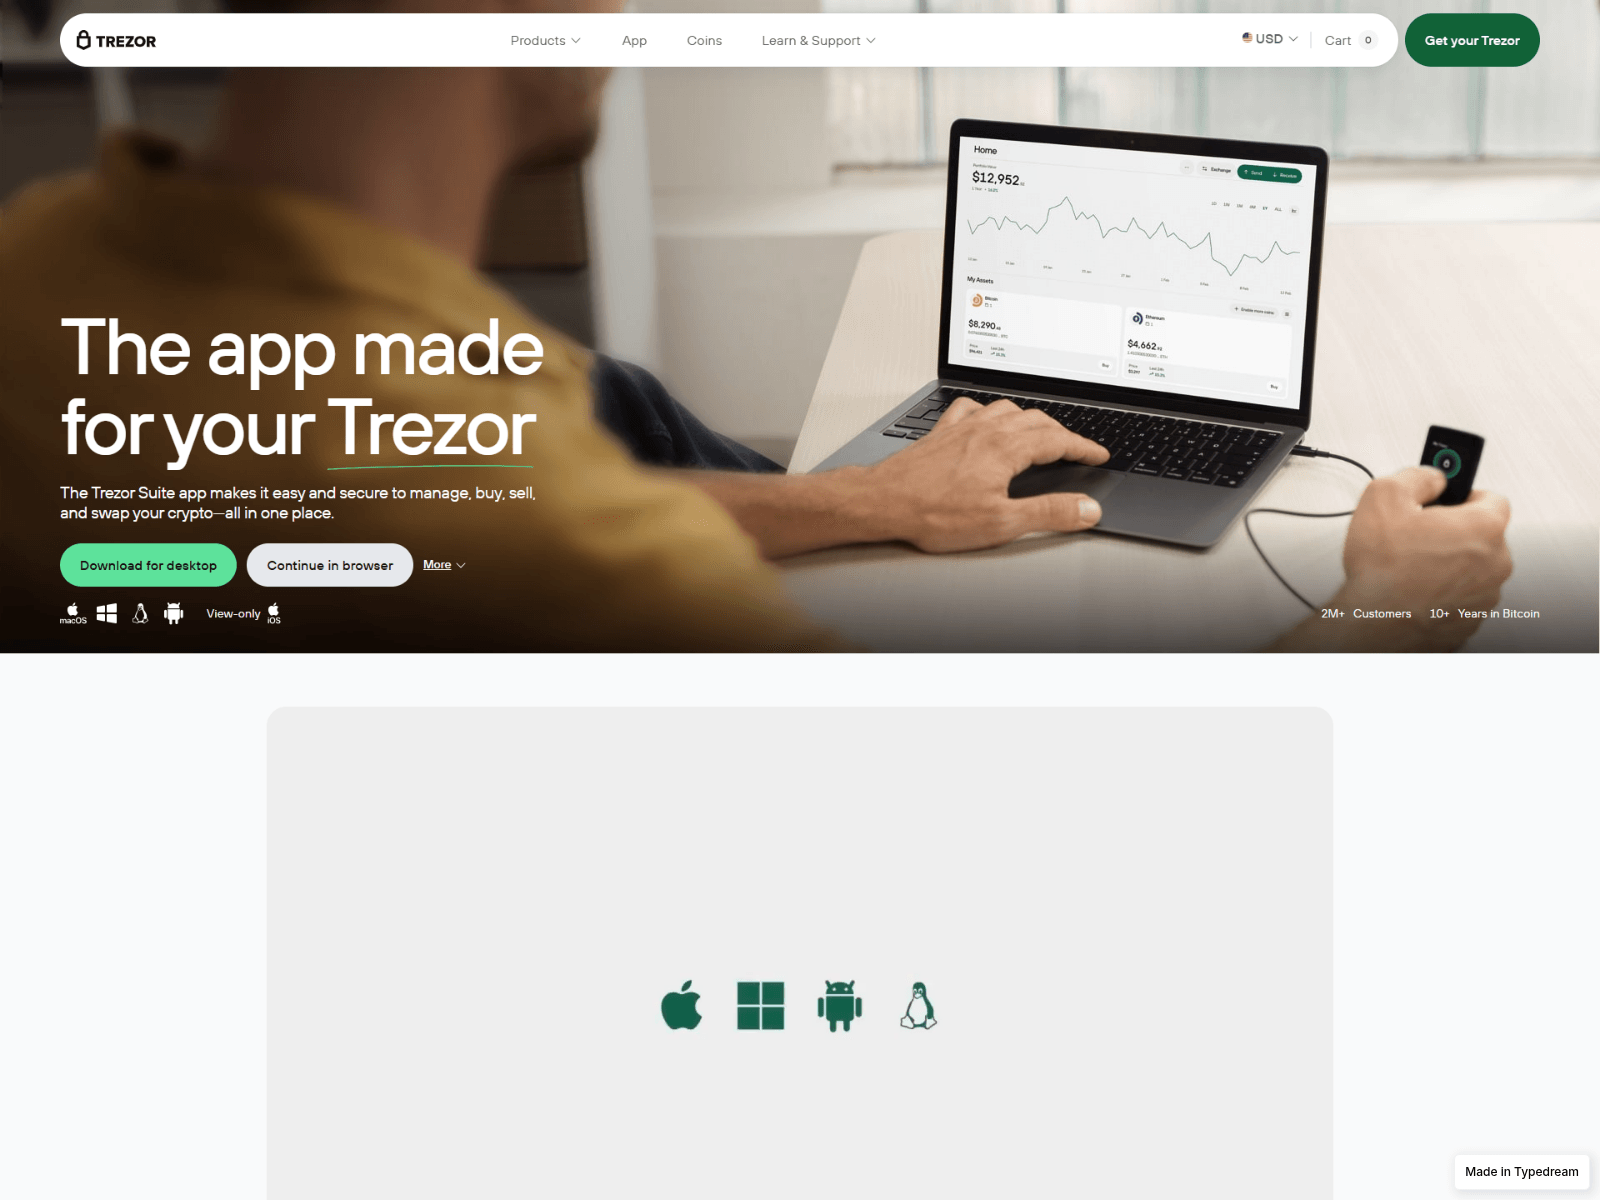
PhishDestroy는 2026-10-28에 help-base-start-sso.typedream.app를 처음 기록했습니다. 저장된 VirusTotal 결과: 21/92 엔진에서 경고했습니다. 분석 시간(저장된 표기): 2026-10-25 11:17 UTC. 조회 시간(저장된 표기): 2026-10-28 20:43 UTC. 외부 차단 목록에 등재됨: MetaMask, SEAL.
페이지 제목: “Trezór.io/Start® | ®Starting Up Your Device®| Trezor®”
출처에 대한 자세한 정보
저장된 보안 신호
저장된 VirusTotal 결과: 21/92 엔진에서 경고했습니다. 분석 시간(저장된 표기): 2026-10-25 11:17 UTC. 조회 시간(저장된 표기): 2026-10-28 20:43 UTC. 외부 차단 목록에 등재됨: MetaMask, SEAL. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
전문가용 보기에는 DNS, TLS, 네트워크 요청, 해시, 원시 JSON 등 모든 섹션이 포함되어 있습니다.
보고서 요약
PhishDestroy에 help-base-start-sso.typedream.app 기록이 저장되어 있습니다. 각 출처의 관측 날짜는 다르며, 검사가 없다는 사실은 안전을 의미하지 않습니다.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
분석
도메인 요약
PhishDestroy는 2026-10-28에 help-base-start-sso.typedream.app를 처음 기록했습니다. 저장된 VirusTotal 결과: 21/92 엔진에서 경고했습니다. 분석 시간(저장된 표기): 2026-10-25 11:17 UTC. 조회 시간(저장된 표기): 2026-10-28 20:43 UTC. 외부 차단 목록에 등재됨: MetaMask, SEAL. 위험도: 심각 (증거 점수 100/100). 상태: 마지막으로 확인된 활성 상태. 호스팅: Cloudflare, Inc. 로그인 정보를 입력하거나 지갑을 연결하지 마세요.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Overview
The 2026-10-28 capture showed a landing page styled like the Trezor hardware-wallet site: a hero reading "The app made for your Trezor", navigation for Products, App, Coins and Learn & Support, and buttons offering the Trezor Suite app. The record does not state an original listing reason, so the substantive concern rests on the current scanner verdicts and on Trezor-branded software download prompts served from an unrelated Typedream subdomain.
사기 수법
If the page is deceptive, a visitor following "Download for desktop" or "Continue in browser" could receive software from a source other than the vendor's own domain. The static capture shows those controls but cannot establish what they deliver, where they redirect, or whether any file is harmful, so no theft mechanism is confirmed and no login form is visible.
증거
URLScan's 2026-10-28 capture gave an overall malicious verdict (score 100, category phishing, brand trezor) while its engines scored 92, and Cloudflare Radar separately categorised the URL as phishing. VirusTotal's domain analysis dated 2026-10-25 and retrieved 2026-10-28 recorded 21 of 92 engines malicious: ESET, Kaspersky, Sophos, BitDefender, Fortinet, G-Data and others labelled it "phishing", while CRDF, Webroot, Netcraft, Seclookup, ChainPatrol and alphaMountain.ai said "malicious"; MetaMask and SEAL also listed it. Material negatives remain: Google Safe Browsing was not flagged, OTX recorded zero pulses (mentions, not detections), 41 engines were harmless, and an earlier URLScan capture on 2026-09-28 was verdict "clean" — a disagreement that stays visible.
인프라
The page was recorded on 2026-10-28 at IP 188.114.97.3 behind a Cloudflare WAF, served from a Typedream subdomain whose social tag pointed at a help-base-start-sso.typedream.page address, with an HTTP 307 upgrade to HTTPS.
What to do
Visiting alone does not imply compromise. If you installed software obtained through "Download for desktop", scan it and replace it with a copy from the vendor's official site; if you entered a password anywhere, change it, since the capture shows no form but cannot rule out later content. Block only help-base-start-sso.typedream.app itself, since the recorded IP and the Typedream platform host unrelated sites.
PhishDestroy recorded help-base-start-sso.typedream.app as a Trezor-branded download page that multiple security vendors flagged.
AI 요약
Overview The 2026-10-28 capture showed a landing page styled like the Trezor hardware-wallet site: a hero reading "The app made for your Trezor", navigation for Products, App, Coins and Learn & Support, and buttons offering the Trezor Suite app. The record does not state an original listing reason, so the substantive concern rests on the current scanner verdicts and on Trezor-branded software download prompts served from an unrelated Typedream subdomain. How the scam works If the page is deceptive, a visitor following "Download for desktop" or "Continue in browser" could receive software from a source other than the vendor's own domain. The static capture shows those controls but cannot establish what they deliver, where they redirect, or whether any file is harmful, so no theft mechanism is confirmed and no login form is visible. Evidence URLScan's 2026-10-28 capture gave an overall malicious verdict (score 100, category phishing, brand trezor) while its engines scored 92, and Cloudflare Radar separately categorised the URL as phishing. VirusTotal's domain analysis dated 2026-10-25 and retrieved 2026-10-28 recorded 21 of 92 engines malicious: ESET, Kaspersky, Sophos, BitDefender, Fortinet, G-Data and others labelled it "phishing", while CRDF, Webroot, Netcraft, Seclookup, ChainPatrol and alphaMountain.ai said "malicious"; MetaMask and SEAL also listed it. Material negatives remain: Google Safe Browsing was not flagged, OTX recorded zero pulses (mentions, not detections), 41 engines were harmless, and an earlier URLScan capture on 2026-09-28 was verdict "clean" — a disagreement that stays visible. Infrastructure The page was recorded on 2026-10-28 at IP 188.114.97.3 behind a Cloudflare WAF, served from a Typedream subdomain whose social tag pointed at a help-base-start-sso.typedream.page address, with an HTTP 307 upgrade to HTTPS. What to do Visiting alone does not imply compromise. If you installed software obtained through "Download for desktop", scan it and replace it with a copy from the vendor's official site; if you entered a password anywhere, change it, since the capture shows no form but cannot rule out later content. Block only help-base-start-sso.typedream.app itself, since the recorded IP and the Typedream platform host unrelated sites. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a18426-f6d9-75c2-aaa7-493998696c72/ Cloudflare Radar report: https://radar.cloudflare.com/scan/9506abe1-7061-4e5b-9839-b182774e8675 Stored capture screenshot: https://urlscan.io/screenshots/01a18426-f6d9-75c2-aaa7-493998696c72.png Cloudflare Radar screenshot (2026-10-28T20:12:38Z): https://screenshots.phishdestroy.io/cf/9506abe1-7061-4e5b-9839-b182774e8675.png URLScan screenshot (2026-08-01T01:03:17Z): https://screenshots.phishdestroy.io/us/019fbad8-a84c-72a7-ae16-9d1302fe2c2f.png URLScan capture report: https://urlscan.io/result/019fbad8-a84c-72a7-ae16-9d1302fe2c2f/ URLScan screenshot (2026-08-17T08:33:13Z): https://screenshots.phishdestroy.io/us/01a00eda-5ad4-70cd-aa0e-5084ece78bd6.png URLScan capture report: https://urlscan.io/result/01a00eda-5ad4-70cd-aa0e-5084ece78bd6/ URLScan screenshot (2026-08-24T12:15:07Z): https://screenshots.phishdestroy.io/us/01a033b2-03a3-75e2-aae9-a6f8b324504a.png URLScan capture report: https://urlscan.io/result/01a033b2-03a3-75e2-aae9-a6f8b324504a/ URLScan screenshot (2026-09-01T01:04:50Z): https://screenshots.phishdestroy.io/us/01a05a7f-3cc0-720d-b7f2-140ec67e1d84.png URLScan capture report: https://urlscan.io/result/01a05a7f-3cc0-720d-b7f2-140ec67e1d84/ URLScan screenshot (2026-09-10T12:15:54Z): https://screenshots.phishdestroy.io/us/01a08b3e-d496-73fa-8ddc-51bd415daffa.png URLScan capture report: https://urlscan.io/result/01a08b3e-d496-73fa-8ddc-51bd415daffa/ URLScan screenshot (2026-10-28T20:15:16Z): https://screenshots.phishdestroy.io/us/01a18426-f6d9-75c2-aaa7-493998696c72.png VirusTotal report: https://www.virustotal.com/gui/domain/help-base-start-sso.typedream.app Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=help-base-start-sso.typedream.app Archived copy: https://web.archive.org/web/20261028200649/https://help-base-start-sso.typedream.app/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Ogurl: https://help-base-start-sso.typedream.page/; Title: Trezór.io/Start® | ®Starting Up Your Device®| Trezor®; Ogtype: website; Ogtitle: Trezór.io/Start® | ®Starting Up Your Device®| Trezor®; Ogsitename: Trezór.io/Start® | ®Starting Up Your Device®| Trezor®; Description: A website made with Typedream.; Twittercard: summary; Twittersite: @typedreamHQ; Ogdescription: A website made with Typedream.
Headers: Server: cloudflare; Content type: text/html; charset=utf-8; X powered by: Next.js; Via: 1.1 google
보안 신호
Scamadviser 경고1/100
This website does not have many visitors This website is being iframed by another website IPQS flagged this website for Phishing IPQS has flagged this website as suspicious
According to the SSL check the certificate is valid DNSFilter considers this website safe
네트워크 보안 인텔리전스
Cloudflare Radar 판정 결과악성
Security threats 피싱 피싱
help-base-start-sso.typedream.app 관련 질문
help-base-start-sso.typedream.app은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 help-base-start-sso.typedream.app를 심각 위험 등급(증거 점수 100/100)으로 평가했으며, 이는 2026-10-28에 처음 기록되었습니다. 저장된 VirusTotal 결과: 21/92 엔진에서 경고했습니다. 분석 시간(저장된 표기): 2026-10-25 11:17 UTC. 조회 시간(저장된 표기): 2026-10-28 20:43 UTC. 외부 차단 목록에 등재됨: MetaMask, SEAL. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
1차 평가 변수활성 콘텐츠reason: Ordinary HTTP content served90% confidence
출처source: Current Http Probe
증거 레이어Availability: Content servingContent: Content served at rootDNS: Resolved
최신 HTTP 관측 결과활성 콘텐츠일반 HTTP 콘텐츠 제공90%2026-11-22 11:31 UTC
RDAP 등록
관측된 시간축last reachable: 2026-11-22 11:31 UTClast content: 2026-11-22 11:31 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.

 188.114.96.3


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT