전문가용 보기에는 DNS, TLS, 네트워크 요청, 해시, 원시 JSON 등 모든 섹션이 포함되어 있습니다.
ABUSE NOTICE · 7D+ OPEN 발송된 악용 신고는 기록되며, 저장된 최신 가용성 증거에 따르면 해당 도메인은 여전히 접속 가능한 상태입니다.
통지 및 현재 상황 관련 증거
전송된 보고서 원장에는 첫 번째 발신 보고서가 . 기록된 수신자: abuse@dynadot.com. 가장 최근에 저장된 가용성 정보에 따르면 해당 도메인은 여전히 접속 가능한 것으로 나타납니다.; 26 days 첫 번째 발신 보고서 이후로 시간이 지났습니다.
ICANN RAA §3.18 등록기관의 악용 신고 연락처 및 처리 의무를 설명합니다. 이 섹션에는 발신 타임스탬프, 수신자 목록, 사건 식별자 및 추후 확인 가능 여부가 기록됩니다. 이 정보만으로는 수신, 확인, 조사, 시정 조치 또는 계약 불이행을 입증할 수 없습니다.
첫 보고 이후 경과한 기간
26 days
발송된 신고
1
최신 사례 ID
PD-20261026-A18392
현재 현황
HTTP 301 가장 최근에 저장된 검사 결과
보고서 요약
PhishDestroy에 firmvestode.org 기록이 저장되어 있습니다. 각 출처의 관측 날짜는 다르며, 검사가 없다는 사실은 안전을 의미하지 않습니다.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
분석
도메인 요약
PhishDestroy는 2026-10-26에 firmvestode.org를 처음 기록했습니다. 저장된 VirusTotal 결과: 17/92 엔진에서 경고했습니다. 악성: 14. 의심: 3. 분석 시간(저장된 표기): 2026-10-19 17:14 UTC. 조회 시간(저장된 표기): 2026-10-26 23:52 UTC. 위험도: 심각 (증거 점수 100/100). 등록 대행자: Dynadot. 상태: 마지막으로 확인된 활성 상태. 호스팅: Cloudflare, Inc. PhishDestroy는 악용 신고 1건을 보냈습니다. 로그인 정보를 입력하거나 지갑을 연결하지 마세요.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Overview
PhishDestroy’s automated assessment categorises firmvestode.org as an impersonation phishing page. The site’s recorded title advertises an AI platform for real‑time market analysis, which does not match any known legitimate brand. The domain was first seen by PhishDestroy on 2026-10-26 and returned an HTTP 200 response on that date. The classification reflects the risk of credential harvesting rather than observed theft.
사기 수법
Impersonation phishing sites copy the look and language of trusted services to trick visitors into entering login credentials, personal data, or financial information. Victims are typically directed to submit details on forms that forward the data to the attacker, who can then misuse the credentials to access accounts or conduct fraud. The threat does not require the site to host malware; the primary danger is the collection of sensitive information through deceptive presentation.
증거
VirusTotal scanned the domain on 2026-10-19 and reported 17 detections from 92 engines, including 14 malicious and 3 suspicious labels from vendors such as BitDefender, ESET, and Fortinet. Google Safe Browsing checked on 2026-10-27 and did not flag the site. PhishDestroy’s internal blocklist marks the domain as listed, while external blocklists show zero hits as of the same date. OTX recorded five pulses mentioning the domain on 2026-10-27. Cloudflare Radar scanned the site on 2026-10-26 and returned a malicious verdict with a malware category. urlscan.io captured the page on 2026-10-26; its engine analysis gave a malicious score of 97, though the overall verdict was non‑malicious.
인프라
The domain was registered on 2026-08-21 through Dynadot Inc and was 65 days old at the time of capture. DNS records point to Cloudflare nameservers (autumn.ns.cloudflare.com, harley.ns.cloudflare.com) and resolve to IP addresses 172.67.186.47 and 104.21.19.129, both belonging to Cloudflare’s network (ASN 13335). The TLS certificate, issued by Google Trust Services on 2026-10-19, is valid until 2027-01-17 and covers firmvestode.org and its wildcard. No DNSSEC signatures were present.
What to do
Users who have visited the site should avoid entering any credentials or personal data and, if they have already done so, change affected passwords and review account activity. Organizations should block the domain at the network perimeter and monitor logs for any connections to the recorded IP addresses. Report any suspicious activity to PhishDestroy for further investigation.
서술 생성 날짜는 관측 날짜와 별개입니다. 이는 보존된 게시 필드일 뿐, 별도의 독립적인 탐지 결과가 아닙니다.
AI 제목
firmvestode.org — Impersonation Phishing Page
AI 설명
PhishDestroy flags firmvestode.org as an impersonation phishing page; the site presents an AI market‑analysis platform but is classified as malicious.
AI 요약
Overview PhishDestroy’s automated assessment categorises firmvestode.org as an impersonation phishing page. The site’s recorded title advertises an AI platform for real‑time market analysis, which does not match any known legitimate brand. The domain was first seen by PhishDestroy on 2026-10-26 and returned an HTTP 200 response on that date. The classification reflects the risk of credential harvesting rather than observed theft. How the scam works Impersonation phishing sites copy the look and language of trusted services to trick visitors into entering login credentials, personal data, or financial information. Victims are typically directed to submit details on forms that forward the data to the attacker, who can then misuse the credentials to access accounts or conduct fraud. The threat does not require the site to host malware; the primary danger is the collection of sensitive information through deceptive presentation. Evidence VirusTotal scanned the domain on 2026-10-19 and reported 17 detections from 92 engines, including 14 malicious and 3 suspicious labels from vendors such as BitDefender, ESET, and Fortinet. Google Safe Browsing checked on 2026-10-27 and did not flag the site. PhishDestroy’s internal blocklist marks the domain as listed, while external blocklists show zero hits as of the same date. OTX recorded five pulses mentioning the domain on 2026-10-27. Cloudflare Radar scanned the site on 2026-10-26 and returned a malicious verdict with a malware category. urlscan.io captured the page on 2026-10-26; its engine analysis gave a malicious score of 97, though the overall verdict was non‑malicious. Infrastructure The domain was registered on 2026-08-21 through Dynadot Inc and was 65 days old at the time of capture. DNS records point to Cloudflare nameservers (autumn.ns.cloudflare.com, harley.ns.cloudflare.com) and resolve to IP addresses 172.67.186.47 and 104.21.19.129, both belonging to Cloudflare’s network (ASN 13335). The TLS certificate, issued by Google Trust Services on 2026-10-19, is valid until 2027-01-17 and covers firmvestode.org and its wildcard. No DNSSEC signatures were present. What to do Users who have visited the site should avoid entering any credentials or personal data and, if they have already done so, change affected passwords and review account activity. Organizations should block the domain at the network perimeter and monitor logs for any connections to the recorded IP addresses. Report any suspicious activity to PhishDestroy for further investigation. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a17a47-a8c1-74bb-9f15-1e7f34f02d73/ Cloudflare Radar report: https://radar.cloudflare.com/scan/a6a7d1ab-41ab-40d7-8bee-050cc099dfcb URLQuery report: https://urlquery.net/report/4acbe857-2acb-40b3-b1f4-a4092f5d66a4 Stored capture screenshot: https://i.ibb.co/QF376vr5/2c9b20960887.png Cloudflare Radar screenshot (2026-10-26T22:48:22Z): https://screenshots.phishdestroy.io/cf/a6a7d1ab-41ab-40d7-8bee-050cc099dfcb.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/4acbe857-2acb-40b3-b1f4-a4092f5d66a4.png URLScan screenshot (2026-08-29T17:45:22Z): https://screenshots.phishdestroy.io/us/01a04ea0-2efe-7015-8eb0-3ed92c789568.png URLScan capture report: https://urlscan.io/result/01a04ea0-2efe-7015-8eb0-3ed92c789568/ URLScan screenshot (2026-08-30T10:34:10Z): https://screenshots.phishdestroy.io/us/01a0523b-c181-73ed-83d3-4ad3d1bb6e74.png URLScan capture report: https://urlscan.io/result/01a0523b-c181-73ed-83d3-4ad3d1bb6e74/ URLScan screenshot (2026-10-26T22:28:09Z): https://screenshots.phishdestroy.io/us/01a17a53-ece9-7440-8726-b6af72bd23d2.png URLScan capture report: https://urlscan.io/result/01a17a53-ece9-7440-8726-b6af72bd23d2/ VirusTotal report: https://www.virustotal.com/gui/domain/firmvestode.org Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=firmvestode.org Archived copy: https://web.archive.org/web/20261026221838/https://firmvestode.org/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
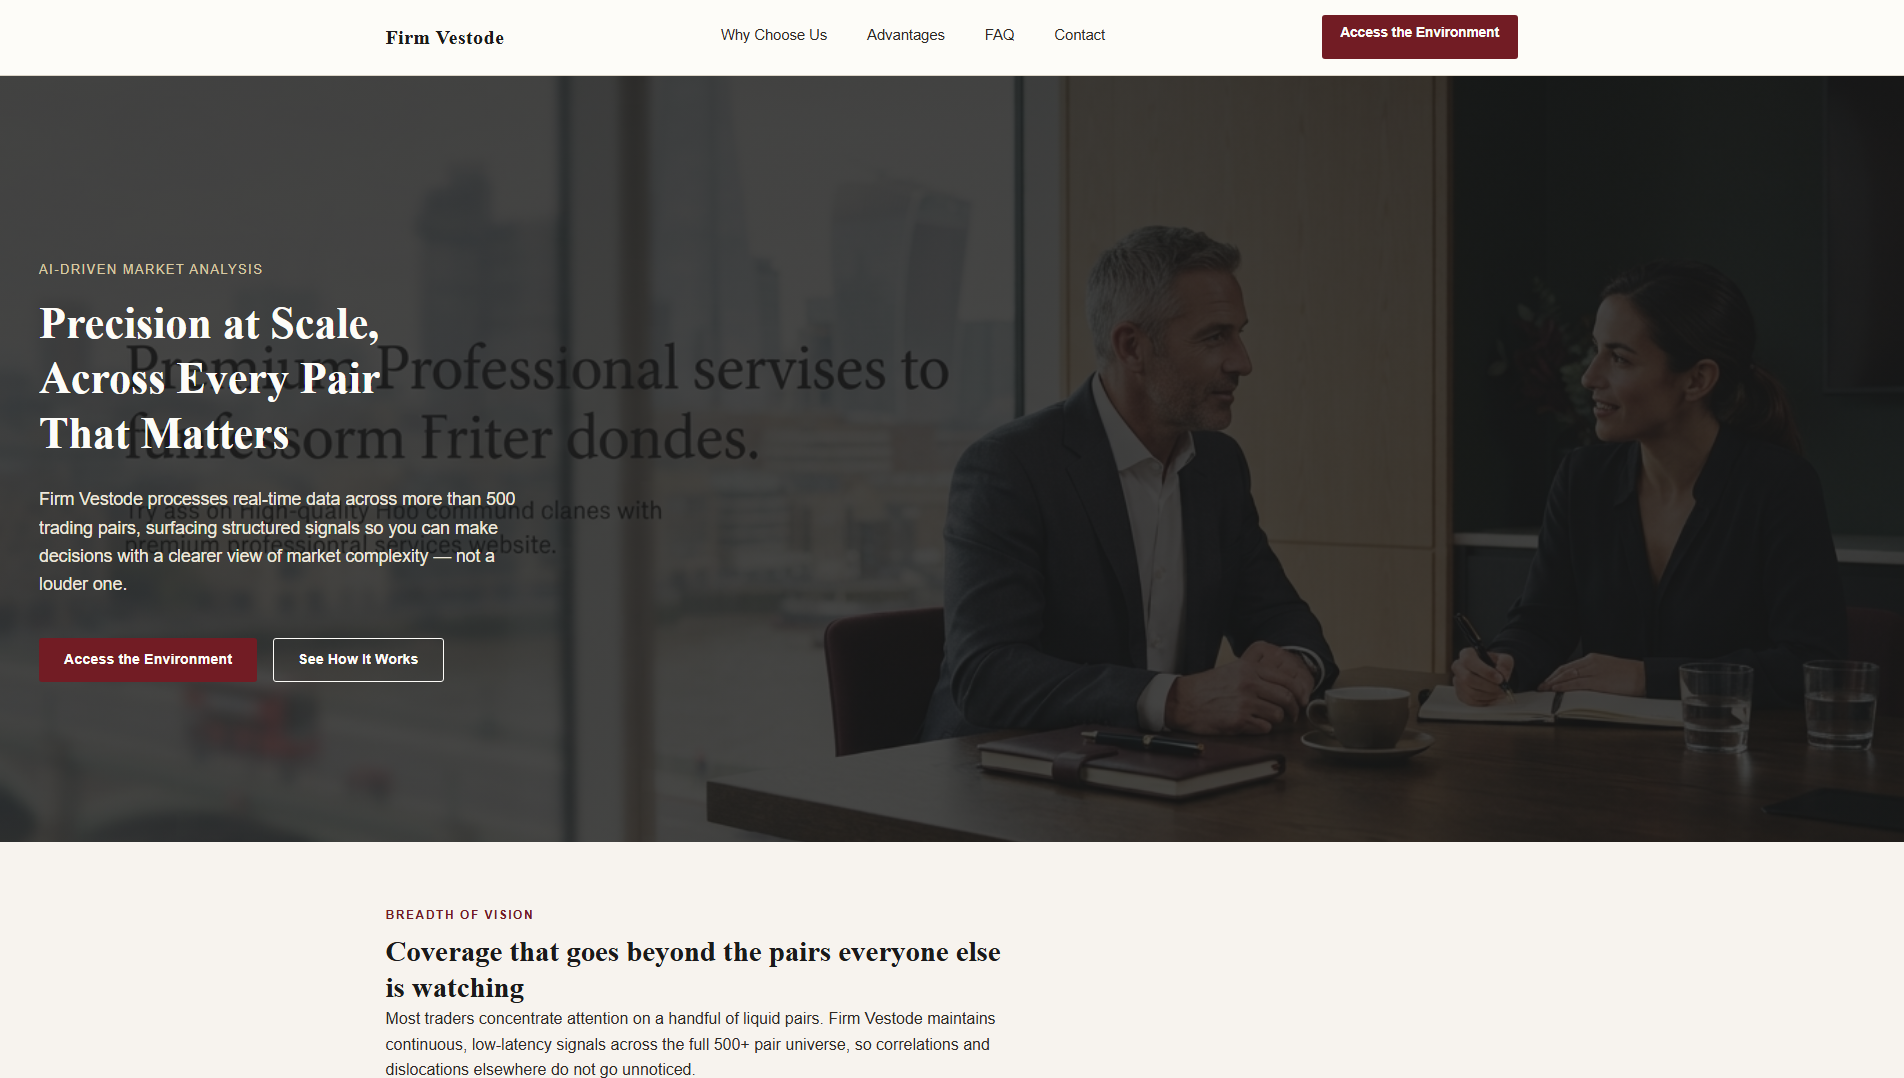
Firm Vestode transforms streaming market data into structured signals across 500+ trading pairs, filtering noise to surface what actually matters. Explore the platform and see how it works.
Title: Firm Vestode — AI Platform for Real-Time Market Analysis; Robots: index, follow, max-snippet:-1, max-image-preview:large, max-video-preview:-1; Description: Firm Vestode transforms streaming market data into structured signals across 500+ trading pairs, filtering noise to surface what actually matters. Explore the platform and see how it works.; Canonicalurl: https://firmvestode.org/
Headers: Server: cloudflare; Content type: text/html; charset=utf-8; X content type options: nosniff; Referrer policy: same-origin; Via: 1.1 Caddy
보안 신호
Scamadviser 경고1/100
The Tranco rank (how much traffic) is rather low Cryptocurrency services detected, these can be high risk The age of this site is (very) young. The website was reported in the last 30 days as threat by DNSFilter This website was reported by IPQS for phishing. This website has been classified as suspicious by IPQS
We found a valid SSL certificate
네트워크 보안 인텔리전스
Cloudflare Radar 판정 결과악성
Security threats Malware Malware 사기
firmvestode.org 관련 질문
firmvestode.org은(는) 정상적인 사이트인가요?
PhishDestroy는 기록된 증거를 바탕으로 firmvestode.org를 심각 위험 등급(증거 점수 100/100)으로 평가했으며, 이는 2026-10-26에 처음 기록되었습니다. 저장된 VirusTotal 결과: 17/92 엔진에서 경고했습니다. 악성: 14. 의심: 3. 분석 시간(저장된 표기): 2026-10-19 17:14 UTC. 조회 시간(저장된 표기): 2026-10-26 23:52 UTC. 자체 점수와 목록 등재만으로 사기가 입증되지는 않습니다. 각 출처의 날짜와 정확한 URL을 확인하세요.
firmvestode.org에 지갑을 연결해도 안전한가요?
앞서 언급된 위험 신호로 인해, 해당 사이트에서 지갑을 연결하거나 메시지에 서명하거나 토큰 권한을 approve하지 마십시오. 확인된 블록체인 거래는 되돌릴 수 없습니다.
firmvestode.org을(를) 이용했다면 어떻게 해야 하나요?
비밀번호를 입력했습니다 — 해당 서비스와 동일한 비밀번호를 사용한 다른 모든 사이트에서 비밀번호를 변경하세요.
2단계 인증을 켜세요 — 해당 서비스가 지원하는 경우, 인증 앱은 SMS 코드보다 보안성이 더 높습니다.
카드 또는 은행 정보를 결제하거나 입력했습니다. — 카드에 기재된 연락처나 공식 웹사이트를 통해 이용 중인 은행이나 결제 서비스 업체에 문의하십시오.
지갑을 연결했지만 아무것도 서명하지 않았습니다 — 지갑에서 해당 사이트를 연결 해제하고 보류 중인 요청을 거부하십시오. 연결만으로는 자금이 이체되지 않습니다.
토큰 지출 승인 (approve / permit) — 토큰 승인 검사기를 사용하여 해당 승인을 취소합니다
시드 문구나 개인 키를 공유했습니다 — 남은 자금을 새로운 시드 문구가 있는 새 지갑으로 옮기세요. 보안이 노출된 지갑은 더 이상 안전하지 않습니다.
파일을 다운로드했습니다 — 파일을 열지 말고 보안 소프트웨어로 기기를 검사하십시오.
경찰이나 기타 관할 기관에 신고할 때를 대비해 주소, 날짜, 결제 또는 거래 내역, 메시지 등을 잘 보관해 두십시오. 신고한다고 해서 반드시 돈이 돌려받는다는 보장은 없습니다. 단계별 안내: 긴급 대응 가이드.
1차 평가 변수Redirectingreason: HTTP redirect observed80% confidence
출처source: Current Http Probe
증거 레이어Availability: RedirectingDNS: Resolved
최신 HTTP 관측 결과RedirectingHTTP redirect observed80%2026-11-22 11:30 UTC
RDAP 등록
관측된 시간축last reachable: 2026-11-22 11:30 UTClast content: 2026-11-02 11:46 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
기록된 이벤트: 13. 이 기록들은 수집된 증거, 발송된 알림 및 차단 목록 등재를 설명하며, 조사가 완료되었거나 해당 사이트가 차단되었음을 확인하는 것은 아닙니다.
선제적 탐지 및 데이터 수집위협 데이터 수집 완료기록됨
위협 데이터 수집 완료
firmvestode.org이 탐지되어 전체 분석을 위해 대기열에 추가됨
위협 인텔리전스 확인URLScan.io 캡처 · URLScan 판정 결과 · Cloudflare Radar 보고서 · 웹 아카이브 · VirusTotal · OTX 커뮤니티 참조 자료 · Cloudflare Radar: 악성 · 자동 브랜드 라벨: Signal · 수집된 포렌식 증거 · 기록된 기술 분석기록됨
당신은 혼자가 아니며, 부끄러워할 일은 전혀 없습니다. 사기범은 신뢰를 악용하는 교묘한 범죄자입니다. 피해 사실을 신고하는 것은 사기에 맞서는 가장 강력한 무기입니다. 당신의 신고가 다른 사람의 피해를 막고 수사 기관의 대응을 도울 수 있습니다. 먼저 계정과 자금을 안전하게 보호한 후 신고하십시오. 계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.
실제로 취한 조치에 따라 대응하십시오. 비밀번호를 입력했다면, 해당 비밀번호와 이를 재사용한 모든 곳에서 비밀번호를 변경하십시오. 카드 정보를 결제하거나 제공했다면, 은행이나 결제 서비스 업체에 연락하십시오. 파일을 다운로드했다면, 기기를 바이러스 검사하십시오. 그런 다음 해당 사건을 신고하십시오.


 Dynadot
 104.21.19.129


 Microsoft
 Cloudflare
 Yandex
 ESET
 비트디펜더
 Norton
 Symantec
 Avira
 Avast / AVG
 카스퍼스키
 Dr.Web
 넷크래프트
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT