VirusTotal
6 / 89 engine detections
보고서 열기

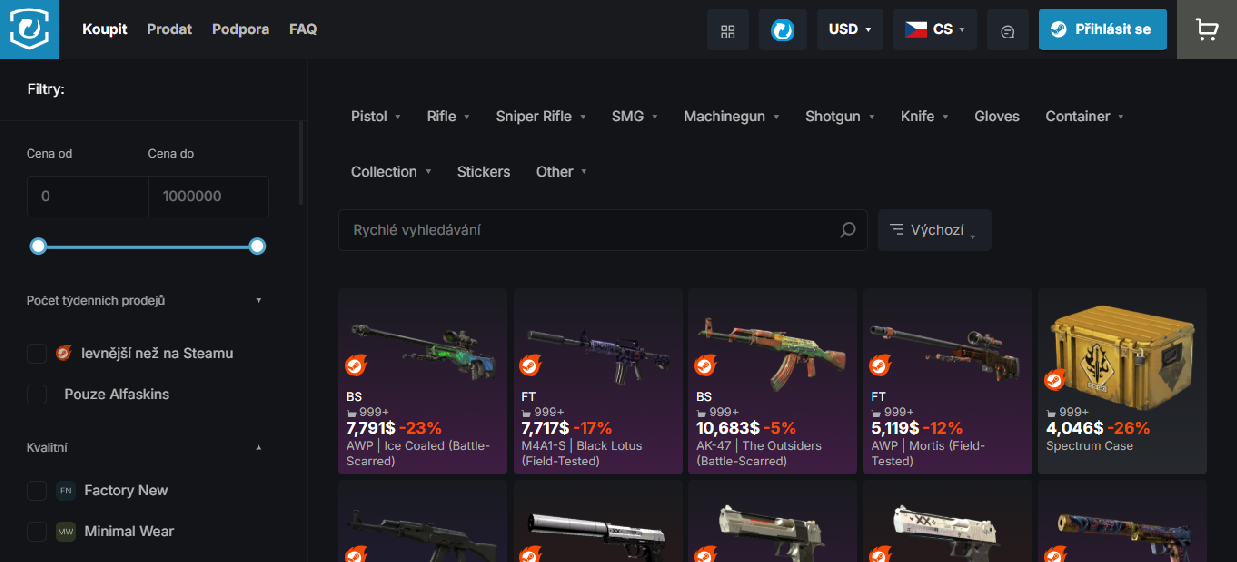
“Buy and Sell Counter-Strike 2 (CS2) Skins - CS GO Market”
cs2.market — 클로킹됨 · 접근 가능 (HTTP 301). 사기 유형: Generic Phishing. 증거 요약: VirusTotal 6/89 (BitDefender, ESET, G-Data, Gridinsoft, SafeToOpen); cloaking observed; PhishDestroy score 100/100. 등록기관: GoDaddy.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
6 / 89 engine detections
보고서 열기checked — no detections recorded
보고서 열기checked — no match recorded
23 community references
보고서 열기provider verdict: clean
보고서 열기14 확인됨 — 차단 없음
No threat flag
보고서 열기No malicious flag
보고서 열기Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
This domain, cs2.market, is currently flagged as a high-risk generic phishing site. Created on March 12, 2026, the domain has been identified in various threat intelligence reports and is listed on at least one security blocklist. The page title 'Buy and Sell Counter-Strike 2 (CS2) Skins - CS GO Market' suggests that the site is attempting to impersonate a legitimate market for Counter-Strike 2 skins, a popular feature in the gaming community. Analysis indicates that the domain is still active and has been flagged by 10 out of 95 security vendors on VirusTotal, further corroborating its malicious nature. The domain is registered through GoDaddy.com, LLC and resolves to the IP address 195.85.59.45. Notably, the site employs several advanced technologies, including HSTS, Cloudflare Browser Insights, and HTTP/3, which may be used to enhance the credibility of the phishing site and evade detection. Additionally, the domain is blocked by PhishDestroy and has been mentioned in 23 threat intelligence pulses on AlienVault OTX, highlighting its significance in ongoing phishing campaigns. Defenders should immediately block access to this domain and monitor network traffic for any signs of users attempting to access it. Given the domain's high risk level and the specific targeting of gamers interested in CS2 skins, organizations should also educate their users about the dangers of phishing sites, especially those that mimic legitimate gaming platforms. Infrastructure analysis reveals the use of a Google Trust Services SSL certificate, which, while legitimate, does not guarantee the safety of the site and should not be used as a sole indicator of trustworthiness. Overall, the combination of the domain's creation date, security vendor flags, and technological features strongly suggests that cs2.market is a sophisticated phishing operation targeting gamers, and proactive measures are essential to mitigate potential risks.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
https://t.me/marketcsgoskinsStored page referenceIoC extraction recorded 2026-07-29 02:26:10 UTC
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Edge-IP 평판은 이 도메인에 귀속되지 않습니다.
coby.ns.cloudflare.comLocation describes the IP network.
99fb789afd77046a4f71fb01037ad96489b9e7431b4d89813bc36e2c6a13f7e4Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of cs2.market · checked Jul 12, 2026
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
content_divergence · redirect: raw=redirect_301; http=301; via=https_proxy; location=https://cs2.market/en/; server=cloudflare
cs2.market
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
1→10
No threat flag
View source23 community references
View source6/89 engine detections
View sourcePage captured
View sourcecs2.market
View source각 레인은 도메인이 이 호스트에 연결된 이유 중 하나를 나타냅니다. 노드의 크기는 VirusTotal 탐지 건수를 나타내며, 점선으로 표시된 노드는 이미 오프라인 상태입니다. 전체 목록은 아래와 같습니다.
Unknown 피싱 캠페인의 일부입니다. 모든 캠페인 도메인 보기 →
동일한 등록 기관을 통해 등록되었습니다. 등록 기관은 서로 관련이 없는 수백만 명의 고객을 상대하기 때문에, 이는 두 항목 간의 연관성을 입증하기보다는 단순히 보고를 묶어놓은 것에 불과합니다.
커뮤니티 구성원 1명이 신고 · 최초 확인 2026년 3월 12일
Listed domains receive at least one abuse report; this entry has no retained notification history.
계정 자격 증명, 개인 정보 또는 결제 정보를 입력했거나 이 도메인에서 파일을 다운로드한 경우 즉시 조치를 취하세요. 다음은 사건을 신고하고 자신을 보호하는 데 도움이 되는 리소스입니다.
공식 사이버 범죄 연락처 또는 불만사항 초안 작성 →를 받으려면 국가를 선택하세요.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
cs2.market)비록 모든 세부 사항을 알지 못하더라도 — 어쨌든 신고를 하세요. 부분적인 정보라도 수사에 도움이 됩니다.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.