Cloudflare Radar
Suspicious
보고서 열기

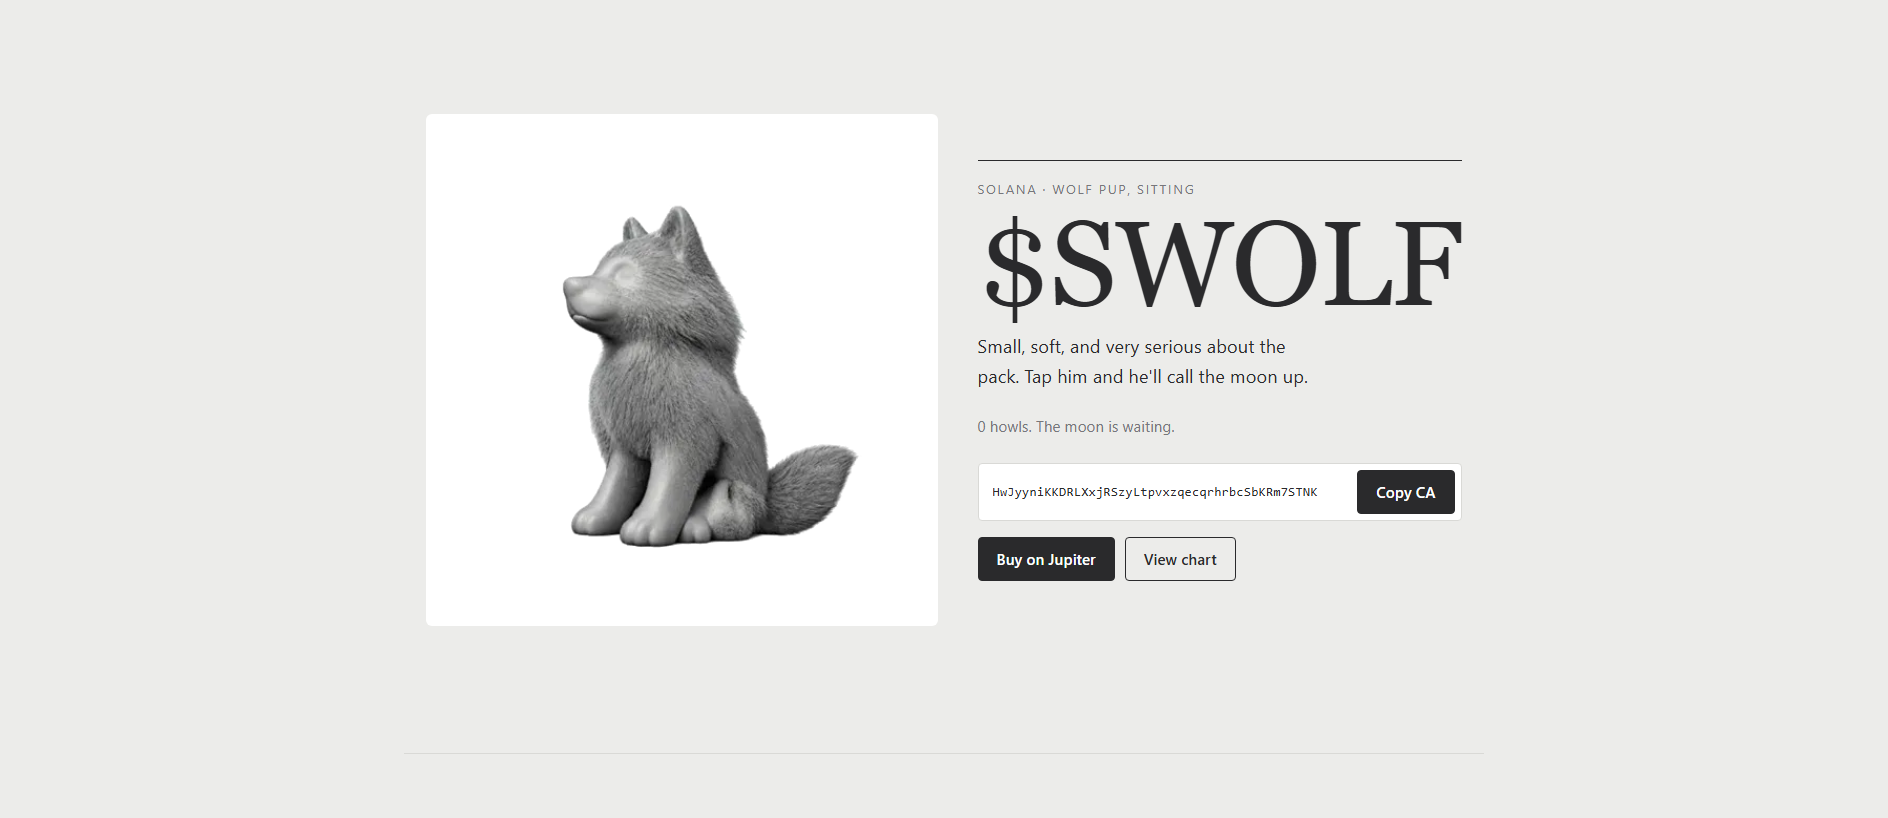
“$SWOLF”
binderfinance.lol — 콘텐츠를 사용할 수 없음. 브랜드 사칭: Backpack; 사기 유형: Impersonation. 증거 요약: VirusTotal 0/92; 1 external blocklist match (ScamSniffer); PhishDestroy score 78/100. 등록기관: PDR.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
Suspicious
보고서 열기0 / 92 engine detections
보고서 열기Scan report
보고서 열기3 community references
보고서 열기No threat flag
보고서 열기No malicious flag
보고서 열기Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
binderfinance.lol is an impersonation phishing page that presented itself under the title "$SWOLF", a token-style ticker aimed at crypto users chasing a new memecoin. PhishDestroy first flagged it on 2026-10-14. The site is now dead: its DNS stopped resolving and it has been offline since 2026-10-17, which our check on 2026-10-19 confirmed. The page title shows a token ticker, while the domain name suggests a finance brand, and we classified the site as impersonation.
Pages like this borrow the look and name of a token project, here branded as $SWOLF, so a visitor believes they are on an official buy, claim or presale page. The visitor is then pushed to connect a wallet and approve a transaction or signature, or sometimes to type in a recovery phrase to "verify" eligibility. Whatever the victim approves or reveals hands control to the operator, who can move tokens out of the wallet. Funds taken this way are generally not recoverable.
ScamSniffer, a blocklist focused on crypto wallet threats, lists the domain alongside PhishDestroy. VirusTotal returned 0 detections out of 92 engines on 2026-10-14, the same day we caught it. That clean score shows how new crypto lures slip past general-purpose scanners in their first days. Three AlienVault OTX pulses also reference the domain, so other researchers had tracked it independently.
The domain was registered on 2026-10-06 through PDR Ltd. d/b/a PublicDomainRegistry.com, only eight days before we detected it. It ran on Amazon's AS16509 network from servers in Germany, on a Let's Encrypt certificate, so a padlock in the browser said nothing about whether the site was legitimate. The whole run, from registration to going dark on 2026-10-17, lasted about eleven days, which fits a short campaign built around a single token hype cycle.
If you connected a wallet to this site, open a token-approval manager and revoke any permissions you granted around 2026-10-14 to 2026-10-17. Move remaining assets to a fresh wallet if you signed anything you did not understand. If you typed in a seed phrase, treat that wallet as compromised and transfer everything to a new one created from a new phrase. Only reach token projects through links published on their verified official channels. Defenders should block the domain and watch for lookalike finance-themed domains that use .lol or other cheap TLDs and carry token-ticker page titles, because a zero score on VirusTotal is not a reliable all-clear for this kind of page.
Last checked
 (DE)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Edge-IP 평판은 이 도메인에 귀속되지 않습니다.
dns1.p04.nsone.netdns2.p04.nsone.netdns3.p04.nsone.netdns4.p04.nsone.netLocation describes the IP network.
ff4f3e35eada8109771bb8d56847f9095230e4130423d606b11f75b6f5dd1db1Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of binderfinance.lol · checked Oct 14, 2026
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
http://binderfinance.lol/https://binderfinance.lol/Cache-Control: public,max-age=0,must-revalidateContent-Encoding: gzipContent-Type: text/html; charset=UTF-8Server: Netlifybytes2public,max-age=0,must-revalidate"Netlify Edge"; fwd=miss; fwd-status=200; storedgziptext/html; charset=UTF-8Wed, 14 Oct 2026 19:42:09 GMT"04996471c8ac183ee25e8a6cf8e50dff-ssl-df"Netlifymax-age=31536000chunkedAccept-Encoding01M4XYZEGSAZHVZN102D1RYQ3DValues retained by the collector; long values may be shortened during collection.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
알 수 없음→dns_inactive
dns_nxdomain
알 수 없음→dns_inactive
dns_nxdomain
접속 가능→이용 불가
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
접속 가능
No threat flag
View source3 community references
View source0/92 engine detections
View sourcePD-20261014-75CA67
binderfinance.lol
View sourcePage captured
View source각 레인은 도메인이 이 호스트에 연결된 이유 중 하나를 나타냅니다. 노드의 크기는 VirusTotal 탐지 건수를 나타내며, 점선으로 표시된 노드는 이미 오프라인 상태입니다. 전체 목록은 아래와 같습니다.
이 호스트와 동일한 파비콘 해시이거나 동일한 페이지 제목을 가진 경우.
이러한 보고서는 동일한 공유 에지 IP로 확인됩니다. 이는 보고서 검색에 도움이 되지만 공통 소유권이나 공유 원본 서버를 의미하지는 않습니다.
Reports with the same collector label. A shared label does not establish impersonation or common ownership. View matching reports →
동일한 등록 기관을 통해 등록되었습니다. 등록 기관은 서로 관련이 없는 수백만 명의 고객을 상대하기 때문에, 이는 두 항목 간의 연관성을 입증하기보다는 단순히 보고를 묶어놓은 것에 불과합니다.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
binderfinance.lol
PD-20261014-75CA67 Recipient: abuse@publicdomainregistry.com AUP & Terms of Service Violations: Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices. Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension. Applicable Legal Framework (DE): German Criminal Code § 263 (Fraud) German Criminal Code § 263a (Computer Fraud) Telemedia Act (TMG) German law prohibits fraud and computer-based deception. Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
계정 자격 증명, 개인 정보 또는 결제 정보를 입력했거나 이 도메인에서 파일을 다운로드한 경우 즉시 조치를 취하세요. 다음은 사건을 신고하고 자신을 보호하는 데 도움이 되는 리소스입니다.
공식 사이버 범죄 연락처 또는 불만사항 초안 작성 →를 받으려면 국가를 선택하세요.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
binderfinance.lol)비록 모든 세부 사항을 알지 못하더라도 — 어쨌든 신고를 하세요. 부분적인 정보라도 수사에 도움이 됩니다.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.