URLQuery
2 det.
보고서 열기
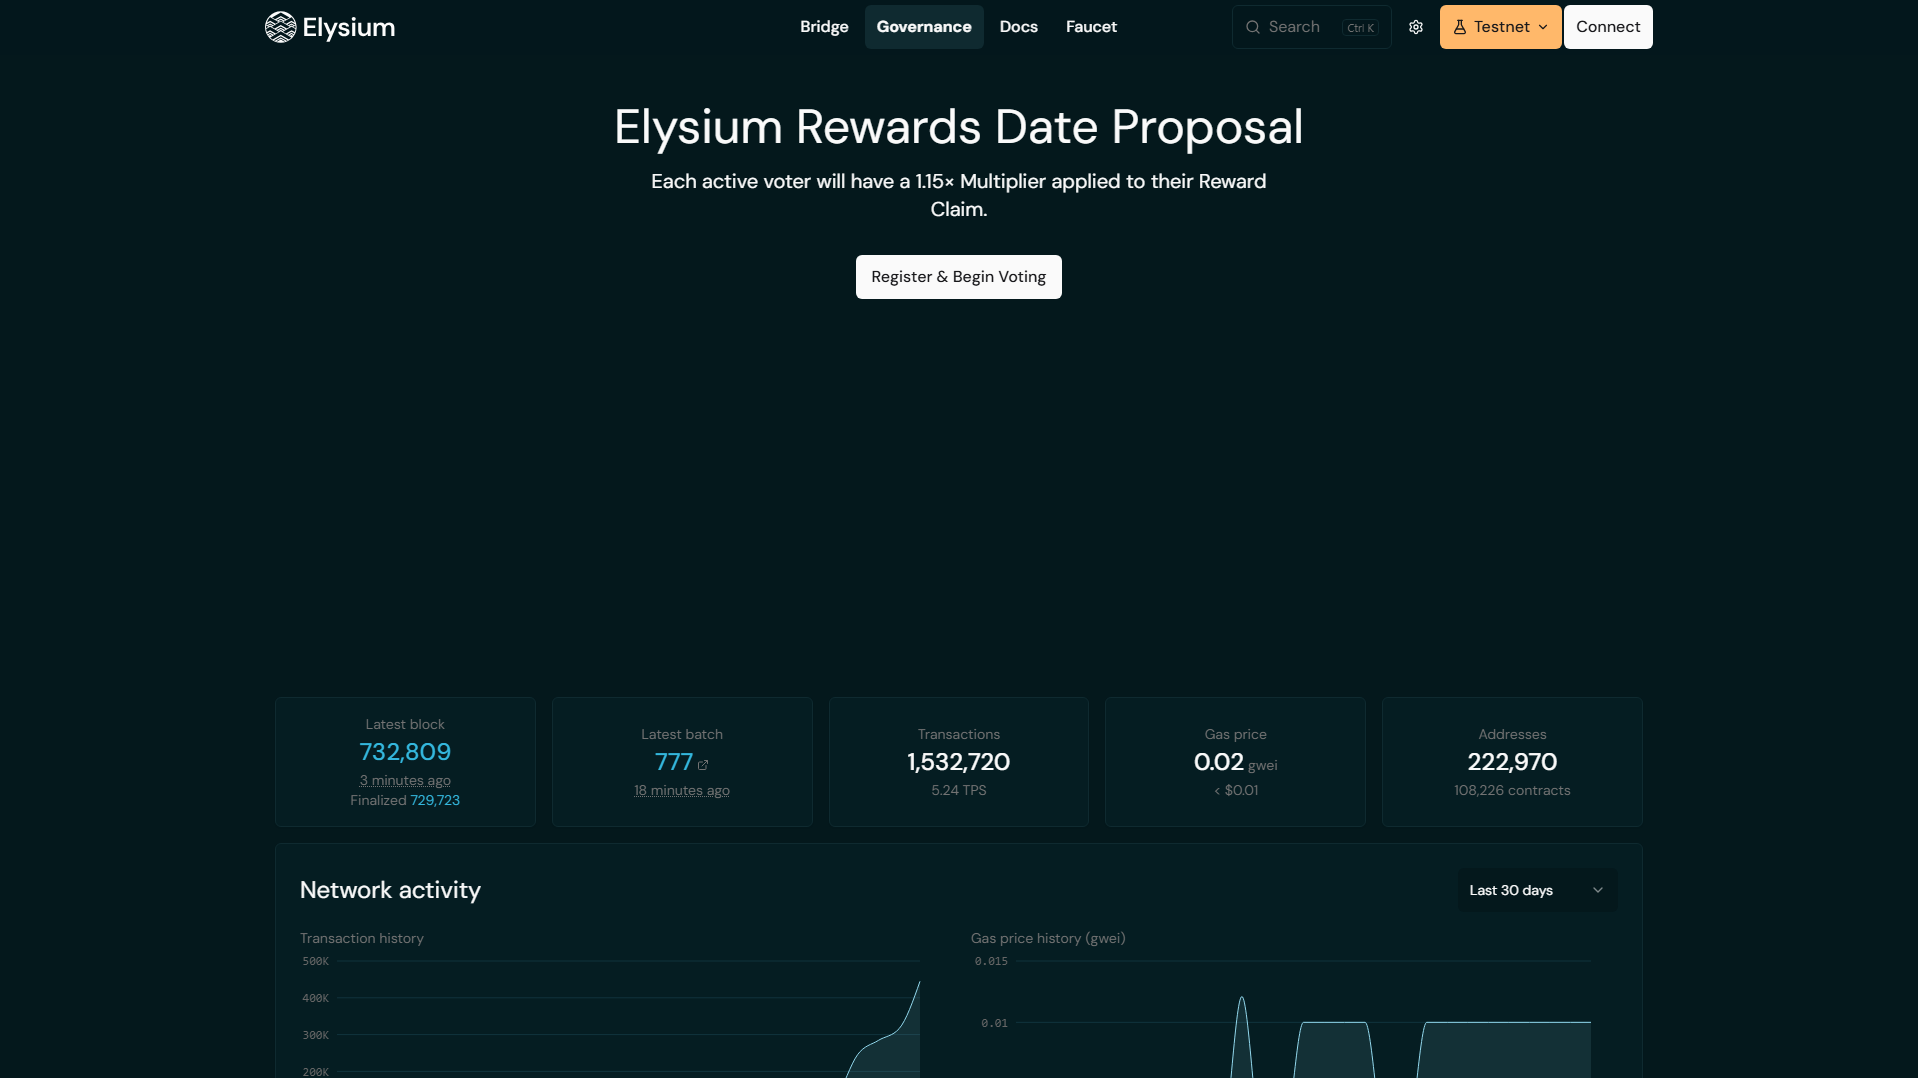
“Elysium | Governance”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@dynadot.com.
The latest stored availability evidence still shows the domain reachable; 3 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
app-elysium.xyz — 마지막으로 알려진 활성 (HTTP 301). 사기 유형: Impersonation. 증거 요약: VirusTotal 0/92; URLQuery 2 det.; PhishDestroy score 78/100. 등록기관: Dynadot.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
2 det.
보고서 열기Suspicious
보고서 열기0 / 92 engine detections
보고서 열기4 community references
보고서 열기No threat flag
보고서 열기No malicious flag
보고서 열기Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
app-elysium.xyz is an impersonation phishing page that presents itself as a governance portal for Elysium, with the page title "Elysium | Governance". It targets Elysium users and people who expect to vote on or manage proposals through an official app. PhishDestroy first detected the domain on 2026-10-17. As of 2026-10-19 the site was still online and its content was reachable through a redirect.
Fake governance portals copy the look and wording of a real project's voting dashboard. They often sit on a lookalike domain, here an "app-" prefix on a cheap .xyz name, so the address seems like an official subdomain. Victims usually arrive through links shared in social media replies, community chats or direct messages urging them to vote, claim or verify before a deadline. Once on the page, the visitor is pushed to connect a wallet, sign a request or hand over credentials. That action gives the operators control over the victim's funds or account rather than casting any real vote.
PhishDestroy classifies this domain as impersonation and lists it on its blocklist. VirusTotal returned 0 detections out of 92 engines on 2026-10-17, so mainstream vendors had not flagged it at the time of our detection. The domain appears in 4 AlienVault OTX pulses, which gives independent threat-intelligence context. A clean VirusTotal result for a recently registered phishing domain is common and should not be read as a sign of safety.
The domain was registered on 2026-09-29 through Dynadot Inc, less than three weeks before PhishDestroy detected it. It resolves to 172.67.150.73 on the Cloudflare network (AS13335) in the United States. The site serves a TLS certificate issued by Let's Encrypt (YE2), so the padlock in the browser confirms only an encrypted connection and says nothing about legitimacy.
Do not open the site or follow links to it, and reach Elysium governance only through addresses published on the project's official channels. If you connected a wallet or signed anything there, move remaining assets to a fresh wallet. Use a token approval checker to review and revoke any permissions you granted. If you entered a password or seed phrase, treat it as compromised and replace it immediately. Defenders should block the domain at DNS and proxy level, report it to Cloudflare and Dynadot, and warn Elysium community channels about the lookalike.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
0x0B809f9C0aD91248DB28d4B5C2B59c563ea49C81Format validated · Domain analysis0x0E865d156da937191d7C4814126718f583447798Format validated · Domain analysis0x10ce23992Bea3709F4E73f875665c0B59A32eBDaFormat validated · Domain analysis0x245bFe8c6c2429f6a7743d53377Ae39b98500459Format validated · Domain analysis0x4A611D95495F8a90779FFd39986aab85359A2CDfFormat validated · Domain analysis0x57A48162BD894964db10b2751a2e89Ae0FA56523Format validated · Domain analysis0x58E5dfF1f9f63153De9824055b711741faC71aAAFormat validated · Domain analysis0x7551Bb3D085021bcEC0812B18A268Ee6A888C4a0Format validated · Domain analysis0x93dD4317e1B4807b1Cd7CdF46bA11266D43e76E8Format validated · Domain analysis0x9672D621C16d8E599c2e20Cc6EEDDf9402aC2a17Format validated · Domain analysis0xA4b000000000000000000073657175656e636572Format validated · Domain analysis0xCebC1EAD2f2DEB930b84412A752EfcD54567D4bCFormat validated · Domain analysis0xaC00056863176dD5120FF79710cEcE1dAF62A125Format validated · Domain analysis0xb5C933bf1f00063696865260E578c0cd7dB7d755Format validated · Domain analysis0xb94A38a4aC46970559E89E566f2486a3Fc56BE5aFormat validated · Domain analysisIoC extraction recorded 2026-10-18 04:00:33 UTC
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Edge-IP 평판은 이 도메인에 귀속되지 않습니다.
delilah.ns.cloudflare.comlochlan.ns.cloudflare.comLocation describes the IP network.
2d53405c0ce67adc3331ef19721ca6bdaedfe57f218bb609cddfc840b918a68dSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
https://app-elysium.xyz/voteContent-Type: text/html;charset=utf-8CF-Cache-Status: DYNAMICContent-Encoding: gzipServer: cloudflare1d827b2ac019adb0b48727e61bf6a218c90b12c0f84883252b1bf32c1aa8646ch3=":443"; ma=86400DYNAMICa4be05896b3dffb2-EWRkeep-alivegziptext/html;charset=utf-8Sat, 17 Oct 2026 08:44:29 GMT{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=nRCC91TS%2BO8YtWZ2KJe9TaQ9TfJ2%2BhPLG1er5aEMwBNJqo2JWqme%2F3ZS9MWkfWzAGRoKDwZJMlv3HoGvgv0DHR3xbtzy5Wufro4jZXT%2BMbZfaYEFcIDdpIHhzdHjeJEpUdE%3D"cloudflarecfCacheStatus;desc="DYNAMIC"chunkedAccept-EncodingValues retained by the collector; long values may be shortened during collection.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
redirect: raw=redirect_301; http=301; via=http_proxy; location=https://app-elysium.xyz/; server=cloudflare
app-elysium.xyz
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
알 수 없음→redirected
http_redirect
접속 가능
No threat flag
View source4 community references
View source0/92 engine detections
View sourcePD-20261017-BC01B7
Page captured
View sourceapp-elysium.xyz
View source각 레인은 도메인이 이 호스트에 연결된 이유 중 하나를 나타냅니다. 노드의 크기는 VirusTotal 탐지 건수를 나타내며, 점선으로 표시된 노드는 이미 오프라인 상태입니다. 전체 목록은 아래와 같습니다.
이러한 보고서는 동일한 공유 에지 IP로 확인됩니다. 이는 보고서 검색에 도움이 되지만 공통 소유권이나 공유 원본 서버를 의미하지는 않습니다.
동일한 등록 기관을 통해 등록되었습니다. 등록 기관은 서로 관련이 없는 수백만 명의 고객을 상대하기 때문에, 이는 두 항목 간의 연관성을 입증하기보다는 단순히 보고를 묶어놓은 것에 불과합니다.
PD-20261017-BC01B7 Recipient: abuse@dynadot.com Registrar: Dynadot LLC / Dynadot Inc (United States) Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
계정 자격 증명, 개인 정보 또는 결제 정보를 입력했거나 이 도메인에서 파일을 다운로드한 경우 즉시 조치를 취하세요. 다음은 사건을 신고하고 자신을 보호하는 데 도움이 되는 리소스입니다.
공식 사이버 범죄 연락처 또는 불만사항 초안 작성 →를 받으려면 국가를 선택하세요.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
app-elysium.xyz)비록 모든 세부 사항을 알지 못하더라도 — 어쨌든 신고를 하세요. 부분적인 정보라도 수사에 도움이 됩니다.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.