VirusTotal
5 / 92 engine detections
보고서 열기

admin.foundation.byrds.dev: Foundation 사칭. PhishDestroy가 2026-09-08에 탐지했습니다. 위험도: 심각 (85/100). 등록 대행자: OVH sas. 상태: 마지막으로 알려진 활성. 호스팅: OVH OVH SAS, FR. PhishDestroy는 악용 신고 1건을 보냈습니다. VirusTotal: 엔진 5/92개가 탐지. 로그인 정보를 입력하거나 지갑을 연결하지 마세요.
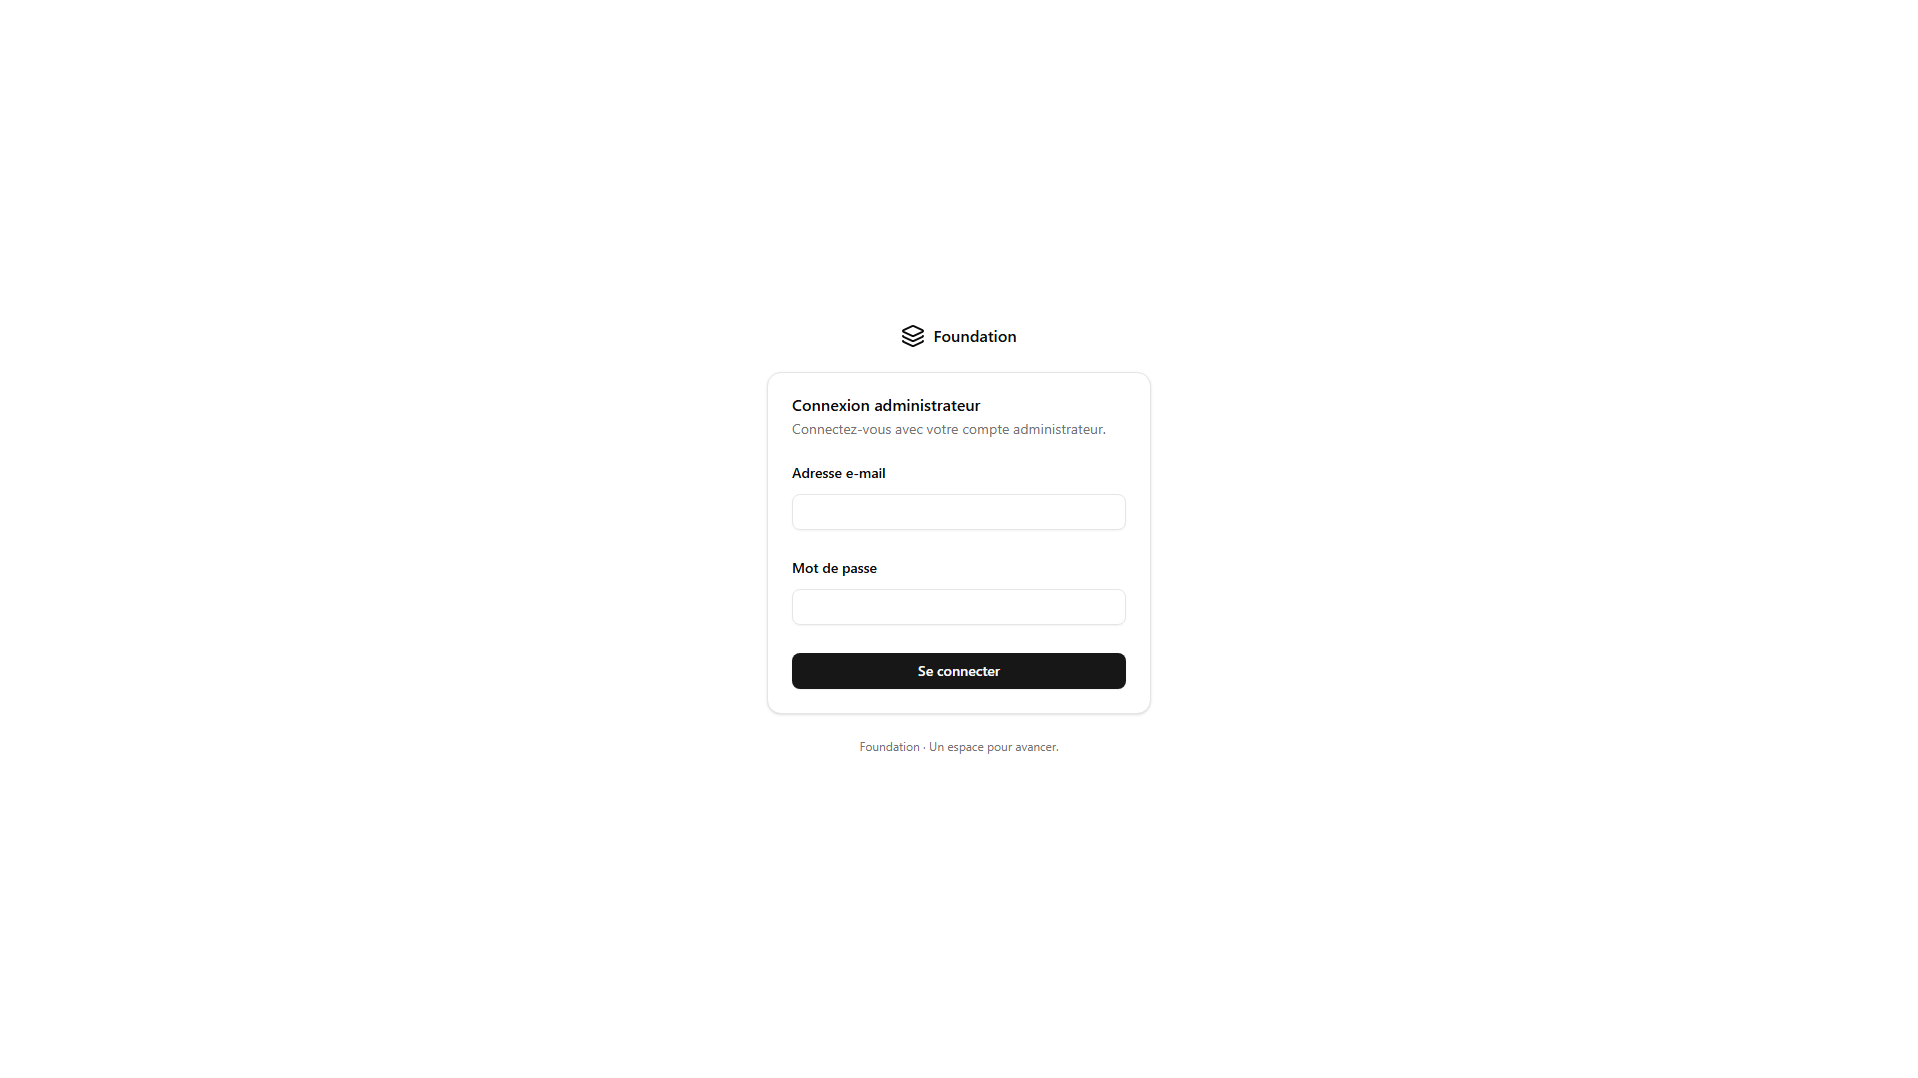
“Foundation · Administration”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@ovh.net.
The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Foundation 사칭: admin.foundation.byrds.dev — 마지막으로 알려진 활성 (HTTP 200). 증거 요약: VirusTotal 5/92 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Gridinsoft…
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
5 / 92 engine detections
보고서 열기확인됨 — 탐지 기록 없음
보고서 열기커뮤니티 참조 없음
보고서 열기provider verdict: clean
보고서 열기위협 플래그 없음
보고서 열기악성 플래그 없음
보고서 열기결과는 각 출처의 수집 시점을 기준으로 합니다. 탐지 0건이 안전을 보장하지는 않습니다. OTX 참조는 커뮤니티 게시물입니다.
PhishDestroy threat report
admin.foundation.byrds.dev is an impersonation phishing page posing as Foundation. Its page title is "Foundation · Administration", so it presents itself as an internal admin console rather than the public site, and it targets people who use Foundation or hold crypto wallets. PhishDestroy first flagged it on 2026-09-08. As of 2026-10-19 the site was still alive and its content now redirects visitors elsewhere.
Impersonation pages like this borrow a trusted brand's name and look so visitors will act without second-guessing. An "Administration" label adds false authority. It can make a request to log in, verify an account or connect a wallet feel like official procedure. Whatever the victim types or approves goes to the operator, not to Foundation. Depending on what is entered, that can mean stolen account credentials, a leaked recovery phrase or a malicious wallet signature that moves assets out.
Wallet-security blocklists back the classification. MetaMask and SEAL both list the domain alongside PhishDestroy, so users of those protections should already see a warning. Coverage on VirusTotal is thinner, with 5 of 89 engines flagging it as of 2026-09-22: alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Gridinsoft and SOCRadar. That low count means many general-purpose security tools will still let the page load without a warning.
The page sits on a subdomain of byrds.dev, which was registered on 2020-10-27 through OVH sas. That is nearly six years before PhishDestroy detected this page, so the age of the parent domain says little about how trustworthy this subdomain is. The site is hosted in France on the OVH SAS network at 146.59.151.218. Its certificate comes from Let's Encrypt, so the padlock in the browser only means the connection is encrypted, not that the site is genuine.
If you entered a Foundation login or email password here, change it now. Do the same anywhere you reused it, and turn on two-factor authentication. If you typed a seed or recovery phrase, treat that wallet as compromised and move your funds to a newly created wallet. If you connected a wallet or signed anything, check the token approvals on a revocation tool and revoke any you don't recognize. Defenders should block the full hostname, including future redirect targets from it, and add it to wallet and mail filtering, since most antivirus engines still don't flag it.
저장된 페이지, 네트워크, 스캐너 관측 결과를 출처와 관측 시각별로 묶어 보여 줍니다.
관측됨: · Retrieved:
| Uuid | 01a08075-0372-754a-89fa-1ba728bc61db |
|---|---|
| Final url | https://admin.foundation.byrds.dev/ |
| 상태 | 200 |
| 리디렉션됨 | https-only |
| Redirects | [
{
"to": "https://admin.foundation.byrds.dev/",
"from": "http://admin.foundation.byrds.dev/",
"status": 307
}
] |
| Ip | 146.59.151.218 |
| Ptr | vps-3f658227.vps.ovh.net |
| Contacted IP addresses | [
"146.59.151.218"
] |
| Asns | [
"16276"
] |
| Countries | [
"FR"
] |
| Linked domains | [
"foundation.byrds.dev"
] |
| Document hash | b9aadcc6ecadf35b7022a2a04d9cd16c0733ba9ee5904b8fd4a63d303edc433a |
| Script hashes | [
"853a466edd3d82da3e68b67122a9542b03981f24eee46c706b2da224a474747b",
"848b0037fdae0e756eb091eb981f29c451eecadc7866dfee8bbcd6f584a5b31e",
"e91810e5d0cf8d930d485e32bf41b9dc4cc9a1add9afdc14e149187a707a92fe"
] |
| Globals | [
"$R",
"nanostoresGlobal",
"__zod_globalConfig",
"__zod_globalRegistry",
"__TSR_ROUTER__",
"__TSS_START_OPTIONS__"
] |
| Tls | {
"san": [
"admin.foundation.byrds.dev",
"app.foundation.byrds.dev",
"foundation.byrds.dev"
],
"cipher": "AES_128_GCM",
"issuer": "YE1",
"subject": "admin.foundation.byrds.dev",
"protocol": "TLS 1.3",
"valid_to": "2026-12-06T21:15:41Z",
"valid_from": "2026-09-07T21:15:42Z"
} |
| 도메인 연령(일) | 0 |
| Apex age days | 2141 |
| Tls age days | 0 |
| TLS 유효 일수 | 89 |
| Requests | 8 |
| Provider verdicts | {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-60c5e22"
],
"score": 21,
"malicious": true
},
"overall": {
"score": 0,
"malicious": false
}
} |
| HTTP headers | {
"server": "openresty",
"content-type": "text/html; charset=utf-8"
} |
관측됨: · Retrieved:
| Uuid | c8c1b676-cf5b-400f-9044-40c16dd7bb21 |
|---|---|
| Final url | https://admin.foundation.byrds.dev/ |
| 상태 | 200 |
| History | [
{
"url": "https://admin.foundation.byrds.dev/",
"status": 200
}
] |
| DOM structure hash | 029d85b5144b314f660a608b0ab4cc781c5454f84fe0ccfee7c2c34d6b100dff |
| Document hash | 40e6541809603faffed47004f0d9e815761f94889ba59a91cd0dc7b3ee3ce060 |
| Radar rank | {
"bucket": ">200000"
} |
| DNS 레코드 | [
{
"name": "admin.foundation.byrds.dev",
"type": "CNAME",
"value": "byrds.dev"
},
{
"name": "byrds.dev",
"type": "A",
"value": "146.59.151.218"
},
{
"name": "admin.foundation.byrds.dev",
"type": "CNAME",
"value": "byrds.dev"
}
] |
| DNSSEC 유효 | false |
| Ip | 146.59.151.218 |
관측됨: · Retrieved:
| Vendor result counts | {
"timeout": 0,
"harmless": 53,
"malicious": 4,
"suspicious": 1,
"undetected": 34
} |
|---|---|
| Vendor labels | {
"CRDF": "malicious",
"SOCRadar": "phishing",
"Gridinsoft": "suspicious",
"alphaMountain.ai": "phishing",
"Forcepoint ThreatSeeker": "phishing"
} |
| Reputation | 0 |
| 등록기관 | OVH sas |
| 생성됨 | 2020-10-27T20:47:49Z |
| Expires | 2025-10-27T20:47:49Z |
| Updated | 2024-02-04T12:21:22Z |
| 최초 발견 | 2026-09-07T22:35:56Z |
| DNS 레코드 | [
{
"ttl": 3600,
"type": "NS",
"value": "ns200.anycast.me"
},
{
"ttl": 3600,
"type": "A",
"value": "146.59.151.218"
},
{
"ttl": 3600,
"type": "NS",
"value": "dns200.anycast.me"
},
{
"ttl": 3600,
"type": "CNAME",
"value": "byrds.dev"
},
{
"ttl": 3600,
"type": "SOA",
"rname": "tech.ovh.net",
"value": "dns200.anycast.me"
}
] |
| Dns at | 2026-10-09T09:33:23Z |
| Jarm | 27d40d40d00040d00042d43d000000e1ea2a807a629b496b664cf07ad7c08d |
| Certificate | {
"san": [
"admin.foundation.byrds.dev",
"app.foundation.byrds.dev",
"foundation.byrds.dev"
],
"issuer": "Let's Encrypt / YE1",
"serial": "6a6a8dc476f29b8ece91ce5a6685e07fc96",
"sha256": "60677b3b741b9786cbd70f7a2cf12793848d2967d101987c726d04a5c98b1e46",
"subject": "admin.foundation.byrds.dev",
"valid_to": "2026-12-06T21:15:41Z",
"valid_from": "2026-09-07T21:15:42Z"
} |
| 등록 기록 | {
"registrar": "OVH sas",
"registrar_iana_id": "433",
"registrar_url": "https://www.ovh.com",
"created": "2020-10-27T20:47:49Z",
"updated": "2024-02-04T12:21:22Z",
"expires": "2025-10-27T13:02:42Z",
"status": [
"clientDeleteProhibited",
"clientTransferProhibited"
],
"nameservers": [
"dns200.anycast.me",
"ns200.anycast.me"
],
"dnssec": "unsigned"
} |
아니요. PhishDestroy는 admin.foundation.byrds.dev을(를) Foundation 사칭(으)로 분류합니다(위험도: 심각, 85/100). 처음 탐지된 날짜는 2026-09-08입니다. VirusTotal: 엔진 5/92개가 탐지. 안전하지 않은 사이트로 취급하세요.
아니요. admin.foundation.byrds.dev에서 지갑을 연결하거나 메시지에 서명하거나 토큰을 승인하지 마세요. 피싱 사이트는 운영자가 자산을 옮길 수 있게 하는 승인(approve, setApprovalForAll, Permit2)을 요청하며, 확정된 거래는 되돌릴 수 없습니다.
그곳에 입력한 모든 비밀번호를 바꾸고 2단계 인증을 켜세요. 지갑을 연결했거나 무언가에 서명했다면 승인을 취소하고 남은 자금을 새 지갑으로 옮기세요. 시드 문구는 절대 공유하지 마세요. 단계별 안내: 긴급 대응 가이드.
마지막 확인
For the registrable domain byrds.dev behind this subdomain, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
dns200.anycast.mens200.anycast.me위치는 IP 네트워크 기준입니다.
60677b3b741b9786cbd70f7a2cf12793848d2967d101987c726d04a5c98b1e46app.foundation.byrds.devfoundation.byrds.dev저장된 인증서 메타데이터입니다. 시간대 정보가 없는 인증서 날짜는 저장된 그대로 표시됩니다. 전송 구간 암호화가 사이트의 신뢰성을 입증하지는 않습니다.
Google PageSpeed Insights — 다음 도메인의 모바일 성능 감사: admin.foundation.byrds.dev · checked Sep 8, 2026
추정 시각은 관측 구간을 나타냅니다. 레지스트라의 조치나 사이트가 접속 불가 상태가 된 정확한 시점을 입증하지는 않습니다.
모니터와 출처 수집기가 보관한 날짜별 변경 기록입니다. 최신 관측이 먼저 표시되며, 출처 상태가 테이크다운을 입증하지는 않습니다.
알 수 없음→live_content
content_served
live_content→redirected
http_redirect
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
redirected→live_content
content_served
알 수 없음→redirected
http_redirect
알 수 없음→live_content
content_served
redirected→live_content
content_served
live_content→redirected
http_redirect
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
알 수 없음→live_content
content_served
4→5
3→4
2→3
1→2
0→1
접속 가능
각 레인은 도메인이 이 호스트에 연결된 이유 중 하나를 나타냅니다. 노드의 크기는 VirusTotal 탐지 건수를 나타내며, 점선으로 표시된 노드는 이미 오프라인 상태입니다. 전체 목록은 아래와 같습니다.
이 호스트와 동일한 파비콘 해시이거나 동일한 페이지 제목을 가진 경우.
동일한 수집기 레이블이 붙은 보고서입니다. 레이블이 같다고 해서 사칭이나 동일 소유가 입증되지는 않습니다. 일치하는 보고서 보기 →
동일한 등록 기관을 통해 등록되었습니다. 등록 기관은 서로 관련이 없는 수백만 명의 고객을 상대하기 때문에, 이는 두 항목 간의 연관성을 입증하기보다는 단순히 보고를 묶어놓은 것에 불과합니다.
브라우저와 크롤러가 받는 응답을 비교하고 Keitaro 트래픽 라우팅 여부를 확인합니다.
admin.foundation.byrds.dev
PD-20260908-455E40 Recipient: abuse@ovh.net 계정 자격 증명, 개인 정보 또는 결제 정보를 입력했거나 이 도메인에서 파일을 다운로드한 경우 즉시 조치를 취하세요. 다음은 사건을 신고하고 자신을 보호하는 데 도움이 되는 리소스입니다.
공식 사이버 범죄 연락처 또는 불만사항 초안 작성 →를 받으려면 국가를 선택하세요.
Template-based draft · optional AI wording assistance requires separate consent
공유한 정보에 해당하는 조치를 선택하세요. 이 보고서 사본을 본인의 기록과 함께 보관하세요.
의심스러운 사이트 사용을 중단하세요. 실제 서비스는 공식 앱이나 이미 신뢰하는 주소를 통해 접속하세요.
원본 이메일, 영수증, 메시지, 스크린샷을 안전한 곳에 보관하세요. 사실에 기반한 시간순 기록은 접수 기관이 경위를 파악하는 데 도움이 됩니다. IC3 evidence guidance ↗
admin.foundation.byrds.dev)비록 모든 세부 사항을 알지 못하더라도 — 어쨌든 신고를 하세요. 부분적인 정보라도 수사에 도움이 됩니다.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
이 보고서는 저장된 페이지 캡처, 등록 및 네트워크 기록, 스캐너 결과, PhishDestroy 신고 이력을 종합한 것입니다. 각 출처는 고유한 관측일을 유지합니다. 원본 결과를 확인하려면 출처 보고서를 여세요.
AI 지원 분석 작성 시각: . 이 분석은 작성 당시 확보된 증거를 설명하며, 이후 출처 확인 결과는 달라질 수 있습니다.
캡처는 당시 표시된 내용을 기록한 것입니다. 스캐너 결과는 검사 시점의 해당 제공업체 평가를 기록한 것입니다. 유효한 인증서나 탐지 0건 결과 모두 안전을 보장하지 않습니다.