元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
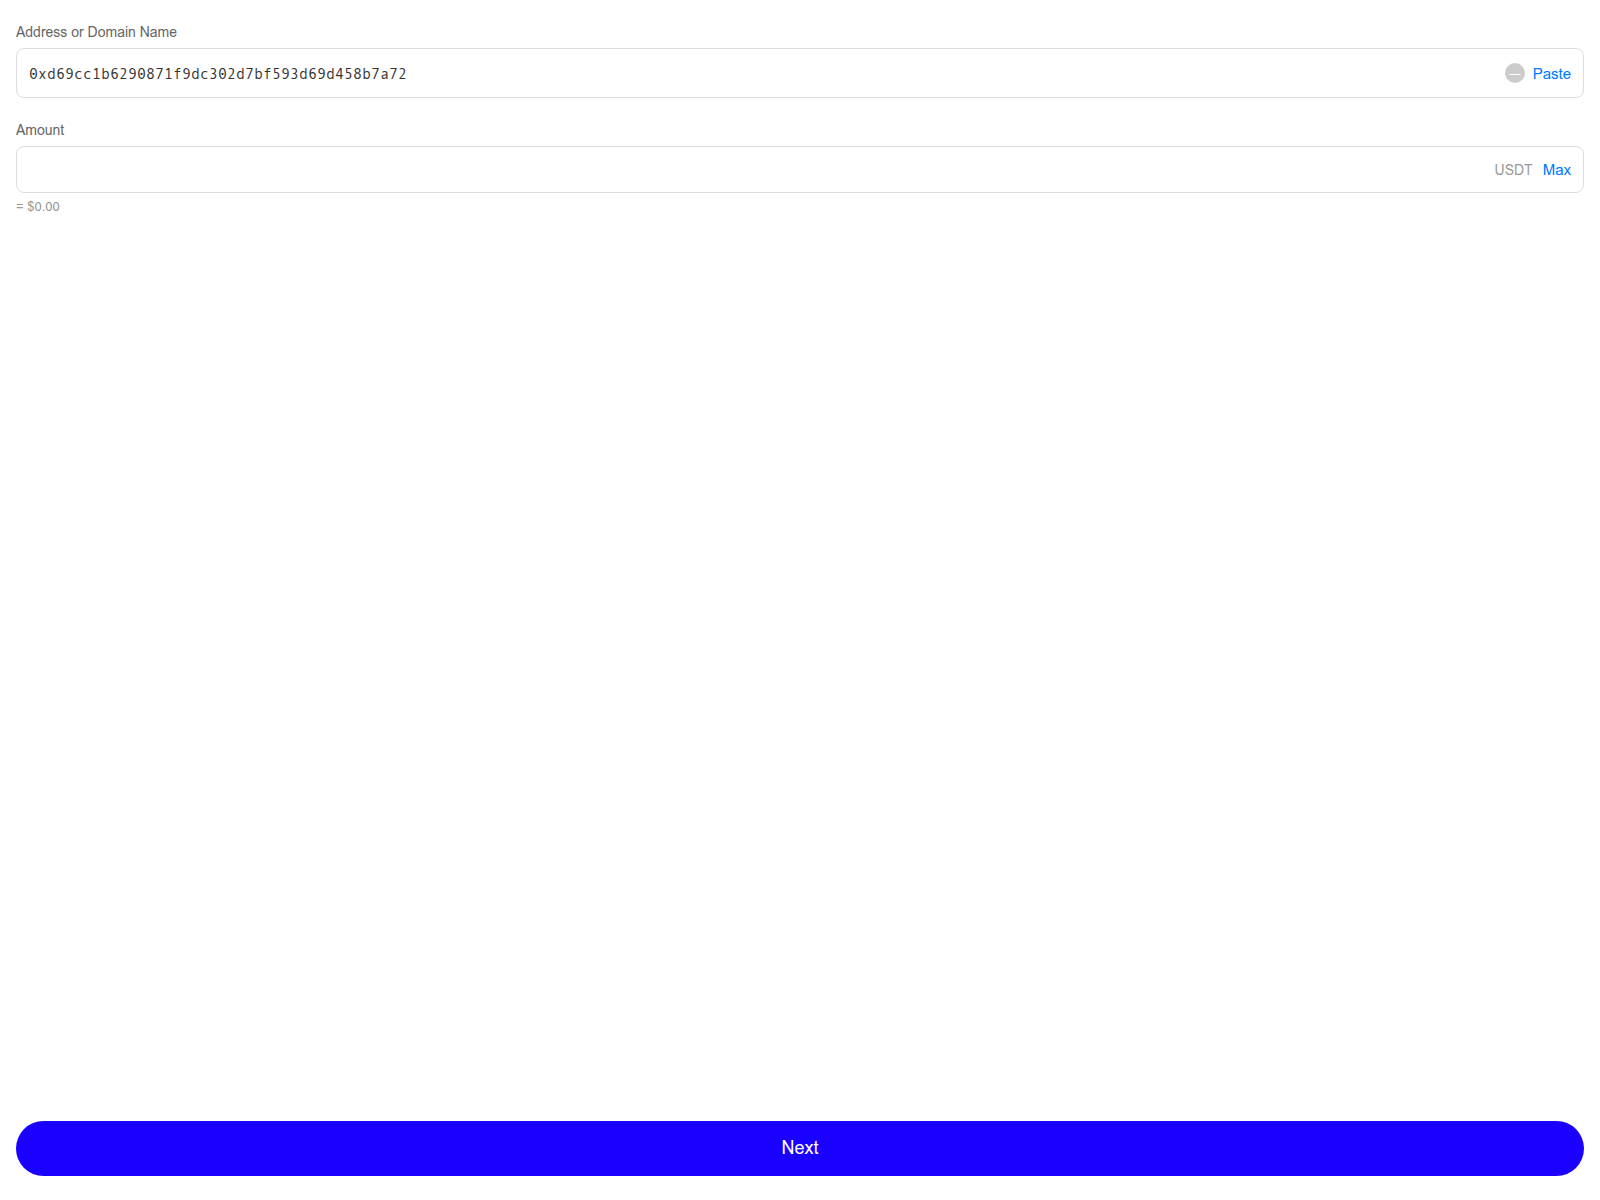
transfer-usdt.online is an impersonation phishing page built around Tether's USDT stablecoin. Its page title is simply "USDT", and the domain name promises a transfer service, which is aimed at people who want to send or receive stablecoins. PhishDestroy first flagged it on 2026-08-27. On 2026-10-19 the site was still online and serving live content, so it remains a current danger.
詐欺の手口
Pages like this borrow USDT's name to look like an official or convenient way to move funds. The visitor is then pushed to hand over control in one of a few ways: connecting a wallet and signing a transaction or token approval, typing in a seed phrase or private key to "verify" the transfer, or sending USDT to an address the page supplies. Whichever route is used, the result is the same. Stablecoins leave the victim's wallet and go to the operator, and on-chain transfers cannot be reversed.
証拠
On 2026-10-07, 12 of 92 VirusTotal engines flagged the domain. The vendors included alphaMountain.ai, BitDefender, Chong Lua Dao, CRDF, CyRadar, Forcepoint ThreatSeeker, Fortinet and G-Data. That is a minority of engines, but they come from several unrelated security vendors, including a Vietnamese anti-scam community and major commercial filters, so this is not one vendor's opinion. The domain also appears in four AlienVault OTX threat pulses, which shows other researchers are tracking it. It is listed on the PhishDestroy blocklist.
インフラ
The domain was registered through GoDaddy.com, LLC on 2026-06-14, about ten weeks before PhishDestroy detected it. That gap leaves room for a site to be prepared or to run quietly before it draws attention. It is hosted on GoDaddy's network in the United States, which blends it in with ordinary small-business websites. A free Let's Encrypt certificate gives it the browser padlock, but the padlock only means the connection is encrypted and says nothing about whether the site is honest.
What to do
If you connected a wallet here, review its token approvals with a revocation tool and cancel any you do not recognize, starting with USDT allowances. If you entered a seed phrase or private key, treat that wallet as compromised and move the remaining assets to a new wallet with a fresh phrase. If you sent USDT, record the transaction hash and report it to your exchange or wallet provider, and never pay anyone who promises to recover the funds for a fee. Defenders should block the domain at DNS and proxy level, watch for lookalike domains that combine "usdt" with transfer wording, and report the site to the registrar and hosting provider.
transfer-usdt.online is an impersonation phishing page posing as a USDT transfer service, targeting Tether holders moving stablecoins between wallets.
AIによる要約
Overview transfer-usdt.online is an impersonation phishing page built around Tether's USDT stablecoin. Its page title is simply "USDT", and the domain name promises a transfer service, which is aimed at people who want to send or receive stablecoins. PhishDestroy first flagged it on 2026-08-27. On 2026-10-19 the site was still online and serving live content, so it remains a current danger. How the scam works Pages like this borrow USDT's name to look like an official or convenient way to move funds. The visitor is then pushed to hand over control in one of a few ways: connecting a wallet and signing a transaction or token approval, typing in a seed phrase or private key to "verify" the transfer, or sending USDT to an address the page supplies. Whichever route is used, the result is the same. Stablecoins leave the victim's wallet and go to the operator, and on-chain transfers cannot be reversed. Evidence On 2026-10-07, 12 of 92 VirusTotal engines flagged the domain. The vendors included alphaMountain.ai, BitDefender, Chong Lua Dao, CRDF, CyRadar, Forcepoint ThreatSeeker, Fortinet and G-Data. That is a minority of engines, but they come from several unrelated security vendors, including a Vietnamese anti-scam community and major commercial filters, so this is not one vendor's opinion. The domain also appears in four AlienVault OTX threat pulses, which shows other researchers are tracking it. It is listed on the PhishDestroy blocklist. Infrastructure The domain was registered through GoDaddy.com, LLC on 2026-06-14, about ten weeks before PhishDestroy detected it. That gap leaves room for a site to be prepared or to run quietly before it draws attention. It is hosted on GoDaddy's network in the United States, which blends it in with ordinary small-business websites. A free Let's Encrypt certificate gives it the browser padlock, but the padlock only means the connection is encrypted and says nothing about whether the site is honest. What to do If you connected a wallet here, review its token approvals with a revocation tool and cancel any you do not recognize, starting with USDT allowances. If you entered a seed phrase or private key, treat that wallet as compromised and move the remaining assets to a new wallet with a fresh phrase. If you sent USDT, record the transaction hash and report it to your exchange or wallet provider, and never pay anyone who promises to recover the funds for a fee. Defenders should block the domain at DNS and proxy level, watch for lookalike domains that combine "usdt" with transfer wording, and report the site to the registrar and hosting provider. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a04113-9a25-70ea-bdf8-847f8d781016/ VirusTotal report: https://www.virustotal.com/gui/domain/transfer-usdt.online Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=transfer-usdt.online Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:51 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:51 UTClast content: 2026-11-22 11:51 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
JSDelivr is a free public CDN for open-source projects. It can serve web files directly from the npm registry and GitHub repositories without any configuration.

 GoDaddy


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT