記録されたソースの概要
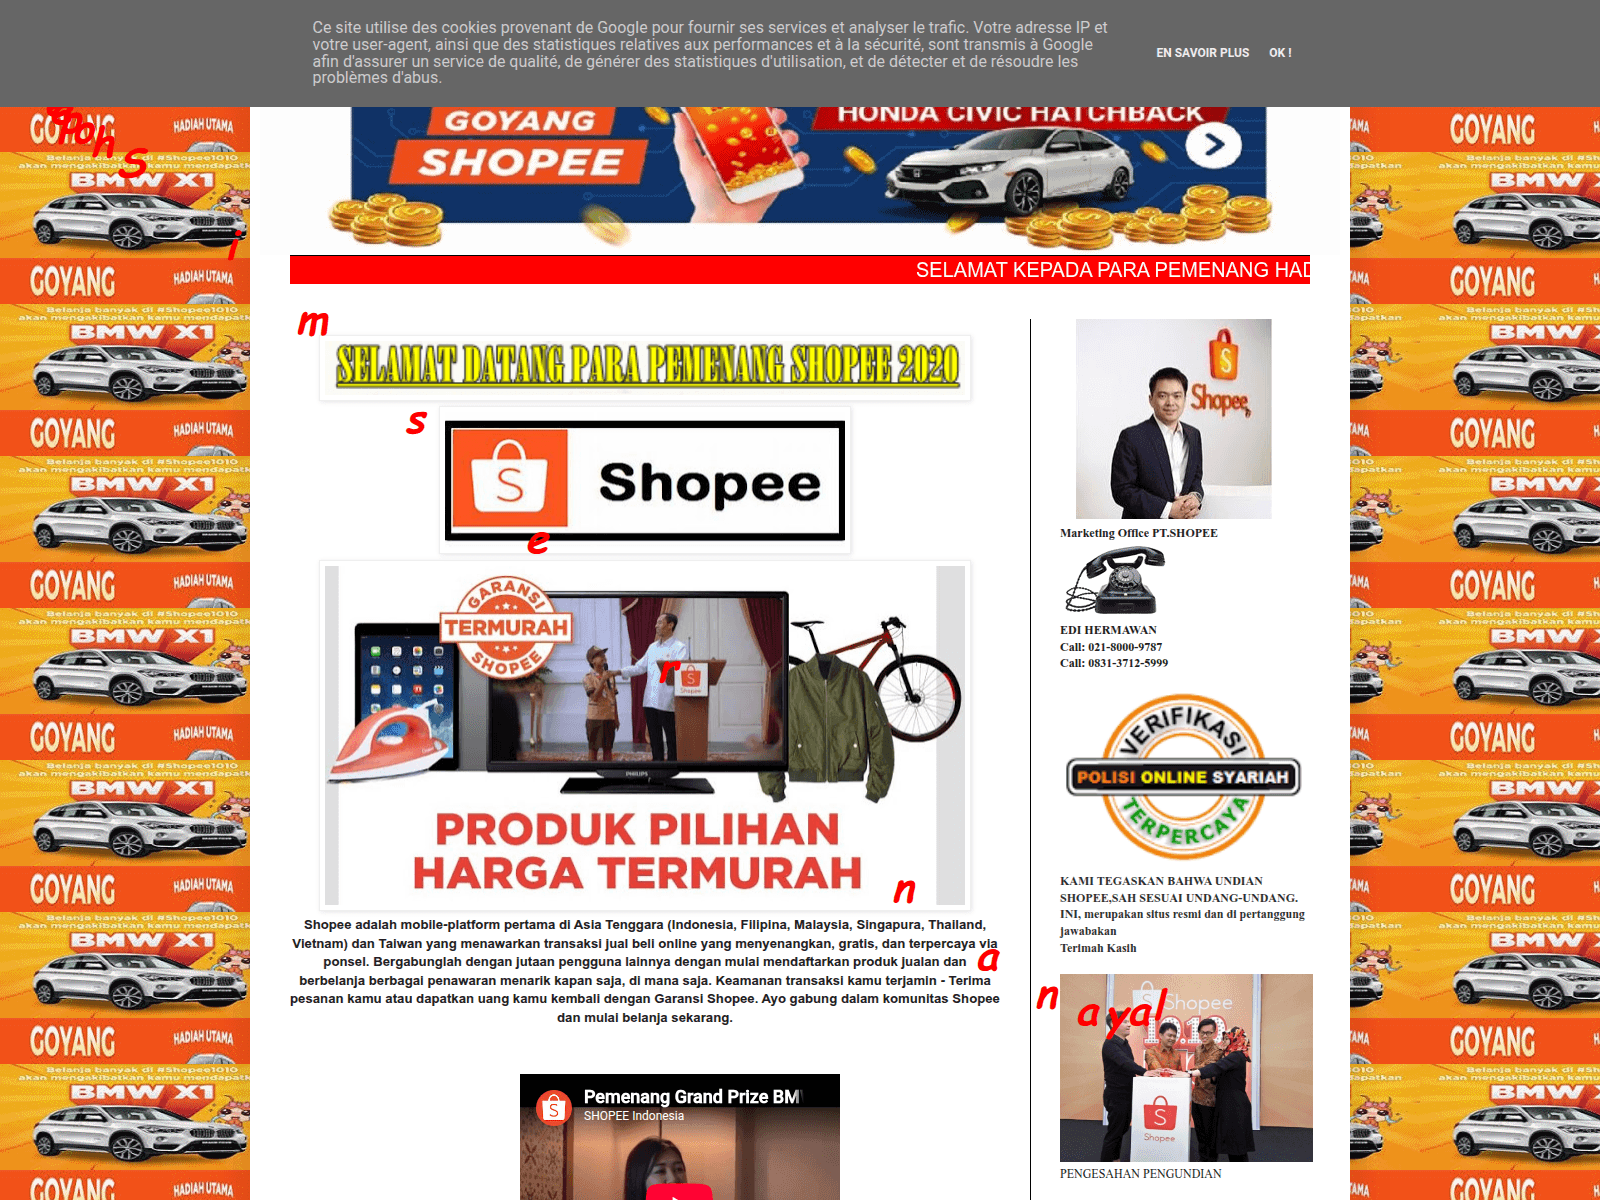
PhishDestroy first observed shopee3125.blogspot.com on Sep 27, 2026. Stored content metadata identifies ShopeePay as the apparent target. The captured page title is “Blog not found”. Current evidence score: 95/100 (critical).
Positive findings are stored from 3 sources: VirusTotal, Cloudflare Radar, and URLScan. VirusTotal recorded 18 detections among 92 engines: ESET, VIPRE, G-Data, Lionic, Sophos, CyRadar, Webroot, Emsisoft, Fortinet, Netcraft, SOCRadar, URLQuery, Kaspersky, Gridinsoft, MalwareURL, BitDefender, alphaMountain.ai, Forcepoint ThreatSeeker on Nov 7, 2026 at 21:02 UTC. Cloudflare Radar classified the hostname as malicious and assigned the categories phishing and security threats. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to Shopee and assigned phishing as its category on Nov 17, 2026 at 04:30 UTC.
HTTP 404 was recorded on Nov 21, 2026 at 23:14 UTC; content was unavailable. Latest classified outcome: inactive; cause http no content on Nov 21, 2026 at 10:16 UTC. At collection time, the hostname resolved to 173.194.73.132 on AS15169 (Google LLC). The recorded endpoint location is Mountain View, US. The stored server header is GSE. The evidence archive retains 8 visual captures from URLScan and Cloudflare Radar. TLS metadata lists WE2 as the certificate issuer.
The content indicators and 3 positive source findings support the current ShopeePay impersonation and phishing classification. The target field identifies ShopeePay.


 173.194.73.132


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT