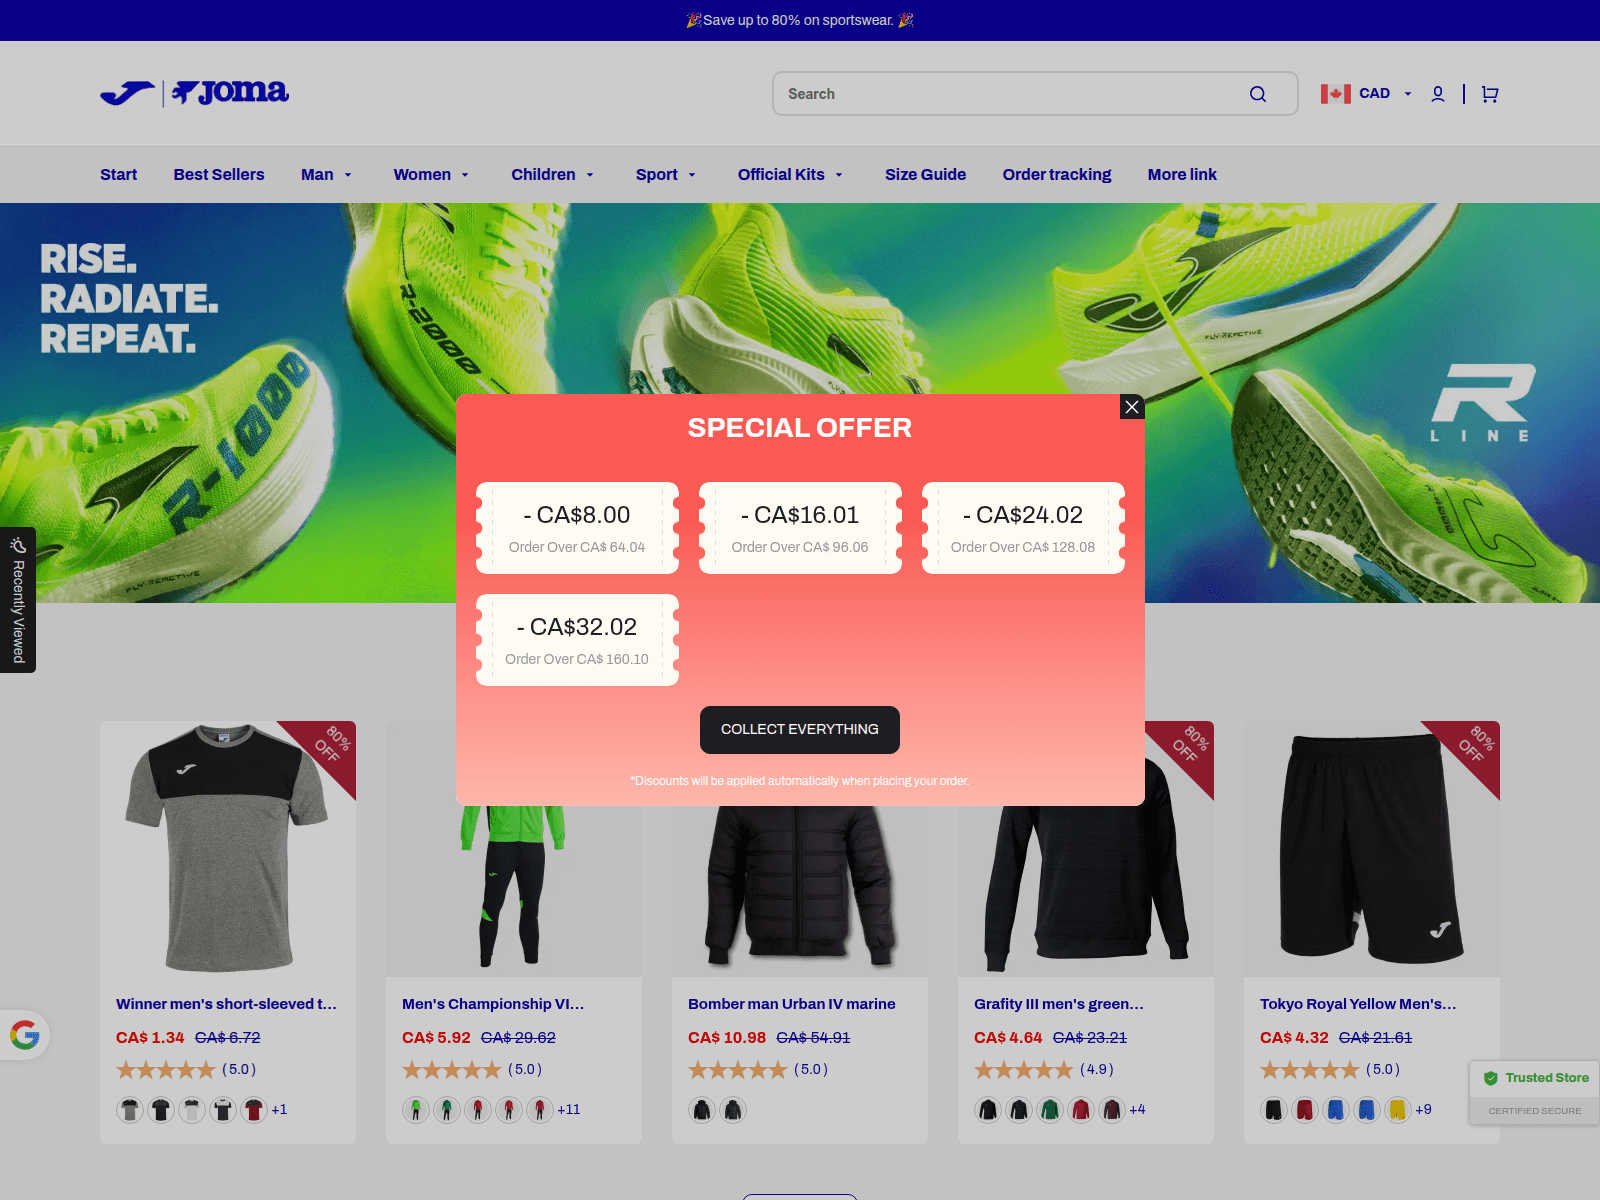
The savingsdeal.shop domain mimics a Joma sportswear store offering heavy discounts and coupon tickets, but functions as an untrusted retail clone. If you entered your payment card or personal details on this site, contact your bank immediately to secure your accounts.
URLScanによるキャプチャ · 2026-05-15 09:05 UTC · SHA-256 9c38b5c2…f12f2e9
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Joma sportswear store layout and coupon popup
The savingsdeal.shop webpage opens with a top banner stating "Save up to 80% on sportswear" and displays the Joma brand logo alongside standard navigation links such as "Start", "Best Sellers", "Man", and "Order tracking". Below the main banner showing athletic footwear, a large red promotional overlay titled "SPECIAL OFFER" appears, featuring coupon tickets with deductions like "- CA$8.00", "- CA$16.01", and "- CA$32.02" tied to minimum order thresholds. A dark button labeled "COLLECT EVERYTHING" sits at the bottom of the popup above fine print noting "*Discounts will be applied automatically when placing your order." The grid below showcases apparel items like "Winner men's short-sleeved t..." priced at CA$ 1.34 alongside star ratings and color options, while a badge in the corner reads "Trusted Store CERTIFIED SECURE".
Independent security vendor telemetry
The checkout and form elements interact with external services like translate.googleapis.com, and Spamhaus DBL lists it as phishing, VirusTotal showed 16 of 92 engines flagging it on 15 Nov 2026, and 1 AlienVault OTX community report references it. Security vendors including Kaspersky, ESET and BitDefender classify this setup as malicious. This consensus among independent scanners highlights that the site operates as a deceptive shopping clone rather than a legitimate retailer.
Shared hosting infrastructure and operator patterns
4 other domains on PhishDestroy's list share its IP address, including valuesdeal.shop, savemoredeal.shop and hot-sellingstores.shop. These neighboring addresses present similar discount shop layouts, which indicates a coordinated operator pattern deploying multiple look-alike storefronts from the same server infrastructure.
savingsdeal.shop copies a Joma sportswear shop with steep discount offers, flagged by Spamhaus DBL and 16 VirusTotal engines, so do not submit payment details.
AIによる要約
Joma sportswear store layout and coupon popup The savingsdeal.shop webpage opens with a top banner stating "Save up to 80% on sportswear" and displays the Joma brand logo alongside standard navigation links such as "Start", "Best Sellers", "Man", and "Order tracking". Below the main banner showing athletic footwear, a large red promotional overlay titled "SPECIAL OFFER" appears, featuring coupon tickets with deductions like "- CA$8.00", "- CA$16.01", and "- CA$32.02" tied to minimum order thresholds. A dark button labeled "COLLECT EVERYTHING" sits at the bottom of the popup above fine print noting "*Discounts will be applied automatically when placing your order." The grid below showcases apparel items like "Winner men's short-sleeved t..." priced at CA$ 1.34 alongside star ratings and color options, while a badge in the corner reads "Trusted Store CERTIFIED SECURE". Independent security vendor telemetry The checkout and form elements interact with external services like translate.googleapis.com, and Spamhaus DBL lists it as phishing, VirusTotal showed 16 of 92 engines flagging it on 15 Nov 2026, and 1 AlienVault OTX community report references it. Security vendors including Kaspersky, ESET and BitDefender classify this setup as malicious. This consensus among independent scanners highlights that the site operates as a deceptive shopping clone rather than a legitimate retailer. Shared hosting infrastructure and operator patterns 4 other domains on PhishDestroy's list share its IP address, including valuesdeal.shop, savemoredeal.shop and hot-sellingstores.shop. These neighboring addresses present similar discount shop layouts, which indicates a coordinated operator pattern deploying multiple look-alike storefronts from the same server infrastructure.
The Tranco rank (how much traffic) is rather low The server of the site has several low reviewed other websites The site does not allow us to analyze its content This website was reported by IPQS for phishing. This website has been classified as suspicious by IPQS
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:14 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:14 UTClast content: 2026-11-22 11:14 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 47.251.94.120


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT