元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
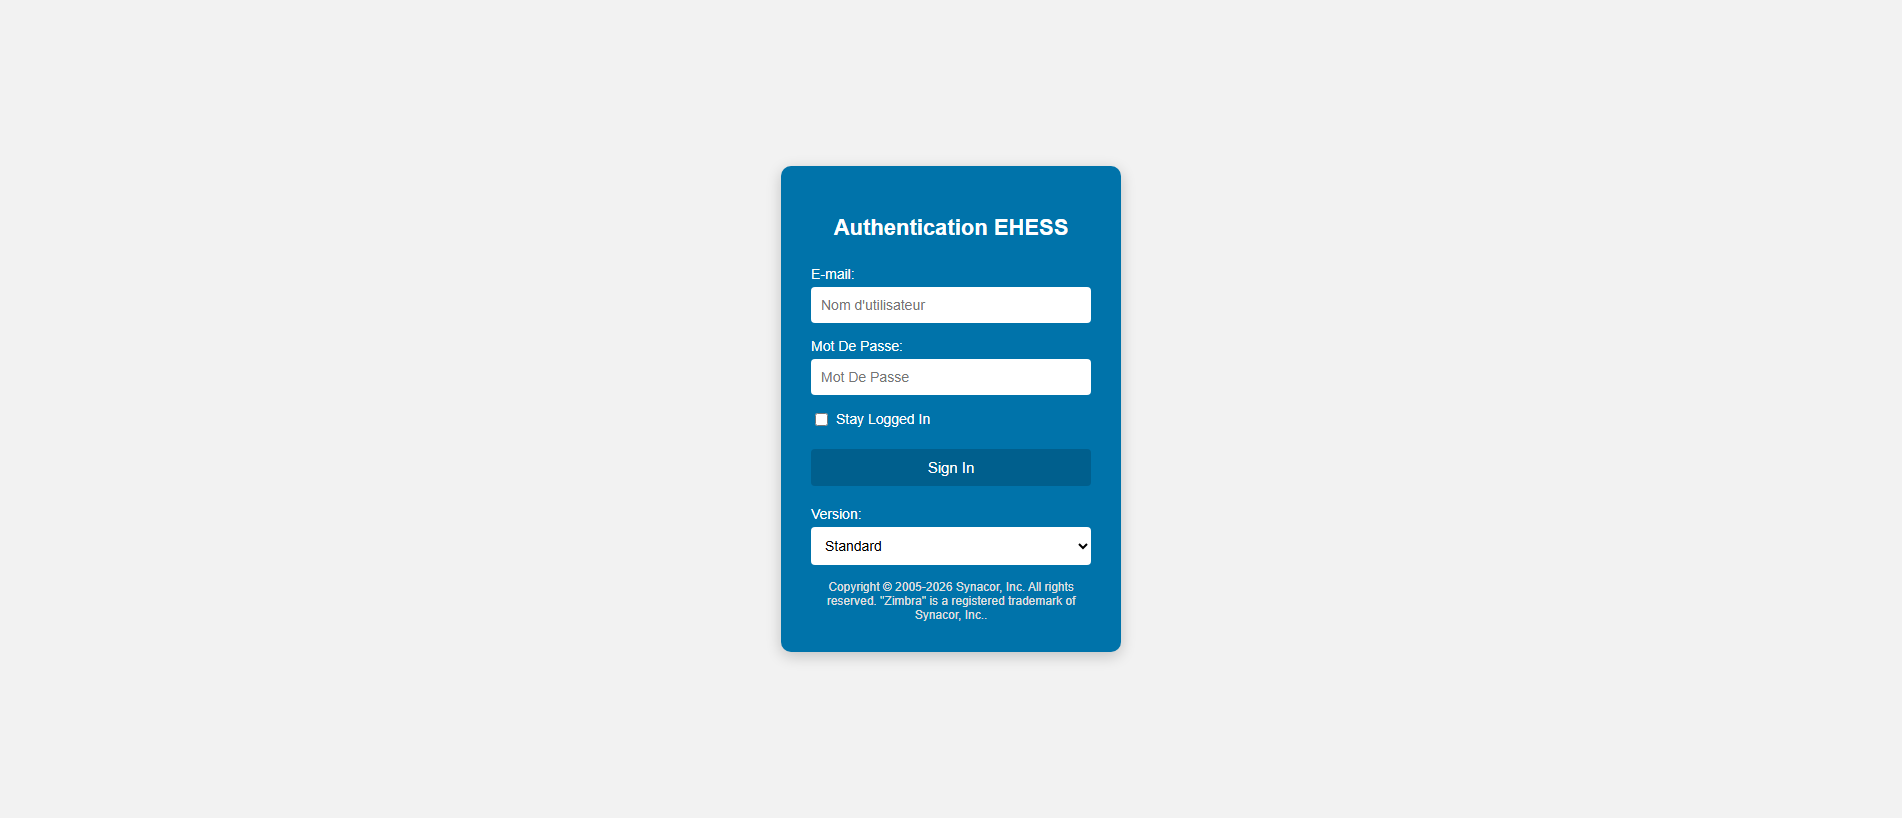
As observed on 2026-10-26, the captured screenshot shows a blue sign-in card headed Authentication EHESS with an E-mail field, a Mot De Passe password field, a Stay Logged In checkbox, a Sign In button, a Version dropdown set to Standard, and a footer naming Zimbra as a registered trademark of Synacor, Inc. PhishDestroy listed the domain after its automated assessment classified it as a credential phishing page, first seen on 2026-10-26.
詐欺の手口
The page imitates a Zimbra web mail sign-in so that a visitor arriving from a lure types a mailbox address and password into attacker-controlled fields. Because the form mirrors a familiar login, submitted credentials can be captured and replayed against the genuine mailbox, enabling account takeover and follow-on email abuse.
証拠
The captured screenshot shows French-labelled login fields asking for E-mail and Mot De Passe beneath an Authentication EHESS heading, with a Zimbra trademark footer. urlscan returned a malicious verdict with an ML score of 99 and an overall phishing score of 100 on 2026-10-26, and its capture records a 307 redirect funnel from the plain HTTP form to the HTTPS form of the same host, with one tracker request observed. VirusTotal flagged the domain as malicious, while Spamhaus recorded no listing, Google Safe Browsing was not flagged, and OTX recorded 0 pulses, all checked on 2026-10-26. PhishFeed and PhishDestroy's internal blocklist flagged it on 2026-10-26, and one of twelve tested DNS resolvers, CloudFlare Family, blocked it.
インフラ
The page was served through Vercel infrastructure with the server header recording Vercel, and the TLS certificate is a wildcard issued for the hosting platform rather than for the displayed brand. Notable weaknesses: Content-Security-Policy, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy and COOP/COEP/CORP are all absent while strict-transport-security carries a long max-age; DNSSEC unsigned; no email authentication with zero SPF lookups and no DKIM or DMARC recorded; CAA records present. Transport security used TLS 1.3, AES-128-GCM, forward secrecy and ALPN h2 as observed on 2026-10-26.
What to do
Anyone who entered credentials on rosaehessfrzimbra.vercel.app should immediately change the password on the genuine Zimbra mailbox and enable two-factor authentication. Review recent mail activity and sign-in history for unauthorized access, and treat the entered password as exposed wherever it was reused. Security teams should block rosaehessfrzimbra.vercel.app at proxy and DNS layers and hunt for similar lookalike sign-in pages.
PhishDestroy assesses rosaehessfrzimbra.vercel.app as a Zimbra credential phishing page captured on 2026-10-26.
AIによる要約
Overview As observed on 2026-10-26, the captured screenshot shows a blue sign-in card headed Authentication EHESS with an E-mail field, a Mot De Passe password field, a Stay Logged In checkbox, a Sign In button, a Version dropdown set to Standard, and a footer naming Zimbra as a registered trademark of Synacor, Inc. PhishDestroy listed the domain after its automated assessment classified it as a credential phishing page, first seen on 2026-10-26. How the scam works The page imitates a Zimbra web mail sign-in so that a visitor arriving from a lure types a mailbox address and password into attacker-controlled fields. Because the form mirrors a familiar login, submitted credentials can be captured and replayed against the genuine mailbox, enabling account takeover and follow-on email abuse. Evidence The captured screenshot shows French-labelled login fields asking for E-mail and Mot De Passe beneath an Authentication EHESS heading, with a Zimbra trademark footer. urlscan returned a malicious verdict with an ML score of 99 and an overall phishing score of 100 on 2026-10-26, and its capture records a 307 redirect funnel from the plain HTTP form to the HTTPS form of the same host, with one tracker request observed. VirusTotal flagged the domain as malicious, while Spamhaus recorded no listing, Google Safe Browsing was not flagged, and OTX recorded 0 pulses, all checked on 2026-10-26. PhishFeed and PhishDestroy's internal blocklist flagged it on 2026-10-26, and one of twelve tested DNS resolvers, CloudFlare Family, blocked it. Infrastructure The page was served through Vercel infrastructure with the server header recording Vercel, and the TLS certificate is a wildcard issued for the hosting platform rather than for the displayed brand. Notable weaknesses: Content-Security-Policy, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy and COOP/COEP/CORP are all absent while strict-transport-security carries a long max-age; DNSSEC unsigned; no email authentication with zero SPF lookups and no DKIM or DMARC recorded; CAA records present. Transport security used TLS 1.3, AES-128-GCM, forward secrecy and ALPN h2 as observed on 2026-10-26. What to do Anyone who entered credentials on rosaehessfrzimbra.vercel.app should immediately change the password on the genuine Zimbra mailbox and enable two-factor authentication. Review recent mail activity and sign-in history for unauthorized access, and treat the entered password as exposed wherever it was reused. Security teams should block rosaehessfrzimbra.vercel.app at proxy and DNS layers and hunt for similar lookalike sign-in pages. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a1780a-4769-75db-88b6-094032f6ea02/ Stored capture screenshot: https://i.ibb.co/5x2g6H6F/91a313f4a73c.png URLScan screenshot (2026-10-25T00:15:47Z): https://screenshots.phishdestroy.io/us/01a17069-c00a-72df-97f2-d902023ddfad.png URLScan capture report: https://urlscan.io/result/01a17069-c00a-72df-97f2-d902023ddfad/ URLScan screenshot (2026-10-26T01:04:14Z): https://screenshots.phishdestroy.io/us/01a175bc-741f-71bb-b644-387be4486d7a.png URLScan capture report: https://urlscan.io/result/01a175bc-741f-71bb-b644-387be4486d7a/ URLScan screenshot (2026-10-26T04:49:28Z): https://screenshots.phishdestroy.io/us/01a1768a-ac16-76df-92f4-2414a1284c59.png URLScan capture report: https://urlscan.io/result/01a1768a-ac16-76df-92f4-2414a1284c59/ URLScan screenshot (2026-10-26T07:40:55Z): https://screenshots.phishdestroy.io/us/01a17726-4208-71bc-af67-5d9d4a9c32f6.png URLScan capture report: https://urlscan.io/result/01a17726-4208-71bc-af67-5d9d4a9c32f6/ URLScan screenshot (2026-10-26T11:04:05Z): https://screenshots.phishdestroy.io/us/01a177e1-80c5-774d-936b-3b63c34c6559.png URLScan capture report: https://urlscan.io/result/01a177e1-80c5-774d-936b-3b63c34c6559/ URLScan screenshot (2026-10-26T11:46:32Z): https://screenshots.phishdestroy.io/us/01a17808-5c00-733a-825a-f02c03fd8071.png URLScan capture report: https://urlscan.io/result/01a17808-5c00-733a-825a-f02c03fd8071/ VirusTotal report: https://www.virustotal.com/gui/domain/rosaehessfrzimbra.vercel.app Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=rosaehessfrzimbra.vercel.app Archived copy: https://web.archive.org/web/20261026113936/https://rosaehessfrzimbra.vercel.app/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
出典Vercelmechanism: Deployment Disabledsource: Current Http Probe
エビデンスレイヤーAvailability: Provider blockedContent: Provider blockedDNS: Stale
最新のHTTP観測結果プロバイダーブロックが確認されたVercel Deployment DisabledVercelDeployment Disabled95%プロバイダーの認証済みマーク2026-11-21 02:00 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-10-30 12:05 UTClast content: 2026-10-30 12:05 UTCcurrent episode first observed: 2026-10-30 23:53 UTCobserved RIP window: 2026-10-30 12:05 UTC → 2026-10-30 23:53 UTC · 11.80hmidpoint estimate ≈ 2026-10-30 17:59 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 64.29.17.131


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT