元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
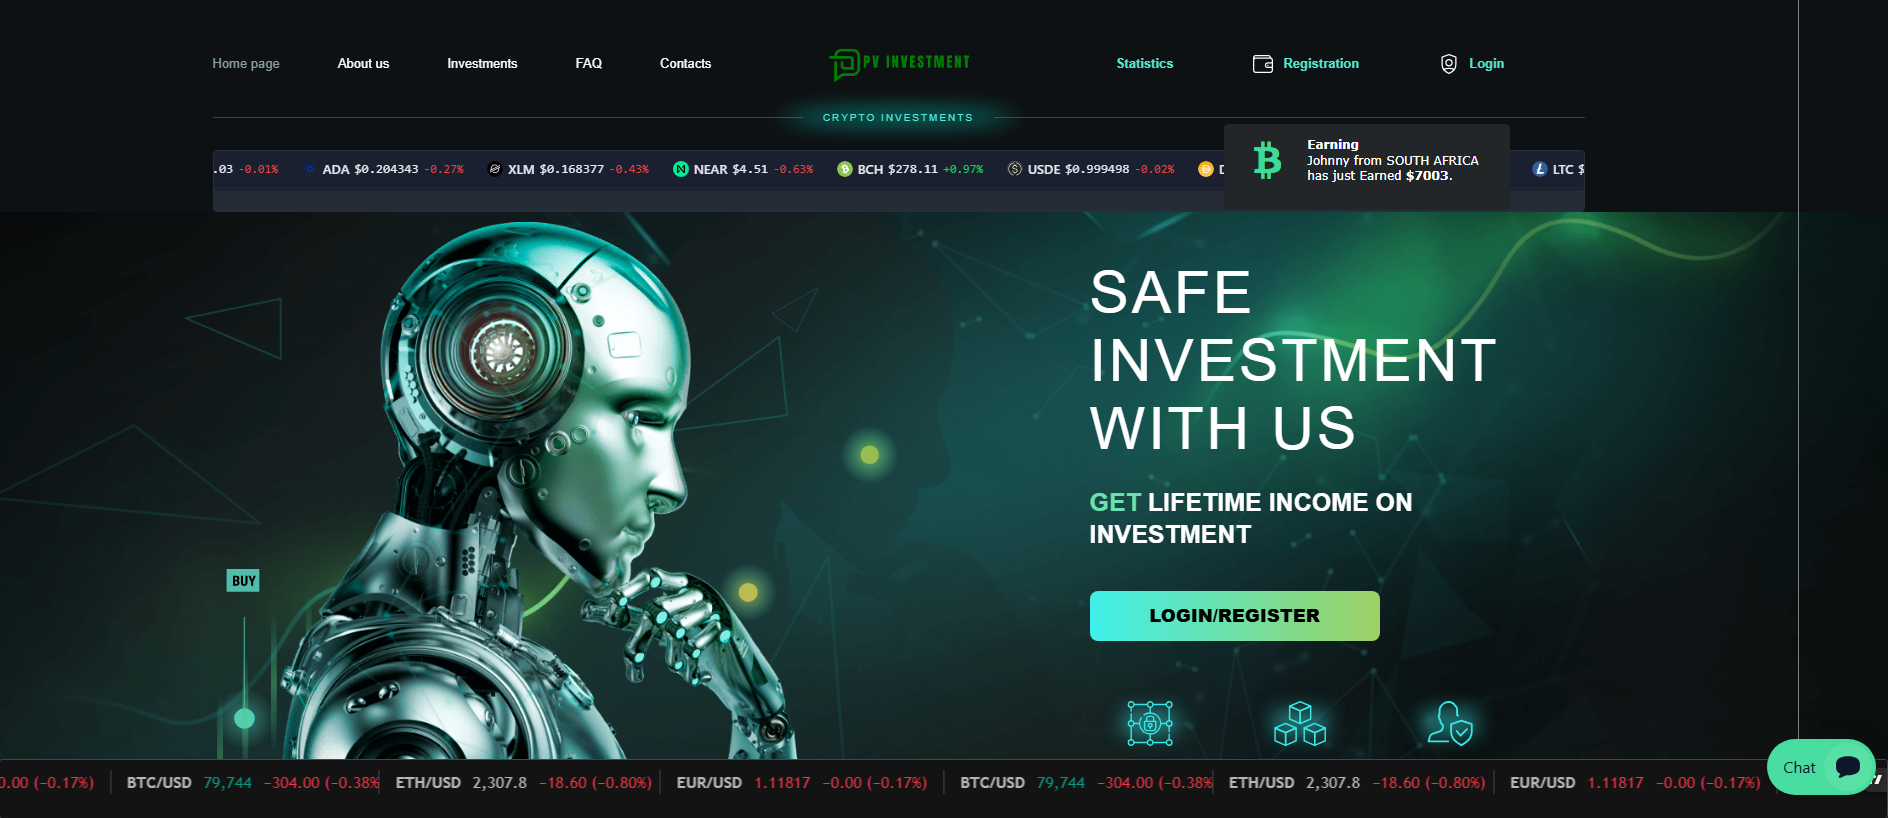
The captured screenshot shows a dark themed crypto investment landing page branded PV INVESTMENT, with the headline SAFE INVESTMENT WITH US, the offer GET LIFETIME INCOME ON INVESTMENT and a LOGIN/REGISTER button beside a scrolling crypto price ticker. The page title read Pvf Invest – Safe investment with Pvf Invest as observed on 2026-10-26. PhishDestroy listed the domain after malicious verdicts from urlscan and VirusTotal, first seen by PhishDestroy on 2026-10-26.
詐欺の手口
The page presented guaranteed lifetime income from crypto trading through a registration and login flow, a common investment scam pattern that lures visitors into opening accounts and depositing funds. The promised automated trading robot and passive returns act as the bait, while deposits are requested before any payout. In this category, funds sent are considered at risk of loss.
証拠
Observed on 2026-10-26, the captured screenshot shows the lifetime income offer, the LOGIN/REGISTER button, automated trading claims and price tickers. urlscan marked the page malicious with an ML score of 98 and an overall score of 100, categorised as phishing and labelled crypto scam on 2026-10-26, after a 307 redirect upgraded requests to HTTPS. VirusTotal flagged the domain as malicious, with Netcraft labelling it malicious and Fortinet labelling it spam. Google Safe Browsing did not flag it on 2026-10-26, external blocklists recorded 0 entries while PhishDestroy's internal blocklist matched on 2026-10-26 and AlienVault OTX held 3 pulses on 2026-10-26; site inspection recorded 5 distinct script SHA256 hashes beginning f554d2f09272 for campaign pivoting, with jQuery, GSAP, CreateJS, Adobe Animate, Smartsupp chat, Google Translate and Microsoft Clarity observed as trackers.
インフラ
Notable weaknesses: missing Content-Security-Policy and HSTS, unsigned DNSSEC, no COOP, COEP or CORP; TLS 1.3 with forward secrecy and ALPN h2, X-Frame-Options, X-Content-Type-Options, Referrer-Policy and Permissions-Policy present; SPF and DKIM configured; CAA present. The domain was registered through Gransy, s.r.o. on 2026-10-23, with recorded hosting at OVH.
What to do
If you submitted credentials or funds through primevalleyassetmanagement.com, stop interacting with it, change any password reused on a genuine service and enable 2FA on that account, and preserve screenshots, emails and transaction records before reporting to your bank and local authorities. Defenders should block the exact domain primevalleyassetmanagement.com, hunt on the recorded script hashes, and watch for the same campaign across newly registered domains.
PhishDestroy assesses primevalleyassetmanagement.com as a fraudulent crypto investment scheme promising lifetime income.
AIによる要約
Overview The captured screenshot shows a dark themed crypto investment landing page branded PV INVESTMENT, with the headline SAFE INVESTMENT WITH US, the offer GET LIFETIME INCOME ON INVESTMENT and a LOGIN/REGISTER button beside a scrolling crypto price ticker. The page title read Pvf Invest – Safe investment with Pvf Invest as observed on 2026-10-26. PhishDestroy listed the domain after malicious verdicts from urlscan and VirusTotal, first seen by PhishDestroy on 2026-10-26. How the scam works The page presented guaranteed lifetime income from crypto trading through a registration and login flow, a common investment scam pattern that lures visitors into opening accounts and depositing funds. The promised automated trading robot and passive returns act as the bait, while deposits are requested before any payout. In this category, funds sent are considered at risk of loss. Evidence Observed on 2026-10-26, the captured screenshot shows the lifetime income offer, the LOGIN/REGISTER button, automated trading claims and price tickers. urlscan marked the page malicious with an ML score of 98 and an overall score of 100, categorised as phishing and labelled crypto scam on 2026-10-26, after a 307 redirect upgraded requests to HTTPS. VirusTotal flagged the domain as malicious, with Netcraft labelling it malicious and Fortinet labelling it spam. Google Safe Browsing did not flag it on 2026-10-26, external blocklists recorded 0 entries while PhishDestroy's internal blocklist matched on 2026-10-26 and AlienVault OTX held 3 pulses on 2026-10-26; site inspection recorded 5 distinct script SHA256 hashes beginning f554d2f09272 for campaign pivoting, with jQuery, GSAP, CreateJS, Adobe Animate, Smartsupp chat, Google Translate and Microsoft Clarity observed as trackers. Infrastructure Notable weaknesses: missing Content-Security-Policy and HSTS, unsigned DNSSEC, no COOP, COEP or CORP; TLS 1.3 with forward secrecy and ALPN h2, X-Frame-Options, X-Content-Type-Options, Referrer-Policy and Permissions-Policy present; SPF and DKIM configured; CAA present. The domain was registered through Gransy, s.r.o. on 2026-10-23, with recorded hosting at OVH. What to do If you submitted credentials or funds through primevalleyassetmanagement.com, stop interacting with it, change any password reused on a genuine service and enable 2FA on that account, and preserve screenshots, emails and transaction records before reporting to your bank and local authorities. Defenders should block the exact domain primevalleyassetmanagement.com, hunt on the recorded script hashes, and watch for the same campaign across newly registered domains. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a17911-cbb2-7152-8aa6-3f2f991b80e5/ Cloudflare Radar report: https://radar.cloudflare.com/scan/09a0c2cc-7165-43d8-b1b3-35e1fa53b42b URLQuery report: https://urlquery.net/report/c8b77ee9-755d-4ebb-a53c-ab34ed005bd2 Stored capture screenshot: https://i.ibb.co/Xx2z2kcN/df8792378c9d.png Cloudflare Radar screenshot (2026-10-26T16:30:42Z): https://screenshots.phishdestroy.io/cf/09a0c2cc-7165-43d8-b1b3-35e1fa53b42b.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/c8b77ee9-755d-4ebb-a53c-ab34ed005bd2.png URLScan screenshot (2026-10-26T01:20:01Z): https://screenshots.phishdestroy.io/us/01a175ca-dd38-702b-86cb-9a6807f02840.png URLScan capture report: https://urlscan.io/result/01a175ca-dd38-702b-86cb-9a6807f02840/ VirusTotal report: https://www.virustotal.com/gui/domain/primevalleyassetmanagement.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=primevalleyassetmanagement.com Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
No sri: https://translate.google.com/translate_a/element.js, https://s3.tradingview.com/external-embedding/embed-widget-market-overview.js, https://s3.tradingview.com/external-embedding/embed-widget-forex-cross-rates.js, https://s3.tradingview.com/external-embedding/embed-widget-ticker-tape.js, https://code.createjs.com/createjs-2015.11.26.min.js; Third party scripts: 5
出典mechanism: Access Restrictionsource: Current Http Probe
エビデンスレイヤーAvailability: Reachable but protectedDNS: Resolved
最新のHTTP観測結果アクセス可能だが保護されているHTTP access restrictedAccess Restriction50%2026-11-22 11:20 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:20 UTClast content: 2026-11-01 23:50 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 5.135.193.192


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT