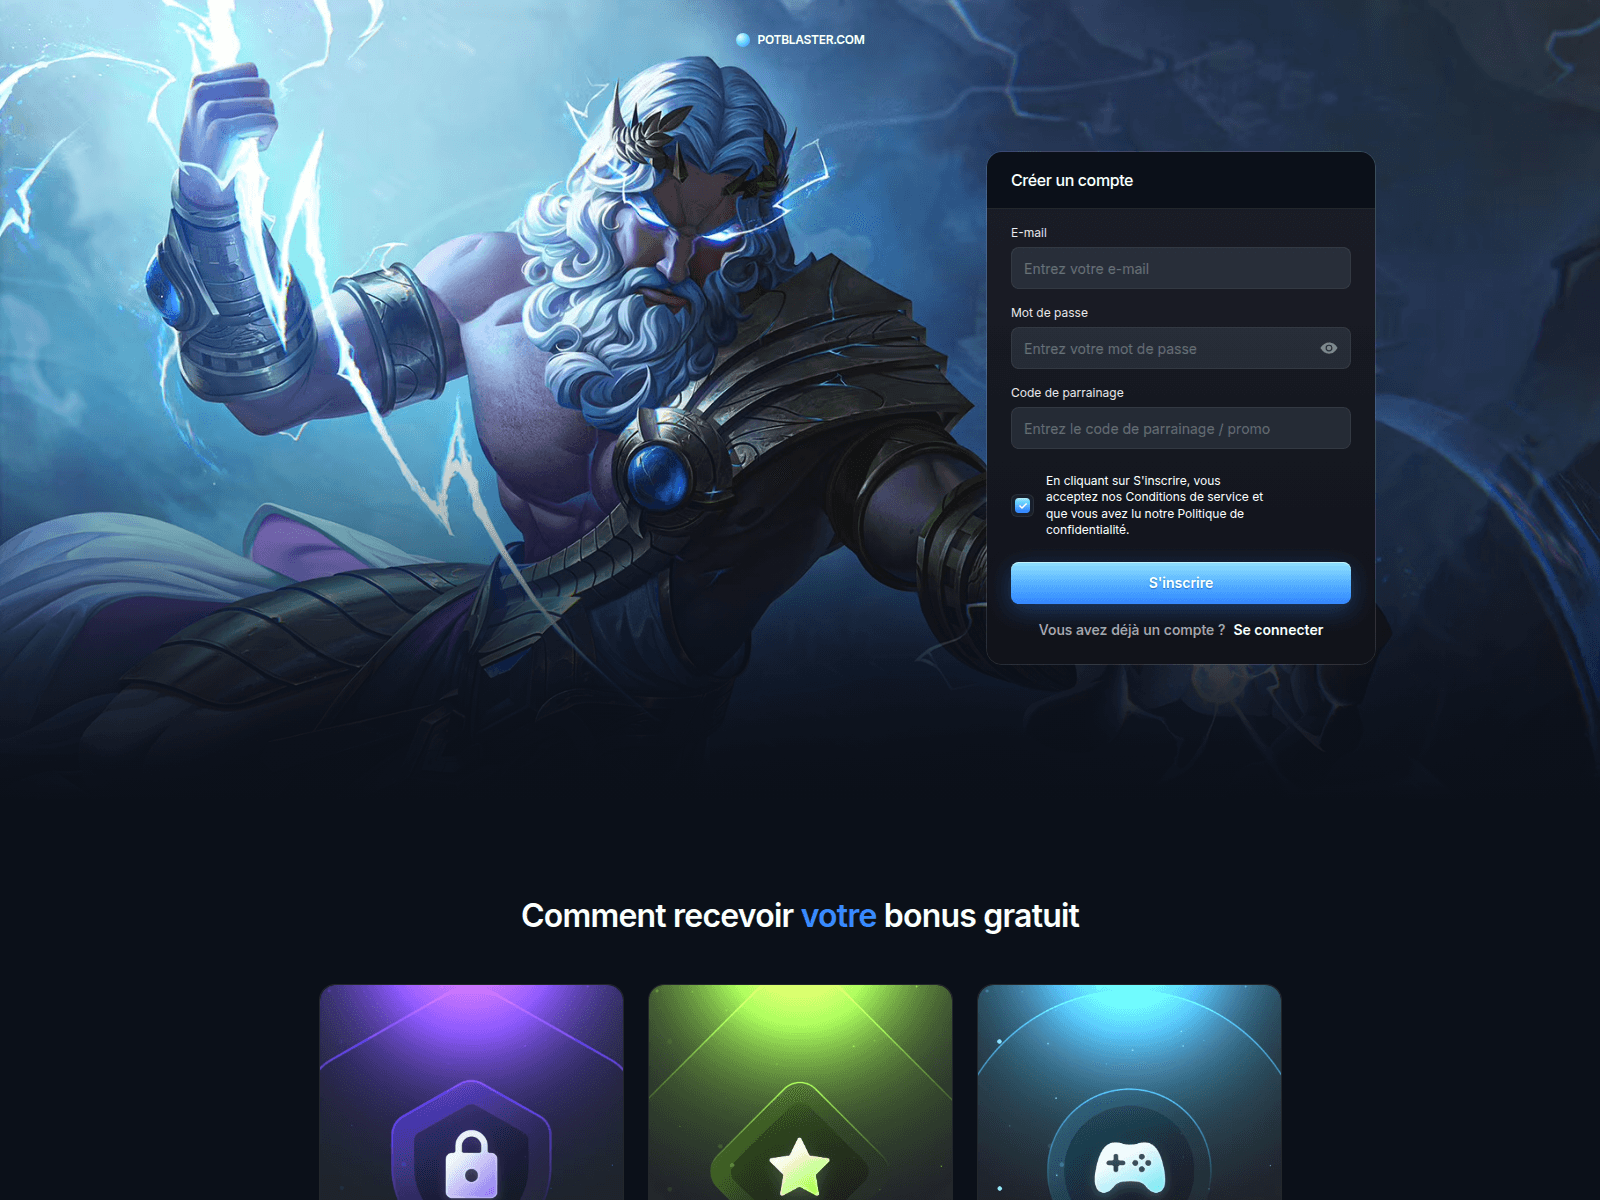
On 2026-11-15, potblaster.com displayed a POTBLASTER.COM-branded account creation page featuring a dark-themed layout with fantasy artwork depicting a figure wielding lightning. The interface provides input fields for an email address, password, and optional referral or promo code, alongside a terms acceptance checkbox and a registration button labeled S'inscrire. Below the main form, text prompts users who already have an account to log in, and three graphical cards appear above a heading discussing how to receive a free bonus.
URLScanによるキャプチャ · 2026-11-15 16:58 UTC · SHA-256 94b987e8…55dea13
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
On 2026-11-15, potblaster.com displayed a POTBLASTER.COM-branded account creation page featuring a dark-themed layout with fantasy artwork depicting a figure wielding lightning. The interface provides input fields for an email address, password, and optional referral or promo code, alongside a terms acceptance checkbox and a registration button labeled S'inscrire. Below the main form, text prompts users who already have an account to log in, and three graphical cards appear above a heading discussing how to receive a free bonus.
The stored VirusTotal domain result reports 1 detections out of 92 engines. Gridinsoft reported "phishing".
potblaster.com: Recorded page content and analysis
AIによる説明
PhishDestroy analyzes potblaster.com, presenting an overview of its visible page content, features, and security context.
AIによる要約
On 2026-11-15, potblaster.com displayed a POTBLASTER.COM-branded account creation page featuring a dark-themed layout with fantasy artwork depicting a figure wielding lightning. The interface provides input fields for an email address, password, and optional referral or promo code, alongside a terms acceptance checkbox and a registration button labeled S'inscrire. Below the main form, text prompts users who already have an account to log in, and three graphical cards appear above a heading discussing how to receive a free bonus. The stored VirusTotal domain result reports 1 detections out of 92 engines. Gridinsoft reported "phishing".
最新のHTTP観測結果RedirectingHTTP redirect observed80%2026-11-22 11:10 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:10 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 Dynadot
 188.114.96.3


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT