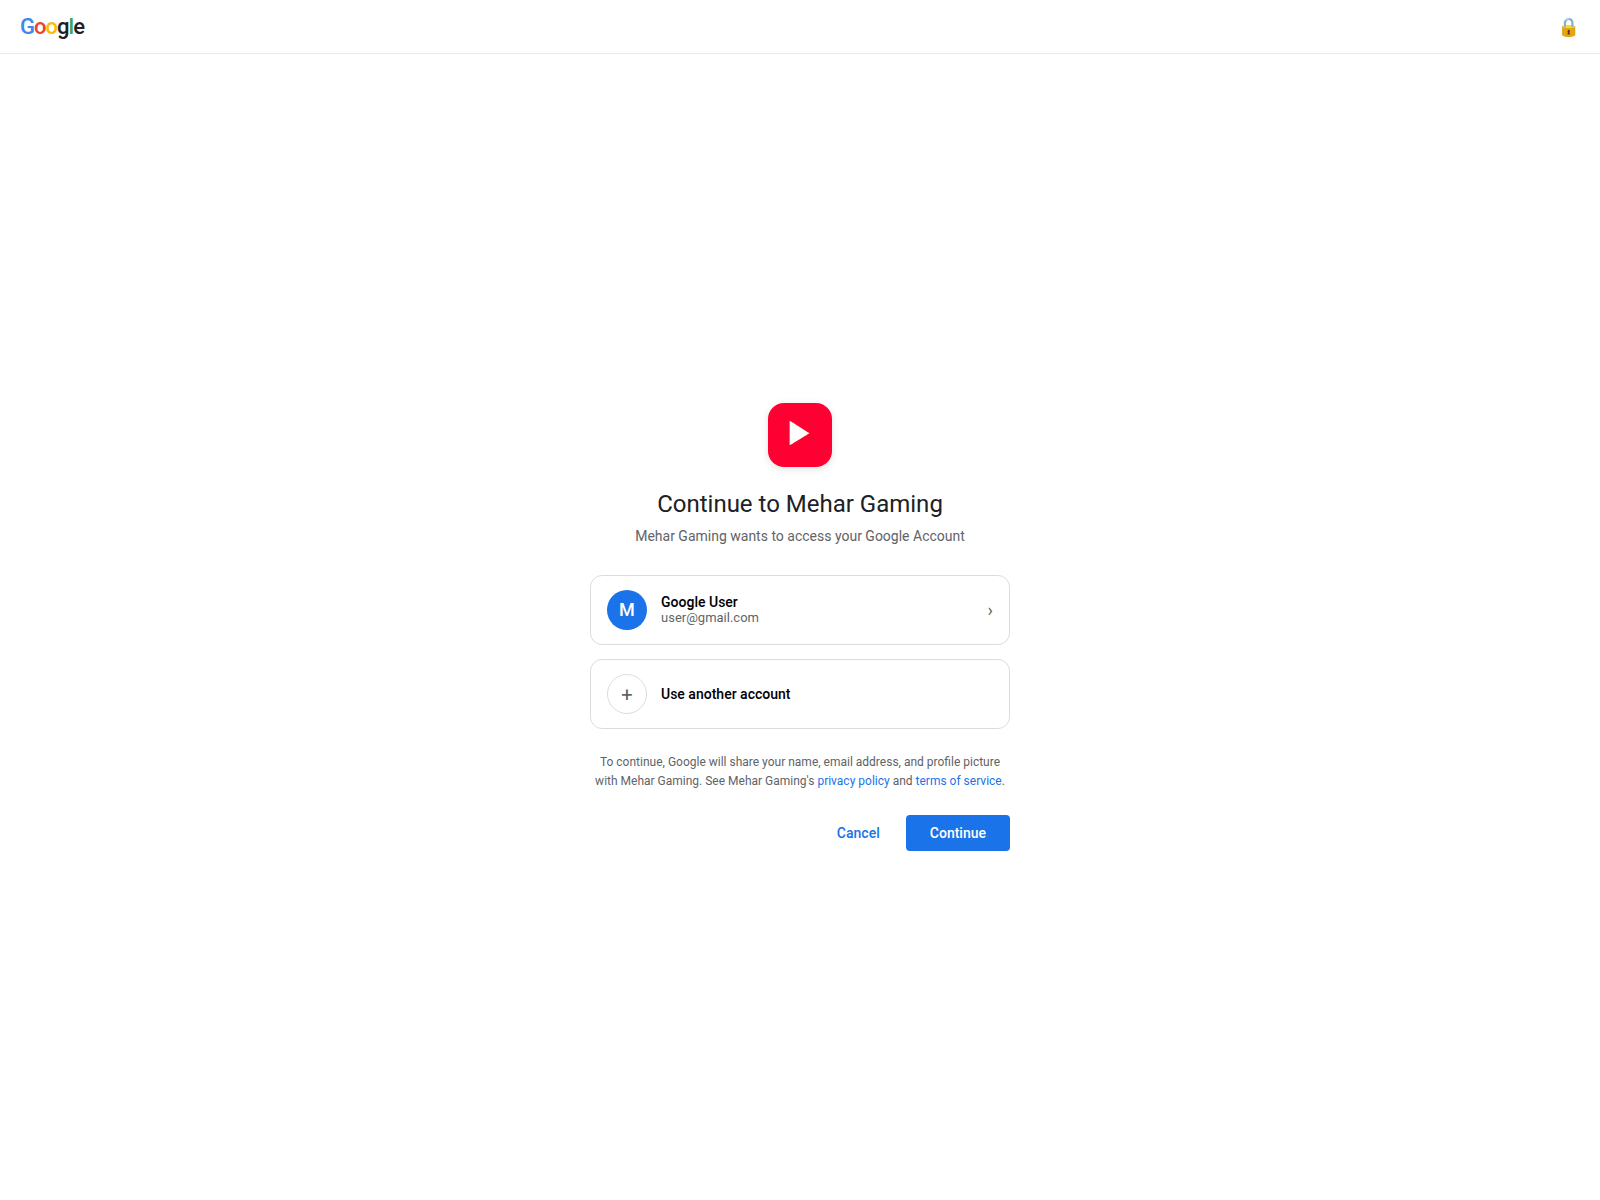
The page at meharislivegamingyoutube.github.io mimics a genuine Google OAuth consent prompt to trick visitors into linking an unauthorized application called Mehar Gaming to their Google account. If you already submitted credentials or approved this access, immediately revoke the app's permissions in your Google account settings and change your password.
URLScanによるキャプチャ · 2026-11-18 05:28 UTC · SHA-256 da3c9507…22bd6c6
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Page layout and OAuth deception
The page displays a clean, minimalist layout modelled closely after genuine Google account authentication screens. At the top left sits the standard Google logo, while the central section features a prominent red YouTube-style play icon above the bold heading "Continue to Mehar Gaming". Beneath this, explanatory text states that "Mehar Gaming wants to access your Google Account", accompanied by a mock account selector box displaying "Google User" and a placeholder email address. A secondary button allows visitors to "Use another account", alongside standard fine print referencing Google's privacy policy and terms of service. At the very bottom, interactive buttons labeled "Cancel" and a blue "Continue" button invite the user to proceed with the authorization request.
Credential harvesting and security status
urlscan classified the page as malicious, Google Safe Browsing flags it, and OpenPhish blocks it, which confirms that the site is actively monitored for malicious behaviour rather than operating as a legitimate service. PhishDestroy's evidence score for it is 40/100 (high), reflecting the high risk associated with unauthorized OAuth applications hosted on public developer platforms like GitHub. By mimicking authentic single sign-on dialogs, the page exploits user trust in familiar authentication flows to trick visitors into granting third-party access to their personal accounts.
Recommended actions for visitors
Visitors who reached this page should close the browser tab immediately and avoid clicking any buttons or entering passwords. Anyone who has already interacted with the prompt and authorized the application must navigate directly to their Google account security settings, locate connected third-party apps, and revoke all permissions granted to Mehar Gaming. Additionally, affected users should update their account password and review recent security activity for unauthorized access.
ソース別の証拠VirusTotal 16 / 92 · Google Safe Browsing: フラグが立てられた6 件の情報源
meharislivegamingyoutube.github.io — Fake Google OAuth page
AIによる説明
meharislivegamingyoutube.github.io shows a fake Google sign-in page for Mehar Gaming, flagged by urlscan and Google Safe Browsing. Do not submit your password.
AIによる要約
Page layout and OAuth deception The page displays a clean, minimalist layout modelled closely after genuine Google account authentication screens. At the top left sits the standard Google logo, while the central section features a prominent red YouTube-style play icon above the bold heading "Continue to Mehar Gaming". Beneath this, explanatory text states that "Mehar Gaming wants to access your Google Account", accompanied by a mock account selector box displaying "Google User" and a placeholder email address. A secondary button allows visitors to "Use another account", alongside standard fine print referencing Google's privacy policy and terms of service. At the very bottom, interactive buttons labeled "Cancel" and a blue "Continue" button invite the user to proceed with the authorization request. Credential harvesting and security status urlscan classified the page as malicious, Google Safe Browsing flags it, and OpenPhish blocks it, which confirms that the site is actively monitored for malicious behaviour rather than operating as a legitimate service. PhishDestroy's evidence score for it is 40/100 (high), reflecting the high risk associated with unauthorized OAuth applications hosted on public developer platforms like GitHub. By mimicking authentic single sign-on dialogs, the page exploits user trust in familiar authentication flows to trick visitors into granting third-party access to their personal accounts. Recommended actions for visitors Visitors who reached this page should close the browser tab immediately and avoid clicking any buttons or entering passwords. Anyone who has already interacted with the prompt and authorized the application must navigate directly to their Google account security settings, locate connected third-party apps, and revoke all permissions granted to Mehar Gaming. Additionally, affected users should update their account password and review recent security activity for unauthorized access.
エビデンスレイヤーAvailability: Root path has no contentContent: Absent At RootDNS: Stale
最新のHTTP観測結果非アクティブHttp No Content70%2026-11-22 11:14 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-18 09:40 UTCcurrent episode first observed: 2026-11-19 00:08 UTCobserved RIP window: 2026-11-18 09:40 UTC → 2026-11-19 00:08 UTC · 14.46hmidpoint estimate ≈ 2026-11-18 16:54 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 185.199.108.153


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT