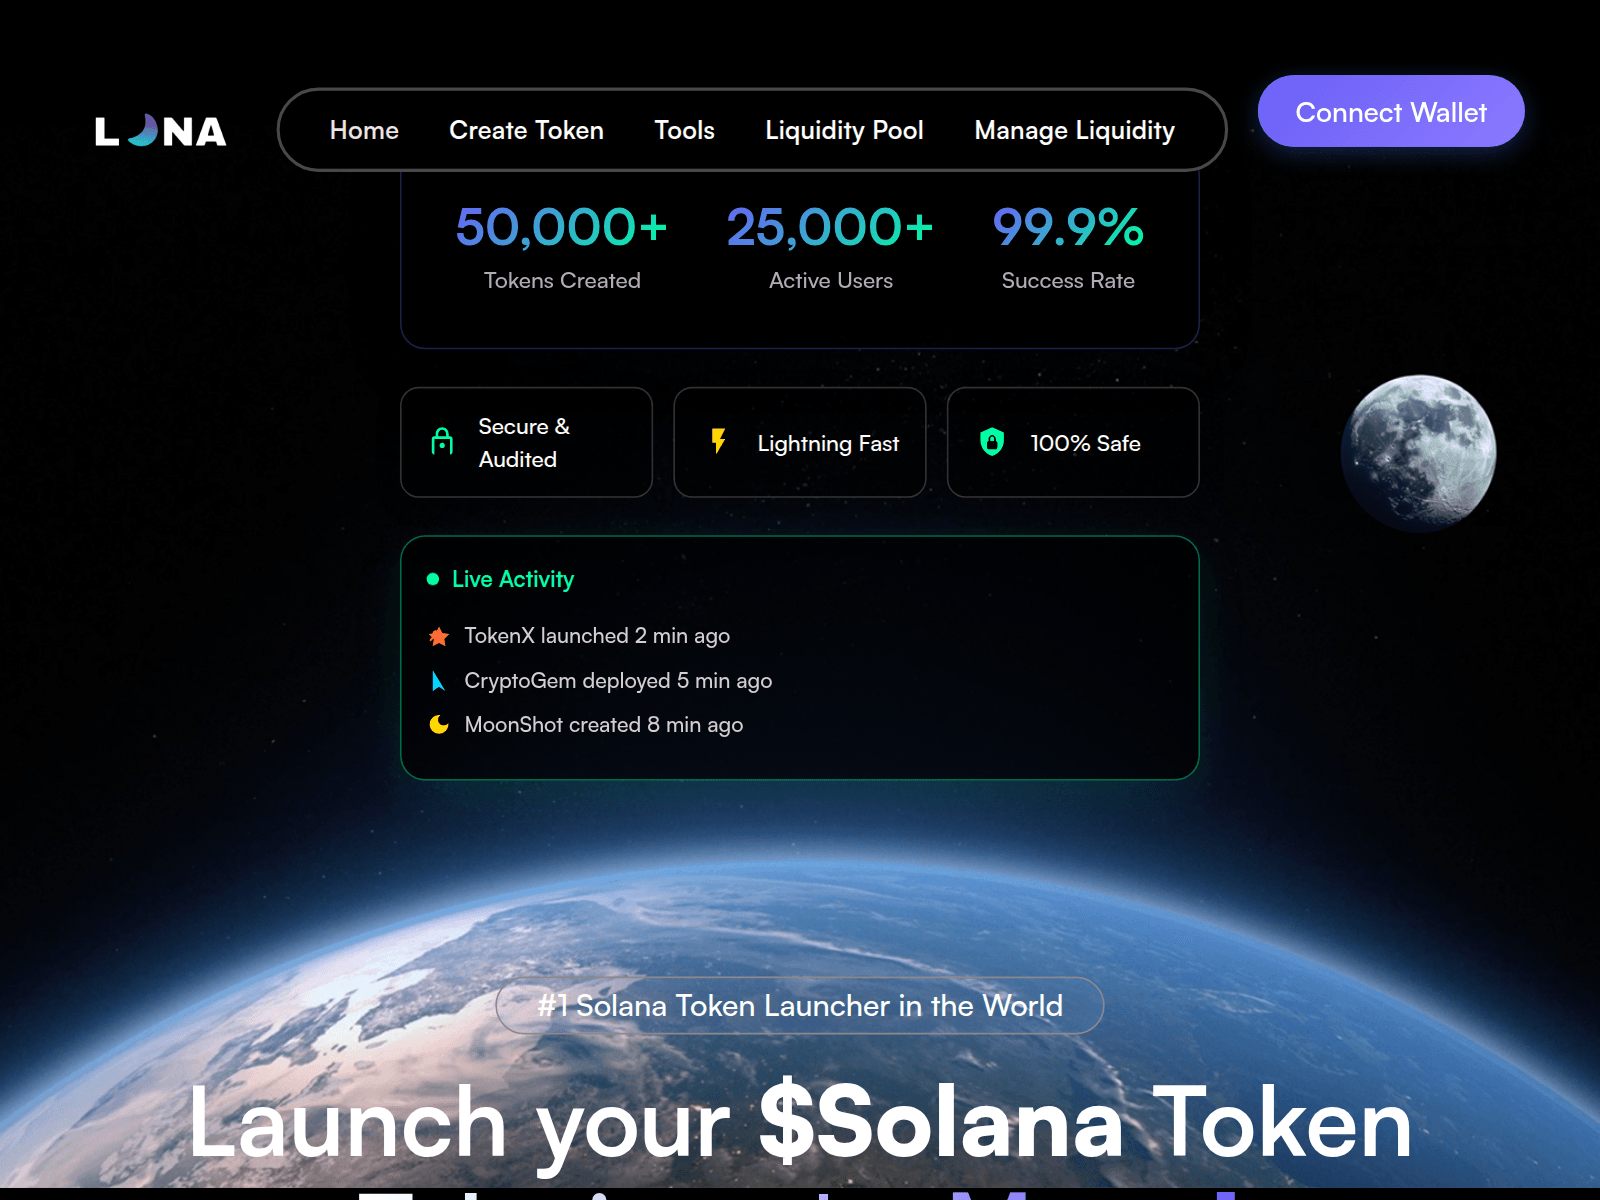
The site lunacreatmeme.com presents a fake Solana token launcher that invites users to connect their cryptocurrency wallets through a reown prompt. Visitors should immediately disconnect any linked wallets and revoke token approvals if they interacted with the page.
URLScanによるキャプチャ · 2026-11-14 22:03 UTC · SHA-256 47239a96…b492000
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Interface design and wallet connection lure
The page for lunacreatmeme.com loads with a dark space-themed background displaying a rotating moon and a view of Earth. The navigation bar includes links for "Home", "Create Token", "Tools", "Liquidity Pool", and "Manage Liquidity", alongside a prominent "Connect Wallet" button in the top right corner. Large statistics headers boast "50,000+ Tokens Created", "25,000+ Active Users", and a "99.9% Success Rate", accompanied by badges claiming the service is "Secure & Audited", "Lightning Fast", and "100% Safe". A live activity ticker shows recent actions like "TokenX launched 2 min ago" and "CryptoGem deployed 5 min ago", while a central banner declares the site to be the "#1 Solana Token Launcher in the World" above the massive header "Launch your $Solana Token". When a visitor clicks the connect button, the interface triggers a reown wallet connection prompt designed to harvest permissions.
Domain age and inflated platform claims
It was registered on 5 Nov 2026, 9 days before it was first reported, which directly contradicts the grand platform claims visible on the interface. While the site asserts it has facilitated over fifty thousand token creations with tens of thousands of active users, it sits behind Cloudflare, which hides the real server. This mismatch between an extremely recent creation date and boasts of being a top-tier global token launcher highlights the deceptive nature of the portal.
Security vendor telemetry and threat indicators
Because Spamhaus DBL lists it as phishing, 6 of 92 engines on VirusTotal flagged it, Cloudflare Radar rated it suspicious (New Domains, Security Risks), and MetaMask and SEAL block it, security scanners such as Fortinet, Forcepoint ThreatSeeker and CRDF classify the domain as malicious, and it sits behind Cloudflare, which hides the real server while it still answered requests on 19 Nov 2026 at 04:13 UTC. Furthermore, PhishDestroy scores the evidence against it at 90/100 (critical), so the malicious classification is supported by multiple independent entities rather than a single automated false alarm.
lunacreatmeme.com — Phishing reown wallet connection site
AIによる説明
lunacreatmeme.com presents a fake Solana token platform asking visitors to connect wallets, flagged by Spamhaus DBL and 6 VirusTotal engines.
AIによる要約
Interface design and wallet connection lure The page for lunacreatmeme.com loads with a dark space-themed background displaying a rotating moon and a view of Earth. The navigation bar includes links for "Home", "Create Token", "Tools", "Liquidity Pool", and "Manage Liquidity", alongside a prominent "Connect Wallet" button in the top right corner. Large statistics headers boast "50,000+ Tokens Created", "25,000+ Active Users", and a "99.9% Success Rate", accompanied by badges claiming the service is "Secure & Audited", "Lightning Fast", and "100% Safe". A live activity ticker shows recent actions like "TokenX launched 2 min ago" and "CryptoGem deployed 5 min ago", while a central banner declares the site to be the "#1 Solana Token Launcher in the World" above the massive header "Launch your $Solana Token". When a visitor clicks the connect button, the interface triggers a reown wallet connection prompt designed to harvest permissions. Domain age and inflated platform claims It was registered on 5 Nov 2026, 9 days before it was first reported, which directly contradicts the grand platform claims visible on the interface. While the site asserts it has facilitated over fifty thousand token creations with tens of thousands of active users, it sits behind Cloudflare, which hides the real server. This mismatch between an extremely recent creation date and boasts of being a top-tier global token launcher highlights the deceptive nature of the portal. Security vendor telemetry and threat indicators Because Spamhaus DBL lists it as phishing, 6 of 92 engines on VirusTotal flagged it, Cloudflare Radar rated it suspicious (New Domains, Security Risks), and MetaMask and SEAL block it, security scanners such as Fortinet, Forcepoint ThreatSeeker and CRDF classify the domain as malicious, and it sits behind Cloudflare, which hides the real server while it still answered requests on 19 Nov 2026 at 04:13 UTC. Furthermore, PhishDestroy scores the evidence against it at 90/100 (critical), so the malicious classification is supported by multiple independent entities rather than a single automated false alarm.
Registered contact email address is a free one According to Tranco this site has a low rank The registrar has a high % of spammers and fraud sites This website is (very) young.
The SSL certificate is valid This website is safe according to DNSFilter
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:10 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:10 UTClast content: 2026-11-22 11:10 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 PDR
 172.67.189.75


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT