元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
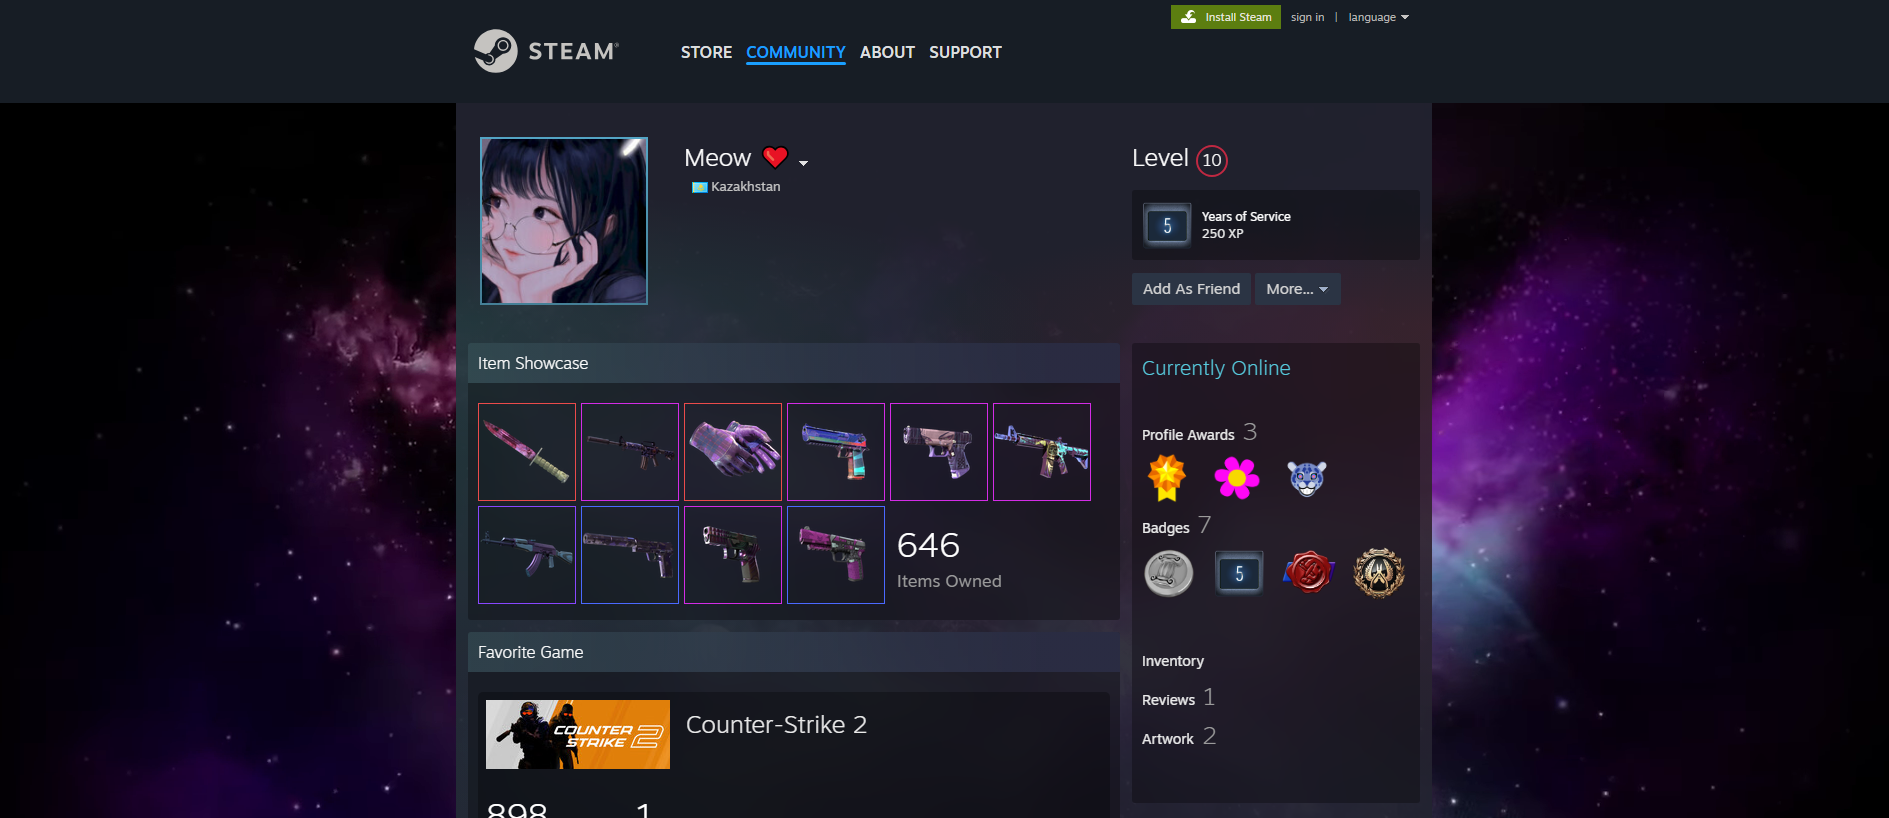
The captured screenshot from 2026-10-26 shows a blank browser error screen reading This page isn't working, naming login.steamcommunutty.com, citing HTTP ERROR 500 and offering a Reload button. PhishDestroy listed the domain after automated assessment classified it as a credential phishing page, first seen by PhishDestroy on 2026-10-26. Independent scanners tied the captured content to the Steam brand.
詐欺の手口
Scanner records show the page served a user-profile route that acts as a lure into an imitation Steam sign-in flow, the standard setup for capturing account usernames and passwords. Anyone who submits credentials on such a copy transfers them to the operator behind the domain. In the captured frame the backend failed, so the sign-in form itself was not rendered.
証拠
Beyond the 500 error screen, the capture shows the domain name and Reload control exactly as presented on 2026-10-26. URL scanning gave an ML score of 98 and an overall score of 100 in the phishing category with Steam named as the brand, and the traversal passed through a redirect funnel of 307, 301 then 307 responses. VirusTotal flagged the domain as malicious, with CRDF labelling it malicious and CyRadar and Gridinsoft labelling it phishing; Google Safe Browsing did not flag it, Spamhaus DBL was unlisted, OTX recorded 0 pulses, while OpenPhish and Phishunt blocklists listed it alongside PhishDestroy's internal blocklist. Site inspection recorded Prototype JavaScript globals such as Ajax and Form, one tracker request, and 2 distinct script SHA256 hashes, for example 7b31bc98d352, for campaign pivoting.
インフラ
Weaknesses first: DNSSEC unsigned; no email-authentication result and no HTTP security-header result recorded; TLS over QUIC with AES-128-GCM. Cloudflare name servers fronted the domain and the server header identified Cloudflare as the CDN and firewall, with no registrar data recorded.
What to do
If you submitted credentials on login.steamcommunutty.com, change your password on the genuine Steam service, enable two-factor authentication and watch for unexpected account activity. Security teams should block login.steamcommunutty.com at proxy, mail and DNS layers and hunt for the recorded script hashes.
PhishDestroy assesses login.steamcommunutty.com as a credential phishing page impersonating Steam, captured on 2026-10-26.
AIによる要約
Overview The captured screenshot from 2026-10-26 shows a blank browser error screen reading This page isn't working, naming login.steamcommunutty.com, citing HTTP ERROR 500 and offering a Reload button. PhishDestroy listed the domain after automated assessment classified it as a credential phishing page, first seen by PhishDestroy on 2026-10-26. Independent scanners tied the captured content to the Steam brand. How the scam works Scanner records show the page served a user-profile route that acts as a lure into an imitation Steam sign-in flow, the standard setup for capturing account usernames and passwords. Anyone who submits credentials on such a copy transfers them to the operator behind the domain. In the captured frame the backend failed, so the sign-in form itself was not rendered. Evidence Beyond the 500 error screen, the capture shows the domain name and Reload control exactly as presented on 2026-10-26. URL scanning gave an ML score of 98 and an overall score of 100 in the phishing category with Steam named as the brand, and the traversal passed through a redirect funnel of 307, 301 then 307 responses. VirusTotal flagged the domain as malicious, with CRDF labelling it malicious and CyRadar and Gridinsoft labelling it phishing; Google Safe Browsing did not flag it, Spamhaus DBL was unlisted, OTX recorded 0 pulses, while OpenPhish and Phishunt blocklists listed it alongside PhishDestroy's internal blocklist. Site inspection recorded Prototype JavaScript globals such as Ajax and Form, one tracker request, and 2 distinct script SHA256 hashes, for example 7b31bc98d352, for campaign pivoting. Infrastructure Weaknesses first: DNSSEC unsigned; no email-authentication result and no HTTP security-header result recorded; TLS over QUIC with AES-128-GCM. Cloudflare name servers fronted the domain and the server header identified Cloudflare as the CDN and firewall, with no registrar data recorded. What to do If you submitted credentials on login.steamcommunutty.com, change your password on the genuine Steam service, enable two-factor authentication and watch for unexpected account activity. Security teams should block login.steamcommunutty.com at proxy, mail and DNS layers and hunt for the recorded script hashes. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a17806-4f90-74ab-b33e-a7f5f89c5701/ Cloudflare Radar report: https://radar.cloudflare.com/scan/03abe0b2-1118-4863-a0c6-00c83f4724af URLQuery report: https://urlquery.net/report/41b9c1dc-4498-4702-816d-d9bbf822ffb9 Stored capture screenshot: https://i.ibb.co/0RSfqrP7/355ee1bff614.png Cloudflare Radar screenshot (2026-10-26T11:42:31Z): https://screenshots.phishdestroy.io/cf/03abe0b2-1118-4863-a0c6-00c83f4724af.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/41b9c1dc-4498-4702-816d-d9bbf822ffb9.png URLScan screenshot (2026-10-26T01:01:24Z): https://screenshots.phishdestroy.io/us/01a175b9-d5dd-716d-b439-9e5286f9bff6.png URLScan capture report: https://urlscan.io/result/01a175b9-d5dd-716d-b439-9e5286f9bff6/ URLScan screenshot (2026-10-26T04:31:43Z): https://screenshots.phishdestroy.io/us/01a1767a-0a7b-70a9-945a-a23fc6e233dc.png URLScan capture report: https://urlscan.io/result/01a1767a-0a7b-70a9-945a-a23fc6e233dc/ URLScan screenshot (2026-10-26T06:08:17Z): https://screenshots.phishdestroy.io/us/01a176d2-cca3-73ef-9a07-22aaead74a38.png URLScan capture report: https://urlscan.io/result/01a176d2-cca3-73ef-9a07-22aaead74a38/ URLScan screenshot (2026-10-26T11:15:39Z): https://screenshots.phishdestroy.io/us/01a177ec-346b-75b8-89d5-19bc1fc84472.png URLScan capture report: https://urlscan.io/result/01a177ec-346b-75b8-89d5-19bc1fc84472/ VirusTotal report: https://www.virustotal.com/gui/domain/login.steamcommunutty.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=login.steamcommunutty.com Archived copy: https://web.archive.org/web/20261026114101/https://login.steamcommunutty.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
主要評価項目DNS 非アクティブreason: DNS NXDOMAIN80% confidence
出典source: Dns Cache
エビデンスレイヤーAvailability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP登録
観測されたタイムラインlast reachable: 2026-11-04 09:20 UTClast content: 2026-10-29 03:32 UTCcurrent episode first observed: 2026-11-04 10:21 UTCobserved RIP window: 2026-11-04 09:20 UTC → 2026-11-04 10:21 UTC · 1.01hmidpoint estimate ≈ 2026-11-04 09:50 UTC · precision high · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 CNOBIN INFORMATION TEC…
 104.21.15.242


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT