元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
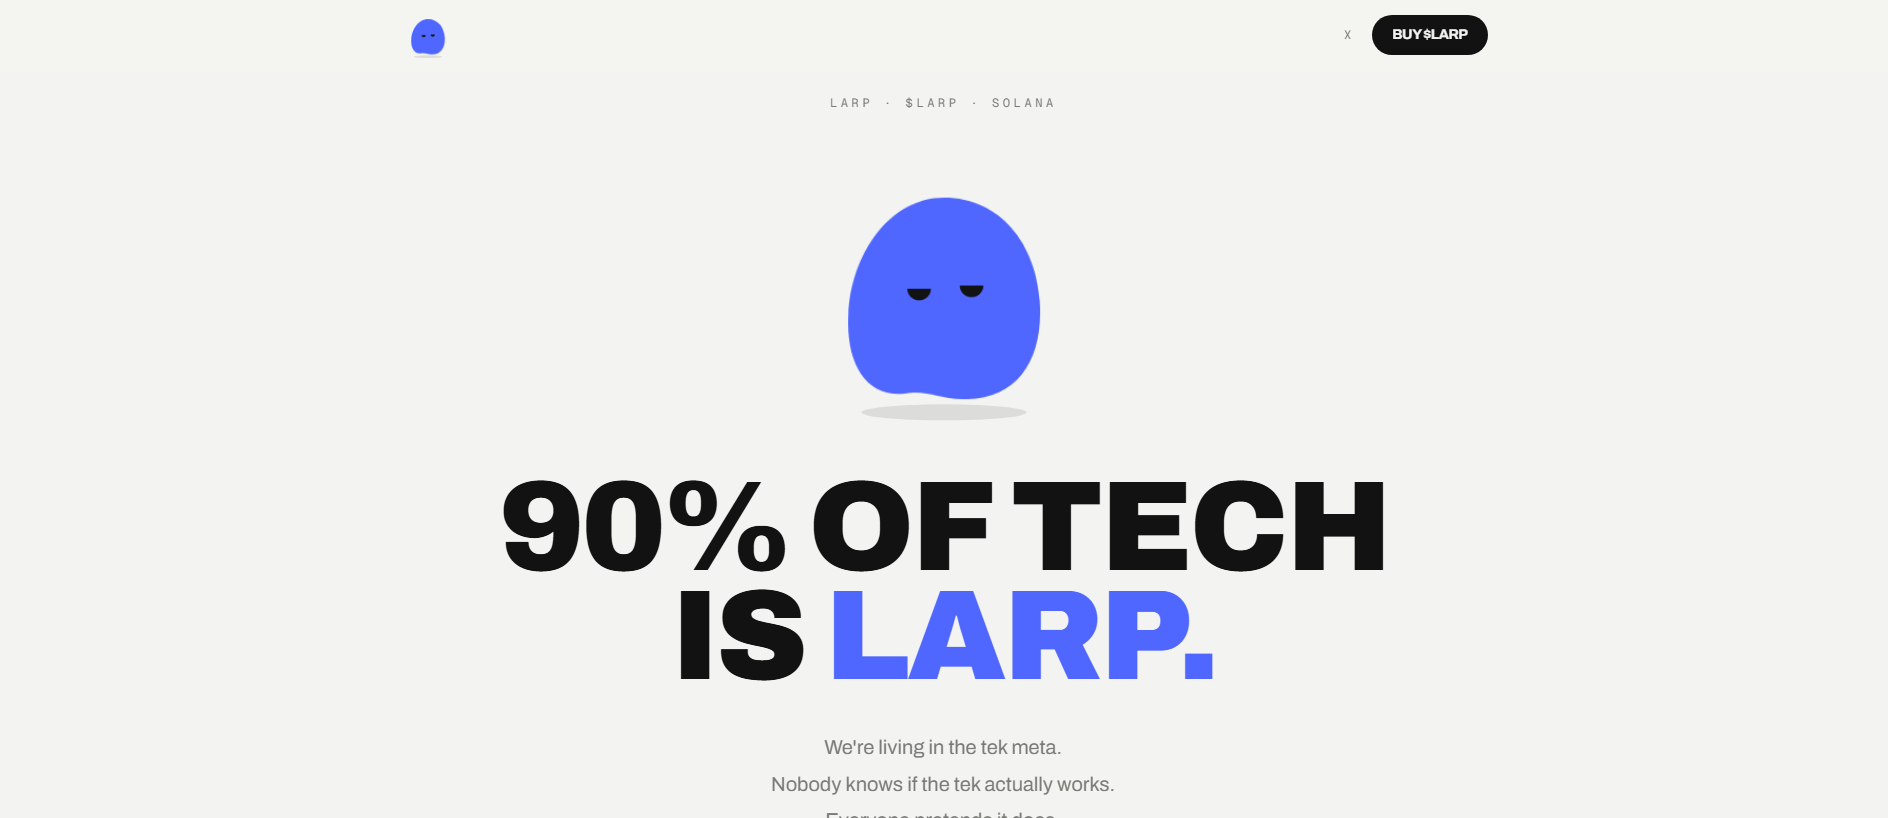
larpsol.today is an impersonation phishing page that presents itself as the LARP project, using that project's tagline "LARP — 90% of tech is LARP." as its page title. The "sol" in the name points at Solana token holders and traders who go looking for LARP online. PhishDestroy first flagged it on 2026-10-07. As of 2026-10-19 the domain was still alive and redirecting visitors onward.
詐欺の手口
Impersonation sites like this borrow a project's name, branding and slogan so that a visitor arriving from a search result, reply thread or direct message believes they have reached the official page. The usual hook is a claim, presale, airdrop or "connect wallet" button. Behind it sits a signature or transaction request that hands the operator control of tokens, or a form that collects a seed phrase. Because the page redirects, the domain may also work as a front door that forwards victims to wherever the payload currently lives. Either way, the loss is the contents of the connected wallet, and on-chain transfers cannot be reversed.
証拠
Detection by outside vendors is still thin. Four of 92 VirusTotal engines (Forcepoint ThreatSeeker, Gridinsoft, SOCRadar and VIPRE) marked the domain malicious when it was checked on 2026-10-19. The site also appears in four AlienVault OTX threat pulses, so other researchers have independently tied it to malicious activity. Among blocklists it is currently listed by PhishDestroy, which means many browsers and wallets will not warn you yet.
インフラ
The domain was registered on 2026-09-28 through NICENIC INTERNATIONAL GROUP CO., LIMITED, nine days before it came to our attention. That short gap fits a site set up quickly to catch interest in a trending token. It resolves to 216.150.1.1 on Amazon.com, Inc. network space in the US. Its Let's Encrypt certificate gives it a padlock, which shows only that the connection is encrypted, not that the site is genuine.
What to do
If you connected a wallet to larpsol.today, open a Solana approval manager right away, revoke any delegations or permissions you do not recognise, and move remaining funds to a fresh wallet. If you typed in a seed phrase, treat that wallet as compromised and transfer everything out before the attacker does. Reach the LARP project only through links it publishes on its verified channels. Security teams should block the domain and its redirect targets, and add it to wallet and browser blocklists while vendor coverage catches up.
larpsol.today is an impersonation phishing page copying the LARP crypto project, aimed at Solana users looking for the token, a mint or an airdrop.
AIによる要約
Overview larpsol.today is an impersonation phishing page that presents itself as the LARP project, using that project's tagline "LARP — 90% of tech is LARP." as its page title. The "sol" in the name points at Solana token holders and traders who go looking for LARP online. PhishDestroy first flagged it on 2026-10-07. As of 2026-10-19 the domain was still alive and redirecting visitors onward. How the scam works Impersonation sites like this borrow a project's name, branding and slogan so that a visitor arriving from a search result, reply thread or direct message believes they have reached the official page. The usual hook is a claim, presale, airdrop or "connect wallet" button. Behind it sits a signature or transaction request that hands the operator control of tokens, or a form that collects a seed phrase. Because the page redirects, the domain may also work as a front door that forwards victims to wherever the payload currently lives. Either way, the loss is the contents of the connected wallet, and on-chain transfers cannot be reversed. Evidence Detection by outside vendors is still thin. Four of 92 VirusTotal engines (Forcepoint ThreatSeeker, Gridinsoft, SOCRadar and VIPRE) marked the domain malicious when it was checked on 2026-10-19. The site also appears in four AlienVault OTX threat pulses, so other researchers have independently tied it to malicious activity. Among blocklists it is currently listed by PhishDestroy, which means many browsers and wallets will not warn you yet. Infrastructure The domain was registered on 2026-09-28 through NICENIC INTERNATIONAL GROUP CO., LIMITED, nine days before it came to our attention. That short gap fits a site set up quickly to catch interest in a trending token. It resolves to 216.150.1.1 on Amazon.com, Inc. network space in the US. Its Let's Encrypt certificate gives it a padlock, which shows only that the connection is encrypted, not that the site is genuine. What to do If you connected a wallet to larpsol.today, open a Solana approval manager right away, revoke any delegations or permissions you do not recognise, and move remaining funds to a fresh wallet. If you typed in a seed phrase, treat that wallet as compromised and transfer everything out before the attacker does. Reach the LARP project only through links it publishes on its verified channels. Security teams should block the domain and its redirect targets, and add it to wallet and browser blocklists while vendor coverage catches up. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a1169a-9422-701d-a70f-54933d155234/ VirusTotal report: https://www.virustotal.com/gui/domain/larpsol.today Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=larpsol.today Archived copy: https://web.archive.org/web/20260928220936/https://www.larpsol.today/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Last: 2026-10-09T18:32:02Z; First: 2026-09-28T21:46:13Z; Changes: 1; Days archived: 2; Scans per day: 0.09; Avg page bytes: 634
ページタイトルとメタデータ
Title: LARP — 90% of tech is LARP.; Ogimage: https://www.larpsol.today/brand/x-announcement.png; Ogtitle: LARP — 90% of tech is LARP.; Generator: v0.app; Themecolor: #f3f3f1; Description: We're living in the tek meta. Nobody knows if the tek actually works. So we made LARP. $LARP on Solana.; Twittercard: Summary large image; Twittersite: @LarpTekPF; Ogdescription: Same glorp. Different costume. $LARP on Solana.
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
エビデンスレイヤーAvailability: RedirectingDNS: ResolvedRegistration: Active
最新のHTTP観測結果RedirectingHTTP redirect observed80%2026-11-22 12:02 UTC
RDAP登録アクティブNICENIC INTERNATIONAL GROUP CO., LIMITED · IANA 3765RDAP HTTP 200source: Rdap Status CollectorclientDeleteProhibitedclientTransferProhibitedexpires 2027-09-28 17:12 UTCチェック済み 2026-10-09 04:34 UTC
観測されたタイムラインlast reachable: 2026-11-22 12:02 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 NiceNIC
 216.150.1.1


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT