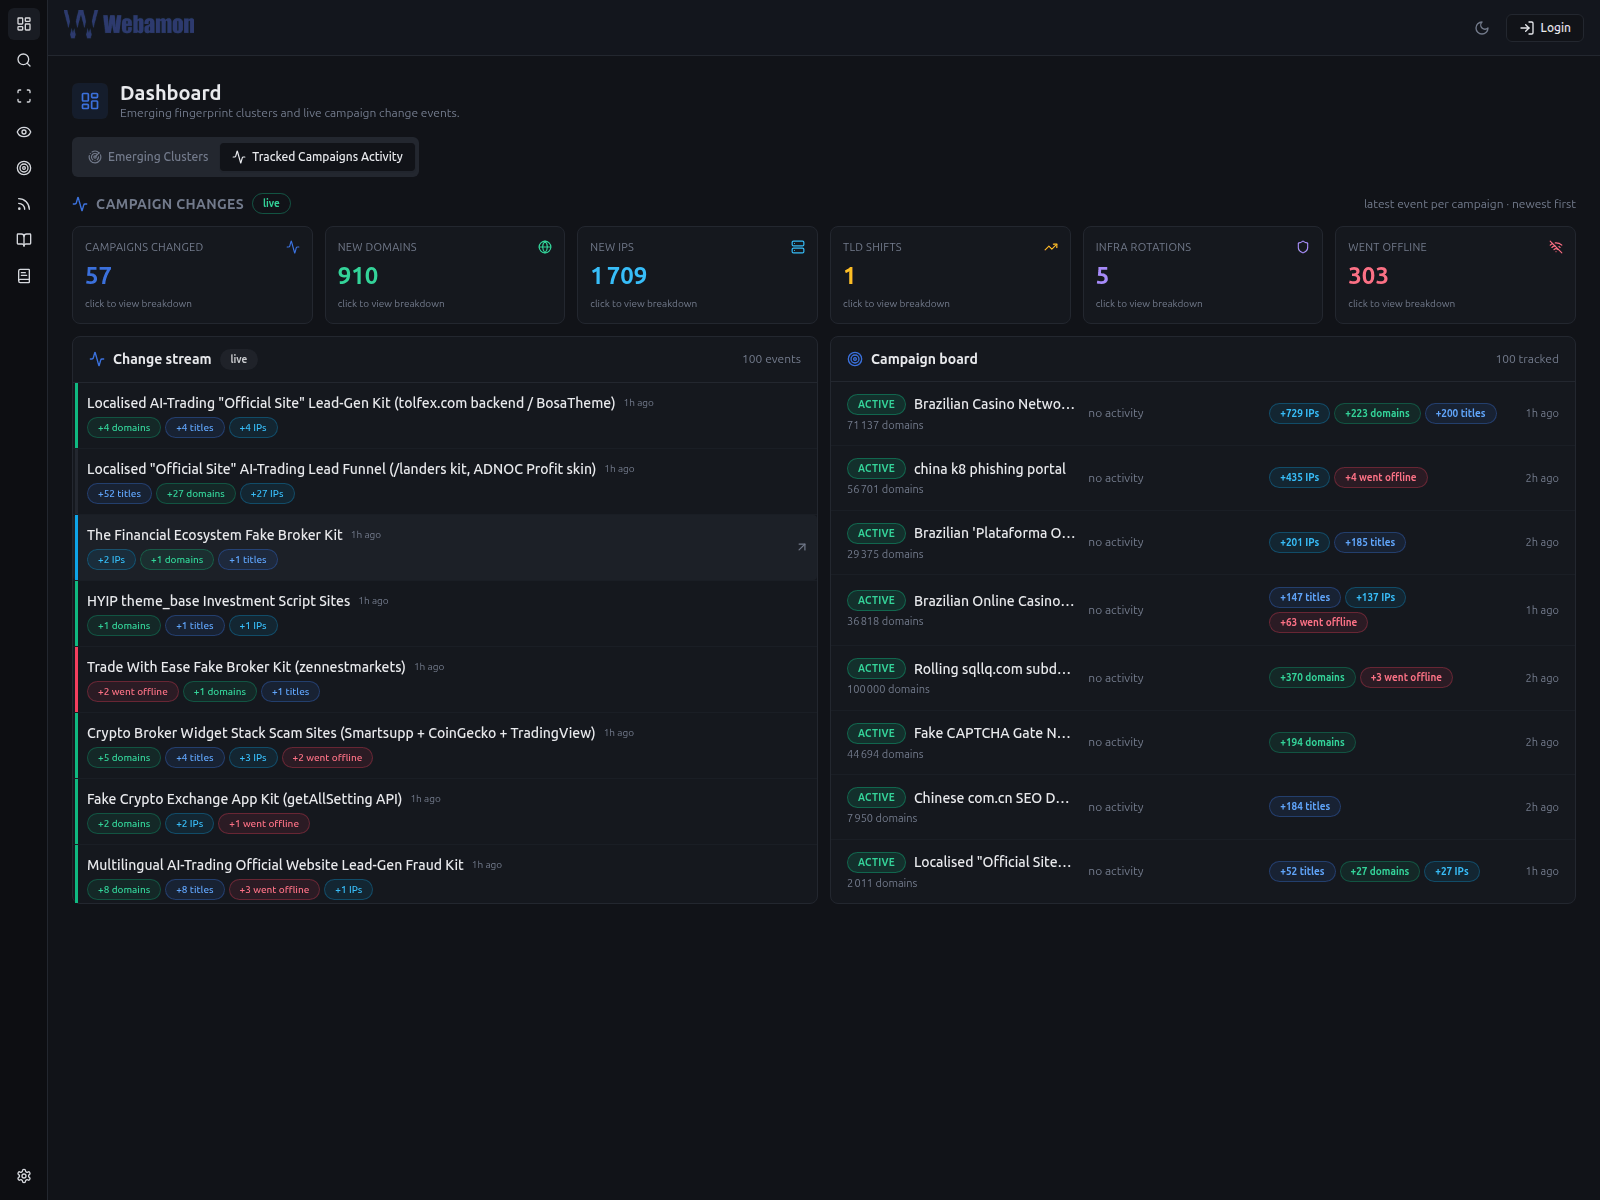
intel.webamon.com is a threat intelligence portal that displays live telemetry and campaign metrics alongside authentication prompts. Visitors who attempted to log in or connect external wallets should immediately disconnect active sessions and revoke any granted permissions.
URLScanによるキャプチャ · 2026-11-20 20:29 UTC · SHA-256 68e7c4ce…31c1bb1
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Dashboard interface and layout
The page opens with a dark interface bearing the Webamon brand logo in the top left corner and a prominent "Dashboard" heading accompanied by the description "Emerging fingerprint clusters and live campaign change events." Navigation tabs include options for "Emerging Clusters" and "Tracked Campaigns Activity," while metric cards display live statistics such as campaigns changed, new domains, new IPs, TLD shifts, infra rotations, and items gone offline. The main content area splits into a change stream showing entries like "Localised AI-Trading 'Official Site' Lead-Gen Kit" alongside a campaign board listing active entries including "Brazilian Casino Networks" and "china k8 phishing portal." A login button rests in the top right corner, inviting users to authenticate.
Security telemetry and independent findings
2 of 92 VirusTotal engines flagged it on 20 Nov 2026, and ScamSniffer blocks it. Security engines such as Forcepoint ThreatSeeker and Gridinsoft classify aspects of the domain as malicious, and PhishDestroy's evidence score for it is 50/100 (high). Because it was flagged by 2 VirusTotal engines, security teams recognize the target profile as monitored infrastructure rather than an isolated interface.
Wallet connection and session risks
The platform interface includes interaction elements that prompt visitors to connect external web wallets or log in through authenticated endpoints. Interacting with these prompts can expose session identifiers, browser fingerprints, or connected wallet assets to the underlying platform. Users who followed connection prompts on intel.webamon.com should immediately disconnect active sessions and revoke any granted token approvals through a trusted interface.
intel.webamon.com shows an active threat tracking dashboard with change streams and authentication elements, flagged by 2 VirusTotal engines.
AIによる要約
Dashboard interface and layout The page opens with a dark interface bearing the Webamon brand logo in the top left corner and a prominent "Dashboard" heading accompanied by the description "Emerging fingerprint clusters and live campaign change events." Navigation tabs include options for "Emerging Clusters" and "Tracked Campaigns Activity," while metric cards display live statistics such as campaigns changed, new domains, new IPs, TLD shifts, infra rotations, and items gone offline. The main content area splits into a change stream showing entries like "Localised AI-Trading 'Official Site' Lead-Gen Kit" alongside a campaign board listing active entries including "Brazilian Casino Networks" and "china k8 phishing portal." A login button rests in the top right corner, inviting users to authenticate. Security telemetry and independent findings 2 of 92 VirusTotal engines flagged it on 20 Nov 2026, and ScamSniffer blocks it. Security engines such as Forcepoint ThreatSeeker and Gridinsoft classify aspects of the domain as malicious, and PhishDestroy's evidence score for it is 50/100 (high). Because it was flagged by 2 VirusTotal engines, security teams recognize the target profile as monitored infrastructure rather than an isolated interface. Wallet connection and session risks The platform interface includes interaction elements that prompt visitors to connect external web wallets or log in through authenticated endpoints. Interacting with these prompts can expose session identifiers, browser fingerprints, or connected wallet assets to the underlying platform. Users who followed connection prompts on intel.webamon.com should immediately disconnect active sessions and revoke any granted token approvals through a trusted interface.
Headers: Server: AmazonS3; Content type: text/html; Via: 1.1 a95e3ddc09a8118950740e900d11ffc8.cloudfront.net (CloudFront); X cache: Hit from cloudfront
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:58 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:58 UTClast content: 2026-11-22 11:58 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 Amazon
 3.174.46.46


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT