元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
indta.co.id is an Indonesian .co.id domain that PhishDestroy classifies as an impersonation phishing page. It first appeared on our radar on 2026-10-11. As of 2026-10-19 the site was still online and serving content, so anyone who receives a link to it should treat it as an active threat.
詐欺の手口
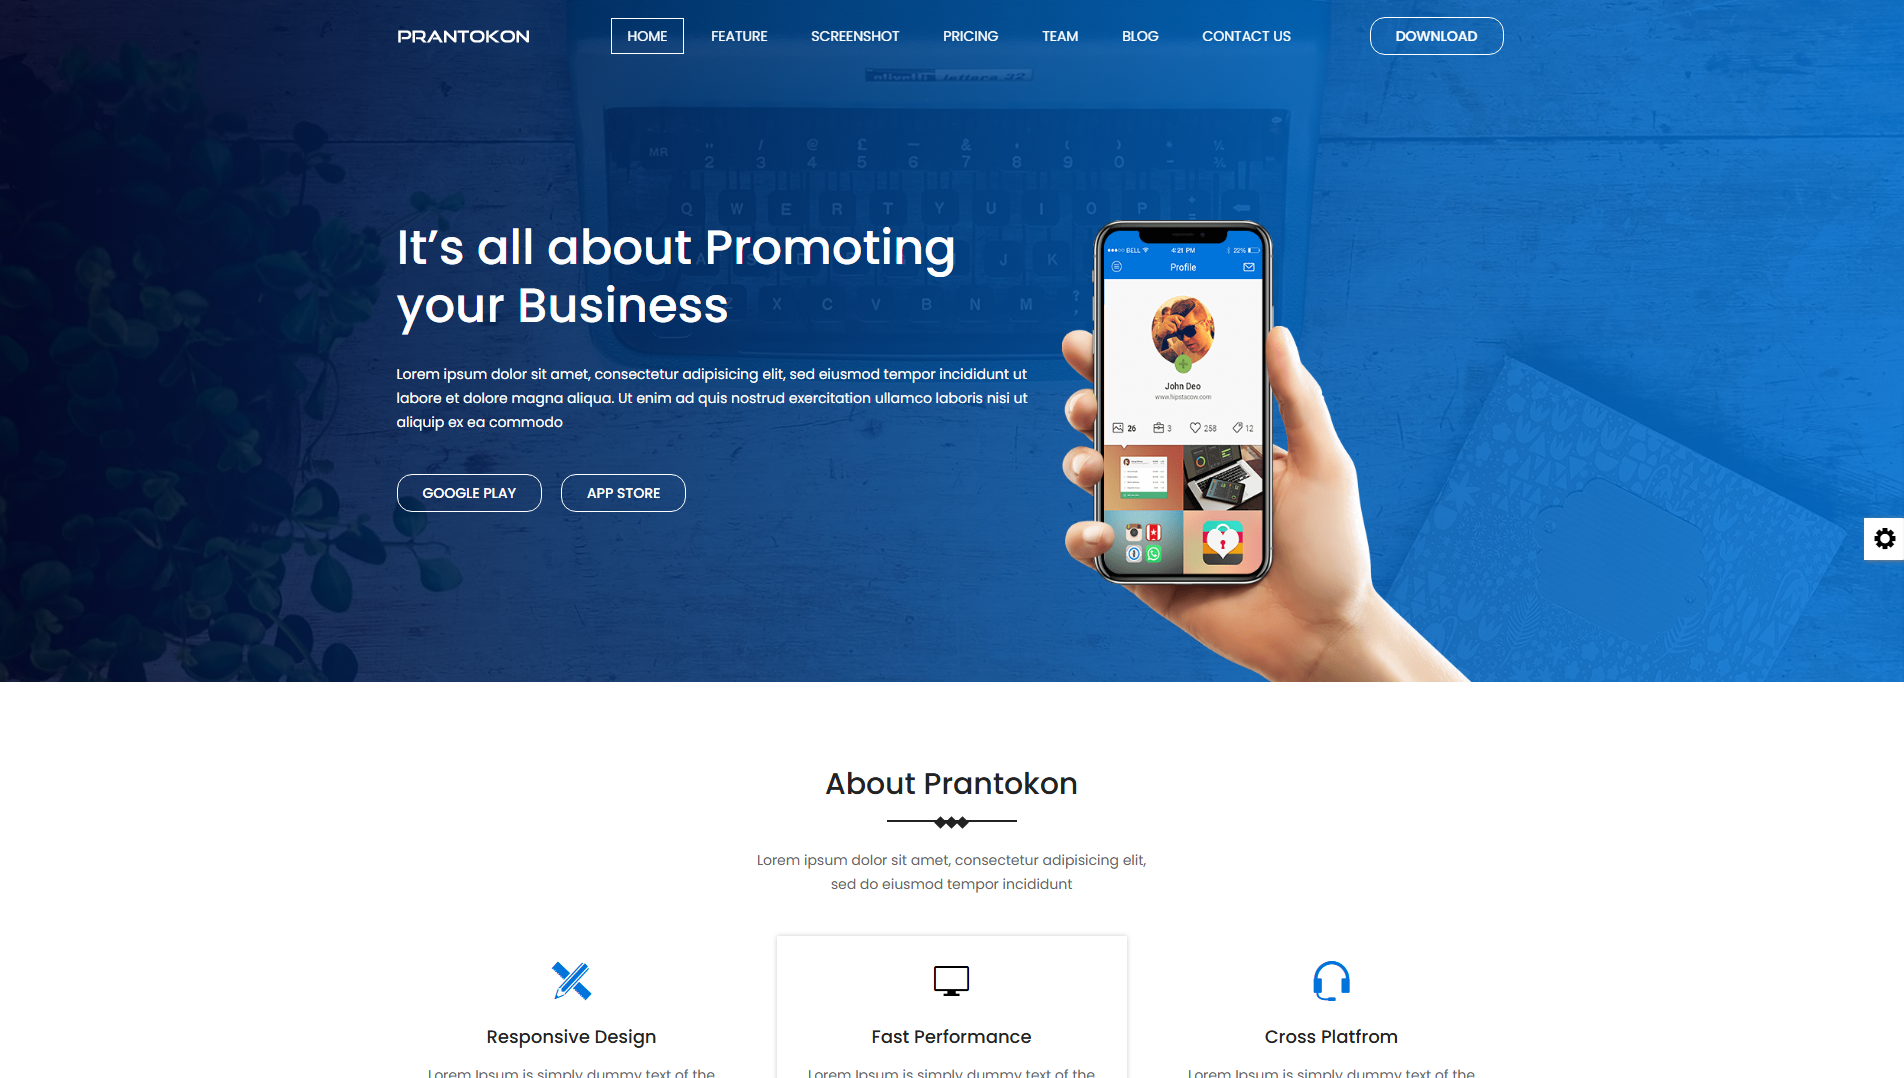
Impersonation pages borrow the look, name or branding of a service people already trust, so visitors drop their guard and type in passwords, one-time codes, personal details or wallet recovery phrases. Whatever is entered goes straight to the operator, who can then take over the real account or empty the wallet. The page carries the title "Prantokon - App Landing Html Template", which is the name of an off-the-shelf app landing page template rather than a specific brand. That generic title differs from our impersonation classification, which reflects the site's behavior rather than its page label.
証拠
On 2026-10-12, 12 of 92 VirusTotal engines flagged the domain. Those engines include ADMINUSLabs, alphaMountain.ai, BitDefender, Dr.Web, Fortinet, G-Data, Gridinsoft and Kaspersky. That is a minority of engines, but it is a broad mix of established antivirus and URL-reputation vendors reaching the same verdict independently. The domain also appears in 34 AlienVault OTX threat pulses, which shows other researchers have been tracking it. Among blocklists, it is currently listed by PhishDestroy.
インフラ
The domain is old. It was registered on 2017-04-06, more than nine years before PhishDestroy first saw it. A long registration history means the name alone can look trustworthy to filters and to people. It is registered through PT JC Indonesia and hosted on that same company's network (JOGJACAMP-AS-ID) in Indonesia. Its Let's Encrypt certificate gives the browser padlock but says nothing about who runs the site.
What to do
Do not enter anything on indta.co.id, and close the page if it opens. If you typed a password there, change it right away on the genuine service and on any other account that shares it. Then turn on or reset two-factor authentication and review recent logins. If you entered a wallet recovery phrase or private key, assume that wallet is compromised and move any remaining funds to a newly created wallet. Security teams should block the domain at DNS and the mail gateway, and search proxy and email logs for users who visited it after 2026-10-11.
indta.co.id is an impersonation phishing page flagged by PhishDestroy that poses as a trusted service to trick visitors into handing over logins and secrets.
AIによる要約
Overview indta.co.id is an Indonesian .co.id domain that PhishDestroy classifies as an impersonation phishing page. It first appeared on our radar on 2026-10-11. As of 2026-10-19 the site was still online and serving content, so anyone who receives a link to it should treat it as an active threat. How the scam works Impersonation pages borrow the look, name or branding of a service people already trust, so visitors drop their guard and type in passwords, one-time codes, personal details or wallet recovery phrases. Whatever is entered goes straight to the operator, who can then take over the real account or empty the wallet. The page carries the title "Prantokon - App Landing Html Template", which is the name of an off-the-shelf app landing page template rather than a specific brand. That generic title differs from our impersonation classification, which reflects the site's behavior rather than its page label. Evidence On 2026-10-12, 12 of 92 VirusTotal engines flagged the domain. Those engines include ADMINUSLabs, alphaMountain.ai, BitDefender, Dr.Web, Fortinet, G-Data, Gridinsoft and Kaspersky. That is a minority of engines, but it is a broad mix of established antivirus and URL-reputation vendors reaching the same verdict independently. The domain also appears in 34 AlienVault OTX threat pulses, which shows other researchers have been tracking it. Among blocklists, it is currently listed by PhishDestroy. Infrastructure The domain is old. It was registered on 2017-04-06, more than nine years before PhishDestroy first saw it. A long registration history means the name alone can look trustworthy to filters and to people. It is registered through PT JC Indonesia and hosted on that same company's network (JOGJACAMP-AS-ID) in Indonesia. Its Let's Encrypt certificate gives the browser padlock but says nothing about who runs the site. What to do Do not enter anything on indta.co.id, and close the page if it opens. If you typed a password there, change it right away on the genuine service and on any other account that shares it. Then turn on or reset two-factor authentication and review recent logins. If you entered a wallet recovery phrase or private key, assume that wallet is compromised and move any remaining funds to a newly created wallet. Security teams should block the domain at DNS and the mail gateway, and search proxy and email logs for users who visited it after 2026-10-11. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a12970-d8ea-7387-8a93-4bdad9478844/ VirusTotal report: https://www.virustotal.com/gui/domain/indta.co.id Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=indta.co.id Archived copy: https://web.archive.org/web/20241213210654/https://indta.co.id/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:37 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:37 UTClast content: 2026-11-22 11:37 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 PT JC Indonesia


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT