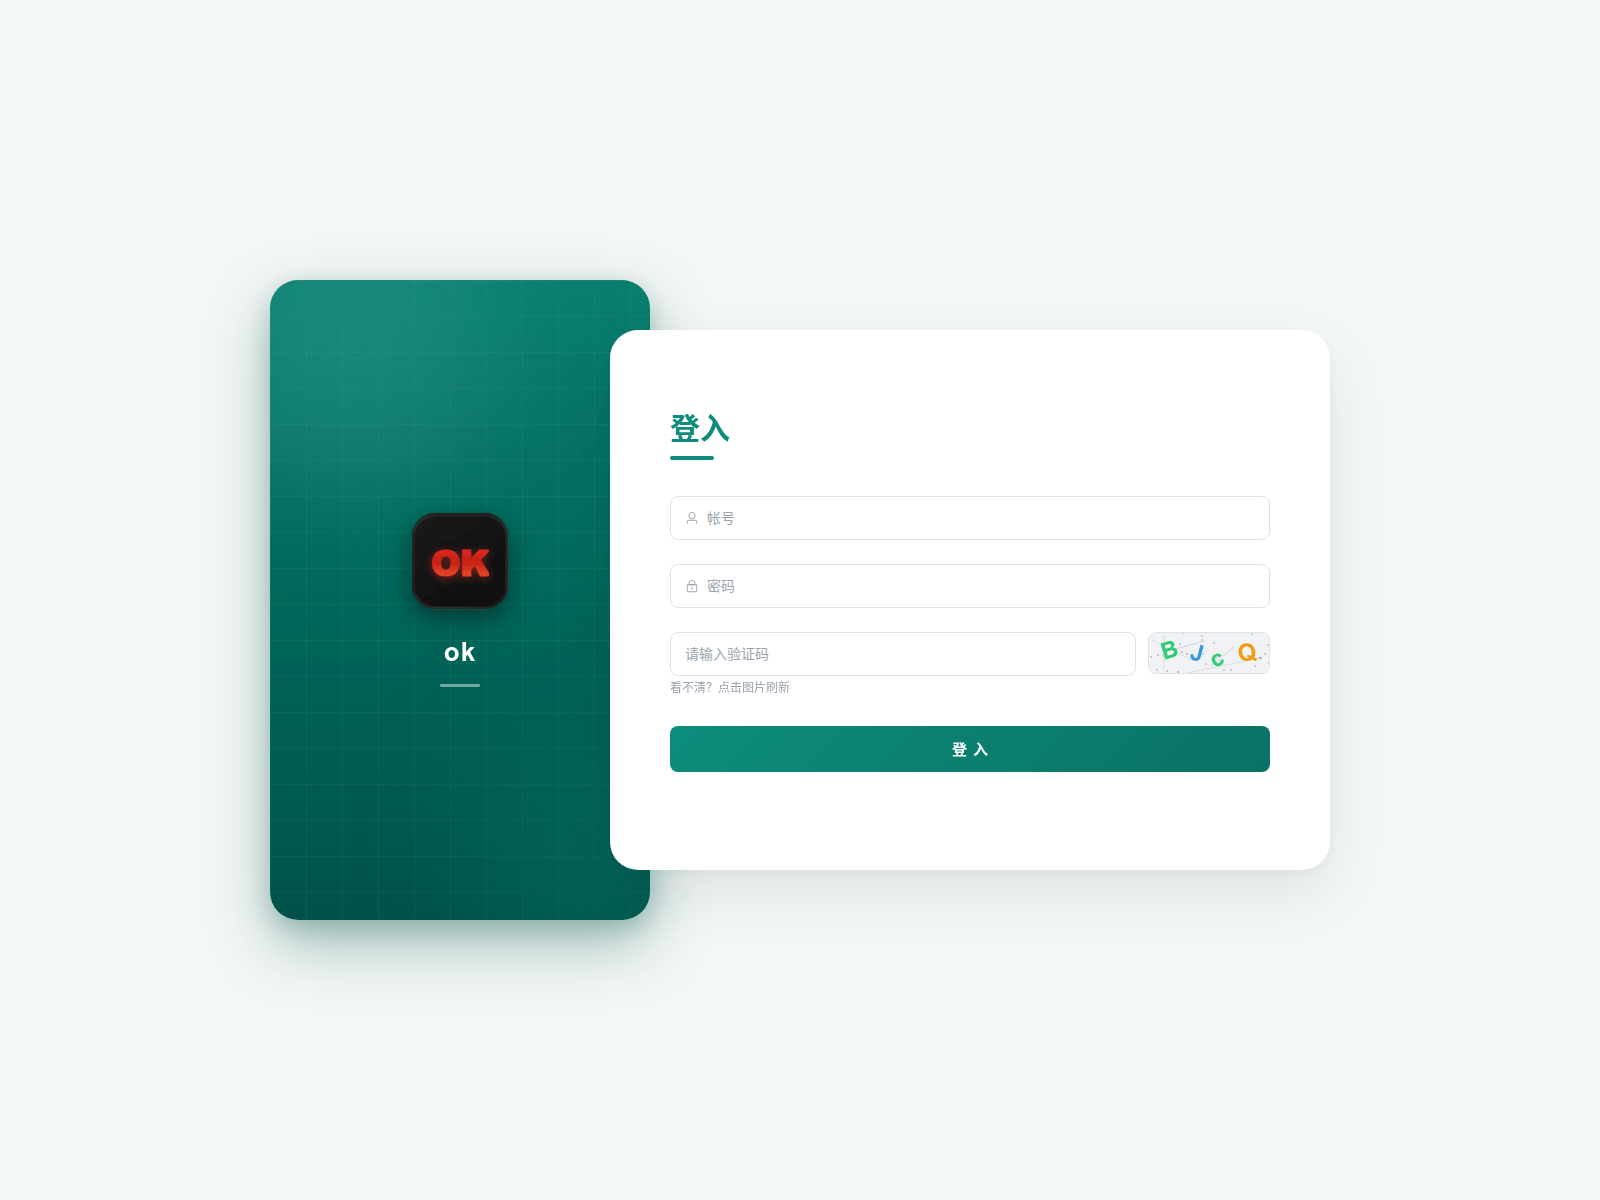
On 2026-11-08, icloud-jpz.xyz displayed a Chinese-language sign-in page. The layout pairs a dark teal panel bearing an "OK" logo tile with the label "ok" against a white card headed "登入" (sign in). The card contains three input fields: an account field (帐号), a password field (密码), and a verification code field (请输入验证码) accompanied by a distorted-character CAPTCHA image and a link to refresh it if unreadable. A full-width teal button labeled "登入" sits below the fields.
URLScanによるキャプチャ · 2026-11-08 13:17 UTC · SHA-256 4ae3dc07…c29e68f
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
On 2026-11-08, icloud-jpz.xyz displayed a Chinese-language sign-in page. The layout pairs a dark teal panel bearing an "OK" logo tile with the label "ok" against a white card headed "登入" (sign in). The card contains three input fields: an account field (帐号), a password field (密码), and a verification code field (请输入验证码) accompanied by a distorted-character CAPTCHA image and a link to refresh it if unreadable. A full-width teal button labeled "登入" sits below the fields.
The stored VirusTotal domain result reports 7 detections out of 92 engines. CRDF reported "malicious"; Lionic reported "phishing".
ソース別の証拠VirusTotal 7 / 92 · Google Safe Browsing: フラグが立てられた6 件の情報源
icloud-jpz.xyz: Recorded Chinese-language account sign-in form
AIによる説明
PhishDestroy records icloud-jpz.xyz showing a Chinese-language sign-in page with account, password and verification code fields.
AIによる要約
On 2026-11-08, icloud-jpz.xyz displayed a Chinese-language sign-in page. The layout pairs a dark teal panel bearing an "OK" logo tile with the label "ok" against a white card headed "登入" (sign in). The card contains three input fields: an account field (帐号), a password field (密码), and a verification code field (请输入验证码) accompanied by a distorted-character CAPTCHA image and a link to refresh it if unreadable. A full-width teal button labeled "登入" sits below the fields. The stored VirusTotal domain result reports 7 detections out of 92 engines. CRDF reported "malicious"; Lionic reported "phishing".
主要評価項目DNS 非アクティブreason: DNS NXDOMAIN80% confidence
出典source: Dns Cache
エビデンスレイヤーAvailability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP登録
観測されたタイムラインlast reachable: 2026-11-08 23:00 UTClast content: 2026-11-08 23:00 UTCcurrent episode first observed: 2026-11-09 22:22 UTCobserved RIP window: 2026-11-08 23:00 UTC → 2026-11-09 22:22 UTC · 23.36hmidpoint estimate ≈ 2026-11-09 10:41 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.