元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
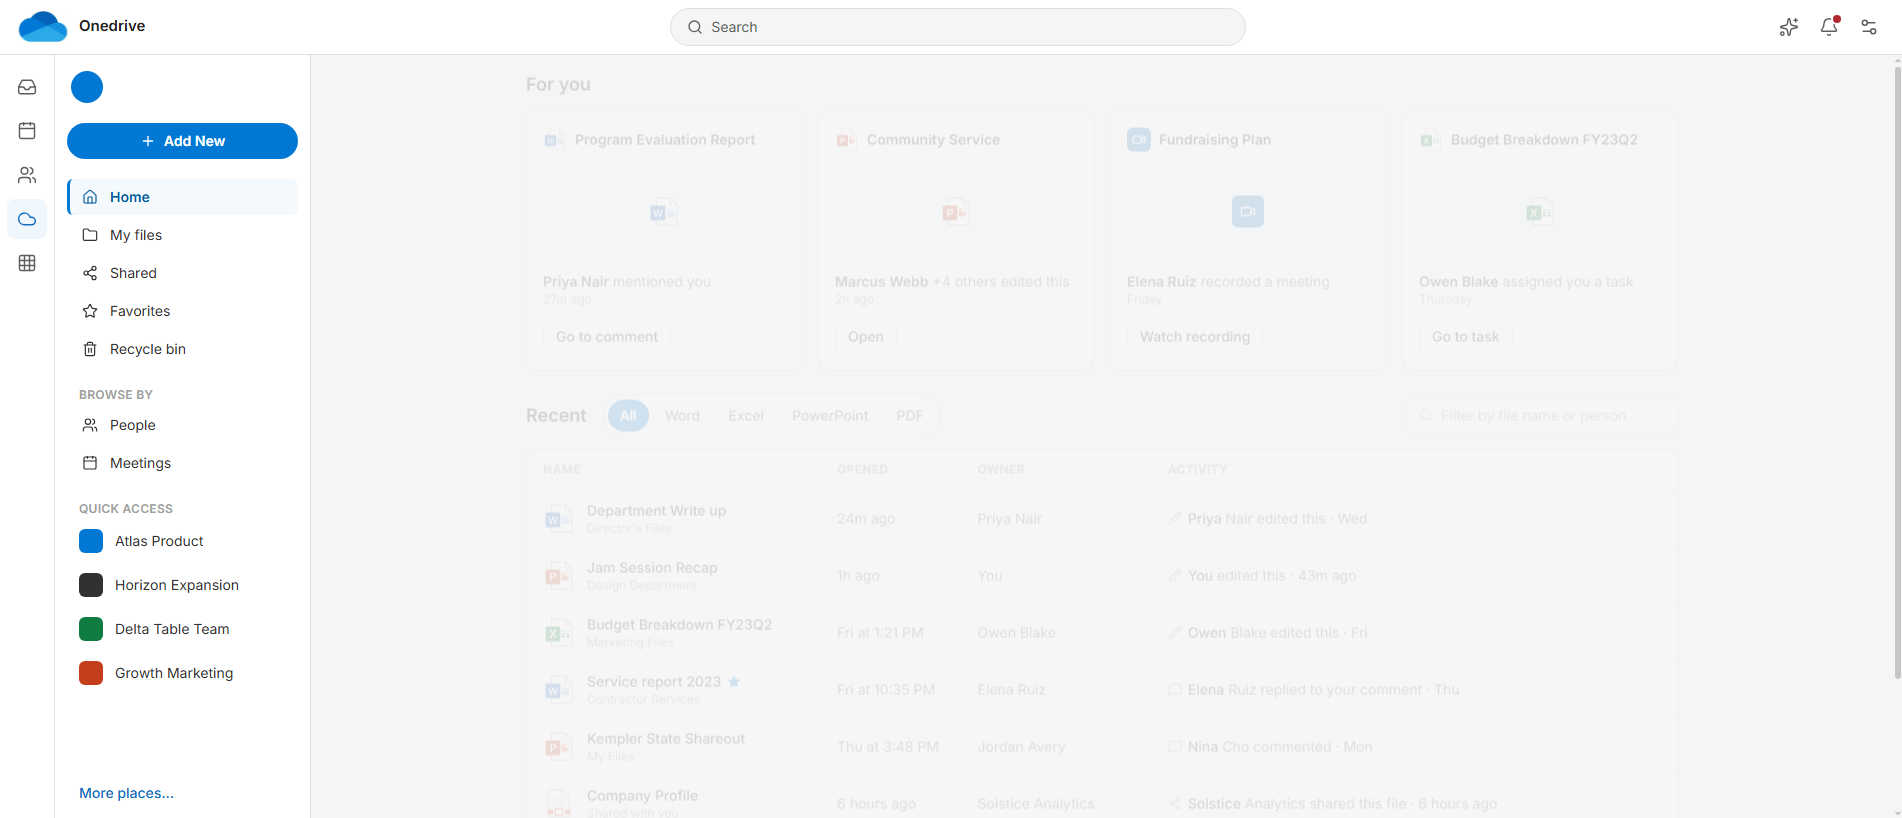
The capture shows a file-storage dashboard titled "Onedrive", with a document grid, a recent-file table and activity attributed to named people. PhishDestroy's recorded intake reason was a VirusTotal result of 5 malicious vendors, an administrative detection count rather than an observation of the page itself. The substantive concern now comes from independent scanners that categorised the checked domain as phishing on 2026-10-28.
詐欺の手口
If this page were used to collect credentials, a visitor would need to be routed to a sign-in step that the single capture does not show. The screenshot displays only a dashboard with file rows, activity messages such as "Priya Nair mentioned you", and navigation controls; it contains no visible password field, and a still image cannot establish whether any form is functional or where data would be sent. The record therefore supports a phishing categorisation by scanners, not a demonstrated credential-capture mechanism.
証拠
VirusTotal's domain-scope snapshot retrieved and analysed on 2026-10-28 recorded 5 malicious detections out of 92 engines: VIPRE, LevelBlue, Scantitan and Yandex Safebrowsing labelled it "phishing" and Webroot "malicious". URLScan's overall verdict was malicious with score 100 and category "phishing" (brand OneDrive), while its engine verdict was malicious at 96; Cloudflare Radar likewise recorded a malicious phishing verdict and a domain risk of Phishing. Material negatives: Google Safe Browsing was not flagged, OTX had 0 pulses (mentions, not detections), and external blocklists showed 0 entries, all checked 2026-10-28. Webcheck found the title "Onedrive" and blocking by 1 of 12 resolvers, CloudFlare Family.
インフラ
The capture returned HTTP 200 on 2026-10-28, following a 307 redirect from the http version of the same hostname. The page sits on the shared edgeone.dev hosting platform, which may host unrelated sites.
What to do
Avoid entering credentials on this hostname, and block only global-fuchsia-9par6vcz-dp5x4caf1rmk.edgeone.dev, since shared hosting can carry unrelated sites. If you did type your Microsoft or work account password here, change it from Microsoft's own site and review recent sign-in activity; no such exposure is shown by the capture alone.
global-fuchsia-9par6vcz-dp5x4caf1rmk.edgeone.dev shows an Onedrive-branded file dashboard that PhishDestroy records with multiple phishing verdicts from…
AIによる要約
Overview The capture shows a file-storage dashboard titled "Onedrive", with a document grid, a recent-file table and activity attributed to named people. PhishDestroy's recorded intake reason was a VirusTotal result of 5 malicious vendors, an administrative detection count rather than an observation of the page itself. The substantive concern now comes from independent scanners that categorised the checked domain as phishing on 2026-10-28. How the scam works If this page were used to collect credentials, a visitor would need to be routed to a sign-in step that the single capture does not show. The screenshot displays only a dashboard with file rows, activity messages such as "Priya Nair mentioned you", and navigation controls; it contains no visible password field, and a still image cannot establish whether any form is functional or where data would be sent. The record therefore supports a phishing categorisation by scanners, not a demonstrated credential-capture mechanism. Evidence VirusTotal's domain-scope snapshot retrieved and analysed on 2026-10-28 recorded 5 malicious detections out of 92 engines: VIPRE, LevelBlue, Scantitan and Yandex Safebrowsing labelled it "phishing" and Webroot "malicious". URLScan's overall verdict was malicious with score 100 and category "phishing" (brand OneDrive), while its engine verdict was malicious at 96; Cloudflare Radar likewise recorded a malicious phishing verdict and a domain risk of Phishing. Material negatives: Google Safe Browsing was not flagged, OTX had 0 pulses (mentions, not detections), and external blocklists showed 0 entries, all checked 2026-10-28. Webcheck found the title "Onedrive" and blocking by 1 of 12 resolvers, CloudFlare Family. Infrastructure The capture returned HTTP 200 on 2026-10-28, following a 307 redirect from the http version of the same hostname. The page sits on the shared edgeone.dev hosting platform, which may host unrelated sites. What to do Avoid entering credentials on this hostname, and block only global-fuchsia-9par6vcz-dp5x4caf1rmk.edgeone.dev, since shared hosting can carry unrelated sites. If you did type your Microsoft or work account password here, change it from Microsoft's own site and review recent sign-in activity; no such exposure is shown by the capture alone. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a1842f-6db1-716b-afb6-e6d32bcf046b/ Cloudflare Radar report: https://radar.cloudflare.com/scan/de5683f0-11a2-418c-93d3-81edf12953d6 Stored capture screenshot: https://i.ibb.co/6JY4kYPp/0cfa65a7a574.png Cloudflare Radar screenshot (2026-10-28T20:12:38Z): https://screenshots.phishdestroy.io/cf/de5683f0-11a2-418c-93d3-81edf12953d6.png URLScan screenshot (2026-10-27T18:15:21Z): https://screenshots.phishdestroy.io/us/01a17e91-c3e2-728f-80ed-098e3d49e4e1.png URLScan capture report: https://urlscan.io/result/01a17e91-c3e2-728f-80ed-098e3d49e4e1/ URLScan screenshot (2026-10-28T01:02:35Z): https://screenshots.phishdestroy.io/us/01a18007-afb9-7041-8ab7-8f7b6c80c3ed.png URLScan capture report: https://urlscan.io/result/01a18007-afb9-7041-8ab7-8f7b6c80c3ed/ URLScan screenshot (2026-10-28T04:47:36Z): https://screenshots.phishdestroy.io/us/01a180d5-a747-7010-b1a1-db108b8018ee.png URLScan capture report: https://urlscan.io/result/01a180d5-a747-7010-b1a1-db108b8018ee/ URLScan screenshot (2026-10-28T11:12:29Z): https://screenshots.phishdestroy.io/us/01a18236-0995-77ee-a617-828ed818c60b.png URLScan capture report: https://urlscan.io/result/01a18236-0995-77ee-a617-828ed818c60b/ VirusTotal report: https://www.virustotal.com/gui/domain/global-fuchsia-9par6vcz-dp5x4caf1rmk.edgeone.dev Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=global-fuchsia-9par6vcz-dp5x4caf1rmk.edgeone.dev Archived copy: https://web.archive.org/web/20261028201123/https://global-fuchsia-9par6vcz-dp5x4caf1rmk.edgeone.dev/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-21 11:33 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-21 11:33 UTClast content: 2026-11-21 11:33 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
使用技術 · 1 identified
HSTS
HTTP Strict Transport Security (HSTS) informs browsers that the site should only be accessed using HTTPS.


 43.174.247.29


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT