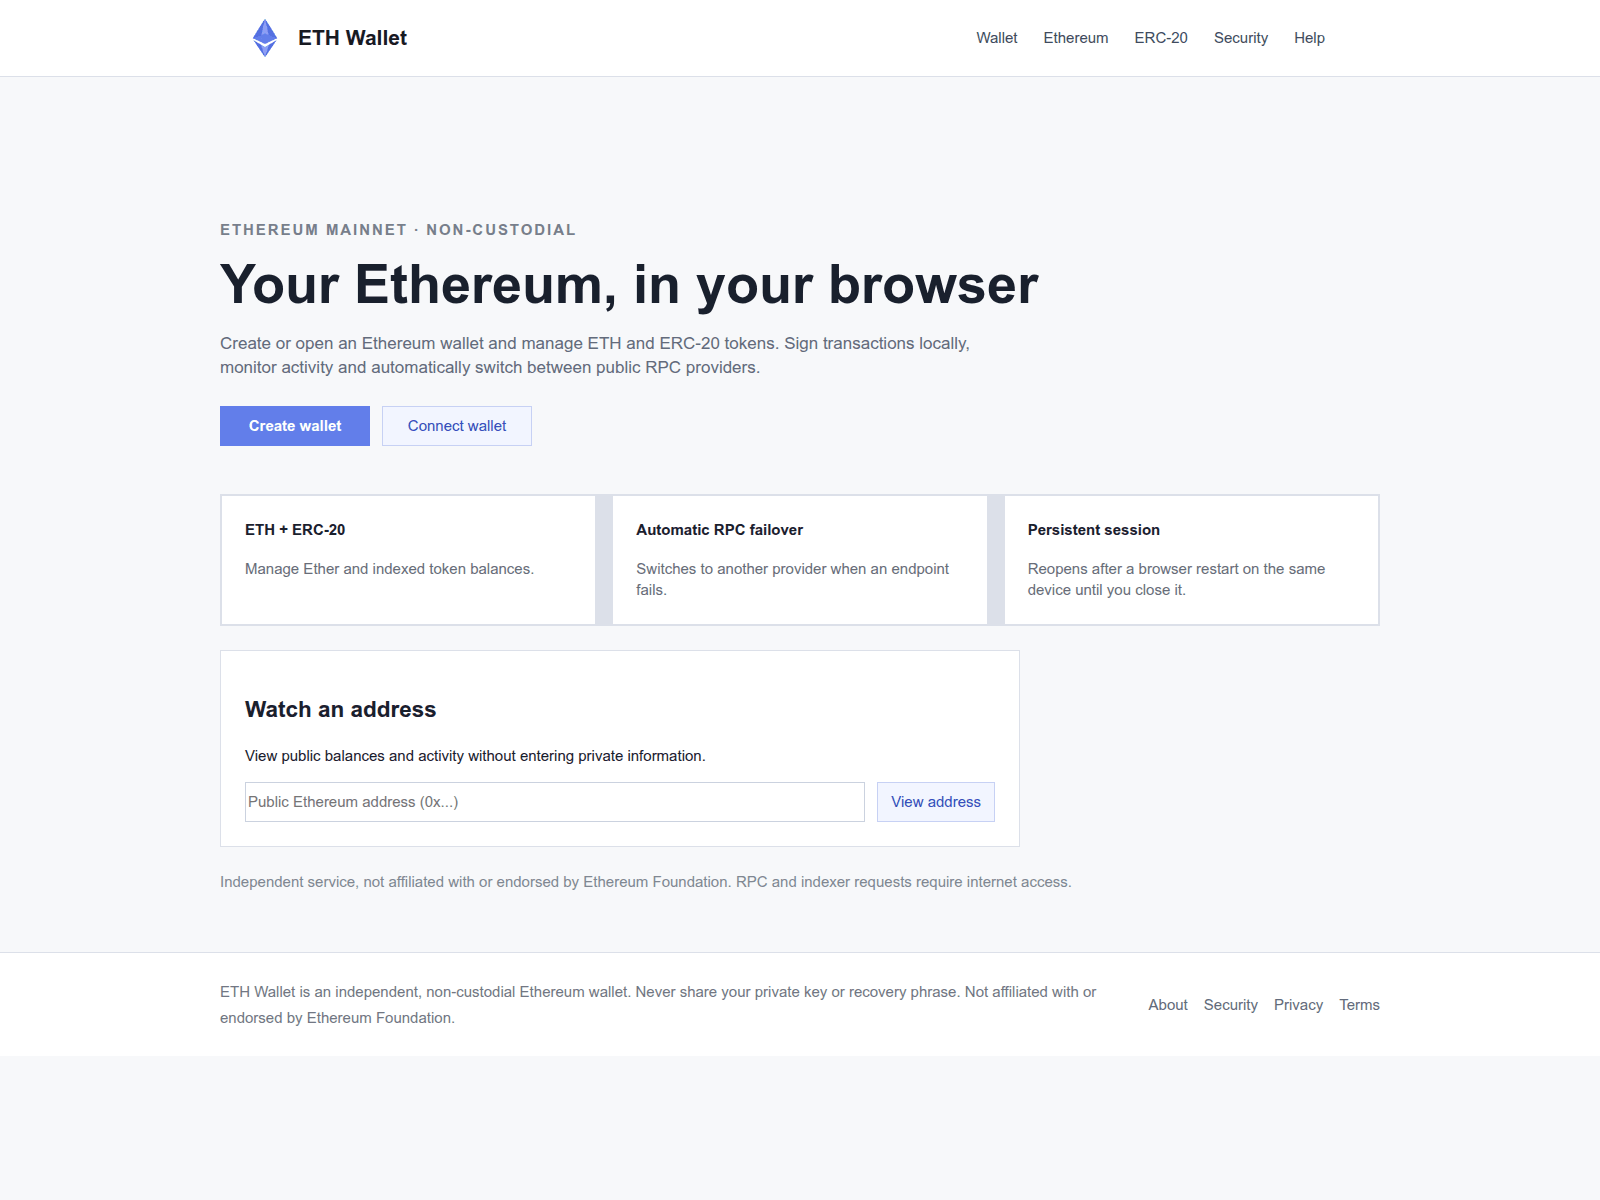
The site ethwebwallet.co impersonates an Ethereum browser wallet interface designed to harvest recovery phrases and private credentials. Anyone who interacted with this page should immediately transfer funds to a secure wallet and revoke any granted smart contract permissions.
URLScanによるキャプチャ · 2026-11-21 17:35 UTC · SHA-256 b16eaed7…7c186b8
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Fake Ethereum browser wallet layout and lures
The page opens with the header "ETH Wallet" and top navigation links for Wallet, Ethereum, ERC-20, Security, and Help. Its main headline reads "Your Ethereum, in your browser" directly above descriptive text stating "Create or open an Ethereum wallet and manage ETH and ERC-20 tokens." Two prominent buttons labeled "Create wallet" and "Connect wallet" invite immediate user interaction alongside feature boxes detailing automatic RPC failover and persistent sessions. Below these elements, a section titled "Watch an address" provides an input field for a "Public Ethereum address (0x...)" next to a "View address" button. The interface attempts to appear trustworthy while enticing visitors to click through and input sensitive security credentials.
Credential harvesting and independent security detections
When a visitor attempts to create or connect a wallet, the interface prompts for sensitive inputs such as recovery seed phrases and private passwords designed to compromise their funds. 11 of 92 VirusTotal engines flagged it on 21 Nov 2026, and MetaMask and SEAL block it, with Kaspersky, BitDefender and Sophos among them. PhishDestroy's evidence score for it is 80/100 (critical).
Domain registration history and lack of operational background
It was registered on 5 Nov 2026, 15 days before it was first reported, so the domain lacks any established operational history matching its claims of providing a trusted browser-based Ethereum management service. Operating with a newly registered domain is a common trait of phishing infrastructure built to capture digital assets before blocklists catch up.
ethwebwallet.co imitates an Ethereum browser wallet interface to steal recovery phrases and credentials, flagged by 11 VirusTotal engines. Avoid entering seeds.
AIによる要約
Fake Ethereum browser wallet layout and lures The page opens with the header "ETH Wallet" and top navigation links for Wallet, Ethereum, ERC-20, Security, and Help. Its main headline reads "Your Ethereum, in your browser" directly above descriptive text stating "Create or open an Ethereum wallet and manage ETH and ERC-20 tokens." Two prominent buttons labeled "Create wallet" and "Connect wallet" invite immediate user interaction alongside feature boxes detailing automatic RPC failover and persistent sessions. Below these elements, a section titled "Watch an address" provides an input field for a "Public Ethereum address (0x...)" next to a "View address" button. The interface attempts to appear trustworthy while enticing visitors to click through and input sensitive security credentials. Credential harvesting and independent security detections When a visitor attempts to create or connect a wallet, the interface prompts for sensitive inputs such as recovery seed phrases and private passwords designed to compromise their funds. 11 of 92 VirusTotal engines flagged it on 21 Nov 2026, and MetaMask and SEAL block it, with Kaspersky, BitDefender and Sophos among them. PhishDestroy's evidence score for it is 80/100 (critical). Domain registration history and lack of operational background It was registered on 5 Nov 2026, 15 days before it was first reported, so the domain lacks any established operational history matching its claims of providing a trusted browser-based Ethereum management service. Operating with a newly registered domain is a common trait of phishing infrastructure built to capture digital assets before blocklists catch up.
This website does not have many visitors We found many low rated websites on the same server Several spammers and scammers use the same registrar We detected cryptocurrency services which can be high risk This website has only been registered recently.
According to the SSL check the certificate is valid DNSFilter considers this website safe
エビデンスレイヤーAvailability: Reachable but protectedDNS: Resolved
最新のHTTP観測結果アクセス可能だが保護されているCaptchaChallenge85%2026-11-22 11:59 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 TLD Registrar Solutions
 31.220.3.200


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT