元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
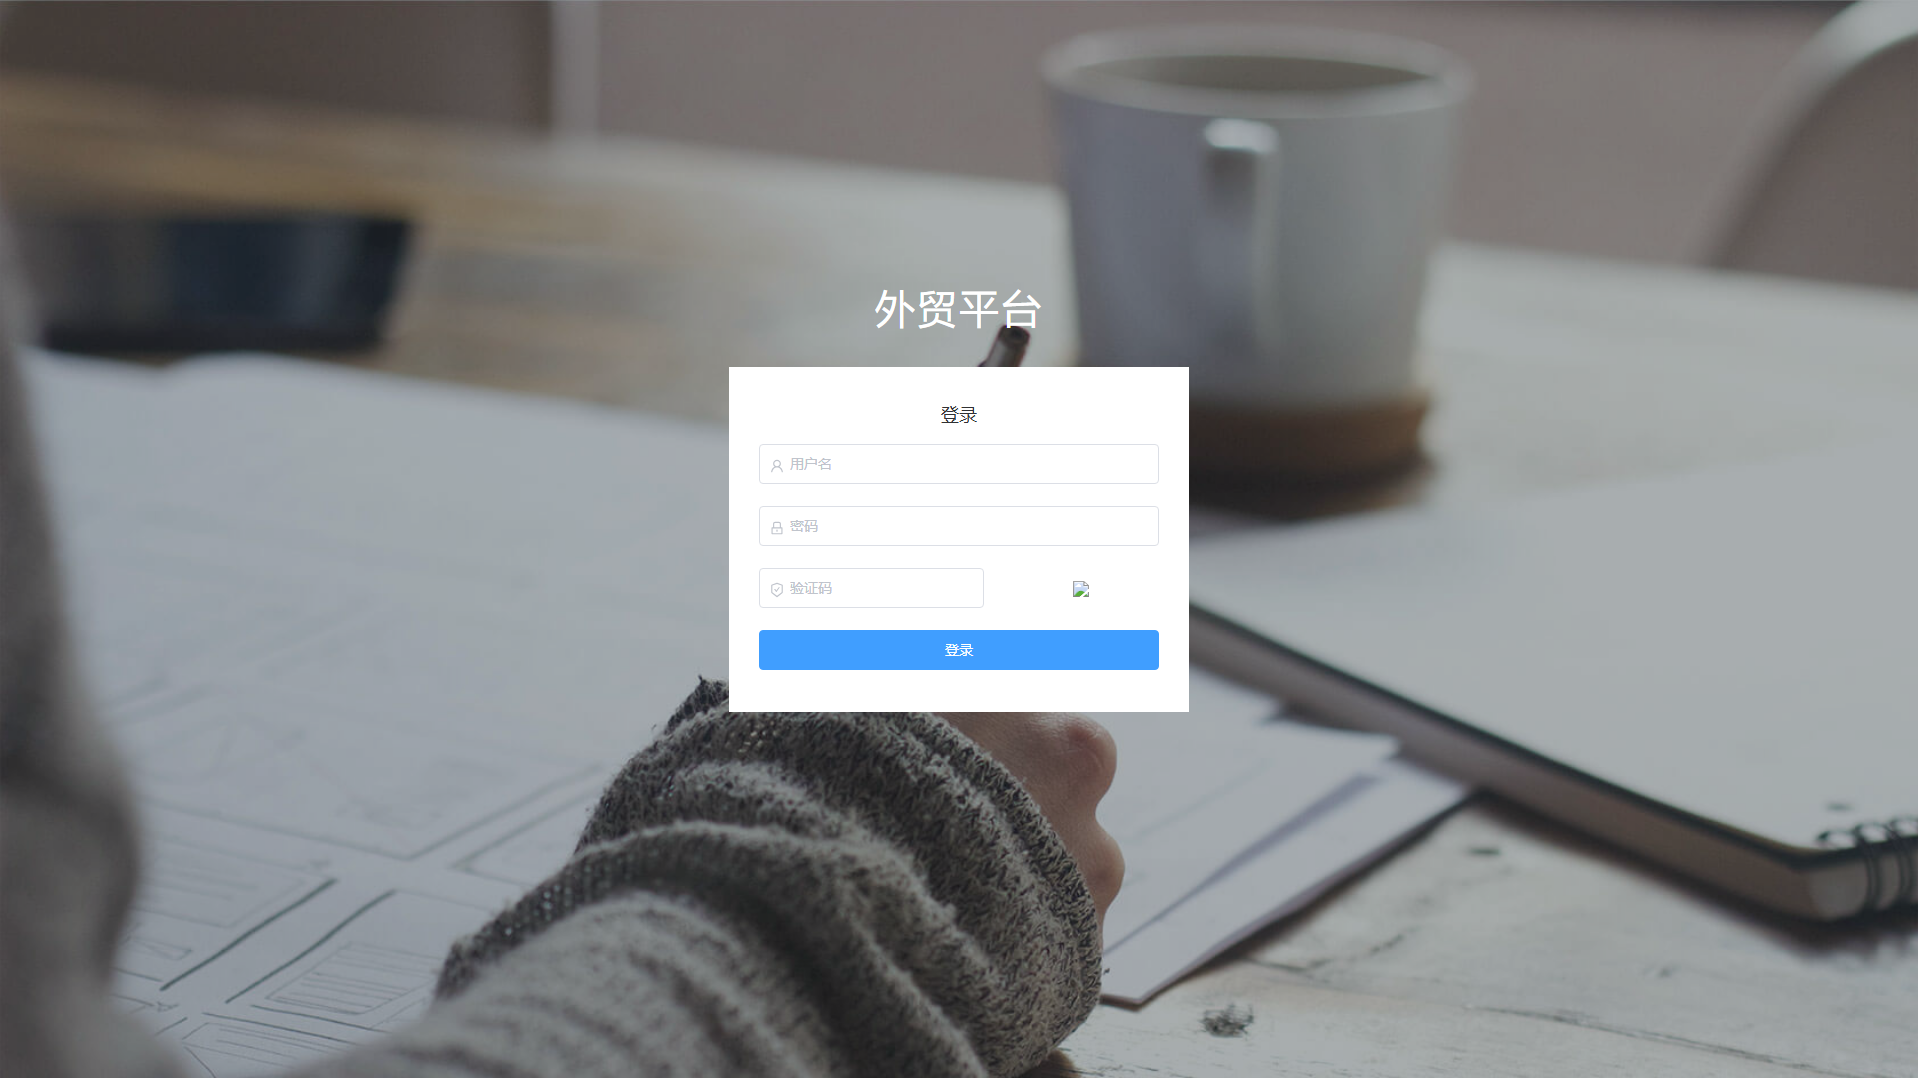
The captured screenshot from 2026-10-25 shows a Chinese-language page headed 外贸平台 with a login card offering username, password and verification-code fields and a blue 登录 button over a desk photograph. PhishDestroy classified ebaymediagmdi.com as Impersonation after first seeing it on 2026-10-25.
詐欺の手口
The page imitates a familiar platform login so visitors type their username, password and captcha into fields controlled by the operator. Any submitted credentials could be replayed against the genuine service or reused elsewhere, which is the standard credential-harvesting risk of such landing pages. Visitors typically reach it from an unsolicited link or message.
証拠
The captured screenshot shows the username, password and captcha inputs together with the 登录 submission button, the observed lure. urlscan's ML engine scored the page malicious at 98 on 2026-10-25 although its overall verdict was not malicious, while Cloudflare Radar returned a malicious phishing verdict on 2026-10-25. VirusTotal flagged the domain as malicious, with Fortinet labelling it phishing. Google Safe Browsing reported SOCIAL_ENGINEERING on 2026-10-26 and Spamhaus DBL recorded no listing on 2026-10-25; OTX held 0 pulses on 2026-10-25; Phishunt and PhishDestroy blocklists flagged it; a 307 redirect funneled plain HTTP to HTTPS; and inspection recorded webpackJsonp globals showing a webpack-built front end, 163 tracker requests, and 3 script SHA256 hashes including d718edcd98cb.
インフラ
Registration was created 2026-08-20 through Aceville Pte. Ltd., and hosting was recorded behind Cloudflare with its WAF present on 2026-10-25. Notable weaknesses: CSP, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy and COOP/COEP/CORP all absent; HSTS present with max-age=31536000 but no includeSubDomains; no SPF lookups, DKIM or DMARC recorded; CAA present; DNSSEC unsigned; TLS 1.3, TLS-AES-256-GCM-SHA384, forward secrecy, ALPN h2.
What to do
If you entered credentials on ebaymediagmdi.com, change your password on the genuine service and enable two-factor authentication, and do not reuse that password elsewhere. Treat any message linking to the domain as hostile and report it to PhishDestroy. Defenders should block ebaymediagmdi.com at proxy, DNS and mail gateways and add the recorded script hashes to hunting.
PhishDestroy assesses ebaymediagmdi.com as an impersonation phishing page that presents a fake login form to capture credentials.
AIによる要約
Overview The captured screenshot from 2026-10-25 shows a Chinese-language page headed 外贸平台 with a login card offering username, password and verification-code fields and a blue 登录 button over a desk photograph. PhishDestroy classified ebaymediagmdi.com as Impersonation after first seeing it on 2026-10-25. How the scam works The page imitates a familiar platform login so visitors type their username, password and captcha into fields controlled by the operator. Any submitted credentials could be replayed against the genuine service or reused elsewhere, which is the standard credential-harvesting risk of such landing pages. Visitors typically reach it from an unsolicited link or message. Evidence The captured screenshot shows the username, password and captcha inputs together with the 登录 submission button, the observed lure. urlscan's ML engine scored the page malicious at 98 on 2026-10-25 although its overall verdict was not malicious, while Cloudflare Radar returned a malicious phishing verdict on 2026-10-25. VirusTotal flagged the domain as malicious, with Fortinet labelling it phishing. Google Safe Browsing reported SOCIAL_ENGINEERING on 2026-10-26 and Spamhaus DBL recorded no listing on 2026-10-25; OTX held 0 pulses on 2026-10-25; Phishunt and PhishDestroy blocklists flagged it; a 307 redirect funneled plain HTTP to HTTPS; and inspection recorded webpackJsonp globals showing a webpack-built front end, 163 tracker requests, and 3 script SHA256 hashes including d718edcd98cb. Infrastructure Registration was created 2026-08-20 through Aceville Pte. Ltd., and hosting was recorded behind Cloudflare with its WAF present on 2026-10-25. Notable weaknesses: CSP, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy and COOP/COEP/CORP all absent; HSTS present with max-age=31536000 but no includeSubDomains; no SPF lookups, DKIM or DMARC recorded; CAA present; DNSSEC unsigned; TLS 1.3, TLS-AES-256-GCM-SHA384, forward secrecy, ALPN h2. What to do If you entered credentials on ebaymediagmdi.com, change your password on the genuine service and enable two-factor authentication, and do not reuse that password elsewhere. Treat any message linking to the domain as hostile and report it to PhishDestroy. Defenders should block ebaymediagmdi.com at proxy, DNS and mail gateways and add the recorded script hashes to hunting. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a17379-9677-7467-a2eb-688823efb52e/ Cloudflare Radar report: https://radar.cloudflare.com/scan/f93e84b2-eb17-483f-895a-89e58d836a8d URLQuery report: https://urlquery.net/report/9a9aa775-4a90-4767-804e-14e51dad64ee Stored capture screenshot: https://i.ibb.co/9mV7z9Zt/0874b010512b.png Cloudflare Radar screenshot (2026-10-25T14:30:46Z): https://screenshots.phishdestroy.io/cf/f93e84b2-eb17-483f-895a-89e58d836a8d.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/9a9aa775-4a90-4767-804e-14e51dad64ee.png URLScan screenshot (2026-08-20T13:03:32Z): https://screenshots.phishdestroy.io/us/01a01f44-c425-70bf-974a-56c3bb99c36d.png URLScan capture report: https://urlscan.io/result/01a01f44-c425-70bf-974a-56c3bb99c36d/ URLScan screenshot (2026-10-18T18:47:06Z): https://screenshots.phishdestroy.io/us/01a15056-9f75-747f-8d70-9655f4447e5b.png URLScan capture report: https://urlscan.io/result/01a15056-9f75-747f-8d70-9655f4447e5b/ URLScan screenshot (2026-10-18T18:47:52Z): https://screenshots.phishdestroy.io/us/01a15057-58bb-75e9-a492-3863b4cdf908.png URLScan capture report: https://urlscan.io/result/01a15057-58bb-75e9-a492-3863b4cdf908/ URLScan screenshot (2026-10-19T10:19:44Z): https://screenshots.phishdestroy.io/us/01a153ac-893a-70bc-a971-419a958e5256.png URLScan capture report: https://urlscan.io/result/01a153ac-893a-70bc-a971-419a958e5256/ URLScan screenshot (2026-10-19T22:53:47Z): https://screenshots.phishdestroy.io/us/01a1565e-e120-75cb-b43c-eea71f86193b.png URLScan capture report: https://urlscan.io/result/01a1565e-e120-75cb-b43c-eea71f86193b/ URLScan screenshot (2026-10-21T18:44:45Z): https://screenshots.phishdestroy.io/us/01a15fc7-91ae-7618-bdbb-72a00f6650ef.png URLScan capture report: https://urlscan.io/result/01a15fc7-91ae-7618-bdbb-72a00f6650ef/ VirusTotal report: https://www.virustotal.com/gui/domain/ebaymediagmdi.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=ebaymediagmdi.com Archived copy: https://web.archive.org/web/20261025142621/https://ebaymediagmdi.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/

 188.114.97.3


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT