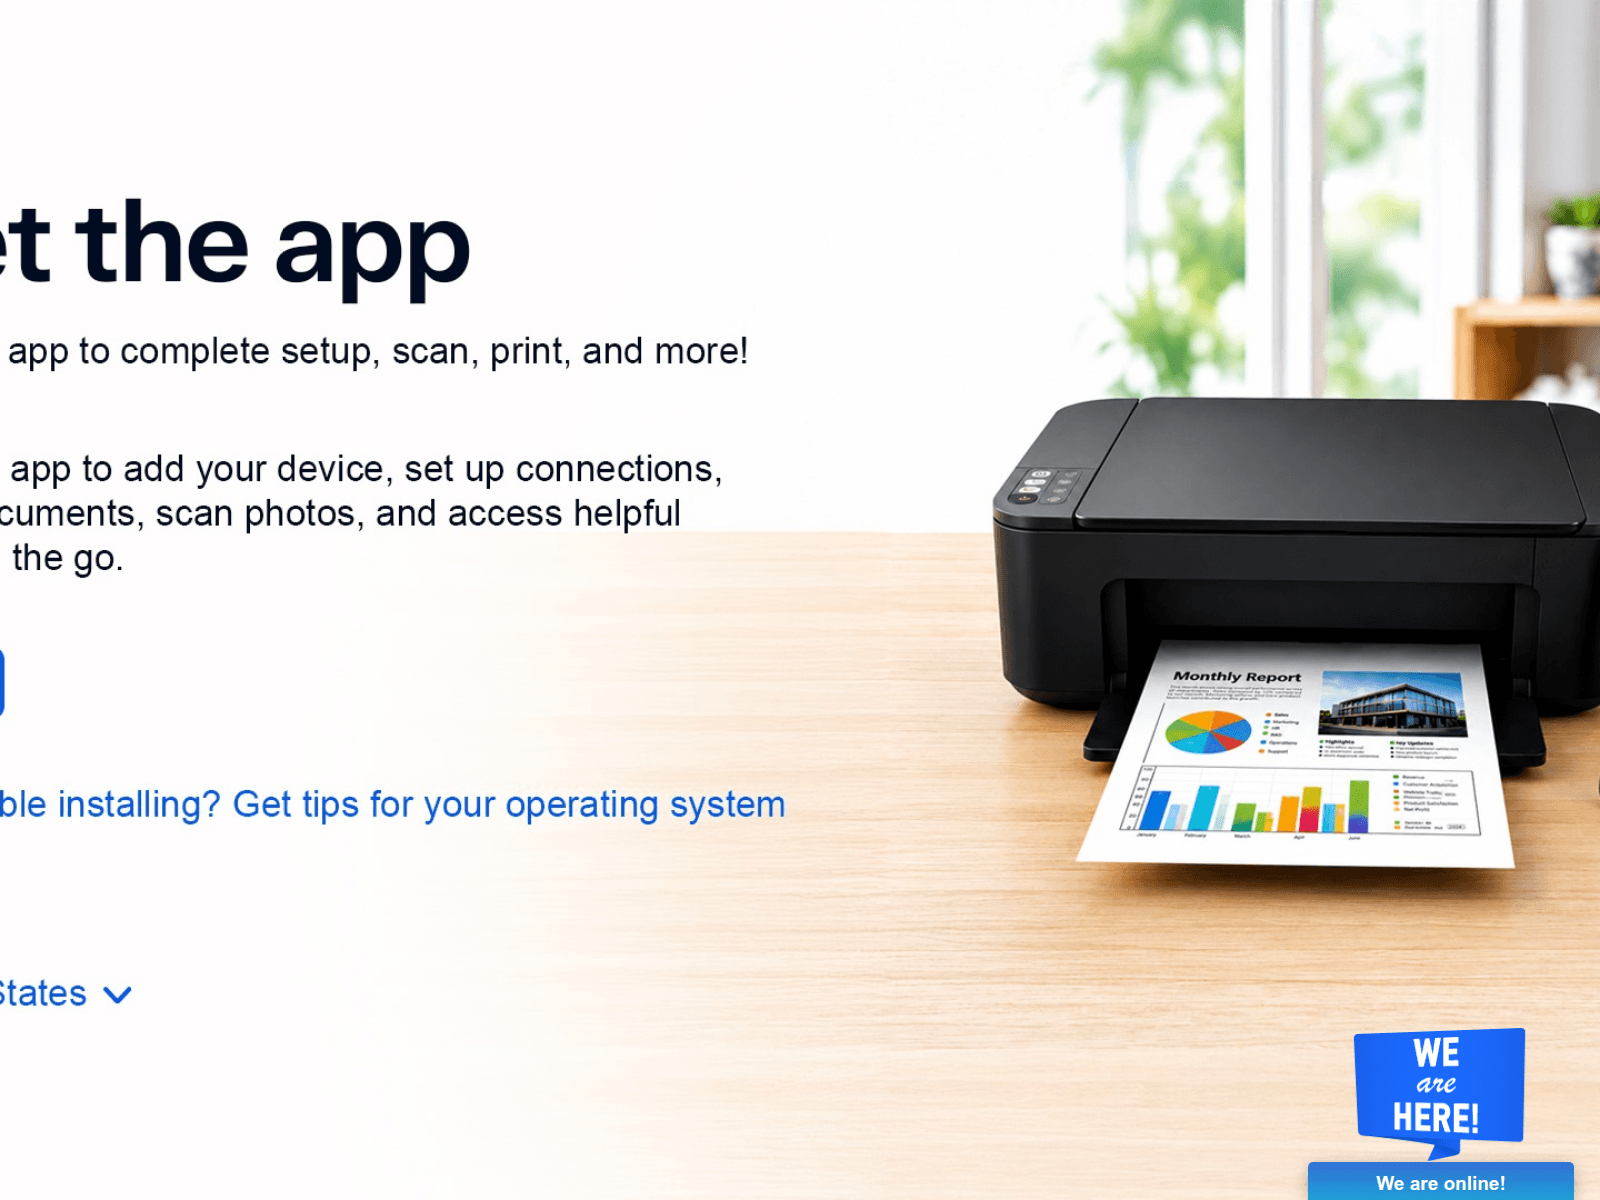
The drivershubnet.co page displays a setup utility prompting visitors to download an application for printer configuration and document management. If you have downloaded and installed software from this site, remove the application immediately and run a security scan.
URLScanによるキャプチャ · 2026-11-21 21:39 UTC · SHA-256 8666c1de…2f9cdea
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Printer application download interface
The page on drivershubnet.co features a clean layout centered around printer setup and utility installation. Large headings invite the visitor to "Get the app" in order "to complete setup, scan, print, and more!" Accompanying text encourages users to add devices, establish connections, and handle document workflows on the go. An image of a modern desktop printer with a printed monthly report sits on a wooden desk alongside interface elements like a regional dropdown menu and floating chat badges stating "WE are HERE!" and "We are online!". The primary call to action directs visitors toward software installation links tailored to their operating system.
Utility portal context and telemetry
While drivershubnet.co presents itself as a routine driver and utility resource, 1 of 92 engines on VirusTotal flagged it on 25 Oct 2026. The domain was registered on 26 Aug 2026 through NAMECHEAP INC and it still responded on 21 Nov 2026 at 22:40 UTC, adding context to a newly active software distribution endpoint. Visitors encountering unfamiliar utility portals should verify whether the software genuinely originates from the device manufacturer before running any executable installer.
Recommended precautions
Visitors should exercise caution when encountering unexpected software distribution pages and verify the publisher identity before downloading executable files. If you already ran an installer downloaded from drivershubnet.co, disconnect the device from the network, remove the newly added application, and perform a full malware scan using trusted endpoint security software.
drivershubnet.co presents a desktop printer configuration app download utility and flagged by 1 VirusTotal engine from independent security checks.
AIによる要約
Printer application download interface The page on drivershubnet.co features a clean layout centered around printer setup and utility installation. Large headings invite the visitor to "Get the app" in order "to complete setup, scan, print, and more!" Accompanying text encourages users to add devices, establish connections, and handle document workflows on the go. An image of a modern desktop printer with a printed monthly report sits on a wooden desk alongside interface elements like a regional dropdown menu and floating chat badges stating "WE are HERE!" and "We are online!". The primary call to action directs visitors toward software installation links tailored to their operating system. Utility portal context and telemetry While drivershubnet.co presents itself as a routine driver and utility resource, 1 of 92 engines on VirusTotal flagged it on 25 Oct 2026. The domain was registered on 26 Aug 2026 through NAMECHEAP INC and it still responded on 21 Nov 2026 at 22:40 UTC, adding context to a newly active software distribution endpoint. Visitors encountering unfamiliar utility portals should verify whether the software genuinely originates from the device manufacturer before running any executable installer. Recommended precautions Visitors should exercise caution when encountering unexpected software distribution pages and verify the publisher identity before downloading executable files. If you already ran an installer downloaded from drivershubnet.co, disconnect the device from the network, remove the newly added application, and perform a full malware scan using trusted endpoint security software.
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Resolved
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:59 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:59 UTClast content: 2026-11-22 11:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 Namecheap


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT