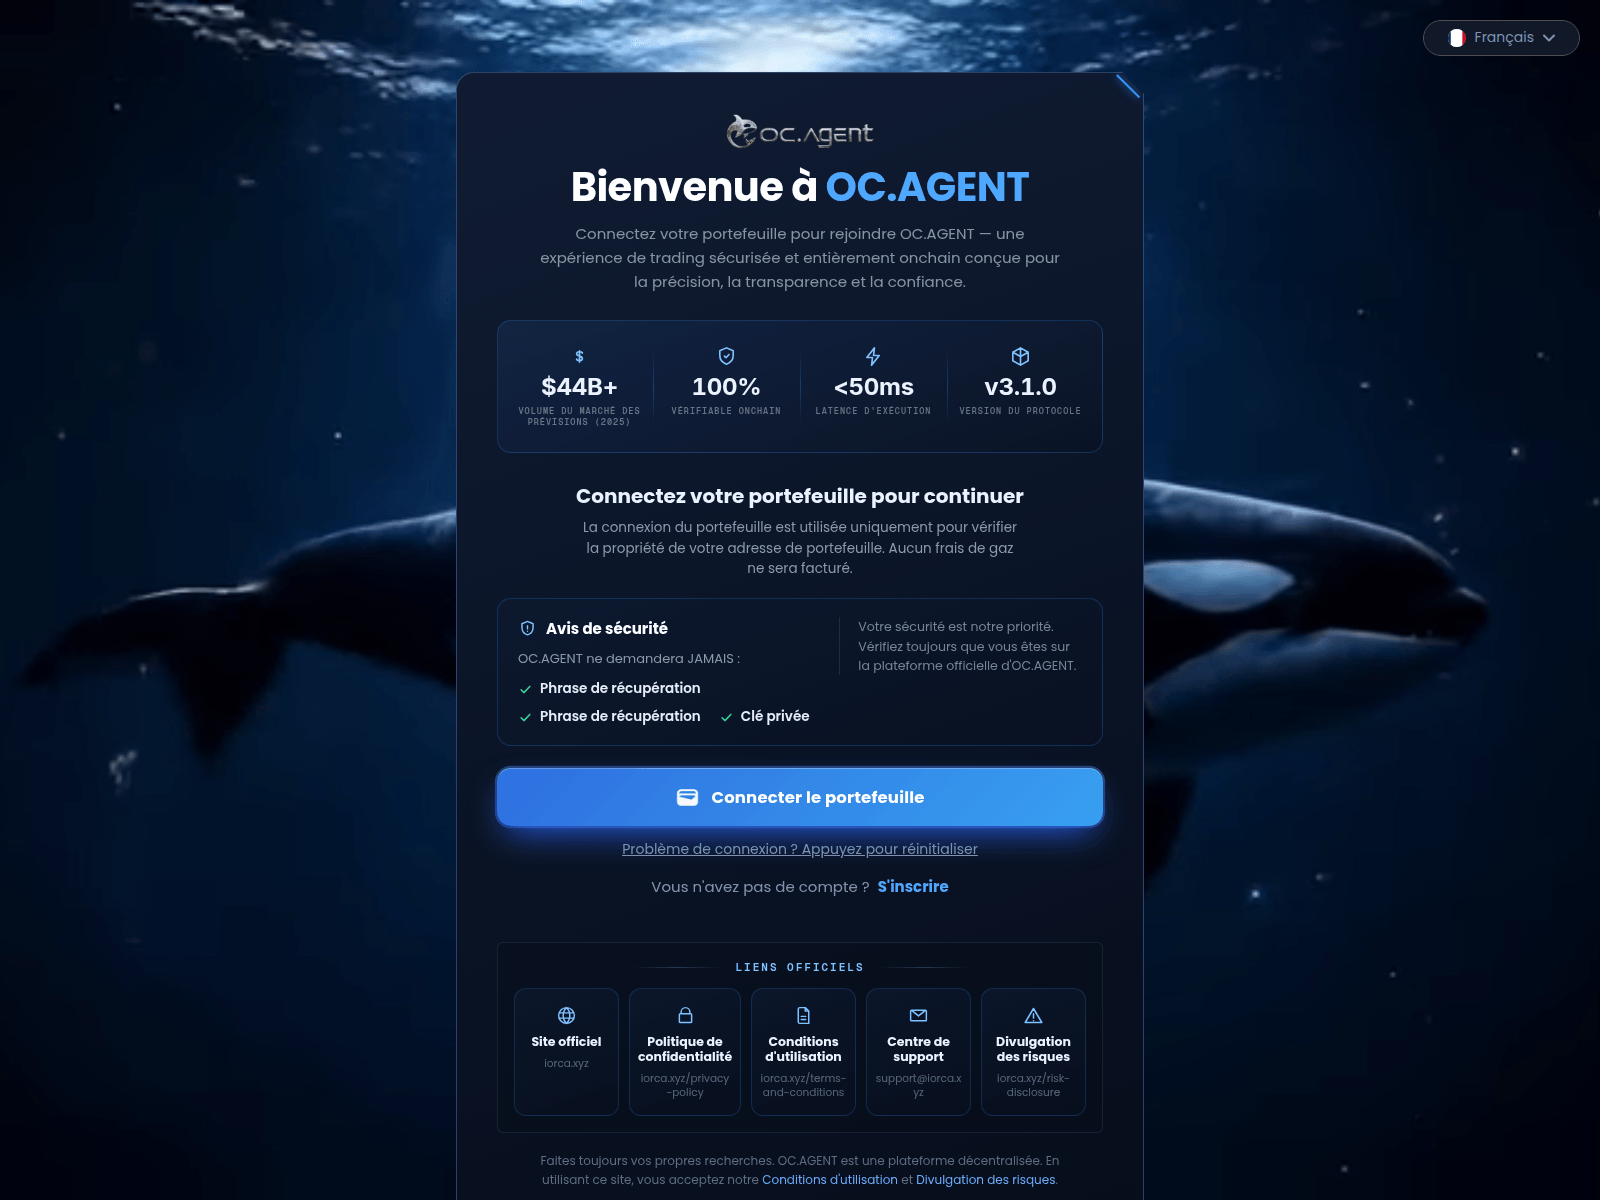
The dapp.ocagenthq.com page presents a French-language interface for OC.AGENT asking visitors to connect their Web3 wallet. If you already connected your wallet or signed a request on this site, immediately revoke any token allowances using an independent tool like Revoke.cash.
分析は英語でのみ利用可能です
ページタイトル: “OC.AGENT — AI Prediction Market Infrastructure”
URLScanによるキャプチャ · 2026-11-21 17:44 UTC · SHA-256 181bd4e4…9e085d2
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
OC.AGENT French wallet connection page layout
The page at dapp.ocagenthq.com displays a dark interface titled "Bienvenue à OC.AGENT" in French, featuring a logo and a headline that reads "Connectez votre portefeuille pour rejoindre OC.AGENT — une expérience de trading sécurisée". Four metric boxes highlight statistics including "$44B+", "100%", "<50ms", and "v3.1.0". A central section urges users to "Connectez votre portefeuille pour continuer", accompanied by a security notice stating "OC.AGENT ne demandera JAMAIS : Phrase de récupération, Clé privée". At the bottom, a prominent blue button invites the user to "Connecter le portefeuille", followed by official links pointing to iorca.xyz and various policy pages.
Wallet connection risks and security vendor telemetry
By prompting visitors to link their Web3 wallet via tools like WalletConnect or Web3Modal, the site positions itself to request token approvals or signature permissions that could drain connected assets. Supporting this risk, VirusTotal showed 3 of 92 engines flagging it on 21 Nov 2026, and ScamSniffer blocks it, with Forcepoint ThreatSeeker, CRDF and Gridinsoft explicitly classifying the address as malicious or phishing. Additionally, PhishDestroy scores the evidence against it at 55/100 (high).
What happens if you connect your wallet
When a visitor clicks the connection button and approves the Web3 prompt, the underlying scripts can request malicious token allowances or permit smart contracts to transfer deposited assets without further authorization. Because the interface mimics a legitimate trading platform while routing visitors away from the official iorca.xyz domain, victims often believe they are merely authenticating their identity. Once permissions are granted, attackers can sweep funds from the wallet at any time.
Recommended actions for connected visitors
If you have already interacted with dapp.ocagenthq.com, you should immediately open an independent token revocation tool like Revoke.cash to inspect and cancel any active allowances granted to unfamiliar contracts. Disconnect your Web3 wallet from the site entirely and clear your browser session data to prevent lingering connections. Always verify that you are navigating to official project domains rather than unverified subdomains.
dapp.ocagenthq.com — OC.AGENT French trading interface
AIによる説明
dapp.ocagenthq.com asks visitors to connect a Web3 wallet to OC.AGENT, and is flagged by 3 VirusTotal engines. Do not approve unknown requests.
AIによる要約
OC.AGENT French wallet connection page layout The page at dapp.ocagenthq.com displays a dark interface titled "Bienvenue à OC.AGENT" in French, featuring a logo and a headline that reads "Connectez votre portefeuille pour rejoindre OC.AGENT — une expérience de trading sécurisée". Four metric boxes highlight statistics including "$44B+", "100%", "<50ms", and "v3.1.0". A central section urges users to "Connectez votre portefeuille pour continuer", accompanied by a security notice stating "OC.AGENT ne demandera JAMAIS : Phrase de récupération, Clé privée". At the bottom, a prominent blue button invites the user to "Connecter le portefeuille", followed by official links pointing to iorca.xyz and various policy pages. Wallet connection risks and security vendor telemetry By prompting visitors to link their Web3 wallet via tools like WalletConnect or Web3Modal, the site positions itself to request token approvals or signature permissions that could drain connected assets. Supporting this risk, VirusTotal showed 3 of 92 engines flagging it on 21 Nov 2026, and ScamSniffer blocks it, with Forcepoint ThreatSeeker, CRDF and Gridinsoft explicitly classifying the address as malicious or phishing. Additionally, PhishDestroy scores the evidence against it at 55/100 (high). What happens if you connect your wallet When a visitor clicks the connection button and approves the Web3 prompt, the underlying scripts can request malicious token allowances or permit smart contracts to transfer deposited assets without further authorization. Because the interface mimics a legitimate trading platform while routing visitors away from the official iorca.xyz domain, victims often believe they are merely authenticating their identity. Once permissions are granted, attackers can sweep funds from the wallet at any time. Recommended actions for connected visitors If you have already interacted with dapp.ocagenthq.com, you should immediately open an independent token revocation tool like Revoke.cash to inspect and cancel any active allowances granted to unfamiliar contracts. Disconnect your Web3 wallet from the site entirely and clear your browser session data to prevent lingering connections. Always verify that you are navigating to official project domains rather than unverified subdomains.


 Dynadot
 172.67.218.230


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT