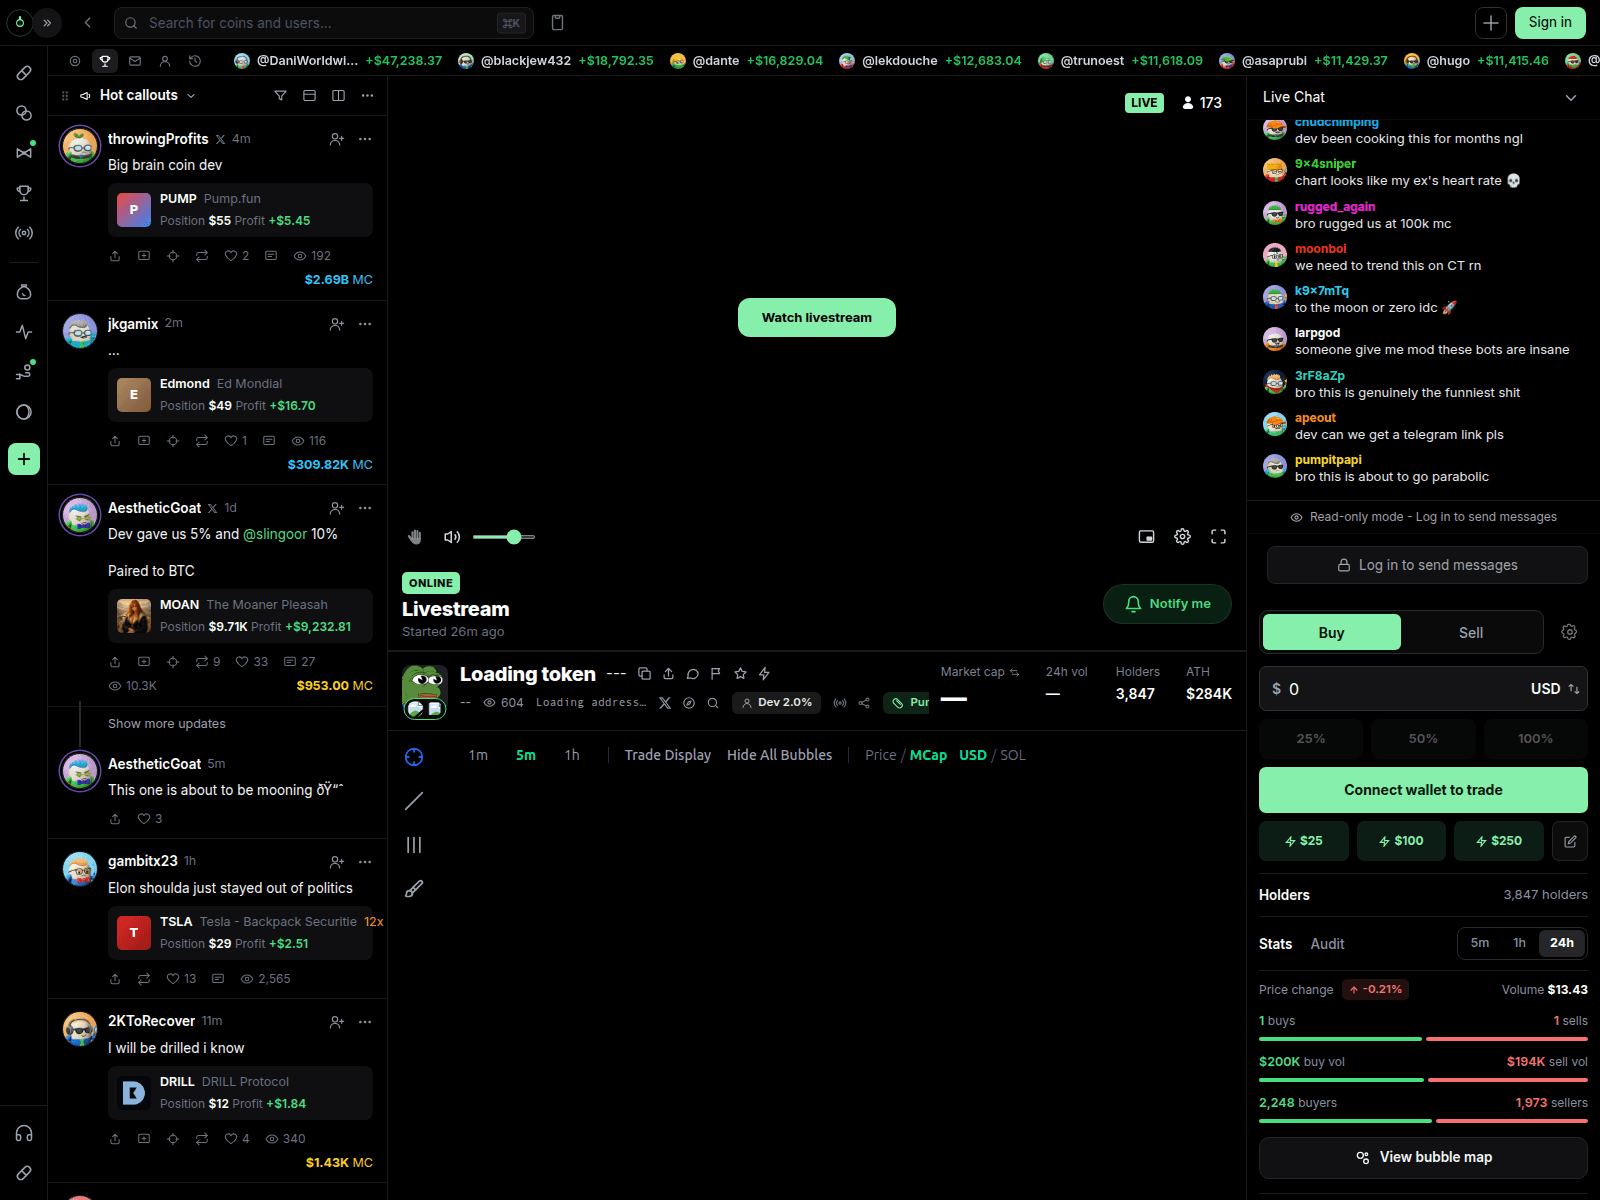
The site coin-stream.fun copies Pump.fun, featuring a mock livestream and a prominent button asking visitors to connect their cryptocurrency wallet. If you connected your wallet, immediately revoke any token approvals granted to unfamiliar contracts.
URLScanによるキャプチャ · 2026-11-21 17:41 UTC · SHA-256 a1f290b8…718d7c1
PhishDestroyの分析(レビュー済み版)
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Interface design and wallet prompt
The page on coin-stream.fun mimics the layout and dark theme of Pump.fun, displaying a sidebar with live coin updates, chat messages on the right, and a central video player area labeled "Watch livestream". The interface shows simulated trading statistics, holder counts, and buy-and-sell panels with buttons marked "Buy", "Sell", and a large green "Connect wallet to trade" button. Visitors are expected to click the connection prompt to interact with the mock token stream, which pulls in reown and wagmi libraries to initiate wallet connections. VirusTotal showed 3 of 92 engines flagging it on 21 Nov 2026, and MetaMask and SEAL block it, with Forcepoint ThreatSeeker, Gridinsoft and alphaMountain.ai among them. PhishDestroy scores the evidence against it at 60/100 (high). It was registered on 19 Nov 2026, 2 days before it was first reported, while the interface presents active trading volumes and numerous user interactions that suggest an established platform.
Risks of connecting a wallet
When a visitor clicks the connection prompt, the underlying scripts use reown and wagmi to request access to the user's cryptocurrency wallet. Malicious interfaces using this setup typically request token approvals or signature permissions that allow automated drains of assets from connected accounts. Because the official platform operates at pump.fun, this copycat address exists solely to intercept visitor wallet sessions.
Recommended precautions
Users who have not interacted with coin-stream.fun should avoid the address entirely and use pump.fun for the genuine service. Anyone who already connected a wallet should immediately open their wallet settings, check active connections, and revoke permissions granted to unrecognized applications.
coin-stream.fun — Pump.fun clone with wallet prompt
AIによる説明
coin-stream.fun imitates Pump.fun with chat feeds and trade panels, urging visitors to connect their wallet, flagged by 3 VirusTotal engines.
AIによる要約
Interface design and wallet prompt The page on coin-stream.fun mimics the layout and dark theme of Pump.fun, displaying a sidebar with live coin updates, chat messages on the right, and a central video player area labeled "Watch livestream". The interface shows simulated trading statistics, holder counts, and buy-and-sell panels with buttons marked "Buy", "Sell", and a large green "Connect wallet to trade" button. Visitors are expected to click the connection prompt to interact with the mock token stream, which pulls in reown and wagmi libraries to initiate wallet connections. VirusTotal showed 3 of 92 engines flagging it on 21 Nov 2026, and MetaMask and SEAL block it, with Forcepoint ThreatSeeker, Gridinsoft and alphaMountain.ai among them. PhishDestroy scores the evidence against it at 60/100 (high). It was registered on 19 Nov 2026, 2 days before it was first reported, while the interface presents active trading volumes and numerous user interactions that suggest an established platform. Risks of connecting a wallet When a visitor clicks the connection prompt, the underlying scripts use reown and wagmi to request access to the user's cryptocurrency wallet. Malicious interfaces using this setup typically request token approvals or signature permissions that allow automated drains of assets from connected accounts. Because the official platform operates at pump.fun, this copycat address exists solely to intercept visitor wallet sessions. Recommended precautions Users who have not interacted with coin-stream.fun should avoid the address entirely and use pump.fun for the genuine service. Anyone who already connected a wallet should immediately open their wallet settings, check active connections, and revoke permissions granted to unrecognized applications.


 Dynadot
 168.113.215.192


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT